
ट्रैक किए गए डोमेन खोजें और संग्रहीत साक्ष्य, डिटेक्शन और नवीनतम देखी गई उपलब्धता की समीक्षा करें।
219,828
कुल ट्रैक किए गए
213,490
वीटी का पता चला
91,923
अंतिम बार सक्रिय देखा गया
127,905
अंतिम जाँच पर अनुपलब्ध
576
वीटी लंबित

How This Attack Works
The scam exploits growing awareness of AML/KYC compliance requirements in crypto. Users who want to verify their funds are "clean" land on a convincing clone and unknowingly authorize a wallet drainer.
STEP 1
Lure via Search & Social
Victims encounter fake AML check sites through Google Ads, टेलीग्राम DMs, social media posts, or SEO-poisoned search results for queries like "check wallet AML" or "is my crypto clean."
STEP 2
Clone Legitimate UI
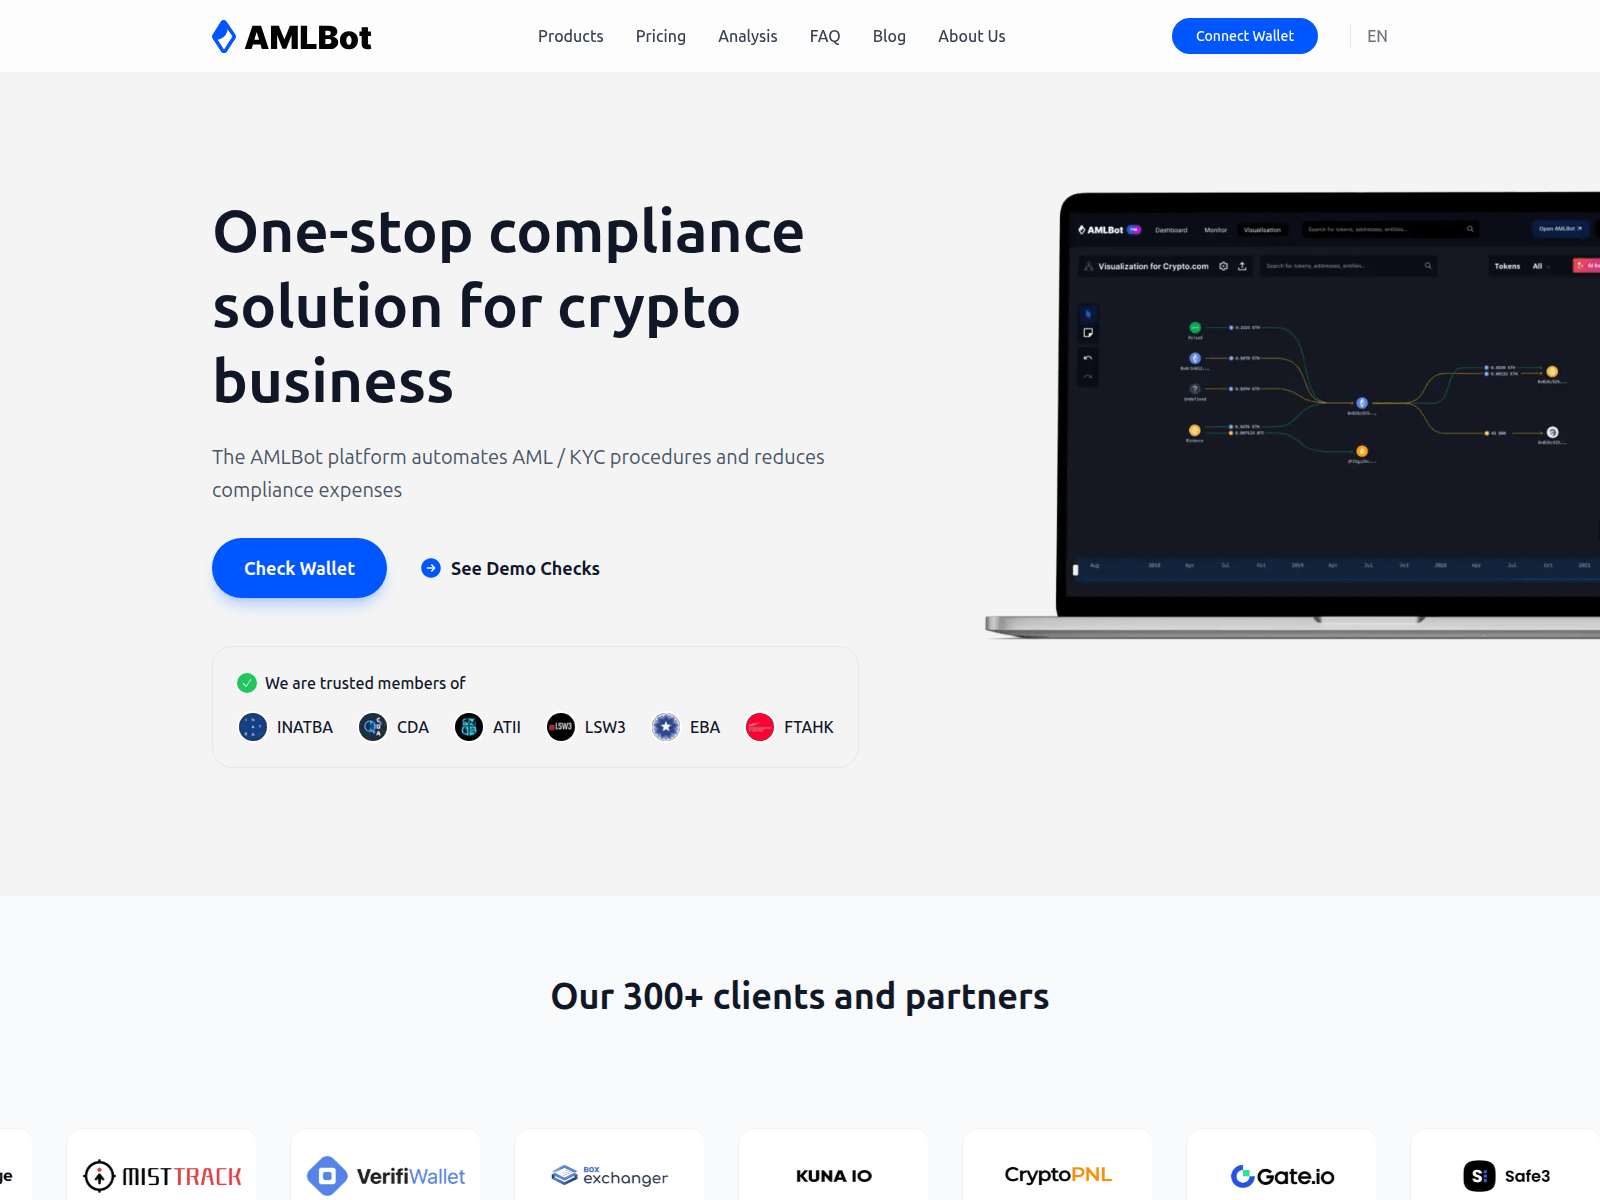
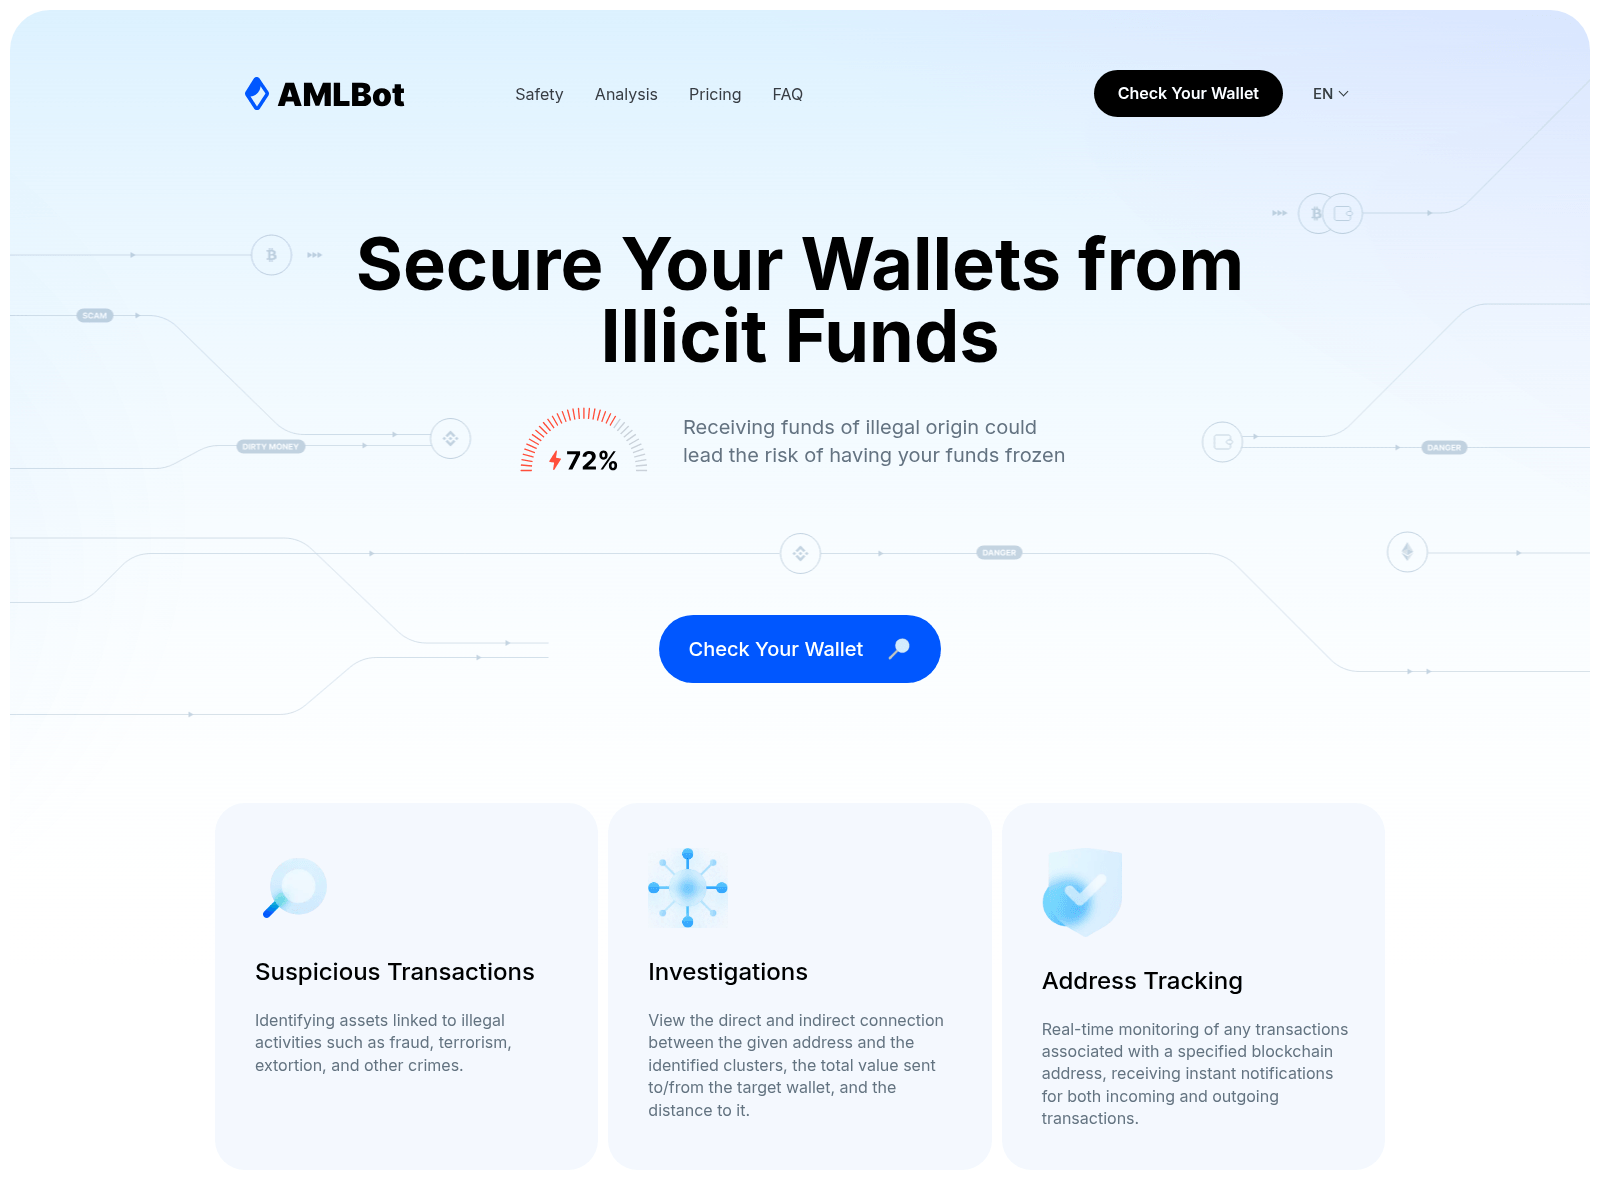
The site closely mimics the official AMLBot.com design, branding, and interface. Some clones replicate staff profiles and create fake टेलीग्राम accounts impersonating AMLBot team members.
STEP 3
Request Wallet Connection
Unlike the real AMLBot (which only needs a wallet address as text input), the fake site asks users to "connect wallet" via MetaMask or WalletConnect to "generate an AML report."
STEP 4
Drain Assets via Smart Contract
The wallet connection triggers a malicious smart contract (setApprovalForAll or token approval) that scans all tokens/NFTs, prioritizes highest-value assets, and drains everything to attacker-controlled wallets. Transactions are irreversible.
Technical Analysis
The AML scam ecosystem uses sophisticated infrastructure. डोमेन typically use .com, .org, .app TLDs registered through privacy-friendly registrars (NICENIC, WEBCC account for 163+ domains). Many use Cloudflare CDN for legitimacy.
The drainer mechanism is identical to other wallet-connect phishing: upon connection, the site calls setApprovalForAll() or increaseAllowance() on the victim's token contracts. The drainer scans all assets, estimates value, and prioritizes extraction of highest-value tokens first.
According to AMLBot's 2025 Crypto Crime रिपोर्ट, 65% of crypto incidents are driven by social engineering rather than technical exploits, with phishing ranking as the #2 attack type (18% of all incidents).
Key technical indicators: domains containing 'aml', 'amlbot', 'aml-check', 'aml-verify' in the URL; wallet connection prompts (the real AMLBot never requires this); recently registered domains; missing or fake एसएसएल certificates.
Real Cases
AMLBot Clone Wave (2024-2026) (2024-2026)
1,350+ fake domains stolen
AMLBot officially warned about an alarming rise in scammers impersonating AMLBot on various platforms, including fake टेलीग्राम bots and clone websites.
amlcheckwallet.cc Drainer (2024)
Wallet drainer active stolen
Registered via Dynadot Inc, resolved to Cloudflare IP 104.21.25.10. Served a fake "AML wallet check" interface with wallet-connect drainer. PhishDestroy report.
PCRisk AML Warning (Jan 2026) (January 2026)
12+ documented domains stolen
PCRisk documented a new wave of fake AMLBot sites including amlbotchecks.com, aml-safety.app, amlrobotsaveru.com, amlpremium.top. FTC reports over 46,000 people lost $1 billion to crypto scams since 2021. PCRisk report.
amlbotchecking.com Campaign (2024)
Multiple victims stolen
Typosquat of AMLBot serving crypto drainer via fake compliance check UI. Documented by Malware Guide and PCRisk.
How to Detect
Site asks to "connect wallet" — the real AMLBot only needs a wallet ADDRESS as text input, never a wallet connection
डोमेन contains "aml" variations: amlbot, aml-check, aml-verify, amlcrypto (verify against official amlbot.com)
Recently registered domain (check कौन है — legitimate AML services have years of history)
अत्यावश्यक messaging: "Your wallet may be flagged" or "जाँचें compliance before funds are frozen"
Promoted via टेलीग्राम DMs, Google Ads, or unsolicited emails instead of organic search
How to Protect Yourself
1
Bookmark the official AMLBot at amlbot.com — never click links from ads, DMs, or emails
2
Remember: legitimate AML tools only need a wallet address (text), never a wallet connection or private keys
3
जाँचें any AML domain on PhishDestroy before interacting with it
4
Use a separate "burner" wallet with minimal funds when testing any new DeFi/Web3 service
5
If you connected your wallet to a suspicious site: immediately transfer remaining funds to a NEW wallet and revoke approvals at रद्द करें.कैश
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,109 domains tracked for this threat type
Fake AML जाँचें Scam 2,109 domains

amlprobot.org

amlprotect.app
amlprotection.online

amlrating.net


amlscan.zip

amlscanning.com

amlsecure.rest

amlsecuritywallet.org

amlshield.site
amlspace.com

amlsystemcheck.com

amltronscan.com

amltronscan.xyz

amltrust.sbs

amltrustwallet.help
amlunion.com

amlverifier.guru

amlvex.com

amlwalletverification.com
amly.shop

app-amlbot.com

audit-aml.net
authb-umusic-com-saml20-idp-st.atoms.world
botamls.pro

business-aml.com
bybitaml.icu

bybitamlverification.online
chainguard-aml.com
clear-aml.com

crpto.shop

cryptoaml-check.com

cryptomuspayye.icu

egean.ciamlogin.com
egfin.app

eip-dapp-restore.xyz
eth-compliance.app

exploreraml.com
ext-en-coinbsewlet.daftpage.com

fcjknkjdsnckjwjkkke.com
fiskgkr.pages.dev

free-aml-checks.org

gzsm.com
hebaxy.xyz
in-gate.cc

invoice-coinbase.com
kamlno.cfd
learn.by-bita.com
myamlchecker.sbs

pdf.streamlinedweb.de

pidort.pages.dev
quickamlbot.com
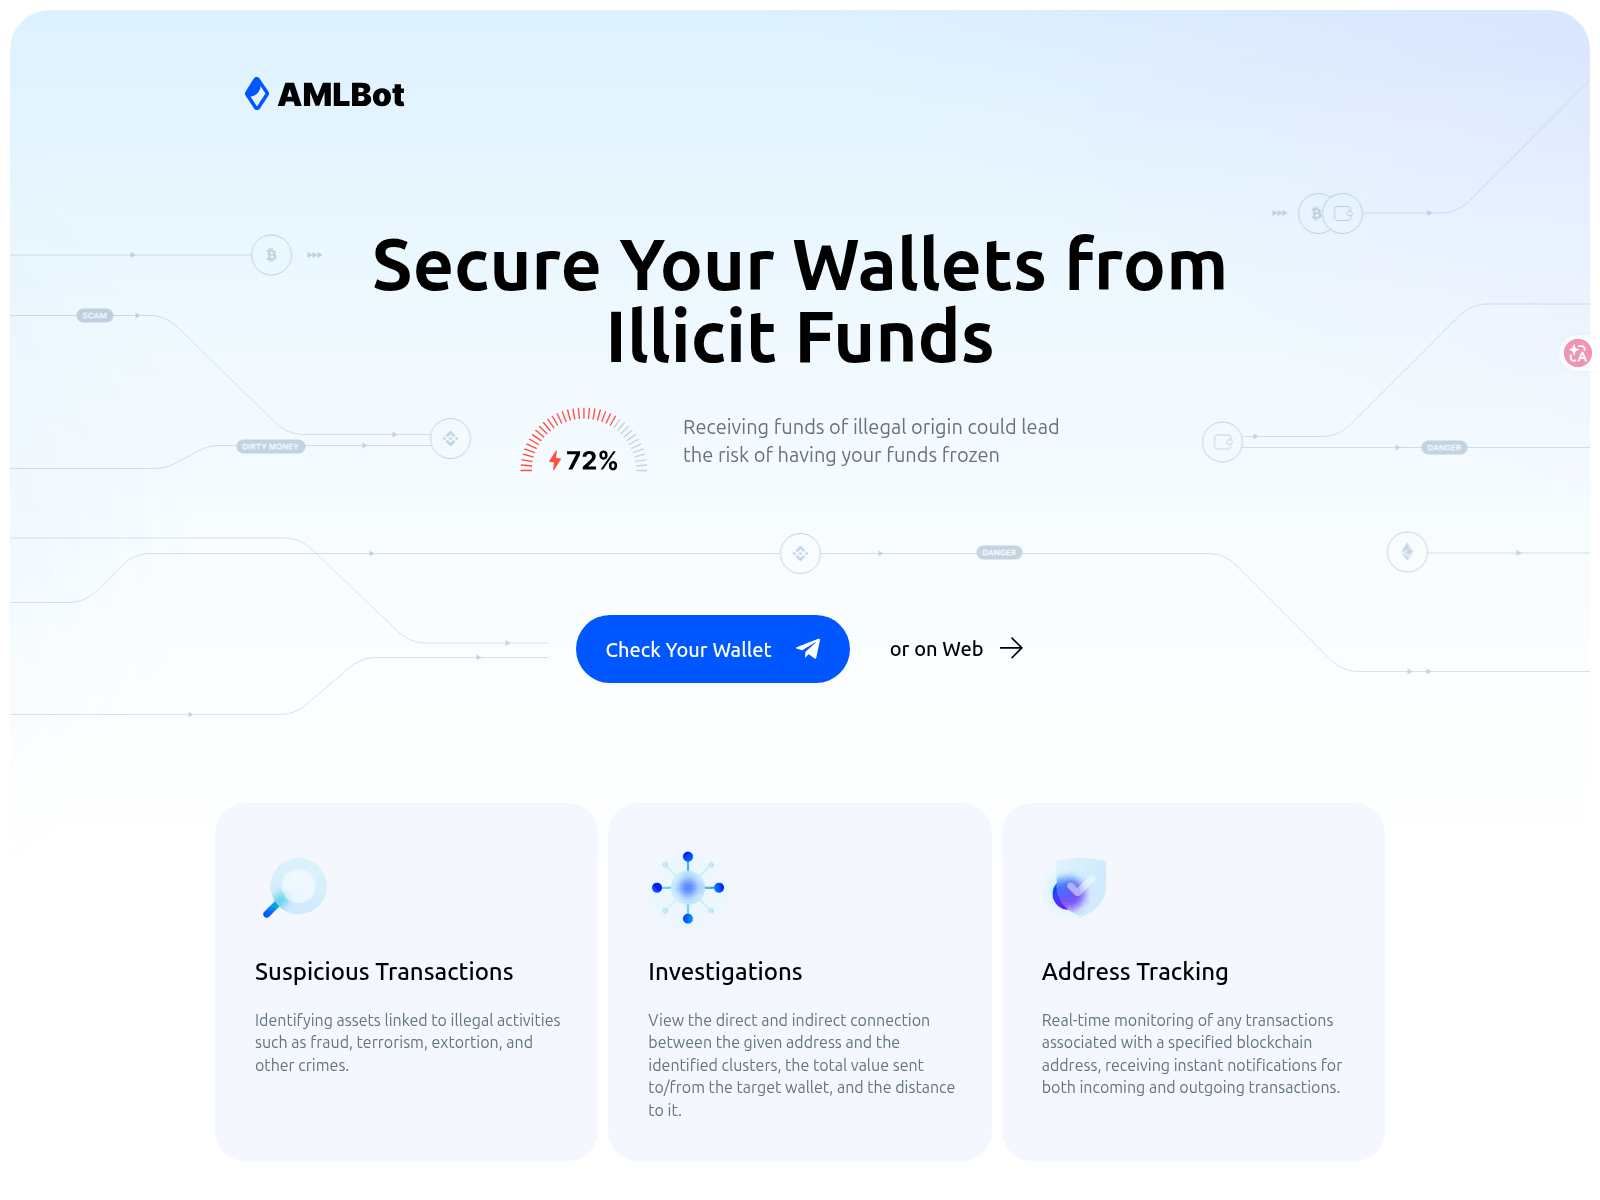
search-aml.net
securebithelp.com

testtrust.app
tether-confirmation.com

tracker-aml.com

trc-amlcheck.com

trnaml.com
trust-monitor.org
trustaml.app
usdt-amlscan.com
usdt-secure.net
usdtmixer.top

verify-streamline-1162.vercel.app

vnundefinedapi.info
vote-id-kjamltwr.portallogonapp.best

walletaml.org

walletcheckeraml.xyz

walletpolitics.info
whitewalletlist.top

yoursaml.com

acrosstobrldge.org

aml-bots.world

aml-chain-guard.icu

aml-check.cfd

aml-check.click

aml-check.inzc4jw.top

aml-checkingusdt.com

aml-checks.com

aml-click.com
aml-coinanalysis.com

aml-cryptobot.cfd

aml-finance.net

aml-free.com
aml-funds.net

aml-one.org
aml-probot.org

aml-report.click
aml-riskscore.com

aml-safety.one
aml-scan.app

aml-security.cfd

aml-solutions.icu
धमकी प्रतिक्रिया पाइपलाइन
इस हब में प्रत्येक डोमेन की कैसे पुष्टि की जाती है और पुष्ट खतरों को कैसे निष्प्रभावी किया जाता है। पूर्ण पाइपलाइन दृश्यीकरण →
खतरे की खुफिया जांचें— प्रत्येक डोमेन को स्कैन किया जाता है और निम्नलिखित के खिलाफ क्रॉस-चेक किया जाता है:
urlscan.ioस्क्रीनशॉट · DOM · HTTPVirusTotal90+ AV enginesगूगल सुरक्षित ब्राउज़िंगTransparency रिपोर्टक्लाउडफ्लेयर रडारडीएनएस · certs · categoriesएलियनवॉल्ट ओटीएक्सThreat-intel pulsesवेबैक मशीनHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate Transparencyडीएनएस सुरक्षा Filtersक्वाड9 · AdGuard · क्लीनब्राउज़िंगWeb-जाँचेंFull surface scan
 crt.sh
वैश्विक विक्रेता सिंक— पुष्टि किए गए डिटेक्शन 29 पार्टनर्स को भेजे जाते हैं:
GoogleSafe BrowsingGoogleWeb Risk एपीआईMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe Browsingयूआरएलस्कैन डॉट आईओPublic scanईएसईटीWebGuardबिटडेफ़ेंडरThreat exchangeNortonSafe WebSymantecसाइट समीक्षाअवीराCloud detectionAvast / AVGWeb Shieldकास्परस्कीOpenTIPडॉ.वेबOnline scannerनेटक्राफ्टहटाना एपीआईफ़िशटैंकVerified voteAPWG eCXBulk feedफ़िशस्टैट्सOpen feedPhish.रिपोर्टHosting abuseSpamhausDBL feedपॉलीस्वार्मMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust