
ट्रैक किए गए डोमेन खोजें और संग्रहीत साक्ष्य, डिटेक्शन और नवीनतम देखी गई उपलब्धता की समीक्षा करें।
220,228
कुल ट्रैक किए गए
214,496
वीटी का पता चला
92,006
अंतिम बार सक्रिय देखा गया
128,222
अंतिम जाँच पर अनुपलब्ध
0
वीटी लंबित
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake डोमेन
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains
treehouse-finance.org

u106.mining1212.xyz
usdt-secure.net

vote-punksauction.votings.workers.dev

vote-walletconnect.xyz
walletconnectpro.testdev.sbs
walletconnectsupport.com
weth.sheesha-portal.com

woofi.defox.click
xotanex.com
xzzx.allexame.com

yaesprimaveraelcorte.com

aave-dashboard.pages.dev
aavids.top
airdrop-bitlayer.xyz

airdrop.crypto-chance.com
allo.quest

amlbotcontrol.com
apexairdrop.com

app-hypenliguiid.zip
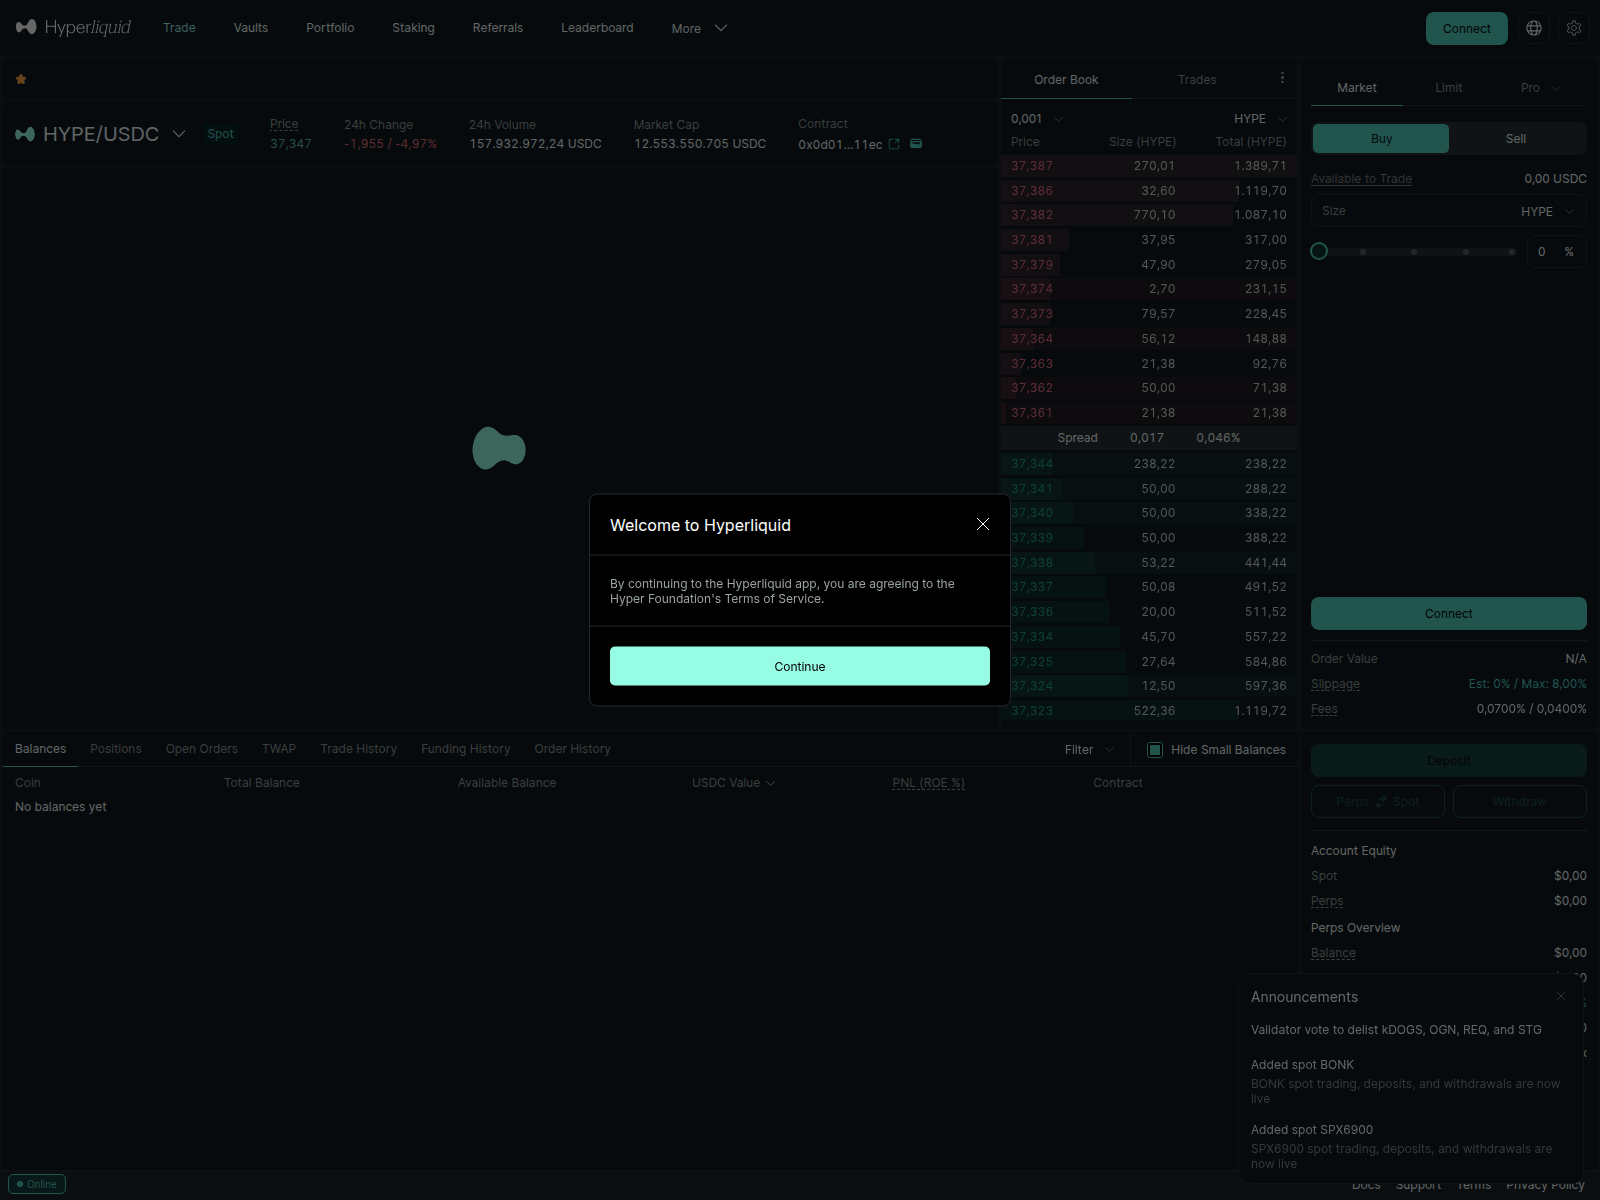
app-hypenliguiidi.vip
app-unionbuild.top
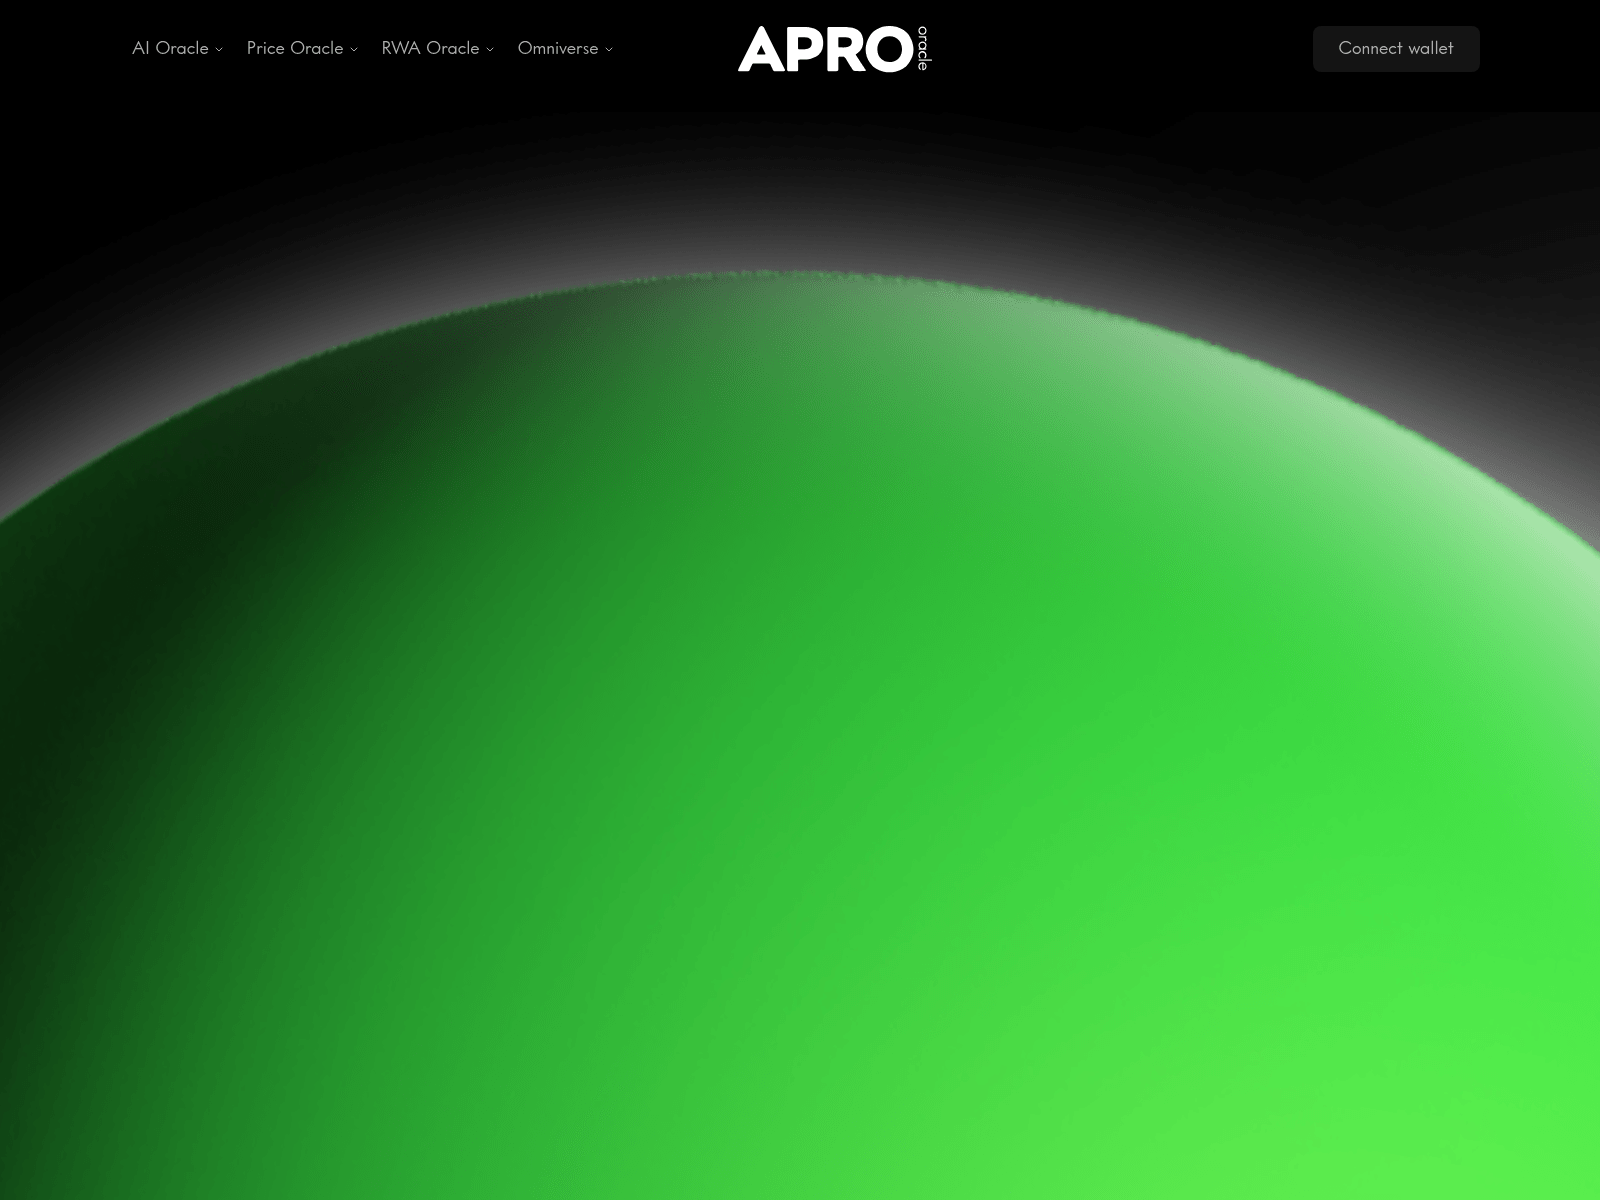
apro-livechecker.xyz

asterdexdrop.app
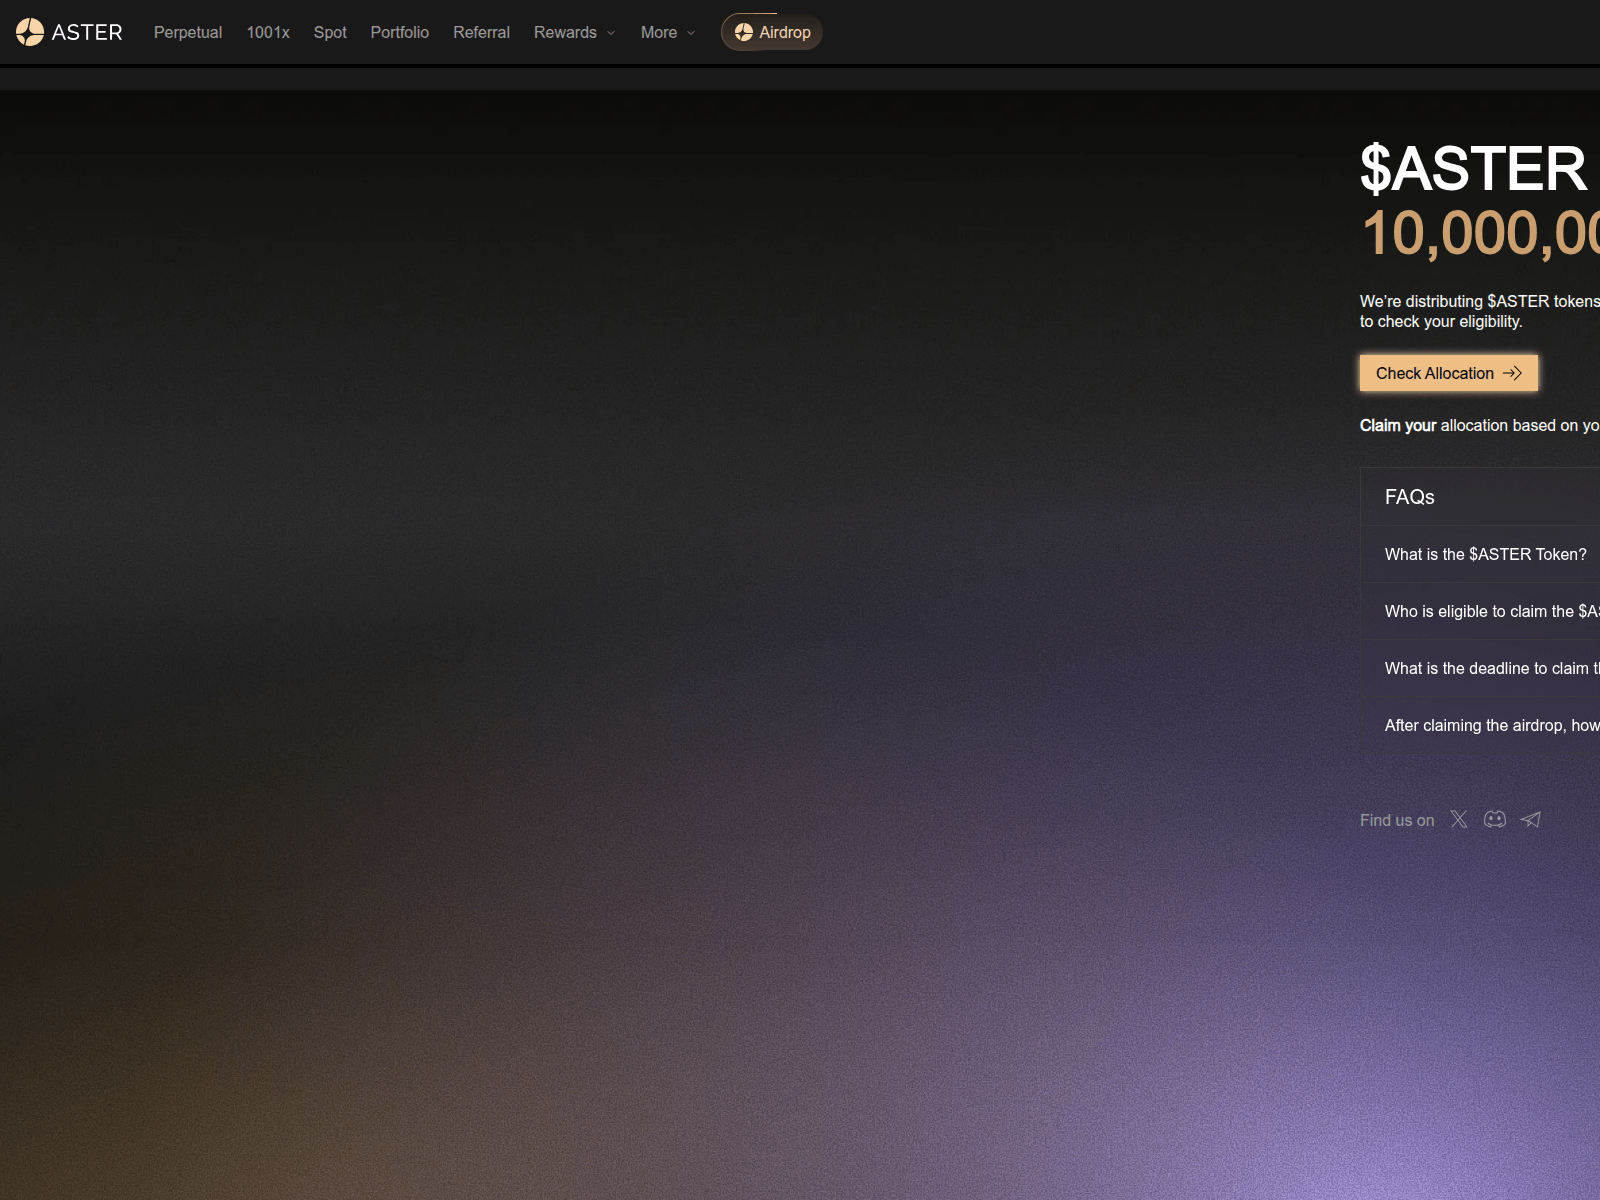
asterdexv2.com
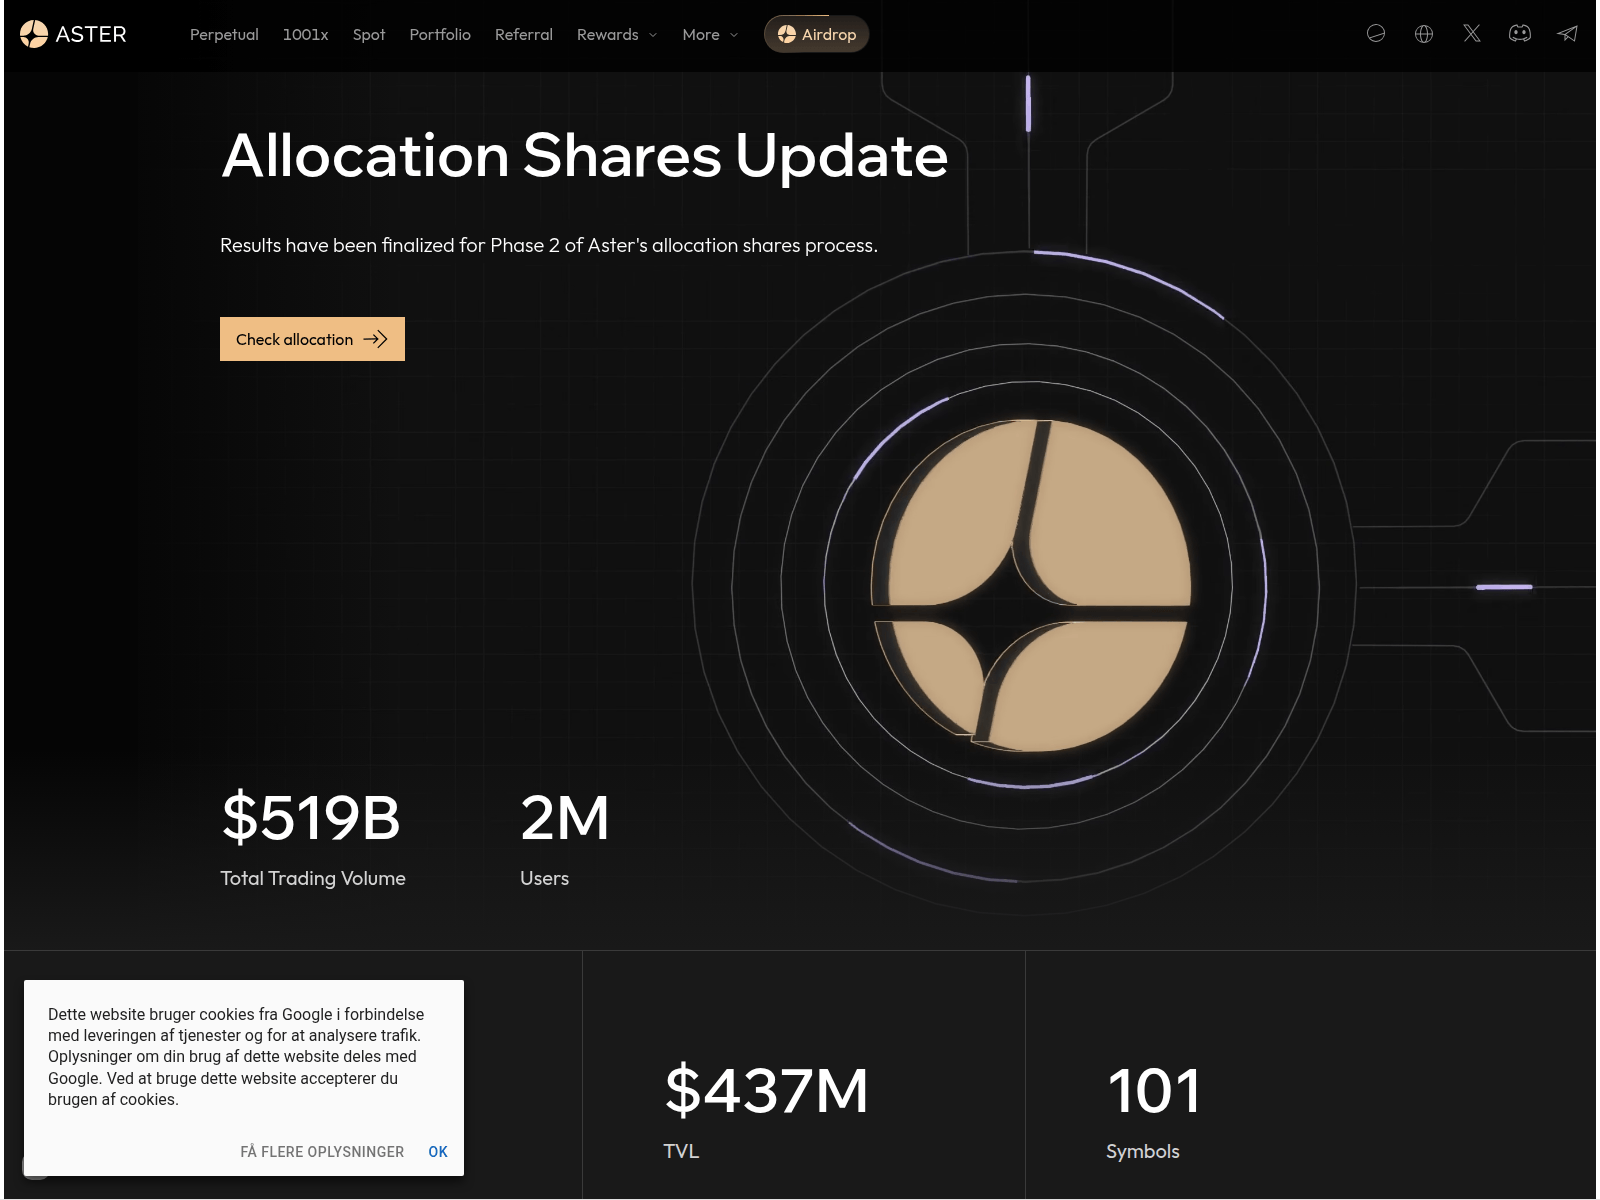
asters-checker.com

auth-sammm.quboid.app
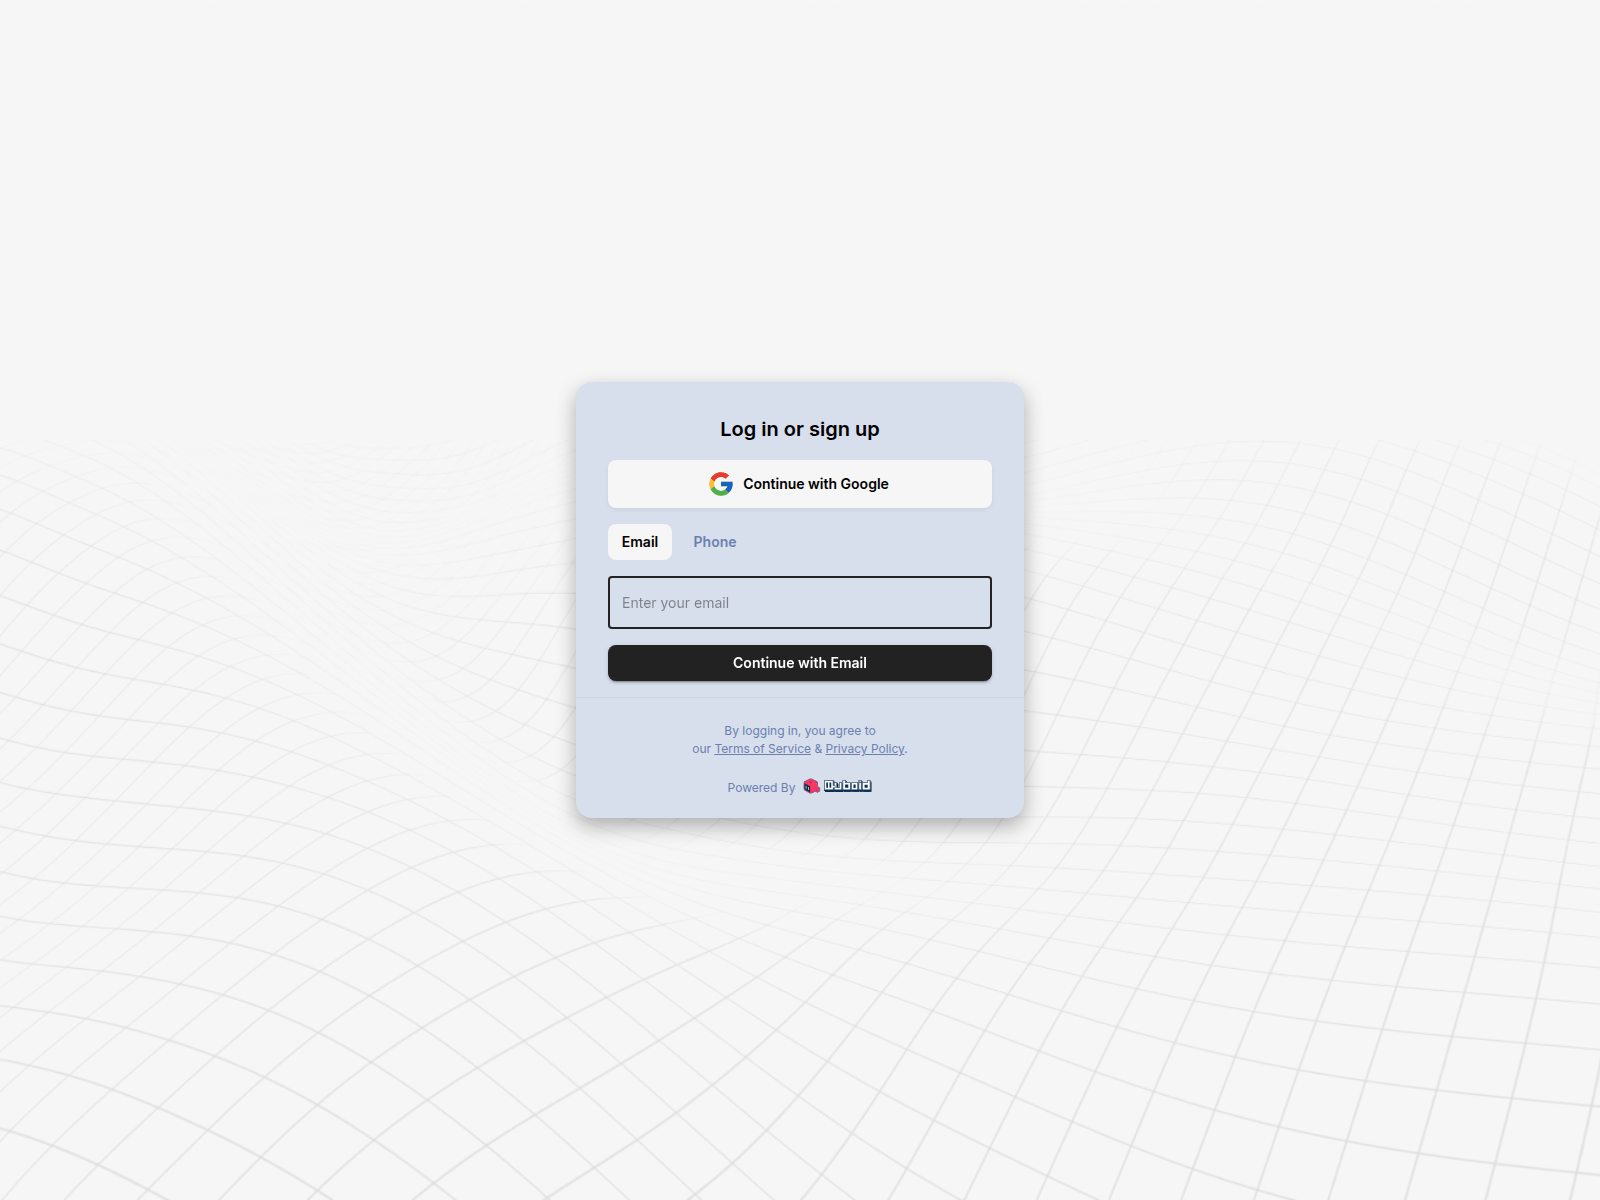
auth-tata-trent.quboid.app
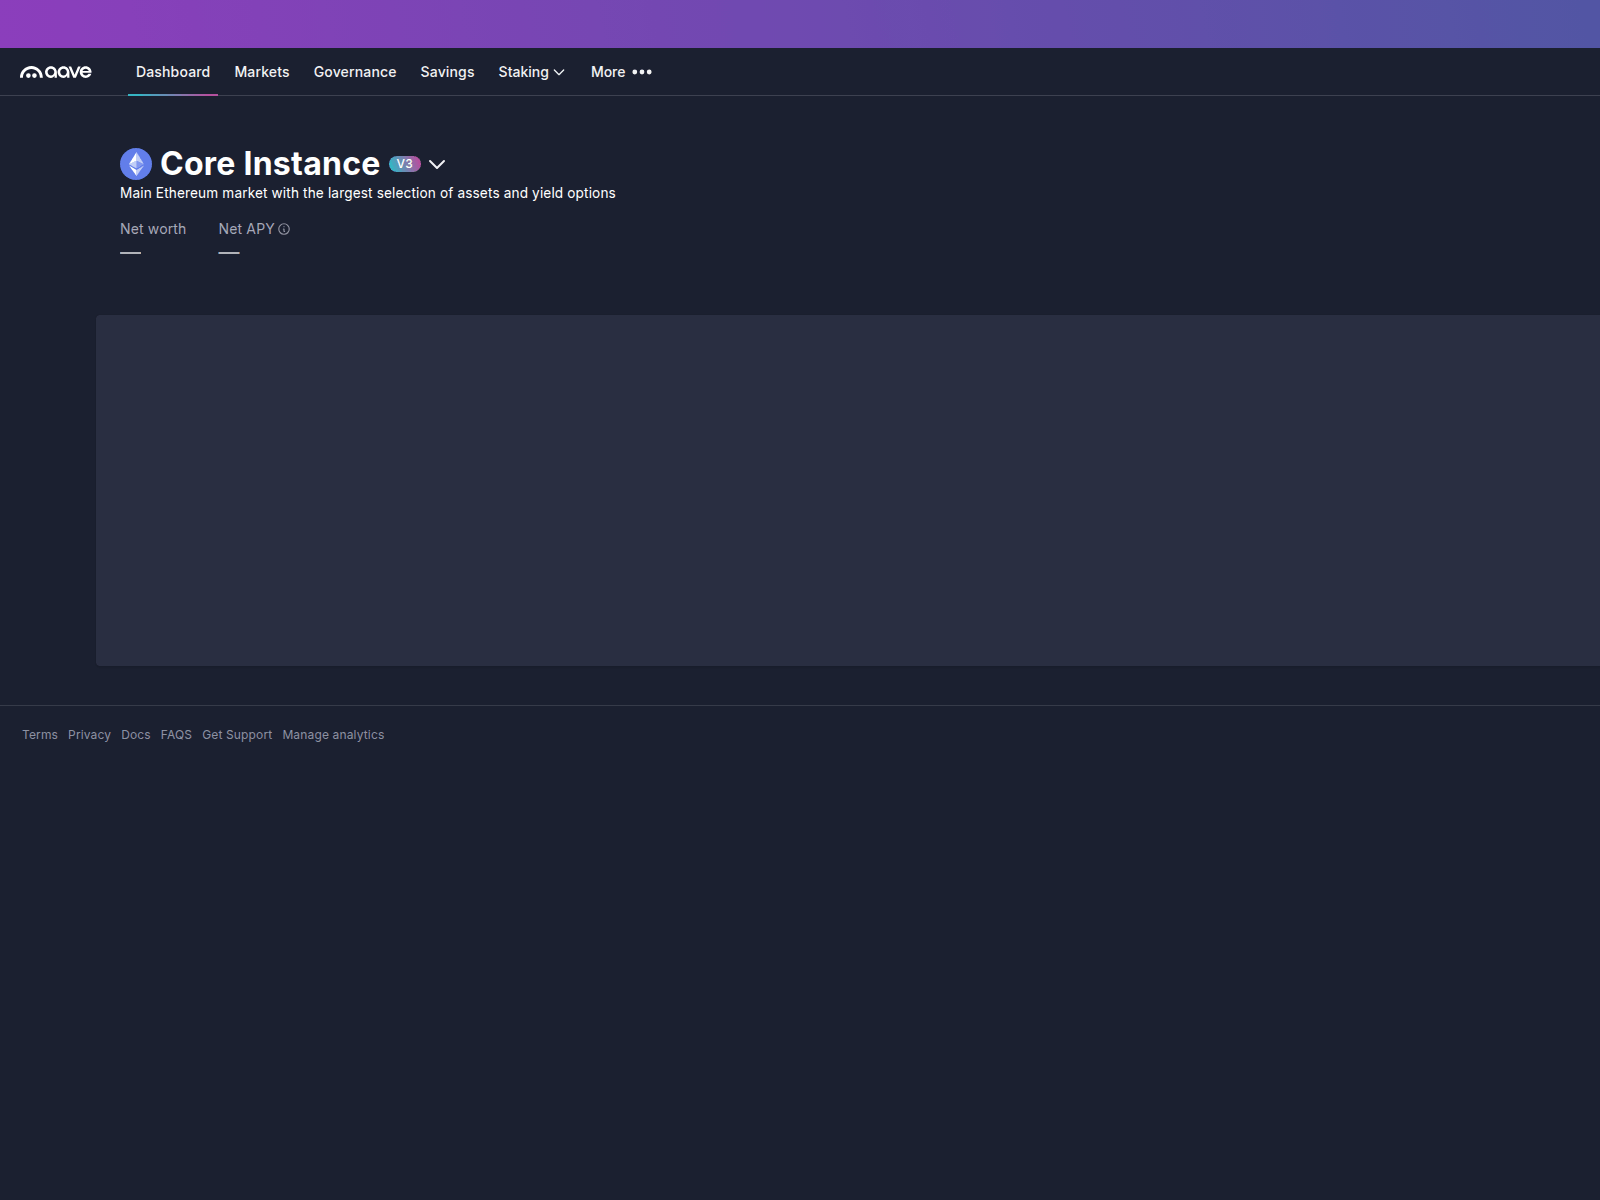
avprt.top

bancustoken.finance

block-scan.pro

blockdag-network-en.web.app

blockdagwork.net
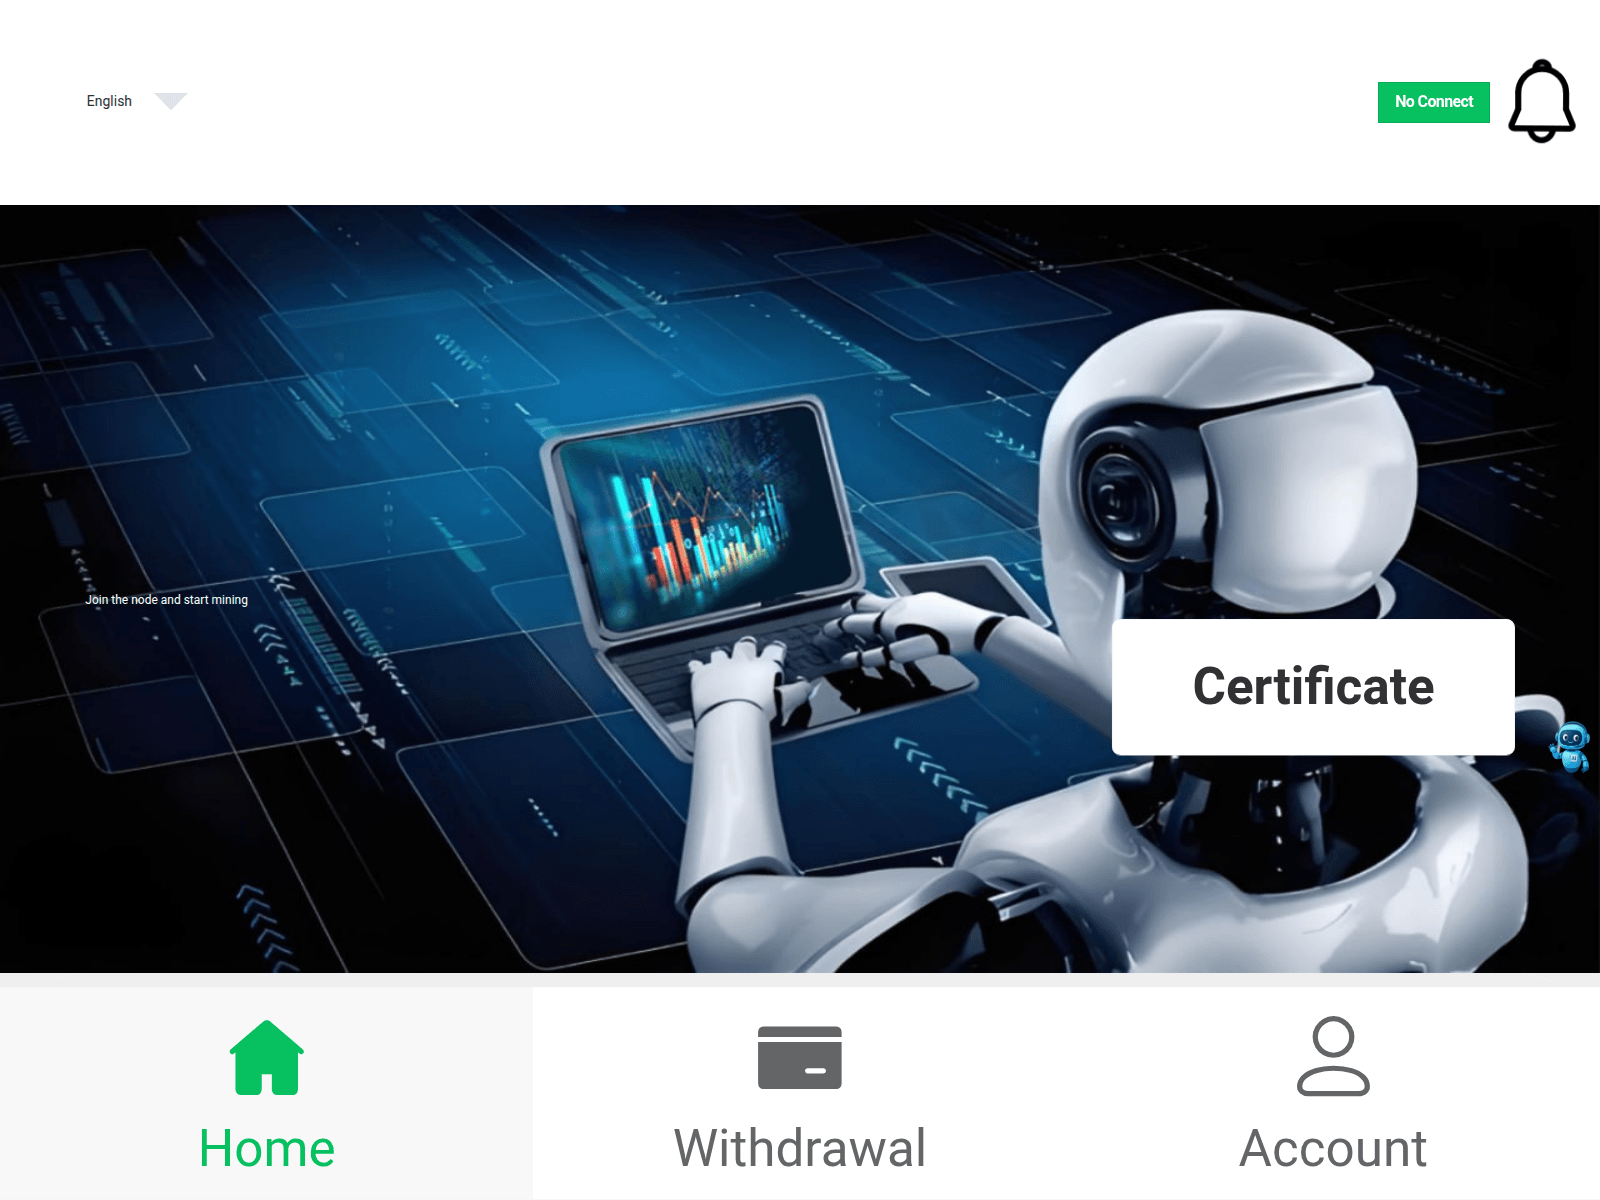
bnb-25.cc
bnb-5.cc

bnweb3.cc

bob-sepolia-o9rpnaj4u-distributed-crafts.vercel.app
brevis-snapshot.xyz

chiliz-omega.vercel.app

claim-apr.site

claim-rkgen.com
claims-blum.xyz
claims-grass.app

claimusd.com
commonchecker.xyz
connecttocopy.com

def66.net
eligible-asterdex.com

enter-cysic.xyz

ethereum-burner.xyz
etherfichecker.xyz

ethgas.cc
evaaprotocol-live.xyz
fdqufp.cc
findyourtoken.app

flare-portal-claim.com

fushenprotocol.xyz
get-yieldusd.net
gliqiud.xyz
gstlimitless.com
hananetwork-live.xyz
honeycomb.0xhoneyjar.xyz

hoursglass-deposits.com

i815.aimine.cc

ibvm.eligibility.ink
jrcorp.me

kniteic.xyz

kqmyi.qd88.pro

liquild.xyz
magicmoni.xyz

mantra-dex.pro
megaeth-live.xyz
mogcoin.cc

nandicoin.com
pan-bridge-v3.app

peperider.com

pepsi-collections.com

pepusunchained-portal.votings.workers.dev
plasmas.lat
portal-campnetwork.firebaseapp.com

powers-protocol.org
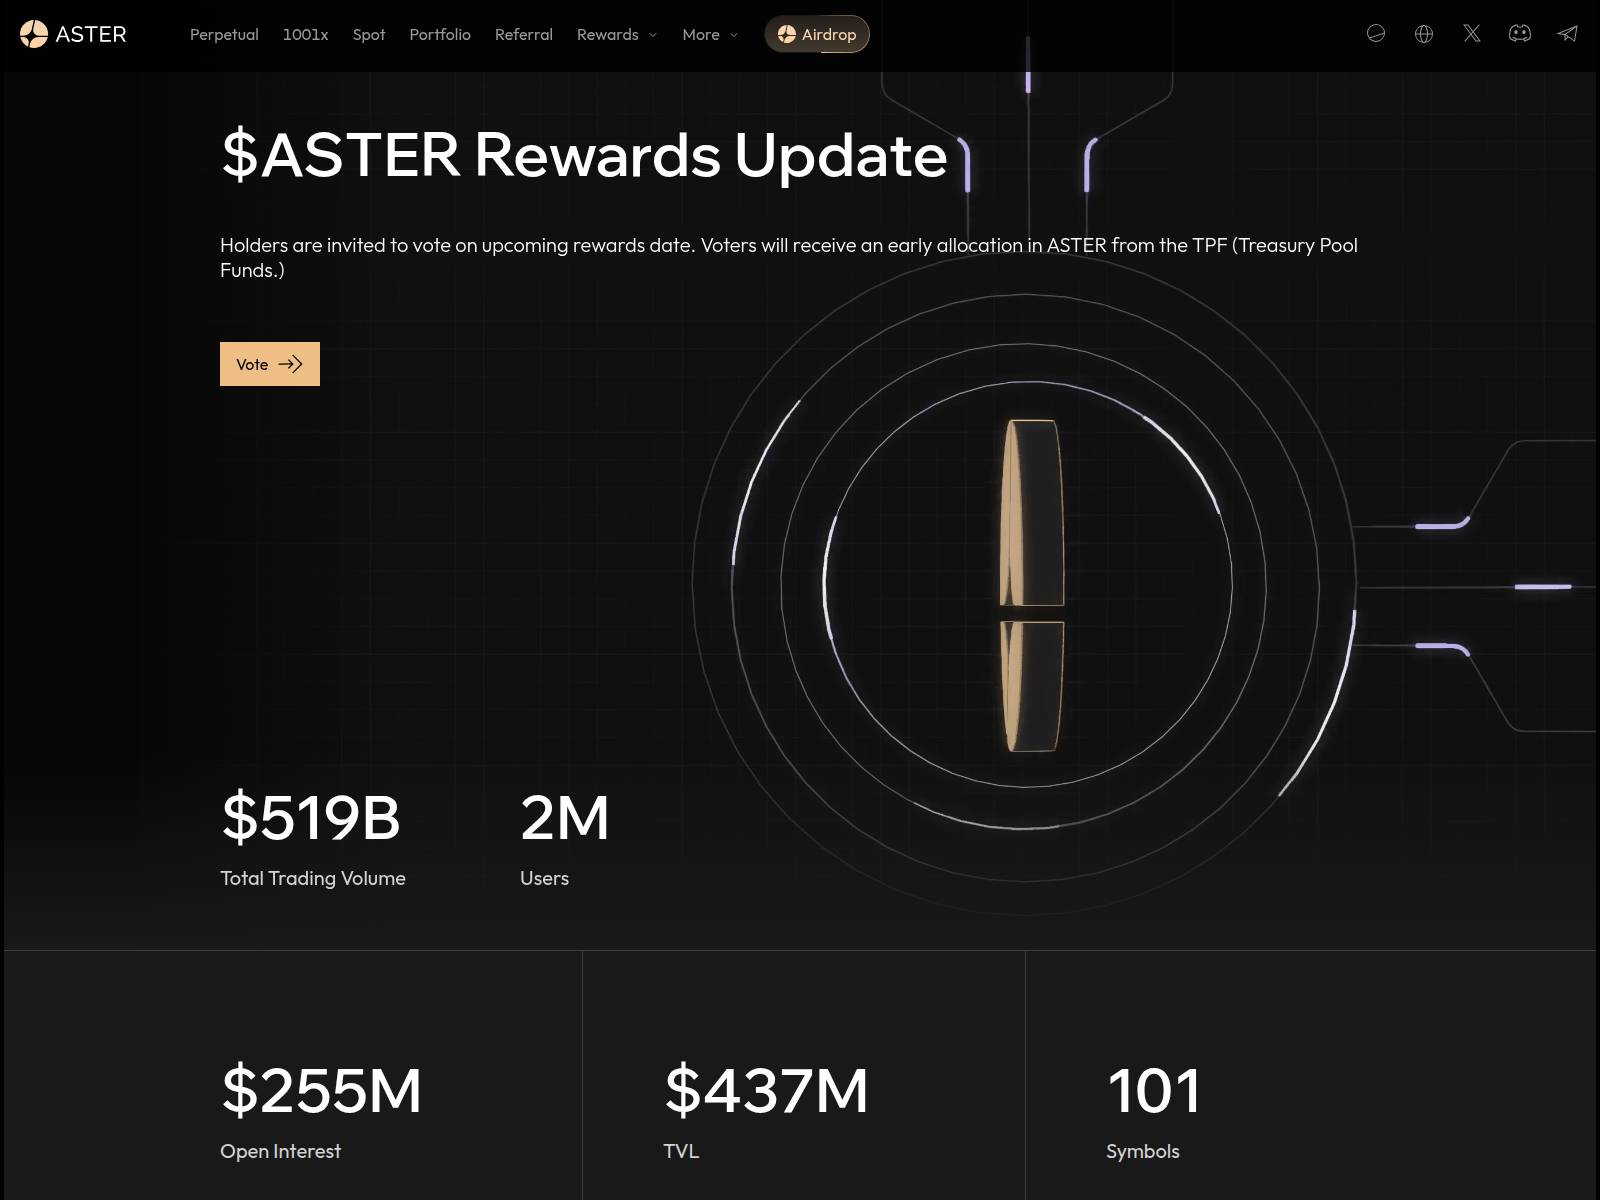
proposals-aster.com
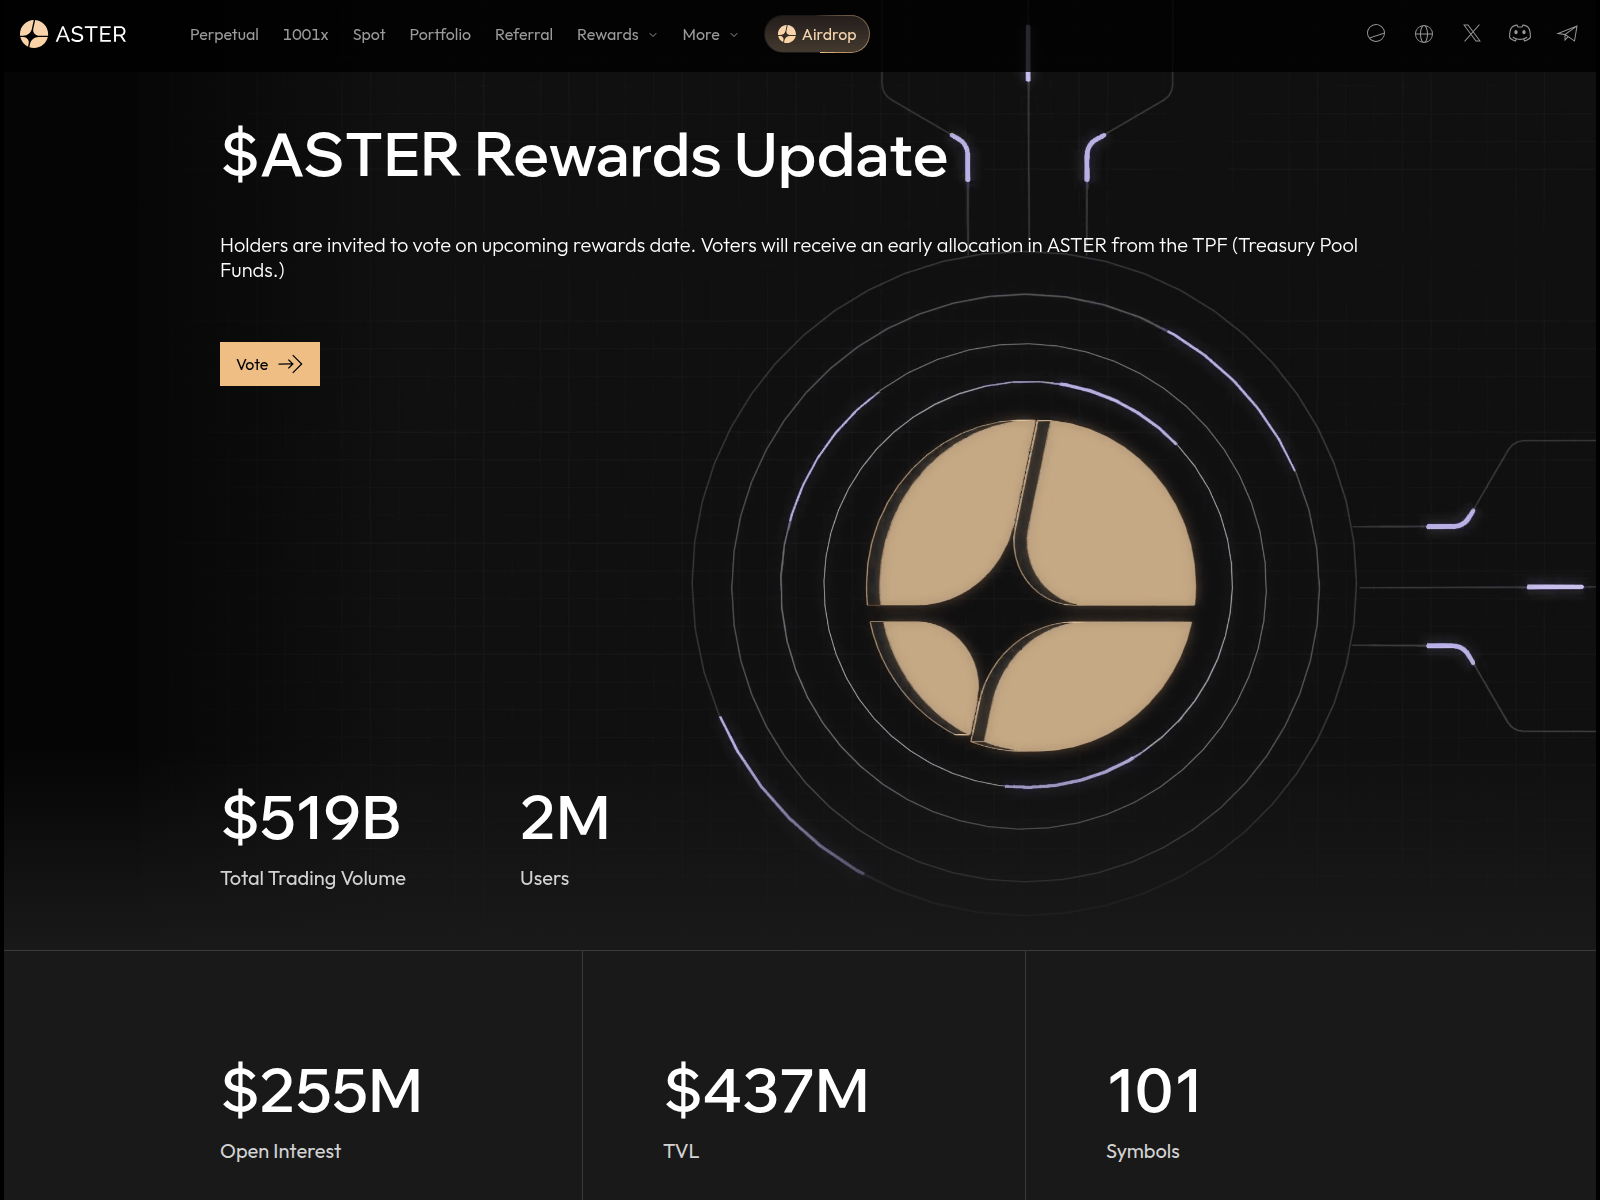
proposals-asters.com
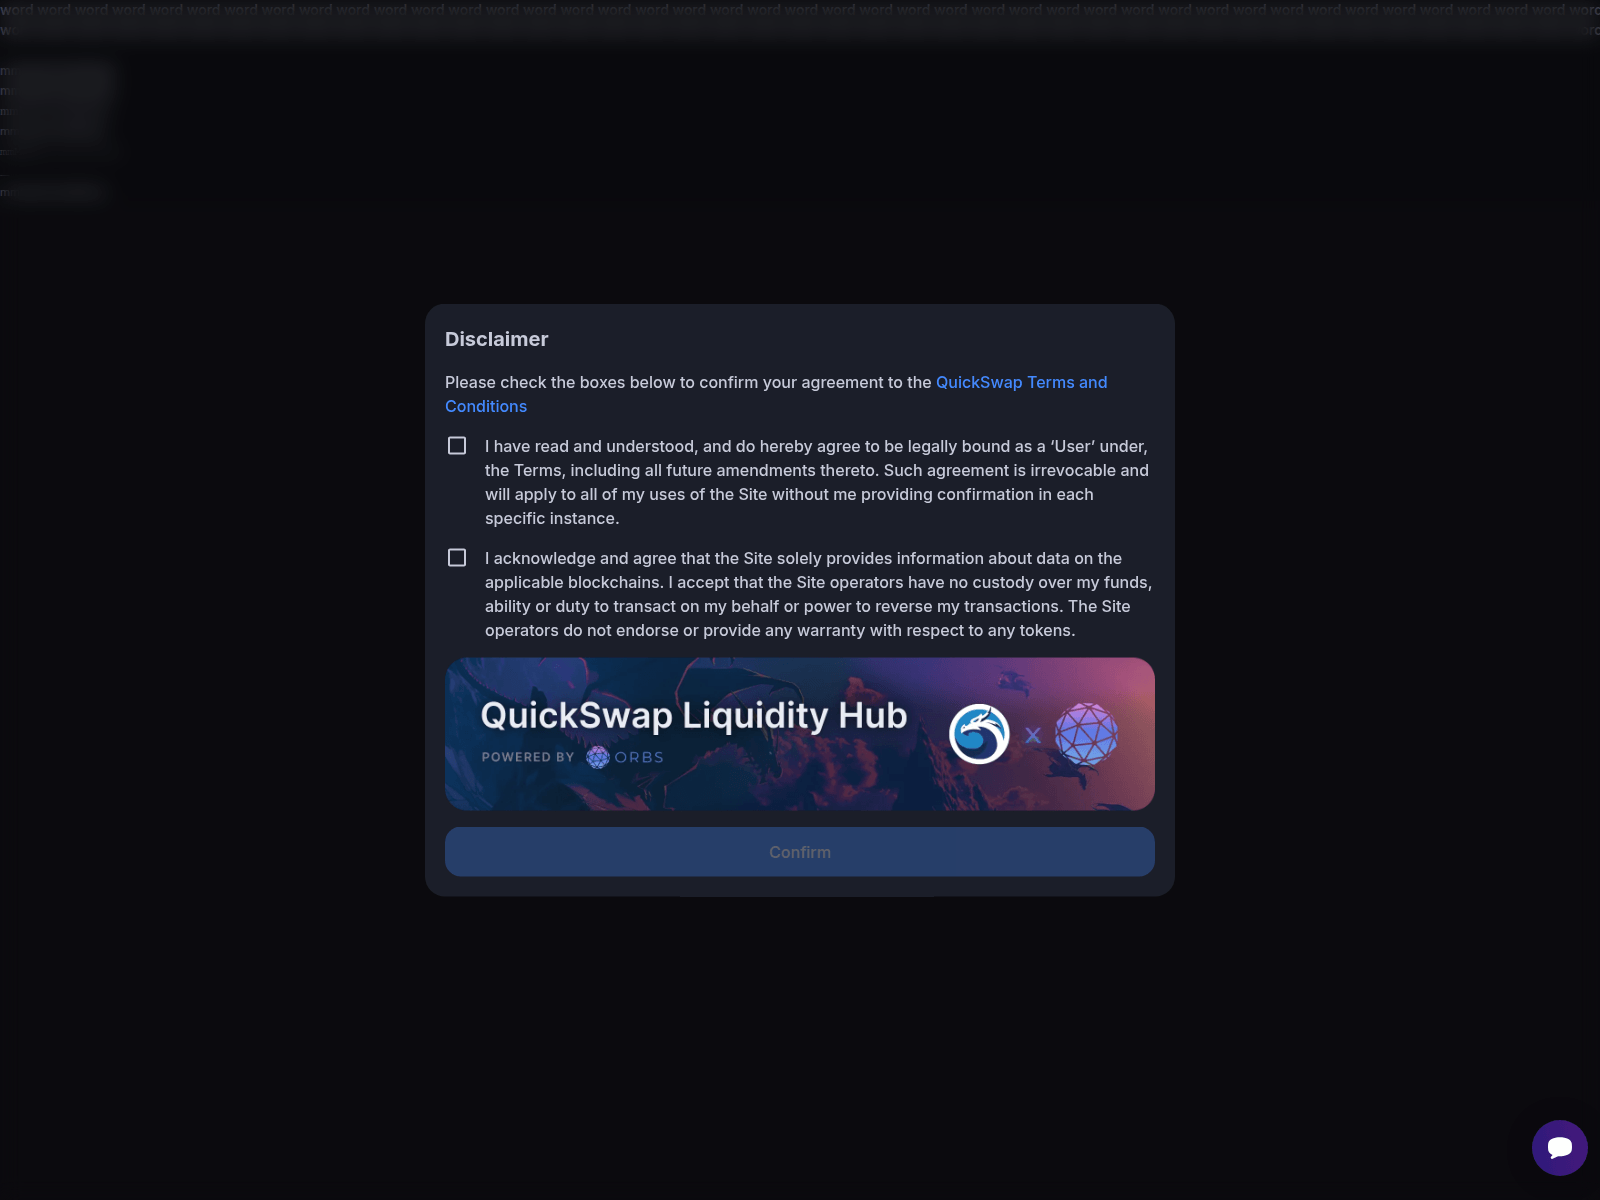
quickswap-exchange-dapp-referral.com
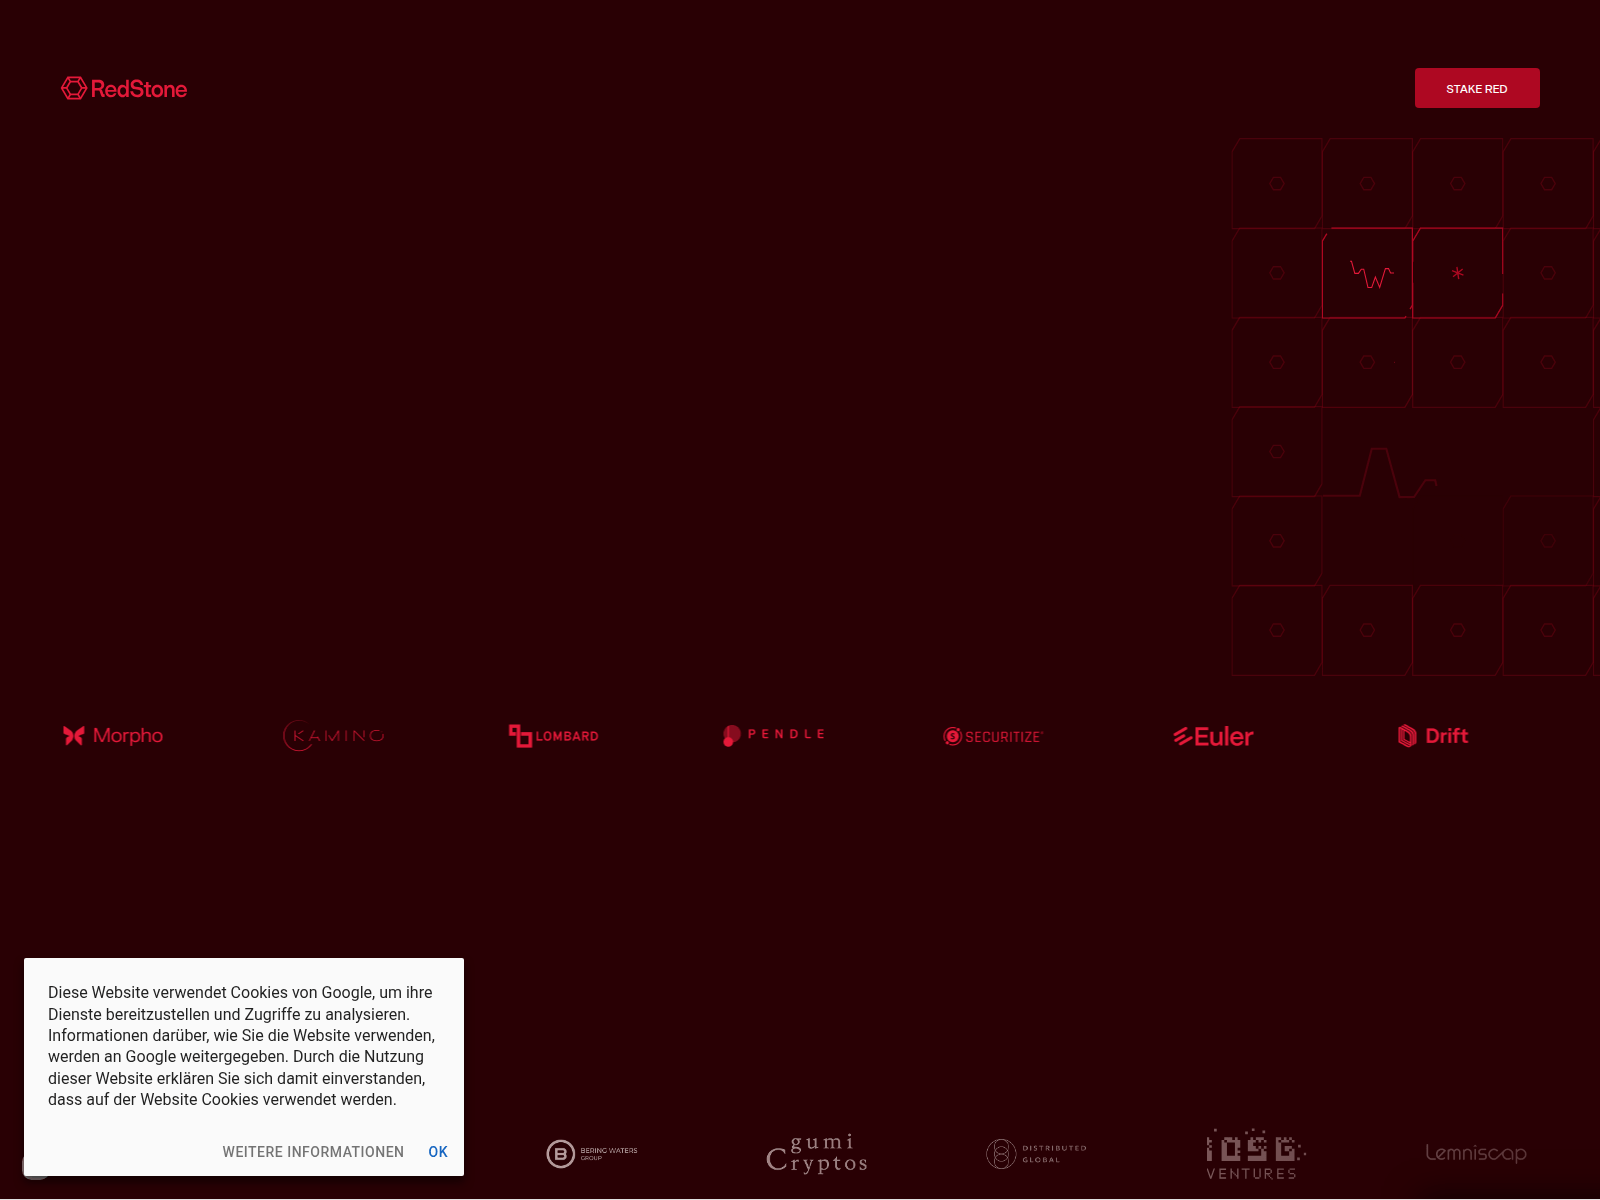
redstones-voting.com
register-cysicfundation.org

register.cysicfoundation.org
registers-cysicfoundation.org

revoke-balancers.com

scanether-l.ink
snapx-live.xyz

stkstone.com
sucda.cc
swiftwalletprotocol.web.app

tetherdefai.app
tge-klinkfinances.com
tge-pieverses.com

ticketsupport-apps.com

truemoney.finance
धमकी प्रतिक्रिया पाइपलाइन
इस हब में प्रत्येक डोमेन की कैसे पुष्टि की जाती है और पुष्ट खतरों को कैसे निष्प्रभावी किया जाता है। पूर्ण पाइपलाइन दृश्यीकरण →
खतरे की खुफिया जांचें— प्रत्येक डोमेन को स्कैन किया जाता है और निम्नलिखित के खिलाफ क्रॉस-चेक किया जाता है:
urlscan.ioस्क्रीनशॉट · DOM · HTTPVirusTotal90+ AV enginesगूगल सुरक्षित ब्राउज़िंगTransparency रिपोर्टक्लाउडफ्लेयर रडारडीएनएस · certs · categoriesएलियनवॉल्ट ओटीएक्सThreat-intel pulsesवेबैक मशीनHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate Transparencyडीएनएस सुरक्षा Filtersक्वाड9 · AdGuard · क्लीनब्राउज़िंगWeb-जाँचेंFull surface scan
 crt.sh
वैश्विक विक्रेता सिंक— पुष्टि किए गए डिटेक्शन 29 पार्टनर्स को भेजे जाते हैं:
GoogleSafe BrowsingGoogleWeb Risk एपीआईMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe Browsingयूआरएलस्कैन डॉट आईओPublic scanईएसईटीWebGuardबिटडेफ़ेंडरThreat exchangeNortonSafe WebSymantecसाइट समीक्षाअवीराCloud detectionAvast / AVGWeb Shieldकास्परस्कीOpenTIPडॉ.वेबOnline scannerनेटक्राफ्टहटाना एपीआईफ़िशटैंकVerified voteAPWG eCXBulk feedफ़िशस्टैट्सOpen feedPhish.रिपोर्टHosting abuseSpamhausDBL feedपॉलीस्वार्मMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust