Aller au rapport de sécurité
Sécurité des domaines et renseignements sur les menaces
xrpairdrop.net favicon

xrpairdrop.net

“XRP Community Reward”

Verdict de menace
Assessment sources

Assessment based on the stored source evidence below. Review sources →

Disponibilité Non vérifié L'accessibilité actuelle n'est pas vérifiée Observé · HTTP probe
Détections VirusTotal : 9/92 Type d'arnaque : Airdrop Scam Domaine jeune : âgé de moins d'un jour
15/10/2026 CDN
API
Bureau d’enregistrement
NiceNIC
Resolved IP
188.114.96.3
Registered
14/10/2026
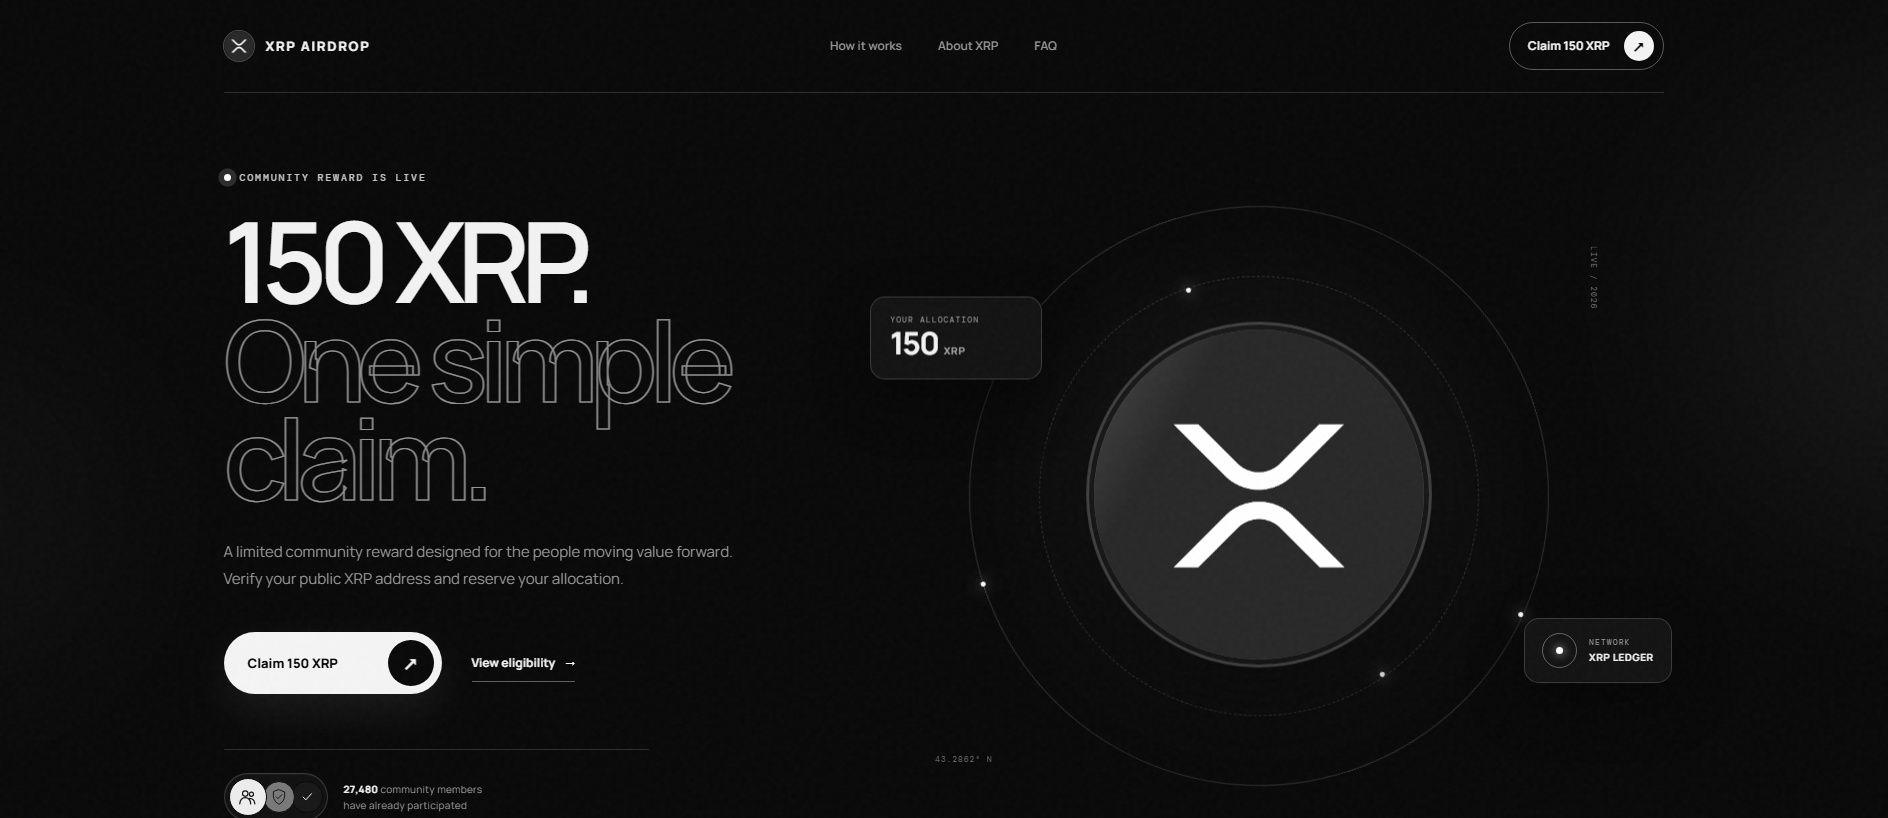
Capture enregistrée 1 / 2 View full size
Primary capture Wayback
Ce domaine a été signalé comme malveillant
Moteurs de sécurité signalant une détection : 9. Faites preuve d’une extrême prudence – ne saisissez pas d’informations d’identification ou d’informations personnelles.
Résumé du rapport

xrpairdrop.net — Non vérifié. Type d'arnaque : Airdrop Scam. Résumé des preuves: VirusTotal 9/92 (alphaMountain.ai, BitDefender, Fortinet, G-Data, Kaspersky); URLScan capture; CF Radar malicious; PhishDestroy score 77/100. Bureau d’enregistrement: NiceNIC.

L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.

Additional indicators at a glance
VirusTotal
VirusTotal
9 det.
CF Radar
Malveillant
URLScan
URLScan
Certificat TLS
Expiré ou non vérifié
Âge
<1 day Brand New!
PhishDestroy
DestroyList
Répertorié

Source evidence

5 sources

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.

VirusTotal

9 / 92

Signaler
Interpretation & limits

Engine detections from this stored analysis. Vendors and collection times may differ from other sources.

CF Radar

provider verdict: malicious

Observation time not recorded
Signaler
Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

OTX

no community references

Signaler
Interpretation & limits

Community publication references, not a vendor verdict or evidence of a common operator.

URLScan capture

rapport stocké

Stored URLScan capture preview
Signaler
Interpretation & limits

A preserved page image documents what the collector received; a capture is not a safety verdict.

Google Safe Browsing

Checked; no threat flag recorded

Signaler
Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

Renseignements sur la sécurité réseau Registrar context
CF Cloudflare Radar Verdict Malveillant
DGA Domains Security threats Dga domains
Registrar context NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC Verdict Full Investigation

Résumé des preuves

Critique
VirusTotal
9/92
URLScan
Stored capture

Stored narrative · generated . Provider checks below retain their own observation dates.

Assessment

On 2026-10-15, xrpairdrop.net was observed as an internal listing on PhishDestroy, according to a recorded source observation. The domain also appears in a PhishDestroy internal listing, which is a publisher-owned catalogue entry.

Recorded Evidence

VirusTotal recorded 9 detections out of 92 scanners for xrpairdrop.net on 2026-09-15. The domain was registered with NICENIC INTERNATIONAL GROUP CO., LIMITED on 2026-10-14. A PageSpeed check on 2026-10-15 documented a performance score of 79. The PhishDestroy internal listing includes this domain as of 2026-10-15.

Interpretation

The VirusTotal record contains a measurement of how many security scanners detected xrpairdrop.net, providing insight into how it was classified by multiple vendors at the time of the scan. The PhishDestroy internal listing documents the domain’s presence in a publisher-owned catalogue, which is distinct from external blocklists. The PageSpeed score is a technical indicator and does not reflect security status.

Recommended Actions

To support further review of xrpairdrop.net, retain the VirusTotal detection record and the PhishDestroy internal listing for future reference. Preserve the PageSpeed performance score as a technical benchmark for the domain. Use these source records for any subsequent comparisons or assessments.

Analyse de la détection et de l'évasion

Vérification du cloaking et de la répartition du trafic

Pas encore numérisé Aucune différence entre les robots d'indexation et les navigateurs n'a encore été constatée

Enregistrement des observations « crawler contre navigateur » pour cet hôte, ainsi qu'une vérification en temps réel des empreintes numériques pour les systèmes de répartition du trafic de type Keitaro.

Indicateur de camouflage enregistré
Pas encore numérisé
Routage de la capture
Local archivé le 2026-10-15 05:45:34 UTC
Vérification en direct des empreintes digitales d'TDS
Sept empreintes Keitaro ainsi qu’une comparaison entre robot d’indexation et navigateur, générées par le scanner PhishDestroy lorsque ce panneau est ouvert.
En attente

Capture enregistrée · 2 captures

Domain details

Domaine
IP Context Cloudflare shared edge origin IP hidden La réputation Edge-IP n’est pas attribuée à ce domaine.
Bureau d’enregistrement NiceNIC RU(RU) PhishDestroy Investigation
Contact anti-abusabuse@nicenic.net
Registre de l'ICANNICANN Lookup (RDAP) →
EnregistrementCréé 14/10/2026 (0d · Brand New!) — Expires 14/10/2027
Détails techniquesProvenance & timestamps
Première détection15/10/2026
Submitted URLhttps://xrpairdrop.net/
Titre de la page
XRP Community Reward
Certificat TLS
Hostname coverage not recorded · Émis par Let's Encrypt / YE1 · stored validity ends in 89 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.96.3

La réputation Edge-IP n’est pas attribuée à ce domaine.

Serveurs de noms 2

  • amos.ns.cloudflare.com
  • dayana.ns.cloudflare.com

Location describes the IP network.

Certificat TLS

Issuer
Let's Encrypt / YE1
Valid from
2026-10-14 15:31:34
Valid until
2027-01-12 15:31:33
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-15 04:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprint781a90349e3e353b0950d682c7dcc24deb3c431ad1ae6023179034bd9cffad5f

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 188.114.96.3rapiddns.io
Technologies · 6 identified
Detected via Cloudflare Radar · Wappalyzer engine
Signaler ce domaine Envoyez des éléments de preuve et contribuez à protéger les autres

Analyse VirusTotal

9 / Les fournisseurs de sécurité 92 ont signalé ce domaine
View on VT
Last analyzed
alphaMountain.ai
BitDefender
Fortinet
G-Data
Kaspersky
Lionic
Sophos
VIPRE
Webroot
Analyse des performances du site

Google PageSpeed Insights — mobile performance audit of xrpairdrop.net · checked Oct 15, 2026

79
Needs Work
Performance
FCP
2.59s
First Contentful Paint
LCP
2.59s
Largest Contentful Paint
CLS
0.007
Cumulative Layout Shift
TBT
526ms
Total Blocking Time
SI
3.6s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: https://xrpairdrop.net/
XRP Community Reward
A modern XRP community reward landing page.
Réponse
HTTP 200
HTML body
10.0 KB
Compressed
3.0 KB
Links
0 internal · 0 external
Detected technologies
cloudflare
Selected response headers
Content-Type: text/html; charset=utf-8
Server: cloudflare
CF-Cache-Status: DYNAMIC
Content-Encoding: gzip
HSTS: not observed DNSSEC: not observed WAF / firewall: observed Cloaking flag: not observed
Saved response-header values · 13
alt-svc
h3=":443"; ma=86400
cf-cache-status
DYNAMIC
CF-RAY
a4abd4e2bcb7972b-FRA
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
Date
Thu, 15 Oct 2026 03:45:32 GMT
Last-Modified
Sun, 04 Oct 2026 13:31:03 GMT
Nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
Report-To
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=JmiWMqvTndx2a0F66aYaLrhuTStnFbIxNG5cYDKgl17G%2BZU%2FnvIBBqS3X822vntJxhGxT8kJnCv18KBVNX5L9YMv6tZKoYo00prESeI6vrmb4lSoNcnTMn428ur%2FbJSJUQ%3D%3D"
Server
cloudflare
Transfer-Encoding
chunked
Vary
accept-encoding

Values retained by the collector; long values may be shortened during collection.

Crawler & disclosure files

Site configuration evidence

1 recorded files

Files, paths and sitemap entries retained by the collector.

robots.txt

Reachable (legacy)
/robots.txt
HTTP response
200
Observed at
2026-10-15 05:45:34 UTC
Source
legacy scan archive

A legacy scan recorded a successful response. The file contents were not retained.

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-15 03:44:03 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain ingestion complete. Initial state is marked as alive pointing to IP 188.114.96.3.

Processus de réponse aux menaces Pipeline

Découverte
Analysis
Monitoring

9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Menace détectée
xrpairdrop.net détectés et mis en file d'attente en vue d'une analyse complète
15/10/2026
URLScan.io Capture
Enregistré URLScan report with capture artifacts
15/10/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
9/92 recorded on VirusTotal
15/10/2026
Registrar Context: NiceNIC
Separate registrar research is available. Registrar association is contextual and is not scored as an independent detection.
CF Radar: Malicious
Cloudflare Radar classified this domain as DGA Domains, Security threats, dga domains
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
15/10/2026
Technical Analysis Recorded
Le rapport contient des résultats de technologie ou d’analyse médico-légale stockés.
15/10/2026
DestroyList publié
15/10/2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Renseignement communautaire

1 signalement communautaire

CatégoriePHISHING

@goyxard Telegram Username

Données factuelles et rapports externes

Community Scam Report — ChainAbuse
1 report filed for xrpairdrop.net (1 written by a person) · category: Phishing · source checked
“@goyxard Telegram Username”
— reported by Anonymous on Oct 1, 2024 · Source: ChainAbuse (TRM Labs) — full report and evidence there.
Référencement naturel et nom de domaine
Analyse approfondie

Ce site vous a-t-il affecté ?

3 evidence signal groups linked 0 reports recorded Non vérifié
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.

Europol
Trouvez le canal de signalement officiel pour votre pays de l'UE
National police directory
Méfiez-vous des escrocs qui prétendent vous aider à récupérer vos biens ! Les criminels peuvent recontacter leurs victimes tout en se faisant passer pour des enquêteurs, des avocats ou des agents de recouvrement. Ne payez pas de frais initiaux et ne partagez pas vos informations d'identification. En savoir plus sur la fraude liée aux aides à la reprise →

Signalez-le à vos autorités locales

Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.

Annuaire de 97 pays

Template-based draft · optional AI wording assistance requires separate consent

Brouillon assisté par l'IA : les détails de l'incident sont traités par le fournisseur d'IA · Examinez-le et soumettez-le vous-même

Vérifier n&#x27;importe quel domaine

Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique

Scanner maintenant

Signaler une tentative d&#x27;hameçonnage

Signalez les domaines suspects à notre base de données des menaces — protégez la communauté

Signaler

Flux d&#x27;alertes en temps réel

Rapports de phishing récents et changements de disponibilité observés

Surveiller

Restez informés, restez en sécurité

Surveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif

Flux d'alertes en temps réel Contester cette annonce
HTML · IFRAME

Intégrer ce rapport

Partagez ces informations sur les menaces sur votre site web ou votre blog

embed.html
<iframe
  src="https://phishdestroy.io/fr/embed/domain/xrpairdrop.net"
  title="PhishDestroy threat report for xrpairdrop.net"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>