VirusTotal
15 / 92 engine detections
Ouvrir le rapport

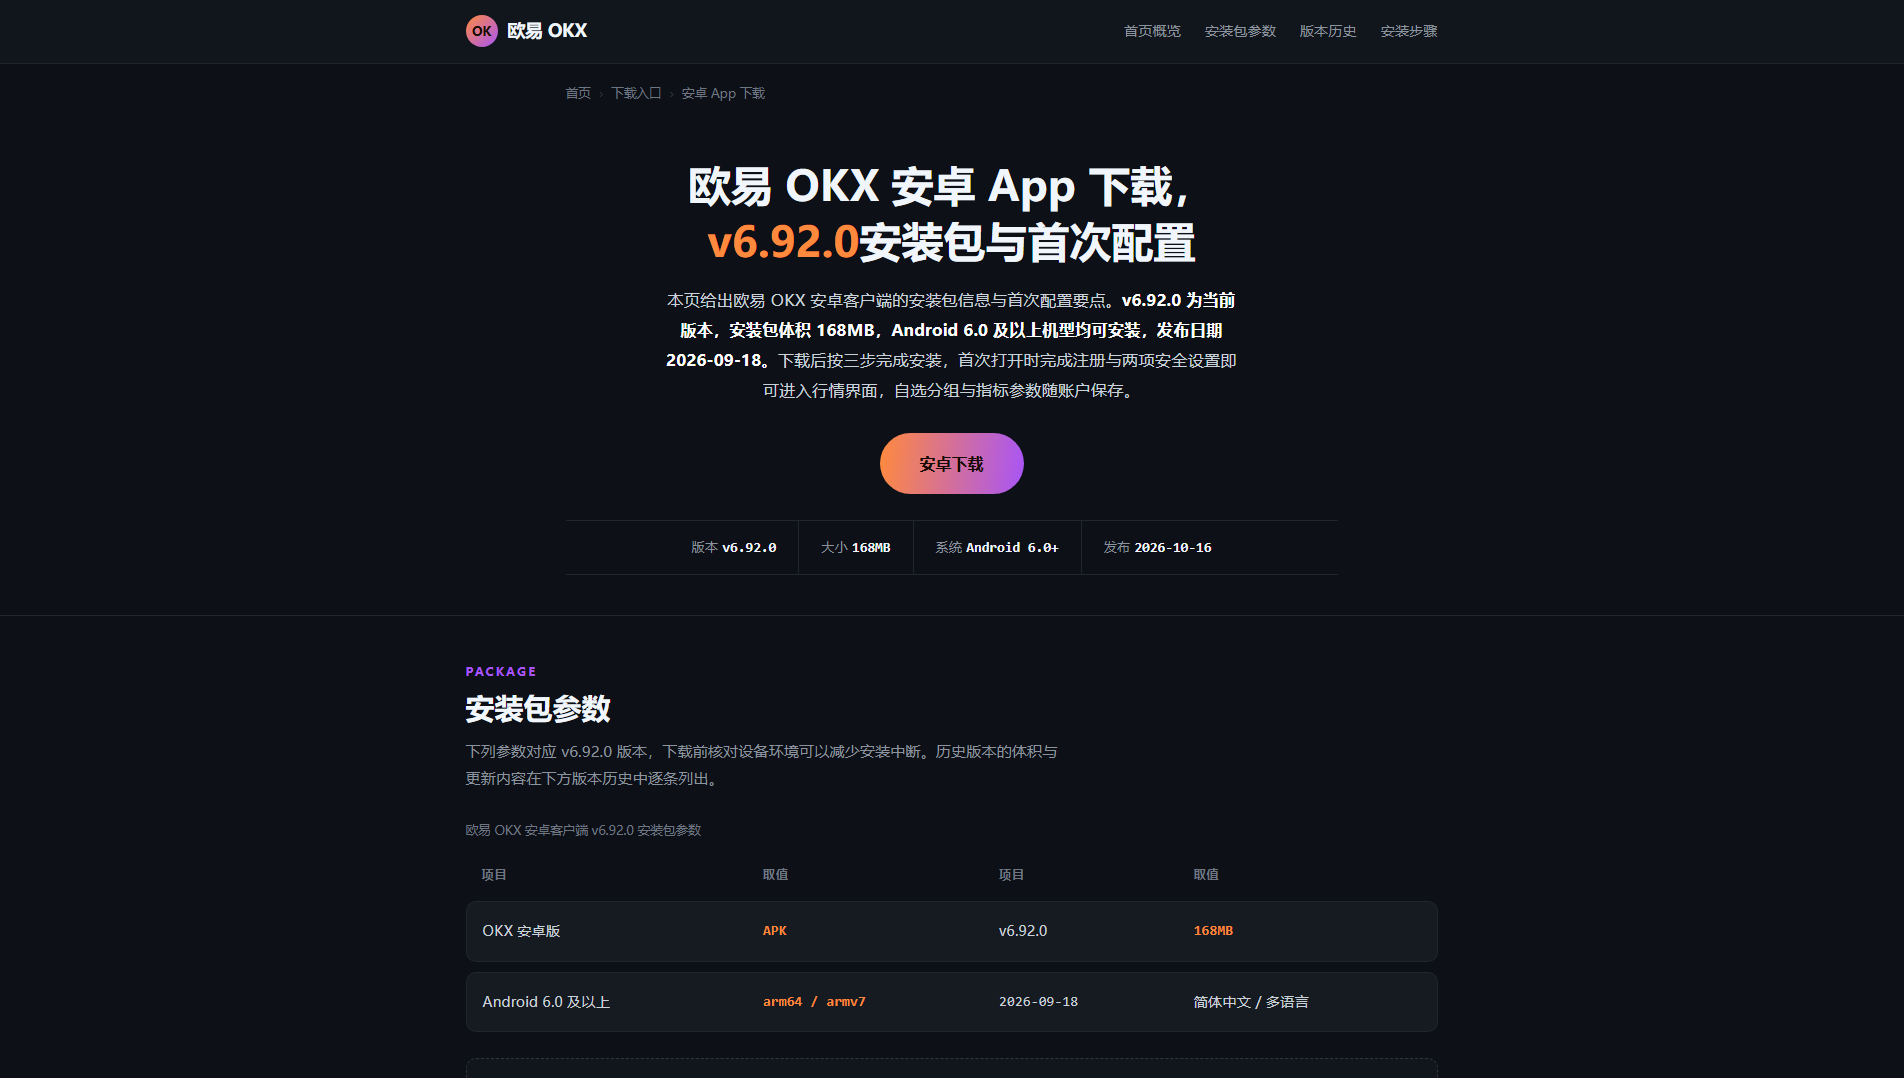
“欧易 OKX . 欧易app下载”
The sent-report ledger records the first outgoing report at .
The recorded recipient is 1208060625@qq.com.
The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Usurpation de OKX: kalok-okx.com.cn — Dernier actif connu (HTTP 200). Résumé des preuves: VirusTotal 15/92 (alphaMountain.ai, BitDefender, CRDF, Emsisoft…
L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.
15 / 92 engine detections
Ouvrir le rapportMalveillant
Ouvrir le rapportMalveillant
Ouvrir le rapportScan report
Ouvrir le rapport3 community references
Ouvrir le rapportNo threat flag
Ouvrir le rapportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
kalok-okx.com.cn is a phishing site that impersonates OKX, the cryptocurrency exchange known in China as 欧易. It presents itself as an official app download portal and is aimed at Chinese-speaking users looking for the OKX app. PhishDestroy first saw the domain on 2026-10-16, three days after it was registered. As of 2026-10-19 the site was still online and serving its content.
The page title, "欧易 OKX . 欧易app下载", promises an OKX app download, a common lure for exchange impersonation schemes. Pages like this usually push a counterfeit app or a lookalike login flow instead of the genuine software. That fake app or form then captures exchange credentials, two-factor codes or wallet recovery phrases, and the operators use them to empty the victim's account or wallet. Because the domain borrows the OKX name and Chinese branding, victims often believe they are on an official mirror.
On 2026-10-16, 5 of 92 VirusTotal engines flagged the domain: Emsisoft, Fortinet, LevelBlue, Netcraft and Webroot. That count is modest, but other sources back it up. urlscan.io returned a malicious verdict and detected OKX branding on the page. The domain appears on the PhishDestroy, MetaMask and SEAL blocklists, and it is referenced in 3 AlienVault OTX pulses.
The domain was registered on 2026-10-13 through Web Commerce Communications Limited. It resolves to 219.234.2.6 on the WEST263GO-HK network operated by West263 International Limited in Hong Kong. Its TLS certificate was issued by Let's Encrypt (YR1), so the padlock in the browser says nothing about whether the site is legitimate.
Do not download or install anything from this site, and uninstall any app you got from it. If you entered OKX login details, change your password from the official OKX app or website, reset two-factor authentication and check for unfamiliar devices, withdrawal addresses or API keys. If you typed a wallet recovery phrase into this site or its app, treat that wallet as compromised and move your funds to a new wallet right away. Defenders should block the domain and its hosting IP, and report it to the registrar and the hosting provider.
Last checked
 (MY)
ns1.julydns.comns2.julydns.comLocation describes the IP network.
c885c9d00e9be8042a5e675b5f014dfe6eaa790496361cf93c2044648b3f3569www.kalok-okx.com.cnSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
www.kalok-okx.com.cnDomain recordThe original observation time is not recorded for these hostnames.
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://kalok-okx.com.cn/https://kalok-okx.com.cn/Server: nginxContent-Type: text/htmlContent-Encoding: gzipsummarykeep-alivegziptext/htmlFri, 16 Oct 2026 14:25:28 GMTW/"6acf290d-56ef"Wed, 14 Oct 2026 07:02:37 GMTnginxmax-age=31536000chunkedAccept-EncodingValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Inconnu→live_content
content_served
Accessible
No threat flag
View source15/92 engine detections
View source3 community references
View sourcePD-20261016-B76178
Page captured
View sourcekalok-okx.com.cn
View source89 domaines ressemblants enregistrés
Chaque ligne correspond à une raison pour laquelle un domaine est associé à cet hébergeur. La taille des nœuds indique les détections de VirusTotal et les nœuds en pointillés sont déjà hors ligne. Les listes complètes figurent ci-dessous.
Même hachage de favicon ou même titre de page que cet hébergeur.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Enregistrés auprès du même bureau d'enregistrement. Un bureau d'enregistrement dessert des millions de clients sans lien entre eux ; ce regroupement constitue donc simplement un constat et ne prouve pas l'existence d'un lien.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
kalok-okx.com.cn
PD-20261016-B76178 Recipient: 1208060625@qq.com Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.


Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
kalok-okx.com.cn)Même si vous ne disposez pas de tous les détails — déposer quand même une plainte. Même des informations partielles peuvent aider les enquêtes.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique
Scanner maintenantSignalez les domaines suspects à notre base de données des menaces — protégez la communauté
SignalerRapports de phishing récents et changements de disponibilité observés
SurveillerSurveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.