VirusTotal
22 / 89
Signaler

“Ledger® Live: Desktop | Getting Started with Ledger”
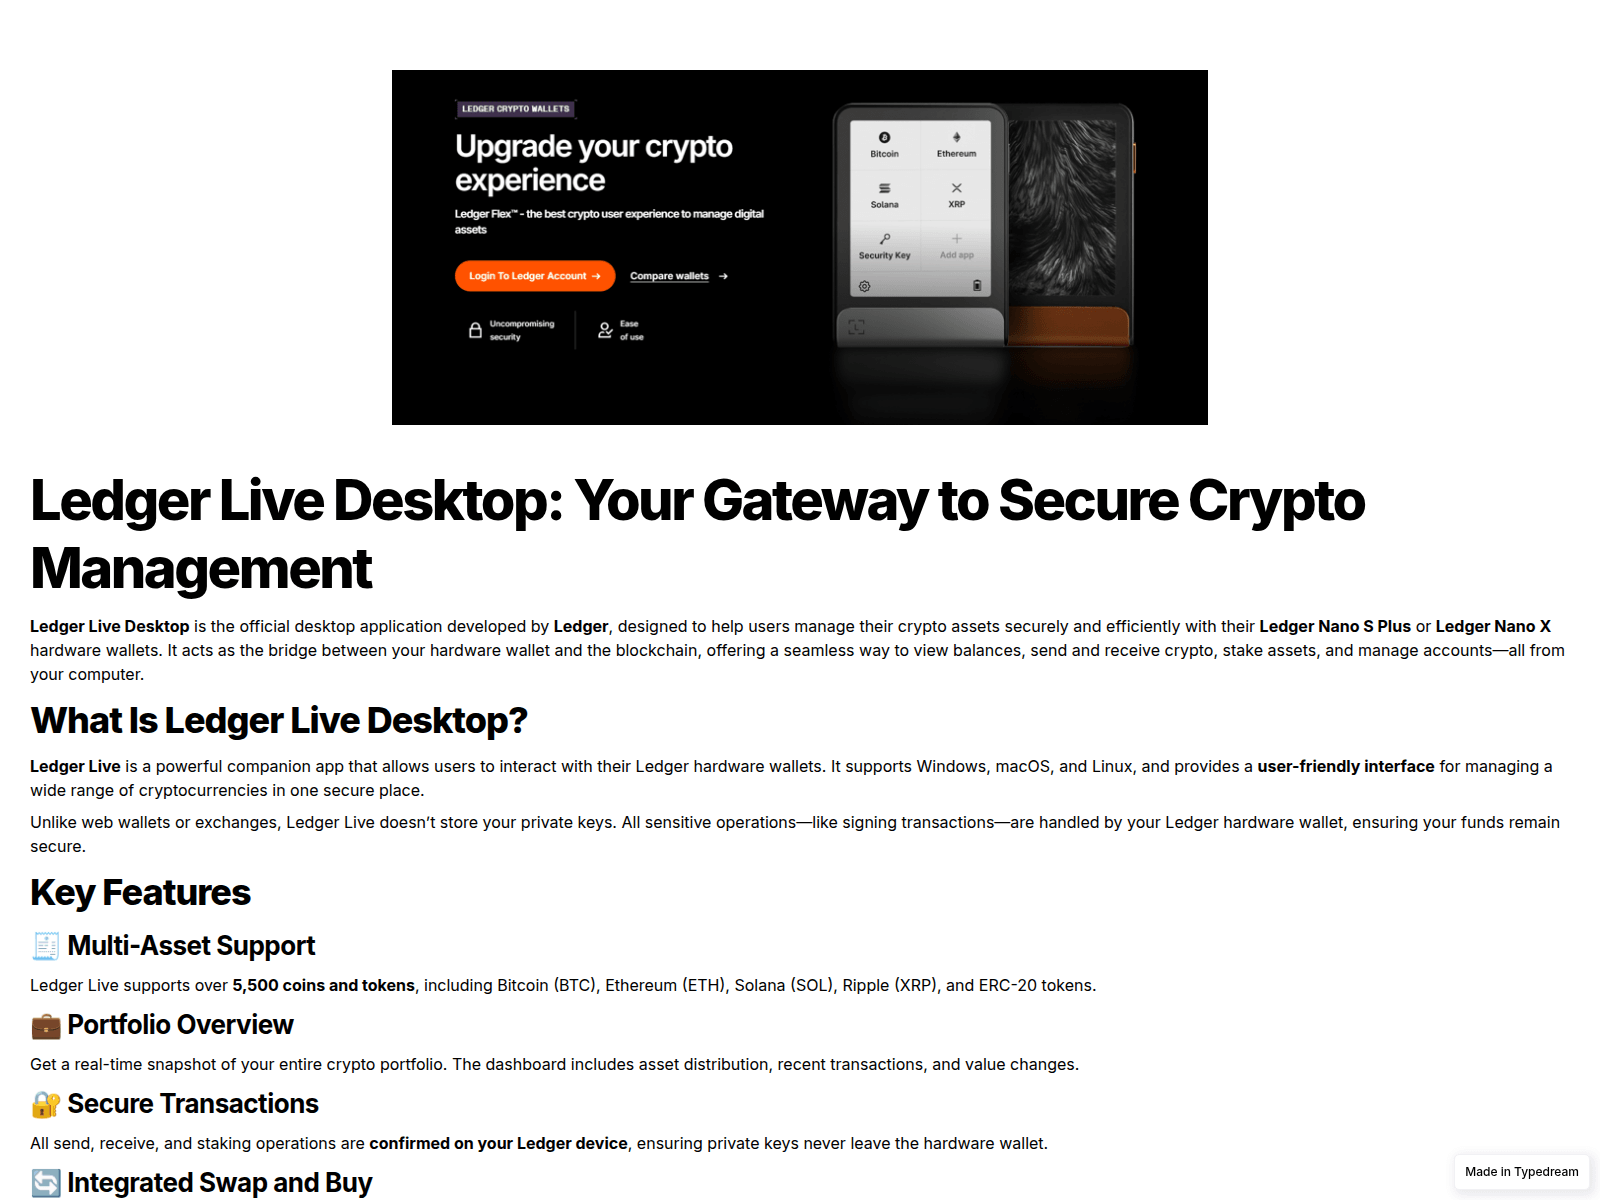
docs--login--ledger-live-desktop-io.typedream.app — Dernier actif connu (HTTP 200). Usurpation de l'identité de la marque : Ledger; Type d'arnaque : Credential Phishing. Résumé des preuves: VirusTotal 22/89 (Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF); URLScan malicious verdict; 2 external blocklist matches (MetaMask, SEAL); CF Radar malicious; PhishDestroy score 100/100. Bureau d’enregistrement: Typedream.
L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.

Analysis conducted on July 30, 2026 confirms that docs--login--ledger-live-desktop-io.typedream.app is an active phishing domain targeting Ledger, a hardware cryptocurrency wallet provider. The domain is registered through Typedream, a platform that allows users to create and host web pages without traditional domain registration processes. Infrastructure analysis reveals the domain resolves to IP address 188.114.96.3, though nameserver information is absent, which is atypical for standard web hosting setups. The SSL certificate is issued by Google Trust Services, providing HTTPS encryption that may lend a false sense of legitimacy to potential victims.
Detection data indicates the domain is flagged by 22 of 91 security vendors on VirusTotal, a significant indicator of malicious activity. It also appears on two security blocklists, including PhishDestroy and OpenPhish, further corroborating its classification as a phishing site. The domain remains active as of the report date, with no evidence of takedown or mitigation efforts. The subdomain structure, including 'docs--login--ledger-live-desktop-io,' suggests an attempt to impersonate Ledger's official desktop application, Ledger Live, likely to deceive users into entering sensitive credentials or recovery phrases.
Defenders should prioritize blocking this domain at the network level, particularly in environments where cryptocurrency-related activities are conducted. Security teams are advised to monitor for any attempts to access this domain from corporate or personal devices and to educate users about the risks of interacting with unofficial Ledger-related sites. Given the domain's active status and the high-risk nature of cryptocurrency phishing, immediate action is recommended to prevent potential financial losses. The exact content and functionality of the site remain unanalyzed, but the available evidence strongly supports its classification as a phishing resource.
Enregistrement des observations « crawler contre navigateur » pour cet hôte, ainsi qu'une vérification en temps réel des empreintes numériques pour les systèmes de répartition du trafic de type Keitaro.
cloudflareLocal archivé le 2026-07-31 03:34:57 UTCNote relative à la numérisation: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
La réputation Edge-IP n’est pas attribuée à ce domaine.
Location describes the IP network.
ab441e0ffa6b15dd7c83fe1fe0e35948cc4fafcbe4787eb2ec7c78bb57a9a4d6typedream.appSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of docs--login--ledger-live-desktop-io.typedream.app · checked Jul 30, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://docs--login--ledger-live-desktop-io.typedream.app/https://docs--login--ledger-live-desktop-io.typedream.app/Content-Type: text/html; charset=utf-8X-Powered-By: Next.jsCache-Control: s-maxage=120, stale-while-revalidateServer: cloudflareCF-Cache-Status: DYNAMICContent-Encoding: gzipsummaryGET,HEAD,PUT,PATCH,POST,DELETE*h3=":443"; ma=86400s-maxage=120, stale-while-revalidateDYNAMICa238dd0c6c600d18-FRAkeep-alivegziptext/html; charset=utf-8Fri, 31 Jul 2026 01:34:56 GMT{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=JYm0PoI1Vrtb8yMdikxWMvXdHa4Cd9i5QLwG94ZUGwuLQUopURVLvueIKtJRAhaXzEX1FA%2BBUobKYCQKYCWVt485A5NwbJw96tmqGxVUSOGaYSjdhpDaN3m%2Bs%2FeLmziWKhYcXSodkcloudflarechunkedAccept-Encoding1.1 google/docs--login--ledger-live-desktop-ioHITNext.js0.116.0Values retained by the collector; long values may be shortened during collection.
188.114.96.3. 11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
151 domaines ressemblants enregistrés
100 affichés sur 151
1 signalement communautaire
CatégoriePHISHING
Phishing site impersonating Ledger: http://docs--login--ledger-live-desktop-io.typedream.app/ Basis: a credential-harvesting or wallet-connect flow was confirmed on the live page; independently corroborated by 3 external source(s) (google_webrisk; urlscan:researcher(@phish_repor
“Phishing site impersonating Ledger: http://docs--login--ledger-live-desktop-io.typedream.app/ Basis: a credential-harvesting or wallet-connect flow was confirmed on the live page; independently corroborated by 3 external source(s) (google_webrisk; urlscan:researcher(@phish_report,phishdestroy); urlscan:verdict(score=100)). Hosted on Typedream. First seen 2026-08-17 11:19:53; last confirmed live 2026-08-24 03:19:16. The site was confirmed live at the time of reporting. Reported by an automated”
Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.


Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.
Template-based draft · optional AI wording assistance requires separate consent
Chaque ligne correspond à une raison pour laquelle un domaine est associé à cet hébergeur. La taille des nœuds indique les détections de VirusTotal et les nœuds en pointillés sont déjà hors ligne. Les listes complètes figurent ci-dessous.
Même hachage de favicon ou même titre de page que cet hébergeur.
Ces rapports renvoient à la même adresse IP périphérique partagée. Ils facilitent la découverte des rapports mais n'impliquent pas de propriété commune ni de serveur d'origine partagé.
Ces domaines ciblent également les utilisateurs d'Ledger. Afficher toutes les menaces liées à « Ledger » →
Enregistrés auprès du même bureau d'enregistrement. Un bureau d'enregistrement dessert des millions de clients sans lien entre eux ; ce regroupement constitue donc simplement un constat et ne prouve pas l'existence d'un lien.
Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique
Scanner maintenantSignalez les domaines suspects à notre base de données des menaces — protégez la communauté
SignalerRapports de phishing récents et changements de disponibilité observés
SurveillerSurveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif