IC3 del FBI
Denunciar delitos cometidos a través de Internet en los Estados Unidos
Federal tips line1-800-CALL-FBI

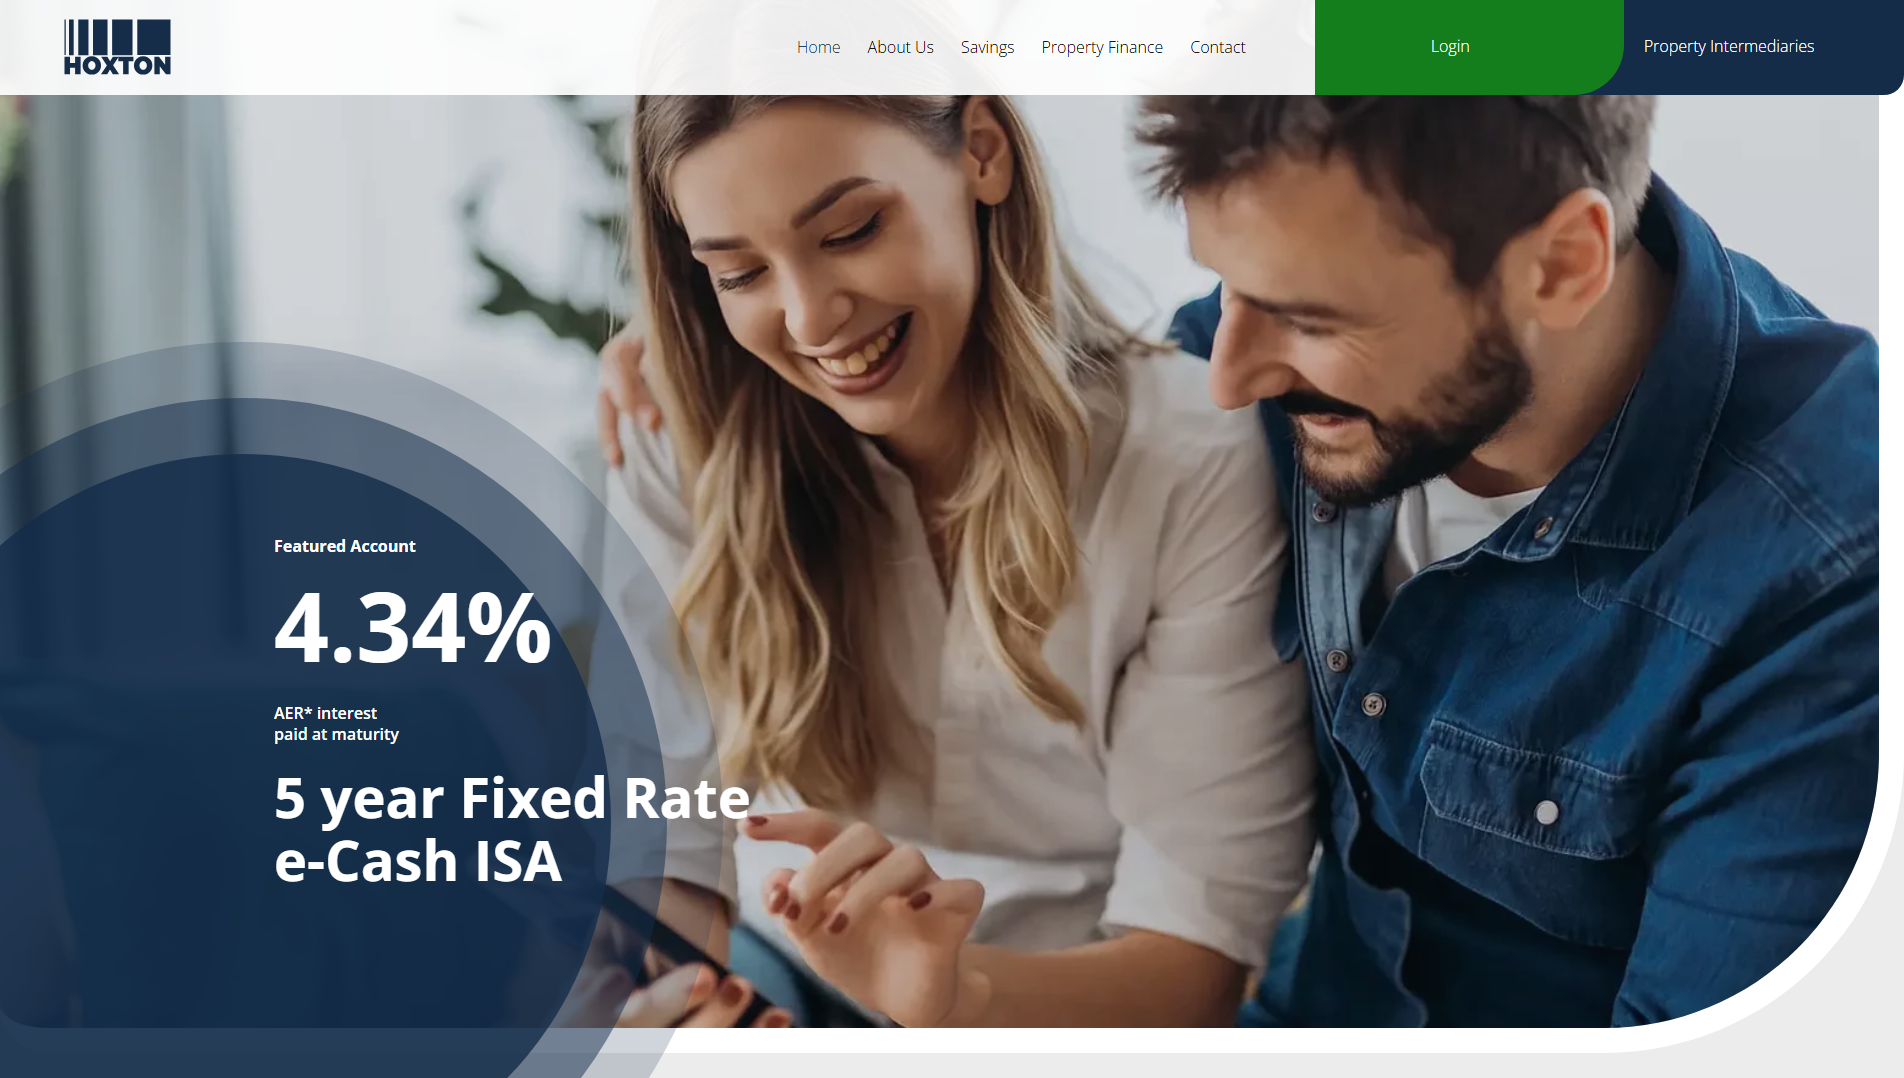
“Savings and Property - we'll help you achieve your goals”
The domain www.hoxtonbank.com was observed on 2026-07-12 and is classified as a high‑risk banking phishing site.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
The domain www.hoxtonbank.com was observed on 2026-07-12 and is classified as a high‑risk banking phishing site. The site presents a page titled “Savings and Property – we’ll help you achieve your goals,” mimicking a legitimate financial institution to lure victims into disclosing credentials. Threat intelligence assigns a risk level of high and marks the status as active.
The domain was registered on 2026-02-20 through Unstoppable Domains Inc. It uses the authoritative name servers ns5.nl.hostsailor.com and ns6.nl.hostsailor.com. DNS resolution points to the IPv4 address 194.36.191.196, which belongs to Host Sailor Ltd operating under AS60117 and is geolocated in the Netherlands.
The site serves an SSL certificate issued by Let’s Encrypt (R12), indicating the presence of HTTPS encryption but not authenticity. HTTP requests receive a 302 redirect response, a common technique to hide the final landing page. On VirusTotal the domain received a single positive detection out of 95 scanners, and it appears on one external blocklist. The Gridinsoft trust score is 0 out of 100, and PhishDestroy has already blocked the domain.
While the exact phishing payload has not been disclosed, the combination of a brand‑spoofing page title, active status, low trust score, and the presence on a phishing‑specific blocklist justifies immediate mitigation. Defenders should add 194.36.191.196 to outbound and inbound blocklists, enforce DNS sink‑hole rules for www.hoxtonbank.com, and monitor the associated name servers for future changes. Continuous re‑scanning with multiple AV engines is advised to capture any emerging detections. Organizations should also educate users about unsolicited requests for banking credentials that reference “Savings and Property” or similar phrasing.

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
LiteSpeedNota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=./home/; server=LiteSpeed
 (US)

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Forma parte de la campaña de phishing «Unknown». Ver todos los dominios de la campaña →
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Estos dominios también se dirigen a los usuarios de Unknown. Ver todas las amenazas de «Unknown» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.