Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
usdtflashpro.online favicon

usdtflashpro.online

“Not Found”

Registrador
GoDaddy
Resolved IP
92.119.166.5
Registered
07/04/2026
Veredicto de amenaza Crítico
Disponibilidad No verificado La accesibilidad actual no está verificada Observado
Source: HTTP probe
VirusTotal detecciones: 2/92 URLQuery threat systems: 1 alert Suplantación de marca: Binance
OTX: 24 refs 07/04/2026 Binance 1 Report Sent
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 2. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@hosting-manage.com. The latest stored availability evidence still shows the domain reachable; 6 months has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
6 months
Reports sent
1
Latest case ID
PD-20260407-4A839A
Current status
HTTP 409 at latest stored check
Resumen del informe

usdtflashpro.online is a confirmed USDT crypto drainer scam. Detected by 5/95 security vendors, this domain targets cryptocurrency users with fraudulent.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

VirusTotal
VirusTotal
2 det.
URLQuery
URLQuery
1 threat alert
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
17/100Very Likely Unsafe
Certificado TLS
Caducado o no verificado
Edad
6 mo
PhishDestroy
DestroyList
Incluido
Reports Sent
1

Source evidence

10 sources

VirusTotal

2 / 92

Denunciar

URLQuery

1 threat-system alert

Denunciar

PhishStats

checked — no match recorded

OTX

24 community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

URLScan verdict

Análisis finalizado

Denunciar

Bloqueos de DNS

12 comprobado — sin bloqueos

CF Radar

Report stored; verdict not recorded

Denunciar

Google Safe Browsing

Checked; no threat flag recorded

Denunciar
Inteligencia de seguridad de red
Threat Detection Systems 1 alert
Detection System Indicator Verdict Alert
DNS4EU usdtflashpro.online malicious Sinkholed

Resumen de las pruebas

Crítico
VirusTotal
2/92
OTX
24 community refs
URLScan
Stored capture

This domain, usdtflashpro.online, is identified as a USDT crypto drainer, a specialized phishing threat designed to deplete cryptocurrency wallets by tricking users into authorizing malicious transactions. The site likely presented itself as a legitimate USDT (Tether) transaction service or wallet utility, luring victims with promises of instant transfers or token swaps. Once users connected their wallets, the site would execute unauthorized transactions, siphoning funds to attacker-controlled addresses. The use of USDT-specific branding and transaction-themed deception aligns with known crypto drainer tactics targeting stablecoin users. Infrastructure analysis reveals multiple high-risk indicators. The domain was registered on April 07, 2026, through GoDaddy.com, LLC, with an anomalous future creation date suggesting potential domain spoofing or registry manipulation. It resolves to the IP address 92.119.166.5 and uses a Let's Encrypt SSL certificate, a common tactic to appear legitimate. Detection metrics show 5 out of 95 security vendors on VirusTotal flagging the domain, while it appears on one security blocklist. Third-party trust scores are critically low, with Scamadviser assigning 17/100 and Gridinsoft assigning 0/100, further confirming its malicious nature. Users who interacted with usdtflashpro.online should immediately revoke any wallet authorizations granted to the site and disconnect it from all connected applications. Audit recent wallet transactions for unauthorized USDT transfers and report any suspicious activity to the relevant blockchain explorer. If credentials or private keys were entered, transfer remaining assets to a new, secure wallet and monitor for signs of compromise. Given the domain's current offline status, users should remain vigilant for similar scams using comparable naming conventions or branding.

Extracted from stored page analysis

Observed indicators

0 wallet · 2 Telegram

Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.

Telegram
https://t.me/flashproofficilleStored page reference
Telegram
https://t.me/marcocavicchioliufficialeStored page reference

IoC extraction recorded 2026-07-29 02:07:02 UTC

Análisis de detección y evasión

Se sospecha que se está utilizando «cloaking»: los títulos del escáner y del visitante no coinciden

No se ha observado No se ha observado ningún enmascaramiento en la exploración almacenada.

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
No se ha observado
Puntuación de encubrimiento
0/6
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
cloudflare

Nota del escáner: http_other: raw=http_409; http=409; via=http_proxy; server=cloudflare

Título que se muestra en el escáner de seguridadDNS resolution error | usdtflashpro.online | Cloudflare
Título que se muestra al visitante del navegadorNot Found
Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 captures

Título de la página
Not Found
Impersonates
Binance Bybit MetaMask Mexc Phantom Ton Trust Wallet
Certificado TLS
Certificate hostname mismatch · Emitido por Let's Encrypt · stored validity ends in 53 days

Domain details

Dominio
URLScan Verdict Análisis finalizado score 0 report ↗
Reputación de IP abuse score 0/100 0 reports checked 12/10/2026
OTX Tags 2026-04activeall-domainsblocklistcontentcryptodominiosdrainerfraudlivemonthlyphishdestroyphishingscam
Registrador GoDaddy US(US)
Contacto de abusoabuse@hosting-manage.com
Registro de la ICANNICANN Lookup (RDAP) →
RegistroCreado 07/04/2026 (189d) — Expires 04/04/2027
Estado HTTP409 Error
Detalles técnicosProvenance & timestamps
Primera detección07/04/2026
DOM Analysisanalyzed 09/10/2026score 81/1007 brand signals
IoC Extractionscanned 29/07/20260 wallet · 2 Telegram IoCs
Submitted URLhttps://usdtflashpro.online/
Favicon Hash
ID del caso
ICANN OVERSIGHT

Acreditación y contexto RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft No se envía nada automáticamente.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
92.119.166.5
Network ASN
AS213535
Organization
YottaSrc
Observed location
Frankfurt am Main, DE
Server header
Microsoft-HTTPAPI/2.0

Servidores de nombres 1

  • ns3.srvx.ws

Location describes the IP network.

Certificado TLS

Issuer
Let's Encrypt
Valid from
2026-04-07 20:46:57
Valid until
2026-07-06 20:46:56
Hostname coverage
Certificate hostname mismatch
Validity
Stored certificate expired
Collection time
2026-04-08 01:01:19 UTC
Collection source
PhishDestroy collector
Certificate fingerprint14e65ad7d48c2ebe45e80a624121aab924546a5b2879cf1f567b3861d2c2283f
Certificate names · 1 SANs
  • www.usdtflashpro.online

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 92.119.166.5rapiddns.io

Latest Classified Outcome 2026-10-13 22:32:50 UTC

Primary outcome Desconocido reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unknown Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Desconocido Probe Inconclusive 20% 2026-10-13 22:32:50 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-09-15 22:18:14 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

2 / Los proveedores de seguridad de 92 marcaron este dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 2 detections
alphaMountain.ai
Gridinsoft

Evidencias archivadas

Wayback Machine Snapshot
Una instantánea histórica está disponible para revisión de evidencia.
View Archive
Análisis del rendimiento del sitio

Google PageSpeed Insights — mobile performance audit of usdtflashpro.online · checked Jun 26, 2026

76
Needs Work
Performance
FCP
1.71s
First Contentful Paint
LCP
6.4s
Largest Contentful Paint
CLS
0.046
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.71s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-06-26 08:56:24 UTC
    VirusTotal scanner detections updated from 2 to 5. Added scanner alerts: CRDF, CyRadar, Gridinsoft, SOCRadar, alphaMountain.ai.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
usdtflashpro.online detectados y puestos en cola para su análisis completo
07/04/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
08/04/2026
VirusTotal
2/92 recorded on VirusTotal
07/10/2026
OTX Community References
24 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
01/10/2026
Brand Impersonation
Impersonation of Binance
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
14/10/2026
VT Detection +3
+3 new detections (2 → 5): CRDF, CyRadar, Gridinsoft, SOCRadar +1
26/06/2026
Sent Report Recorded
Stored outgoing record associated with registrar GoDaddy.com, LLC, 1 abuse contact
abuse@hosting-manage.com
07/04/2026
Lista de destrucción publicada
07/04/2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Dominios similares

187 dominios similares almacenados

Mostrar todo (88)
binabce.com replacement binacne.com transposition binan.ce.com subdomain binancecom.com various binanci.com vowel-swap binanco.com vowel-swap binancr.com replacement binancs.com replacement binancw.com replacement binande.com replacement binanfe.com replacement binanve.com replacement binanxe.com replacement binnace.com transposition binonce.com vowel-swap binsnce.com replacement binunce.com vowel-swap binynce.com replacement binznce.com replacement bniance.com transposition bunance.com replacement ibnance.com transposition ninance.com replacement b-inance.com hyphenation b8inance.com insertion b8nance.com replacement b9nance.com replacement bbinance.com repetition bhinance.com insertion bi-nance.com hyphenation biance.com omission bibance.com replacement bibnance.com insertion bihance.com replacement bihnance.com insertion biinance.com repetition bijnance.com insertion biknance.com insertion bimance.com homoglyph bimnance.com insertion bin-ance.com hyphenation binaance.com repetition binabnce.com insertion binace.com omission binahce.com replacement binamnce.com insertion binan-ce.com hyphenation binanbce.com insertion binanc-e.com hyphenation binanc.com omission binanc3.com replacement binancce.com repetition binancve.com insertion binancxe.com insertion binancz.com replacement binandce.com insertion binane.com omission binanec.com homoglyph binanhce.com insertion binanmce.com insertion binannce.com homoglyph binanvce.com insertion binanxce.com insertion binarnce.com homoglyph binasnce.com insertion binawnce.com insertion binbance.com insertion binhance.com insertion binmance.com insertion binnance.com homoglyph binnce.com omission binqance.com insertion binsance.com insertion binwnce.com replacement binyance.com insertion bionance.com insertion birnance.com homoglyph biunance.com insertion bjnance.com replacement bnance.com omission bninance.com insertion boinance.com insertion bonance.com replacement buinance.com insertion bvinance.com insertion clinance.com homoglyph dinarce.com homoglyph ginance.com replacement

Se muestran 100 de 187

Inteligencia comunitaria

1 reporte de la comunidad

CategoríaPHISHING

The PhishFort Detection System has flagged this as a domain threat, classified as other. Threat detected at 2026-05-04T18:04:21.899Z.

Reportes de la comunidad

Reportado por 1 miembro de la comunidad; visto por primera vez el 07/04/2026

Reportes almacenados
1
URL únicas reportadas
1
Aceptado1

Datos y informes externos

Third-Party Detection — ChainAbuse
1 report filed for usdtflashpro.online · category: Phishing · source checked
Flagged by PhishFort Detection System on May 4, 2026 — automated submission, not a user testimony. Source: ChainAbuse (TRM Labs).
Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260407-4A839A Recipient: abuse@hosting-manage.com
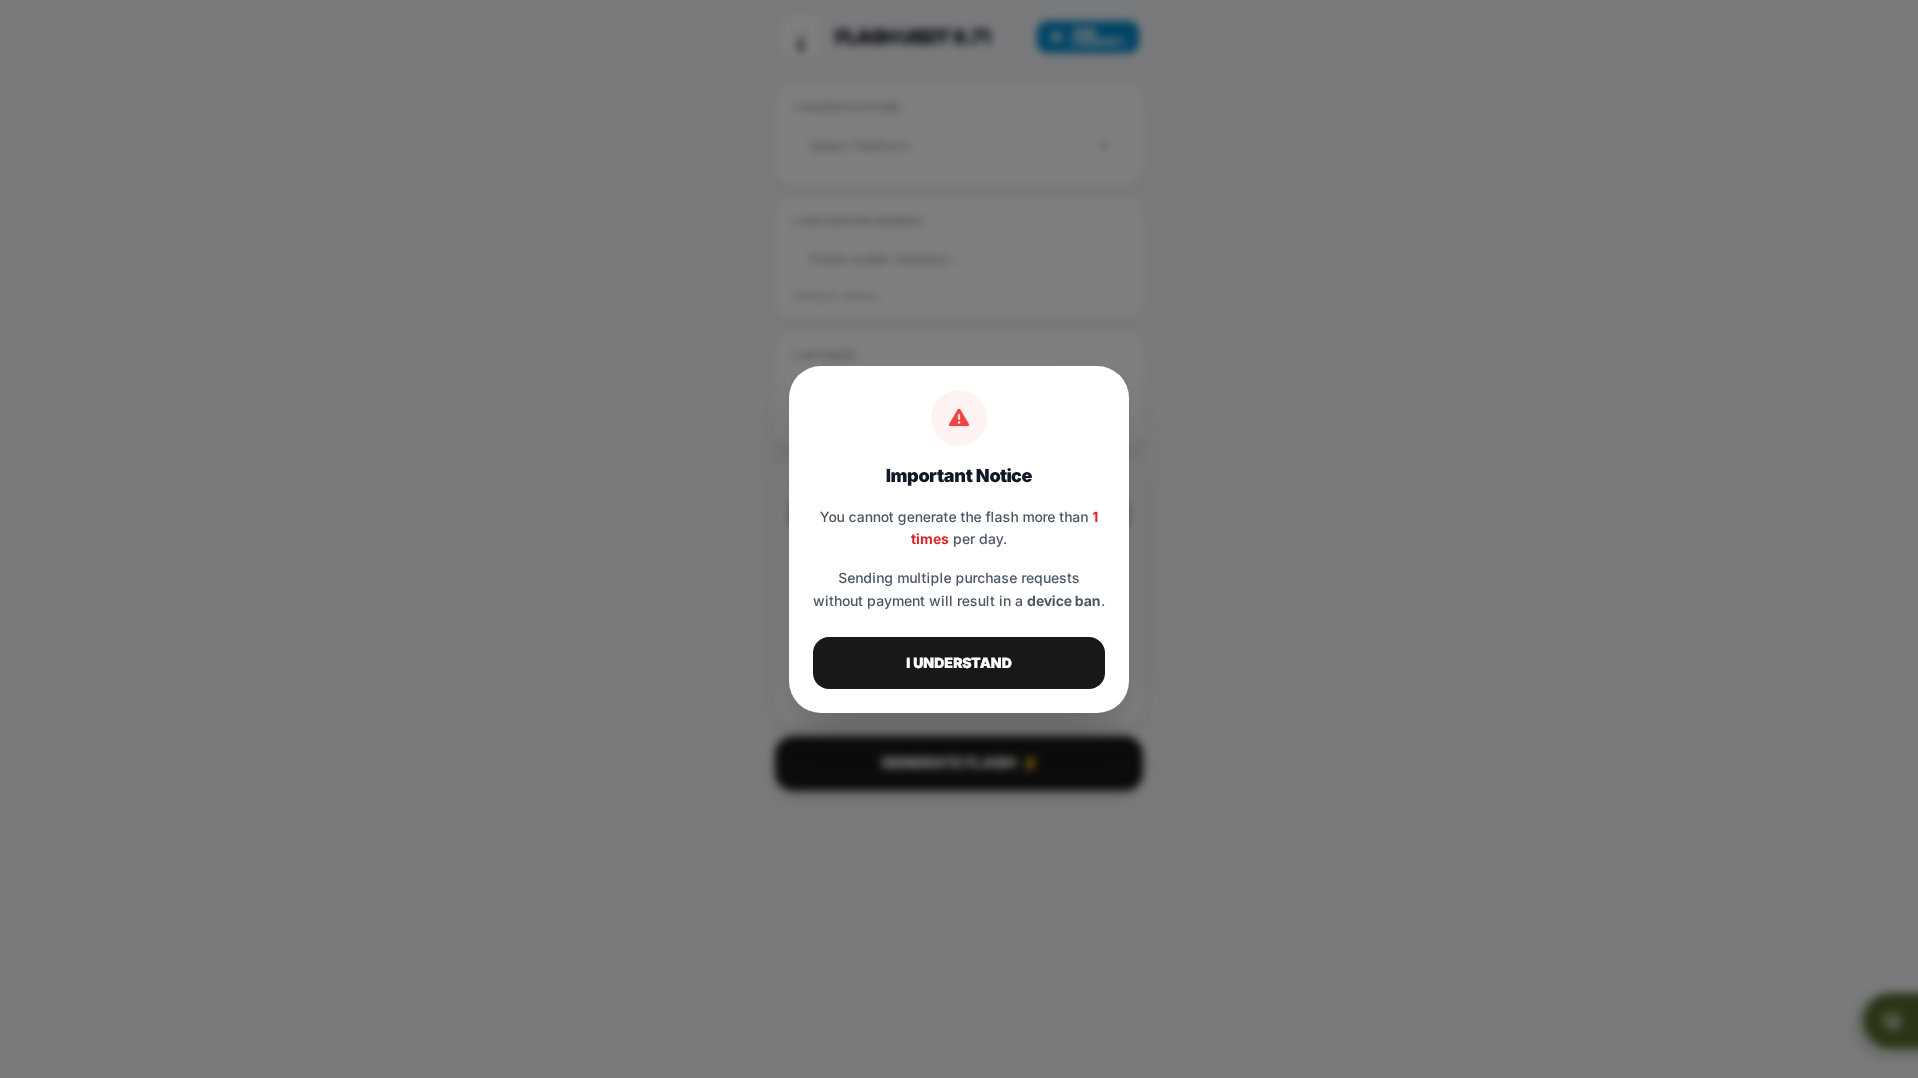
Page title stored with report: FLASH USDT PRO ONLINE 6.71
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 73.1 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Análisis en profundidad

¿Te ha afectado esta página web?

7 evidence signal groups linked 1 reports recorded No verificado
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.

Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/usdtflashpro.online"
  title="PhishDestroy threat report for usdtflashpro.online"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>