Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
uni.sushi-vip.xyz favicon

uni.sushi-vip.xyz

“undefined”

Veredicto de amenaza Crítico Puntuación de evidencia 84/100
Disponibilidad Último activo conocido Última observación de accesibilidad almacenada
VirusTotal detecciones: 8/89 Suplantación de marca: SushiSwap Último activo conocido
16/09/2026 SushiSwap 1 Report Sent CDN
Actions API
⚠️
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 8. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@dynadot.com. The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
4 days
Reports sent
1
Latest case ID
PD-20260916-C72B05
Current status
HTTP 302 at latest stored check
Resumen del informe

uni.sushi-vip.xyz — Último activo conocido (HTTP 302). Suplantación de marca: SushiSwap; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 8/89 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); URLScan malicious verdict; PhishDestroy score 84/100. Registrador: Dynadot.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

Resumen de las pruebas

CRÍTICO
Puntuación
84/100

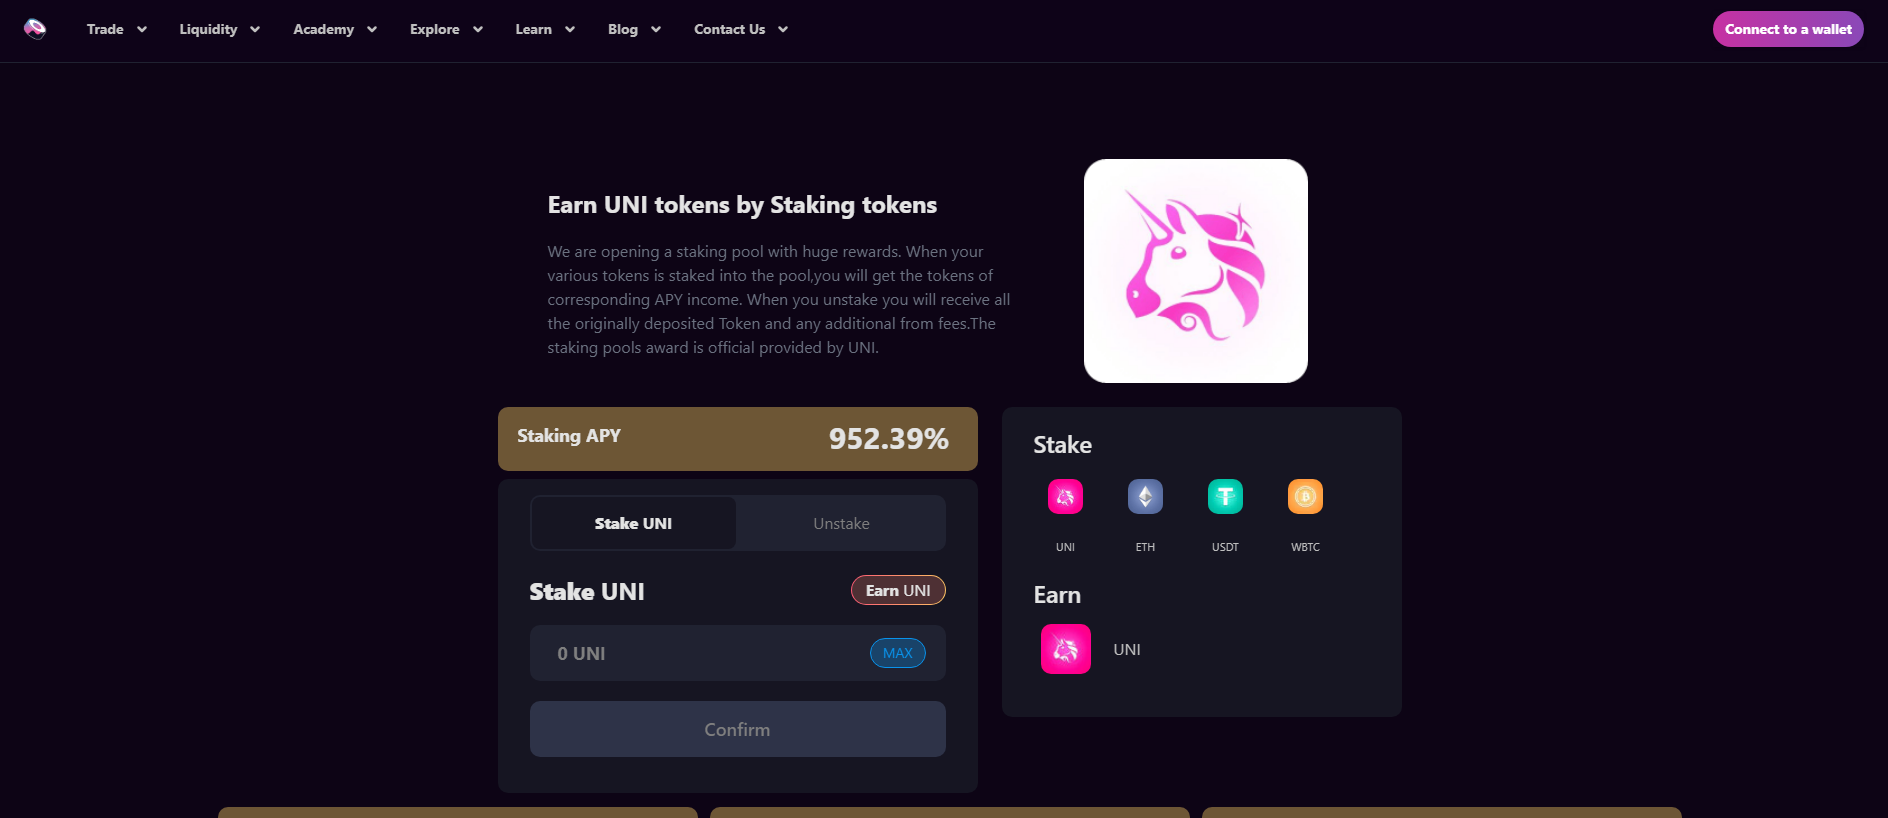
uni.sushi-vip.xyz is a subdomain of sushi-vip.xyz. PhishDestroy first observed the hostname on Sep 16, 2026. Stored content metadata identifies SushiSwap as the apparent target. The captured page title is “undefined”. Page analysis recorded additional brand references to Arbitrum, Avalanche, Discord, Ethereum, Fantom, MetaMask, Optimism, and Polygon. Stored page analysis classifies the content as impersonation. Current evidence score: 84/100 (critical).

Positive findings are stored from 2 sources: VirusTotal and URLScan. VirusTotal recorded 8 detections among 89 engines: alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker, G-Data, SOCRadar, VIPRE on Sep 20, 2026 at 02:10 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Uniswap and assigned phishing as its category on Sep 17, 2026 at 03:30 UTC. Non-positive and contextual checks: The separate external-blocklist snapshot contained no matches on Sep 21, 2026 at 02:20 UTC. URLQuery recorded no positive detection on Sep 16, 2026 at 13:12 UTC. Google Safe Browsing returned no flag on Sep 19, 2026 at 22:01 UTC.

HTTP 302 was recorded on Sep 21, 2026 at 01:34 UTC. Registration records for the registrable domain sushi-vip.xyz list Dynadot Inc as the registrar and Jun 21, 2026 as the creation date. At collection time, the hostname resolved to 104.21.38.3 on AS13335 (Cloudflare, Inc.). The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. DOM analysis on Sep 16, 2026 at 14:20 UTC returned 78/100. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Google Trust Services / WE1 as the certificate issuer with validity through Nov 17, 2026; checked Sep 16, 2026 at 16:02 UTC.

The content indicators and 2 positive source findings support the current SushiSwap-themed impersonation classification.

VirusTotal
VirusTotal
8 det.
URLScan
URLScan
Certificado TLS
Google Trust Services / WE1
Edad
3 mo
Estado observado
Último activo conocido 302
PhishDestroy
DestroyList
Incluido
Reports Sent
1
Cobertura de los datos VirusTotal 8 / 89 URLQuery checked — no detections recorded OTX no community references CF Radar scan completed URLScan capture informe almacenado URLScan verdict malicious TLS valid certificate, 57d WHOIS 3 mo old Captura de pantalla 3 captures · 3 sources

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update Sep 17, 2026 · 04:56 UTC
    VirusTotal scanner detections updated from 4 to 5. Added scanner alerts: CRDF.
  2. VirusTotal Detections Update Sep 16, 2026 · 19:12 UTC
    VirusTotal scanner detections updated from 1 to 4. Added scanner alerts: ESET, Forcepoint ThreatSeeker, alphaMountain.ai.
  3. VirusTotal Detections Update Sep 16, 2026 · 16:15 UTC
    VirusTotal scanner detections updated from 0 to 1. Added scanner alerts: SOCRadar.
  4. Threat First Observed Sep 16, 2026 · 15:11 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 104.21.38.3.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Checks
Reports
Disponibilidad
14/15
Sent Report Recorded
Stored sent-report record for registrar Dynadot Inc, hosting provider, 1 abuse contact
abuse@dynadot.com
16/09/2026

Estado de la lista de bloqueados pública

Evasion analysis

Cloaking & traffic-distribution check

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
cloudflare

Scanner note: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://www.yahoo.com/; server=cloudflare

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Captura guardada · 3 sources

Título de la página
undefined
Impersonates
Arbitrum Avalanche Discord Ethereum Fantom MetaMask Optimism Polygon
Certificado TLS
Valid transport encryption · Emitido por Google Trust Services / WE1 · valid for 57 days

Inteligencia de dominios

Dominio
URLScan Verdict Malicioso score 100 Phishing brand: Uniswap report ↗
Servidor / ASN cloudflare · AS13335 Cloudflare, Inc.
IP Context Cloudflare shared edge origin IP hidden La reputación de Edge-IP no se atribuye a este dominio.
Registrar (base domain) Dynadot US(US)
Dirección IP 104.21.38.3 CDN
UbicaciónCA Toronto, CA
RedAS13335 · Cloudflare, Inc.
La IP de origen está oculta detrás de un proxy CDN. Los resultados de IP inversa para la dirección perimetral contienen inquilinos no relacionados; encontrar el origen requiere DNS pasivo o datos de transparencia de certificado.
Registration (base domain)sushi-vip.xyz · Creado 21/06/2026 (91d) Expires 21/06/2027
Estado HTTP302 Found (Temporary)
Detalles técnicosDNS, SAN de SSL, marcas de tiempo
Primera detección16/09/2026
DOM Analysisanalyzed 16/09/2026score 78/1008 brand signals
IoC Extractionscanned 17/09/20260 wallet · 0 Telegram IoCs
Submitted URLhttps://uni.sushi-vip.xyz/stake/
Servidores de nombreselaine.ns.cloudflare.comnoah.ns.cloudflare.com
TLS Fingerprint
TLS Observationvalid from 19/08/2026scanned 16/09/2026
TLS SAN Domainssushi-vip.xyz
Favicon Hash
ID del caso
ICANN OVERSIGHT Registration: sushi-vip.xyz

Acreditación y contexto RAA

Registrar accreditation and DNS abuse obligations

For the registrable domain sushi-vip.xyz behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft No se envía nada automáticamente.
Tecnologías · 11 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

8 / Los proveedores de seguridad de 89 marcaron este dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 5 detections
alphaMountain.ai
BitDefender
CRDF
ESET
Forcepoint ThreatSeeker
G-Data
SOCRadar
VIPRE

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260916-C72B05 Recipient: abuse@dynadot.com
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 115.0 KB
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act

¿Te ha afectado esta página web?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países
Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.

Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/uni.sushi-vip.xyz"
  title="PhishDestroy threat report for uni.sushi-vip.xyz"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>