Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
ubi.fun favicon

ubi.fun

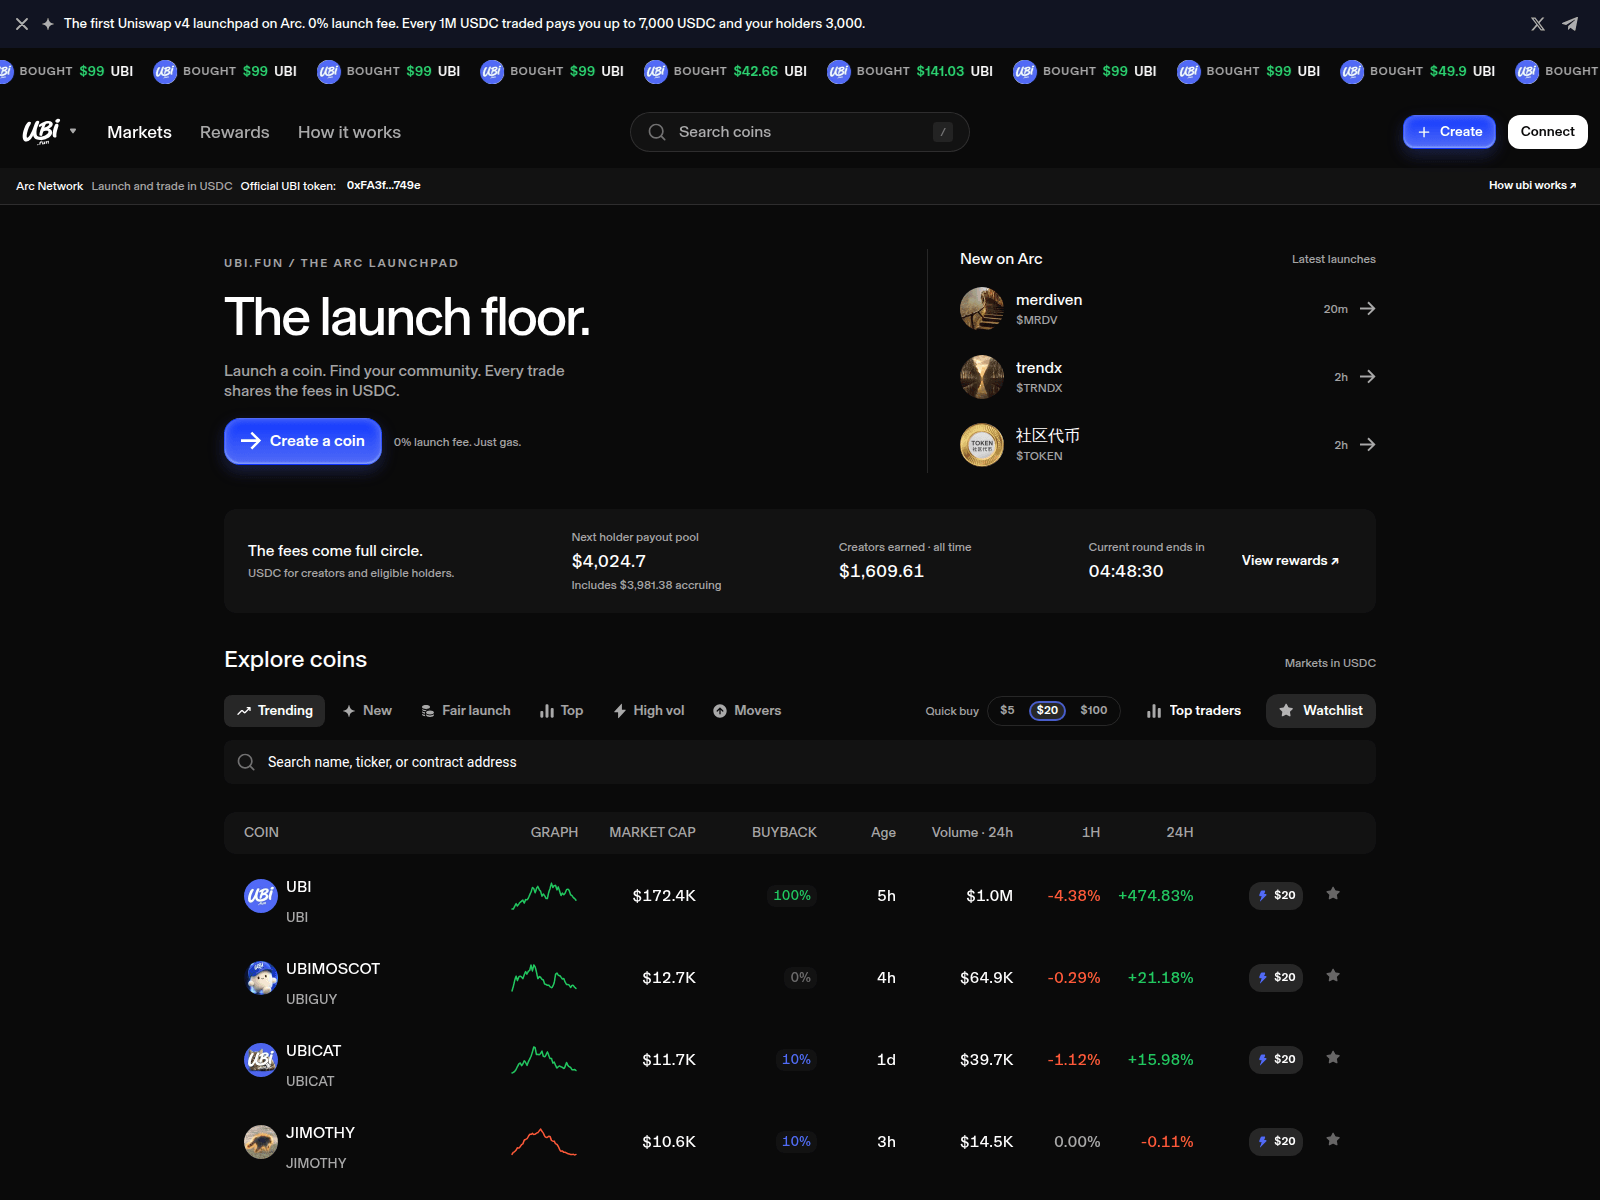
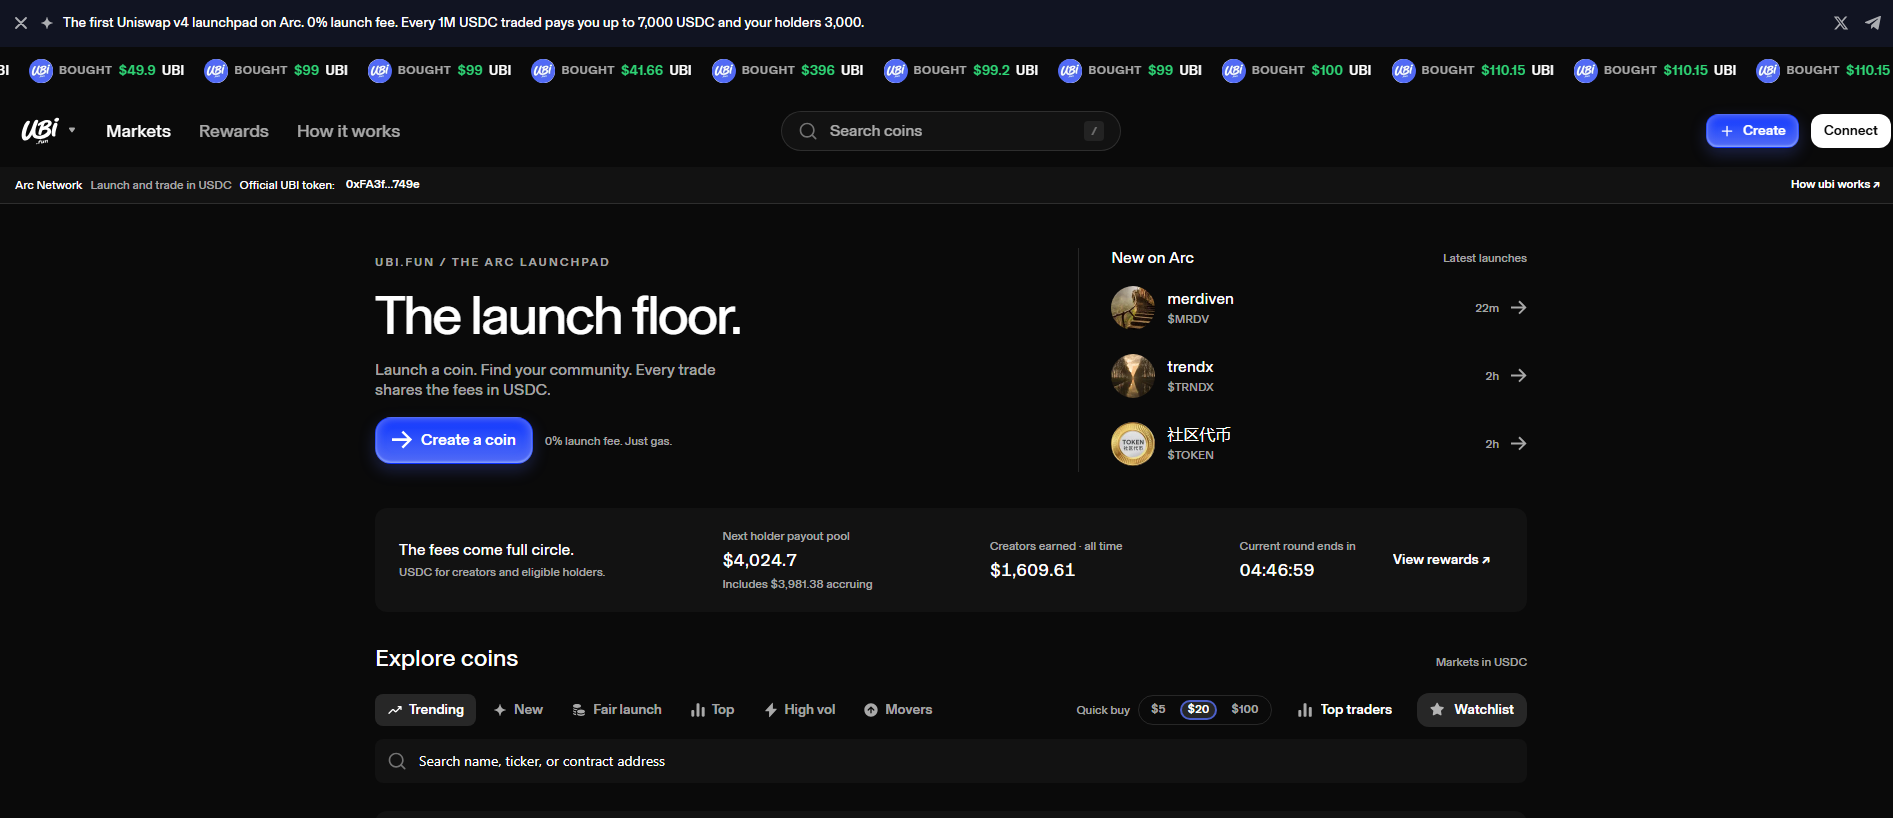
“ubi.fun — Launch & Trade Memecoins on Arc Network”

Registrador
Namecheap
Resolved IP
216.150.16.1
Registered
01/10/2025
Veredicto de amenaza Crítico
Disponibilidad Último activo conocido Última observación de accesibilidad almacenada Observado
Source: HTTP probe
VirusTotal detecciones: 4/92 Suplantación de marca: Morpho
OTX: 4 refs 27/09/2026 Morpho 1 Report Sent CDN
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 4. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@namecheap.com. The latest stored availability evidence still shows the domain reachable; 16 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
16 days
Reports sent
1
Latest case ID
PD-20260927-F6B698
Current status
HTTP 200 at latest stored check
Resumen del informe

ubi.fun — Último activo conocido (HTTP 200). Suplantación de marca: Morpho; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 4/92 (alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar); PhishDestroy score 81/100. Registrador: Namecheap.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

VirusTotal
VirusTotal
4 det.
OTX references
URLScan
URLScan
Certificado TLS
Caducado o no verificado
Edad
1 yr
Estado observado
Último activo conocido 200
PhishDestroy
DestroyList
Incluido
Reports Sent
1

Source evidence

7 sources

VirusTotal

4 / 92

Denunciar

URLQuery

Report stored; detailed verdict not recorded

Denunciar

OTX

4 community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

URLScan verdict

Análisis finalizado

Denunciar

Google Safe Browsing

Checked; no threat flag recorded

Denunciar

Resumen de las pruebas

Crítico
VirusTotal
4/92
OTX
4 community refs
URLScan
Stored capture

Assessment

On 2026-10-01, ubi.fun returned an HTTP status code of 200 according to the recorded HTTP check. This domain was first observed on 2026-09-27, providing a reference point for its earliest recorded activity.

Recorded Evidence

The HTTP check on 2026-10-01 recorded a 200 status code for ubi.fun. VirusTotal, checked on 2026-09-29, reported 1 detection out of 91 total scanners. OTX, checked on 2026-10-01, listed 4 pulses. The PhishDestroy internal listing includes ubi.fun. The PageSpeed performance score was 26 on 2026-09-27. The registration date is 2025-10-01 with registrar NAMECHEAP INC. The SSL certificate, scanned on 2026-09-28, was issued by Let's Encrypt / YR2.

Interpretation

The HTTP 200 response on 2026-10-01 documents only the status code at that specific time. VirusTotal, OTX, and the PhishDestroy internal listing each represent distinct types of source observations, reflecting different methods and timeframes. The PageSpeed score and the registration details provide additional context but do not indicate the domain's behavior or intent. These records allow for comparison of different source findings related to ubi.fun.

Recommended Actions

For ubi.fun, retain the PhishDestroy internal listing and OTX pulse records for future reference. Preserve the VirusTotal detection count and total scanners, as well as the HTTP status code, for ongoing monitoring. Comparing these records with future observations will help track any changes associated with ubi.fun. Keep each source record separate to maintain clarity in ongoing assessments.

Extracted from stored page analysis

Observed indicators

20 wallet · 1 Telegram

Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.

ETH
0x03e80455408be45fb1914d03930e4a70b2a44072Format validated · Domain analysis
ETH
0x05918e4f10066bfac916ae2e65065db462c765b2Format validated · Domain analysis
ETH
0x05aa8e26cd8aaad0d6e6d89140b2835466099085Format validated · Domain analysis
ETH
0x0a557450da027a9afa3e57ff032db5e41ebd9d15Format validated · Domain analysis
ETH
0x0cb08445aa266a73340930524812d603de2335dcFormat validated · Domain analysis
ETH
0x10339b4096b34f753297a653571cc1617279fc70Format validated · Domain analysis
ETH
0x1052086df36d74b343f7b0f805dcf9f3982ce444Format validated · Domain analysis
ETH
0x12a380e0729e7a0022688476c6f2ceb5ec9aef1cFormat validated · Domain analysis
ETH
0x12bf67e219e5634e16a8135f584ba9c6971b59b3Format validated · Domain analysis
ETH
0x138741bf5464d79fecdcee98df0692e6bc430bceFormat validated · Domain analysis
ETH
0x1809861da364e52af75a4f4faf63dfe6a599181aFormat validated · Domain analysis
ETH
0x18e1d0c27aeabdd7dd87585e648b0c36d15860a5Format validated · Domain analysis
ETH
0x1cc551998516b8af539293b3de544dc4a8463976Format validated · Domain analysis
ETH
0x202763ec0c5359e29e455af6256ac5055b945524Format validated · Domain analysis
ETH
0x203a540fd97829d2ef285e4f9ae223579cab30ebFormat validated · Domain analysis
ETH
0x20ec7caebb0907e5529be1fdd2dcf6add2159797Format validated · Domain analysis
ETH
0x22e8858961d29d8b26a510604e204ad68894a000Format validated · Domain analysis
ETH
0x2a1828be95c9735c251e960f82d6f23a4a83a390Format validated · Domain analysis
ETH
0x2a195c0ceb9629f0bc565c9d22c8cba92fb48989Format validated · Domain analysis
ETH
0x2abc82dfa7ffdfcff3be515d37fb00311a1e26a2Format validated · Domain analysis
Telegram
https://t.me/ubidotfunStored page reference

IoC extraction recorded 2026-09-28 04:00:10 UTC

Análisis de detección y evasión

Comprobación del enmascaramiento y la distribución del tráfico

Aún no se ha escaneado Aún no se ha registrado ninguna diferencia entre los rastreadores y los navegadores

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
Aún no se ha escaneado
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
Vercel

Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel

Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 captures

Título de la página
ubi.fun — Launch & Trade Memecoins on Arc Network
Impersonates
Morpho Spark Uniswap
Certificado TLS
Hostname coverage not recorded · Emitido por Let's Encrypt / YR2 · stored validity ends in 66 days

Domain details

Dominio
URLScan Verdict Análisis finalizado score 0 report ↗
IP Context Vercel shared edge origin IP hidden La reputación de Edge-IP no se atribuye a este dominio.
OTX Tags 2026-09activeall-domainsblocklistcontentcryptodominiosdrainerfraudlivemonthlyphishdestroyphishingscam
Registrador Namecheap US(US)
Registro de la ICANNICANN Lookup (RDAP) →
RegistroCreado 01/10/2025 — Expires 01/10/2026
Estado HTTP200
Detalles técnicosProvenance & timestamps
Primera detección27/09/2026
DOM Analysisanalyzed 09/10/2026score 81/1003 brand signals
IoC Extractionscanned 28/09/202620 wallet · 1 Telegram IoCs
Submitted URLhttps://ubi.fun/
Favicon Hash
ID del caso
ICANN OVERSIGHT

Acreditación y contexto RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft No se envía nada automáticamente.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
216.150.16.1
Network ASN
AS16509
Organization
Vercel, Inc
Observed location
Walnut, US
Server header
Vercel

La reputación de Edge-IP no se atribuye a este dominio.

Servidores de nombres 2

  • ray.ns.cloudflare.com
  • vera.ns.cloudflare.com

Mail routing 3 MX records

  • route3.mx.cloudflare.netpriority 30
  • route1.mx.cloudflare.netpriority 90
  • route2.mx.cloudflare.netpriority 93

Location describes the IP network.

Certificado TLS

Issuer
Let's Encrypt / YR2
Valid from
2026-09-20 14:15:41
Valid until
2026-12-19 14:15:40
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 07:02:08 UTC
Collection source
PhishDestroy collector
Certificate fingerprint0b6f779c1631deae346854aa2923774aec2179d376cb6e68fd302380abac8075

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 216.150.16.1rapiddns.io

Latest Classified Outcome 2026-10-13 22:09:01 UTC

Primary outcome Contenido activo reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Contenido activo Ordinary HTTP content served 90% 2026-10-13 22:09:01 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-10-13 22:29:35 UTC last content: 2026-10-13 22:09:01 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Cruce de inteligencia de amenazas · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Tecnologías · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

4 / Los proveedores de seguridad de 92 marcaron este dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 4 detections
alphaMountain.ai
Forcepoint ThreatSeeker
Gridinsoft
SOCRadar

Evidencias archivadas

Wayback Machine Snapshot
Una instantánea histórica está disponible para revisión de evidencia.
View Archive
Análisis del rendimiento del sitio

Google PageSpeed Insights — mobile performance audit of ubi.fun · checked Sep 27, 2026

26
Poor
Performance
FCP
10.52s
First Contentful Paint
LCP
13.89s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
3943ms
Total Blocking Time
SI
10.68s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-09-30 08:06:00 UTC
    VirusTotal scanner detections updated from 3 to 1. Resolved alerts: Forcepoint ThreatSeeker, alphaMountain.ai.
  2. VirusTotal Detections Update 2026-09-29 09:40:11 UTC
    VirusTotal scanner detections updated from 2 to 3. Added scanner alerts: Forcepoint ThreatSeeker.
  3. VirusTotal Detections Update 2026-09-28 12:12:48 UTC
    VirusTotal scanner detections updated from 1 to 2. Added scanner alerts: alphaMountain.ai.
  4. VirusTotal Detections Update 2026-09-27 22:21:09 UTC
    VirusTotal scanner detections updated from 0 to 1. Added scanner alerts: SOCRadar.
  5. Threat First Observed 2026-09-27 19:13:05 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 216.150.16.1.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Notifications
Monitoring

15 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
ubi.fun detectados y puestos en cola para su análisis completo
27/09/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
27/09/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
30/09/2026
VirusTotal
4/92 recorded on VirusTotal
10/10/2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
01/10/2026
Brand Impersonation
Impersonation of Morpho
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
27/09/2026
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
14/10/2026
VT Detection -2
2 detections removed (3 → 1)
30/09/2026
VT Detection +1
+1 new detection (2 → 3): Forcepoint ThreatSeeker
29/09/2026
VT Detection +1
+1 new detection (1 → 2): alphaMountain.ai
28/09/2026
VT Detection +1
+1 new detection (0 → 1): SOCRadar
28/09/2026
Sent Report Recorded
Stored outgoing record associated with registrar NAMECHEAP INC, 2 abuse contacts
abuse@namecheap.comabuse@vercel.com
27/09/2026
Lista de destrucción publicada
27/09/2026
Monitoring Continues
El dominio sigue siendo accesible o tiene acceso restringido; controles futuros pueden actualizar esta observación.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260927-F6B698 Recipient: abuse@namecheap.com
Page title stored with report: ubi.fun — Launch & Trade Memecoins on Arc Network
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 125.3 KB
PDF notice generated Notice text archived (289 chars)
Abuse notice text as sent to the provider
Registrar: Namecheap Inc (United States)
Policy Violations: Domain Registration Agreement prohibits hacking, misuse of domain to conduct attacks, scam and fraudulent activities; AUP allows immediate suspension
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Análisis en profundidad

¿Te ha afectado esta página web?

6 evidence signal groups linked 1 reports recorded Último activo conocido
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.

Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/ubi.fun"
  title="PhishDestroy threat report for ubi.fun"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>