Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
find-helpcenter.com favicon

find-helpcenter.com

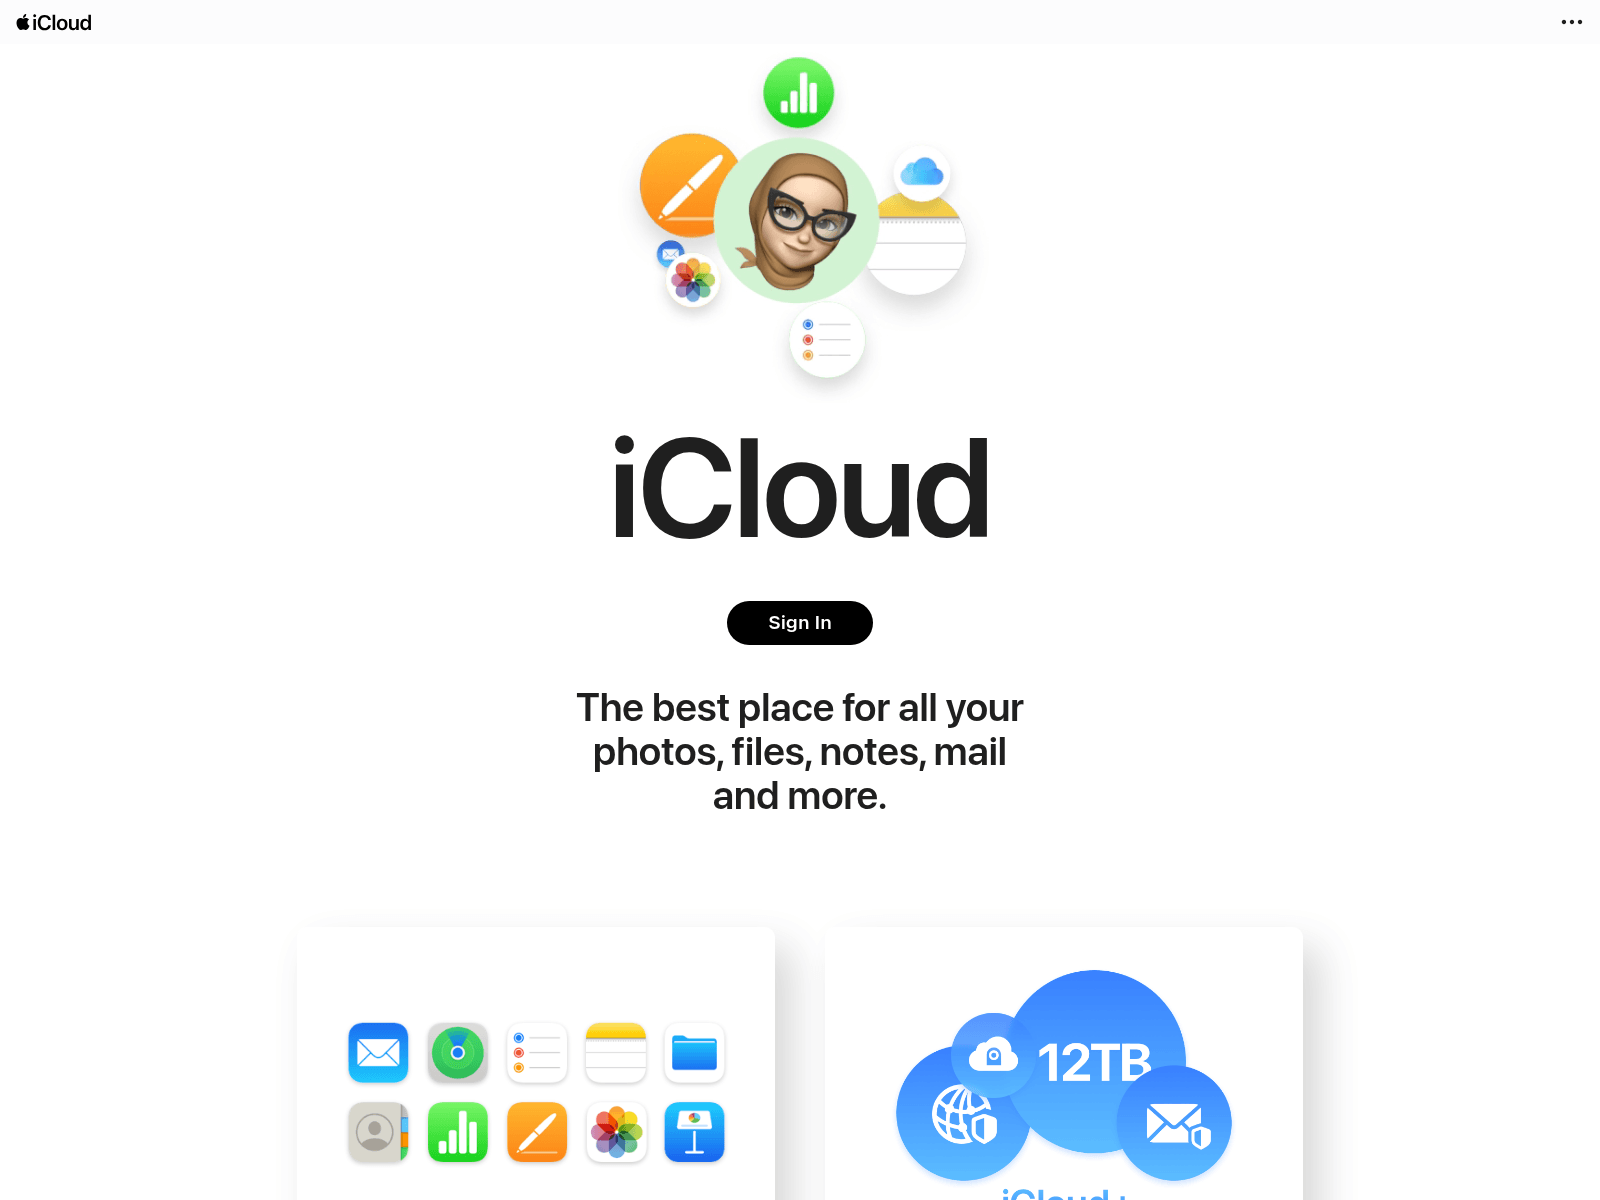
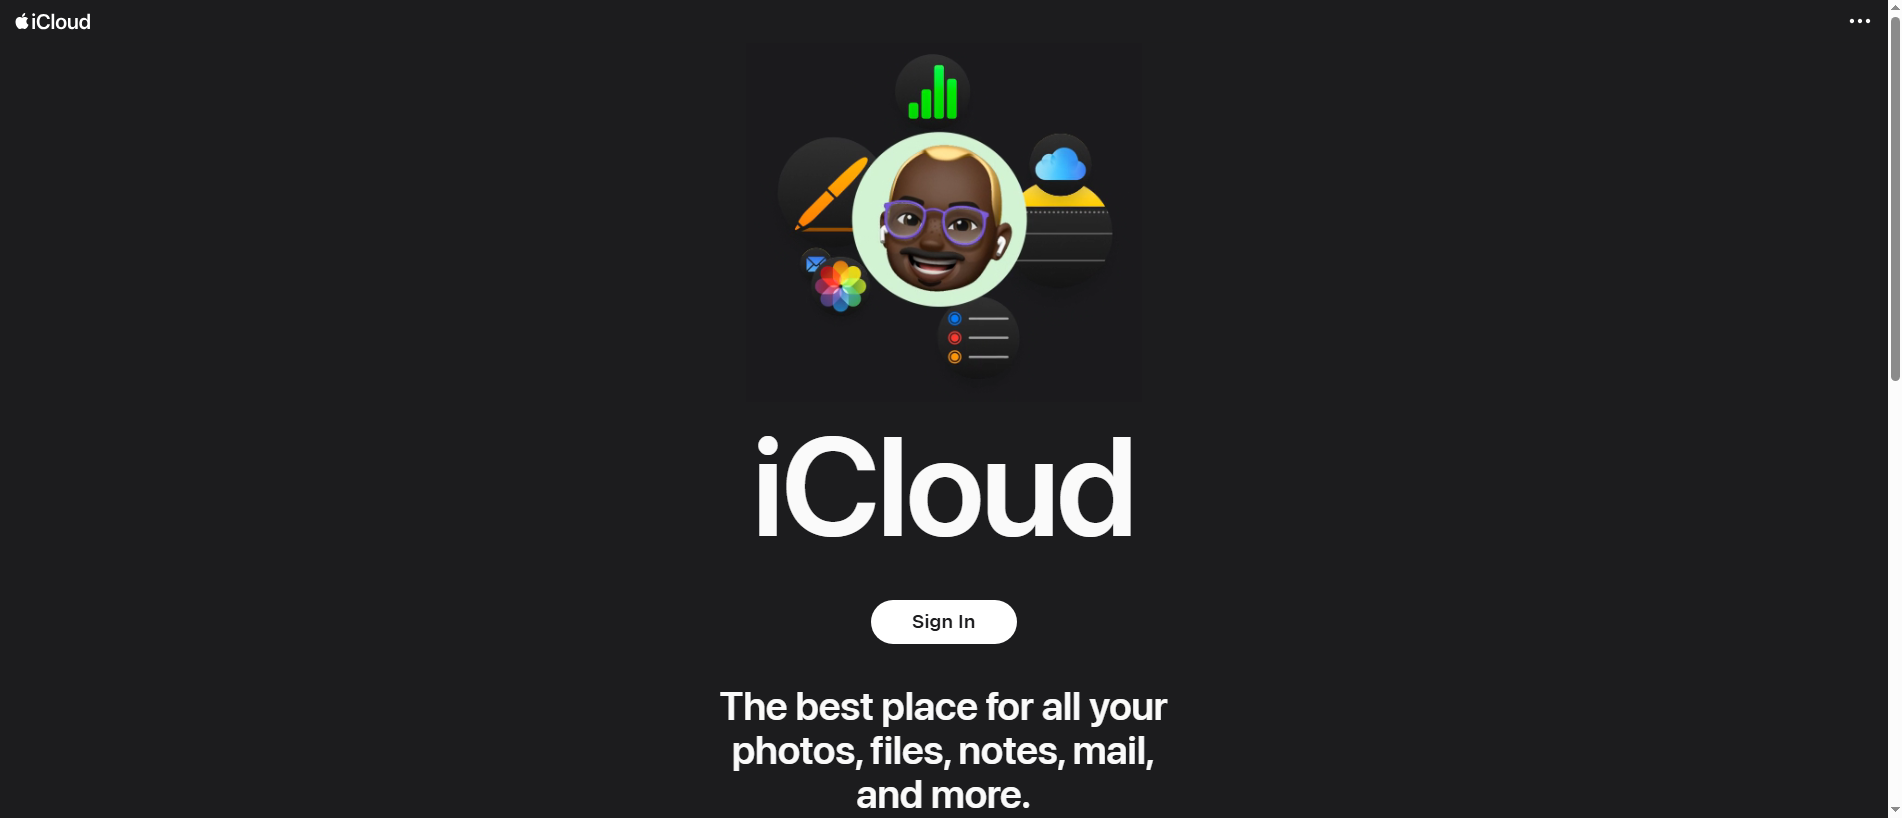
“iCloud”

Registrador
Spaceship
Resolved IP
172.67.223.246
Registered
06/09/2026
Veredicto de amenaza Crítico
Disponibilidad Contenido no disponible El contenido no estaba disponible en la última observación.
VirusTotal detecciones: 12/89 Suplantación de marca: Apple
OTX: 4 refs 07/09/2026 Apple 1 Report Sent CDN
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 12. Tenga extrema precaución: no ingrese credenciales o información personal.
Resumen del informe

find-helpcenter.com — Contenido no disponible (HTTP 404). Suplantación de marca: Apple; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 12/89 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); PhishDestroy score 100/100. Registrador: Spaceship.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

VirusTotal
VirusTotal
12 det.
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
Certificado TLS
Caducado o no verificado
Edad
1 mo New
Estado observado
Contenido no disponible 404
PhishDestroy
DestroyList
Incluido
Reports Sent
1

Source evidence

8 sources

VirusTotal

12 / 89

Denunciar

URLQuery

checked — no detections recorded

Denunciar

OTX

4 community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

URLScan verdict

Análisis finalizado

Denunciar

Google Safe Browsing

Checked; no threat flag recorded

Denunciar

Resumen de las pruebas

Crítico
VirusTotal
12/89
OTX
4 community refs
URLScan
Stored capture

Assessment

The domain find-helpcenter.com returned an HTTP 404 status code on 2026-10-01, indicating that no web page was available at that time. Additionally, this domain was first observed on 2026-09-07, suggesting it is relatively new.

Recorded Evidence

On 2026-09-18, VirusTotal reported 12 detections out of 89 scanners for find-helpcenter.com. The domain was added to the PhishDestroy internal listing as of 2026-09-07. OTX included find-helpcenter.com in four pulses by 2026-09-11. The SSL certificate, issued by Google Trust Services / WE1, was scanned on 2026-09-07.

Interpretation

The sources provide a timeline of observations, with VirusTotal, OTX, and PhishDestroy offering different perspectives on the domain's status over several weeks. The HTTP 404 status observed on 2026-10-01 does not necessarily reflect the domain's state during earlier security scans or listings. Comparing these dates helps identify changes in accessibility and security perceptions over time.

Recommended Actions

Retain all evidence related to find-helpcenter.com for future reference and to monitor any changes in its status. When reviewing subsequent observations, compare them to these dated records for context. Avoid submitting sensitive information to find-helpcenter.com while its security and accessibility remain under review.

Análisis de detección y evasión

Comprobación del enmascaramiento y la distribución del tráfico

Aún no se ha escaneado Aún no se ha registrado ninguna diferencia entre los rastreadores y los navegadores

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
Aún no se ha escaneado
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
cloudflare

Nota del escáner: dead_http: raw=http_404; http=404; via=https_proxy; server=cloudflare

Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 captures

Domain details

Dominio
URLScan Verdict Análisis finalizado score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden La reputación de Edge-IP no se atribuye a este dominio.
OTX Tags 2026-09activeall-domainsblocklistcontentcryptodominiosdrainerfraudlivemonthlyphishdestroyphishingscam
Registrador Spaceship (Unknown)
Contacto de abusoabuse@spaceship.com
Registro de la ICANNICANN Lookup (RDAP) →
RegistroCreado 06/09/2026 (32d · New) — Expires 06/09/2027
Estado HTTP404 Not Found
Tiempo hasta la primera indisponibilidad 22 days
Qué contabilizamos Tiempo transcurrido desde el primer informe de abuso almacenado hasta la primera observación de que el contenido no estaba disponible. Esto no establece la causa.
Qué contiene cada informe Los registros de informes salientes almacenados pueden hacer referencia a evidencia disponible en ese momento, como veredictos de proveedores, datos de registro, detalles de alojamiento, clasificaciones o capturas de pantalla. Esta página no infiere la carga útil entregada, el recibo, el acuse de recibo o la acción exacta por parte de un destinatario.
Detalles técnicosProvenance & timestamps
Primera detección07/09/2026
DOM Analysisanalyzed 07/09/2026score 100/1002 brand signals
Submitted URLhttp://find-helpcenter.com/750e0
Favicon Hash
ID del caso
Título de la página
iCloud
Impersonates
Apple Icloud
Certificado TLS
Hostname coverage not recorded · Emitido por Google Trust Services · stored validity ends in 87 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
172.67.223.246
Network ASN
AS16625
Organization
AS13335 Cloudflare, Inc.
Observed location
San Francisco, US
Server header
AppleHttpServer/cff317772116

La reputación de Edge-IP no se atribuye a este dominio.

Servidores de nombres 2

  • cheryl.ns.cloudflare.com
  • finley.ns.cloudflare.com

Location describes the IP network.

Certificado TLS

Issuer
Google Trust Services
Valid from
2026-09-06 02:22:41
Valid until
2026-12-05 03:20:23
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-09-07 01:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprint054ceb792487418c7fc0fef2a034ac2e2b2a088d3c97f63d71f589671486e790

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 172.67.223.246rapiddns.io

Latest Classified Outcome 2026-10-07 02:11:30 UTC

Primary outcome Desconocido reason: Stale Current Evidence 0% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unknown Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Inactivo Http No Content 70% 2026-10-07 02:11:30 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-09-29 01:54:58 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Tecnologías · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

12 / Los proveedores de seguridad de 89 marcaron este dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 6 detections
alphaMountain.ai
BitDefender
CRDF
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SOCRadar
Sophos
Webroot
Análisis del rendimiento del sitio

Google PageSpeed Insights — mobile performance audit of find-helpcenter.com · checked Sep 7, 2026

60
Needs Work
Performance
FCP
2.07s
First Contentful Paint
LCP
15.57s
Largest Contentful Paint
CLS
0.007
Cumulative Layout Shift
TBT
511ms
Total Blocking Time
SI
3.06s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-09-29 10:24:27 UTC
    Domain state transitioned from alive to dead.
  2. VirusTotal Detections Update 2026-09-07 04:43:35 UTC
    VirusTotal scanner detections updated from 5 to 6. Added scanner alerts: SOCRadar.
  3. VirusTotal Detections Update 2026-09-07 03:09:56 UTC
    VirusTotal scanner detections updated from 4 to 5. Added scanner alerts: alphaMountain.ai.
  4. VirusTotal Detections Update 2026-09-07 02:08:08 UTC
    VirusTotal scanner detections updated from 2 to 4. Added scanner alerts: CRDF, Gridinsoft.
  5. Threat First Observed 2026-09-07 00:33:48 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 172.67.223.246.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Notifications
Monitoring

16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
find-helpcenter.com detectados y puestos en cola para su análisis completo
07/09/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
07/09/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
12/89 recorded on VirusTotal
18/09/2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
11/09/2026
Brand Impersonation
Impersonation of Apple
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
07/09/2026
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
08/10/2026
Content Observed Unavailable
El monitoreo registró una respuesta no disponible (HTTP 404); la causa no se estableció de forma independiente.
29/09/2026
VT Detection +1
+1 new detection (5 → 6): SOCRadar
07/09/2026
VT Detection +1
+1 new detection (4 → 5): alphaMountain.ai
07/09/2026
VT Detection +2
+2 new detections (2 → 4): CRDF, Gridinsoft
07/09/2026
Sent Report Recorded
Stored outgoing record associated with registrar Spaceship, Inc., 1 abuse contact
abuse@spaceship.com
07/09/2026
Lista de destrucción publicada
07/09/2026
Content Observed Unavailable
Las últimas comprobaciones almacenadas indican que el contenido informado no está disponible; esto no establece quién o qué causó el cambio.
29/09/2026
Tiempo hasta la primera indisponibilidad
537 horas transcurrieron desde la detección hasta la primera observación no disponible.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260907-4F328B Recipient: abuse@spaceship.com
Page title stored with report: iCloud
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 124.9 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Análisis en profundidad

¿Te ha afectado esta página web?

7 evidence signal groups linked 1 reports recorded Contenido no disponible
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.


Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/find-helpcenter.com"
  title="PhishDestroy threat report for find-helpcenter.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>