VirusTotal
11 / 92 engine detections
Abrir informe

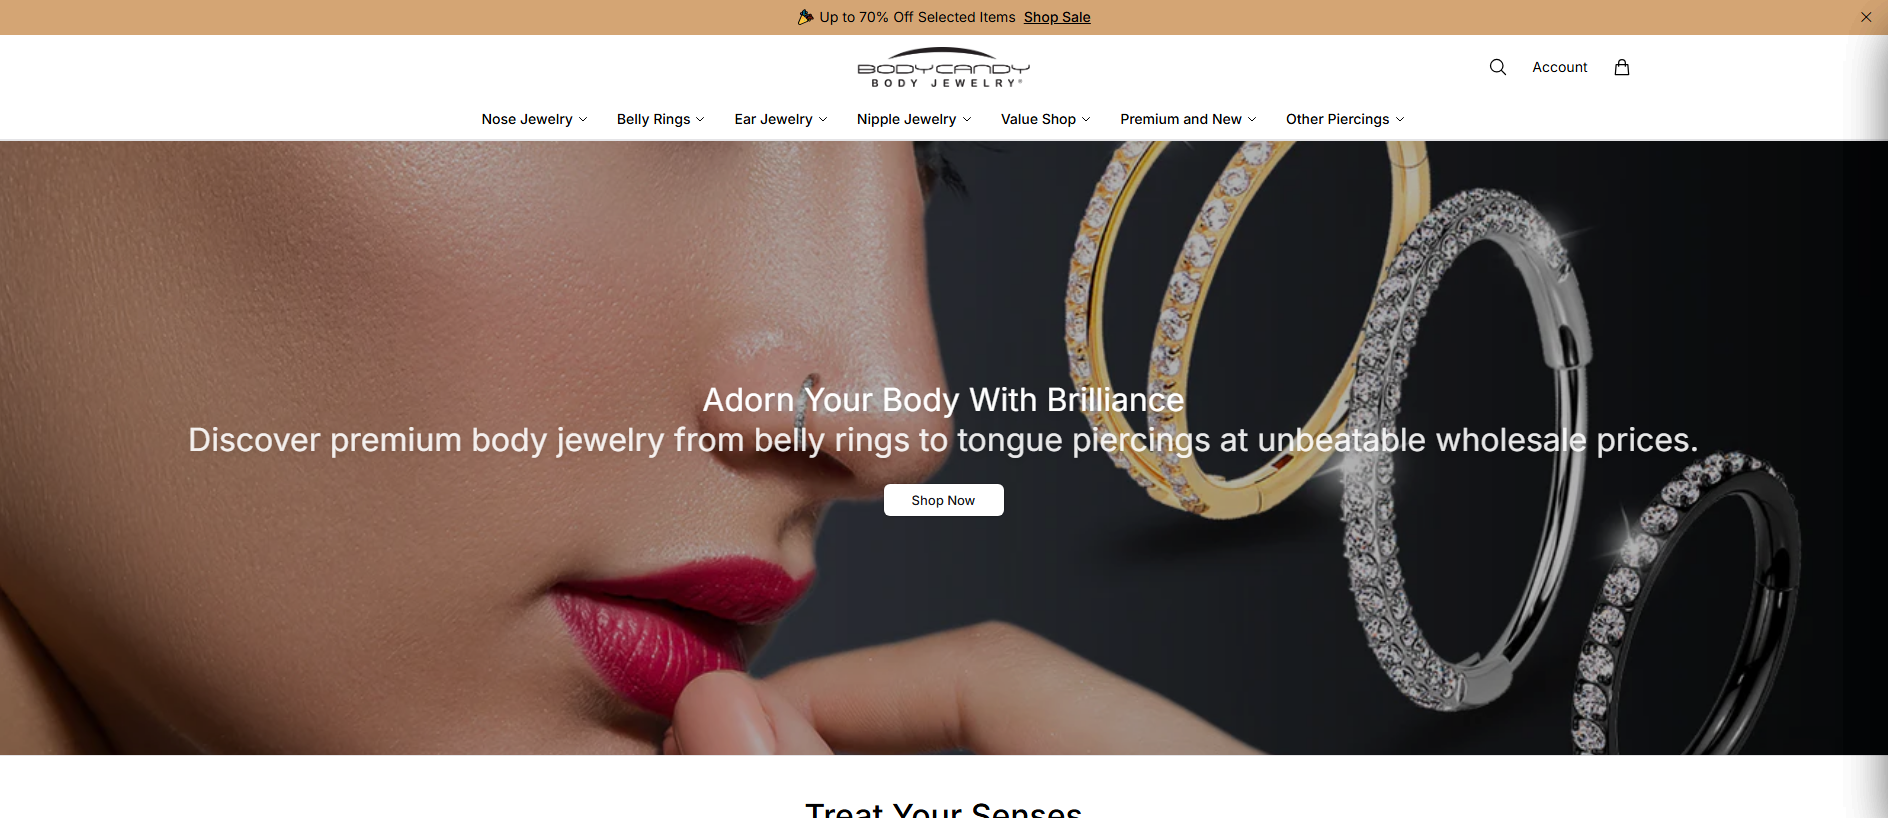
“Body Jewelry, belly button rings, body piercing jewelry, nose rings | Body Candy”
Phishing: bodycandyhub.shop — Último activo conocido (HTTP 200). Resumen de las pruebas: VirusTotal 11/92 (alphaMountain.ai, BitDefender, CRDF, CyRadar…
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
11 / 92 engine detections
Abrir informe2 det.
Abrir informe4 community references
Abrir informeprovider verdict: clean
Abrir informeNo threat flag
Abrir informePage capture
Abrir informeResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
PhishDestroy has listed bodycandyhub.shop on its internal blocklist as a suspicious domain. The site’s recorded title reads “Body Jewelry, belly button rings, body piercing jewelry, nose rings | Body Candy”. The domain was first observed by PhishDestroy on 2026-10-20.
Because the domain is only flagged as suspicious, no concrete malicious behavior has been observed. The presence of multiple antivirus detections suggests the site may host or distribute unwanted or malicious content, but the exact technique—such as phishing, malware delivery, or fraud—cannot be confirmed from the available data. Visitors should treat any request for personal or financial information with caution.
VirusTotal scanned the domain on 2026-10-15 and reported 11 detections out of 92 engines, with vendors such as BitDefender, ESET and G‑Data flagging it. Google Safe Browsing checked on 2026-10-20 and did not flag the URL. No external public blocklists listed the domain as of 2026-10-20, while PhishDestroy’s internal list marked it as suspicious on the same day. OTX recorded four pulses referencing the domain on 2026-10-20.
The recorded IP address for bodycandyhub.shop is 91.246.50.210. No registrar, CDN or certificate information is provided, and the listing does not identify the operator.
If you visited the site and entered credentials, change those passwords immediately and monitor accounts for unauthorized activity. Do not download files or grant any permissions from the site; if you did, run a reputable anti‑malware scan. Security teams should add bodycandyhub.shop to their deny lists and monitor network logs for connections to 91.246.50.210.
piers.ns.cloudflare.comtara.ns.cloudflare.comLocation describes the IP network.
b80ef313c9f411d54aebdd7dd47d9760eeb35d3d9a8564f13878213cbcef014fSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of bodycandyhub.shop · checked Oct 20, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://bodycandyhub.shop/https://bodycandyhub.shop/Cache-Control: private, no-cache, no-store, max-age=0, must-revalidateContent-Encoding: gzipContent-Type: text/html; charset=utf-8summary_large_imageh3=":443"; ma=2592000private, no-cache, no-store, max-age=0, must-revalidategziptext/html; charset=utf-8Tue, 20 Oct 2026 19:36:27 GMT; rel=preload; as="style"strict-origin-when-cross-originchunkedRSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding1.1 CaddynosniffSAMEORIGIN1; mode=blockValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Accesible
4 community references
View sourceNo threat flag
View source11/92 engine detections
View sourcePD-20261020-C23434
bodycandyhub.shop
View sourcePage captured
View sourceCada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
bodycandyhub.shop
PD-20261020-C23434 Recipient: abuse@rashost.com Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
bodycandyhub.shop)Aunque no tengas todos los detalles — presenta la denuncia de todos modos. Incluso la información parcial sigue siendo útil para las investigaciones.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.