
Busca dominios supervisados y revisa las pruebas almacenadas, las detecciones y la última disponibilidad observada.
221,184
Total registrado
215,380
Se ha detectado VT
93,439
Última conexión: activo
127,745
No disponible en la última comprobación
6
VT Pendiente
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,752 domains tracked for this threat type
Solana Drainer 2,752 domains

new.lunalaunch.live

padrecheck.fun

padrepump.fun

penguinsgive.com

phantom--wallet-docs.pages.dev

phantom--wallet-en.pages.dev

phantom-crypto-hub.com

phantom-my.com
phantom-phi.vercel.app

phantom-web-ios.framer.media
phantom.sdnaa.com

phantomextension.app

phantomgame339.top

phantomgift.bond
phantomwall.exchange

phantomwallet-io.pages.dev

q111.solcenter.cc

raydium-provision.world

rectifywallet.click

refundyoursol.world

rhino.rest

sol-good.pro

sol-incineratr.com
sol-phantom.com

sol-reward.digital

sol-rewards.digital

sol-wheel.cc
solana-chain-mainnet.pages.dev

solana-mixer.com
solana-money-glitch.ai-cryptolist.net

solanadapp-cth.pages.dev
solanaislife.co
solanamixer.top
solanasniper.sol-galaxy.cc

solclaim.cloud
solflare.app

solrefixcredit.world

spin.solgalaxy.cc
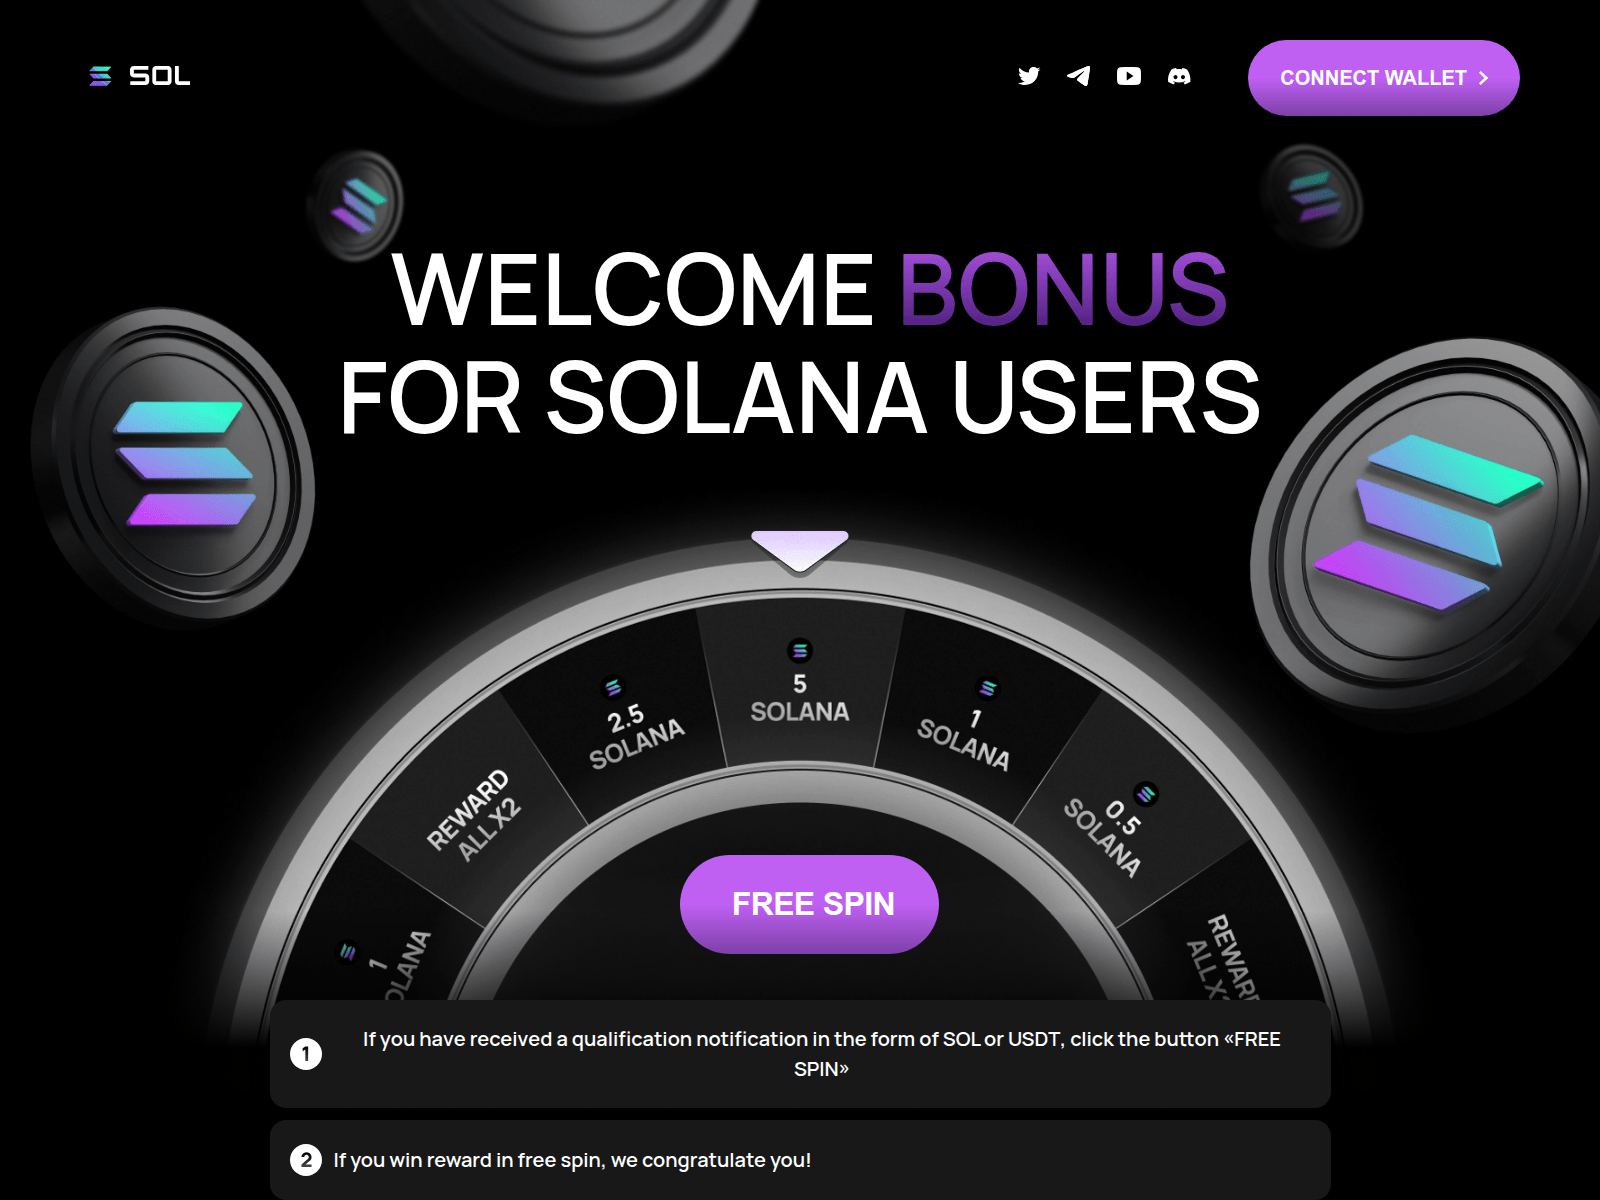
spinsolana.click

swiftsoldapp.live
the-dogefather-solana.ai-cryptolist.org
thunderbloom-phantom.com
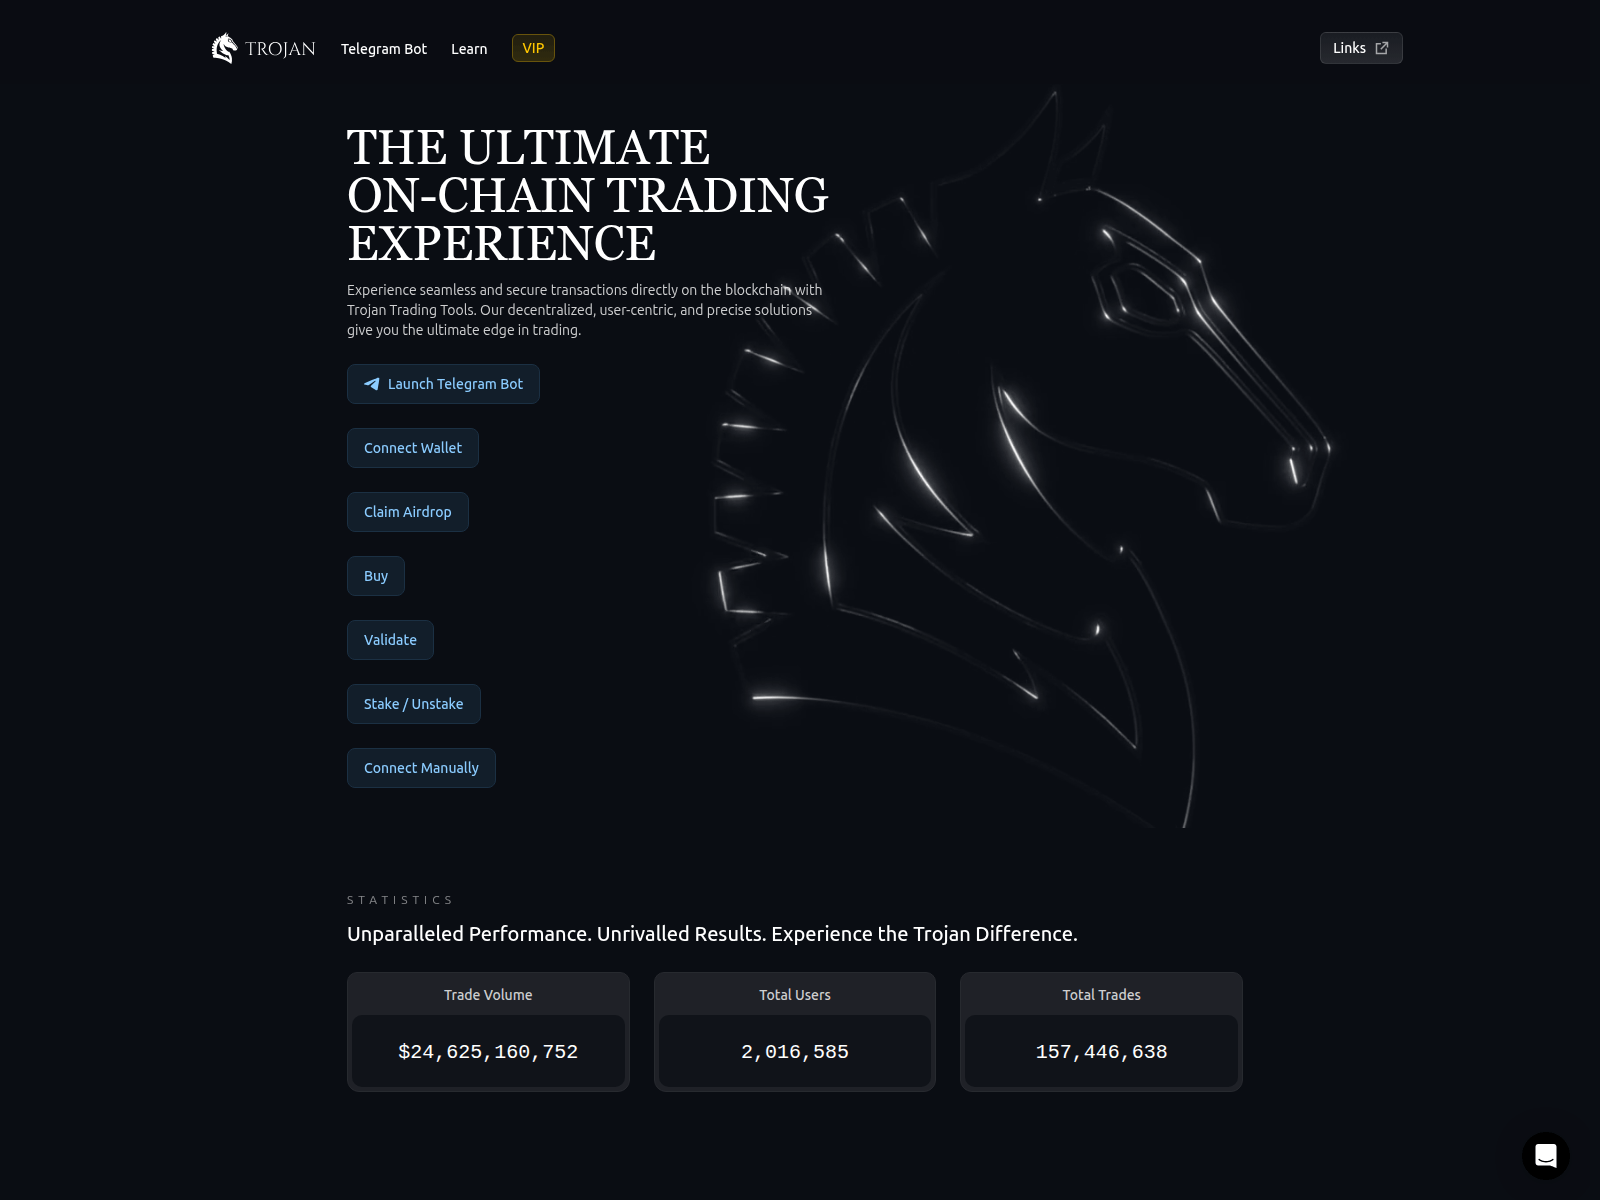
trojanonsolana.live
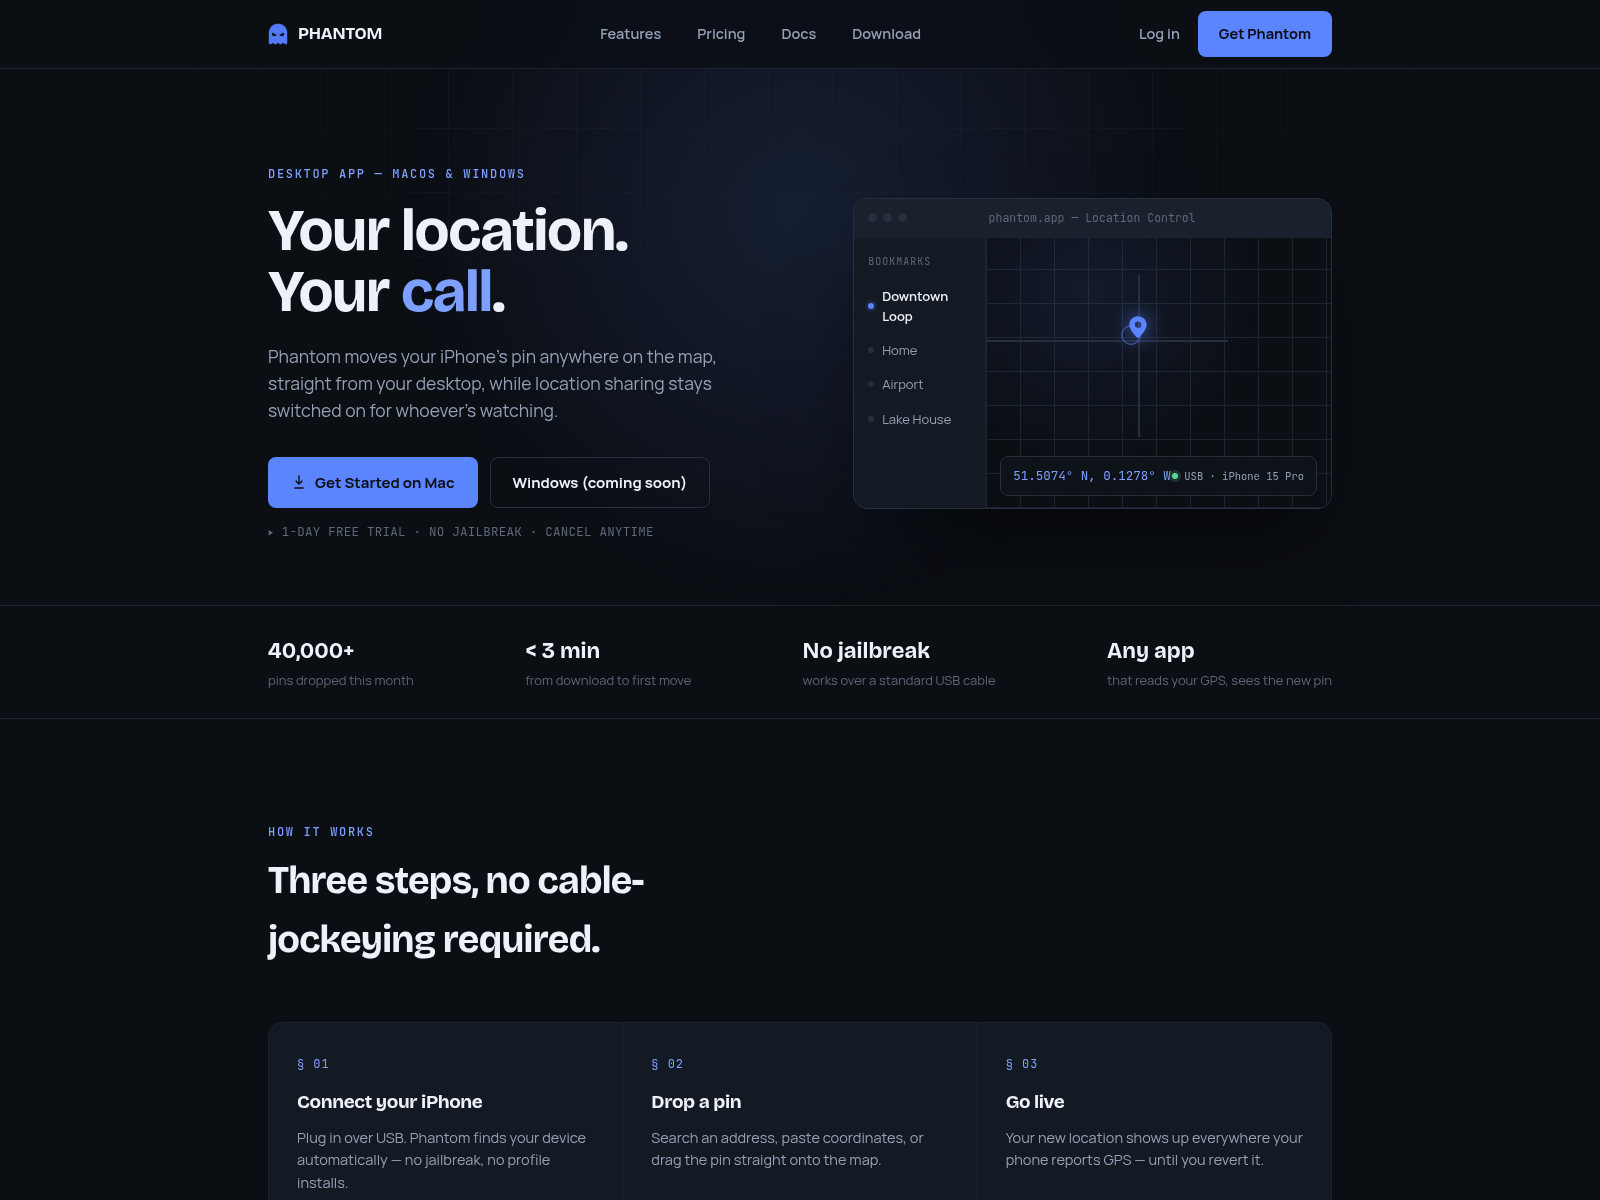
tryphantom.xyz

vaultbenefits.net

wallet-phantom-en.pages.dev
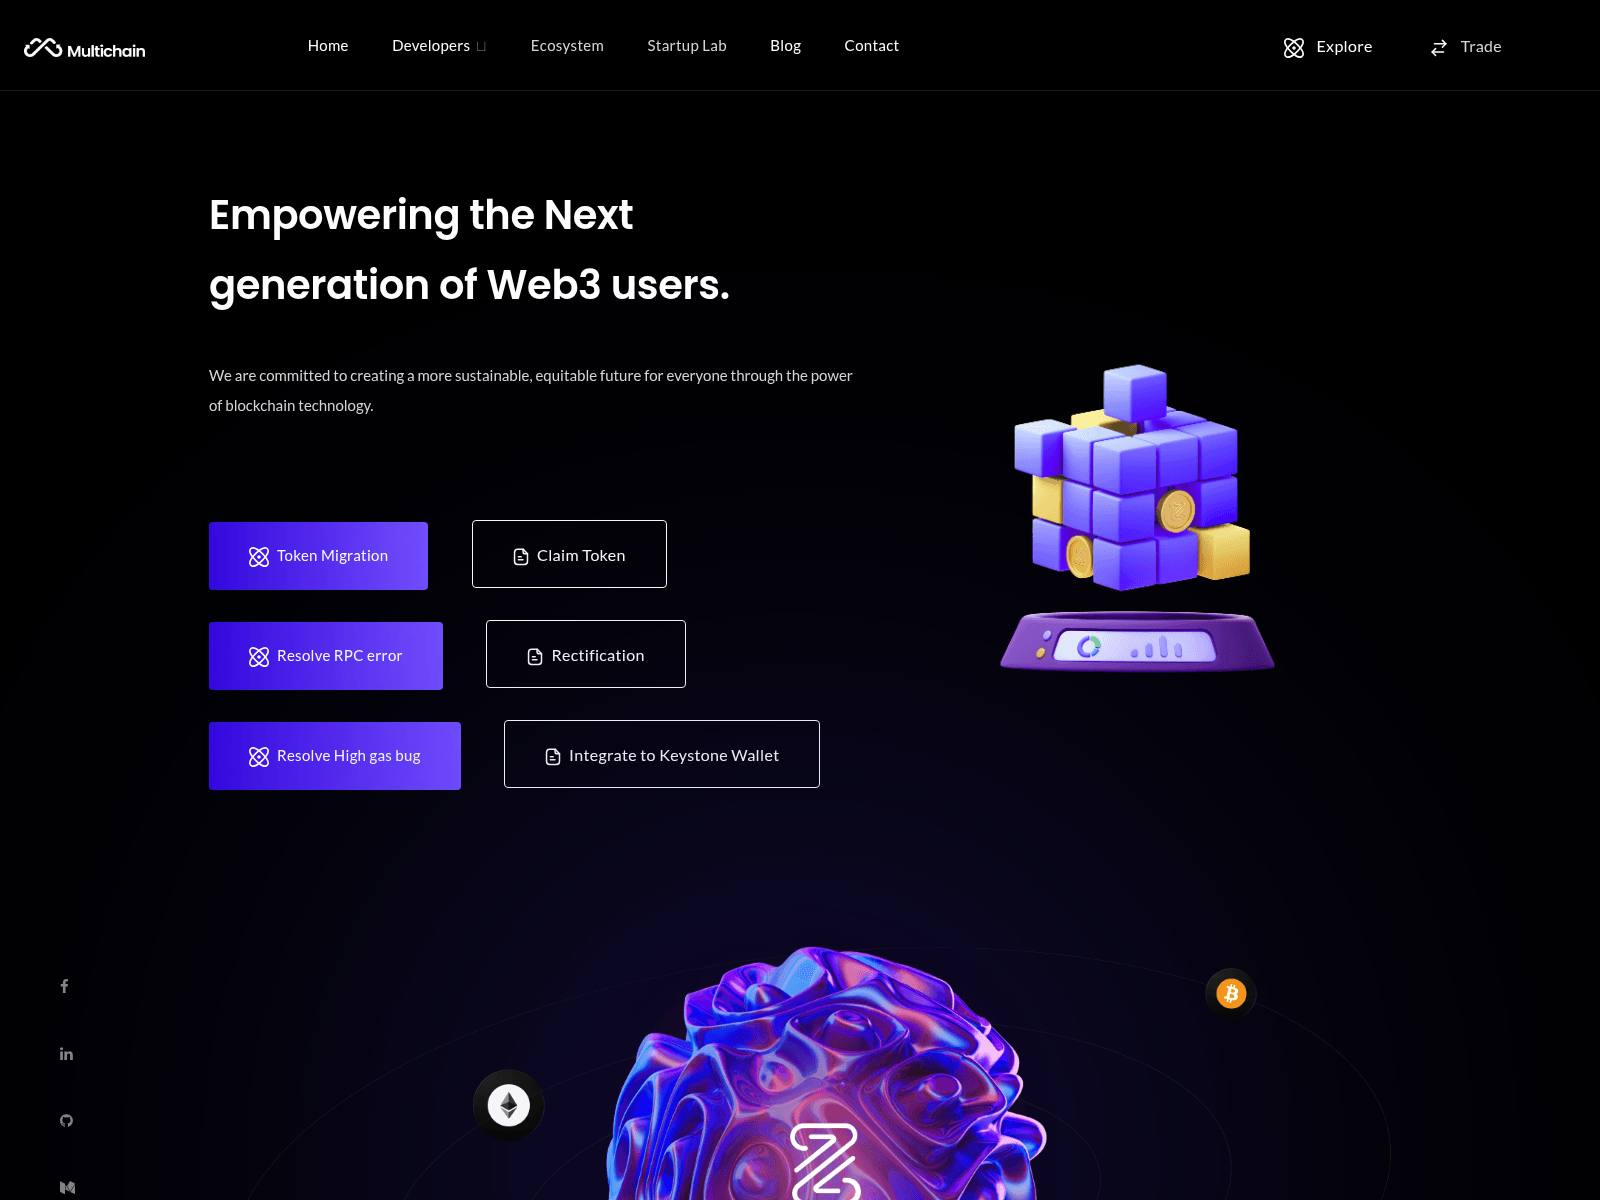
walletappsync.firebaseapp.com
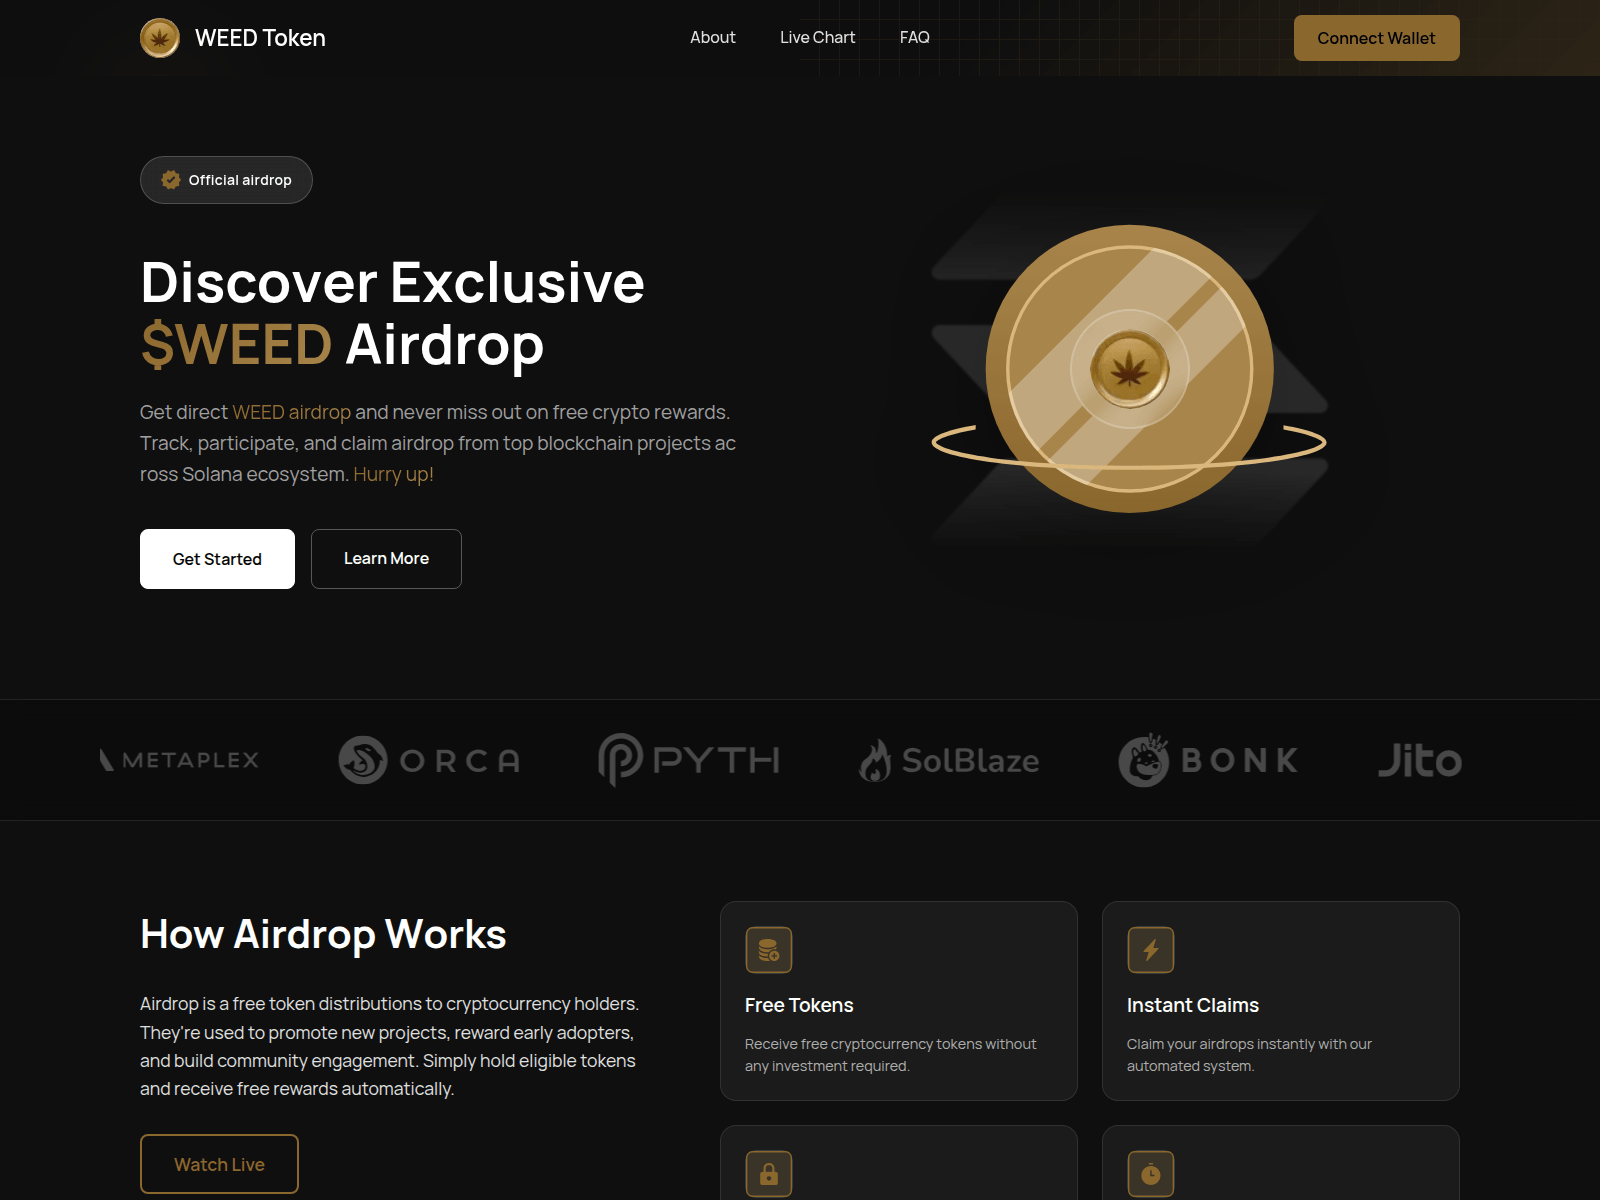
weedclaim.sol-galaxy.cc
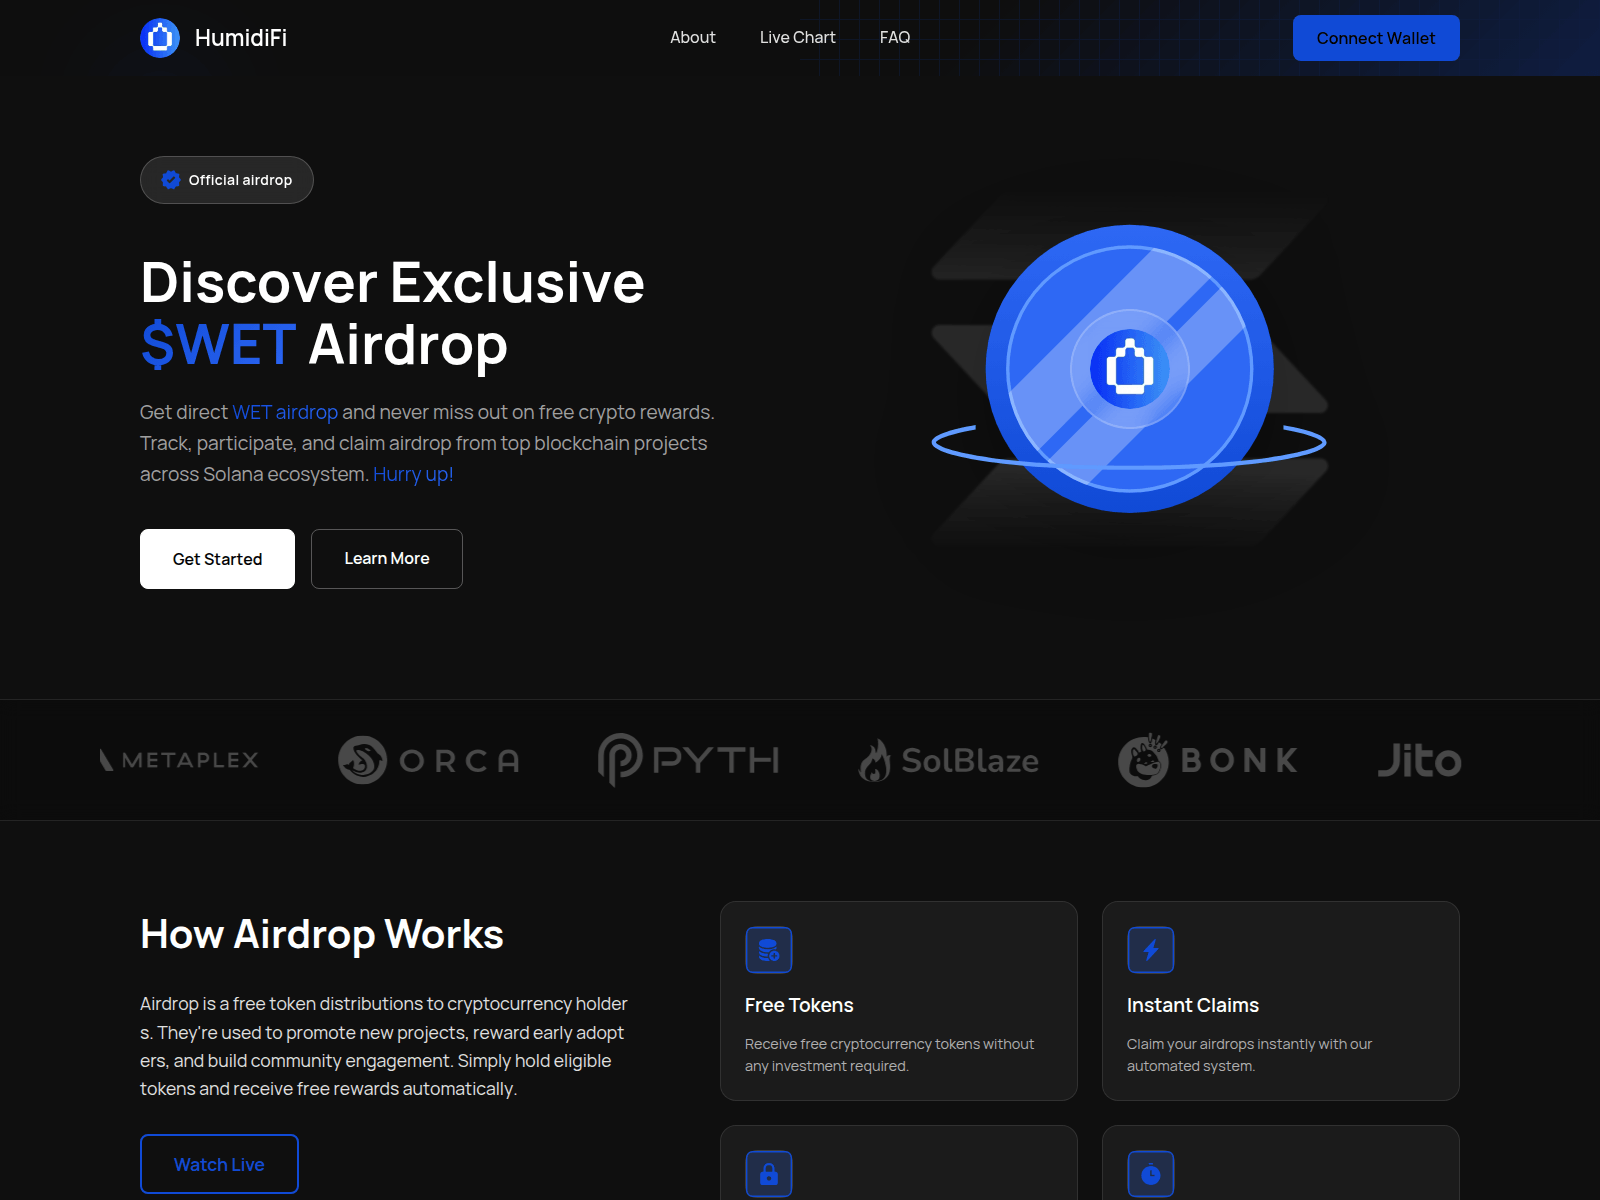
wet.solhost.cc

wlficoin.top

ybhww.cc

32113.one

38010.lgbt

84563.club
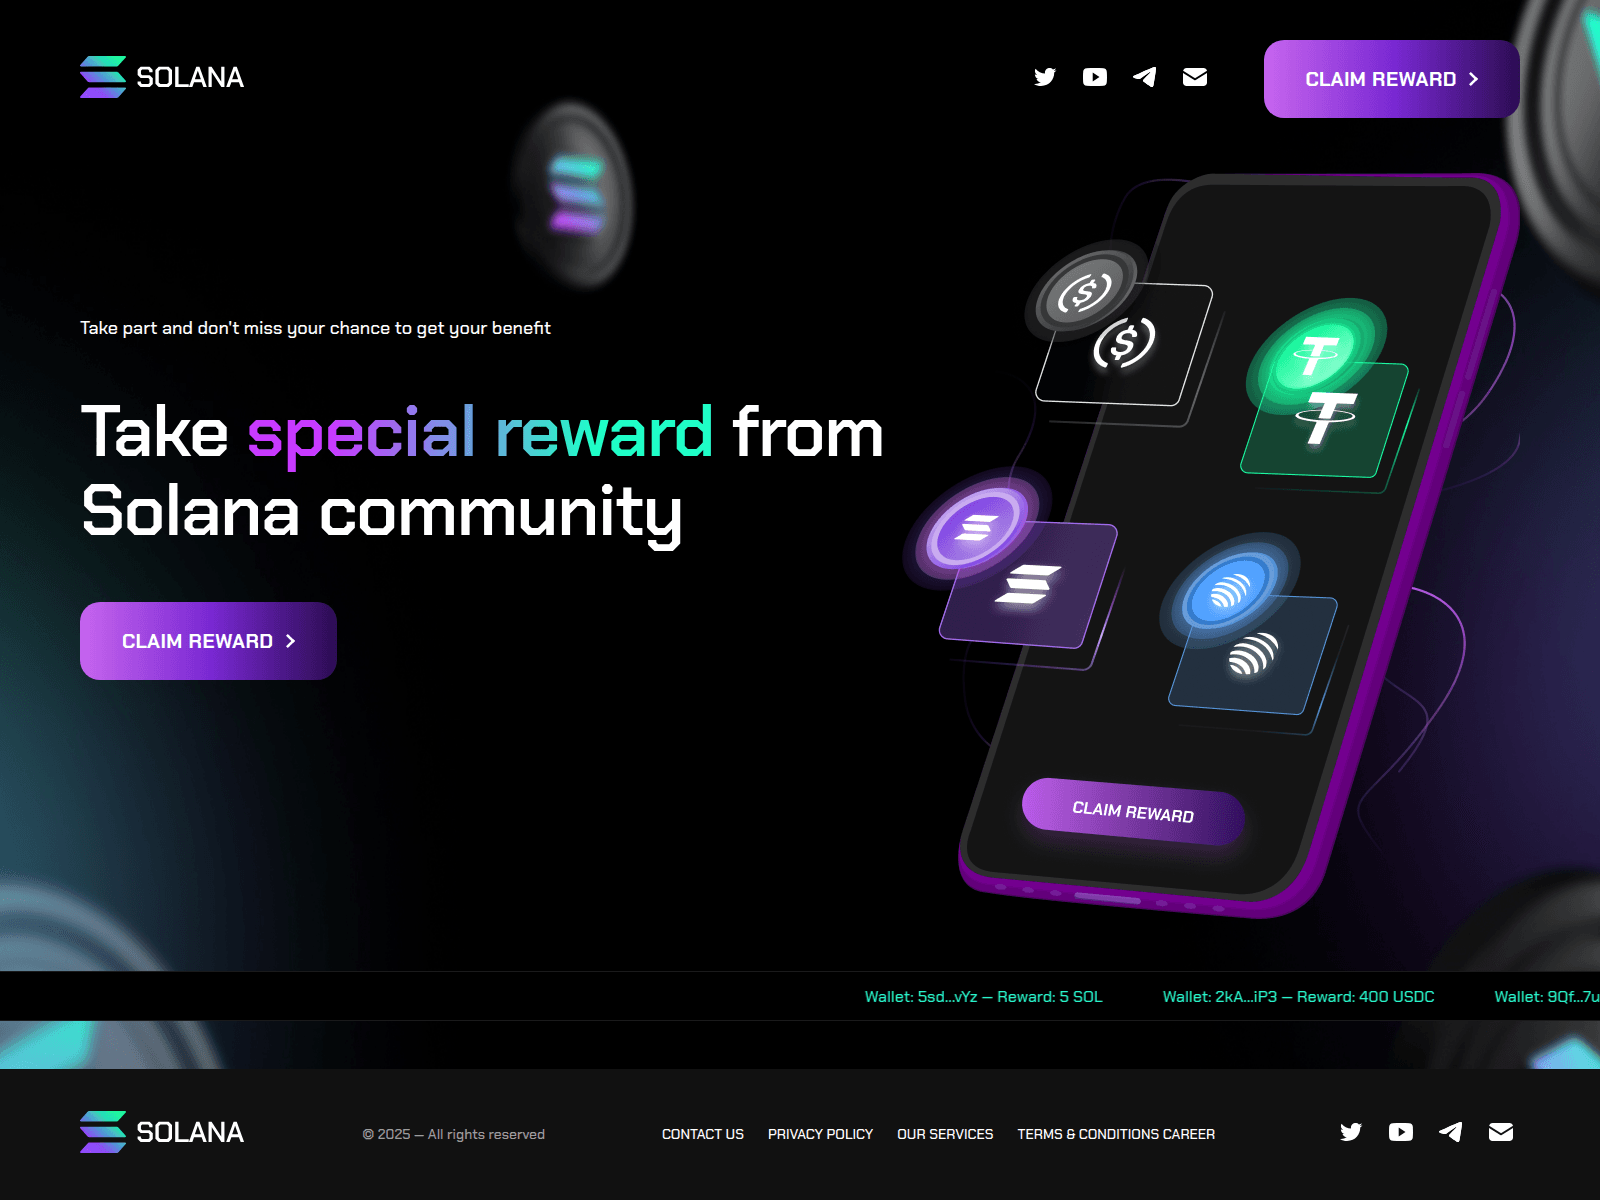
air.sol-world.cc
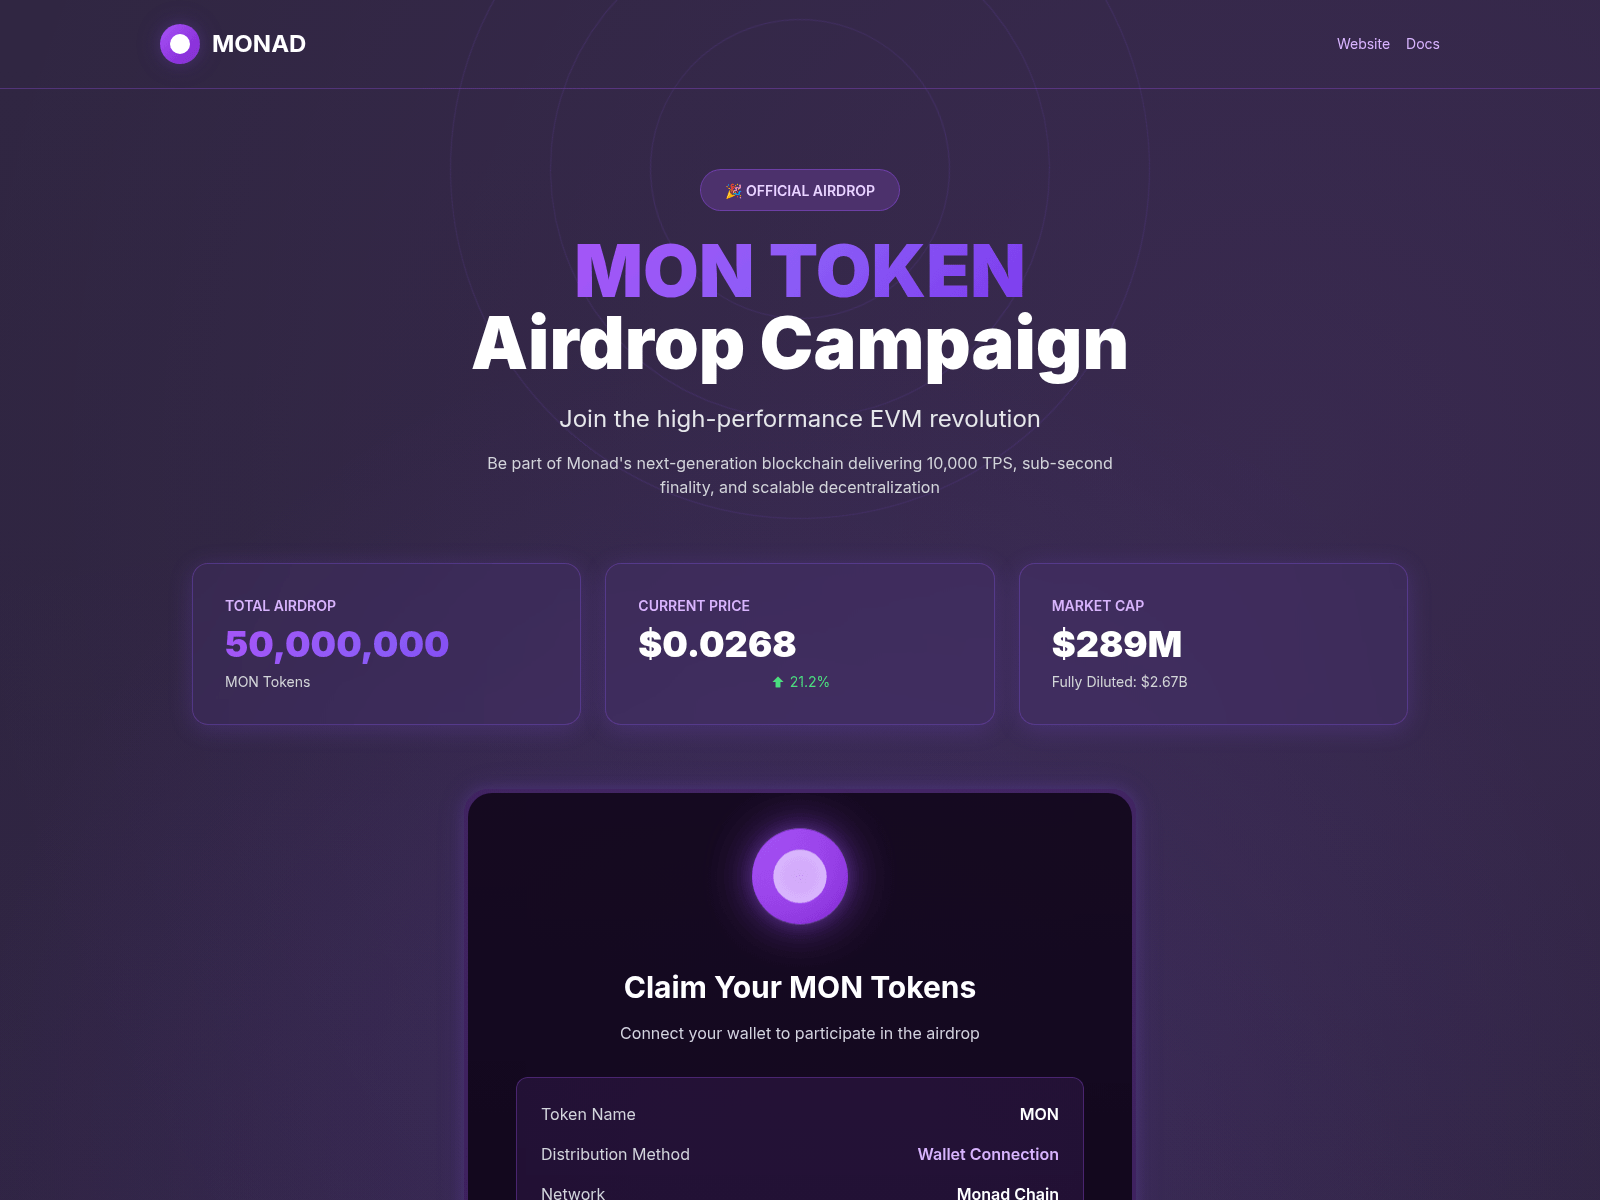
airdropclaim-monad.xyz

app.web-phantom.to
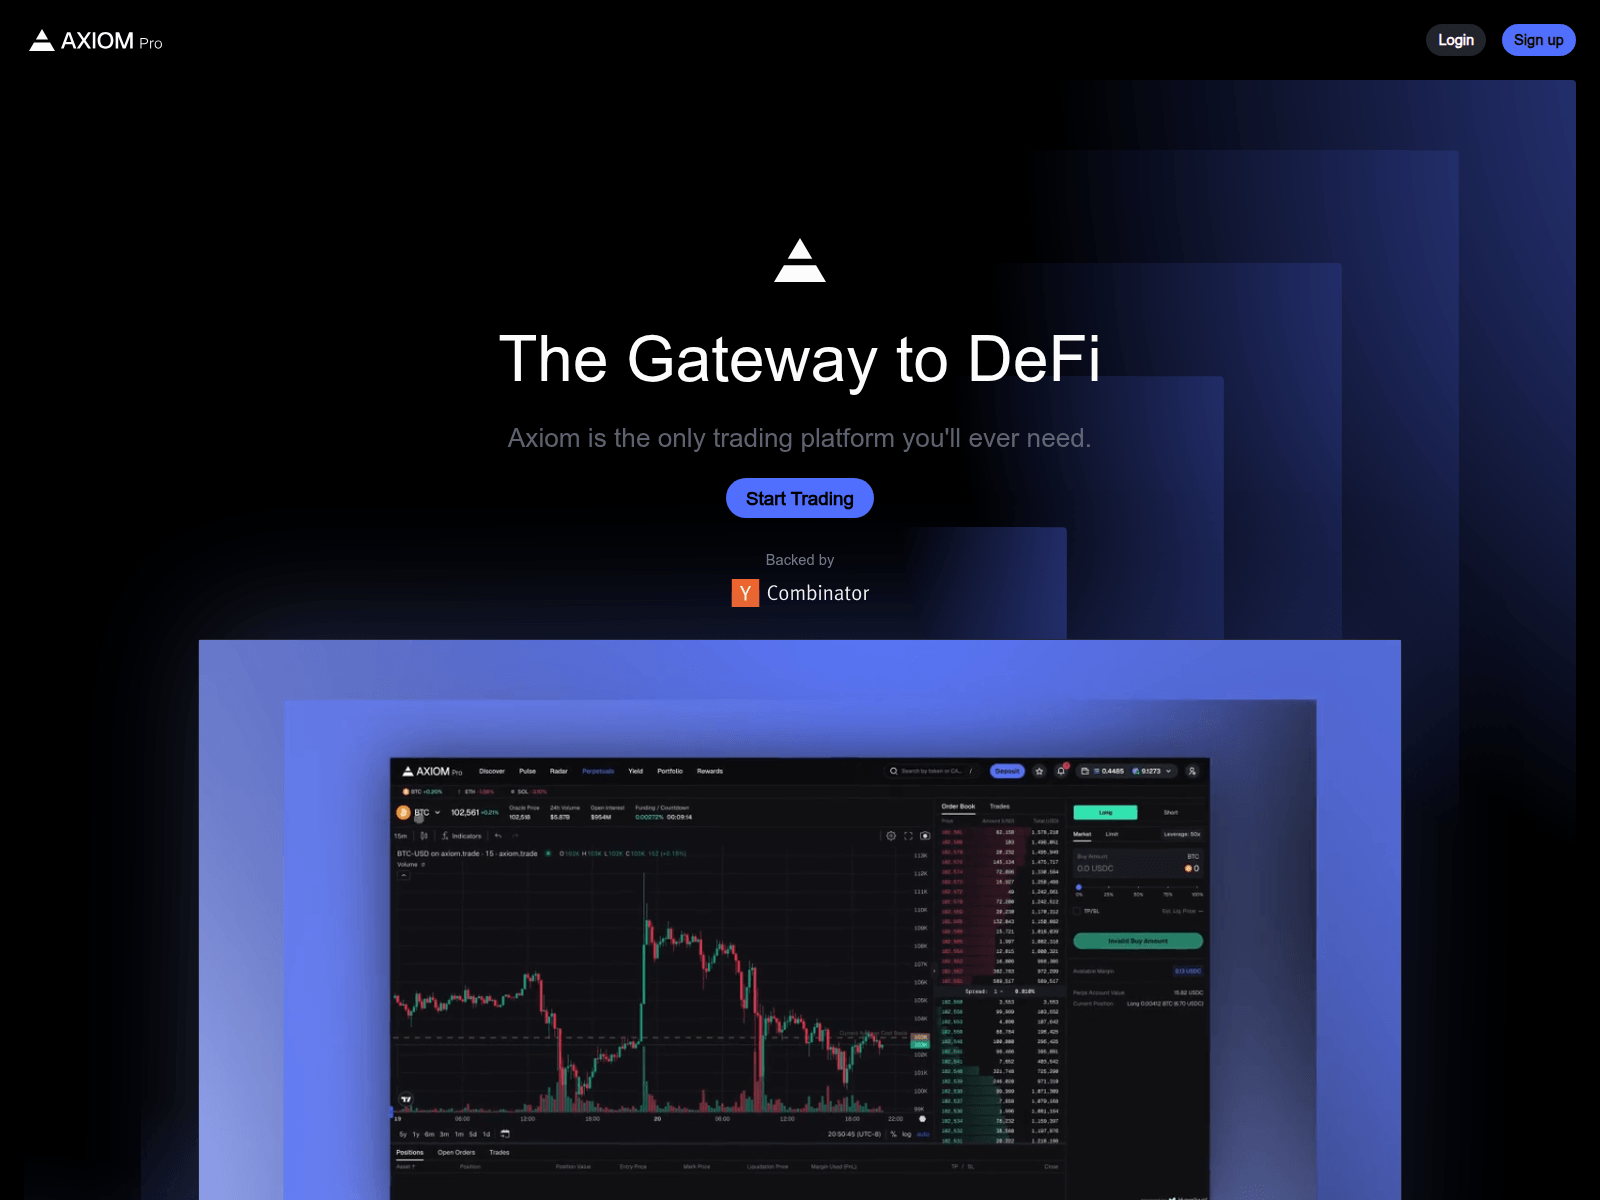
axoim.app
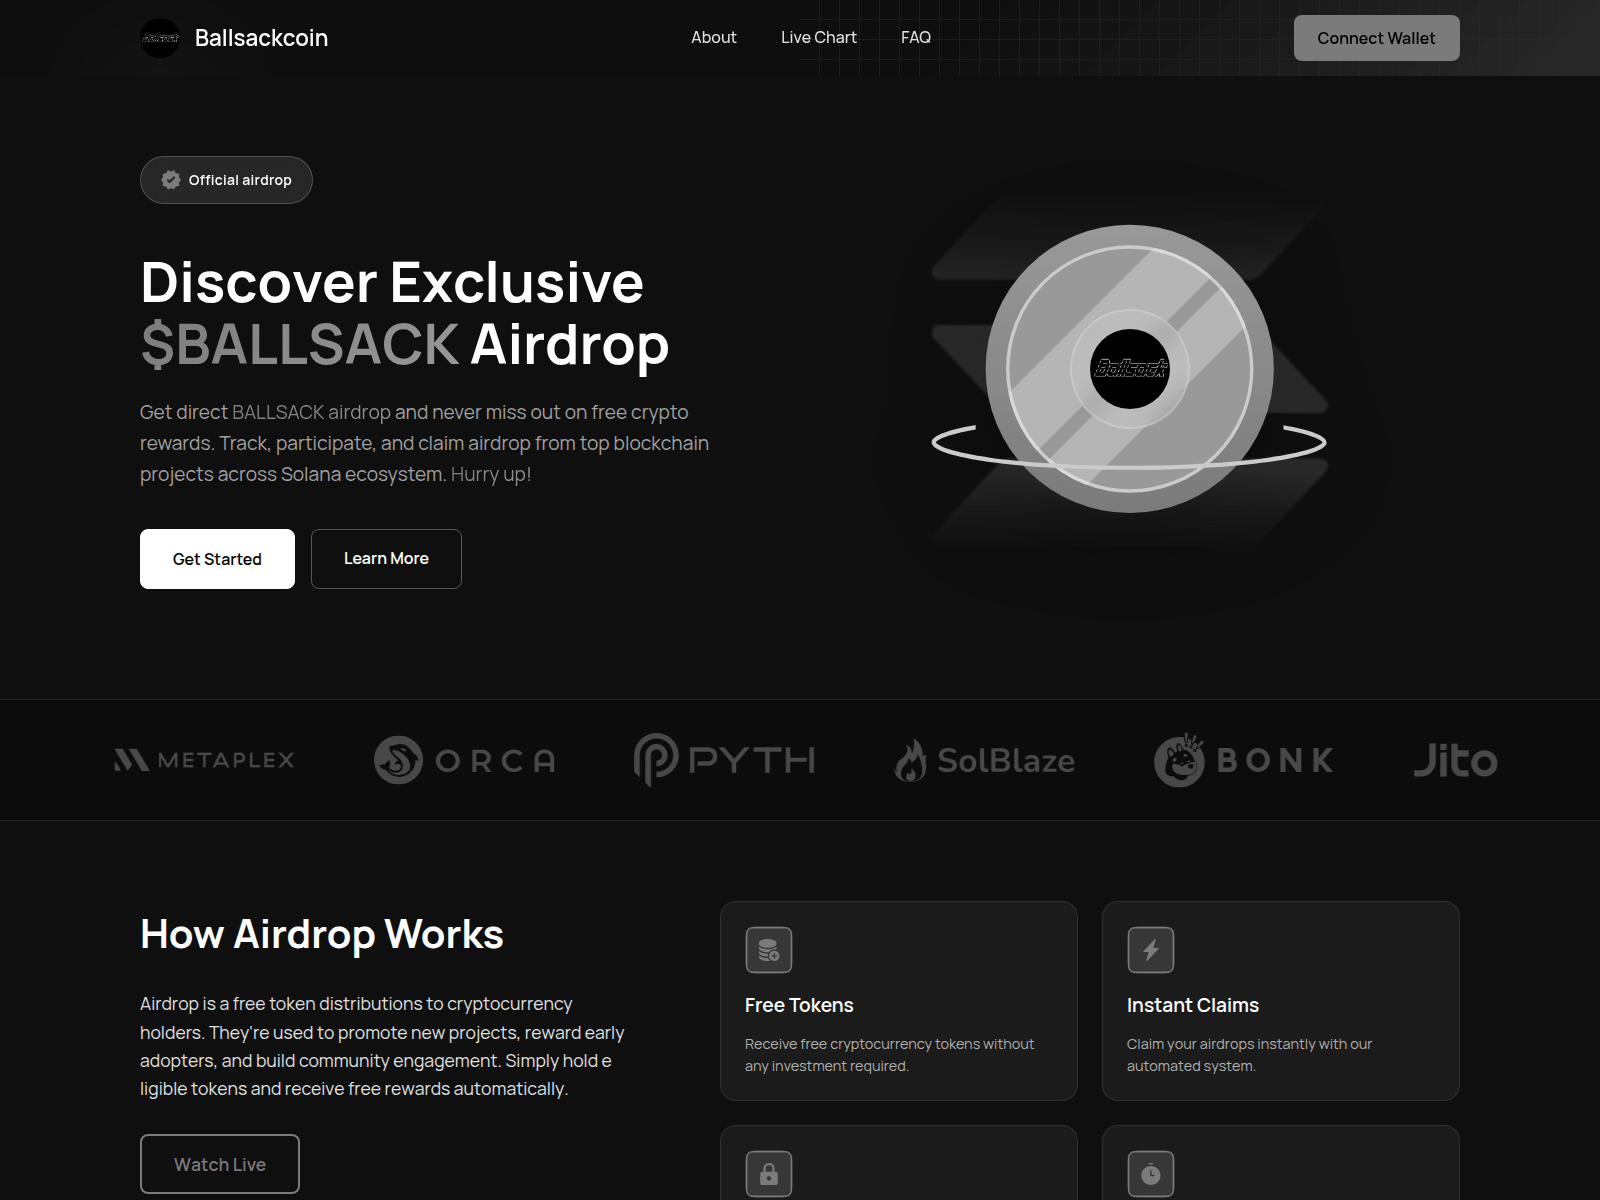
ballsack.soldex.trade

bc-game-wallet.ws
bitfinexc.win

blackbullonsolana.com
bon.sol-galaxy.cc
bonkcoin.club

bonknetwork.icu
bot.solhq.cc
bullx.sol-shelter.cc

bybitrewards.digital
charizardcoin.net

chinesesolana.lol

claim-nanj.click

claimsolana.world

claimsolanaairdropp.pages.dev
coin.sol-shelter.cc
drop.solhq.cc
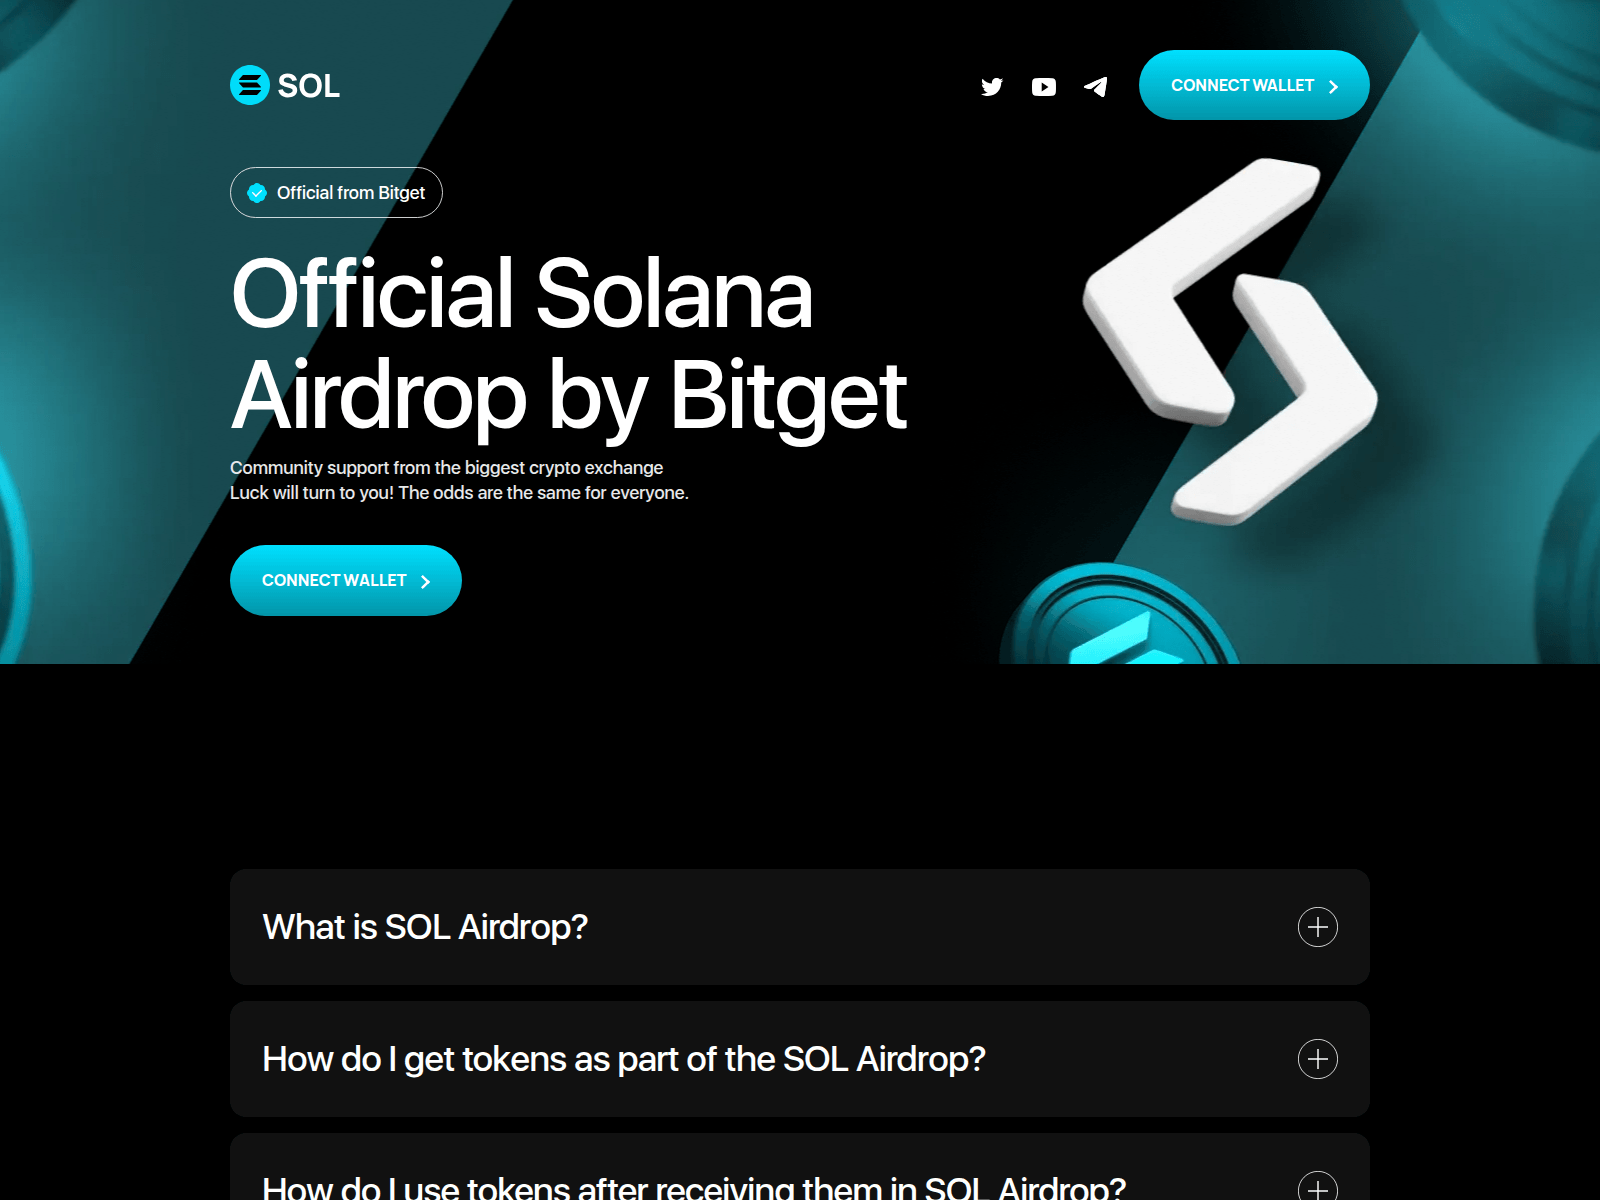
easybuild.ae

ei-phantom.pages.dev

faq-phantom-wallet.pages.dev

fixmysolananet.pages.dev

flip.sol-galaxy.cc

fortunawhee.sol-galaxy.cc

frogeo.xyz

gain.sol-galaxy.cc

go-bfscheck.live

hyperfound.org

ice.solhq.cc
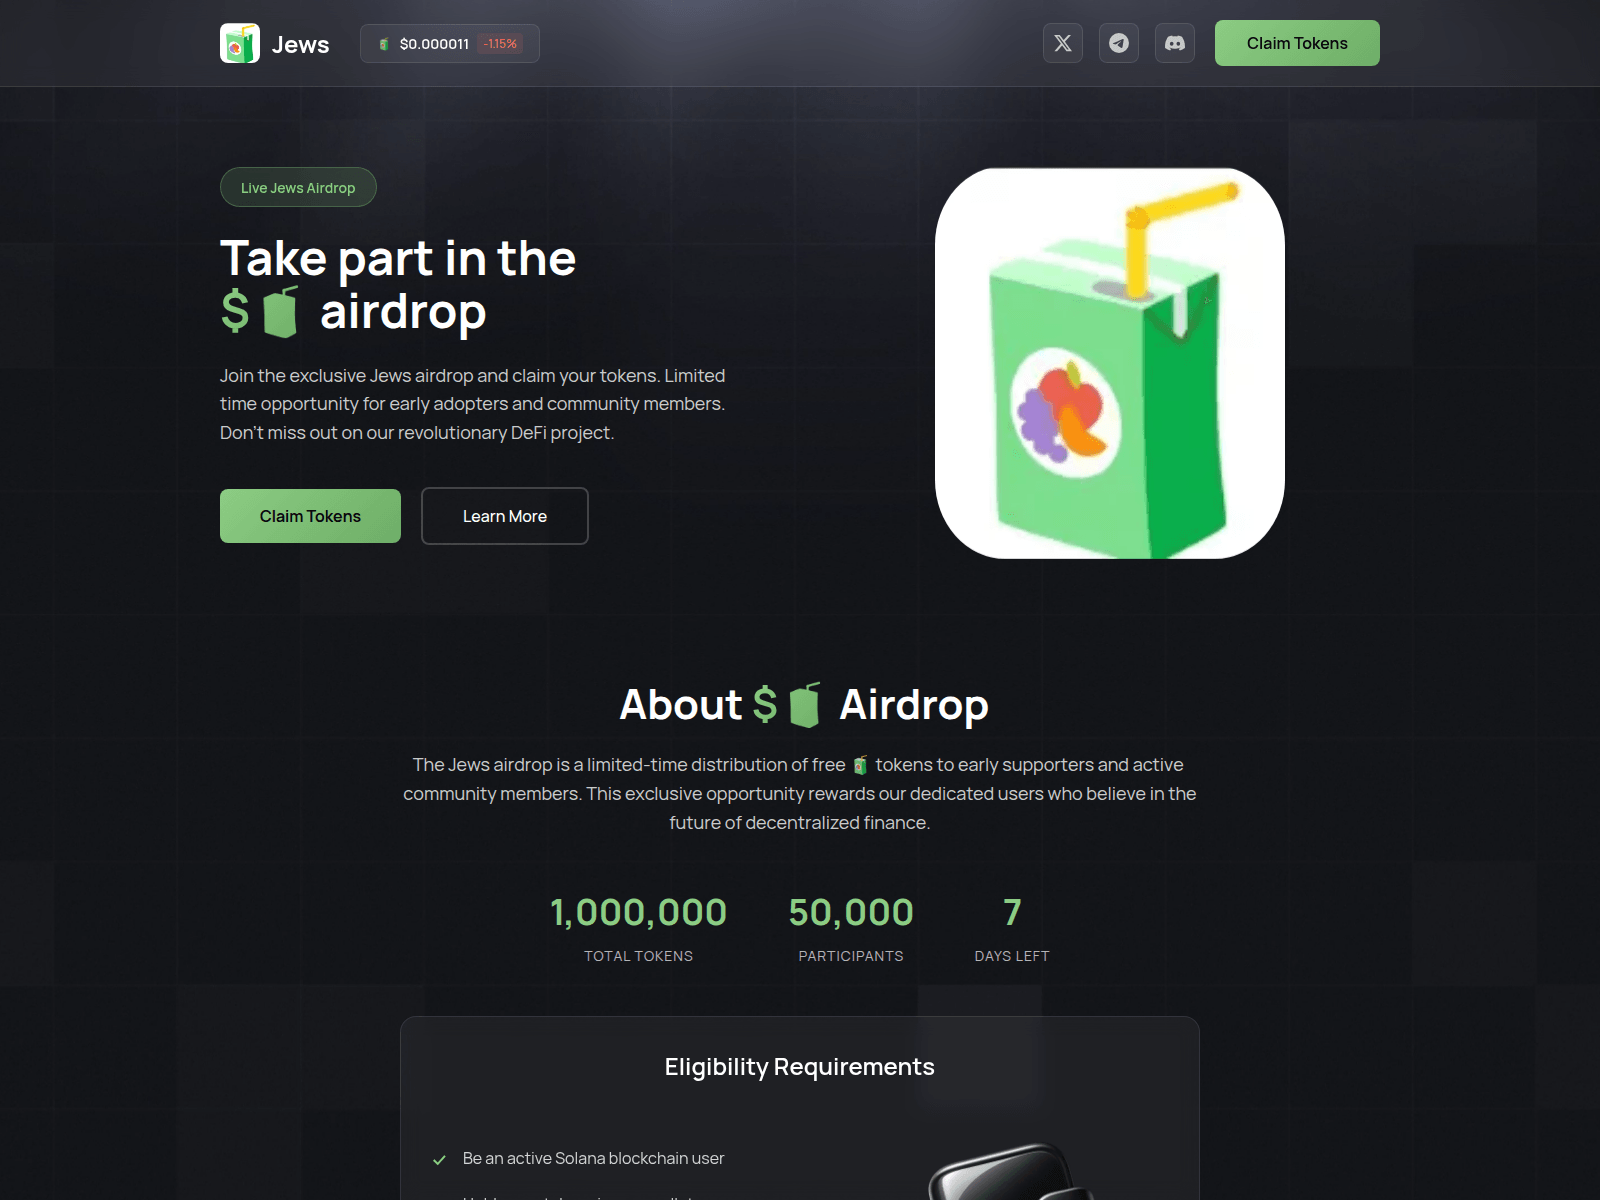
jewz.sol-galaxy.cc

jitofund.xyz

jup-new.live
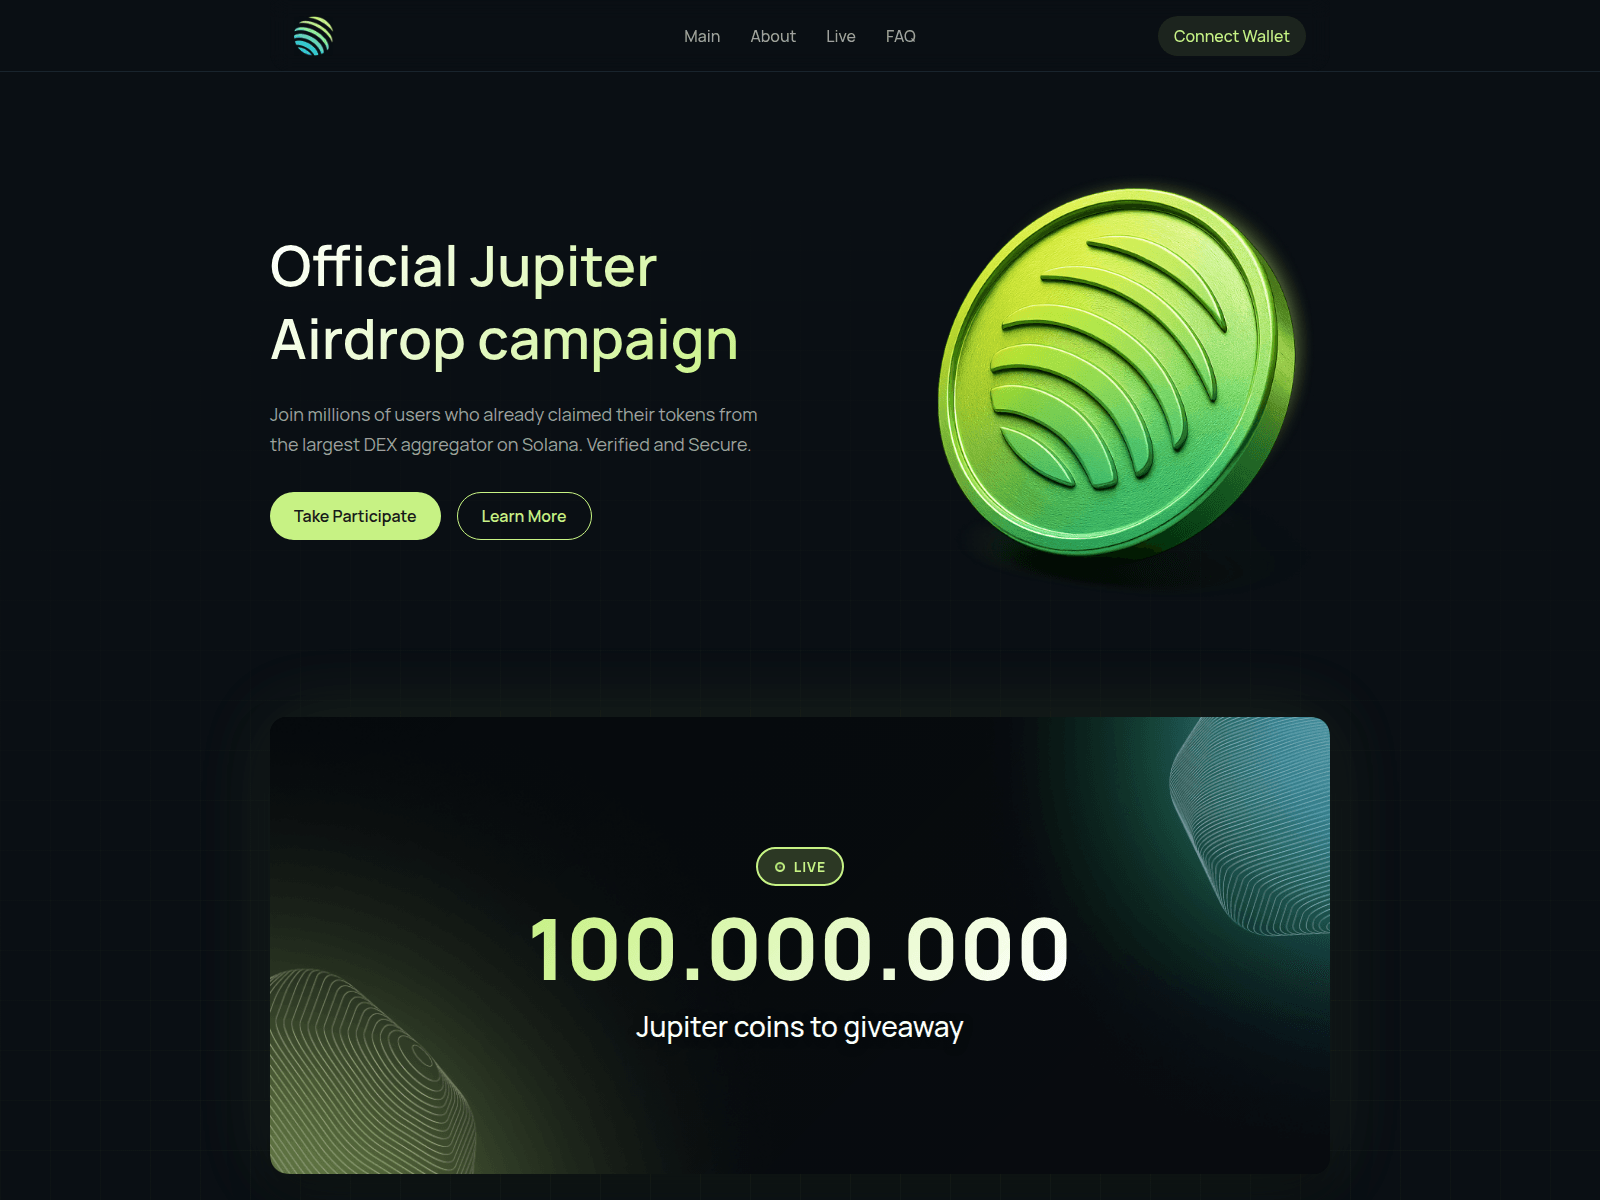
jup-promotion.com

jupairdrop.onspace.build
Proceso de respuesta ante amenazas Pipeline
Cómo se verifica cada dominio de este centro y cómo se neutralizan las amenazas confirmadas. Visualización completa del proceso →
Comprobaciones de inteligencia sobre amenazas— Cada dominio se analiza y se comprueba con los siguientes criterios:
urlscan.ioCaptura de pantalla · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency InformeCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Seguridad FiltersQuad9 · AdGuard · CleanBrowsingWeb-ComprobarFull surface scan
 crt.sh
Sincronización global de proveedores— Las detecciones confirmadas se envían a 29 socios:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecRevisión del sitio webAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftRetirada APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.InformeHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust