VirusTotal
22 / 93
Melden


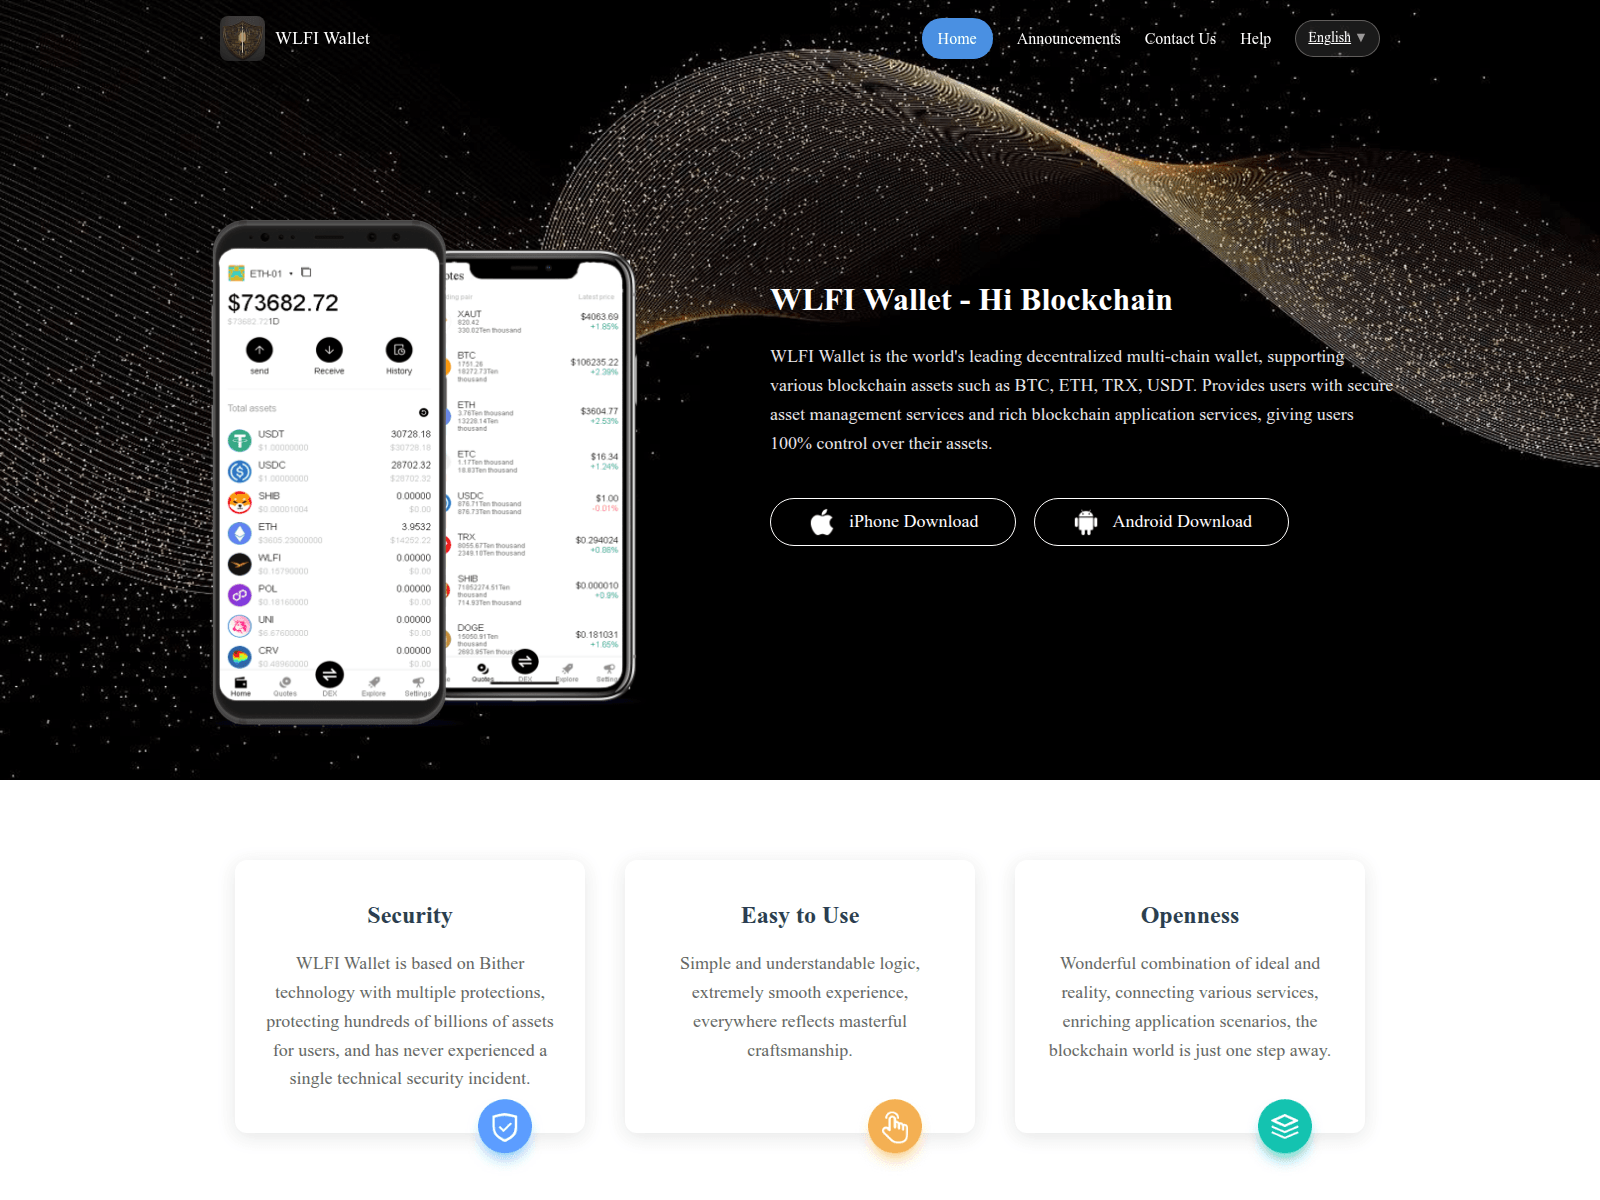
“WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co”
wlfiprobit.com — Inhalt nicht verfügbar. Markenidentität: Arbitrum; Betrugstyp: Crypto Scam. Zusammenfassung der Beweislage: VirusTotal 22/93 (ADMINUSLabs, ChainPatrol, alphaMountain.ai, BitDefender, Cluster25); URLQuery 6 alerts; PhishDestroy score 95/100.
Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | wlfiprobit.com |
malicious | Sinkholed |
| OpenDNS | wlfiprobit.com |
phishing | Phishing Block |
| DigiCert UltraDNS | wlfiprobit.com |
malicious | Sinkholed |
| Hagezi Threat Feed | wlfiprobit.com |
malicious | Sinkholed |
| DNS4EU | wlfiprobit.com |
malicious | Sinkholed |
| Quad9 DNS | wlfiprobit.com |
malicious | Sinkholed |
The domain wlfiprobit.com is identified as a high-risk brand impersonation threat targeting Arbitrum. It masquerades as a legitimate cryptocurrency wallet service, using the page title "WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co" to deceive users. This domain was likely designed to harvest sensitive user data or credentials under the guise of offering cryptocurrency services.
Technical analysis reveals that wlfiprobit.com is flagged by 22 out of 95 security vendors on VirusTotal, indicating significant recognition as a threat. The domain resolves to IP address 172.67.152.201, located in the United States under AS13335 managed by Cloudflare, Inc. It was created on February 21, 2026, and has been blocked by three security blocklists including PhishDestroy, MetaMask, and SEAL. The domain's SSL certificate is identified as WE1, and it is currently offline, reducing immediate exposure.
The domain's current offline status mitigates immediate risk; however, vigilance is advised as it may resurface or similar threats could emerge. Security teams should ensure that blocklists are updated and implement additional monitoring for similar activities. Users should be educated on recognizing phishing attempts, particularly those involving cryptocurrency platforms.
Gespeicherte Beobachtungen zum Vergleich zwischen Crawler und Browser für diesen Host sowie eine Echtzeit-Fingerabdruckprüfung für Verkehrsverteilungssysteme im Keitaro-Stil.
Anmerkung des Scanners: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='wlfiprobit.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError(
Die Edge-IP-Reputation wird dieser Domäne nicht zugeordnet.
Location describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
28 gespeicherte ähnliche Domains
Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.


Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.
Template-based draft · optional AI wording assistance requires separate consent
Jede Spalte gibt einen Grund an, warum eine Domain mit diesem Host verknüpft ist. Knoten in voller Größe kennzeichnen „VirusTotal“-Erkennungen, gestrichelte Knoten sind bereits offline. Die vollständigen Listen folgen weiter unten.
Derselbe Favicon-Hash oder derselbe Seitentitel wie bei diesem Host.
Diese Berichte werden auf dieselbe gemeinsame Edge-IP aufgelöst. Sie helfen bei der Berichtserkennung, bedeuten jedoch keinen gemeinsamen Besitz oder einen gemeinsamen Ursprungsserver.
Diese Domains richten sich ebenfalls an Nutzer von Arbitrum. Alle „Arbitrum“-Bedrohungen anzeigen →
Kürzlich hinzugefügte Berichte aus der PhishDestroy-Datenbank. Diese Discovery-Links implizieren keine gemeinsame Nutzung der Infrastruktur oder des Eigentums.
Bedrohungsanalyse anhand gespeicherter Blocklisten, WHOIS, DNS und öffentlicher Scan-Beweise
Jetzt scannenMelden Sie verdächtige Domains an unsere Bedrohungsdatenbank – schützen Sie die Community
MeldenAktuelle Phishing-Meldungen und beobachtete Verfügbarkeitsänderungen
ÜberwachenBeobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt