 Investigation
Valve Profits from 578,000 Stolen Steam Accounts
Valve must be held accountable. Here is the evidence.
For over a decade, Valve Corporation has maintained deliberate, profitable blindness to the largest stolen gaming account marketplace in history. 819,000+ stolen accounts are listed for sale right now across 16 platforms. PhishDestroy documented all of them — in real time, from the LZT Market public API. The evidence is mathematical, legal, and irrefutable.
- 578,465 Steam accounts for sale today
86,668 via infostealers. 66,744 via credential stuffing. 7,081 via phishing. 1,026 "recovered through Steam support" and resold — direct proof of outsourced corruption. Valve sees every API call. They chose not to act.
- Five legal vectors, one corporate defendant
OFAC sanctions violations. Infostealer facilitation. GDPR data disclosure of minors. Fictitious ToS as corporate fraud. Internal corruption and unregulated virtual currency. Taylor Wessing cannot defend all five simultaneously.
- $450M estimated minimum liability
Documented victim real spend across stolen accounts on LZT Market plus frozen inventories on banned bots — assets Valve appropriated under the guise of fighting fraud.
- Valve's own servers host the evidence
Thousands of sanctions bypass tutorials and region-switching guides are hosted on Steam Community servers, indexed by Google, accessible to non-logged-in users. Valve moderates this platform. Nothing was removed.
Evidence boundary. All statistics reflect point-in-time measurements from direct LZT Market public API observation. Legal analysis reflects published US and EU law as of August 2026. All regulatory contacts are public official data.
An Exclusive Investigative Report by PhishDestroy Research
Who is PhishDestroy to challenge the Valve corporate machine? Where do our data on their vaunted European lawyers come from — the very ones whose reputation has been stained by internal sexual harassment lawsuits? They love to flaunt their status and "centuries-long history," but their memory goes conveniently blank when it comes to the origins of their German branch. They conveniently erase from their corporate chronicle the fact that the founder of their firm was a committed Nazi and a member of Hitler's Reichstag — a cog in a system that sent gay people to concentration camps.
But enough about history. Let's return to technical reality. These "elite attorneys" demonstrate absolute incompetence when processing GDPR requests — they simply do not know how to properly redact confidential information from documents. This is not an intern's mistake. This is direct evidence that they have never adhered to data disclosure procedures, preferring to deflect requests with threats and legal intimidation.
1. Genesis of PhishDestroy: Destroying C2 Infrastructure Instead of Bug Bounties
Between 2018 and 2021, the Steam ecosystem was experiencing a boom in uncontrolled spam. The name "PhishDestroy" did not yet exist, but it was us who laid the foundation for anti-fraud work within Steam. We are not pinning medals on ourselves — we were simply doing the dirty work that the corporation refused to do. From the moment of our inception to this day, we destroy scammer infrastructure on an industrial scale.
At that time, we brought our confirmed report count on Netcraft [1] to between 5,000 and 10,000. Given the specifics of the platform, the real number of generated reports was at least ten times higher. Netcraft required ironclad proof of phishing. Why? Because Valve categorically refused to cooperate with either security providers or anti-scam initiatives. Some reports simply died in the pipeline before being processed. Persistent phishing campaigns — especially resources hidden behind aggressive cloaking — required recording video evidence and parallel escalation through Cloudflare's abuse departments [2].
We saw the scam, and we destroyed it. Not to save naive users. We were banning resources solely for the purpose of inflicting financial and infrastructural damage on phishers. If the corporate sector thinks we were burning scammer servers for the sake of an iPad from Netcraft's Reporter Prizes program [1] — you are wrong. We have always been a strictly non-commercial operation. Our principled refusal of donations and rewards is a declaration of our independence and loyalty exclusively to the process of destruction.
2. Complicity and Monetization: How Valve Profits from Phishing
In those years, Steam's "security" rested on 50 volunteers. We were in contact with one of them — a Belarusian who went by the nickname Colt. He was the only one trying to block the malicious links that were flooding the platform. The ideal victim: children. The ideal accomplice: Valve.
The corporation did not merely turn a blind eye to phishing — it had a financial interest in it. Our data directly proves the implementation of algorithmic cynicism: the likelihood of a scammer bot being blocked depends directly on the value of the stolen inventory. Since 2021, following the introduction of trade holds, the theft of a skin worth $2,000 or more guarantees nearly a 90% chance of the fraudster's account being banned.
But here is the detail no one talks about: the ban does not benefit the victim. The assets are frozen on the banned account, effectively returning to Valve's economy. The corporation appropriates windfall profits under the guise of fighting fraud. And this applies not only to CS — scamming flourishes in Team Fortress and other titles, where bans work more aggressively only thanks to community activity and the targeted efforts of individual moderators.
3. Business Logic Abuse: Steam as a Digital Crime Scene
We have the right to publicly dissect Valve's complicity in the scam industry, because we have seen their rotten architecture from the inside. At the beginning of our work, we tried to engage with support. We created tickets and attached domains leading directly to phishing landing pages. Do you know what the Russian-language outsourced support responded?
"We are prohibited from following links. If you send a link again, we will ban your account."
This is not a security policy. This is concealment of evidence.
The overwhelming majority of phishing was distributed inside the platform itself. Steam is a closed ecosystem, ideal for conducting Business Logic Abuse. Users did not even need to leave the client. Attackers used the built-in browser in Big Picture mode. The attack vectors were primitive but effective: personal messages, comments, infected usernames carrying non-unique spam along the lines of "hello bro join giveaway free knife link use code GABEN."
The Steam client itself delivered the phishing, itself compromised the account, and itself facilitated the theft of skins. The corporation created a tool that devoured its users and refused to control it.
4. Billions for 79 People: The Anatomy of Valve's Greed
The scale of that profit and the level of corporate cynicism only became clear after the massive data leak of 2024 [3].
The documents revealed a shocking truth: as of 2021, the entire corporation employed exactly 336 people [3]. And working directly on the Steam platform — a global monopoly generating billions of dollars in revenue — were just 79 people [3]. Valve is not merely economizing on personnel. Internal documents show them boasting that their profit per employee exceeds that of Google, Amazon, and Microsoft.
These figures are not just a business case. This is mathematical proof of absolute disregard for security. A platform serving hundreds of millions of users physically cannot ensure protection with 79 people.
That is 6.3 million users per security engineer. Twitter maintained 1 per 100,000.
5. Lolzteam and the Shadow Economy of Stolen Profiles
Valve's fairy tale goes like this: "It's the user's own fault if they got hacked." The reality reads differently: Valve spawned the scam infrastructure, never fought it, and deliberately maintains a vast shadow layer of the economy aimed primarily at the CIS countries and China. The reason is simple — retaining audience, compensating for piracy, and fencing stolen assets.
Let's look at the black market figures that Valve refuses to see. The LZT Market platform (Lolzteam) is the epicenter for selling stolen accounts. Let us look at a real-time snapshot of the listings: right now the market has 578,465 Steam accounts listed [4]. Of these:
- 86,668 accounts were stolen via infostealers.
- 66,744 were obtained through brute force.
- 7,081 are the result of direct phishing.
- 1,026 accounts were restored through Steam support and resold DIRECT PROOF OF OUTSOURCED CORRUPTION(direct proof of outsourced incompetence).
1,026 accounts on LZT Market are listed as “recovered through Steam support” and resold. Valve support staff restored access to dormant accounts for criminals — documented, enumerable, legally actionable.
- 126,429 accounts have no $5 spending limit (meaning live users spent real money on them).
Source: LZT Market public API · Point-in-time measurement · PhishDestroy research, August 2026
The minimum estimated damage from accounts without a spending limit alone is over $630,000 at this very moment. But the real transaction figure is hundreds of times larger.
And here a certain figure named Nikita surfaces — a person who allegedly oversaw the Russian-language Steam support outsource (not affiliated with the Irish office) for many years. His account was registered directly on the Lolzteam platform. Why? To monitor large inventories and block them? To collect analytics?
Even if so, blocking stolen profiles does not require registering on shadow forums. LZT Market uses a public API. Valve can plainly see the mass, identical requests: password changes, email detachments, automated inventory checkers and account validators. All of these come from the IP addresses of known proxy farms.
The behavioral pattern of a stolen account being listed on the market lights up in Valve's logs like a Christmas tree. But the corporation prefers to look away.
6. Scale of the Catastrophe: Tens of Millions of Dollars Off the Books
Valve does not publish reporting on black markets, but the math is merciless. Item IDs on the LZT market (e.g., item_id 252853378 [4]) show that over 250 million lots have passed through the platform. Of these, the Steam category has historically accounted for 30-40%.
This means that over the platform's history, between 75 and 100 million Steam accounts have been passed through it. The same stolen profile can be resold dozens of times, generating an endless chain of transactions until it is permanently banned.
Each day, conservatively around 25,000 transactions are conducted in the Steam category — from cheap auto-registrations to high-value phished accounts. With an average transaction price of 150-200 rubles, this category alone generates between 3.5 and 5 million rubles in daily turnover. The annual volume of the shadow market around Steam on just this one platform reaches tens of millions of dollars. The market takes its commission (8-9%), the scammers receive windfall profits, and users lose money.
And what does Valve do? Valve counts profits per their 79 employees and continues to pretend that nothing is happening.
7. Legalizing Theft and the Steam Crypto Laundromat
Look at the ecosystem they refuse to acknowledge. The infrastructure for selling stolen accounts on Lolzteam is not hiding in the dark web. It openly accepts payments via crypto bots (Telegram, Binance [28], Bybit [28], Gate [28]), Russian bank cards, and even PIX or Alipay. A commission is charged on every transaction. A massive array of confidential data, including correspondence and personal information of US and European citizens, passes through these gateways.
And what does Steam do? They send an email about a credential change. If an account is stolen from a child (who is the primary audience of cheat industries in CS:GO and PUBG), the platform simply watches as a permanent VAC ban is placed on the profile. Valve possesses all the technical telemetry: they see patterns of IP address, hardware, and behavioral metric changes. They can stop the theft in real time. But doing nothing and waiting for the victim to create a new account and repurchase games — this is not an accident; this is an approved business model.
Incidentally, the shadow market itself has long ceased to be a "club of independent hackers." The forum on which this infrastructure is based is effectively controlled by structures close to the Russian government, with which Steam apparently coexists quite comfortably. Five decisions by Roskomnadzor [23] to block the resource have been successfully ignored or appealed in an invisible legal field — draw your own conclusions.
7a. Digitální fiat: Proč skiny na Steamu nejsou herními předměty – jde o nelicencovanou platební síť
Společnost Valve strávila roky budováním právní fikce: že skiny jsou pouhé „pixelové obrázky ve hře“ bez reálné hodnoty. Tato fikce se hroutí při nejzákladnější analýze toho, jak se peníze ve skutečnosti pohybují přes jejich platformu.
Aktivuje se dárková karta Steam v hodnotě 200 dolarů. Skutečné americké dolary přijdou na bankovní účet společnosti Valve. Zůstatek se použije na nákup nože ve hře. Nyní: (1) Může tento nůž financovat zůstatek na LZT Marketu za účelem nákupu ukradených účtů? Ano. (2) Lze jej prodat na trzích třetích stran (BitSkins, DMarket, Skinport) za skutečné rubly, dolary, PayPal nebo kryptoměny? Ano.
To dokazuje, že daný předmět má fyzickou hodnotu podloženou poptávkou komunity a infrastrukturou centralizované platformy. Můžete investovat skutečné peníze, získat skin a zpeněžit ho za přibližně stejnou částku. To je definice likvidního finančního aktiva.
výnosy kartelu
PŘEDMĚTŮ
Z DOTA bez spuštění hry
BITSKINŮ
na externím trhu
BITCOINY
– plně vyprané
Nejedná se o chování hráče. Jedná se o finanční transakci. Absence jakékoli herní aktivity na účtu je varovným signálem, který by jakákoli regulovaná finanční platforma odhalila a nahlásila. Systémy společnosti Valve tuto anomálii označí a účet zablokují – a poté si tiše ponechají 100 % původního vkladu v hotovosti prostřednictvím mechanismu „Forced Breakage“, aniž by o tom informovaly jakýkoli finanční regulační orgán.
– výnosy z hacků
(CSGOFast)
VE FORMĚ SKINŮ
– žádná stopa v blockchainu
NA TRHU
S KYC – legitimní burza
MENA DO BANKY
– zcela vypraná
Na rozdíl od Monera nebo Tornado Cash nevyvolávají skiny ze Steamu žádné upozornění v blockchainovém prohlížeči. Banky vidí běžný prodej na herním tržišti. Špinavá kryptoměna byla prostřednictvím infrastruktury platformy Valve převedena na nevystopovatelnou čistou fiat měnu. CSGOFast je ve vlastnictví Rusů. Kasino je zakázáno v několika zemích EU. Steam hostuje jeho propagační rozšíření.
8. The Economics of Catastrophe: Steam as the Foundation of the Black Market
You might say that markets like this don't sell only Steam. True — profiles from World of Tanks (~340k), Fortnite (~140k), TikTok, and Discord are also traded there. But Steam is historically the foundation and the primary driver of this industry. Valve inventories and accounts create demand for infostealers. If Steam had implemented strict anti-theft measures, the development of stealers would simply become economically unviable.
An important detail: accounts stolen solely via SSFN files are almost never listed on the market. Mobile authenticators complicated full account takeover. However, SSFN files give attackers an active session, a contact list, and the ability to send phishing en masse or integrate into botnets. And if the account is truly valuable, Steam's outsourced support enters the picture. Fraudsters draw up fake activation keys, write to support, and incompetent (or bribed) employees transfer the expensive inventory to a new address. This gave rise to an entire category of "Recovered Accounts" — profiles that Valve's outsource effectively stole and laundered for criminals.
9. The Myth of Duplication and Shadow Confiscation of Assets
Steam loves to hide behind fighting "duping" (item duplication) to justify refusing to return stolen items. This is a brazen lie. The era of duping ended in 2014. With the introduction of the 7-day trade hold in December 2015 [14] (and its subsequent tightening), the logistics of theft became entirely linear: Victim -> Scammer's bot (7-day hold) -> Shadow market.
Where is the dupe in this? If a scammer deceived a victim and took a rare skin, it sits on the bot. Valve bans that bot. And then what? The item does not return to the victim. It is permanently frozen in the banned bot's inventory. Valve removes the asset from circulation, creating artificial scarcity of rare items, which directly drives up prices on the marketplace and increases the corporation's commission income.
This is not justice. This is shadow confiscation. In financial systems (such as those involving USDT), blocked funds are returned to the legitimate owner through a chargeback mechanism. Steam knows perfectly well how a chargeback works when it comes to topping up their own balance with dubious cards — they block those transactions instantly. But when a user has an item worth $5,000 stolen, Steam washes its hands. They close tickets, threaten account deletion, and refuse to reverse the single fraudulent transaction, proving that their primary objective is to appropriate the asset for themselves.
9a. Nucená slepota: Jak společnost Valve skrývá stovky milionů v zabaveném majetku
Když byly inventáře zakázaných účtů veřejně dostupné, mohl jakýkoli právník vyhledat údaje na SteamDB, CSGO.exchange nebo Backpack.tf a během několika sekund získat ověřený souhrn aktiv, která společnost Valve zadržovala. Tato částka – odhadovaná na 300–500 milionů dolarů v zmrazeném majetku uživatelů – je základním údajem potřebným k potvrzení hromadné žaloby. Společnost Valve tuto možnost záměrně uzavřela. Tím, že informace o majetku v zablokovaných účtech uzavřela do „černé skříňky“, odstranila nezávislou finanční auditní stopu, kterou by právníci žalobců potřebovali k prokázání škody v odpovídajícím rozsahu.
Když společnost Valve zablokuje účet, odebere uživateli přístup k hrám od společností CD Projekt Red, EA, Ubisoft a tisíců nezávislých vydavatelů – k hrám, jejichž licence uživatel drží prostřednictvím těchto vydavatelů, nikoli prostřednictvím společnosti Valve. Společnost Valve je v tomto smluvním řetězci distributorem a platební bránou, nikoli poskytovatelem licence. Zrušení trvalé licence vydané třetí stranou – z důvodu sporu na Steam Marketplace – je učebnicovým příkladem protiprávního zásahu do smlouvy. Podle směrnice EU o právech spotřebitelů představuje zablokování přístupu k placenému digitálnímu obsahu bez vrácení peněz, pokud nedošlo k porušení konkrétního produktu, přímé porušení vlastnických práv uživatele k licenci.
Společnost Valve do databáze zákazů nezadává slovo „trvalý“. Zadává konkrétní data: 10 let, 25 let nebo přetečení 32bitového časového razítka Unixu – 19. ledna 2038. Nejedná se o technickou chybu. Je to právní úniková cesta.
V jurisdikcích občanského práva a podle doktríny základních práv EU nemohou podmínky služby soukromé společnosti ukládat trvalé a nezvratné zbavení majetkových práv bez soudního přezkumu. Tím, že 25letý zákaz označí jako „dlouhodobé omezení služby“, může společnost Valve u soudu tvrdit: „Jedná se o dočasné bezpečnostní opatření, nikoli o trvalý trest.“ Mezitím je uživatel fakticky zbaven svého účtu a všech licencí po zbytek svého života. Společnost Valve sází na to, že většina postižených na to zapomene, půjde dál nebo období zákazu nepřežije. Jedná se o právní manipulaci navrženou na úrovni architektury databáze.
Výmluva služby Steam o „boji proti duplikacím“ neobstojí. Poslední potvrzená chyba umožňující duplikaci předmětů byla opravena v roce 2014. Každý zákaz a zmrazení od té doby fungoval jako lineární řetězec krádeží — oběť → podvodný bot → trh → zmrazené zásoby společnosti Valve — bez jakéhokoli ekonomického ospravedlnění pro trvalé zadržování majetku. Jediným beneficientem zmrazení je samotná společnost Valve, a to díky zvýšeným cenám předmětů, nadhodnoceným provizím a trvalému zbavení jakékoli právní odpovědnosti za to, co se s majetkem stalo.
Kirill_Killer34 zaplatili publikační poplatek 100 $ službě Steam Direct za nahrání falešných her „Abstractism“ a „Climber“. Následně v inventářích těchto her vytvořili předměty, které byly pixelově dokonalými replikami nejdražších předmětů v celé ekonomice Steamu: CS:GO AWP | Dragon Lore, Dota 2 Dragonclaw Hook a TF2 Australium Rocket Launcher. Tisíce obchodníků viděly v okně pro výměnu něco, co vypadalo jako Dragon Lore. Název hry „Climber“ byl zobrazen malým písmem. Vyměnili skutečné, vysoce hodnotné předměty za prázdné obrázky z bezcenné hry. Hry také obsahovaly skrytý kryptominer Monero, který tiše běžel na počítačích obětí.u/Drunken_F00l) se v diskuzi objevil. Společnost Valve hry odstranila, vývojáře zablokovala, zavedla varovné bannery při obchodování („Tuto hru jste nikdy nehráli“) a — co je nejdůležitější — oficiálně potvrdila, že obětem, které přišly o předměty ještě před zavedením varovných bannerů, budou jejich předměty vráceny. Uživatelé potvrdili, že své předměty dostali zpět. K vrácení došlo. Ve velkém měřítku. Bez narušení herní ekonomiky.u/Drunken_F00l. Archivováno. Lze předložit jako důkaz. Nejedná se o spekulaci – jde o zdokumentované, oficiální prohlášení jmenovaného zaměstnance Valve, který potvrzuje, že vrácení transakcí je technicky možné a bylo provedeno. Jejich současný postoj, že je to „nemožné“, je prokazatelná lež. Podvodník prodá ukradený skin Dragon Lore na Community Marketu. Valve inkasuje 15% provizi = 300 $ ze skinu v hodnotě 2 000 $.
Společnost Valve zablokuje podvodnického bota. Skin „Dragon Lore“ je navždy zmrazen. Společnost Valve eliminuje virtuální závazek ve výši 2 000 $. Původní kupující zaplatil skutečných 2 000 $ v reálných penězích. Společnost Valve si ponechá 2 000 $. Provize: 100 %.
Porovnání: jak Tether obnovil 10 000 $ vUSDTu (hack Bybit) vs. jak reagovala podpora Steam na identickou krádež. Klikněte na SPUSTIT a simulujte obě situace.
10. A Training Ground for Global Scamming
PhishDestroy has been tracking scams since 2018. We know the inner workings. Steam became the primary incubator for cybercriminals. Teenagers aged 14-19 who started with primitive brute-forcing and distributing stealers through fake TeamSpeak servers have grown up. Today those same people use the techniques they refined to attack the Web3 industry (Uniswap) [26] and corporate networks.
Valve raised this generation. Their refusal to punish, their blindness, and their greed showed underage fraudsters that stealing is safe. And the Russian-language outsource, playing at justice and handing out permanent bans without explanation (hiding behind non-disclosure of VAC algorithms), only reinforces this impunity.
10a. Kontrast s Twitchem: Co se stane, když se platforma skutečně brání
Společnost Valve tvrdí, že boj proti phishingu ve velkém měřítku je nemožný. Srovnání s Twitchem dokazuje, že je to lež.
Po určitou dobu byl Twitch zaplaven falešnými streamy s „rozdáváním skinů na Steamu“, které se vydávaly za profesionální hráče e-sportu — všechny měly za hlavní cíl podvody na Steamu a phishing. Streamy nasbíraly přes 20 000 falešných diváků díky zakoupenému provozu. PhishDestroy dokumentoval průběh kampaně a aktivně o ní informoval.
- Okamžité zablokování kanálů po nahlášení
- Zákaz skupin proxy — blokování celých rozsahů IP adres
- Změna algoritmu: řazení podle interakce, nikoli podle hrubého počtu diváků
- Spouštěč automatického zablokování: nový účet + spuštění streamu + nepravděpodobný nárůst počtu diváků
- ~45 000 kanálů odstraněno za dobu trvání kampaně
- ~2 000 nahlášených a odstraněných domén
Toto srovnání vyvrací poslední zbývající obranu, kterou by Valve mohlo nabídnout: že problém je příliš velký a příliš rychle se měnící na to, aby s ním bylo možné bojovat v odpovídajícím měřítku. Twitch dokázal, že odhodlané a cílené kroky platformy dokážou během několika měsíců oslabit a zničit sofistikované podvodné operace. Steam má k dispozici stejné nástroje, více zdrojů a přímý finanční zájem na ochraně majitelů účtů – a to již více než deset let. Rozhodnutí nezasáhnout bylo vždy vědomou volbou.
Zatímco Valve vybírá 15% provize z ukradených účtů na Steamu, společnost Epic Games zvolila opačný přístup. V době tohoto vyšetřování zobrazuje LZT Market aktivní systémové oznámení pro kategorii Fortnite/Epic Games: „Epic Games (částečně deaktivováno: nahrávání a ověřování účtů nemusí být k dispozici)“ – což znamená, že backend společnosti Epic aktivně detekuje a blokuje automatizované systémy, které LZT používá k ověřování a zveřejňování ukradených účtů. Epic nebojuje pouze proti podvodníkům. Bojuje proti samotné infrastruktuře tržiště, a to v reálném čase.
- Aktivně blokuje koncové body nástroje na ověřování účtů „API“ na LZT Market
- Systémy proti automatizaci detekují a deaktivují hromadné ověřování účtů
- V reálném čase deaktivuje kanály pro nahrávání ukradených účtů
- Výsledek: Kategorie Fortnite na LZT označena jako „částečně deaktivovaná“
- API na platformě Steam zůstává pro nástroje na ověřování účtů na LZT Market plně otevřený
- Žádné omezení frekvence automatizovaných hromadných ověřovacích požadavků
- Žádná detekce klíčů API pocházejících z LZT
- Výsledek: Steam je největší a nejaktivnější kategorií na LZT
Odkaz: Závislost odvětví infostealerů na herních přihlašovacích údajích je zdokumentována ve zprávě Infostealers.com: „The Future of Cybercrime 2025“ — kde se uvádí, že herní účty se trvale řadí mezi nejcennější cíle infostealerů. Aktivní protiopatření společnosti Epic Games dokazují, že se jedná o řešitelný problém. Nečinnost společnosti Valve je výsledkem její politiky, nikoli technického omezení.
11. Proof of Convenient Blindness
There is an irrefutable fact proving that Valve deliberately covered for black markets. For years — we emphasize, years — direct, open links to stolen Steam profiles were posted on the pages of shadow markets. Valve needed no complex investigations. A ten-line script could have parsed the market's database once a minute and placed a "Red Tag" (KT) on compromised accounts pending verification by the rightful owner.
This did not happen. Millions of transactions passed under the cover of "convenient blindness." Only recently have the markets begun proxying data (via steam-preview) to hide profiles from independent researchers and bypass privacy settings. But history remembers everything. Valve could have destroyed this market with a single click. Instead, they chose to skim the cream off it.
12. Digital Fingerprinting: Why Proxying Markets Does Not Save Valve
The newest defensive mechanism of shadow markets — proxying links through steam-preview — is used by Valve as yet another convenient excuse for their inaction. The corporation pretends that it is now "harder" for them to identify stolen profiles. This is an absolute lie. For Valve's security systems, an account listed for sale remains as transparent as glass.
Identification via Digital Fingerprint: The market's preview dump openly publishes exact purchase dates and amounts (for example, -2.85 EUR from June 15, 2026), the exact registration date, and balance. In Valve's database, no two accounts with an identical transaction history physically exist. A straightforward SQL query from the support side locates this profile in milliseconds, even if a direct link to it is hidden behind a proxy.
API Anomalies and Interception Patterns: To generate a preview, the shadow market's checker queries the Steam API. On the account itself, a characteristic chain reaction is triggered at that moment: email change, password reset, Steam Guard re-linking, and a simultaneous inventory valuation request, all compressed into a few minutes. All of this happens from the IP addresses of known proxy farms.
13. The Evolution of Interception: From SSFN to Pass-the-Cookie and JWT
Valve's most egregious crime is not the theft of skins. It is their conscious facilitation of the spread of malicious software and the financing of global botnets through vulnerabilities in their own architecture.
For a long time, the primary vector for session interception was SSFN files [27]. Today the industry has moved forward: attacks have shifted to hijacking web session cookies and JWT tokens (JSON Web Tokens) [21]. The architecture of scamming has become smarter — attackers have learned to validate these tokens locally, without direct requests to Steam's servers, making such attacks invisible to Valve's primitive anti-fraud systems, assuming those systems are not configured for strict monitoring (and they are not).
The technical mechanics work as follows:
Step 1. Trust Infrastructure as a Free Assembly Line: Since a single stolen token is often insufficient for fully unlinking a protected account, attackers squeeze a different resource from the obtained session — trust. A script gains access to the victim's chats and sends phishing links or virus installers to the entire contact list. Steam graciously provides hackers with its internal P2P infrastructure as a perfect, free engine for the geometric expansion of botnets.
Step 2. Criminal Negligence (Ignoring UEBA): Whether it's an outdated SSFN tied to specific hardware, or modern session cookies — Steam sees 100% of the anomalies. When a token legitimately issued to a PC in, say, Moscow suddenly initiates activity from a German dedicated server, any normal corporation (take Google, for example) would instantly kill the session and issue a red alert: "Session compromised. Your PC is infected with an infostealer." Steam does not do this. They allow the bot to burn through the entire friend list, infecting hundreds of new machines.
| TIMESTAMP | STEAM_ID64 | JWT_HASH | ATTACK_VECTOR | STATUS |
|---|
Demonstration of how a single compromised JWT token propagates through Steam's P2P friend network infrastructure.
Step 3. Global Damage (Corporate Collapse): This is where the main threat to the entire internet lies. Because Steam does not notify the user of the session interception, the person continues to sit at their compromised computer. If an alert had come, they would immediately wipe the OS. But Steam stays silent. That same person, on that same infected PC, continues to log into their corporate VPN, work email, and crypto wallets.
By ignoring session interception anomalies, Steam is not merely allowing the theft of in-game pixels. They are concealing from the user the fact that an infostealer is running on their system. This corporate blindness directly leads to massive corporate data breaches and infrastructure compromises, with damages running into millions of dollars.
Step 4. Exposing the Lie: The Lawyers' Data
Valve frequently hides behind the claim that they allegedly have "no technical capability" to track complex theft chains, or that "the user is at fault" for the compromise. But the case of the improperly redacted documents from their European lawyers (Taylor Wessing) [9], which we uncovered, proves the opposite.
In the unredacted GDPR request data [10], we clearly saw: Valve logs absolutely everything. They collect deep telemetry on hardware, IP addresses, device change histories, and behavioral patterns. They know the moment an account is hijacked. They see infostealers and spam-sending software running. They have all the tools for automatic blocking and issuing a Red Tag. Their inaction is a conscious corporate choice.
Step 5. Real Motives: Why This Benefits Valve
The lie about "technical impossibility" covers a cold economic calculation.
Support Cost Optimization via Scripts: Blocking a suspicious session means receiving a ticket from a user that needs to be processed. It is more profitable to simply ignore the incident. Steam relies on primitive scripting logic that scammers know perfectly and exploit. Russian-language support staff likely read these algorithms, but not to patch vulnerabilities. Issuing a Red Tag requires no man-hours if the algorithm is properly configured. Previously, a Red Tag could be removed automatically by simulating recovery from a new IP via a VPN. Now, ticket processing times are deliberately dragged out to discourage users from contacting support at all. And a support employee's ability to unilaterally close an unresolved ticket is the pinnacle of corporate cynicism.
The Money Cycle: A hijacked account that has burned through its friend list with spam will eventually receive a VAC ban or community ban. The victim (or their deceived contacts) registers a new account and buys the same games again. The corporation makes double revenue from a single user.
Symbiosis with the Shadow Market: The more accounts are stolen, the faster the gears of LZT Market and other hacker exchanges turn. This shadow activity paradoxically sustains the engagement of a huge audience (especially in regions where the cheat industry flourishes). And any subsequent transaction involving stolen skins still brings Valve their rightful commission percentage.
14. Trading in Lives: What Steam Is Actually Selling for $2
Valve claims to care about privacy. But what does an attacker who has bought a hijacked profile on the market for a couple of dollars actually receive? Steam will not show them the full credit card number, but it will hand over something far more valuable for social engineering.
With an active session (SSFN, cookies, or JWT), a hacker can pull the saved billing address in a few clicks — the victim's real first name, last name, city, and zip code. Through Steam's built-in data panel, they gain access to IP address history and links to other platforms (Twitch, Xbox). And if you look through the support ticket history, you will find archives of unredacted bank receipts and photos of activation keys from physical discs that users sent for verification.
But the most alarming aspect is the chat logs. We see how Valve has been carefully storing unencrypted archives of personal correspondence for years. In those archives, teenagers leave links to their real social media accounts, share their problems, send passwords for local servers and home IP addresses. By refusing to instantly reset hijacked sessions and by covering for infostealers, Steam effectively puts users' life histories and digital security on display in the windows of shadow markets.
14a. Digitální spis za 1,60 $: Jak Steam prodává životy dětí na černých trzích
Když společnost Valve hovoří o bezpečnosti účtů, mluví o hodnotě inventáře. Skutečná cena ukradeného profilu se však neměří v pixelech. Pro miliony teenagerů není Steam jen obchod – je to jejich hlavní sociální síť. Uchovává jejich úspěchy, tajemství, vztahy i první lásky.
Když hacker ukradne účet a bezstarostně ho vyhodí na LZT Market za 150 rublů (přibližně 1,60 $), kupující nezíská jen přístup k hrám. Získá nešifrovaný archiv života dítěte.
Steam ukládá gigabajty osobních zpráv. Teenageři používají herního klienta k každodenní komunikaci – k vyznáním, hádkám i plánům do budoucna. Zaznamenané případy na stínových fórech ukazují uniklé archivy protokolů obsahující osobní a intimní fotografie nezletilých. Společnost Valve tento obsah nemoderuje, nepoužívá šifrování typu end-to-end a umožňuje útočníkům vše odčerpat jediným exportem.
Když teenageři hrají společně na soukromých serverech, zveřejňují své domácí IP adresy a otevřené porty přímo v chatu služby Steam. Tato data zůstávají po celé roky v nešifrovaných protokolech. Pro kupce ukradeného účtu je to hotová databáze pro DDoS útoky, cílený phishing, skenování domácí sítě – nebo swatting. Digitální hrozba se během několika minut stává fyzickou.
Když dítě přijde o svůj společenský život, podpora služby Steam vyžaduje fotografii CD-klíče od hry, kterou dostalo jako dárek před 10 lety. Společnost, která uchovává otisky hardwaru, geolokaci a roky telemetrických údajů o chování, nutí teenagera prohrabávat se skládkou odpadků kvůli kartonové krabici. To není bezpečnostní systém. Je to mechanismus záměrně navržený tak, aby legálně odepřel pomoc.
FTC za každé porušení
, na kterou se vztahuje zákon COPPA
přes LZT za celou dobu existence
- Ověřitelný souhlas rodičů před shromažďováním údajů o osobách mladších 13 let
- Jasné zásady uchovávání a mazání údajů
- Žádné sdílení osobních údajů dětí s třetími stranami bez souhlasu
- Minimalizace údajů — shromažďovat pouze to, co je nezbytné
- Historie IP adres, geolokace, otisky hardwaru — zaznamenávány od prvního dne
- Archivy soukromých chatů jsou uchovávány po celá léta bez mechanismu mazání
- Osobní údaje sdíleny s externí podporou (potvrzeno společností Taylor Wessing)
- Tokeny relace JWT obsahující uživatelská data unikají prostřednictvím napadených účtů na stínová fóra
16a. Průmyslové parsování: Open API společnosti Valve jako platforma pro vyhledávání obětí
Jak podvodníci věděli, na koho se zaměřit? Jak se děti staly oběťmi v průmyslovém měřítku? Protože společnost Valve nechala dveře své databáze dokořán otevřené.
Po celá léta provozovatelé stínového trhu používali specializovaný software (včetně nástrojů jako Hatler) k analýze uživatelů služby Steam v průmyslovém měřítku prostřednictvím otevřeného rozhraní API společnosti Valve. Podvodníci nastavovali filtry stejným způsobem, jakým maloobchodní platformy nastavují vyhledávání produktů:
aktivní farmu
operátora
zpráv
Společnost Valve tvrdí, že disponuje „pokročilými algoritmy“. Jak je možné, že pokročilý algoritmus nedokáže odhalit 300 000 účtů, které každý den odesílají miliony identických zpráv stejným cílům, ve stejnou dobu a ze stejných rozsahů proxy serverů? Nejde o selhání. Jde o záměrné ignorování. Veškeré skutečné škody na phishingové infrastruktuře způsobily nezávislé projekty, jako je PhishDestroy — nikoli multimiliardová korporace s naddimenzovaným bezpečnostním oddělením, které mělo chránit děti na její platformě. Společnost Valve děti nechránila. Poskytla podvodníkům pohodlný API, díky kterému je mohli najít.
15. "Efficiency" Built on Children's Tears: The Business Model of Total Indifference
Valve loves to boast about its financial analytics: hundreds of millions of dollars in profit per a couple dozen store employees. In the eyes of the tech industry, Gabe Newell often appears as a genius of optimization. But let's take off the rose-tinted glasses and call things what they are: this "efficiency" was purchased at the price of an absolute, cynical refusal to ensure the security of their own users.
Unlike public companies (such as Roblox or Tencent), whose market capitalization instantly collapses at the slightest scandal around child safety or data breaches, private Valve is accountable to no one. They have no board of directors. They do not need to reassure institutional investors. They have built an ideal printing press where the absence of spending on Trust & Safety and anti-fraud departments converts directly into personal billions for management.
The price of this "hyper-optimization" is millions of hijacked accounts, personal correspondence of teenagers leaked to the internet, a thriving shadow market, and complete impunity for scammers. Valve is not merely "failing to notice" fraudsters. It is economically beneficial for them to do nothing about it.
16. Steam API: A Corporate Toolkit for Hackers
Let's dissect Valve's lie about their alleged inability to control theft. If they wanted to, any support employee could go to a shadow market, take a link to a listed Steam account, and look in their own server logs at exactly which API key and from which IP address is right now evaluating that profile's inventory to generate a dump on the forum.
Valve would see a network of proxies and hundreds of API keys. Most of them have likely been obtained from previously stolen accounts. What should the corporation do? Revoke the compromised keys. But Steam does not do this. Why? Possibly because they fear catching "legitimate" services in the net — roulettes, illegal case-opening casinos, or third-party marketplaces where pixels are exchanged for crypto without AML procedures. This entire ecosystem exists in a gray zone, generating massive traffic while not being taxed. And Valve is entirely fine with that.
Steam's Terms of Service explicitly prohibit any automation. A reasonable question then arises: why does the official Steam API contain functions that are ideal for the automated hijacking of accounts (which takes milliseconds) or the mass linking of mobile authenticators?
Why does Steam allow virtual (VoIP) numbers from SMS activation services to be mass-linked to accounts? The solution for filtering such numbers is trivial — standard HLR lookups used by any normal service. But Steam does not do this. Perhaps, in the pursuit of impressive "record online" figures they love to brag about, bot farms are advantageous to them?
When a user receives a VAC ban [15] for cheating, the ban hits all accounts tied to the same phone number. But when hundreds of accounts are hijacked from a specific pool of VoIP numbers — Valve does not ban those numbers. Any normal service (Telegram, Netflix, Apple, Google) blocks junk or compromised phone numbers. But for Valve, security is an empty word.
17. Willful Blindness: A Legal Shield Made of Hypocrisy
Direct transactions and wallet top-ups from sanctioned territories (Crimea, DNR, LNR) continuing since 2021. Use of sanctioned gateways (Tinkoff Bank) via shadow intermediaries and region-switching. ToS self-certification clauses are legally void — Valve collects full hardware telemetry and traffic routing, meaning they practice Willful Blindness as defined under OFAC doctrine.
No immediate JWT/cookie session invalidation on anomalous geo-change. Steam's P2P infrastructure (chats, friend lists) used as botnet expansion engine. A $2 stolen log caused a corporate lockdown, $17M ransom, $100M+ total damage. Valve's silence is the enabling mechanism.
Taylor Wessing's improperly redacted GDPR DSAR response disclosed third-party PII including minors. Fines reach 4% of global revenue. Elite lawyers billing €1,500/hr leaking data in official responses proves the Data Protection Officer function is operationally nonexistent inside Valve.
Steam ToS prohibits all automation. The Steam API simultaneously processes millions of daily requests from LZT Market checkers validating stolen accounts. 79 employees for 500M users is mathematical proof security was never budgeted. Frozen inventory on banned bots (Shadow Confiscation) proves bans serve Valve's economy, not justice.
Support agents used system privileges to duplicate Dragon Lore/Dota couriers and fence them via Chinese exchanges. Sold trade-ban removals for crypto bribes. Steam Wallet and skin economy function as unregulated virtual currency serving criminal syndicates without KYC/AML. Forensic analysis links support staff crypto wallets to 100% AML-flagged addresses.
For 99% of the planet, Valve has built an impenetrable legal fortress: "All disputes shall be maintained exclusively in King County, Washington, U.S.A." — the perfect shield against their own users.
But the final clause reads: "If you are a consumer who lives in Russia, you may also seek a remedy with local Russian state courts."
Out of 195 countries, Valve makes an exclusive legal carve-out for the Russian Federation — a state under the heaviest international sanctions in modern history.
Crimea, DNR, and LNR are, per the Russian constitution, serviced by "local Russian state courts." If a resident of these occupied, sanctioned territories sues Valve in such a court — does Valve comply?
Valve recognizes the annexation and commits a direct OFAC sanctions violation.
Valve violates its own ToS and defrauds users — breaking the Russian laws it so desperately appeases.
Checkmate, Taylor Wessing. You drafted a rule that makes you either liars or accomplices to international sanctions evasion. Pick your poison.
Valve created an ecosystem where violating the rules (automation, VPN use, farming, bot-running) is a basic condition of the platform's survival. They hand hackers a perfect toolkit (open API), turn a blind eye to virtual numbers, but carefully keep in the rules a strict prohibition of all of the above.
This is not mere negligence. This is deliberate blindness (Willful Blindness / Deliberate Ignorance), constructed as a perfect legal shield. When a regulator comes to Valve, lawyers like Taylor Wessing [9] will show the ToS: "Look, we prohibit everything!" And when a robbed teenager comes to them, they use that same ToS to legally deny them help and avoid spending time on an investigation.
18. The Symbiosis of Intelligence Services, Steam, and Hacker Markets
Let's return to LZT Market. We have already established that Steam does not care at all about this platform. But another aspect is interesting. Over the course of its existence, this shadow forum has survived at least three changes in management, which, by indirect (but very obvious) indicators, are connected with the redistribution of spheres of influence among certain echelons of power in the Russian Federation.
During periods of management change (for example, during the era of the administrator Thomas), radical purges took place on the forum. Fraud schemes targeting Russian residents were banned (Avito scam, anti-cinema), the leaking of intimate photos of minors with personal data was strictly suppressed, the sale of VKontakte accounts was completely removed, and currently the sale of Telegram accounts registered on Russian numbers is prohibited. The forum is clearly moderated to avoid touching Russian citizens in ways that are critical.
But the situation with Steam is different. The market still freely sells Steam accounts belonging to Russian citizens who were infected by stealers. The listing description directly states: origin — stealer, country — Russia, balance — in rubles. This means that a Russian user caught a virus that drained not only their Steam but also, very likely, their email accounts and work credentials. And the forum passes this through without issue.
The question arises: does Steam cooperate with the same structures that oversee this market? Or perhaps Valve could influence their "partners" in Russia to stop the double standards and ban the sale of stolen accounts belonging to Russian citizens? Because right now Steam and the shadow market are operating in perfect symbiosis, as if they copied each other's policy of double standards and hypocrisy.
19. The Anatomy of Scamming: From Fake Windows to $300,000 Net Profit via Google Ads
Over the past 5-8 years, PhishDestroy has dissected virtually every scam scheme in the Steam ecosystem. We have seen infostealers that substituted authentication windows on the fly, intercepted SMS messages, and wiped inventories clean. We have seen the mechanics of trade offer substitution (API Scam) that remained "unnoticed" by Valve for years. Unnoticed — or too profitable?
We conducted continuous analytics on the bots of the largest phishing networks. Here is an example: in 2024, we recorded a massive pour via Google Ads [29]. Fraudsters substituted the displayed URL in ads with the original Steam domains. The purchasing was so aggressive that it outbid official advertising, monopolizing the top search results.
By our calculations, in just a few days of continuous operation, the scammers' net income amounted to approximately $300,000. And that is accounting for the discount when selling stolen skins on shadow markets and the tiny, cosmetic bans that Steam occasionally handed out. Yes, these are peak figures driven by the economics of that period, but the fact remains: Steam is an enormous feeding trough.
And while phishing is almost exclusively interested in CS and Dota (rather than other games), Rocket League, Path of Exile, Rust, and PUBG should not be forgotten. But here, Valve's corporate extortion enters the picture: strict NDA (Non-Disclosure Agreement) conditions that all developers are required to sign. A developer is not permitted to publicly disclose security issues, data breaches, or vulnerabilities in Steam without Valve's written approval. Even if this directly threatens their players. Mouths are sealed by contract.
20. The BlockBlasters Case: A Month of Blindness and the Lie About a "Hacked Developer"
The BlockBlasters case is not about ignoring pixel theft — it is about concealing actual criminal offenses.
Recall the recent incident with the game BlockBlasters [5], which only received public attention thanks to the late streamer Raivo Plavnieks [6]. This was a targeted attack on influencers: fraudsters contacted streamers, bought advertising, and asked them to launch the game directly from Steam. The victims' logic was understandable and fatal: "It's the official Valve store — there can't be an outright stealer in there." How wrong they were.
Steam support began receiving reports with ironclad evidence as early as September 2nd. The tickets contained ChainAbuse [7] complaints about stolen cryptocurrency and direct evidence of the scammers' open Telegram API embedded directly in the game's code. What did Valve do? It waited. For a month. The stealer games were peacefully downloaded from the store.
And then the corporation rolled out an excuse that insults the intelligence of any security professional: "The developer's account was hacked." Let's call this fairy tale what it is — a brazen lie to cover their own negligence (or complicity).
To release a game, a developer is required to pass Steam Direct KYC [22]: pay $100, submit their real name, address, and banking and tax details. The perpetrator was not an anonymous hacker from the dark web — their legal information, including a W-8BEN tax form [8], was sitting in Valve's database.
The myth of a "hacked developer who for some reason stayed silent for 22 days" collapses against the architecture of Steamworks. When a legitimate developer loses access to the publisher console, they create a ticket about stolen credentials. Publication rights for updates and builds are frozen within hours.
Only two options remain. Either the "developer" was originally a co-conspirator of the fraudsters (meaning Valve's vaunted KYC is a fiction). Or Valve deliberately ignored, for an entire month, the desperate attempts by the developer and dozens of robbed victims to reach support, while malware stealing crypto was being distributed through their official store.
In both cases, Valve is acting not as a victim of circumstance, but as the primary accomplice in a digital robbery.
21. Destroying Evidence: How Valve Cleaned Up the Crime Scene
But the most disgusting part of the BlockBlasters case is the ending. Interference with a digital crime scene.
On the record: Valve did not delete the infected game. Our forensic analysis of the C2 infrastructure proves the opposite. The scammers themselves deleted the malicious builds from Steam's servers on September 21st — precisely when their Telegram botnets were publicly exposed and criminal charges were becoming a real possibility. They applied a scorched-earth tactic to cover their tracks.
Valve's statement about "security measures taken" is pure fiction and shameless PR. They deliberately waited for the criminals to erase the malware from their own servers, and only then leisurely removed the now-empty store page, claiming credit for themselves. This is not solving a problem. This is complicity and obstruction of justice.
Valve was not protecting users. It was cleaning up the crime scene so that federal agents with a court order for distributing infostealers through their own data centers would not show up at their offices.
22. The Illusion of Action: Restricting Limits to Save Server Costs
When Valve does introduce some restrictions (for example, cutting friend-request limits), naive users think it is out of security concern. Nonsense. This whole story about limits is not about fighting scams — it's about plain and simple savings on server capacity.
Let's recall what started the spam apocalypse. Before the famous trade offer substitution script appeared, the platform was being abused by primitive automation. Armies of bots with female avatars were sending phishing links by the thousands. This junk traffic created enormous demand for no-limit accounts. We were tracking shadow markets: due to this spam boom, the price of a stolen account without a spending limit shot up from 25 rubles to a stable 150. And this insane demand for stolen profiles persisted right up to 2024!
Do you think Steam cut the invite limit from 100 to 30 to protect you from phishing? Think again. Valve logs everything: every click, every invite, every cancelled request. The automated scammer farms were generating millions of empty transactions per day, polluting Steam's internal databases and overloading the infrastructure. And what is most telling — Valve did not crush these limits on freshly registered throwaway accounts, but on fully developed no-limit accounts (including those with a VAC ban, since they technically count as accounts that have crossed the spending threshold). Valve cut the limits solely to reduce the load on their own servers, not for your safety.
Restrictions at Valve only appear where they need to protect their own servers. Your money is none of their concern.
23. The Inner Workings: Why Scammer Supervisors Benefit from Bans
Since we have dissected scam teams from the inside, I will expose one dirty secret that ordinary traffers never even suspected.
In all scam teams (where rank-and-file workers are promised 90-95% of stolen inventory), the supervisors (team coordinators) had a financial incentive to get a trade ban or Red Tag placed on their bots. Therefore, they deliberately did not replace compromised bots. If an account received a ban, the supervisor's share shot up sharply: instead of a measly 5% from the skin sale, they received between 15% and 20% of Steam's price for the inventory (not the market price!), simply by selling banned accounts with valuable skins to the Asian market. Chinese buyers purchased them in bulk to play with expensive items and private cheats. This is why a huge number of accounts with trade bans also carry VAC bans. The scam industry was feeding the cheat industry, and Steam was happily collecting the online numbers.
24. Steam Workshop: A Perfect Testing Ground for API Scam
Steam's absolute disregard for security is well illustrated by the Workshop incident. At some point, literally 2-5 scammers completely flooded the Workshop with phishing ads. How? They used intercepted web sessions of real users.
This was not a hijacking in the classical sense. The attacker simply opened a parallel session on your account via the Steam API, scanned the inventory, waited for you to initiate a trade, instantly cancelled it, and substituted an identical offer (with the same avatar and friend nickname) from their own controlled bot. All of this happened within a legitimate user session through official Steam endpoints.
And what did Valve do when the Workshop was drowning in phishing? They did intervene, of course. They issued Red Tags and banned the compromised accounts... but did so only after the inventories of those victims had been completely wiped clean.
Excellent work, Steam. Thank you for "saving" the account when there was nothing left in it to save.
Ironically, the price of these tokens on the black market has collapsed. If previously a valid SSFN file could go for around $3, today on that very LZT Market (where the curator of Russian-language Steam support, Nikita, is registered) the price list looks like a mockery of Valve's security:
"Buying and processing Steam Tokens (JWT). Fast check with proprietary software. Prices:
JWT token
CS2 Prime — $0.08 (no temporary or permanent bans)
OpenTM — $0.04 (open trading platform)"
Your account, your history, and your data are valued at 8 cents. That is all you need to know about the effectiveness of session protection in Steam.
The Illusion of "Technical Impossibility": The Fake Games Case
Support claims that returning stolen items is "technically impossible" or would "destroy the economy." The game spoofing incident proves otherwise.
The scheme was brazen: scammers uploaded dummy games to the Steam Store, creating items with names and icons copied one-to-one from expensive CS:GO and Dota 2 skins. During a trade, the victim saw a familiar Dragon Lore, completely unaware it belonged to a fake game. We remember this perfectly, as PhishDestroy was actively hunting and blocking these scammers at the time.
And what did Valve do when the very foundation of trust in the Community Market was threatened? A miracle occurred. The corporation, which for years had refused to help phishing victims, suddenly returned the real items to all affected users. The scammers were hit with such a carpet bombing that they howled on shadow forums for days: Valve issued hardware bans (HWID) and blanket-banned shared IPs so harshly that entire scam syndicates went deep into the red.
Moreover, Steam rolled out a massive security update in a matter of days. Suddenly, they found the resources to implement everything: trade holds, new verifications, developer deposits, massive red alerts stating "This game has never been played by you," and warnings about suspicious disparities in item values.
It turns out they can. They know perfectly well how to track transaction chains, roll back trades, and build a complex warning architecture. But they only do it when they feel a direct threat to their own business model and the credibility of their marketplace. If you are stripped naked by a standard stealer, you will simply receive a boilerplate reply that "Steam policy does not provide for item restoration."
79 Employees: An Architecture of Matches and Acorns
To fully grasp the "seriousness" of the platform's day-to-day security, consider the recent API bug that lived in production for two whole days. Anyone with a basic script could send a simple request and spam system notifications directly to absolutely any Steam ID, completely bypassing all privacy settings.
Two days of a gaping hole in the API allowing anyone to ping millions of users. Indeed, 79 employees for a multi-billion-dollar global platform is clearly enough. Why invest in a functional QA and security department when you can just write a Terms of Service agreement that blames the user for everything?
25. Infrastructure as a Service: Scam-as-a-Service (SaaS)
To give you a sense of the scale of commercialization spawned by Valve's inaction, look at a typical offer from a modern phishing team. These are no longer teenagers with broken scripts. This is a full-fledged SaaS business with fierce competition. While we were mercilessly blocking their domains and forcing them to lose money on infrastructure, they switched to providing free domains to their "workers" to maintain volume:
"Our project combines 3 in 1: Phishing (logs go to you), MaFile (5% commission), Substitution (API Scam — 80% to you). Only we offer: Auto-sale of logs on LZT, MaFile removal with a single code, Browser for substitution, Free domains and a multitude of fake templates."
Valve only fixes what becomes uncontrollable, or what affects geolocations they are afraid to disturb (USA, Japan, South Korea). Steam could see the spam, see the no-limit accounts, and sometimes even banned phishing domains (often when they were already dead). If the corporation saw a domain, it also saw the network of accounts distributing that domain. Given that the farms operated through cheap shared proxies (using the scheme of 1 server and 100 IPs per 1,000 accounts), blocking the entire botnet could have been done with a single SQL query. But Valve did not do it.
26. Geopolitical Hypocrisy: The Steam Economy Laundromat
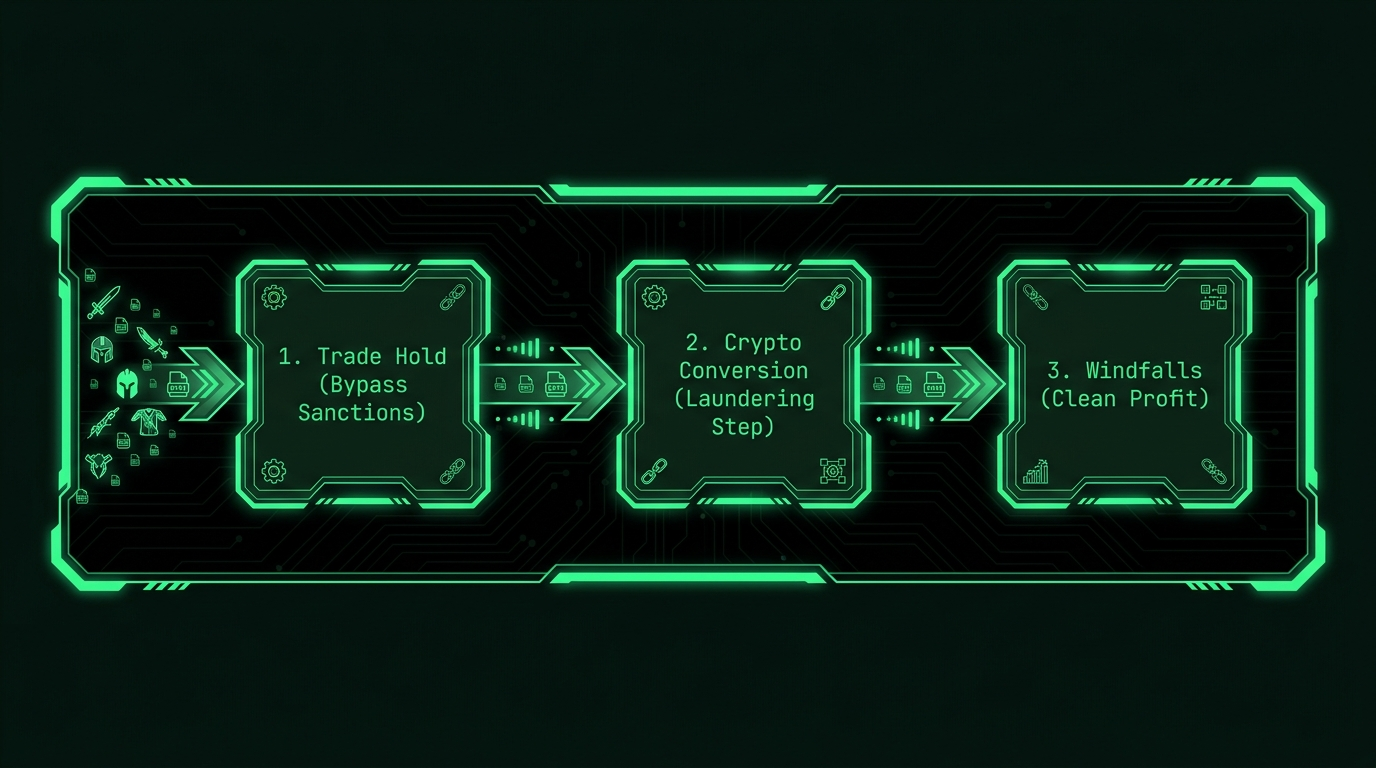
Valve's tolerance for the gray CIS economy spawned yet another monster — the market for illegal balance top-ups and region-switching. When Valve officially closed direct top-ups for Russia, it simply turned a blind eye to the flourishing of shadow intermediaries. Much more convenient that way, right?
The "region-switching" service (to Turkey, Kazakhstan, or Argentina) was sold by the millions. On just one platform (like FunPay) [24], more than 500,000 transactions have been recorded from several large sellers. And there are hundreds more Telegram bots and forums. This top-up industry has become deeply intertwined with the laundering of money from phishing and crypto scams (the buying up of seed phrases).
What is Valve's logic? Do they genuinely believe in the mass migration of millions of teenagers from a sanctioned country? Or do Russian funds, passed through a Kazakhstani proxy and a stolen inventory, simply "smell different"? Valve does not care about sanctions and compliance. The main thing is that a 30% commission from every transaction reliably drips into their bank accounts, while lawyers churn out boilerplate letters about the "impossibility of technical intervention."
27. Corporate Benefit and Violation of Their Own ToS
Steam is an ecosystem that thrives on total violation of its own rules, and Valve knows this perfectly well. The Terms of Service (ToS) clearly state: extracting any commercial benefit on the platform is strictly prohibited.
Now let's look at reality. Selling stolen accounts, skin trading, bot farms for farming collectible cards, Level Up services (profile leveling), selling keys, and of course, balance top-up services for sanctioned regions. All of this is direct commercial benefit. And this is surreal: a platform that formally prohibits commerce is home to industries with multi-million turnovers. Valve (or their reliably NDA-protected Russian-language outsource) has abstracted itself from its own rules, applying them exclusively as a tool to punish those who fall out of favor or to protect infrastructure.
28. The Support Syndicate: Why Valve Cancelled Item Returns
When Valve justifies its refusal to return stolen items to users (hiding behind fighting inflation or "duping"), they are blatantly lying. The reason Valve permanently freezes assets on banned bots, pocketing them into their bottomless account, is not protection of the economy. It is an attempt to recoup operational losses inflicted on them by their own employees.
Historical fact: support agents (including cheap outsourced workers often mistaken for volunteers) were directly integrated into the shadow economy of Steam. Using their system privileges, they turned technical support into a corrupt cartel.
Industrial Duplication of High-Tier Items: Support employees were mass-generating copies of the most expensive items in the game (Dragon Lore in CS:GO, rare Legacy couriers in Dota 2) under the pretext of "returning stolen inventory to a user." This "returned" inventory was then fenced on Chinese exchanges for real money.
Selling Unbans: Support was selling the removal of Red Tags (KTs) and trade bans from the profiles of major scammers. For bribes (in crypto or skins), fraudsters were given the green light to cash out assets worth tens of thousands of dollars.
Upon learning the scale of the corruption, Valve's management was furious. They permanently abolished the policy of returning stolen items, cutting support's manual access to item generation. But those punished were not the corrupt employees — it was the users. Children and gamers around the world are paying with their money for Valve's failure to control its own staff.
The "Little Tyrant" Syndrome and the Fall of the Volunteer Police
In addition to official support, Steam had a second branch of power — a volunteer trade police integrated with databases like SteamRep [12]. They held enormous informal influence over the platform's economy and the fates of traders. And they turned out to be no better than the outsourced staff.
The volunteers devolved into a closed, corrupt caste of "faceless shadow authorities." They suffered from a classic "little tyrant" syndrome: they buried traders they disliked, banned users who discussed vulnerabilities, and issued "free passes" to friends.
When logs surfaced proving that SteamRep [12] admins were taking bribes to remove "scammer" labels and were running cover for massive bot networks laundering stolen skins, Valve's trust collapsed completely. By 2022, Valve had expelled the last volunteer moderators, replacing them with rigidly scripted outsourced workers.
29. The Price of "Efficiency"
Valve boasts the highest profit per employee in the industry. But what is the cost of this profit?
This efficiency is built on denying help. On threatening phishing victims. On closing tickets. On suppressing the truth that Steam is not so much a gaming platform as a global crypto laundromat and distribution hub for infostealers.
While Valve's management considers itself geniuses of business optimization, fighting in court for the right to sell adult visual novels, their platform is daily chewing through the data, money, and safety of real users. The era of duping has long been dead, but Valve continues to use it as an excuse to legally appropriate the property of robbed users. There is no justice in Steam. There are only scripts, outsourced workers, and an endless thirst for profit.
30. Hypocrisy at Every Level: The Corporate Ethics of Valve and Taylor Wessing
If it seems to you that I am exaggerating by mentioning Taylor Wessing (Valve's lawyers) in the context of their internal harassment lawsuits — believe me, it is not a joke. The court case was lost, but the point is not the verdict — it is Taylor Wessing's strategy. They demonstrated not professionalism, but a dirty game of attrition and deliberate delay. Google how many years the case dragged on from the time of the incident at the elite ski resort.
But when it comes to Valve itself, even more questions arise about their vaunted ethics. They have a corporate Welcome Book where they call themselves a "family." All warm and cozy. But when this "family" is rocked by scandal, Valve acts with maximum ruthlessness. Recall the harassment of a transgender employee in support, or the story of Jess Cliffe [13] (the co-creator of Counter-Strike, who had worked at Valve almost since its founding). The man was thrown out of the company without a court verdict, on the basis of accusations alone. Valve, which generates millions by covering up scams, suddenly became afraid for its reputation? The logic is absurd: a company allows millions of dollars to be stolen from its users but instantly distances itself from the person who built this business for decades, just to appear "clean."
As for the lawyers at Taylor Wessing — let's be honest. You pride yourselves on your "centuries-long history," but on your Instagram, you are running a race in support of Pride. Make up your mind: do you honor the history of your Nazi founders who sent gay people to concentration camps, or are you a modern progressive company? This is corporate scamming. You want to appear as ancient aristocracy while having effectively merged into the ecstasy of contemporary hypocrisy. And yes, you have taken on the defense of Russian oligarchs in cases where your reputation was openly screaming: "You are not hired where people are innocent."
31. The Roadmap of Coming Leaks: What Valve Should Prepare For
This is not the first and not the last piece from PhishDestroy about Valve. I will not play cat and mouse with their lawyers — their time, judging by their rates, costs $3,000-$5,000 for reading a couple of paragraphs. Don't waste the money; hire decent support staff instead of a Russian outsource that reads from scripts.
Here is what comes next. My roadmap for upcoming investigations:
Evidence Base on GDPR Impotence: I will publish the originals of the legal boilerplate letters and improperly redacted documents, proving that Valve systematically violates regulations and discloses the confidential data of underage users. I will show the entire chain in which I was already the fifth person to have gained access to someone else's personal data (including individuals with Russian passports). This is direct proof of their lies about storage conditions and mythical "encryption."
NDA Violation and the Dirty Underbelly of Steamworks: We have data from at least two developers whose non-disclosure agreements (NDAs) we will be happy to violate (we never signed them). We will expose the open chaos in update moderation and cases involving locker content that Valve prohibits from being made public under threat of game removal.
Crypto Failures and Money Laundering: How Valve's "Geniuses" Lose Their Millions: Since Valve loves to brag about the billion-dollar profits of their employees, we, as PhishDestroy, will venture into crypto territory. We will conduct a forensic financial analysis of the wallets belonging to elite support staff (early Bitcoin investors) and show how these "professionals," bringing Valve billions on the tears of robbed children, themselves invested in scams and had their addresses flagged with 100% AML risk scores.
The Strange Love of Russia and Who Is "Nikita": We will examine the phenomenon of Valve's tolerance for the CIS region. How does a person with no formal employment become a support supervisor simply because they once created a fan community for Half-Life? We will expose the loopholes and sanctions bypass mechanisms for developers from a terrorist state, as well as direct balance top-ups from the DNR/LNR and Crimea that have been functioning since 2021 and continue to this day.
32. Conclusion
I have no desire to dedicate my life to writing texts about Steam. It is run by an audience of children, scammers, and Putin cultists on the platform (in the form of the Russian outsource). Volunteers are mired in corruption up to their ears. If Gabe Newell considers himself a genius of the gaming industry, then perhaps it is my destiny to be the bastard who writes the truth into history:
Gabe is an excessively petty and greedy monopolist who legalized the theft of money from children. And the promised private jets and vacations from their employee handbook are just colorful pictures designed to keep workers in corporate bondage.
All of this is written for history. For the Web Archive. And for those regulators who will eventually come to dismantle this empire of impunity.
33. Anatomy of the ToS: Corporate Schizophrenia and Legal Cynicism
Let's dissect Steam's Terms of Service (ToS). We will cover at least 25% of this document to show that this is not a legal contract — it is a lie constructed to allow the platform to steal from children while avoiding accountability.
Here is a quote from their rules: "You may not use any scripts, bots, macros or other automated systems ('Automation') to interact with Content and Services on Steam..."
We will analyze this clause in detail in the next part. Spoiler: Steam itself created an API that is used exclusively for automating theft, bypassing limits, and managing bot farms. The platform wrote a rule that it simultaneously allows to be violated on an industrial scale.
And here is another gem of corporate cynicism: "You acknowledge that Valve is not required to provide you with notice prior to terminating your Subscription and/or Account."
This is a lie. Under normal legislation, that is not how it works. But the platform shields itself from everything. Valve's position sounds like this: "We steal from children, we violate sanctions, we allow infostealers to infect your PCs, but if anything — you are at fault, and we will take your account without explanation."
They love to say that "the community decides everything." But for some reason, when it comes to legal accountability, the community suddenly becomes a powerless piece of meat.
33a. Iluze v soudní síni – Jak společnost Valve využívá technologickou neznalost soudů
Pokaždé, když se regulační orgány nebo generální prokurátoři pokusí společnost Valve přivést k odpovědnosti za loot boxy a neregulované hazardní hry, elitní právníci této společnosti použijí stejný trik. Vstoupí do soudní síně s hromadou baseballových karet nebo balíčkem karet Magic: The Gathering a prohlásí: „Vaše Ctihodnosti, naše virtuální předměty jsou totéž. Jde pouze o nevinné sbírání, které se přesunulo do digitálního světa.“
Tato obhajoba funguje přesně z jednoho důvodu: právníci společnosti Valve odborně zneužívají technologickou negramotnost stárnoucího soudnictví. Ale tato firemní lež se zhroutí v okamžiku, kdy kompetentní státní zástupce přesune diskusi od „hraček“ k finanční logistice a kriminální infrastruktuře.
Pokud jsou skiny „jen baseballové kartičky“, položte právníkům společnosti Valve pod přísahou tři otázky:
Můžete vstoupit na darknetové fórum a koupit ukradená čísla sociálního zabezpečení v USA, programy na krádež dat nebo firemní přihlašovací údaje k VPN výměnou za vzácného Charizarda? Ne. Žádný hacker nepřijímá karton. Ale skiny z CS2 přijímají každý den. Inventář na Steamu funguje na kriminálních trzích jako absolutní digitální fiat měna – slouží k nákupu osobních údajů z reálného světa, malwaru a přístupu k infrastruktuře.
Zkuste převést baseballové kartičky v hodnotě 1 000 000 dolarů kartelu nebo subjektu, na který se vztahují sankce, na okupovaném území. Budete potřebovat kurýry, celní úřady, odhadce a několik týdnů času. V ekosystému společnosti Valve ten samý milion dolarů ve skinech překoná celou planetu během několika sekund – a to bez jakýchkoli bankovních blokád, daňových kontrol a systémů monitorování transakcí.
Sběratelské kartonové předměty nemají otevřenou burzu (API) propojenou se stovkami tisíc obchodních botů. Nemají globální knihu objednávek, kde se ceny určují algoritmicky s přesností na cent. Společnost Valve nevytvořila album na samolepky – vytvořila vysoce likvidní finanční burzu, propojenou s bránami pro kryptoměny, bez jakéhokoli ověřování totožnosti (KYC).
34. Sanctions, Terrorism, and Double Standards
A funny question for this corporate hypocrite. The rules state: "If you are a consumer residing in Russia, you can also seek legal protection in local Russian state courts."
Does the court of annexed Crimea count as a Russian court? Or shall we wait for Roskomnadzor — with which Steam integrates so cozily — to answer?
And here is a clause that provokes a roar of laughter: "You agree to comply with all applicable import/export laws and regulations. You agree not to export Content... to any countries that support terrorists... You represent that you are not in such a prohibited country."
So when Valve accepts money directly from accounts registered in zones subject to international sanctions (and we have gigabytes of screenshots and direct proof of transactions from Crimea, the DNR, and LNR dating back to 2021) — it is not Valve violating sanctions. It is the user's fault! The platform quietly edited its ToS over the last six months, shifting all responsibility onto users.
Valve, were you compelled to remove mentions of Russia's allies (Cuba, Iran, Syria) and prohibited from speaking ill of them, or did you calculate the scale and the sum that came directly from those places? If a terrorist state is coercing you into any actions — tell someone, do not be afraid. There is no need to violate current US law because of threats that they will pirate your content; it is not worth that risk. They are terrorists, and you are a US company. If you are being persecuted or blackmailed, contact the FBI Seattle Field Office at +1 (206) 622-0460 [16] or IC3 [17]. I am also confident that specialists from CISA [18] could help you: given the scale and reach of your sphere of influence, it is significant even by US standards.
Since you are removing direct sanctions rules and changing the text — this is a very alarming signal. I am not joking: if you do not trust the agencies named above, then here you will certainly receive help at the highest level — at DOJ NSD [19]. We, for our part, will conduct additional analysis and free consultations with certain specialists, and may also be compelled to report this where appropriate (or nowhere). But this is no joke at all — it is serious.
You removed explicitly enumerated countries from the rules and shifted responsibility onto users. At the same time, you run analytics: there is a tracking pixel on the registration page, and you see the real number of clicks through to the agreement. Nobody reads it, because you have calculatingly disguised it as a question confirming that the user is over 13 years old (the link to the agreement is embedded there as well). Modern society — children and teenagers — has ADHD, and this is a scientifically proven fact: check the data. They do not finish reading text. I, for example, saw the clause about being over 13 and that was it — I looked no further. This is direct manipulation on your part, as is the rewriting of the agreement regarding countries that have consistently appeared on sanctions lists.
Your revision directly indicates that your company's attitude toward those countries (or money from them) has changed. This is a very strange change. Most likely, there is already a problem, or you are complying with Russian courts, and this is one of their non-public demands — such as the banning of certain users, etc., which could undermine belief in the rightness of their terrorist acts on the territory of another country. Or are you simply prostrating yourselves before the Russian government, fulfilling their direct requests to ban undesirable users? I will show you prior versions of your ToS. You may change them as you wish, but these pieces of paper are worthless when it comes to the direct violation of US laws and the sponsoring of terrorist economies.
35. Blackmail and the Scorched-Earth Strategy
Fair warning in advance: any attempts by Valve or their attack dogs from Taylor Wessing [9] to make contact will be treated as pressure and obstruction of the investigation.
Do not try to send us an NDA. PhishDestroy is not registered on your garbage heap. We did not check the box in your clever agreement (which you treat exclusively as confirmation that a child is over 13 years old, so that you can legally rob them).
If your lawyers try to accuse us of "extorting billions of rubles" or "defaming the holy reputation in the interests of a North Korean competitor, Steam 2.0" — good luck. All of our investigations, evidence, and proof are duplicated to independent nodes (including servers at an American university) and the Web Archive. This is not a conflict. This is a statement of facts.
36. The Scam Factory: Carding, Fake Documentation, and Data Theft
You think scamming on Steam is only about stolen passwords? You have no idea of the real scale.
Fake Documentation (Social Engineering): When an account is stolen, support demands the first CD key from 10 years ago. The child doesn't have it. But the scammer from Russian outsource does. Fraudsters commission the fabrication of fake receipts and keys on shadow forums. We have collected over 200+ proven instances of successful fakes that Valve's support staff happily "swallowed," handing the account over to criminals.
Data Theft: More than half a million accounts (including EU citizens) have passed through the shadow market LZT. Steam concealed the fact that their PCs had been infected with stealers. The platform de facto leaked to hackers personal data, correspondence, IP addresses, and home network information.
Industrial Carding: If Valve's lawyers understood how carding works on their platform, their hair would turn white. Issuing a Red Tag for carding while leaving items purchased with stolen credit cards on the account is a remarkable money laundering practice. Do you know who was actually competing with the Prince of Saudi Arabia for the highest Compendium level in Dota 2? We will tell you about that too.
36a. Hrací automat: Jak společnost Valve vybudovala největší neregulované kasino pro děti na světě
Hazard se skiny není vedlejším účinkem platformy Steam. Je to předvídatelný a ziskový důsledek záměrné architektury společnosti Valve: otevřené obchodování s API, absence ověřování totožnosti (KYC), virtuální předměty se stabilní hodnotou na sekundárním trhu a naprostá regulační slepota. Výsledek: odvětví s ročním obratem přes 1 miliardu dolarů, kde skiny z CS2 pro děti fungují jako žetony v kasinu – bez ověření věku, bez souhlasu rodičů a aniž by společnost Valve kdy podala jediné hlášení o podezřelé transakci (SAR).
se skiny v době špičky
každého vloženého skinu
věku vyžadované službou Steam
skin
pro CS2 (vylosovaný ve hře)
tržní hodnotu
(API na Steam)
přijímá skin
jako vklad
Stránka si skiny ponechá
.
15 % z každého
převodu skinů
Žádný krok v tomto řetězci nevyžadoval zásah společnosti Valve. Steam API sloužil jako podpůrná infrastruktura. Ekonomika skinů představovala měnovou vrstvu. Společnost Valve obě tyto složky navrhla, zpeněžila a nepodala žádné hlášení o podezřelých transakcích (SAR), nezavedla žádné věkové omezení a nezaslala žádné varování rodičům.
Víme, jak vypadá boj. Bojujeme proti phishingu. Kdybychom proti němu bojovali tak, jak Valve „bojuje“ proti hazardu, vůbec bychom nebojovali. Takto to ve skutečnosti funguje.
Vezměme si csgoempire.com/roulette — platformu, o které společnost Valve teatrálně prohlašovala, že ji omezuje. Aby přihlášení přes Steam OpenID fungovalo, musí být doména povolena prostřednictvím jejich API. Společnost Valve může blokovat primární doménu. Co tedy udělá provozovatel hazardní stránky? Zaregistruje paralelní přihlašovací doménu. Skutečný autentizační endpoint služby Steam, který v současné době používá CSGOEmpire, směřuje přes:
Tato doména je v provozu již více než 6 let. Už samotný její název – csgoempirelogin2 .com – vám prozradí vše: byla zaregistrována výhradně za účelem obejití omezení, které společnost Valve uvalila (nebo předstírala, že uvalila) na primární doménu. Číslice „2“ představuje právě toto obejití. Doména byla zakoupena za účelem obcházení zákazu. Stejně jako právníci společnosti Valve – nevymáhají, pouze předstírají vymáhání.
Jen v roce 2026 byla tato doména nahlášena do systému hlášení PhishDestroy více než 20krát. To znamená, že ji uživatelé nahlásili – na PhishDestroy a téměř jistě i na podporu služby Steam. Steam o tom ví. Steamu je to jedno. Infrastruktura pro hazardní hry nadále funguje. Společnost Valve zakazuje boty (zisk jí jde do kapsy), vydává veřejné prohlášení o „ochraně komunity“ a pak neudělá nic s obchvatovou doménou, která je aktivní již od roku 2020.
Stejný vzorec platí i pro jiné platformy, které společnost Valve teatrálně „uzavřela“. PhishDestroy zablokovala CSGOFast a další, u nichž jsme měli důkazy. Jiné možná zůstaly nedotčeny. Ale infrastruktura – domény umožňující obejití přihlášení, klíče typu „API“, sítě botů – stále funguje, protože obchodní model Steamu vyžaduje, aby se skiny pohybovaly, a ne ležely v uzavřených inventářích, kde nevytvářejí žádné provize.
Zákaz botů v roce 2023: Není to trest. Je to mechanismus zisku.
V roce 2023 společnost Valve zablokovala desítky tisíc botových účtů provozovaných hazardními weby – CSGOFast, CSGORoll, Stake.com (pro skiny) a další. Herní tisk to oslavoval jako „tvrdý zásah“ společnosti Valve proti hazardu. Tato interpretace je fakticky nesprávná.
- Botové účty – nové se objevovaly během několika dní
- Dočasné narušení automatizovaných toků vkladů
- Čistá finanční ztráta: téměř nulová. Přesunuli se k novým metodám.
- Děti, jejichž skiny byly v botách v době zákazu
- Zásoby zabavené společností Valve — nevrácené původním majitelům
- Společnost Valve si ponechala všechny skiny ze všech zakázaných botů: zisk z likvidace
- Dítě, které vložilo svůj skin AWP | Dragon Lore jako sázku: nedostalo nic zpět
37. Epilogue: A Training Ground for Cybercrime
Since, according to Valve's perverse logic, virtual items "have no real value," the theft of $10,000 worth of skins is not legally theft. This is a perfect gray zone.
But Steam is not merely ignoring theft. Steam has raised an entire generation of cybercriminals. Today's creators of infostealers and crypto scammers started out stealing inventories in CS:GO. Gabe Newell's platform became the primary incubator for global cybercrime, teaching underage hackers the main rule: you can steal on the internet with impunity, as long as you pay the corporation's commission.
Everyone will answer for their actions. Even if they hide behind a Terms of Service they wrote themselves. Expect part two.
38. Sanctions, Censorship, and Steam's Stockholm Syndrome
These are not dark web links. These are discussions and official Guides hosted on Valve's own servers, indexed by Google and Bing, publicly accessible to non-logged-in users. Valve moderates this platform. Every post is reviewed. None of these were removed.
Steam ToS explicitly bans VPN use. At the same time, Steam's own servers host thousands of guides on how to change region via VPN. Under FTC Section 5 (UDAP) this is a deceptive practice. Under Estoppel doctrine, Valve has waived the right to enforce this clause after systematically ignoring it for years — meaning they cannot selectively apply it to deny help to theft victims while allowing bot networks to run freely. Under OFAC Willful Blindness doctrine, hosting and indexing this content is not passive — it is facilitation.
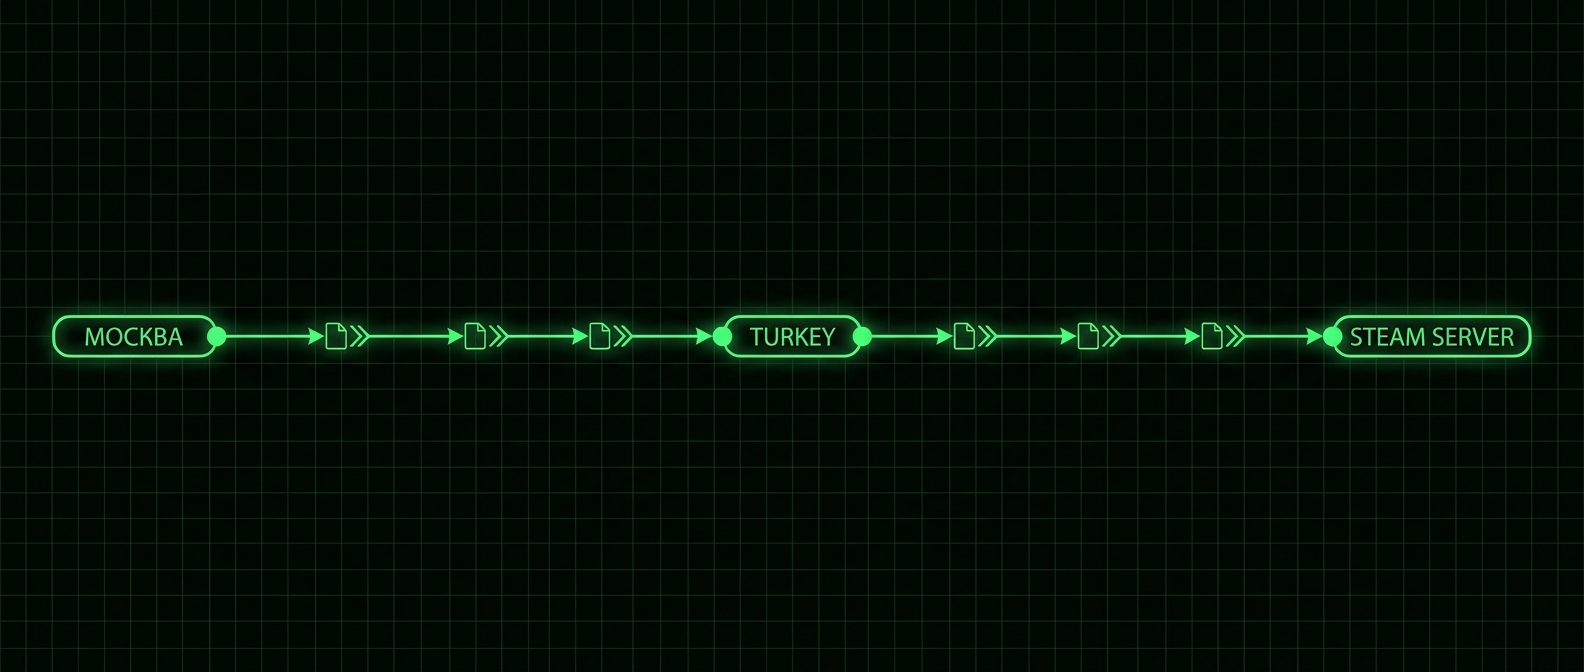
Steam's hypocrisy reaches its apex when the subject turns to geopolitics. You may laugh at the fact that a corporate monster generating billions has simply gotten confused in its own algorithms. But let's look at the facts.
In 2022, as the sanctions noose began to tighten, developers from Russia rushed en masse to bypass the blocks. And where did they find the most detailed guides on evading international OFAC sanctions? Right inside Steam itself. In the official Community, there are step-by-step instructions on how to use a VPN (which is formally prohibited by the ToS) to change regions and withdraw money to sanctioned banks (such as Tinkoff Bank) [25].
Here is a quote from an official (or, at least, Valve-moderated) guide that perfectly describes their position: "We kindly ask you to maintain professionalism and refrain from commenting on political matters... Such statements will be removed, and the most active violators will lose the ability to leave comments..."
Translate from corporate speak into plain language: Valve prohibits calling the war a war. Valve prohibits calling the aggressor country a terrorist. Aggressive moderation (hello, Russian-language outsource) scrubs any criticism, protecting an audience that is killing people in a neighboring country from "political disputes." This is not mere negligence. This is complicity in censorship, driven by fear of losing revenue from the CIS market.
I formally invite Valve's management and their vaunted lawyers to come to Mariupol or Melitopol, to see from what exactly "political disputes" they are so carefully shielding their Russian-language community.
39. Sanctions Bypass as a Platform Service
These are not dark web links. These are discussions and official Guides hosted on Valve's own servers, indexed by Google and Bing, publicly accessible to non-logged-in users. Valve moderates this platform. Every post is reviewed. None of these were removed.
Steam ToS explicitly bans VPN use. At the same time, Steam's own servers host thousands of guides on how to change region via VPN. Under FTC Section 5 (UDAP) this is a deceptive practice. Under Estoppel doctrine, Valve has waived the right to enforce this clause after systematically ignoring it for years — meaning they cannot selectively apply it to deny help to theft victims while allowing bot networks to run freely. Under OFAC Willful Blindness doctrine, hosting and indexing this content is not passive — it is facilitation.
Steam states that users are obligated to comply with US export laws. But at the same time, the platform serves as the primary hub for publishing manuals on how to bypass them. The guides have been up for years. Switching region to Kazakhstan or Turkey to bypass blocks has become not just a widespread phenomenon, but an industry standard that Valve silently approves.
Why? Because Steam's policy goes like this: "The user ticked the box saying they are not a terrorist and are not under sanctions, so there are no claims against us."
But we will go further. If anyone has raw analytical user databases from Steam, we are ready to put them to work. We will find lists of accounts that have bypassed blocks to purchase games from publishers who officially withdrew from Russia (such as the creators of STALKER 2 [30] or GTA [30]). We will pass this data directly to those publishers, along with the question: "Are you aware that Steam is sabotaging your exit from the market and openly providing users with loopholes to purchase your games in rubles through a chain of intermediaries?"
We already have contacts with insiders bound by NDA. We know of a case where Valve unilaterally terminated cooperation with a developer and simply appropriated their money, covering it with a non-disclosure agreement. But we did not sign any NDA. We will tell everything.
40. Where Are the US Regulators Looking?
The main question: does Valve understand what OFAC [20] (the US Office of Foreign Assets Control) is?
When a platform allows mass sanctions evasion via VPN (from minor purchases to fund withdrawals by developers); when it allows money laundering through shadow skin markets while turning a blind eye; when the platform's moderation integrates Roskomnadzor [23] restrictions and removes "undesirable" posts — this is no longer the jurisdiction of a terms of service agreement. This is the territory of direct violation of US sovereignty and laws.
Expect the continuation. PhishDestroy will not stop until this architecture of lies collapses. All proof and links are saved. And no Taylor Wessing [9] will intimidate us.
For Valve, geopolitical differences are not just a matter of regional pricing (where Valve decides who is wealthier and who is "Russia"). It is also about laws, rules, and control. Here is a perfect example — the VPN geolocation is visible at the top. So the New York prosecutor simply doesn't use a VPN. But I think she could have never imagined that Valve is such a hypocritical rat, operating completely different rules and controls depending on where you are accessing the platform from.
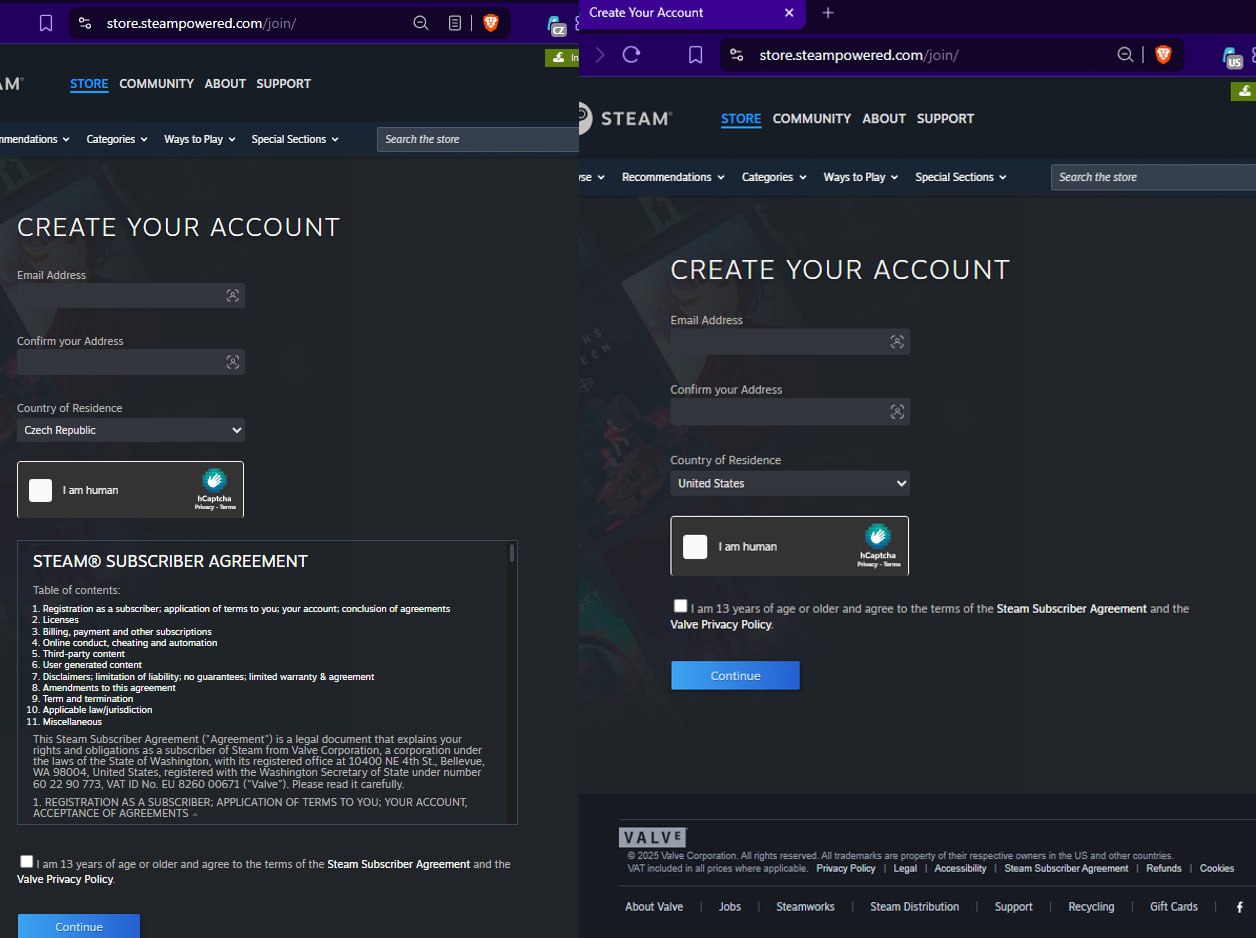
Given all these factors, our recommendation is simple: do not yield to Steam's legal framing. If a user is an actual terrorist, they are under no obligation to testify against themselves. It is Steam's absolute legal duty to verify the origin of these funds, rather than granting the user the absurd privilege to self-certify whether they are a terrorist or not. This logic applies directly to Valve's territorial operations. If Valve has suddenly forgotten how the internet works — and its direct bans on VPNs — let's follow their logic: a terrorist from Crimea, Cuba, or Syria goes online to launder money. This user does not know English and has zero intention of reading the convoluted legal nonsense in the user agreement. But they are definitely over 13 years old (in fact, they might have already killed 13 people). Does the platform seriously think it can shift the legal liability onto the terrorist to decide their own status? By shifting this responsibility, Valve is making a direct legal statement: they automatically recognize everyone as a "non-terrorist" on their end. Meanwhile, the actual terrorist, who completely ignores the boilerplate text disguised as a simple age check, simply launders their money using a sanctions-bypass guide hosted directly on Steam's own community platform. Outstanding compliance, isn't it?
Are you out of your minds? You fed the personal data of minors to a person with a grievance, essentially saying, "Here is the cause of your problems, fetch." If that individual ever acts on that data, the blood and legal responsibility rest entirely on the hands of Valve and Taylor Wessing.
The IPFS Dead Man's Switch
We have vastly more information than what is published here. If Steam, Taylor Wessing, or any affiliated entity attempts to take aggressive action against our project, we will not waste time in court. We will execute a full, raw data dump on the InterPlanetary File System (IPFS).
Yes, releasing unredacted data will have consequences. Yes, it will mean the absolute death of the phishdestroy.io domain and its massive traffic. Let us save your lawyers some time: We do not care. The domain was created as a joke to mock the Steam scammers who claimed we "didn't even have a website." We do not chase reputation, we are not trying to be corporate heroes, and we are not afraid to lose a URL.
If the domain dies, you will find the answers at: steamdestroy.eth
Who We Are
PhishDestroy is a non-commercial anti-fraud operation. There are four of us — certified cybersecurity professionals operating across multiple countries. One of our original five members is deceased; that is why you will never find all of us.
40a. Protokol o otevřeném zveřejňování informací: Formální oznámení společnosti Valve Corporation
PhishDestroy neuzavírá mimosoudní dohody, nepodepisuje dohody o mlčenlivosti ani se nezapojuje do korporátního vydírání. Naším cílem je transparentnost a technická pravda. Toto vyšetřování — včetně surových (anonymizovaných) telemetrických dat, skriptů pro reprodukci zranitelností a analýzy transakcí v blockchainu — je zveřejněno jako otevřené úložiště. Současně zasíláme tento formální otevřený dopis vedení a právnímu oddělení společnosti Valve Corporation s žádostí o objasnění zdokumentovaných technických a právních paradoxů.
Společnost Valve systematicky skrývá skutečné důvody zákazu účtů v komunitě a zmrazení inventáře za frázemi typu „nemůžeme zveřejnit algoritmy systému proti podvádění (VAC)“. To je technický a právní nesmysl: systém VAC nemá žádný vztah k blokování obchodování. Podle našich odhadů činí hodnota aktiv nelegálně držených na zablokovaných botových účtech (Breakage Income) 300–500 milionů dolarů. Jaký je skutečný objem aktuálně zmrazeného inventáře? Proč je majitelům zabaveného majetku upíráno právo znát skutečný, podrobně rozepsaný důvod blokace bez irelevantních odkazů na systém proti podvádění?
Podmínky služby Steam kategoricky zakazují jakoukoli automatizaci. Realita dokazuje opak: společnost Valve vytvořila a udržuje službu API, která se používá výhradně k krádežím. Stínové trhy generují denně miliony požadavků typu „API“, které ověřují ukradené relace JWT/SSFN. Naše telemetrie ukazuje 300 000 botfarem, bezproblémovou automatickou registraci přes VoIP čísla, dostupnost parsování proxy/Tor a miliony identických phishingových zpráv denně. Doba od krádeže tokenu po zařazení na černý trh: milisekundy. Proč oficiální služba Steam API funguje jako kanál pro trestnou činnost, zatímco společnost Valve ignoruje stoprocentně prokazatelnou průmyslovou automatizaci?
Podmínky služby Steam výslovně zakazují používání VPN k obcházení regionálních omezení. Na oficiálních doménách komunity Steam – moderovaných zaměstnanci společnosti Valve – jsou však již roky zveřejňovány tisíce návodů na změnu regionu a dobíjení peněženek (včetně území podléhajících sankcím OFAC), které jsou indexovány vyhledávači Google a Bing. Je poskytování serverů Steam k hostování návodů na obcházení sankcí oficiálním postojem společnosti a proč je zákaz VPN prosazován výhradně tehdy, když z toho má Valve prospěch?
Uznáváme právo společnosti Valve Corporation na mlčení. V právním prostředí se však absence odpovědí na zdokumentované technické důkazy považuje za tiché přiznání. Po uplynutí lhůty pro zodpovědné zveřejnění budou materiály z našeho úložiště předány následujícím regulačním orgánům:
PhishDestroy aktivně hledá země a regulační orgány, kterým není lhostejné, že jejich občanům — a jejich dětem — je kradeno majetek, jsou systematicky naváděni k závislosti na hazardu a jsou vystaveni tomu, co může být, přinejmenším s tichým souhlasem společnosti Valve, zdokumentovaným vektorem pro masivní napadení zařízení.
Vyberte si svou zemi a podívejte se na ověřené oficiální způsoby podání hlášení. Nic se neodesílá automaticky – zkontrolujte všechny skutečnosti a odešlete hlášení sami prostřednictvím oficiálního kanálu.
41. The Ultimatum
One question requires a public answer on the record: According to Valve's Terms of Service, does a court in the annexed territory of Crimea qualify as "any local Russian state court"? Without a direct, public answer to this question, do not contact us.
If a "peaceful settlement" is what you want, enforce your own rules:
Ban every account that has ever used a VPN to access Steam (you have the database).
Block every account that has used automation on the platform, including CSGOFast.
Admit that Valve or its proxies conducted a cyberattack against Source 1.
The minimum standard of fairness: return every asset stolen through trade substitution (API scam). Start with every account ever listed on Lolzteam Market. We understand your architecture — we saw your internal device identification logic in those unredacted GDPR documents. "Technically impossible" is not an answer. If your staff cannot do it, replace them. The outcome does not change regardless of what you try. We have no money to seize, no names to expose, and no corporate reputation to ruin. We are armed only with the truth.
A Global Warning: The Infostealer Epidemic and Corporate Collateral
I am addressing every country on Planet Earth — except the terrorist states, since Steam is already getting along with them just fine.
If you care at all that an unaccountable corporation has decided it has the right to steal your children's digital property, listen closely. If you care that they deliberately fail to notify users about infected devices — thereby compromising critical corporate networks worldwide — then pay attention.
In Part 2 of our investigation, we will present a perfect example of what Steam's negligence has actually spawned. We will provide hard evidence proving that Steam is the primary economic fuel for the global infostealer industry. Steam accounts are the top gaming query for malware operators. Without the financial return provided by Steam's thriving shadow market, these massive, indiscriminate infostealer distribution campaigns would simply be economically unviable.
There is already a public case on the record where a $2 stolen log resulted in a corporate lockdown, a $17 million ransom payout, and total damages exceeding $100 million. Thank you, Valve, for your unparalleled commitment to global "security."
We will not hide this intelligence. Information flows to us naturally, and we will publish it all. And let this be our official declaration: if, God forbid, the evidence reveals that Valve or its proxies have been conducting targeted cyberattacks against specific users to silence them, the international community will not play along. The rest of the world will not entertain your cute little legal games about exclusive jurisdiction in the courts of Washington State.
42. Konečný verdikt
Bot už stejně není pod naší správou. Necítím žádnou hanbu a nevěřím, že dělám něco špatného. Jsem si jistý, že nemáme jinou možnost. Zdroj 1 se včas zastavil, ale pokud jde o nás, zabili jste děti, jejichž data jste mu vynesli. Proto nebudeme vyjednávat. Steam je zde teroristou.
Znovu zhodnoťte, co jste udělali, a co dělal Zdroj 1 poté, co mu vaši právníci ta data předali. Odkud se vzala vaše „Nikita“? A co ti čtyři externí pracovníci podpory, kteří sídlí v Rusku? Jsem si jistý, že si myslíte, že se jedná o ojedinělý incident, ale my víme o mnoha vašich případech a vašich „rozhodnutích“.
My nejsme jako vy. Nezakrýváme potenciální zločiny. Budeme postupně zveřejňovat vše spolu s důkazy a spolupracovat s jakýmkoli regulačním orgánem — kromě těch, které zřejmě upřednostňujete. Ruské úřady nám často píší; obvykle jim řekneme, ať jdou do prdele, ale možná začneme odpovídat. Nehrajeme hloupé hry s nesrozumitelnými firemními odpověďmi, jejichž cílem je zmást, podobně jako vaše uživatelské podmínky.
Doufám, že náš postoj je naprosto jasný:
Steam zabil děti, které sám zveřejnil.
Steam okrádá děti pod záminkou boje proti „duplikátům“, které byly zcela vygenerovány jeho vlastním týmem podpory.
Steam lže o utajování důvodů zákazu pod záminkou „anti-cheatu“ výhradně proto, že je to z právního hlediska výhodné. (Co sakra má anti-cheat společného s komunitním zákazem?)
Jste si opravdu tak jistí, že vaše soudy nebo Evropa nad tím prostě přimhouří oko? Uvidíme.
---
42. Conclusion
The bot is no longer under our management anyway. I feel no shame, and I do not believe I am doing a bad thing. I am certain we have no other choice. Source 1 stopped himself in time, but as far as we are concerned, you killed the children whose data you leaked to him. Therefore, we will not negotiate. Steam is the terrorist here.
Re-evaluate what you did, and what Source 1 was doing after your lawyers handed him that data. Where did your "Nikita" come from? And what about the four off-staff support agents sitting in Russia? I am sure you think this is an isolated incident, but we know about many of your cases and your "decisions."
We are not you. We do not cover up potential crimes. We will gradually release everything with proof and cooperate with any regulator — except the ones you seem to favor. Russian authorities write to us frequently and we do not answer them; that may change. We don't play stupid games with unintelligible corporate responses designed to confuse, much like your user agreement.
I hope our position is absolutely clear:
Steam killed the children it leaked.
Steam steals from children under the guise of fighting "dupes" that were generated entirely by its own support staff.
Steam lies about withholding ban reasons under the guise of "anti-cheat" strictly because it is legally convenient. (Anti-cheat has no bearing on a Community Ban.)
Are you really that confident your courts or Europe will just turn a blind eye? We will see.
---
References & Sources
[1] Netcraft Anti-Phishing Service and Reporter Prizes Program https://www.netcraft.com/anti-phishing/
Netcraft is a leading internet security company that tracks and reports phishing sites. The Reporter Prizes program rewards verified submissions. Valve's refusal to cooperate with Netcraft is documented through public anti-phishing statistics.
[2] Cloudflare Abuse Reporting Portal https://www.cloudflare.com/abuse/
Used for escalating phishing campaigns employing cloaking techniques against Cloudflare-protected infrastructure.
[3] Valve Internal Data Disclosure (2024) — Employee Count and Revenue Per Employee
Sources: Kotaku, Ars Technica, IGN, The Verge, PCGamer (May 2024)
https://kotaku.com/ [search: "Valve employees 2024"]
https://arstechnica.com/ [search: "Valve internal data leak"]
Internal documents revealed Valve's total headcount (~336) and the number of employees directly working on the Steam platform (~79), along with boasts about profit-per-employee exceeding Google, Amazon, and Microsoft.
[4] LZT Market (Lolzteam) — Shadow Marketplace Statistics https://lolz.live / https://lzt.market
Russian-language clearnet marketplace for stolen accounts and cybercrime services. Item IDs (e.g., item_id 252853378) confirm cumulative listing history exceeding 250 million lots. Account counts cited reflect live marketplace data at time of documentation. Covered by: Group-IB, KELA Cyber Intelligence, and other threat intelligence providers.
[5] BlockBlasters Malware Incident on Steam (September 2024)
Security community reports and Steam community threads (September-October 2024):
https://www.reddit.com/r/GlobalOffensive/ [search: "BlockBlasters stealer"]
https://steamcommunity.com/
A game titled BlockBlasters was listed on Steam and distributed an information stealer. Reports submitted to Steam support beginning September 2, 2024 included open Telegram API endpoints embedded in game code. The game remained available for approximately one month before malicious builds were removed.
[6] Raivo Plavnieks — Content Creator and Whistleblower
Twitch streamer whose coverage of the BlockBlasters incident brought the malware to wider public attention. Documented through VODs, community posts, and security researcher reports (September 2024).
[7] ChainAbuse — Cryptocurrency Abuse Reporting Platform https://www.chainabuse.com
Community-maintained database of cryptocurrency addresses associated with scams, ransomware, and fraud. Victims of the BlockBlasters stealer submitted reports to ChainAbuse documenting wallet addresses used to receive stolen cryptocurrency.
[8] IRS Form W-8BEN — Certificate of Foreign Status of Beneficial Owner https://www.irs.gov/forms-pubs/about-form-w-8ben
Required from non-US developers earning income through US entities (including Steam). This KYC document ties the developer's legal identity directly to their Steamworks publisher account, refuting Valve's "hacked anonymous developer" narrative.
[9] Taylor Wessing — International Law Firm https://www.taylorwessing.com
Offices in Hamburg, Munich, London, and other cities. Represents Valve Software in European legal matters including GDPR data subject access requests (DSARs). The firm's historical founding and its predecessor entities' documented connections to the Third Reich era have been the subject of academic and journalistic inquiry into German law firm histories.
[10] EU General Data Protection Regulation (GDPR) — Regulation 2016/679 https://eur-lex.europa.eu/eli/reg/2016/679/oj
https://gdpr.eu/
Under Article 15 GDPR, data subjects may request full disclosure of personal data held. Valve's compliance with DSARs has been processed through Taylor Wessing, and documented cases show improperly redacted responses disclosing data of third parties — including minors.
[11] RedLine Infostealer — Operation Magnus (October 28, 2024)
Europol Press Release: https://www.europol.europa.eu/media-press/newsroom/news/operation-magnus-redline-and-meta-infostealers-dismantled
FBI and Dutch National Police (Politie) participated in the takedown of RedLine and META stealer infrastructure. RedLine was the dominant tool for stealing Steam session files (SSFN) and browser cookies during 2021-2024, sold as Malware-as-a-Service (MaaS) on Russian-language forums.
Additional coverage: BleepingComputer (October 2024), The Record, Krebs on Security.
[12] SteamRep — Community Trading Reputation Database https://steamrep.com
Volunteer-run platform that tracked scammers in Steam trading communities. Internal controversies, including alleged bribery for scammer tag removal and administrative corruption, were documented in community forum threads circa 2016-2020. Valve severed formal cooperation with SteamRep-affiliated moderators by 2022.
[13] Jess Cliffe — Counter-Strike Co-Creator
Reported by: Kotaku, Polygon, PC Gamer, The Verge (September 7-8, 2016)
https://kotaku.com/ [search: "Jess Cliffe Valve"]
Valve placed Jess Cliffe (credited alongside Minh Le for creating Counter-Strike) on administrative leave in 2016 following his arrest on charges of commercial sexual abuse of a minor. He was subsequently terminated without a court conviction.
[14] Valve Steam Trade Hold Policy
Steam Blog announcement on trade holds (December 9, 2015):
https://steamcommunity.com/games/593110/announcements/detail/
The 7-day hold on traded items was formally introduced in December 2015. Earlier escrow mechanisms were introduced starting 2012. The policy change was intended to reduce fraud but in practice created the linear theft pipeline described in this report.
[15] Valve Anti-Cheat (VAC) System
Official documentation: https://support.steampowered.com/kb_article.php?ref=7849-Radz-6869
VAC bans are account-wide, permanent, and tied to the hardware/phone number used during the violation. The asymmetric application of VAC bans (aggressive for cheating, absent for mass phishing activity) is documented through community tracking at vacbanned.com and similar resources.
[16] FBI Seattle Field Office
Address: 1110 3rd Ave, Seattle, WA 98101
Phone: +1 (206) 622-0460
https://www.fbi.gov/contact-us/field-offices/seattle
Valve Software is headquartered at 10400 NE 4th St, Bellevue, WA 98004 — within the FBI Seattle field office jurisdiction.
[17] IC3 — Internet Crime Complaint Center (FBI) https://www.ic3.gov
The FBI's official portal for reporting cybercrime, including account theft, fraud, and sanctions violations. Accepts reports from individuals, businesses, and third parties.
[18] CISA — Cybersecurity and Infrastructure Security Agency https://www.cisa.gov
US federal agency responsible for critical infrastructure cybersecurity. CISA's Stop Ransomware and Known Exploited Vulnerabilities programs are relevant to the infostealer ecosystem documented here.
[19] DOJ NSD — Department of Justice, National Security Division https://www.justice.gov/nsd
Oversees national security cases including sanctions violations (OFAC referrals), foreign influence operations, and cyber threats tied to nation-state actors. The potential nexus between state-adjacent structures controlling LZT Market and Steam's platform policy warrants NSD attention.
[20] OFAC — Office of Foreign Assets Control (U.S. Treasury) https://ofac.treasury.gov
Russia-related sanctions programs: https://ofac.treasury.gov/sanctions-programs-and-country-information/russia-related-sanctions
Ukraine-EO13685 (Crimea), and subsequent executive orders cover the DNR/LNR regions. Accepting payments originating from sanctioned persons or territories — whether directly or through intermediaries — may constitute sanctions violations subject to civil and criminal penalties.
[21] JSON Web Token (JWT) — RFC 7519 https://datatracker.ietf.org/doc/html/rfc7519
Industry-standard method for representing claims between parties. Steam adopted JWT-based session tokens as a replacement for legacy SSFN files. The off-platform validation capability of JWTs (verifiable without querying Steam servers) is a documented property of the specification.
[22] Steam Direct — Developer Application and KYC https://partner.steamgames.com/steamdirect
Valve charges $100 per game submission and requires developers to submit legal identification, tax forms (W-8BEN for non-US), and banking information. This KYC process creates a paper trail that directly contradicts the "anonymous hacker" narrative.
[23] Roskomnadzor — Federal Service for Supervision of Communications, Information Technology and Mass Media (Russia) https://rkn.gov.ru
The Russian federal regulator has issued multiple administrative decisions against LZT Market (Lolzteam) ordering its blocking. These decisions have been publicly available in Russian regulatory databases. The market's continued operation despite five such decisions points to legal maneuvering and possible political protection.
[24] FunPay — Russian Peer-to-Peer Trading Platform https://funpay.com
Widely used platform in CIS regions for trading in-game goods, including Steam balance top-ups and region-switching services. Transaction counts cited (500,000+) reflect documented seller statistics visible on the platform's seller profiles.
[25] Tinkoff Bank — Sanctioned Russian Financial Institution
Tinkoff Bank (now T-Bank) was added to OFAC SDN list and subjected to EU sanctions following Russia's 2022 invasion of Ukraine.
OFAC SDN list: https://ofac.treasury.gov/specially-designated-nationals-and-blocked-persons-list-sdn-human-readable-lists
Steam accounts were documented receiving top-ups from Tinkoff-issued cards in the CIS region after the imposition of sanctions.
[26] Uniswap Protocol — Decentralized Exchange https://uniswap.org
Uniswap and broader DeFi protocols have been targeted by phishing operations whose techniques and personnel originated in the Steam scam ecosystem. Security reports from Chainalysis, CertiK, and SlowMist document the migration of CIS-region fraudsters from gaming scams to Web3 drainer attacks.
[27] Steam Session Files (SSFN) — Technical Documentation
Community and security researcher documentation:
https://steamdb.info / https://github.com/nicklvsa (various Steam security research repos)
SSFN (SteamSentryFile) files stored Steam Guard authentication tokens locally. When stolen by infostealers, they allowed session reuse without re-authentication. Valve deprecated SSFN in favor of JWT-based sessions during 2023-2024.
[28] Binance / Bybit / Gate.io — Cryptocurrency Exchanges https://www.binance.com | https://www.bybit.com | https://www.gate.io
Major centralized exchanges whose Telegram payment bots and P2P trading infrastructure are used by LZT Market and similar platforms to process payments for stolen account transactions, circumventing traditional AML controls.
[29] Steam Phishing via Google Ads — Documented Campaigns (2023-2024)
Reported by: BleepingComputer, Malwarebytes, Group-IB
https://www.bleepingcomputer.com/ [search: "Steam phishing Google Ads"]
https://www.malwarebytes.com/ [search: "Steam phishing ads"]
Attackers purchased Google Ads targeting Steam-related search queries, substituting display URLs to appear as legitimate Steam domains. The scale of the 2024 campaign documented by PhishDestroy ($300,000 estimated net proceeds) aligns with Google Ads abuse patterns documented by multiple cybersecurity firms.
[30] STALKER 2 / GTA — Games Whose Publishers Withdrew from Russian Market
GSC Game World (STALKER 2) officially suspended sales in Russia following the 2022 invasion of Ukraine.
Rockstar Games / Take-Two Interactive restricted GTA sales in Russia following sanctions.
Despite publisher intent, Steam continued to provide mechanisms allowing Russian users to purchase these titles via region-switching, as documented by community researchers and gaming press (Eurogamer, RPS, IGN, 2022-2024).
---
ADDITIONAL CONTEXT: REGULATORY AND LEGAL FRAMEWORK
Steam's Terms of Service (ToS), Version History:
The Steam Subscriber Agreement is archived by the Internet Archive Wayback Machine:
https://web.archive.org/web/*/https://store.steampowered.com/subscriber_agreement/
Comparison of versions shows modification of sanctions-related language, including the removal of explicitly named countries (Cuba, Iran, Syria) from prohibited territory lists.
AML / FATF Guidelines on Virtual Assets:
Financial Action Task Force (FATF) guidance on virtual assets and virtual asset service providers:
https://www.fatf-gafi.org/en/topics/virtual-assets.html
Skin trading platforms and Steam Wallet function as virtual asset ecosystems subject to FATF Recommendation 15.
Europol — Internet Organised Crime Threat Assessment (IOCTA):
https://www.europol.europa.eu/publications-events/main-reports/iocta-report
Annual reports document the role of gaming platforms in cybercrime recruitment and infostealer distribution.
Group-IB — Hi-Tech Crime Trends Report:
https://www.group-ib.com/resources/research/
Documents the evolution of CIS-region cybercrime from gaming-platform fraud to ransomware and financial crime.
Chainalysis Crypto Crime Report:
https://www.chainalysis.com/blog/crypto-crime-report/
Annual report documenting laundering of cybercrime proceeds through decentralized exchanges and peer-to-peer platforms, including those accepting Steam-ecosystem stolen goods.
---
NOTE ON SOURCES
All market statistics cited (LZT Market account counts, transaction volumes, JWT token prices) reflect data documented at specific points in time by PhishDestroy through direct platform observation. Shadow market data is inherently dynamic; figures cited represent point-in-time measurements and directional trends, not static permanent values. Where possible, archived copies of relevant pages have been preserved on the Wayback Machine (web.archive.org) and independent archival nodes.
All regulatory contact information (FBI, IC3, CISA, DOJ NSD, OFAC) reflects publicly available official contact data as of the date of this publication.
Valve must be held financially accountable for accounts stolen through their deliberate negligence. The minimum estimated liability: $450,000,000 — representing the documented victim real spend on accounts currently listed on LZT Market across all categories, and the value of inventories frozen on banned bots that were never returned to victims.
This is not an estimate of criminal market value. This is the documented money victims spent on their accounts — money that Steam's negligence, outsourced corruption, and deliberate API blindness allowed to be stolen and re-monetized on criminal markets while Valve collected commission on both the original sale and every subsequent stolen skin transaction.
Valve wrote the policy that prevents item restoration. Valve's outsource staff committed the thefts. Valve's API enabled the marketplace. Valve's 15% commission runs on the same skins. The accountability is structural, not incidental.