مركز IC3 التابع لمكتب التحقيقات الفيدرالي (FBI)
الإبلاغ عن الجرائم المتصلة بالإنترنت في الولايات المتحدة
Federal tips line1-800-CALL-FBI

“Messenger”
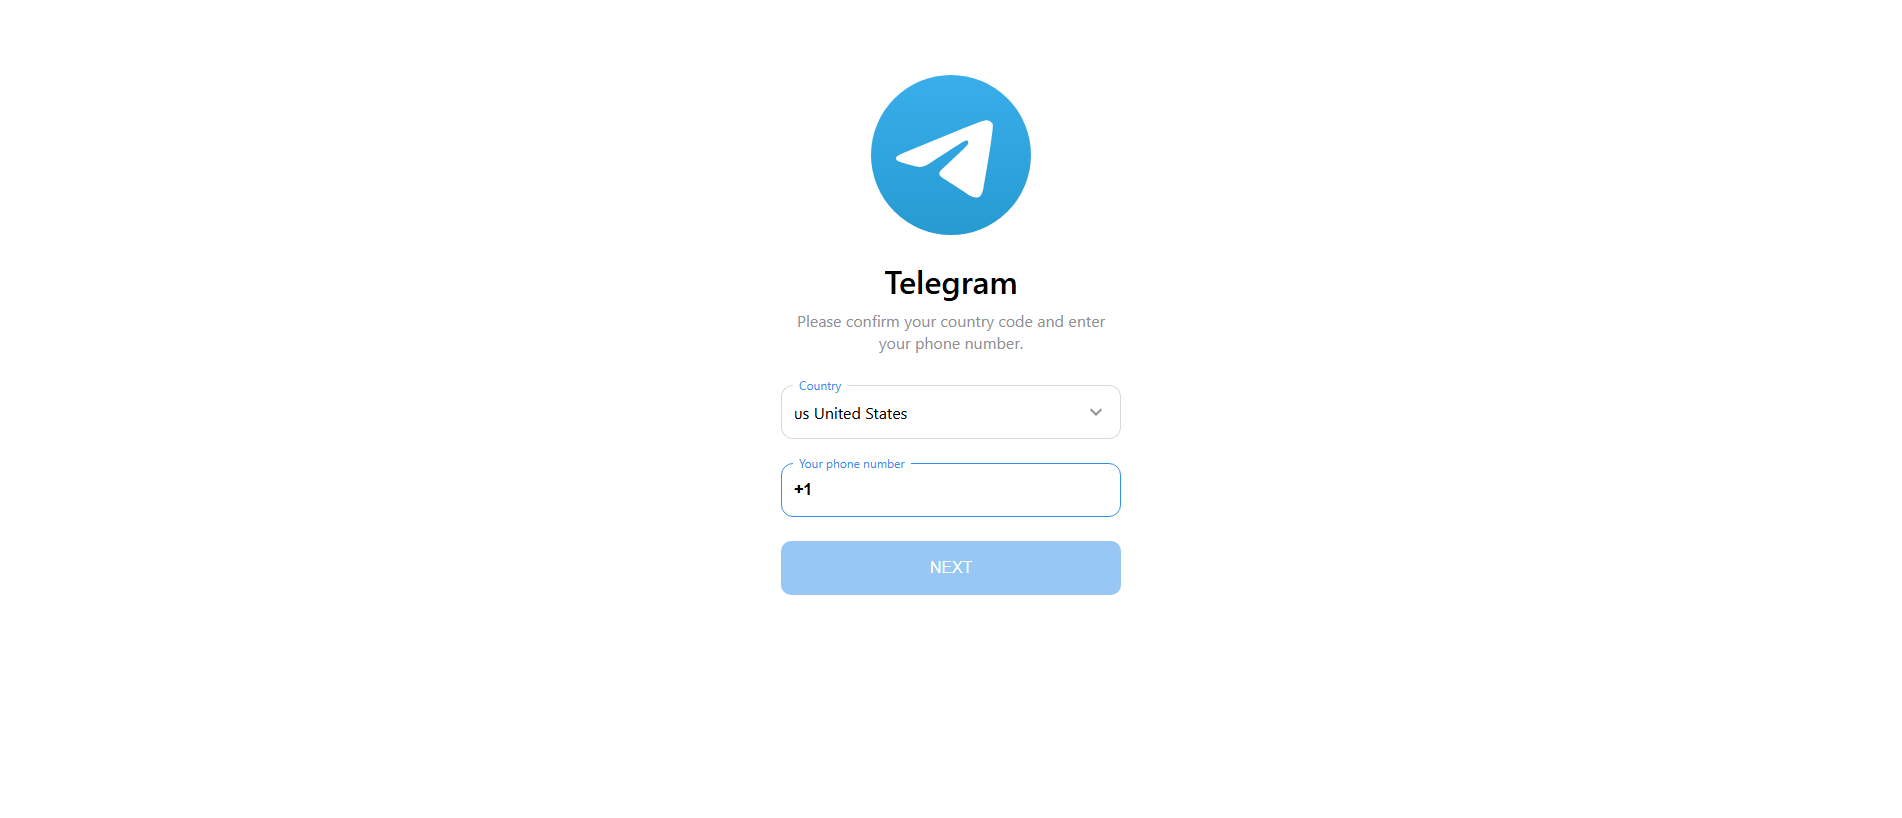
teletfaj.com — المحتوى غير متوفر. انتحال العلامة التجارية: Unknown; نوع الاحتيال: Impersonation. ملخص الأدلة: VirusTotal 10/91 (ADMINUSLabs, alphaMountain.ai, BitDefender, CyRadar, ESET); Google Safe Browsing flagged; Spamhaus DBL_SPAM; PhishDestroy score 100/100. مسجّل النطاق: NiceNIC.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.
This domain is actively engaged in credential phishing targeting users of messaging platforms. Analysis indicates the site mimics legitimate Messenger login interfaces to deceive visitors into submitting account credentials, which are then captured by threat actors for unauthorized access or further exploitation. The fraudulent nature is reinforced by its use of social engineering techniques, as confirmed by its inclusion in security blocklists and Google Safe Browsing’s SOCIAL_ENGINEERING category. Infrastructure analysis reveals multiple technical indicators supporting this assessment. The domain was registered on May 24, 2026, through NICENIC INTERNATIONAL GROUP CO., LIMITED, a registrar frequently associated with high-risk domains. It resolves to the IP address 27.124.47.186 and is currently flagged by 10 out of 95 security vendors on VirusTotal. Additionally, the SSL certificate is falsely labeled as belonging to Telegram, a tactic designed to increase perceived legitimacy. The domain appears on two security blocklists, including InversionDNS and BLP-Malware, further confirming its malicious intent. Users who have visited www.teletfaj.com or entered credentials on the site should take immediate action to mitigate risk. First, change passwords for any accounts accessed or entered on the site, prioritizing email and financial services. Enable multi-factor authentication where available to prevent unauthorized access. Monitor accounts for suspicious activity, such as unrecognized logins or messages sent without consent. If credentials were reused across multiple platforms, update passwords on all affected services. Finally, report the incident to relevant security teams or fraud reporting channels to assist in broader threat mitigation efforts.

Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: dns_error: raw=dns_error; via=local_dns_prefilter
 (RU)
PhishDestroy Investigation
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Infrastructure map · teletfaj.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
يستضيف عنوان IP الأصلي هذا العديد من مجالات التصيد الاحتيالي — وقد تتم مشاركة البنية التحتية عبر الحملات.
These domains also target غير معروف users. View all Unknown threats →
Part of the غير معروف phishing campaign. View all campaign domains →
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب
 wrencapstead.digital
 zywa-capovin.pro
 xtradegrok36.com
 chat-trade-ai.live
 clawnchtoken.com
 primarkpolska.pl