مركز IC3 التابع لمكتب التحقيقات الفيدرالي (FBI)
الإبلاغ عن الجرائم المتصلة بالإنترنت في الولايات المتحدة
Federal tips line1-800-CALL-FBI

“Messenger”
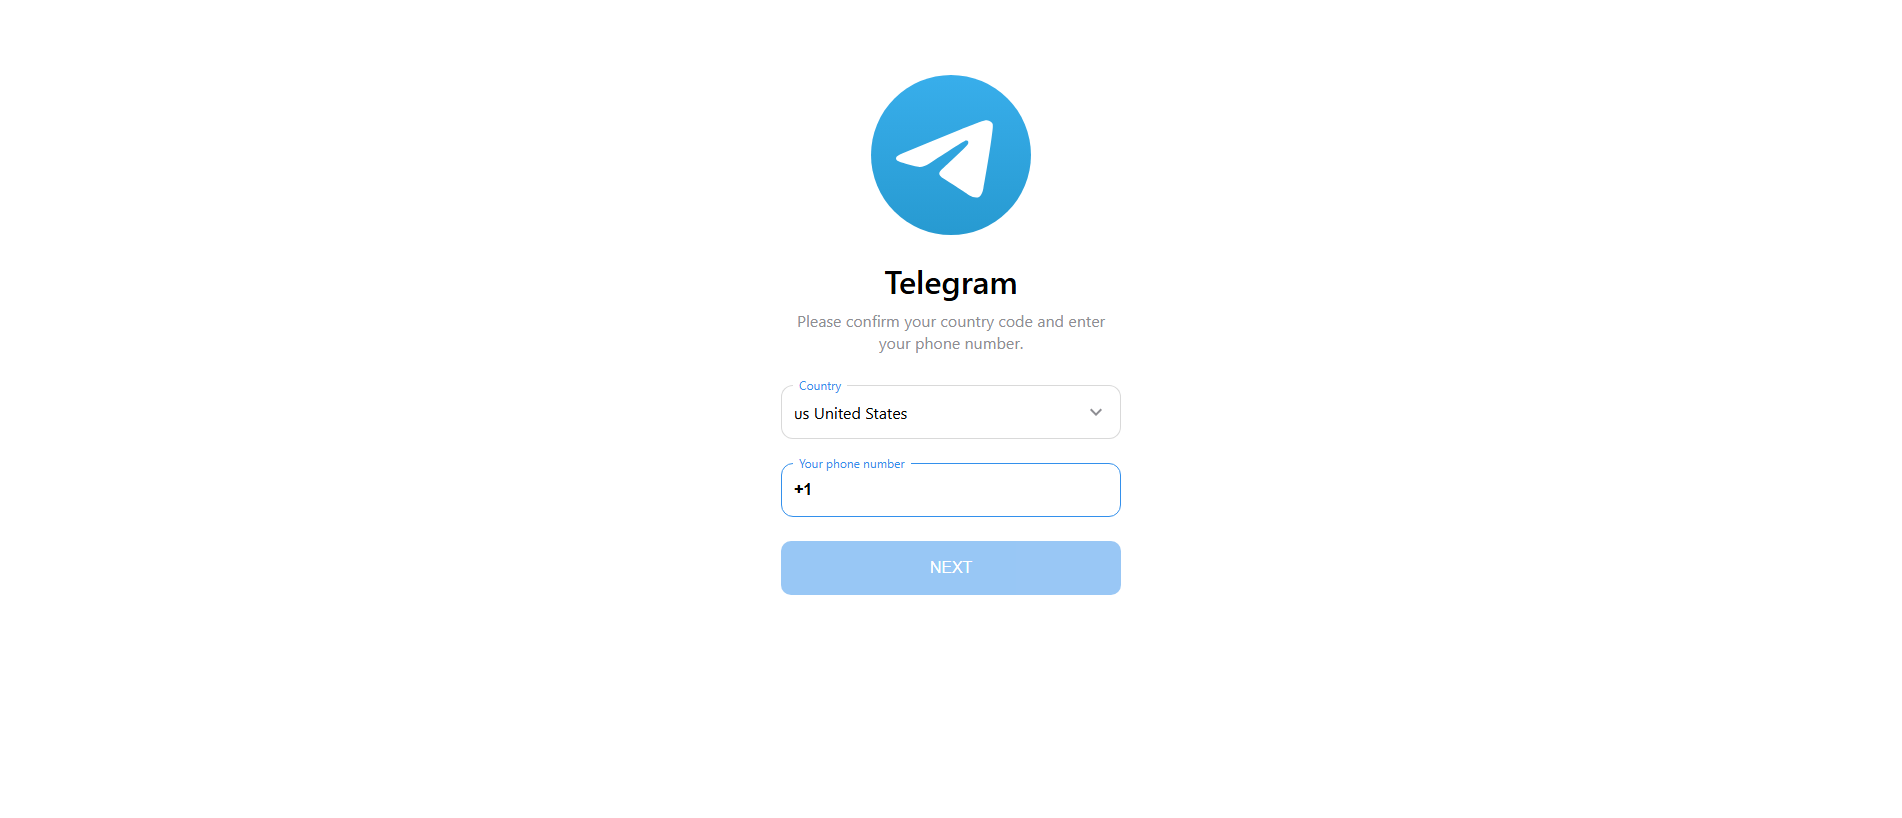
This domain, www.telelhgf.com, is flagged as an active phishing infrastructure targeting users through a Messenger-themed interface.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.
This domain, www.telelhgf.com, is flagged as an active phishing infrastructure targeting users through a Messenger-themed interface. Registered on May 18, 2026, via NICENIC INTERNATIONAL GROUP CO., LIMITED, the domain resolves to IP address 27.124.47.186, hosted on AS152194 (CTG Server Limited) in Hong Kong. Analysis of its nameservers (ns3.my-nddns.com and ns4.my-nddns.com) and SSL certificate (issued for Telegram and *.local) suggests an attempt to mimic legitimate messaging platforms, though the exact content and targeting methodology remain unconfirmed due to limited forensic data. The domain currently returns an HTTP 200 status, indicating operational hosting, and its page title explicitly displays 'Messenger,' reinforcing the likelihood of impersonation. Security vendors have flagged the domain, with 7 of 91 engines on VirusTotal detecting it as malicious. It appears on at least one security blocklist and holds a trust score of 0/100, further corroborating its high-risk classification. Defenders should prioritize blocking this domain at the DNS and network levels, particularly in environments where messaging services are in use. The short registration window (under two months) and lack of historical reputation align with typical phishing campaign timelines. While the specific lure or payload is not yet analyzed, the combination of infrastructure, SSL certificate details, and page title strongly indicates credential harvesting or social engineering activity. Monitoring for related domains using the same nameserver or IP range may uncover additional threats.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | www.telelhgf.com |
malicious | Sinkholed |
Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: timeout: raw=timeout; http=0; via=http_proxy; error=HTTPConnectionPool(host='23.236.170.49', port=9082): Read timed out. (read timeout=7)
 (RU)
PhishDestroy Investigation
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Infrastructure map · telelhgf.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
يستضيف عنوان IP الأصلي هذا العديد من مجالات التصيد الاحتيالي — وقد تتم مشاركة البنية التحتية عبر الحملات.
These domains also target غير معروف users. View all Unknown threats →
Part of the غير معروف phishing campaign. View all campaign domains →
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب
 chat-trade-ai.live
 clawnchtoken.com
 event-netnetcapital.com
 idletron.site
 cp.vexotra.com
 twojdom24.com
 gearivora.com