VirusTotal
22 / 93
إبلاغ


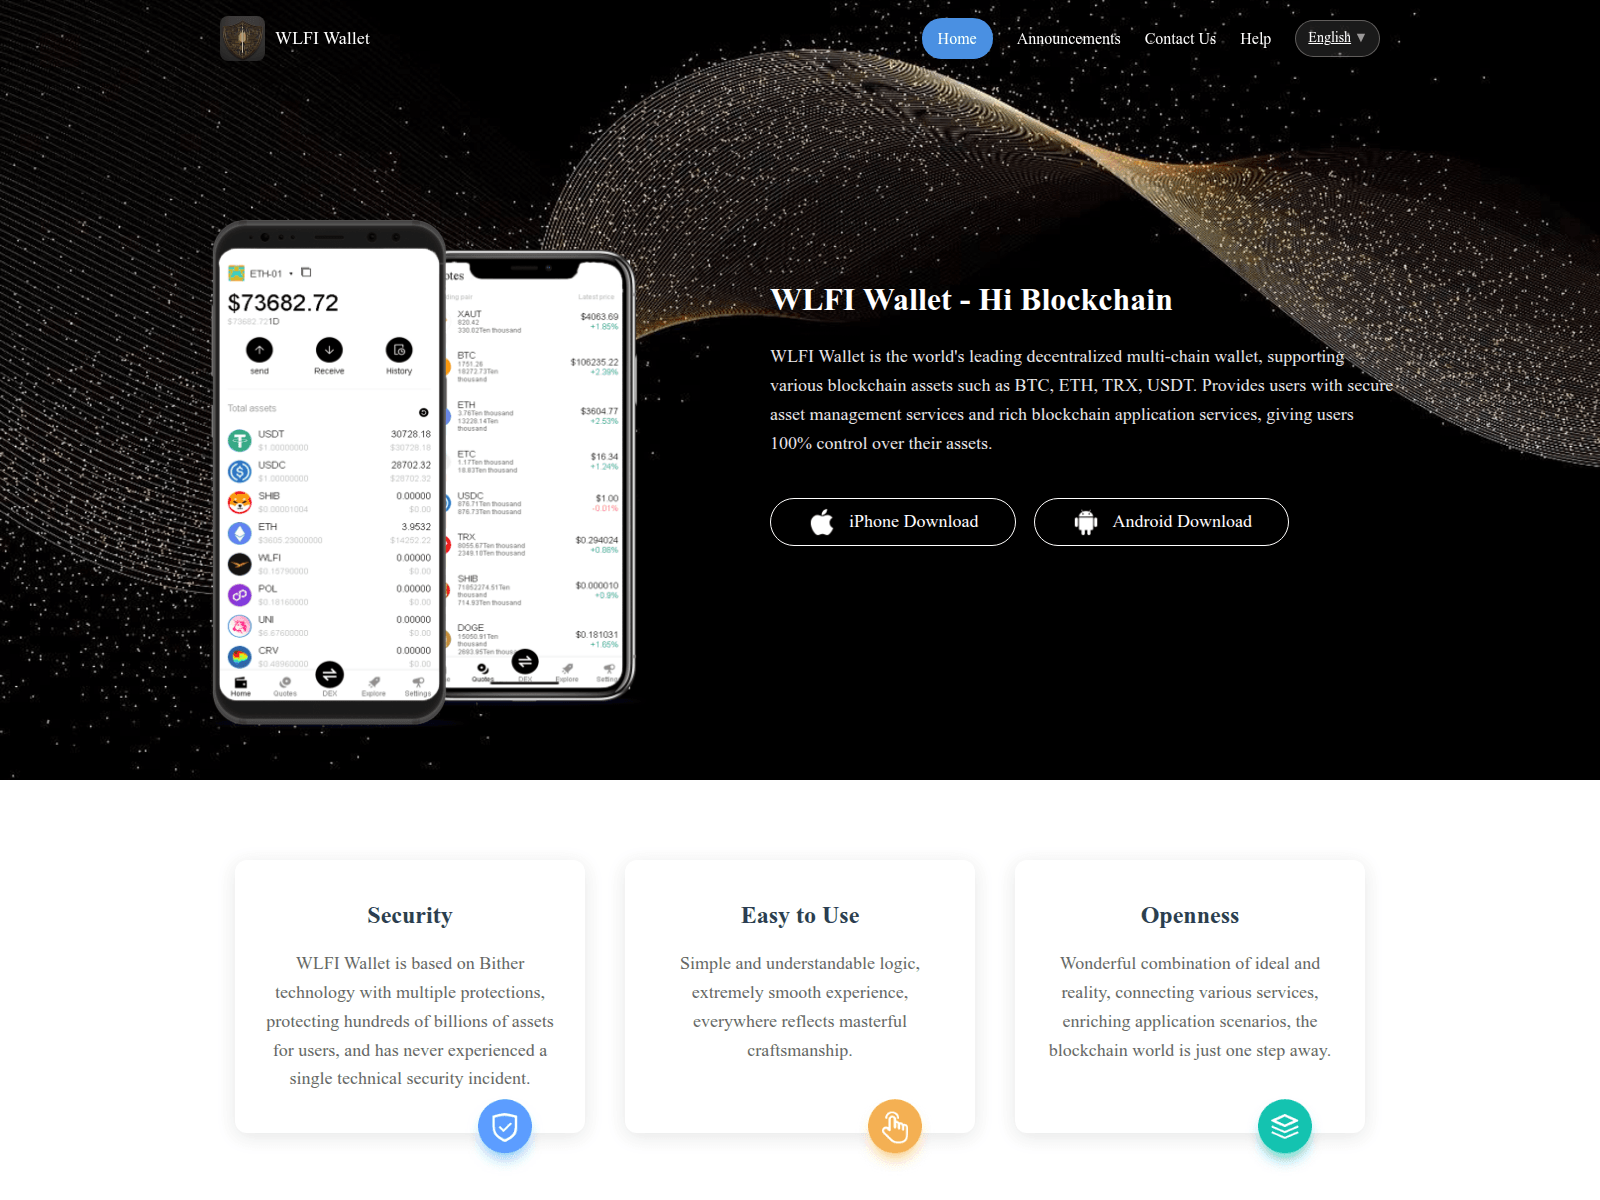
انتحال العلامة التجارية: Arbitrum Page title: “WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co”
Availability last checked First listed 26/02/2026 VirusTotal analysed Feb 23, 2026 UTC
Based on 3 recorded source signals. The score is a heuristic over stored detections, not a probability or confidence level.
View evidenceلم يكن المحتوى متاحًا في الملاحظة الأخيرة
Source checks and detection results recorded for this domain, with the time each was observed.
wlfiprobit.com — المحتوى غير متوفر. انتحال العلامة التجارية: Arbitrum; نوع الاحتيال: Crypto Scam. ملخص الأدلة: VirusTotal 22/93 (ADMINUSLabs, ChainPatrol, alphaMountain.ai, BitDefender, Cluster25); URLQuery 6 alerts; PhishDestroy score 95/100.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | wlfiprobit.com |
malicious | Sinkholed |
| OpenDNS | wlfiprobit.com |
phishing | Phishing Block |
| DigiCert UltraDNS | wlfiprobit.com |
malicious | Sinkholed |
| Hagezi Threat Feed | wlfiprobit.com |
malicious | Sinkholed |
| DNS4EU | wlfiprobit.com |
malicious | Sinkholed |
| Quad9 DNS | wlfiprobit.com |
malicious | Sinkholed |
Stored written summary, generated Jul 7, 2026. It is not updated when source results change.
The domain wlfiprobit.com is identified as a high-risk brand impersonation threat targeting Arbitrum. It masquerades as a legitimate cryptocurrency wallet service, using the page title "WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co" to deceive users. This domain was likely designed to harvest sensitive user data or credentials under the guise of offering cryptocurrency services.
Technical analysis reveals that wlfiprobit.com is flagged by 22 out of 95 security vendors on VirusTotal, indicating significant recognition as a threat. The domain resolves to IP address 172.67.152.201, located in the United States under AS13335 managed by Cloudflare, Inc. It was created on February 21, 2026, and has been blocked by three security blocklists including PhishDestroy, MetaMask, and SEAL. The domain's SSL certificate is identified as WE1, and it is currently offline, reducing immediate exposure.
The domain's current offline status mitigates immediate risk; however, vigilance is advised as it may resurface or similar threats could emerge. Security teams should ensure that blocklists are updated and implement additional monitoring for similar activities. Users should be educated on recognizing phishing attempts, particularly those involving cryptocurrency platforms.
الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».
ملاحظة خاصة بالماسح الضوئي: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='wlfiprobit.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError(
لا تُنسب سمعة Edge-IP إلى هذا المجال.
Location describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
٢٨ نطاقًا متشابهًا محفوظًا
كل مسار يمثل سببًا واحدًا لربط نطاق ما بهذا المضيف. يشير حجم العقدة إلى عمليات الكشف التي أجرتها VirusTotal، أما العقد المتقطعة فهي غير متصلة بالإنترنت بالفعل. وترد القوائم الكاملة أدناه.
نفس هاش أيقونة المفضلة أو نفس عنوان الصفحة الخاص بهذا المضيف.
يتم حل هذه التقارير إلى نفس عنوان IP للحافة المشتركة. إنها تساعد في اكتشاف التقارير ولكنها لا تتضمن ملكية مشتركة أو خادم أصل مشترك.
كما تستهدف هذه النطاقات مستخدمي موقع Arbitrum. عرض جميع التهديدات المتعلقة بـ «Arbitrum» →
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب