VirusTotal
6 / 92
إبلاغ


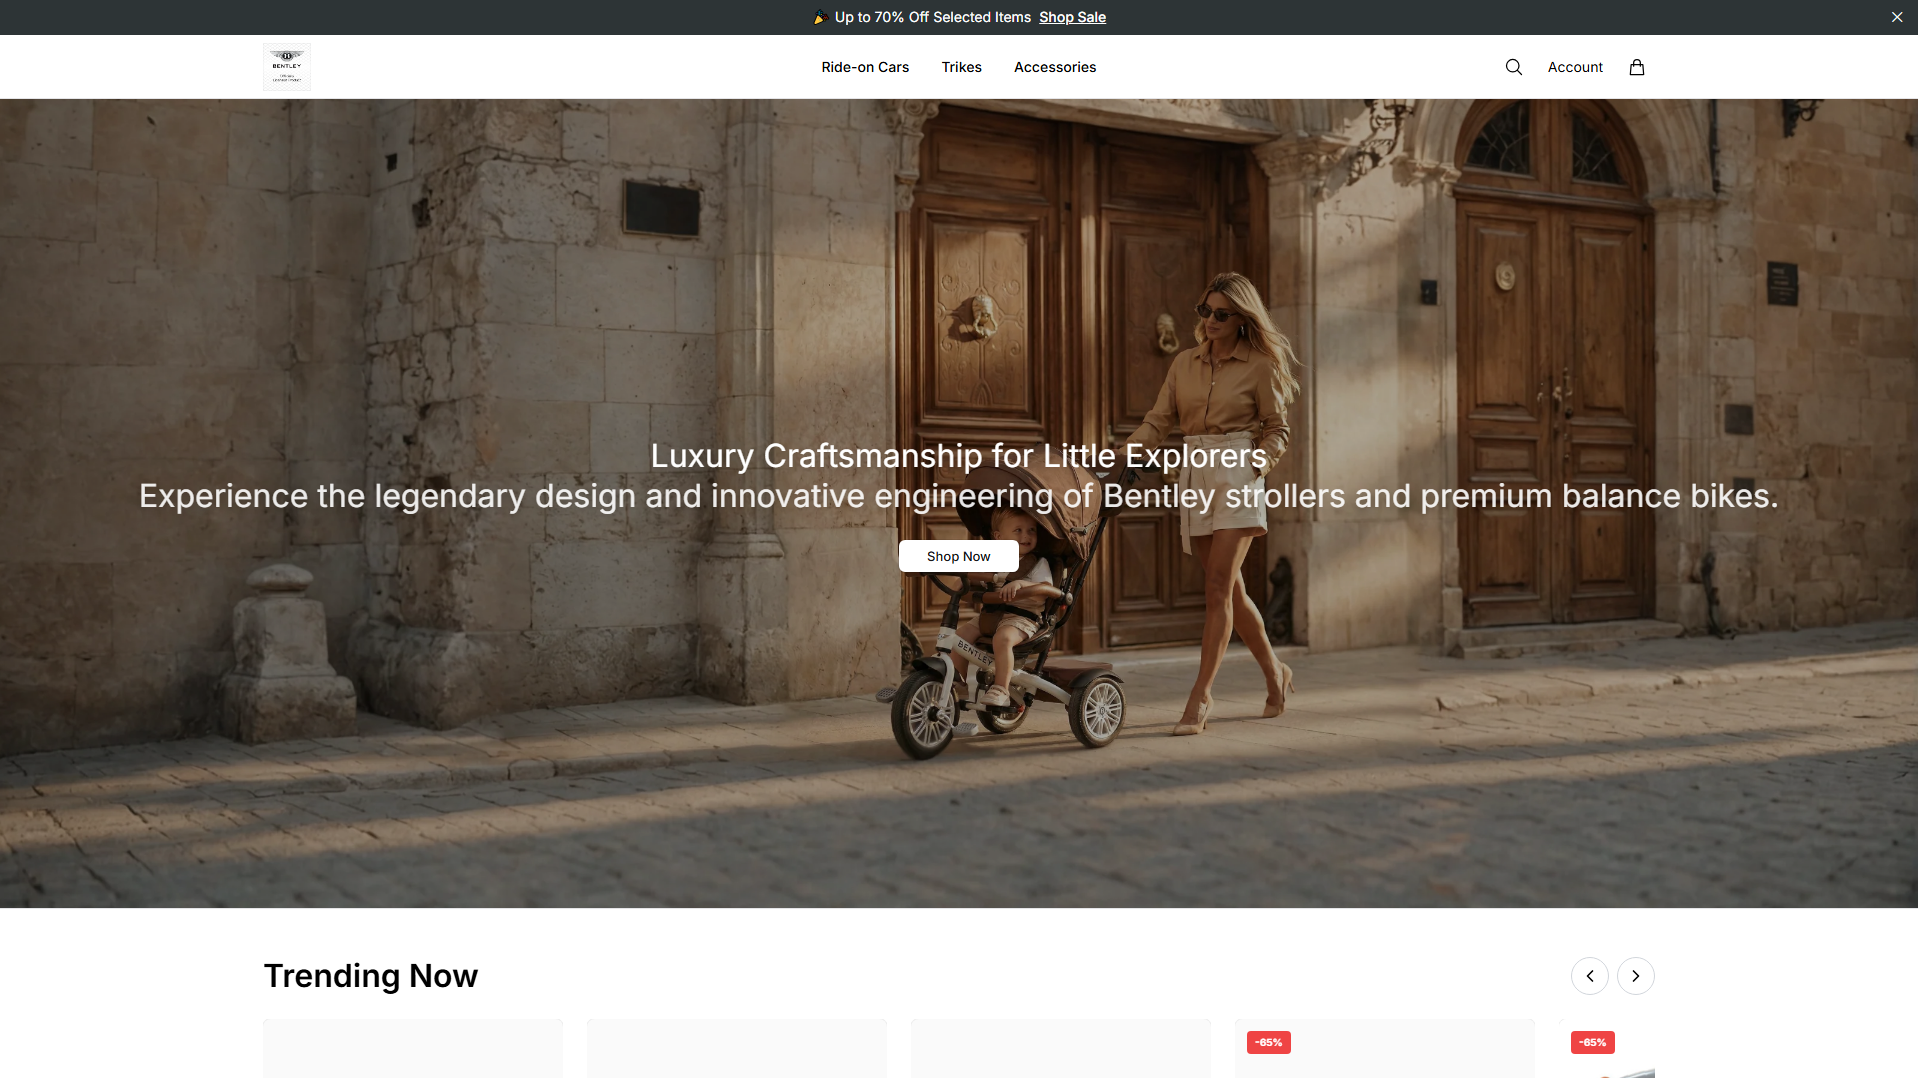
bentleytrikehq.shop — لم يتم التحقق منها. ملخص الأدلة: VirusTotal 6/92 (alphaMountain.ai, CRDF, G-Data, Gridinsoft, LevelBlue); URLQuery 2 det.; URLScan capture; PhishDestroy score 72/100.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.

The domain bentleytrikehq.shop was observed with a PhishDestroy internal listing on 2026-10-13, highlighting a recorded entry in a publisher-owned catalogue. Additional technical evidence was captured from multiple sources within the same timeframe, providing a snapshot of its security profile.
VirusTotal checked bentleytrikehq.shop on 2026-10-11, recording 6 detections out of 92 scanners. OTX referenced the domain in 2 pulses as of 2026-10-13. The domain was also listed internally by PhishDestroy on 2026-10-13. The SSL certificate was issued by Let's Encrypt / YE1 and scanned on 2026-10-13.
PhishDestroy contains a listing for bentleytrikehq.shop, which documents its presence in a publisher-managed catalogue. VirusTotal provides a quantitative measurement of detections from its scanner network, offering insight into the domain's security context. OTX records pulses referencing the domain, which are entries in threat intelligence collections. These sources collectively capture technical and security-related observations within a short timeline.
For bentleytrikehq.shop, preserve the VirusTotal detection record and the PhishDestroy internal listing for ongoing review. Compare future OTX pulse entries and VirusTotal scanner results to these stored observations. Maintain a record of all technical evidence for reference in subsequent security assessments.
الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».
emily.ns.cloudflare.comremy.ns.cloudflare.comLocation describes the IP network.
40c565c8257825f41e90a96858f80eb5f7aea4a85477f5bee91e06eb019831faSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
146.19.203.199. 7 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Template-based draft · optional AI wording assistance requires separate consent
كل مسار يمثل سببًا واحدًا لربط نطاق ما بهذا المضيف. يشير حجم العقدة إلى عمليات الكشف التي أجرتها VirusTotal، أما العقد المتقطعة فهي غير متصلة بالإنترنت بالفعل. وترد القوائم الكاملة أدناه.
يستضيف عنوان IP الأصلي هذا العديد من مجالات التصيد الاحتيالي — وقد تتم مشاركة البنية التحتية عبر الحملات.
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب