URLScan verdict
malicious
إبلاغ

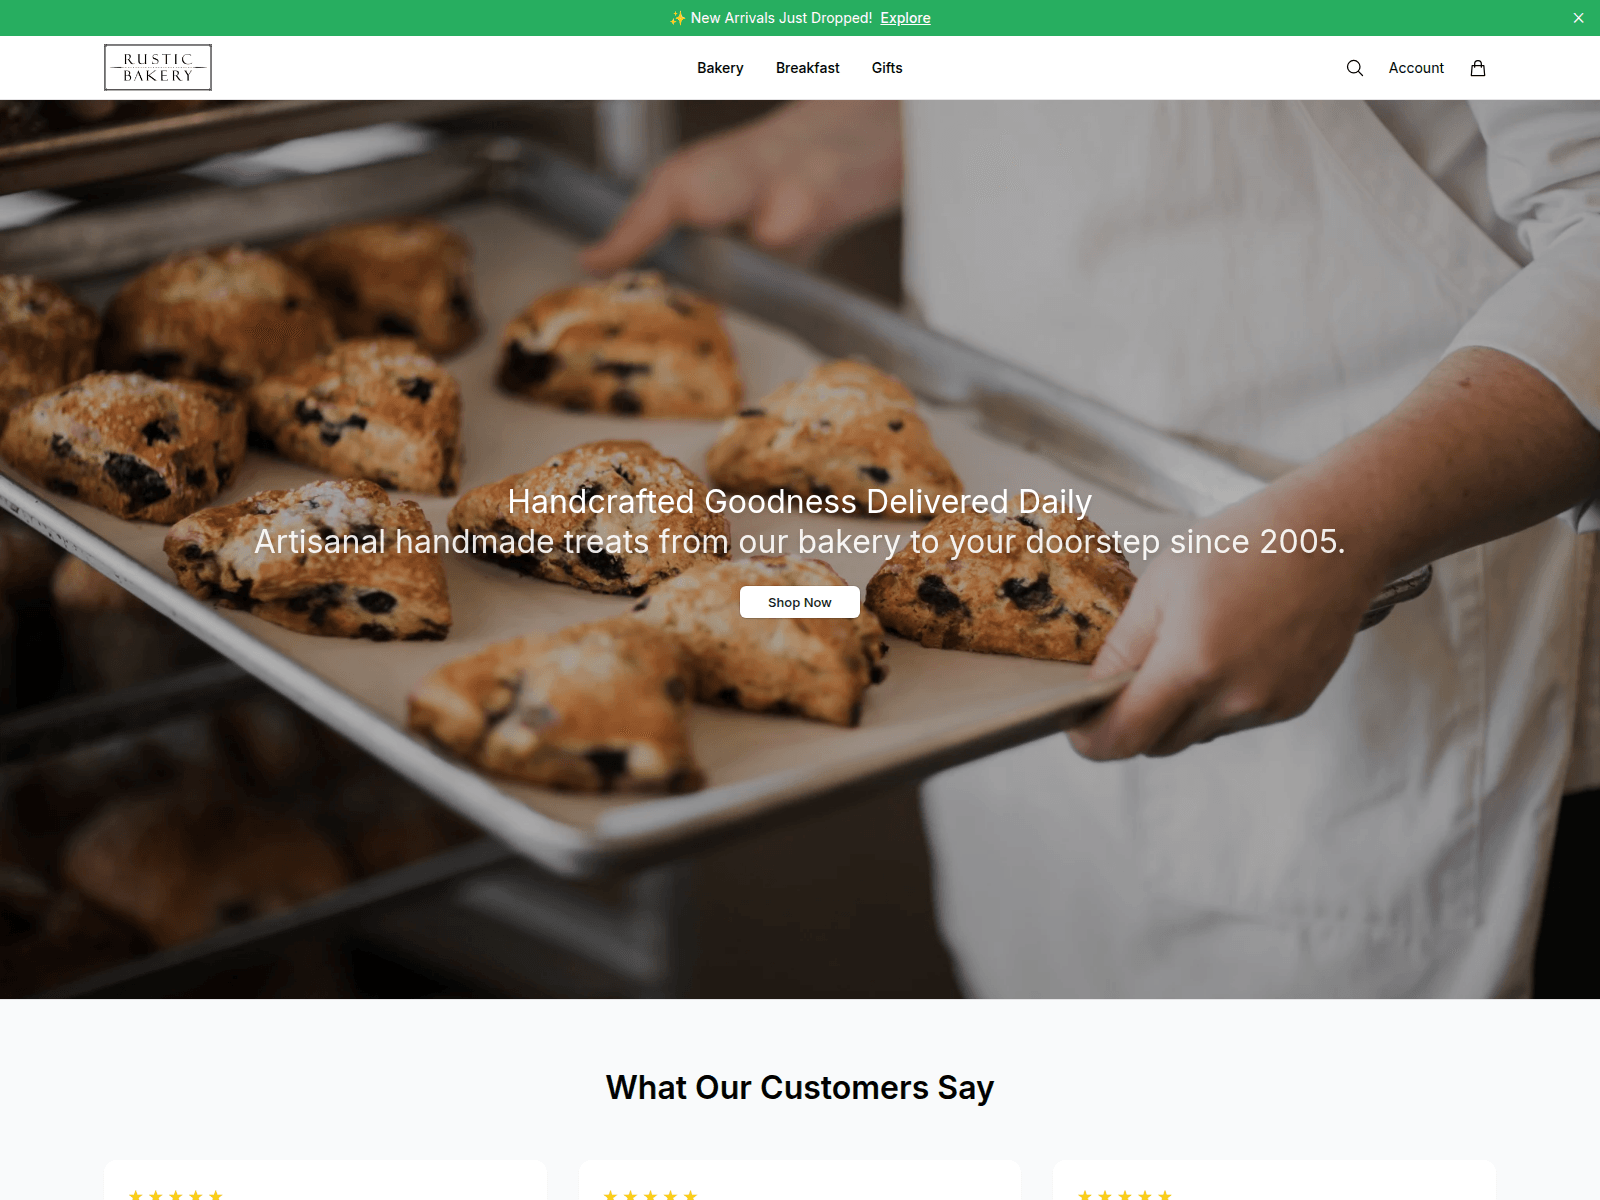
“Fine Organic Foods & Handcrafted Baked Goods | Rustic Bakery”
bakemod.shop — آخر نشاط معروف (HTTP 200). انتحال العلامة التجارية: Fakeshop; نوع الاحتيال: Impersonation. ملخص الأدلة: URLScan malicious verdict; Spamhaus DBL_SPAM; PhishDestroy score 73/100.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.

bakemod.shop was observed in a PhishDestroy internal listing on 2026-10-10, providing a dated record of its inclusion. The domain's IP address was also recorded as 162.222.90.215, adding a technical detail to the available evidence.
PhishDestroy recorded an internal listing for bakemod.shop on 2026-10-10. The domain's IP address at the time was documented as 162.222.90.215. The first observed date for bakemod.shop is 2026-10-10.
The PhishDestroy source contains an internal listing, which documents bakemod.shop as cataloged in its records as of the observation date. This type of measurement provides a reference point for the domain's presence in the source's listings. The recorded IP address adds technical context to the domain's network footprint at that time.
For bakemod.shop, preserve the PhishDestroy internal listing as a key record for future reference. Compare this record with any subsequent observations to monitor changes in its status or presence in security intelligence sources.
الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».
ملاحظة خاصة بالماسح الضوئي: alive_content: raw=ok; http=200; via=https_proxy
annabel.ns.cloudflare.comweston.ns.cloudflare.comLocation describes the IP network.
39030f42fac3971eef30f912db64035d39b17f3340b5fc8f9cd7584cb9f54c8eSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
162.222.90.215. 10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261010-AE3381 Recipient: abuse@rashost.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Template-based draft · optional AI wording assistance requires separate consent
كل مسار يمثل سببًا واحدًا لربط نطاق ما بهذا المضيف. يشير حجم العقدة إلى عمليات الكشف التي أجرتها VirusTotal، أما العقد المتقطعة فهي غير متصلة بالإنترنت بالفعل. وترد القوائم الكاملة أدناه.
يستضيف عنوان IP الأصلي هذا العديد من مجالات التصيد الاحتيالي — وقد تتم مشاركة البنية التحتية عبر الحملات.
كما تستهدف هذه النطاقات مستخدمي موقع Fakeshop. عرض جميع التهديدات المتعلقة بـ «Fakeshop» →
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب