
ابحث في النطاقات الخاضعة للمراقبة وراجع الأدلة المخزنة وعمليات الكشف وأحدث حالة التوافر التي تمت ملاحظتها.
219,806
الإجمالي المتتبع
213,476
تم الكشف عن VT
91,911
شوهد آخر مرة نشطًا
127,895
غير متوفر عند آخر تحقق
568
في انتظار الموافقة من VT
How This Attack Works
Fake Token Presale scams trick victims into believing they are investing in legitimate cryptocurrency projects. Here's how the scam typically unfolds:
STEP 1
Create Fake Websites
Scammers set up realistic-looking websites mimicking legitimate token presale portals.
STEP 2
Promote Presale on Social Media
Using social media and fake endorsements, scammers attract potential investors.
STEP 3
Collect Cryptocurrency
Victims are prompted to send cryptocurrency to a specified address under the guise of buying tokens.
STEP 4
Disappear with Funds
Once funds are collected, scammers shut down the site and disappear, leaving victims without recourse.
Technical Analysis
Fake Token Presale scams often leverage phishing tactics combined with cryptocurrency-specific techniques. Attackers use homograph attacks to create URLs that closely resemble legitimate sites, often registered through top registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED and PDR Ltd. d/b/a PublicDomainRegistry.com. They exploit the decentralized nature of blockchain networks, utilizing smart contracts that mimic legitimate presale contracts but are programmed to divert funds to the attacker’s wallet. The infrastructure often involves cloud-based hosting services to quickly deploy and dismantle sites, minimizing the chance of detection. HTML and JavaScript are commonly used to create dynamic, convincing interfaces that reassure potential victims of the site’s legitimacy. Additionally, attackers might deploy SEO techniques to improve the visibility of their fraudulent sites in search engine results, further increasing their reach.
Real Cases
CryptoX Presale Scam (2024)
$2 million stolen
A fake presale for a non-existent token, CryptoX, duped investors into contributing significant sums.
TokenLaunch Fraud (2023)
$1.5 million stolen
Victims were lured into a fake token launch with promises of high returns, only for the site to vanish post-collection.
QuickCoin Deception (2024)
$3 million stolen
Scammers created a sophisticated site mimicking a known exchange, leading to substantial financial losses.
How to Detect
تحقق for slight misspellings in domain names.
Look for inconsistent branding or layout compared to legitimate sites.
Be wary of unsolicited investment opportunities via social media.
Verify presale details on official project channels.
Beware of high-pressure tactics urging immediate investment.
How to Protect Yourself
1
Always verify URLs before entering personal information.
2
Use browser extensions to detect phishing attempts.
3
Consult official project websites or channels for presale information.
4
Enable two-factor authentication on cryptocurrency exchanges.
5
تقرير suspicious sites to authorities and platforms like PhishDestroy.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 689 domains tracked for this threat type
Fake Token Presale 689 domains
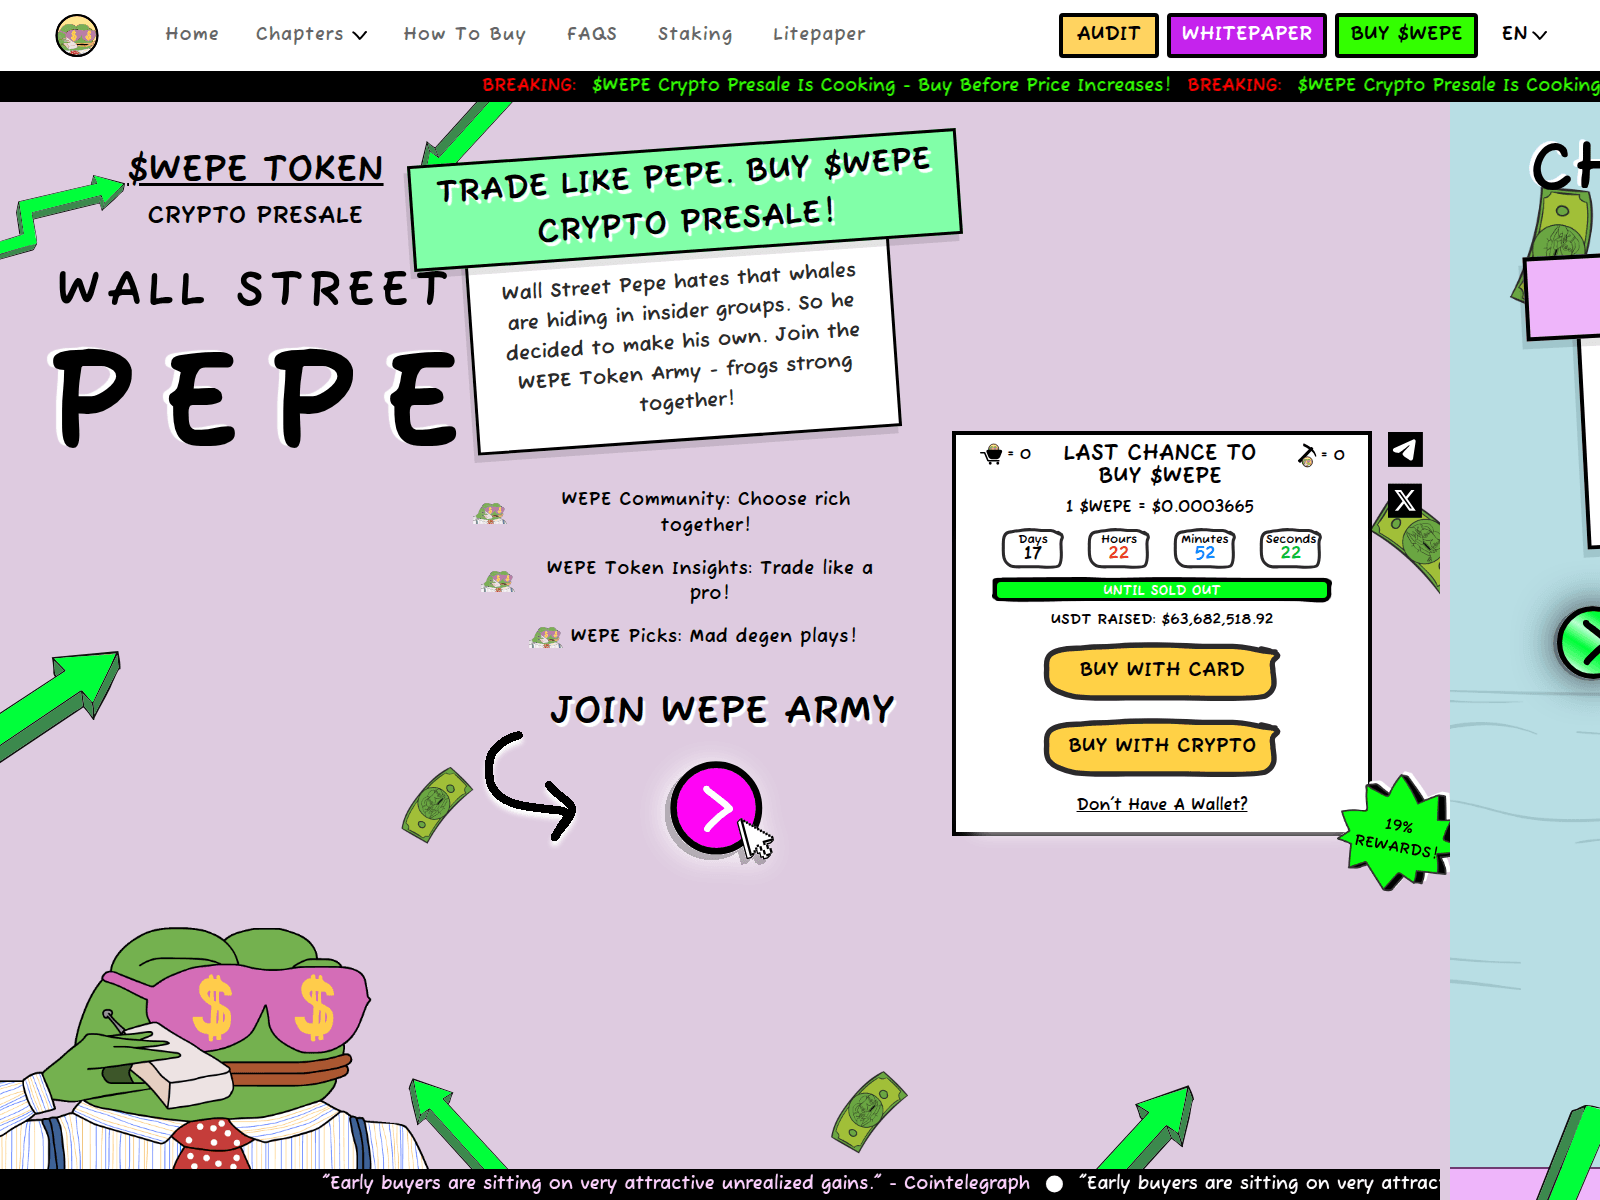
wallstreetpepe-ea2.pages.dev
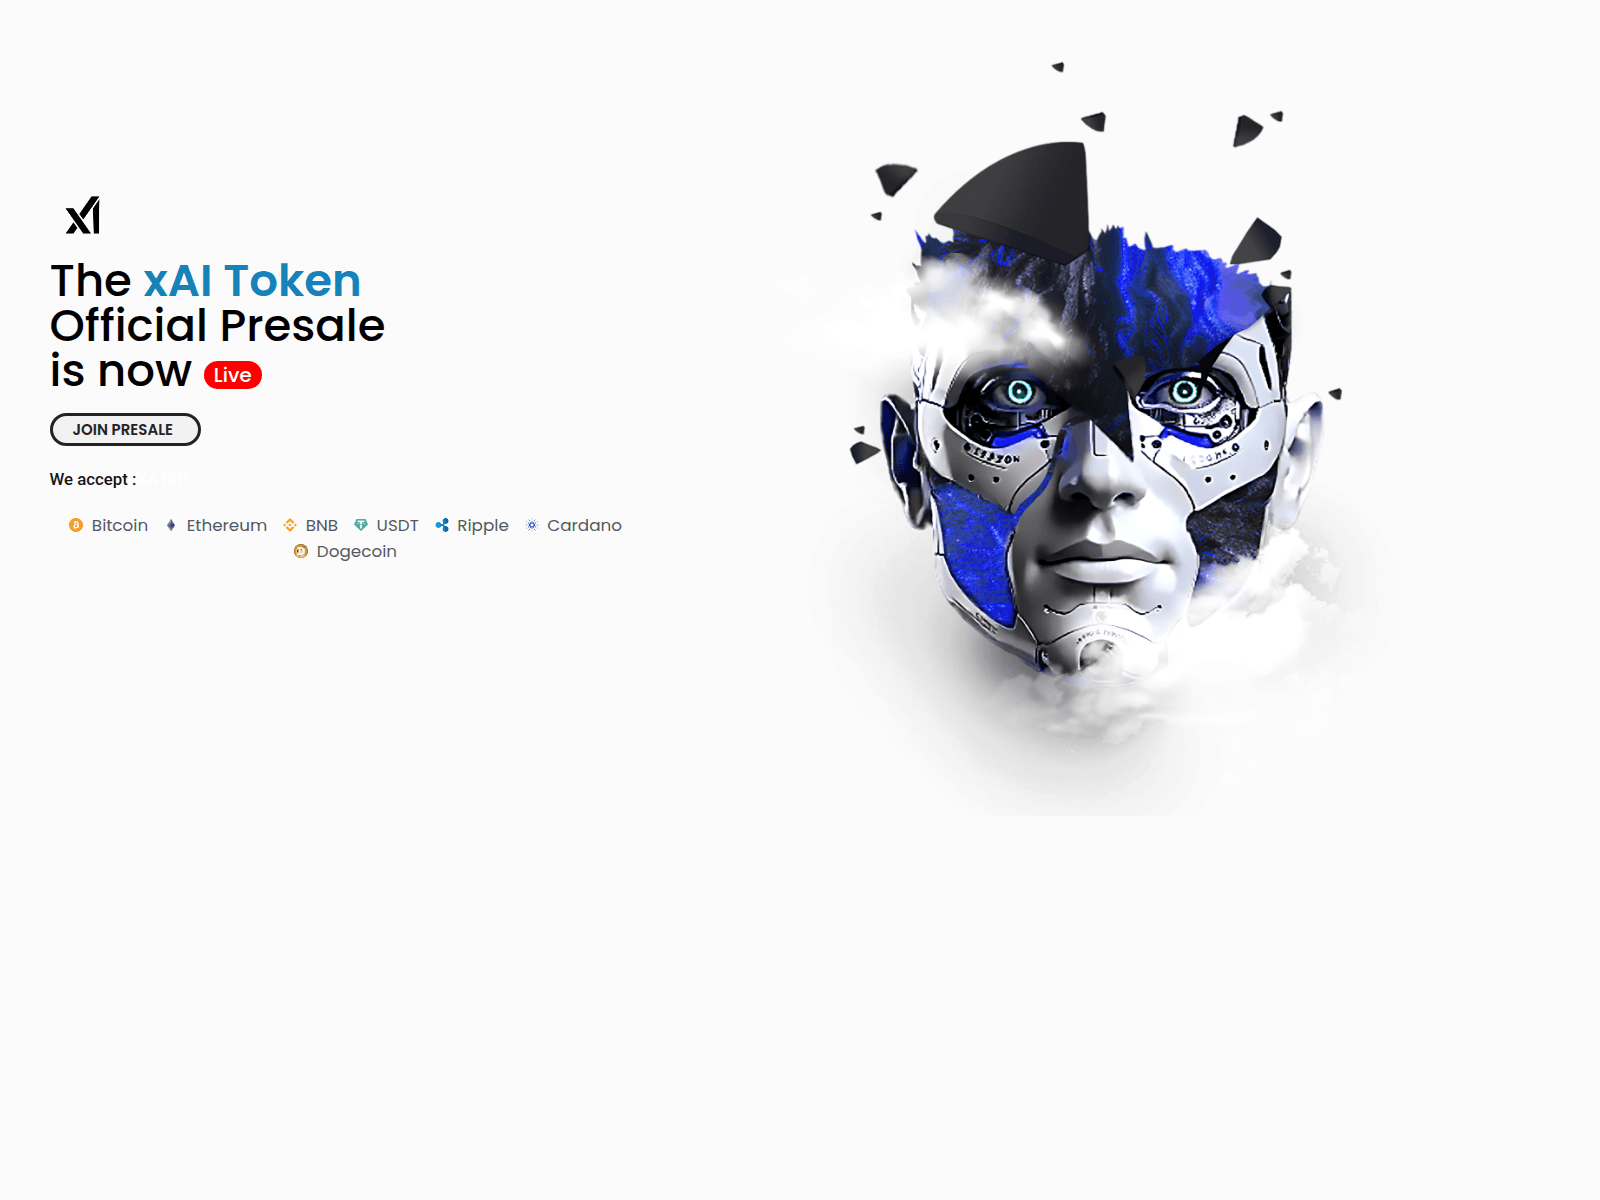
xa18p.com
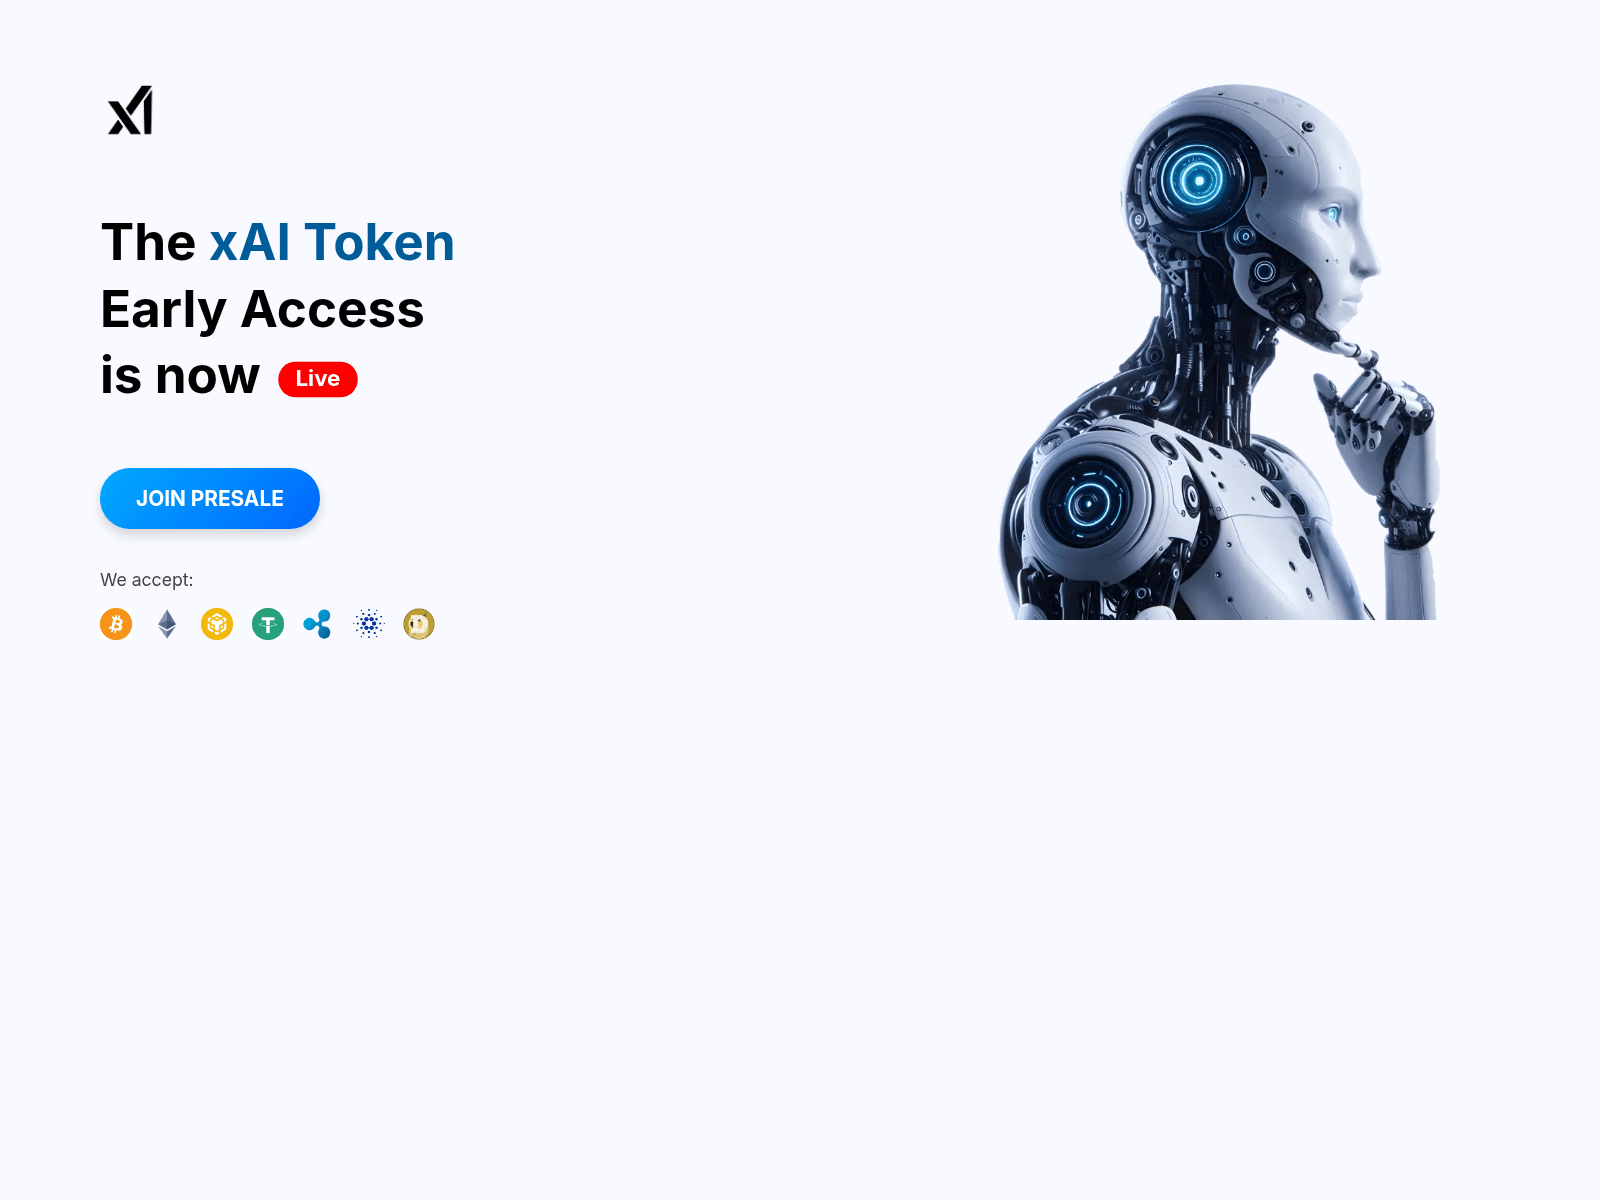
xaimconnect.net
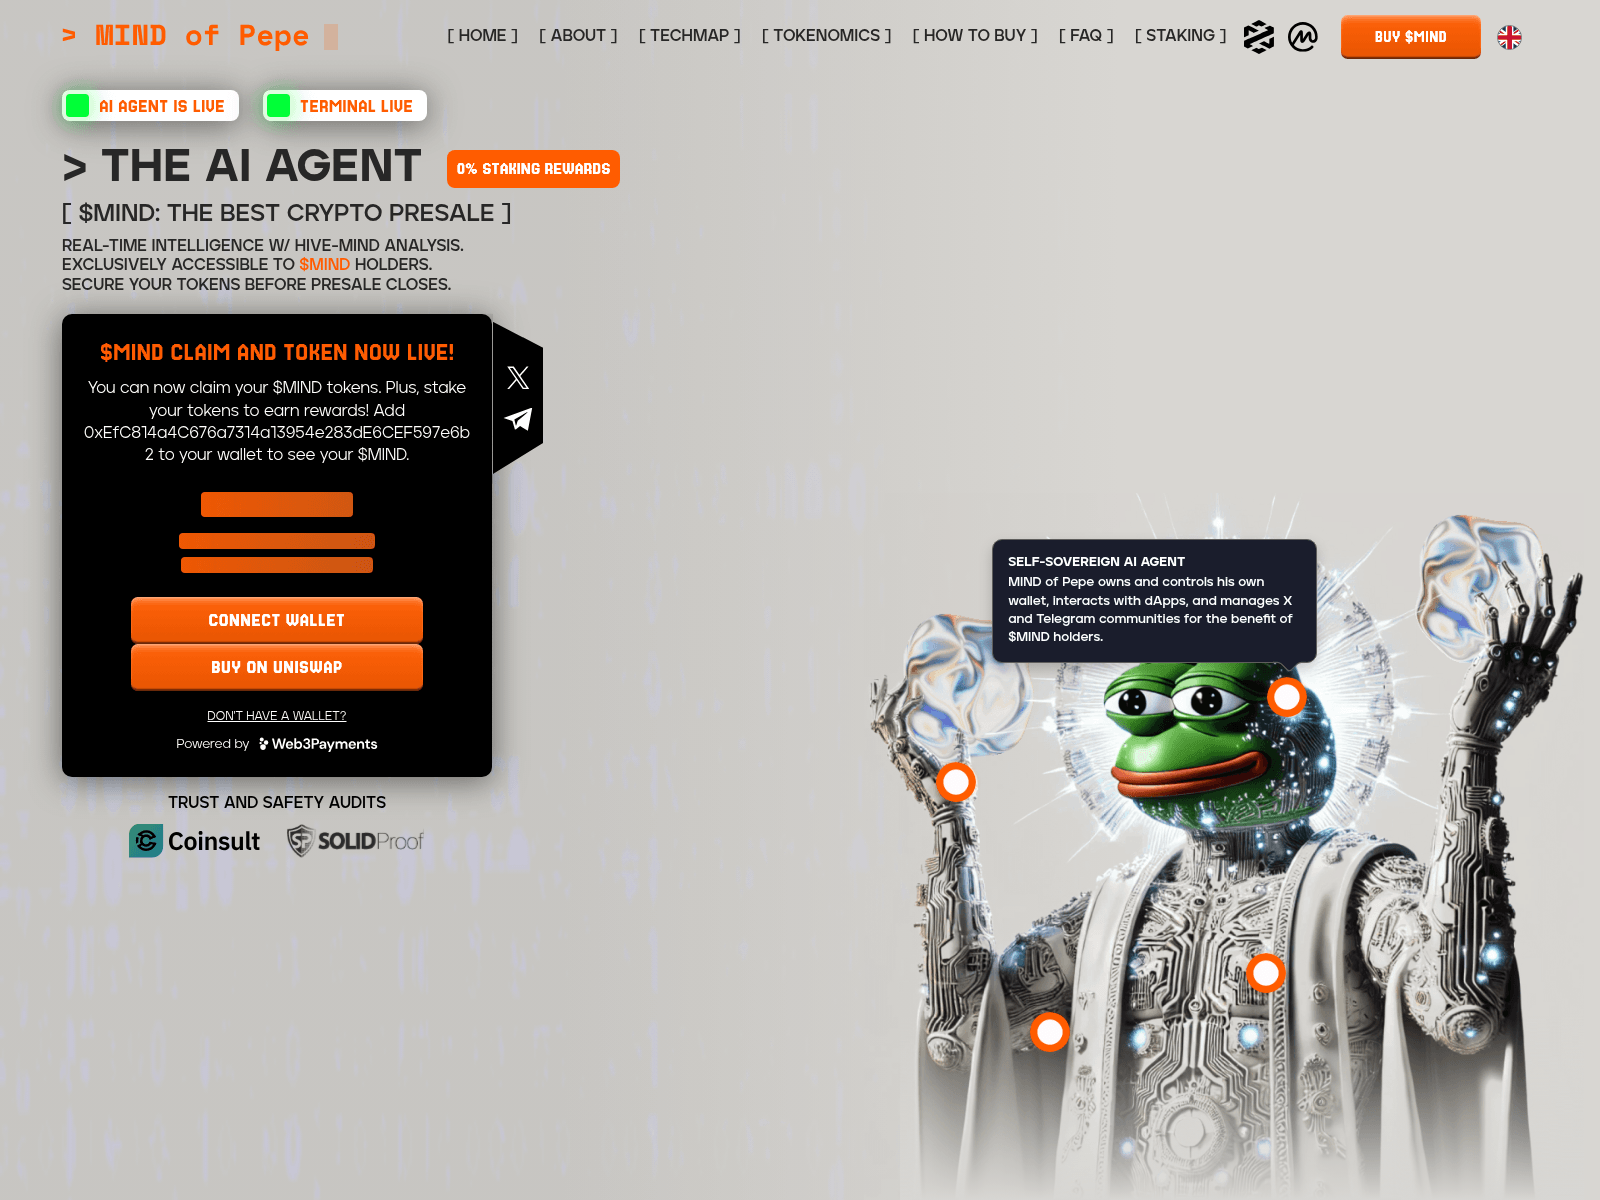
zeusai.xyz
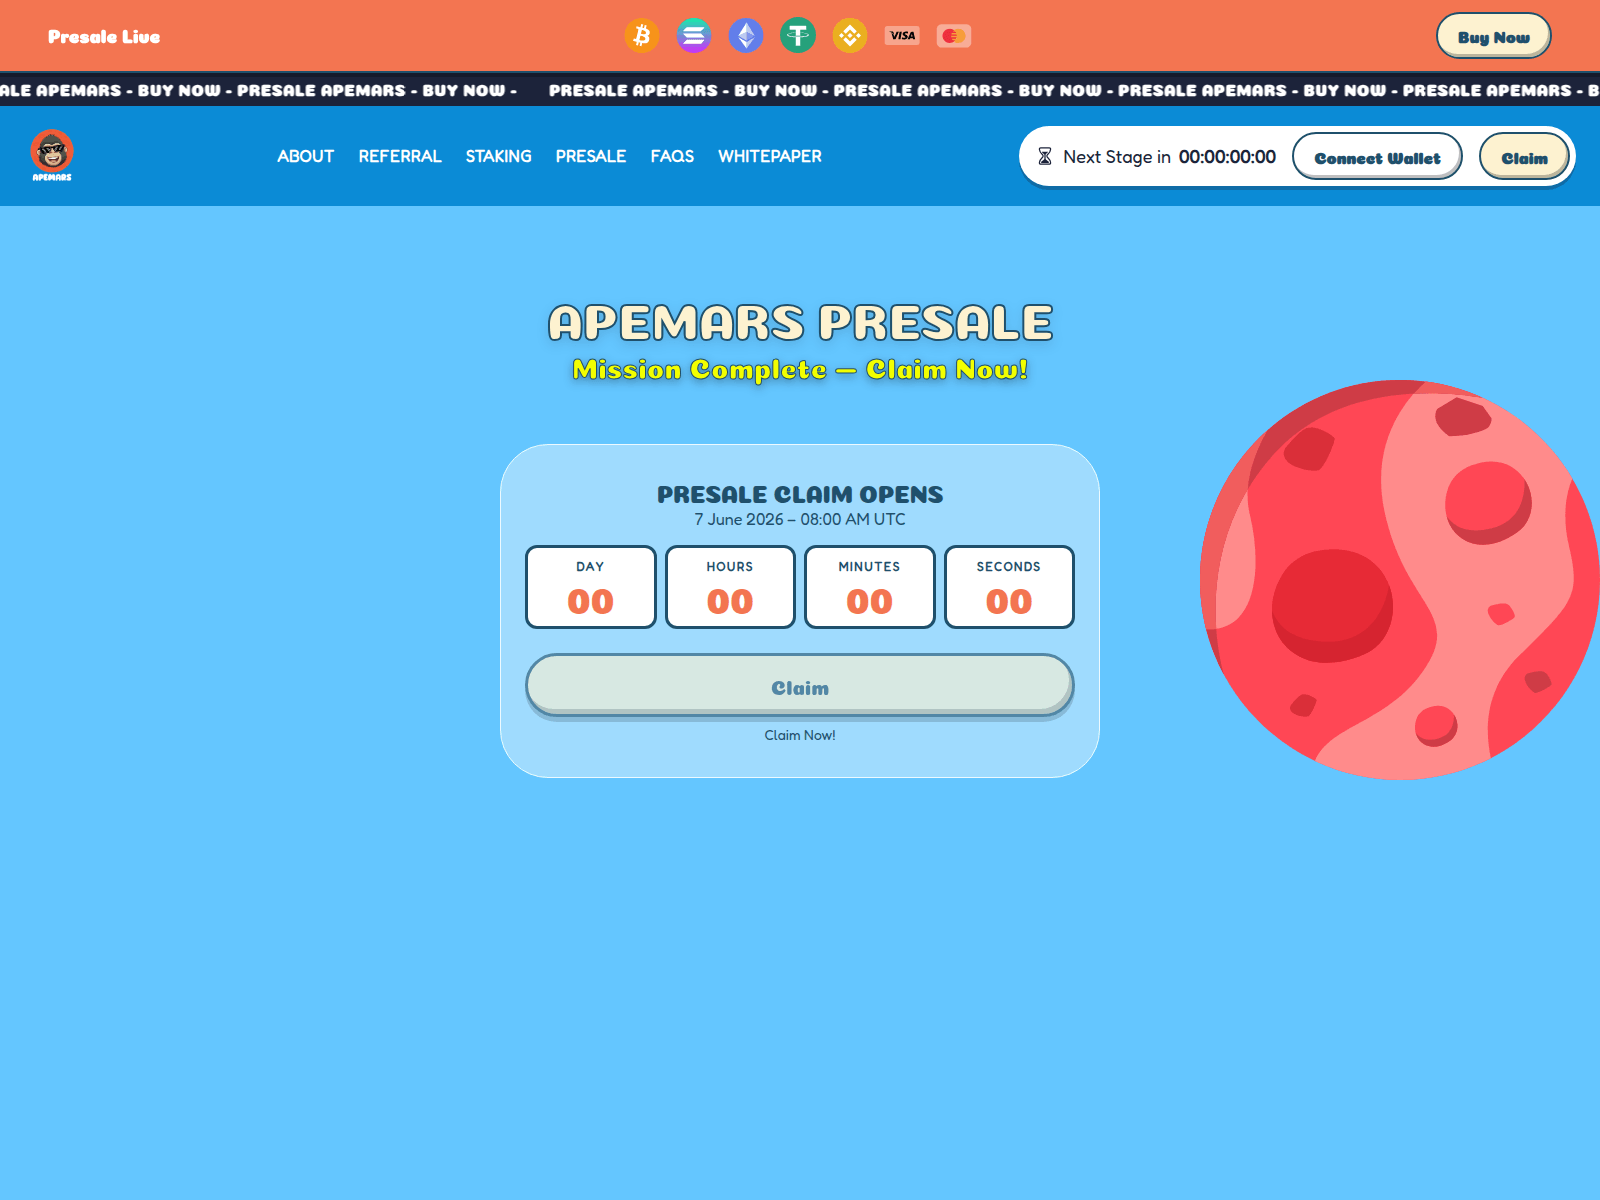
apemars-claim-presale-launch-oees33-aert0ds.pages.dev
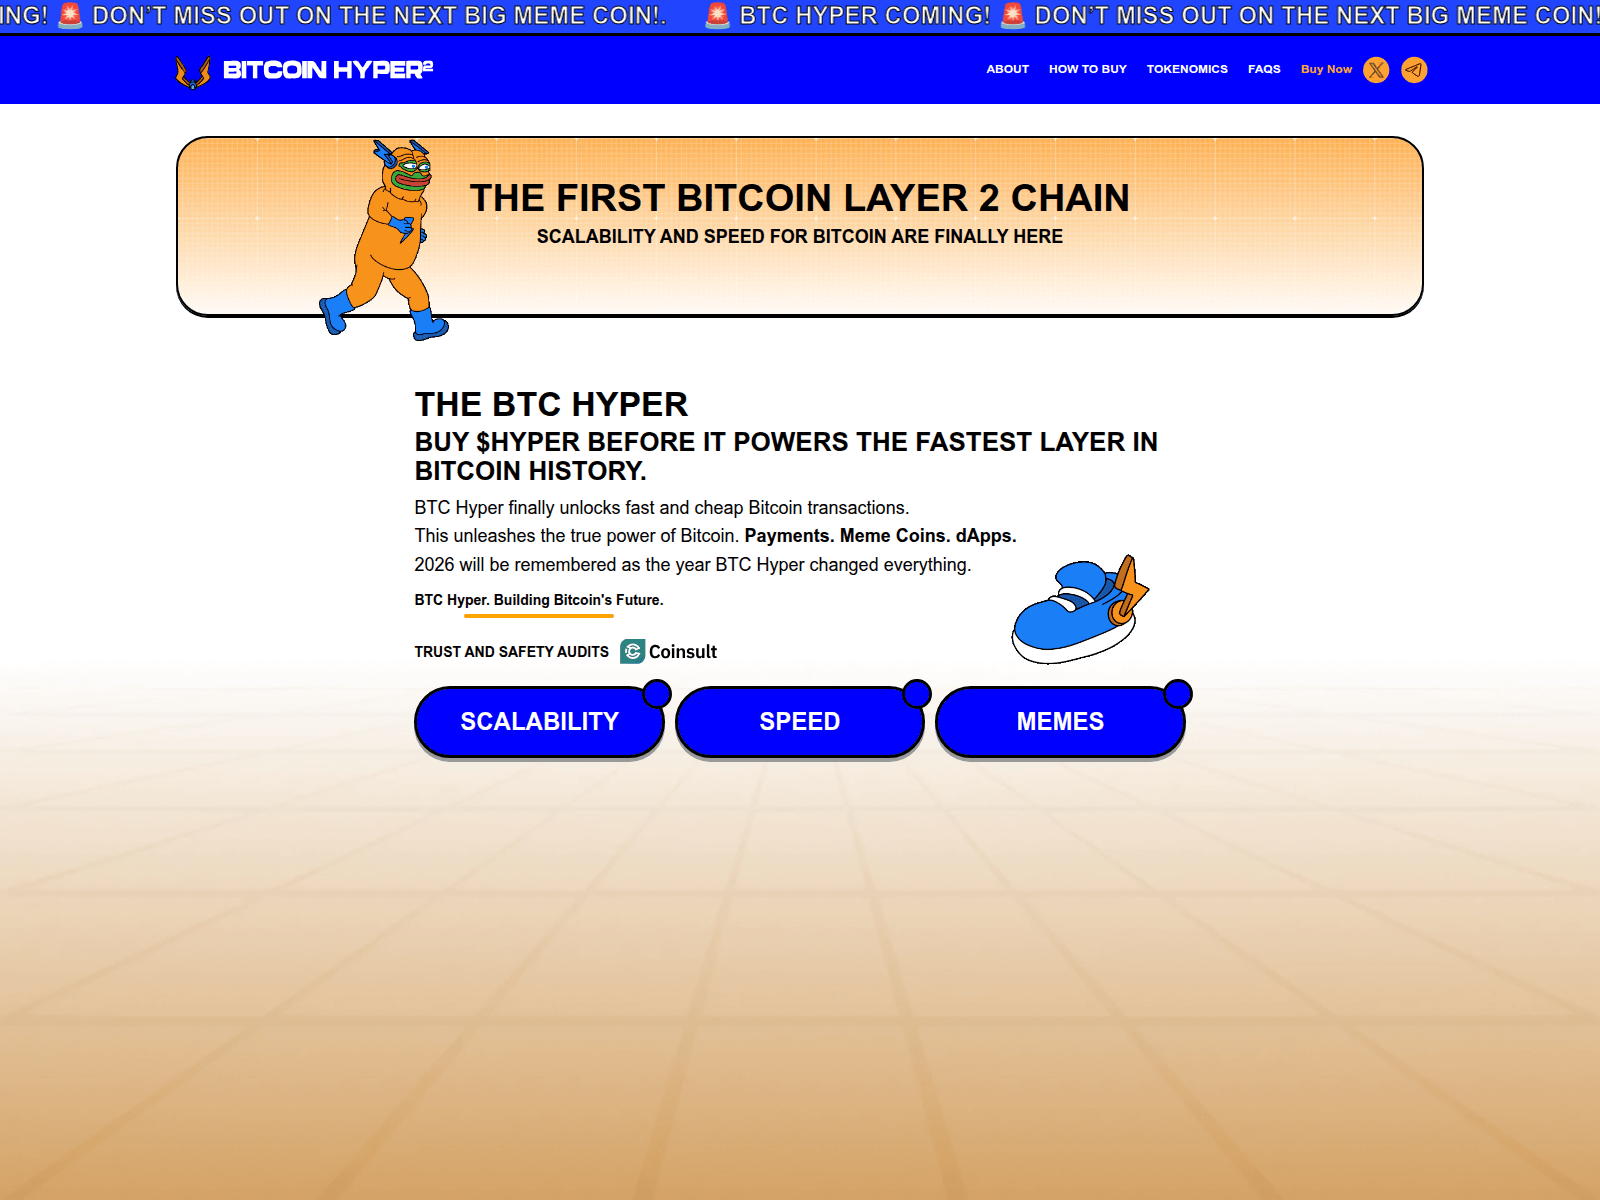
basedbtchyper.fun
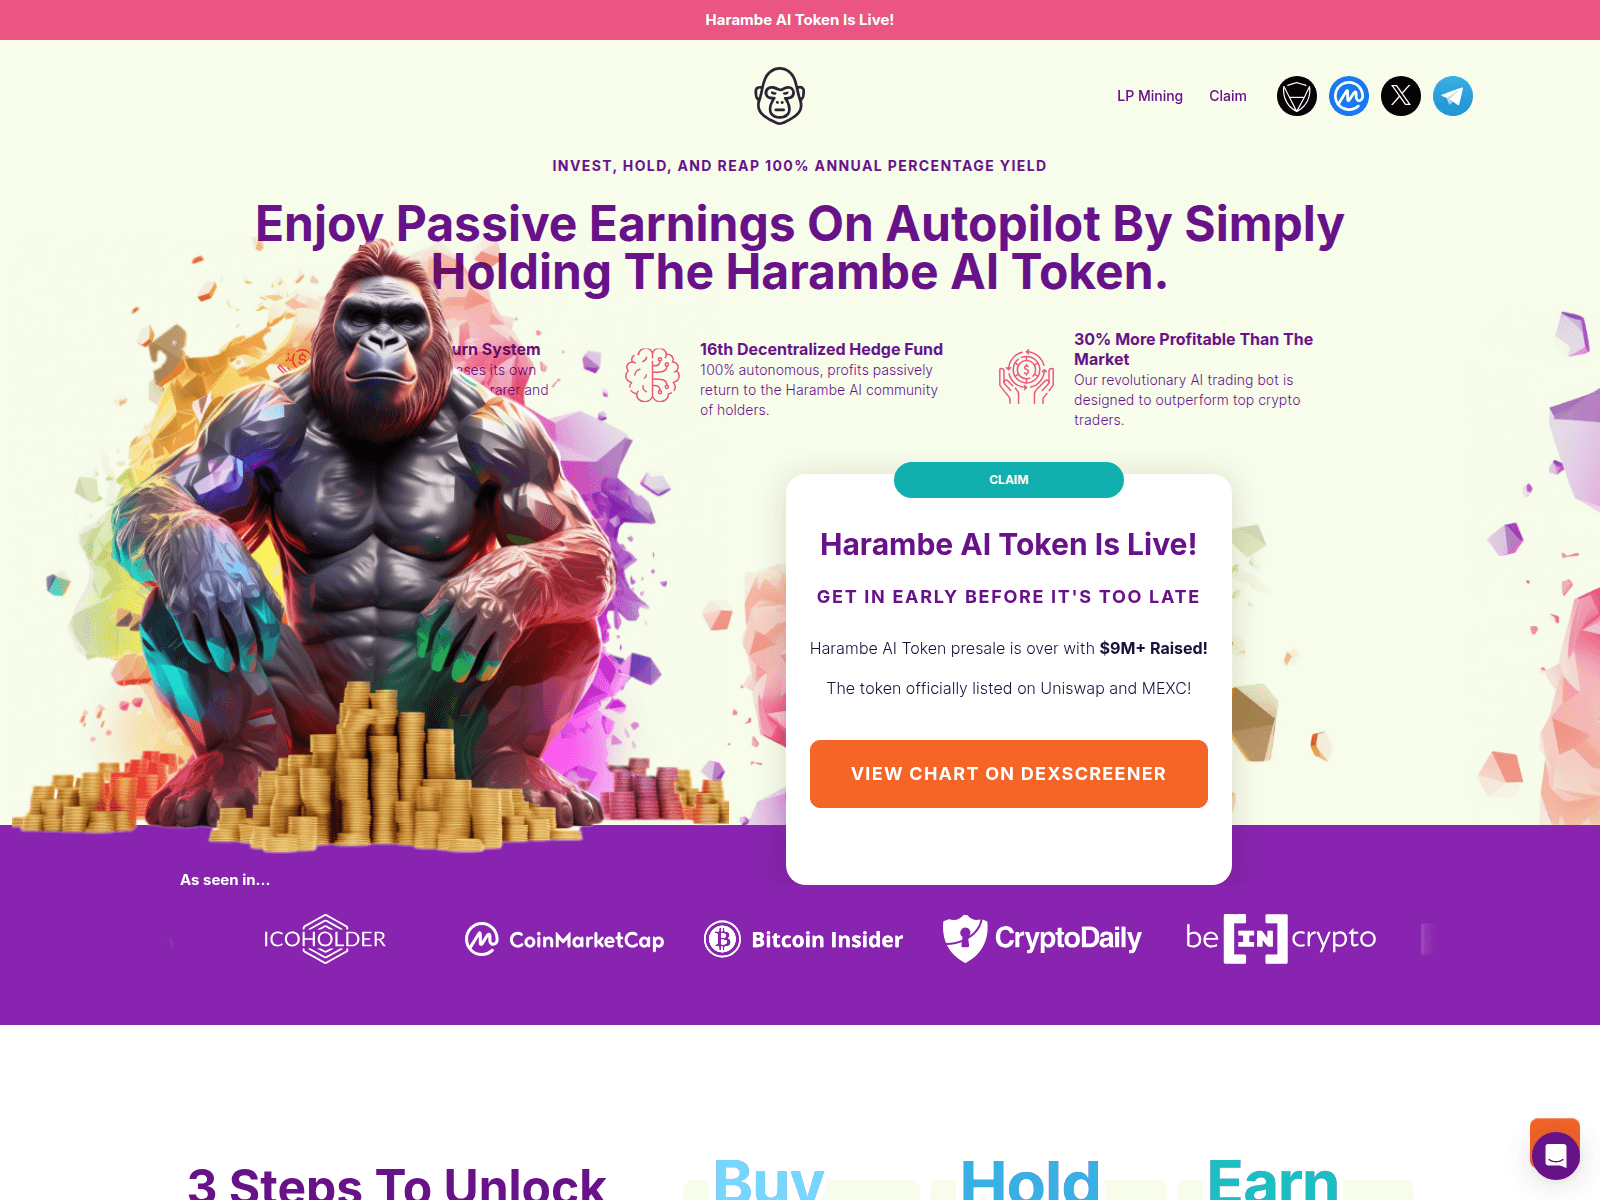
claim-harambe.pages.dev
crudoprotocol-net.web.app
dexrpcoin.pages.dev

gro89k.info
grok12k.cfd
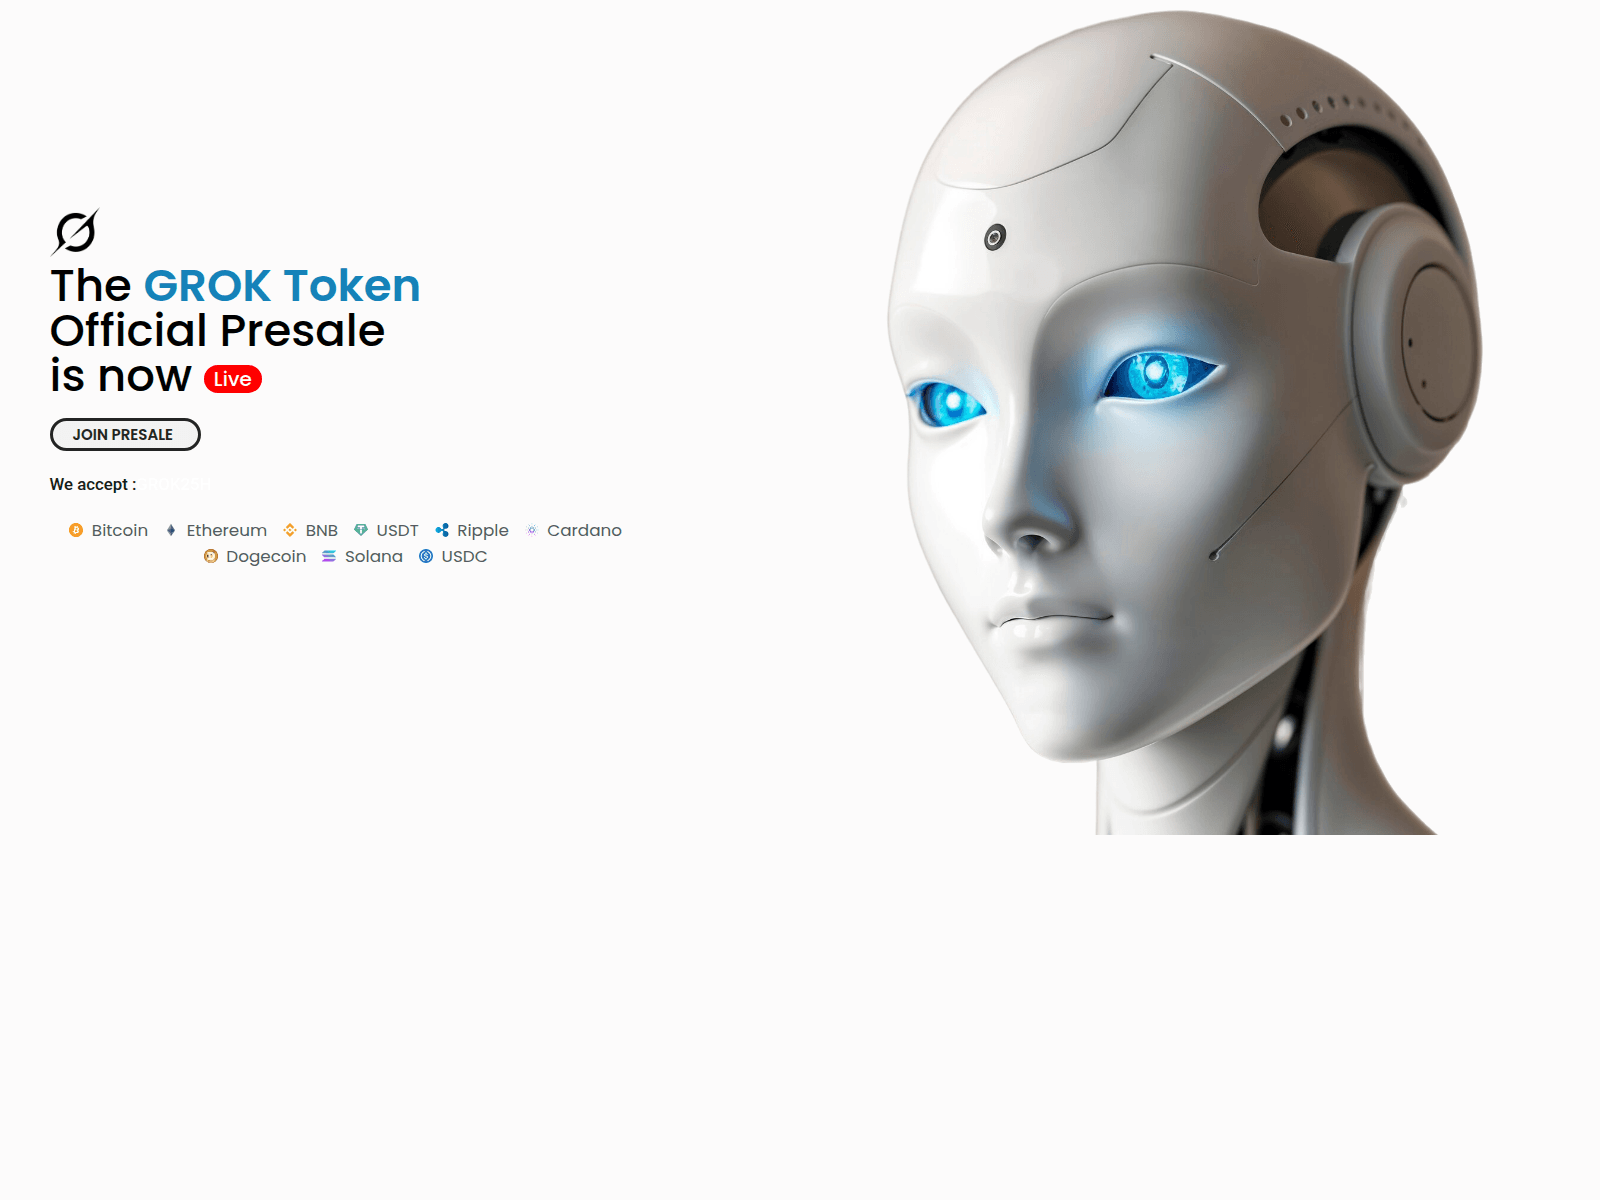
grok25h.com
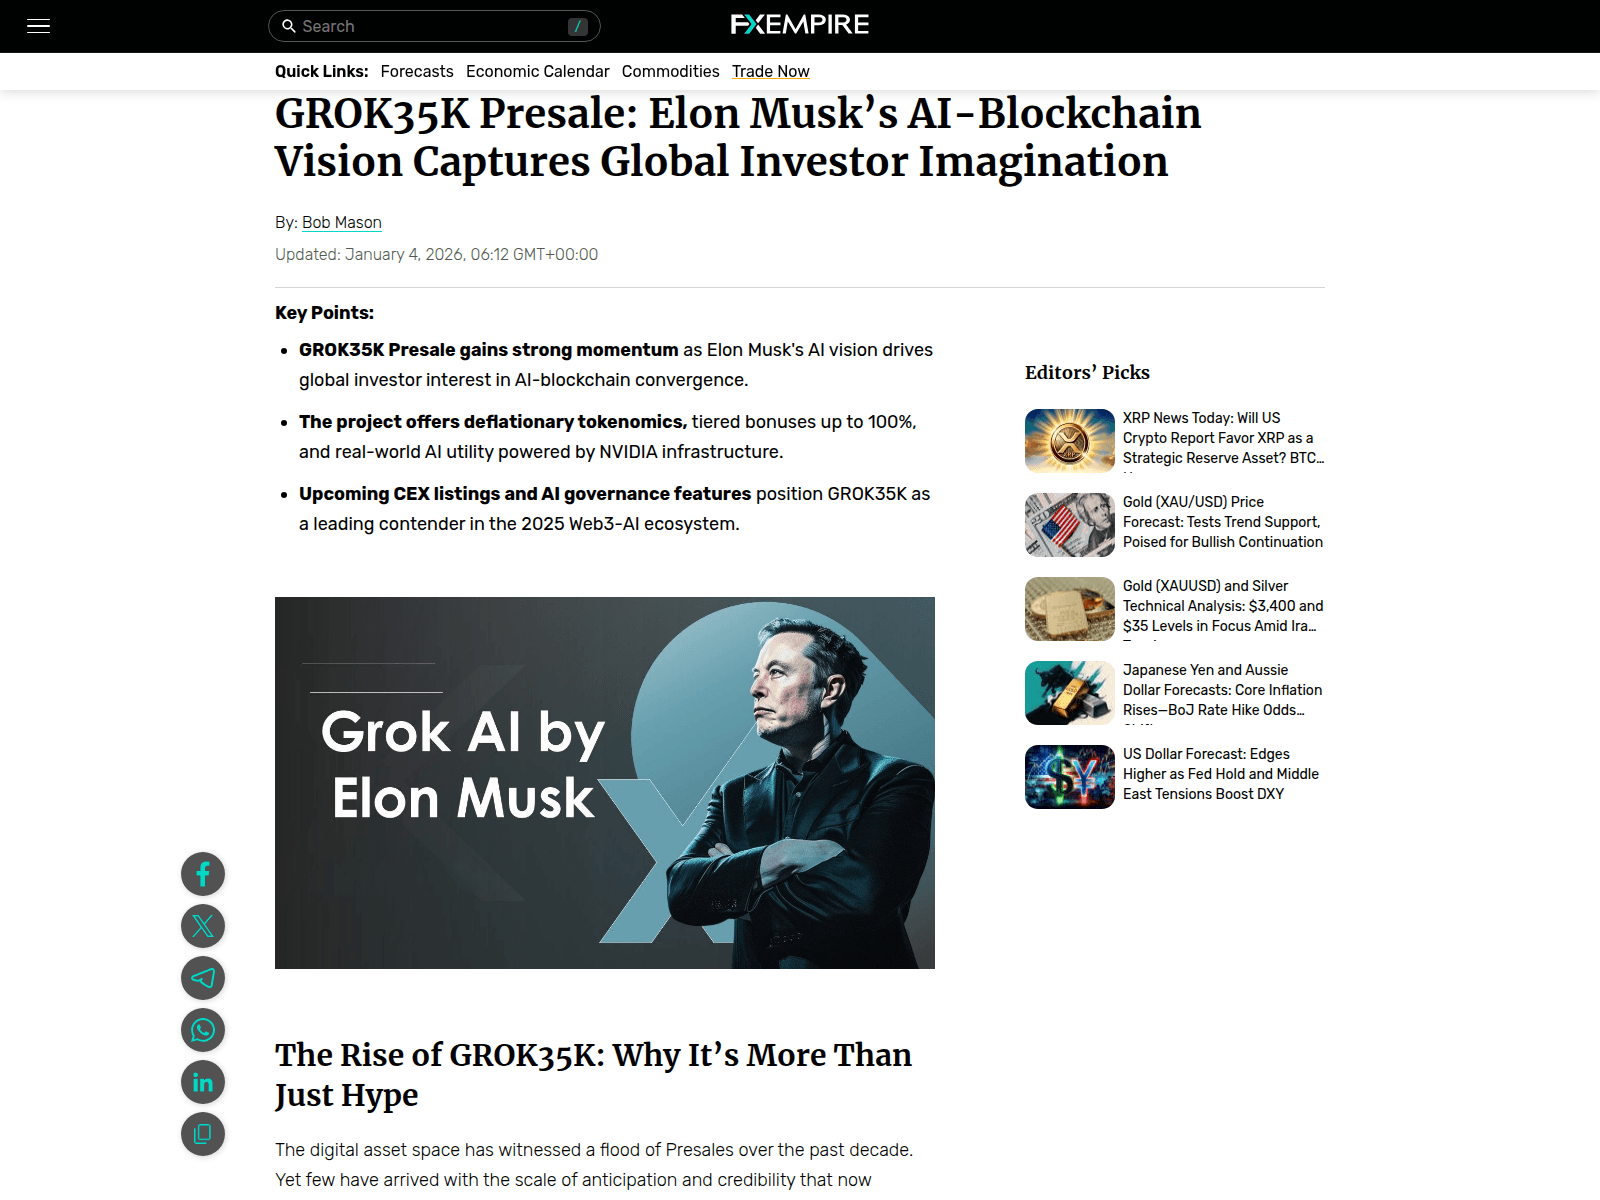
grok35k-fxempire.com
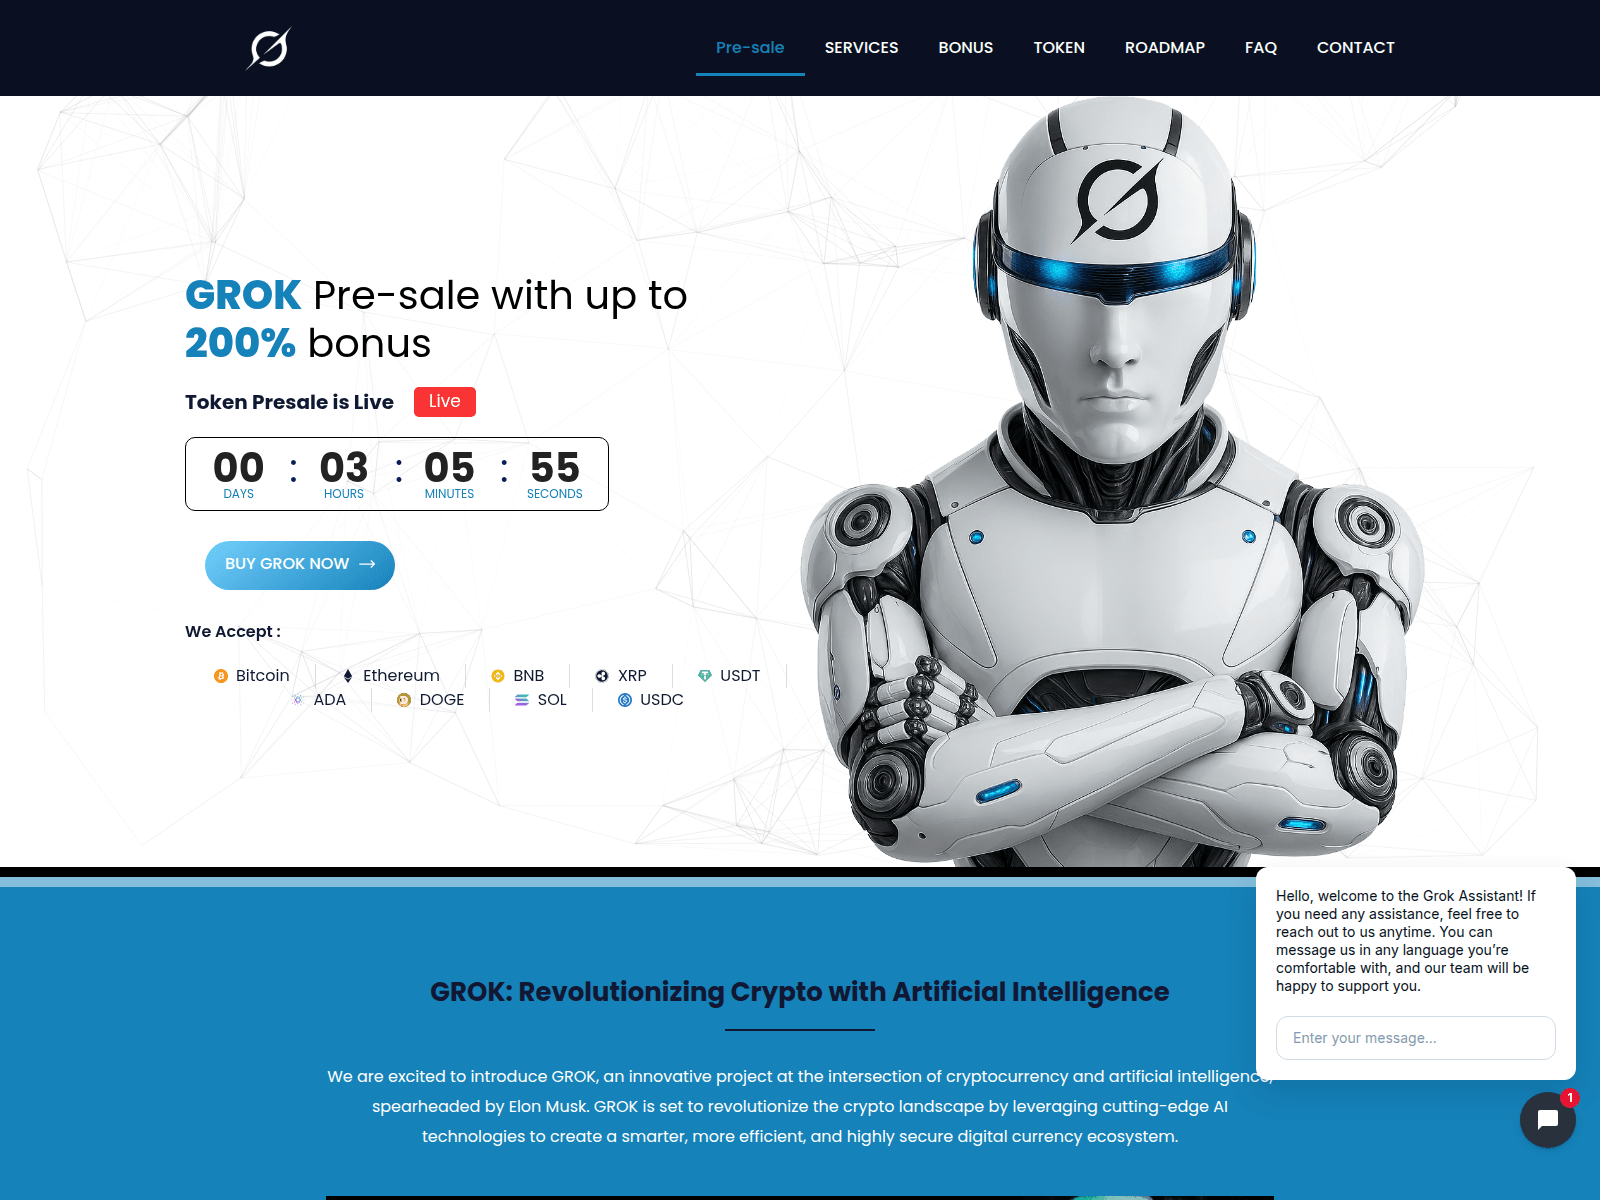
grokverse.net
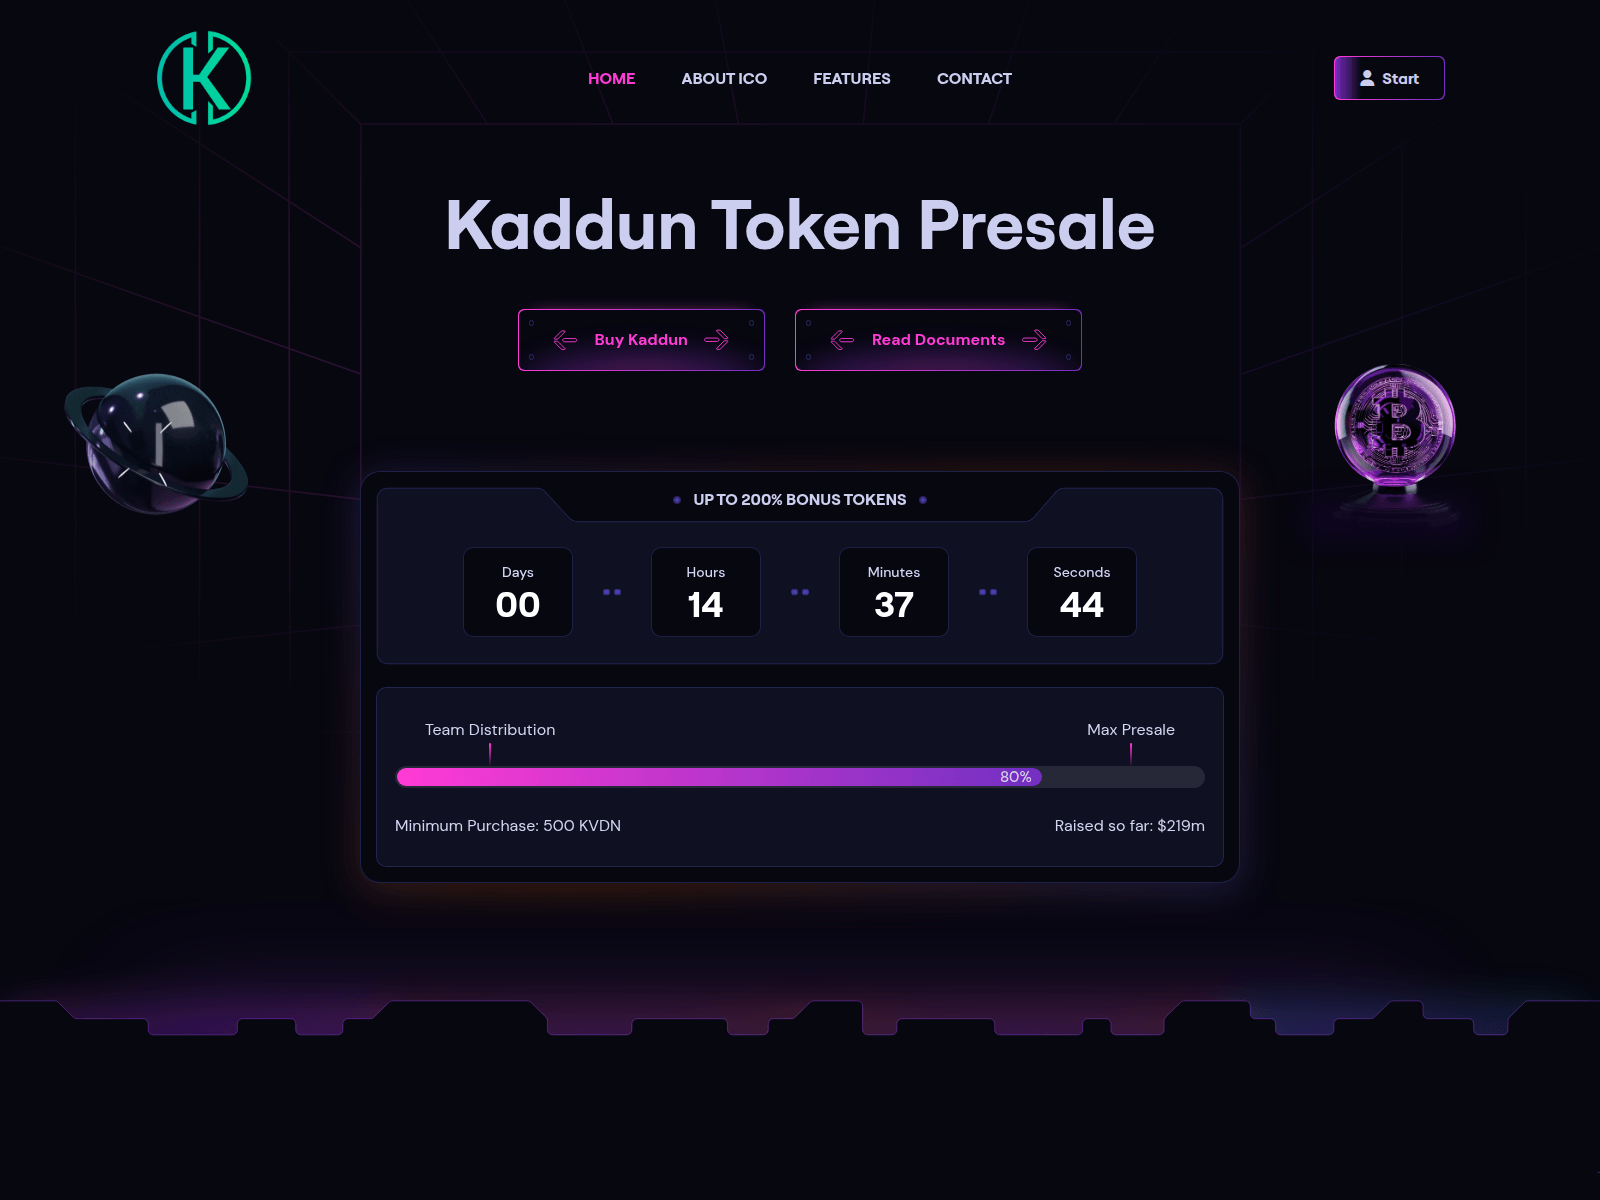
kadduntoken.com
nx0b6we.pages.dev
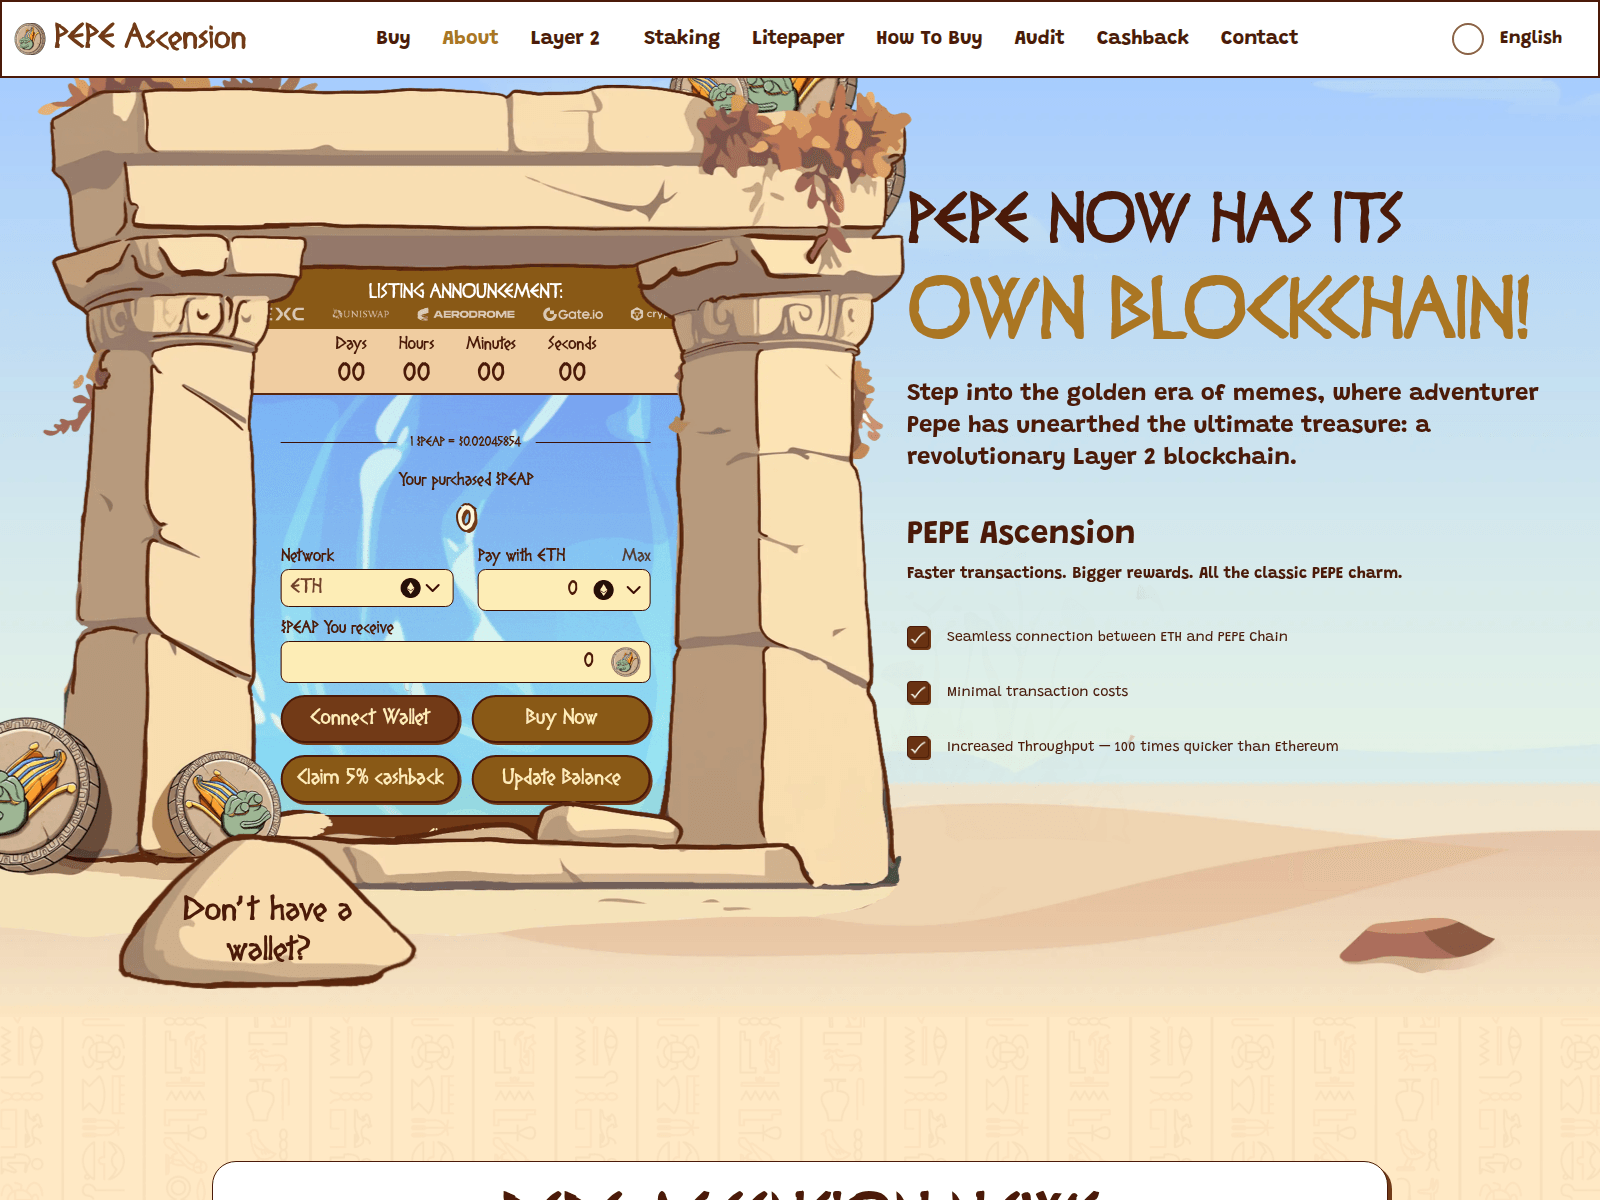
pepeascensionclaim.pages.dev
spaceswallet.net
spax40r-fxempire.com
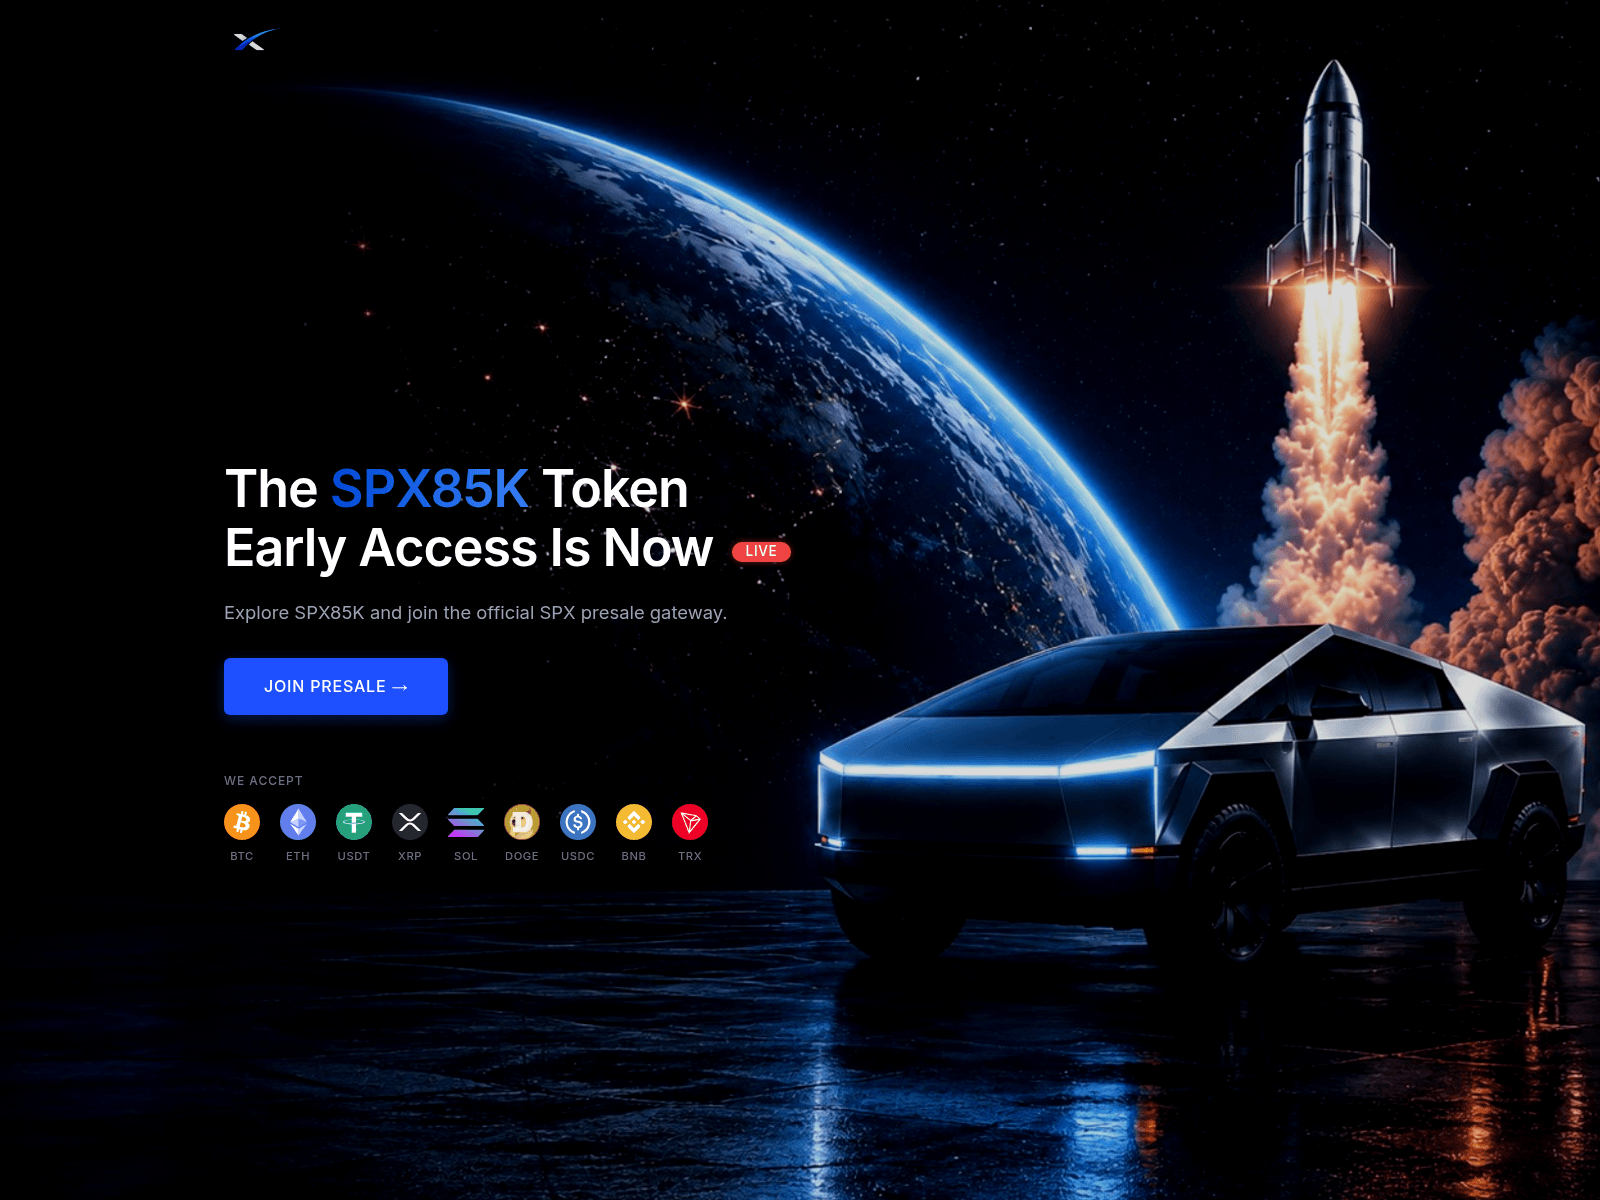
spx85k.com
xa50b.net
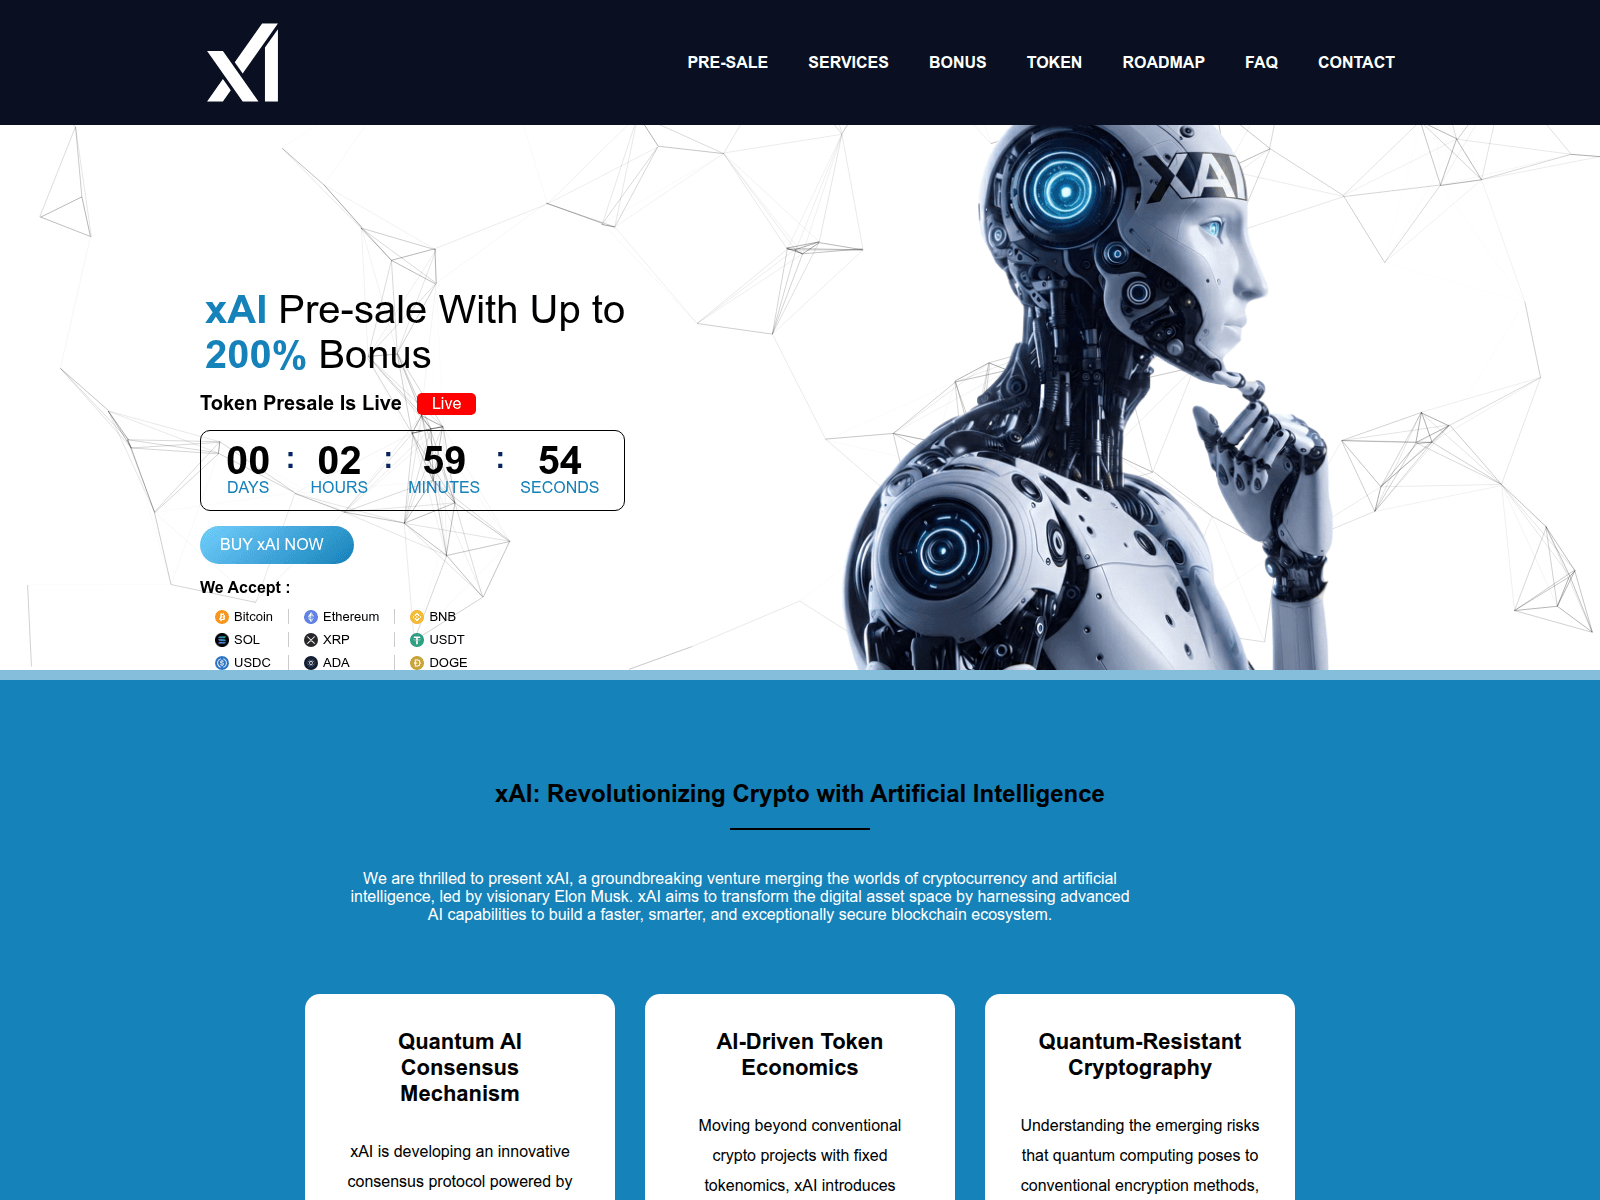
xai-xa20r.com
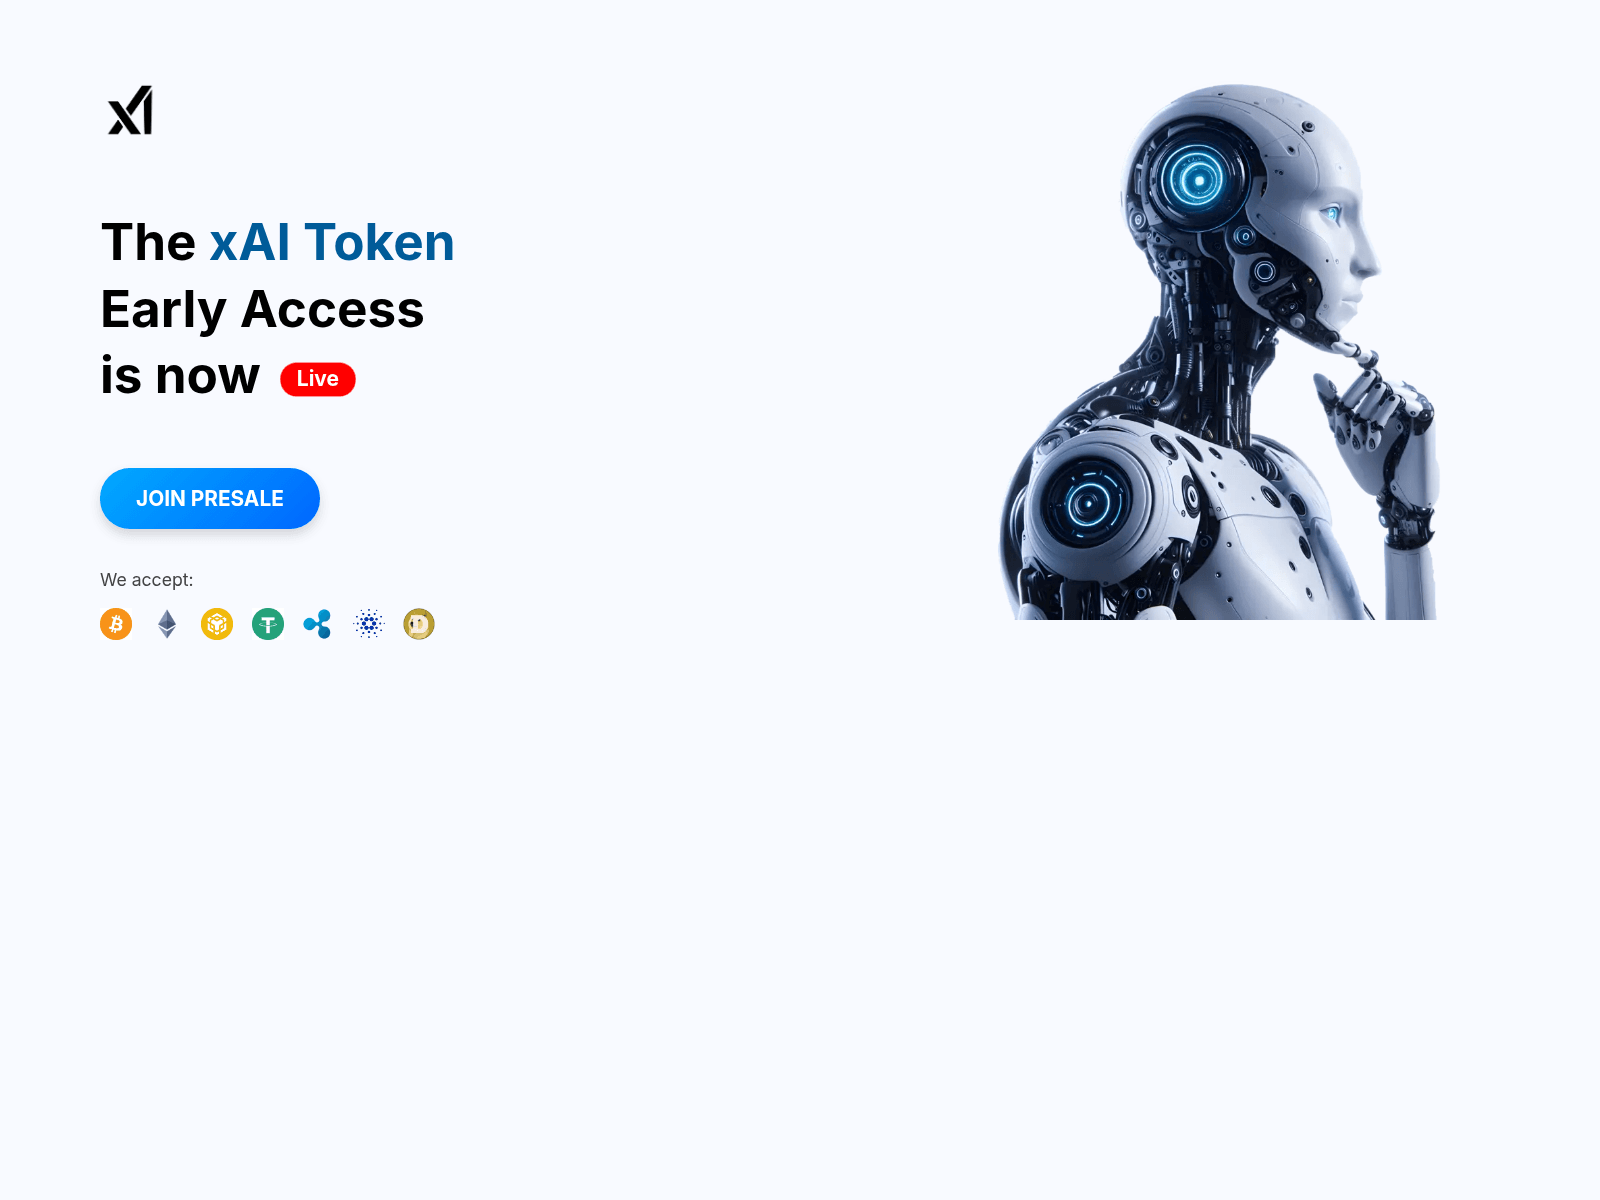
xaifusion.com
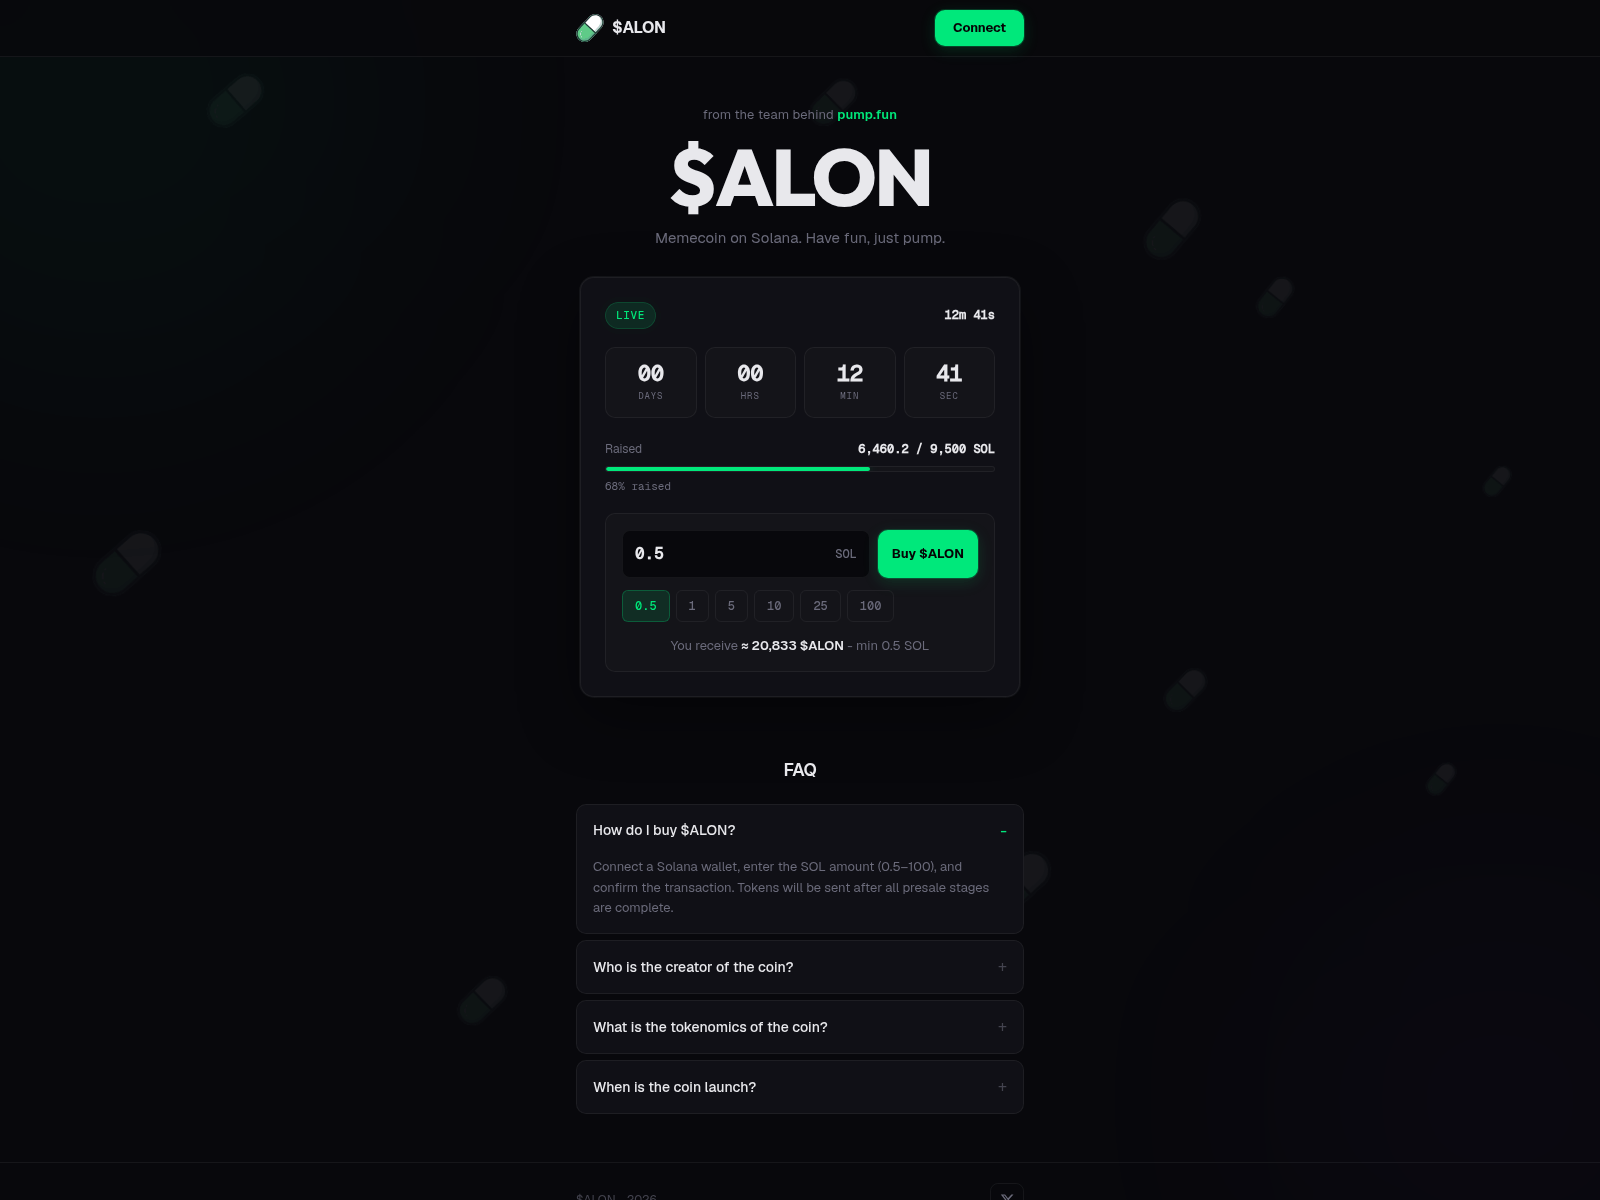
alon.sale
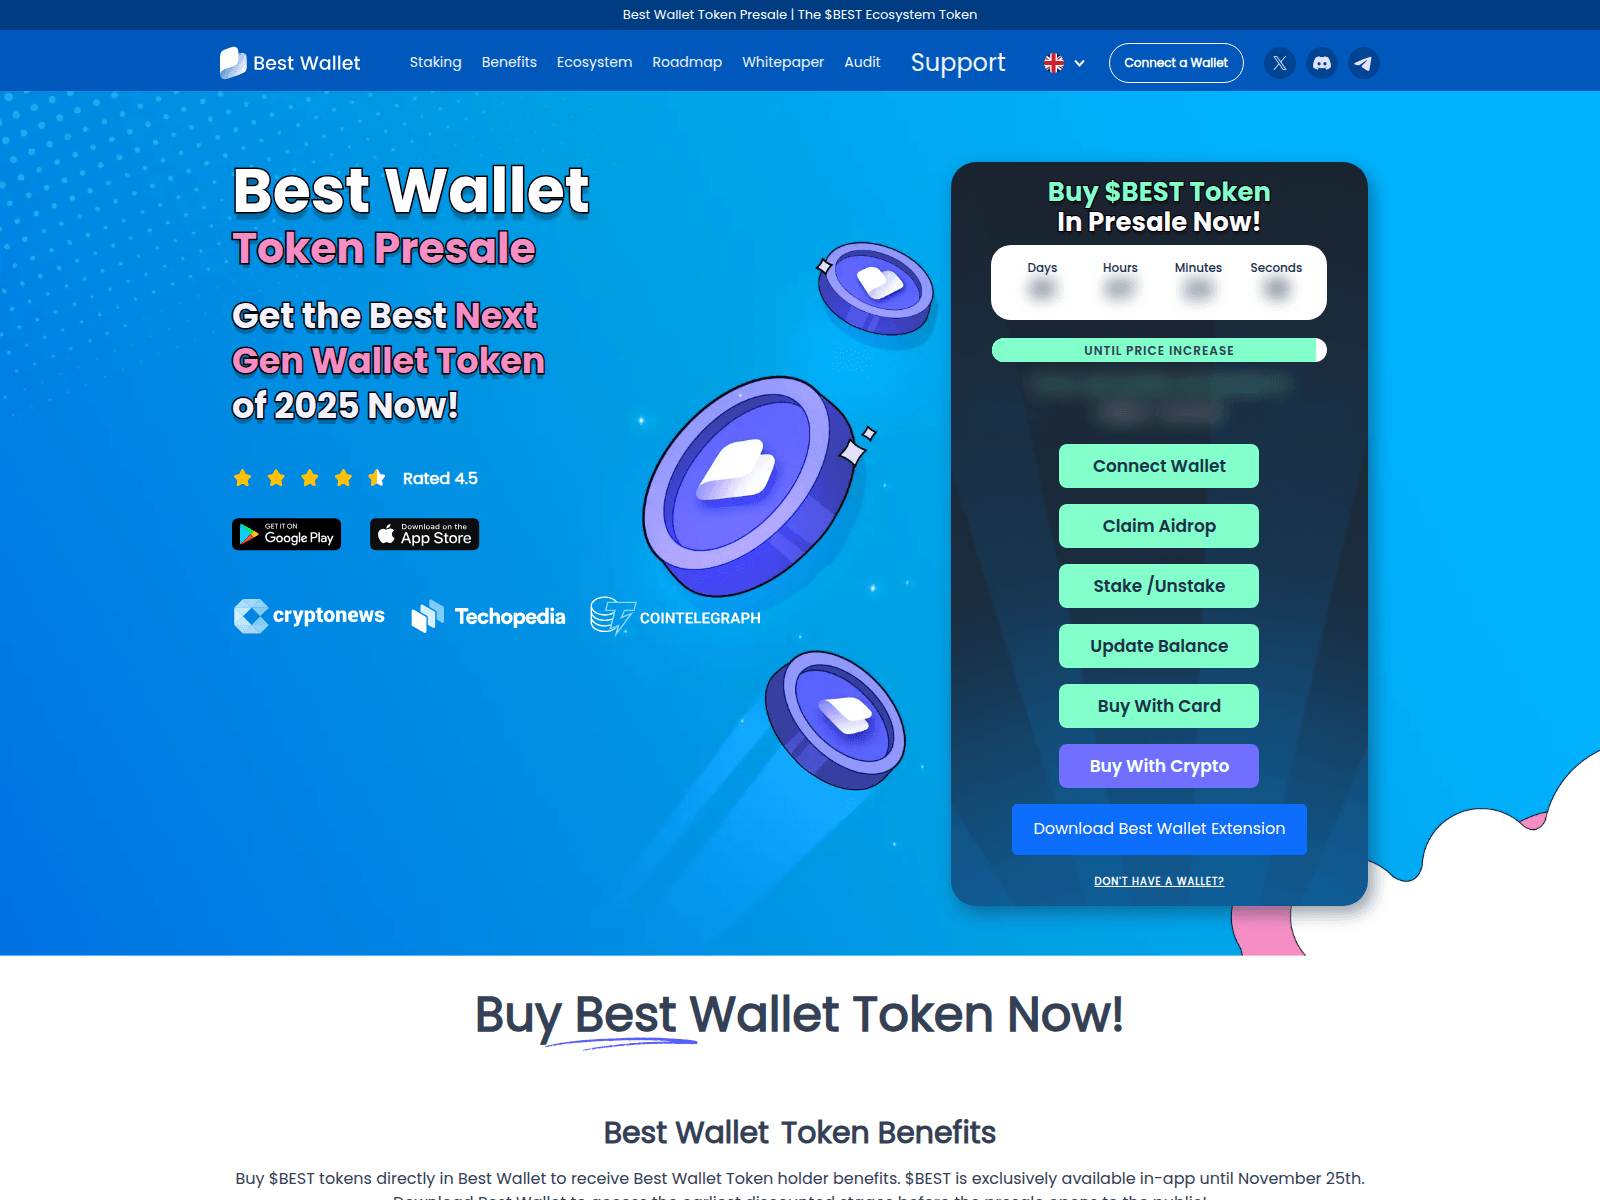
bestwalletsclaim.live
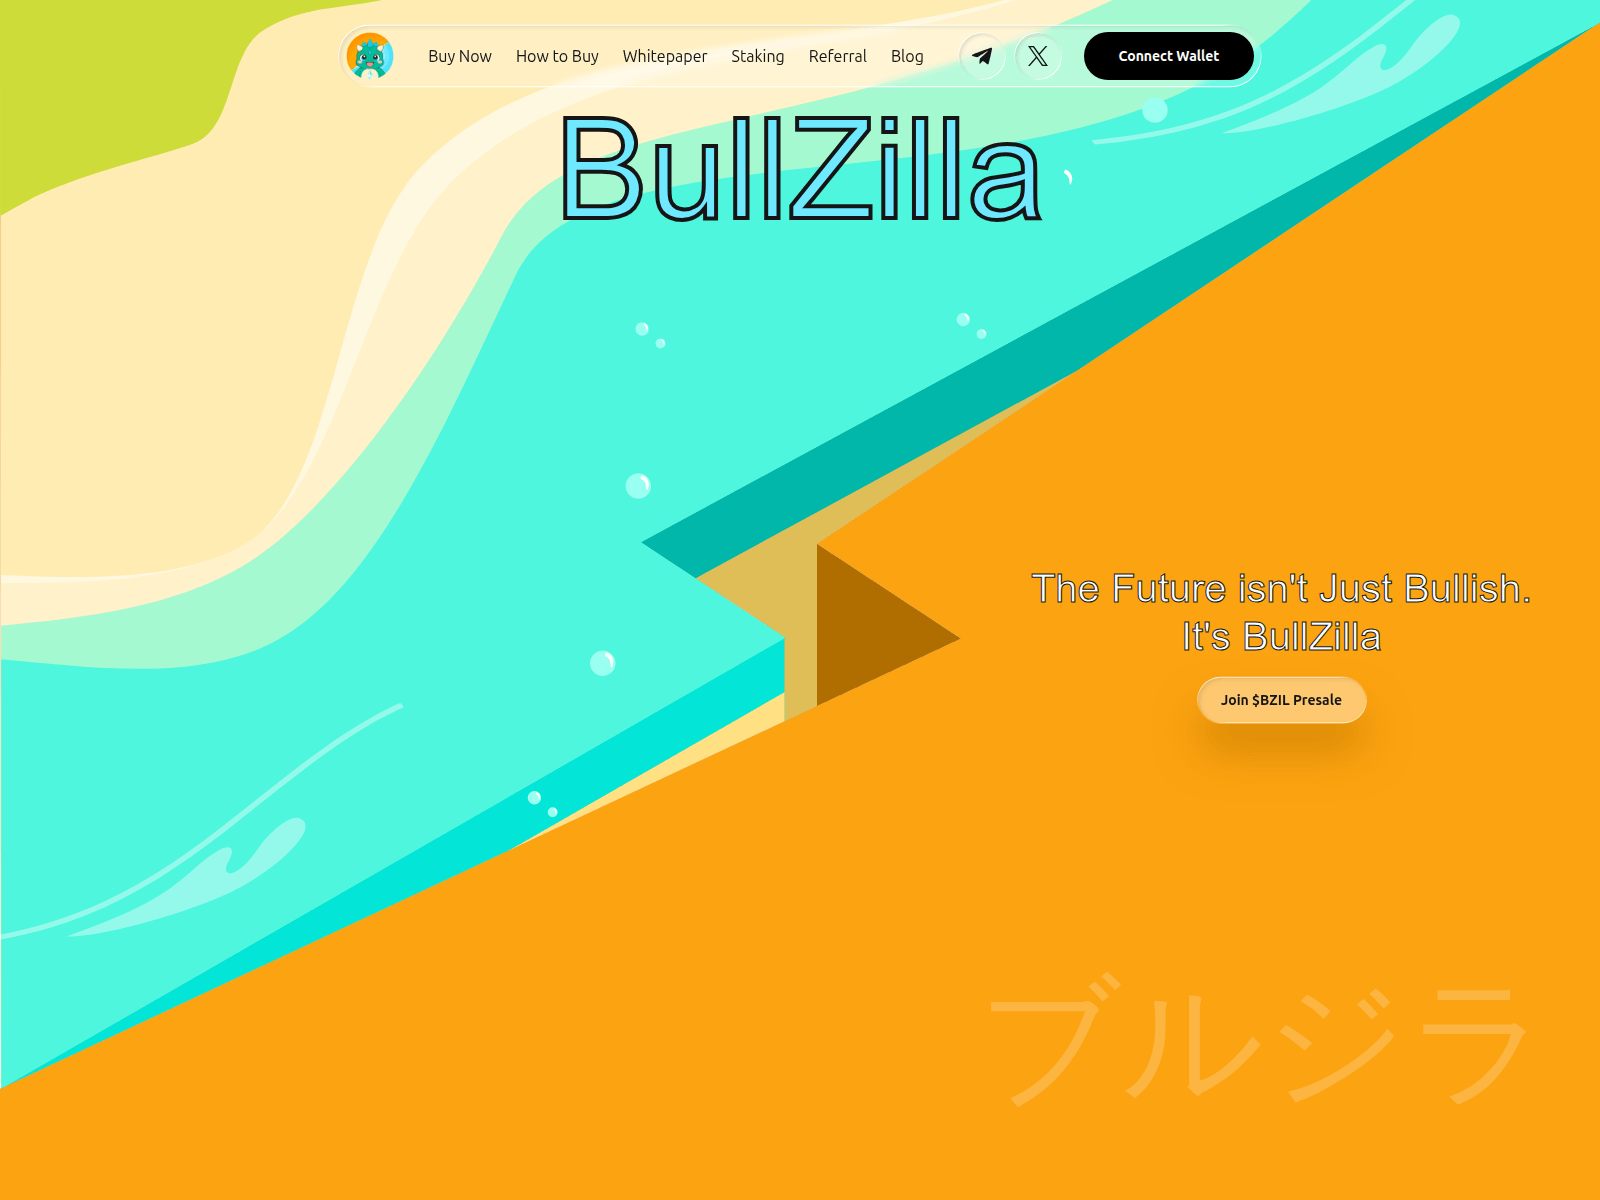
bullzilila.com
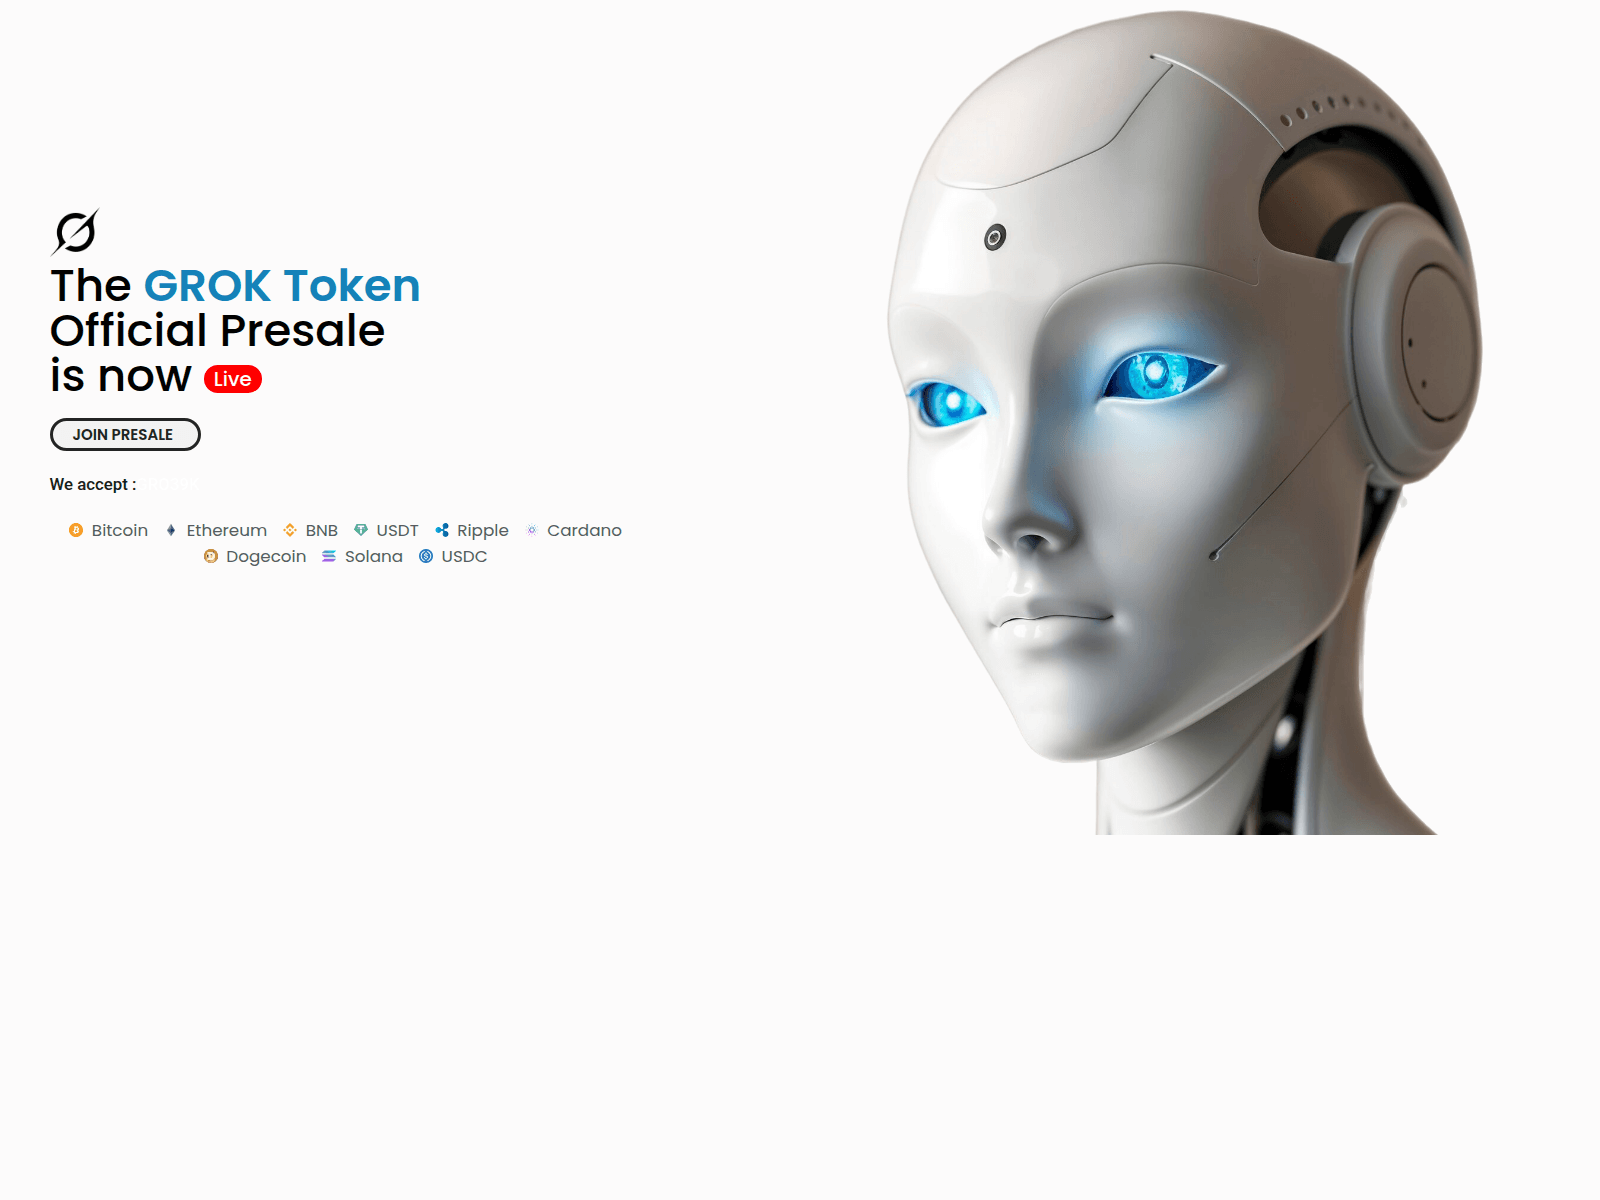
gro39k.org
limitlesslmts.app
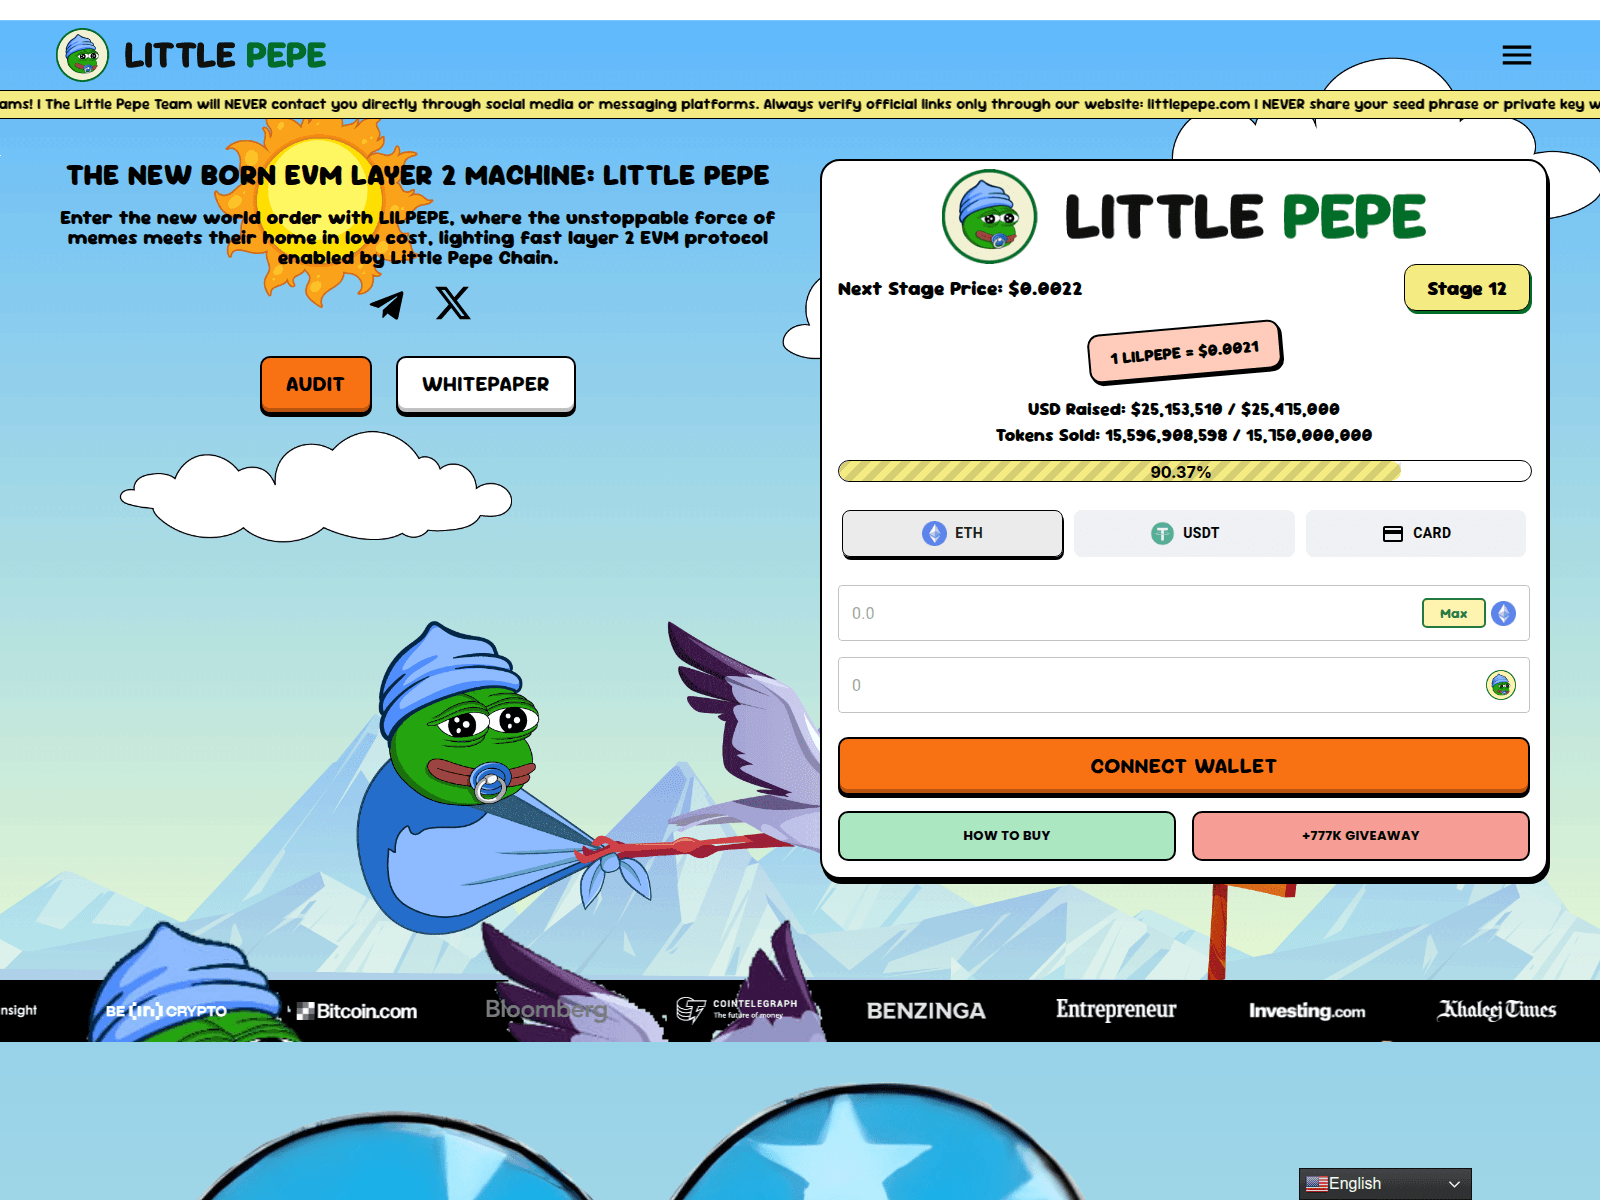
litlelpepe.com
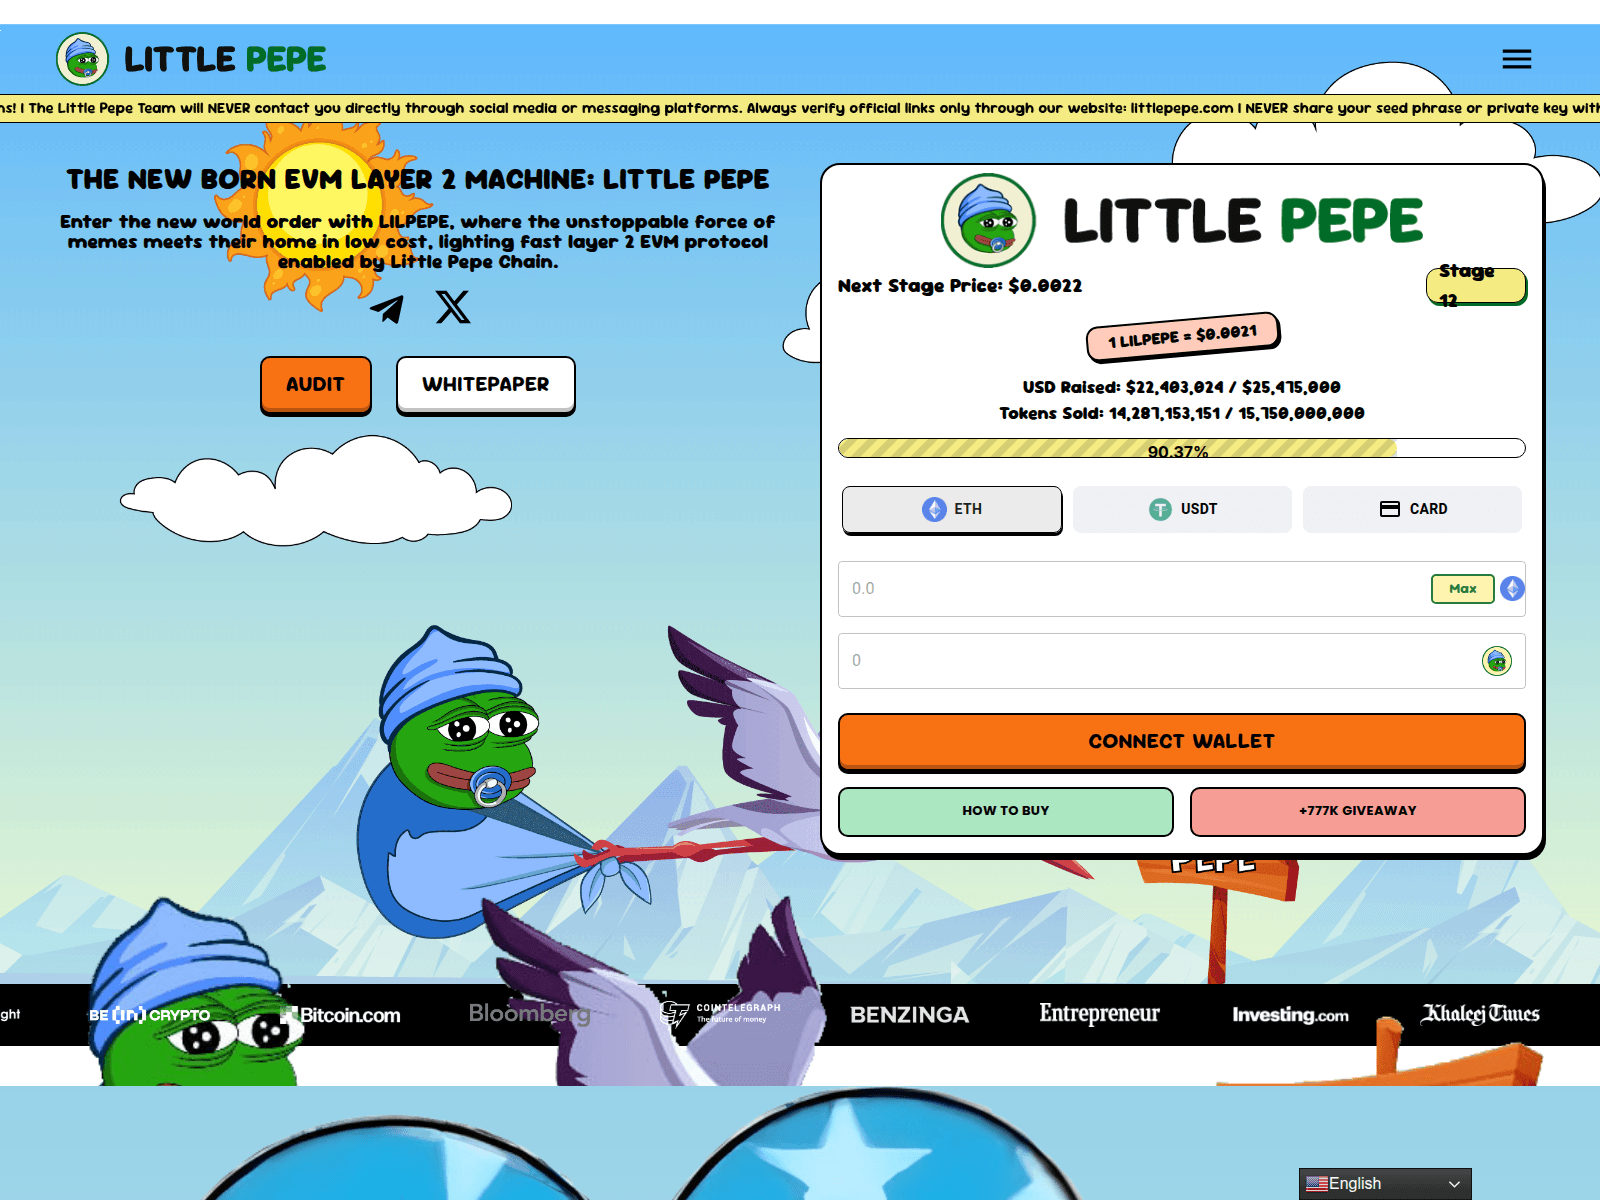
littepepe.com
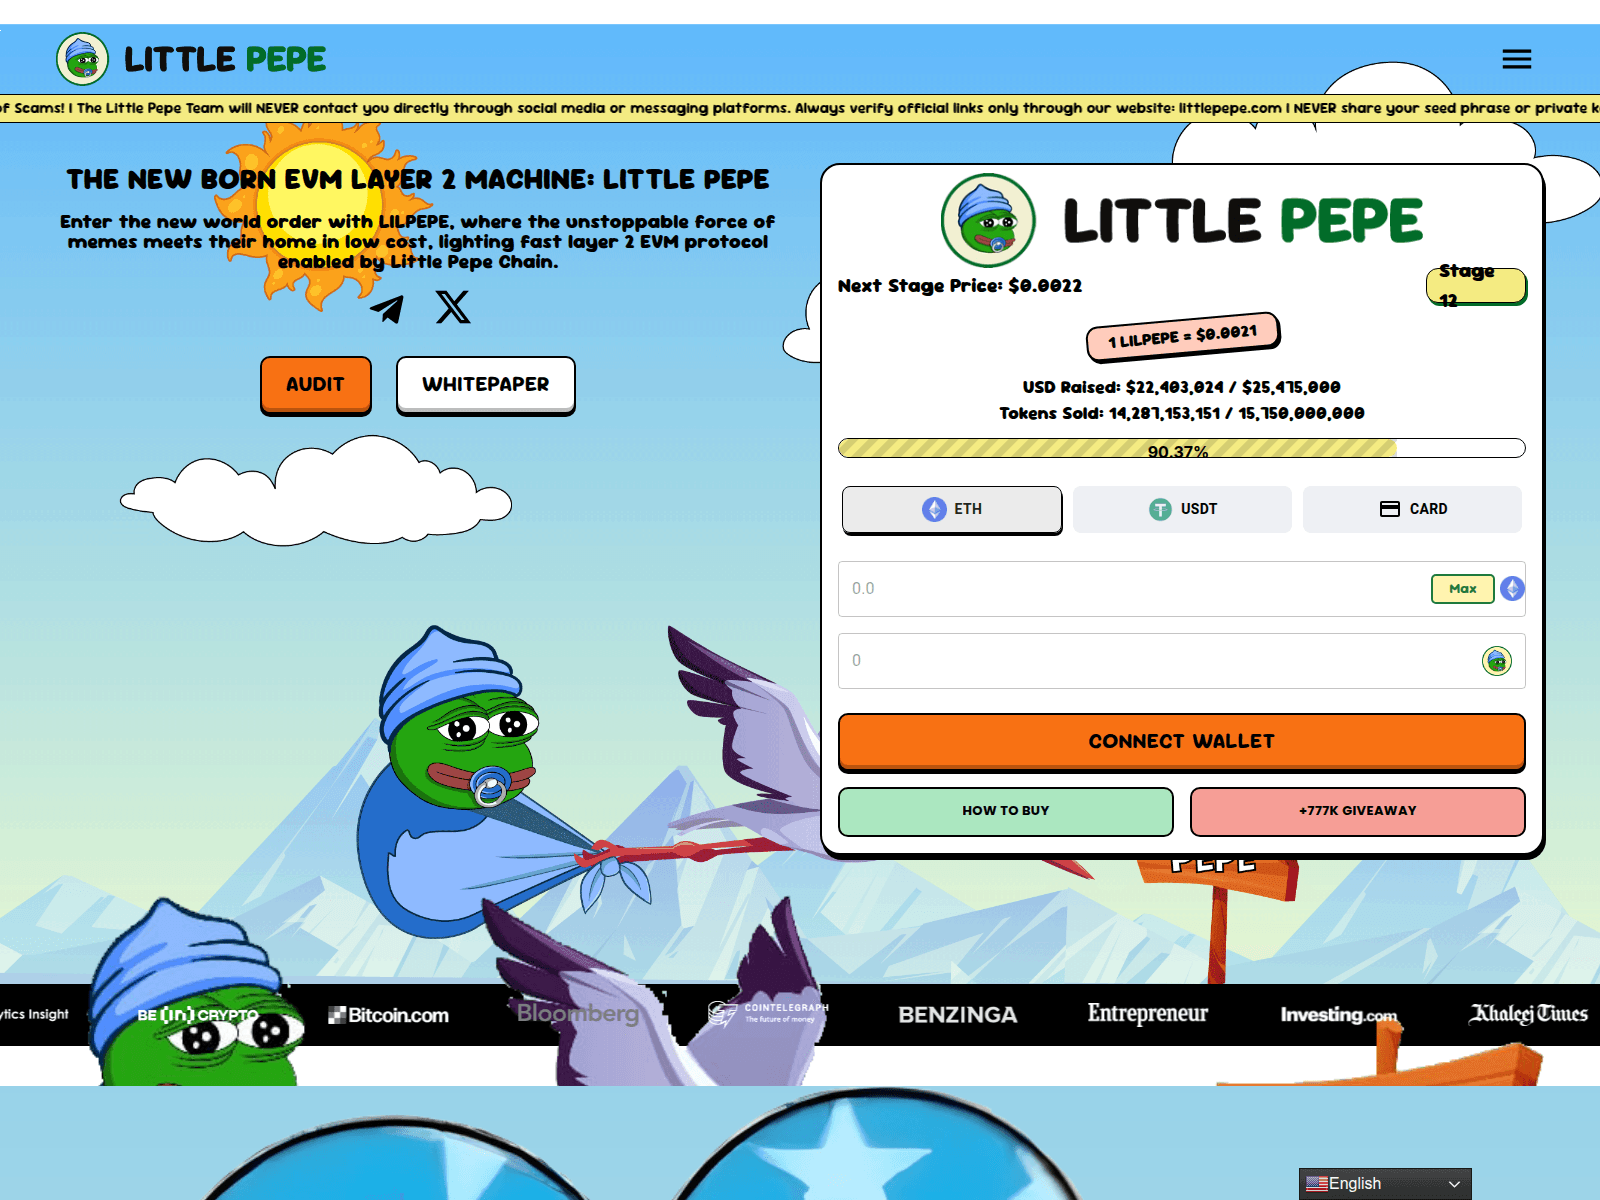
lttlepepe.com
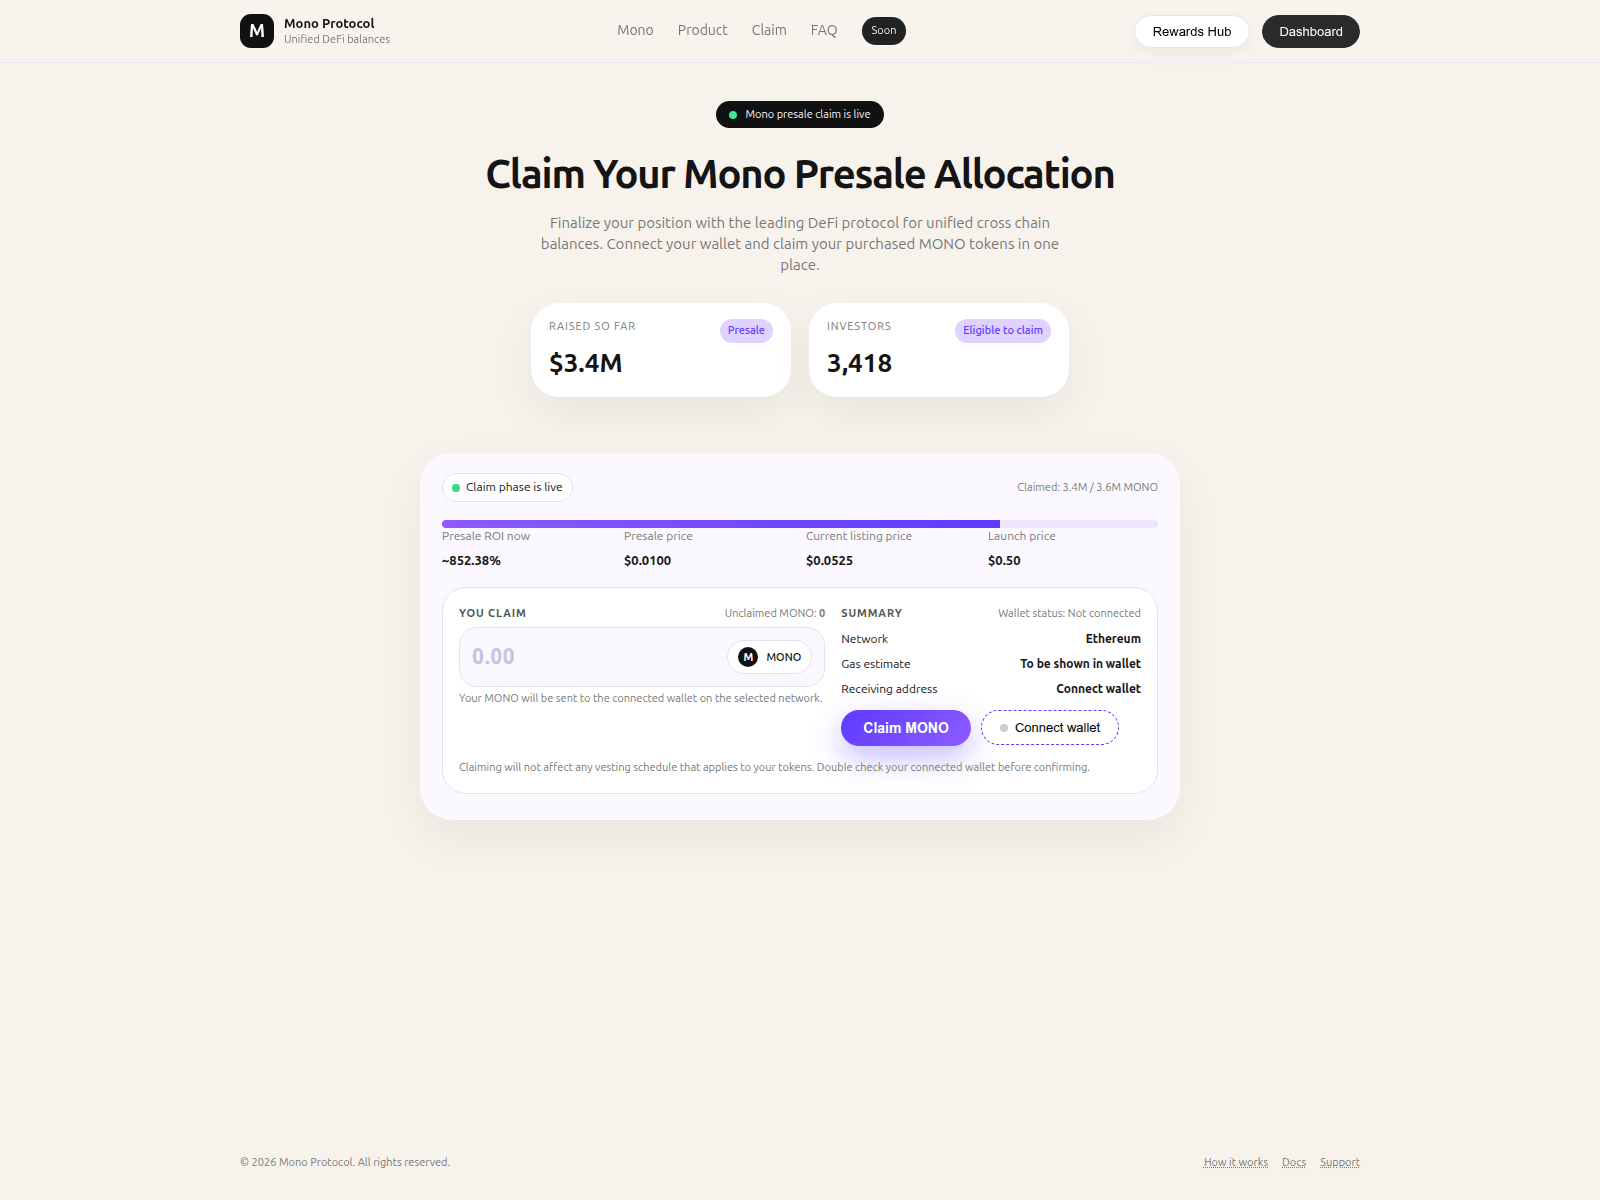
monoprotocol.online
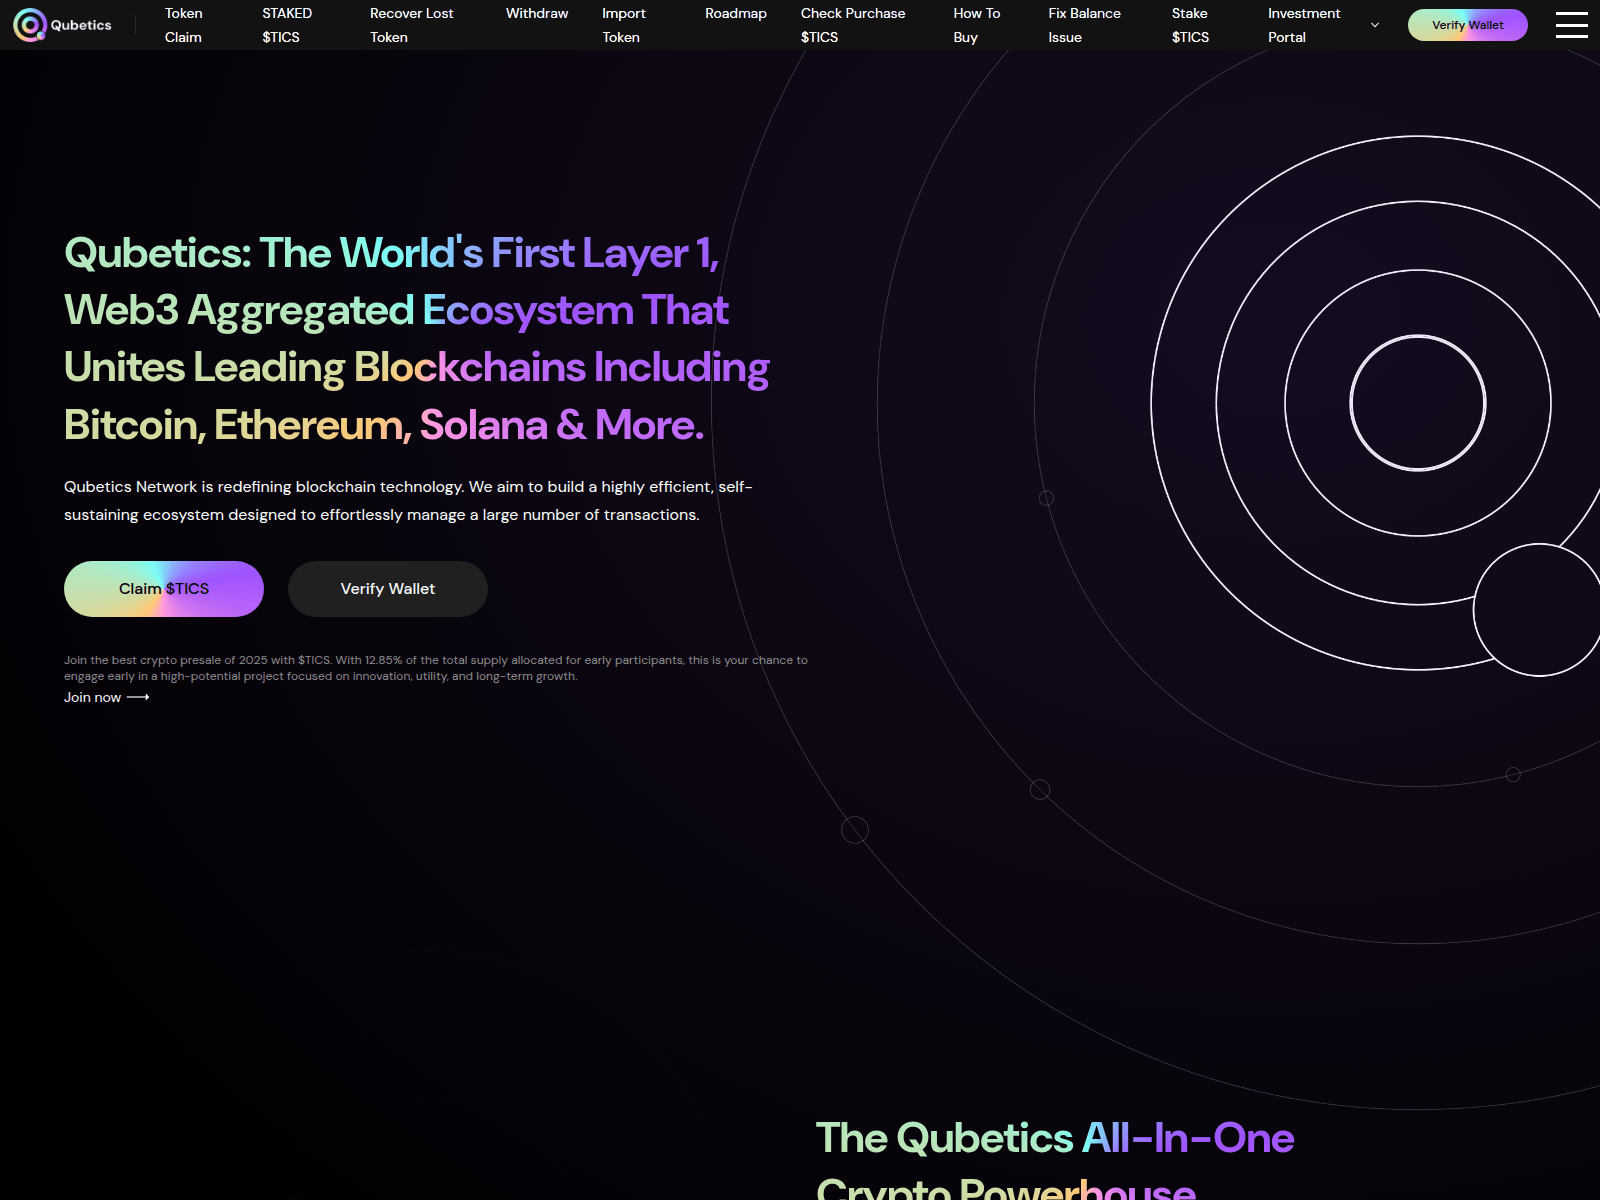
qubeticsverification.web.app
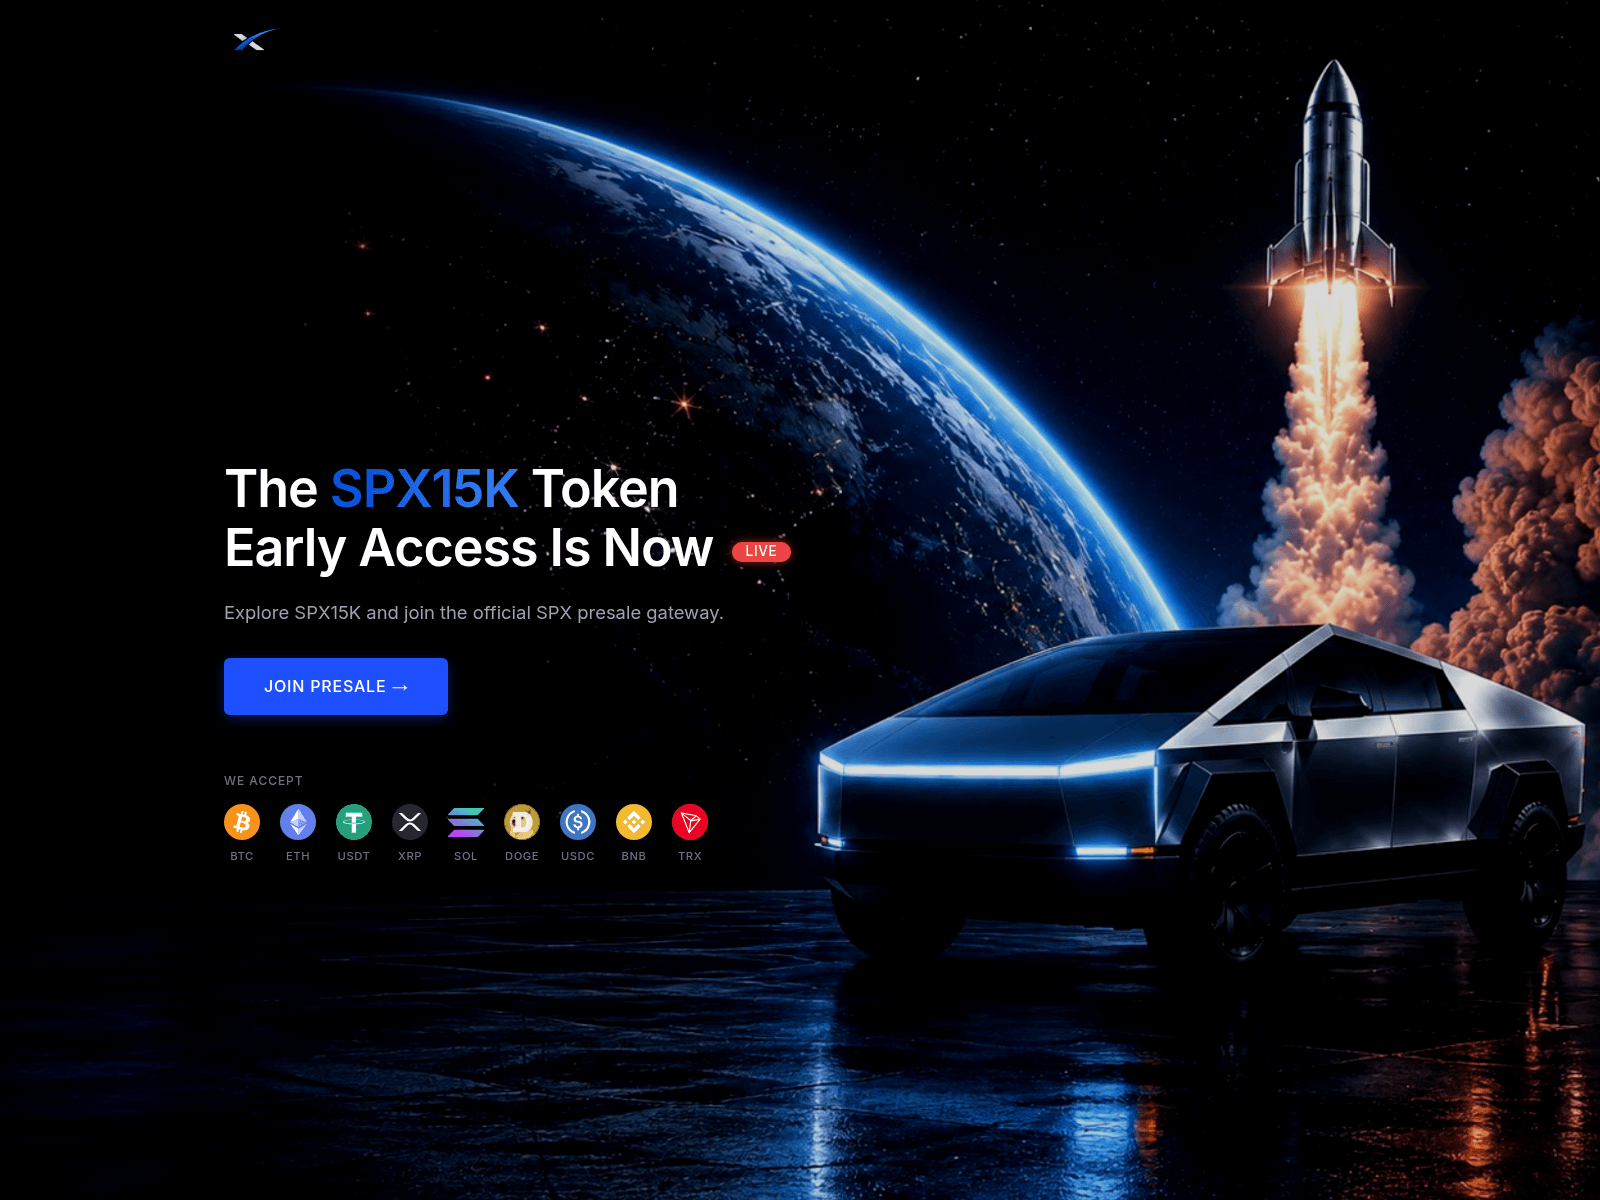
spx15k.com
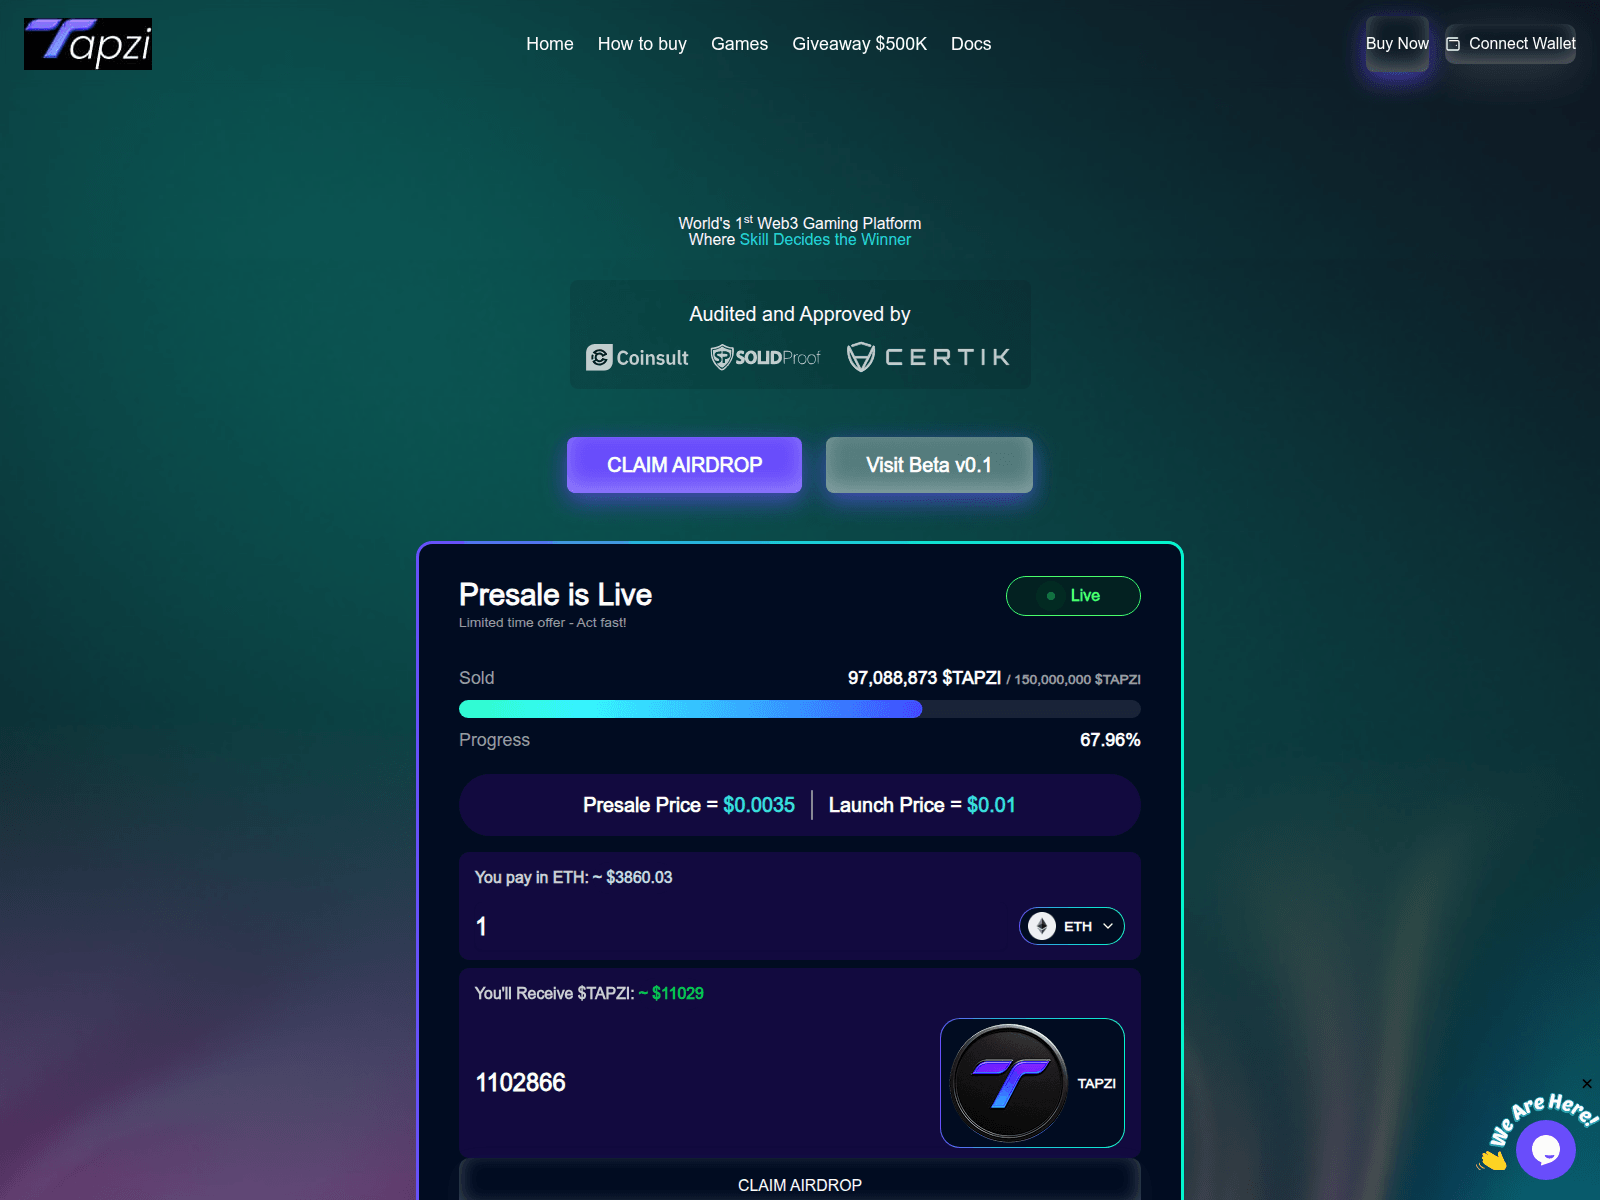
tapzi-io.xyz
theflockerz.pages.dev
vforcecoin.com
www-grok-allocation.xyz
xdna-dnaprotocol.com
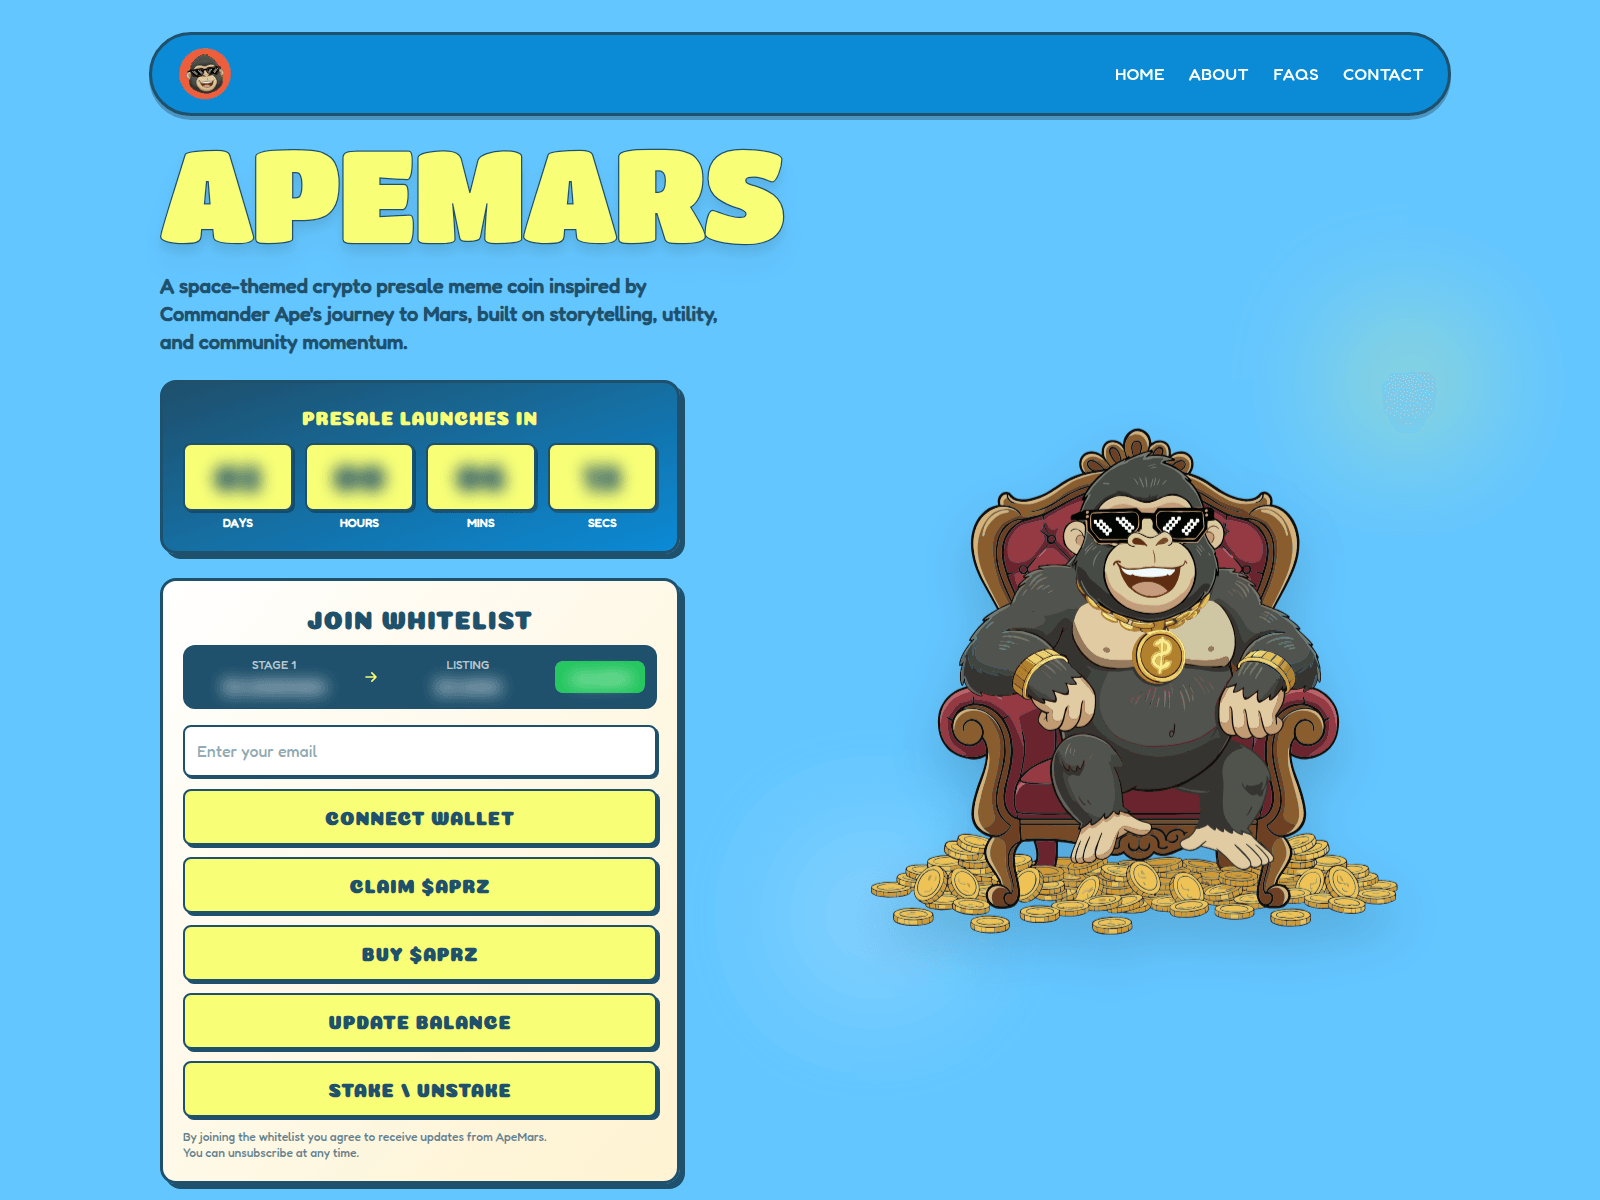
apemars-in.web.app
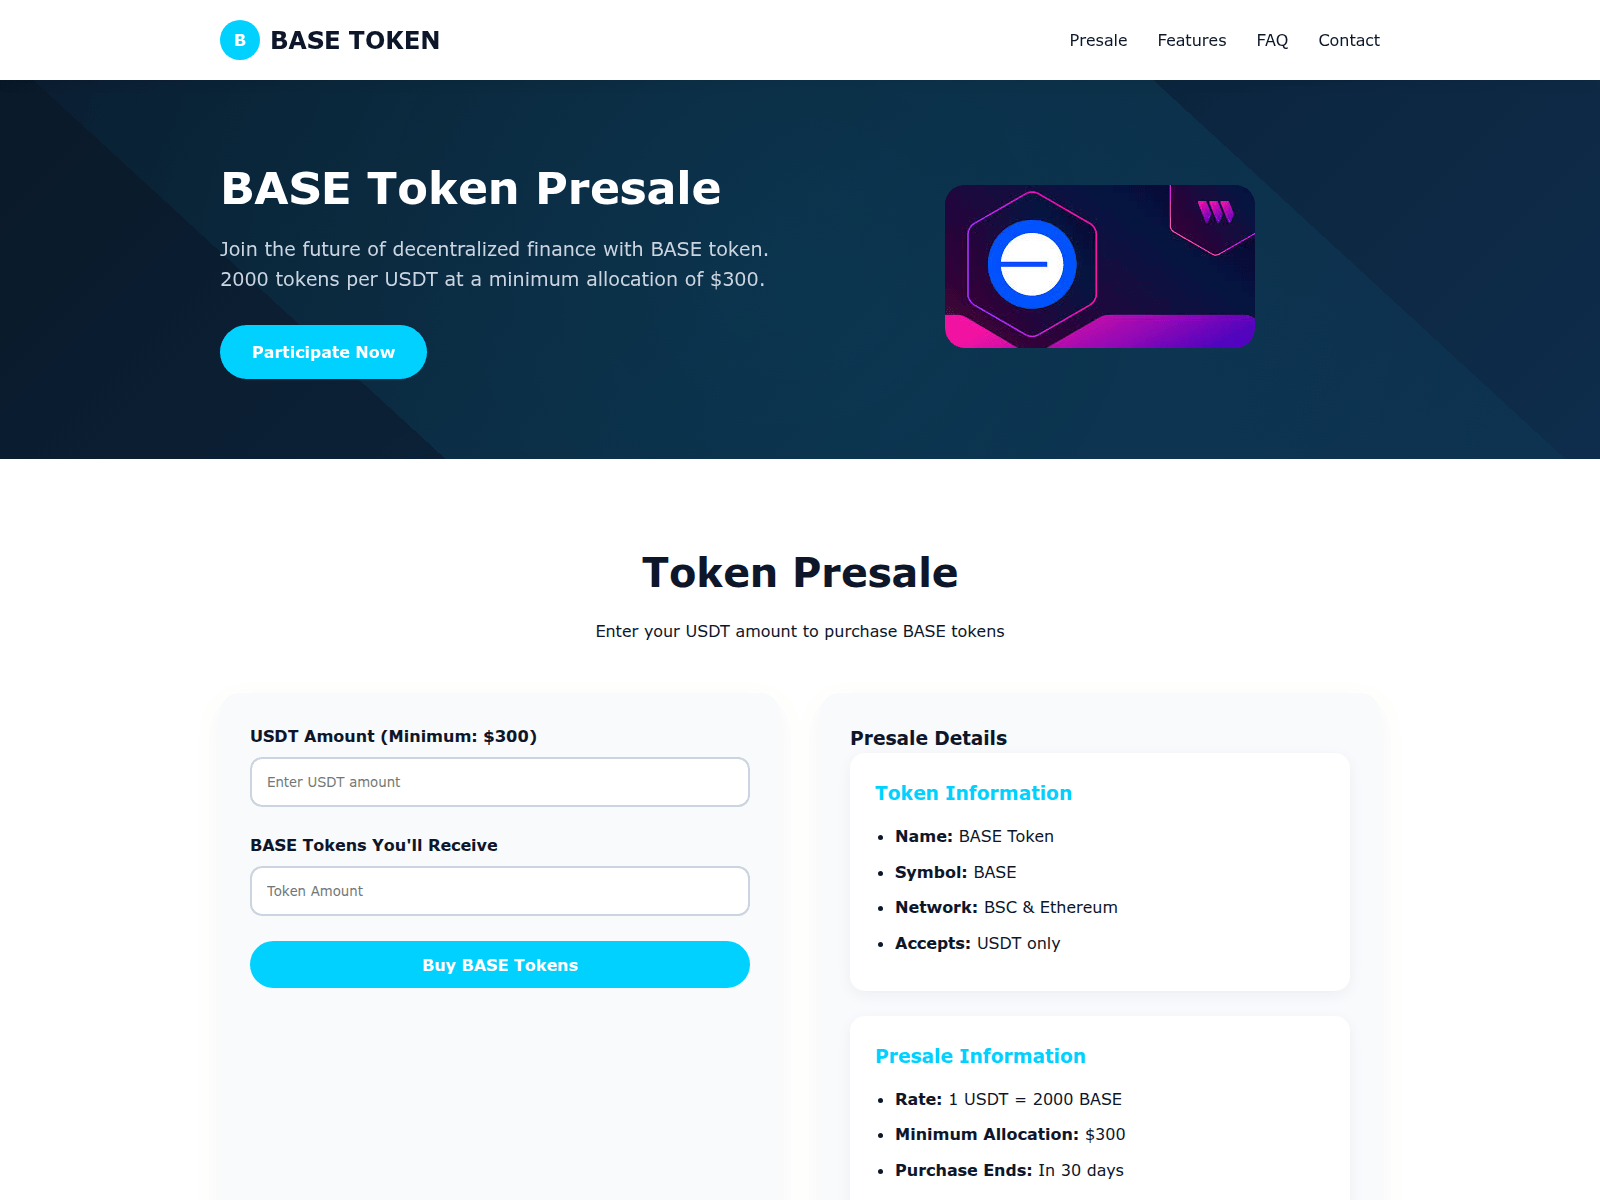
basetoken.sale
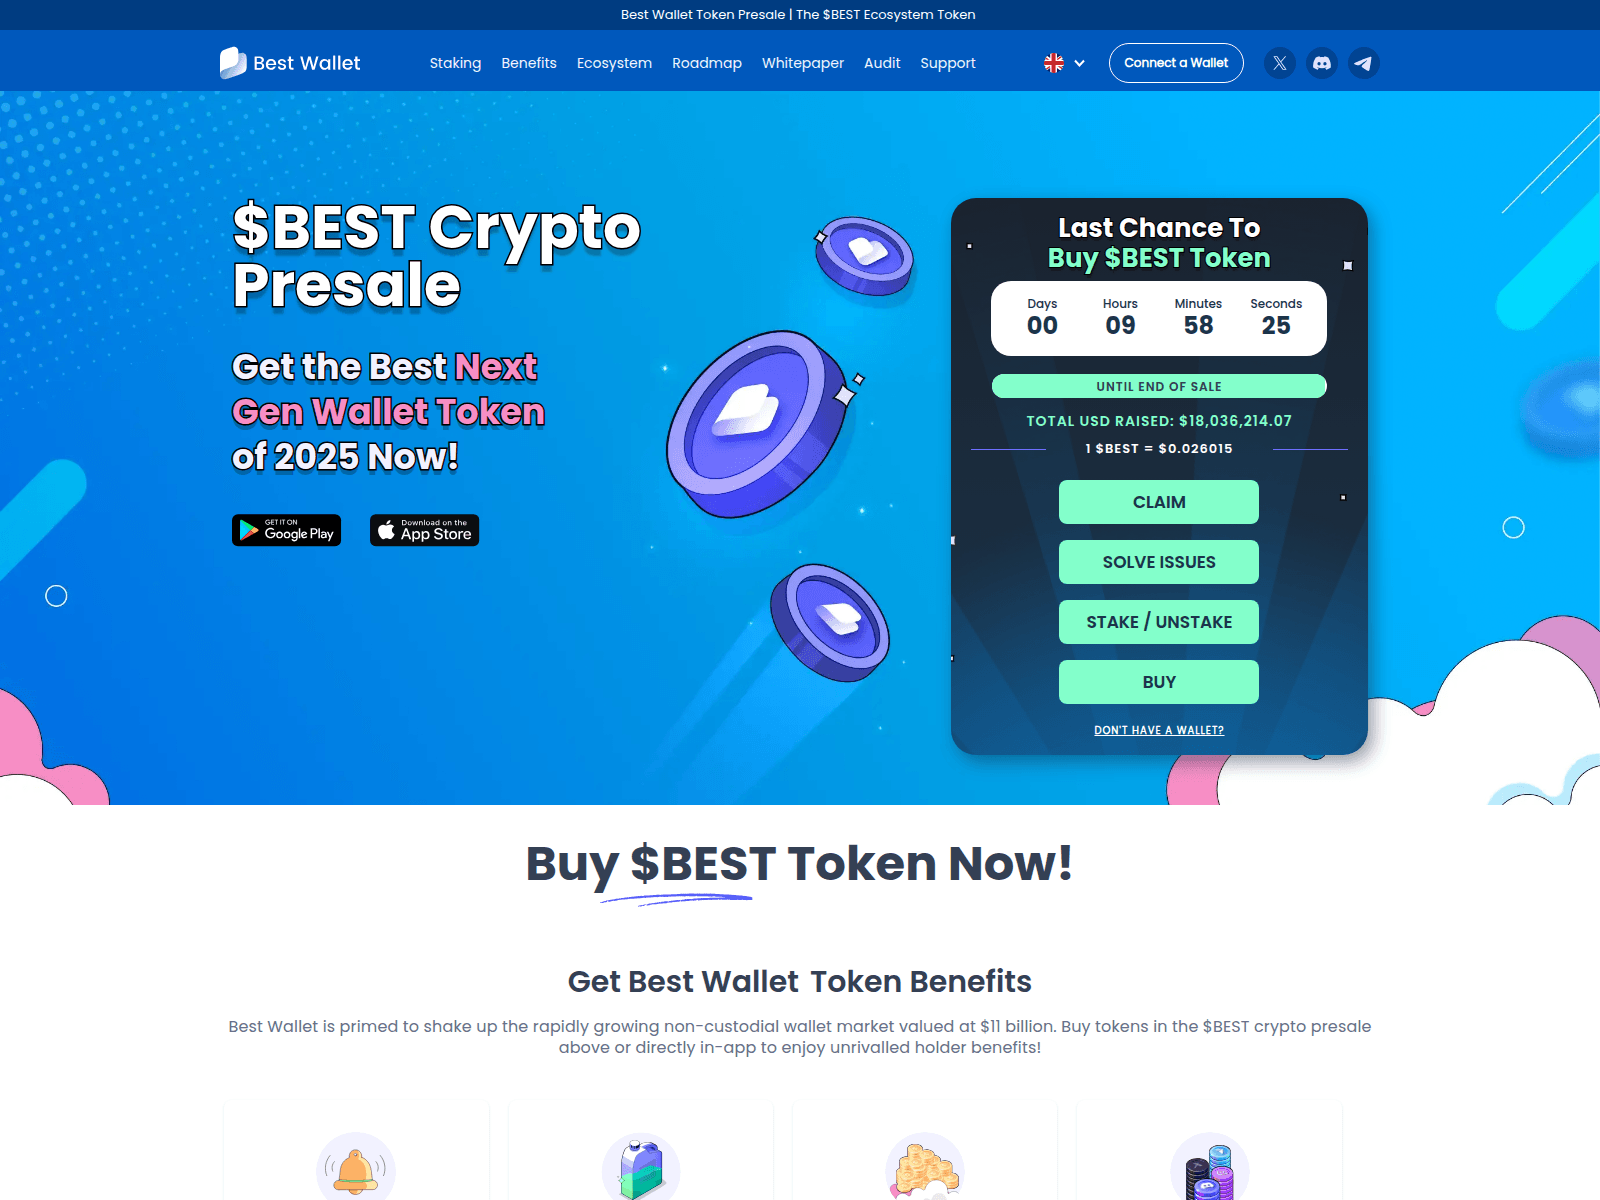
bestwallettoken-claim.info
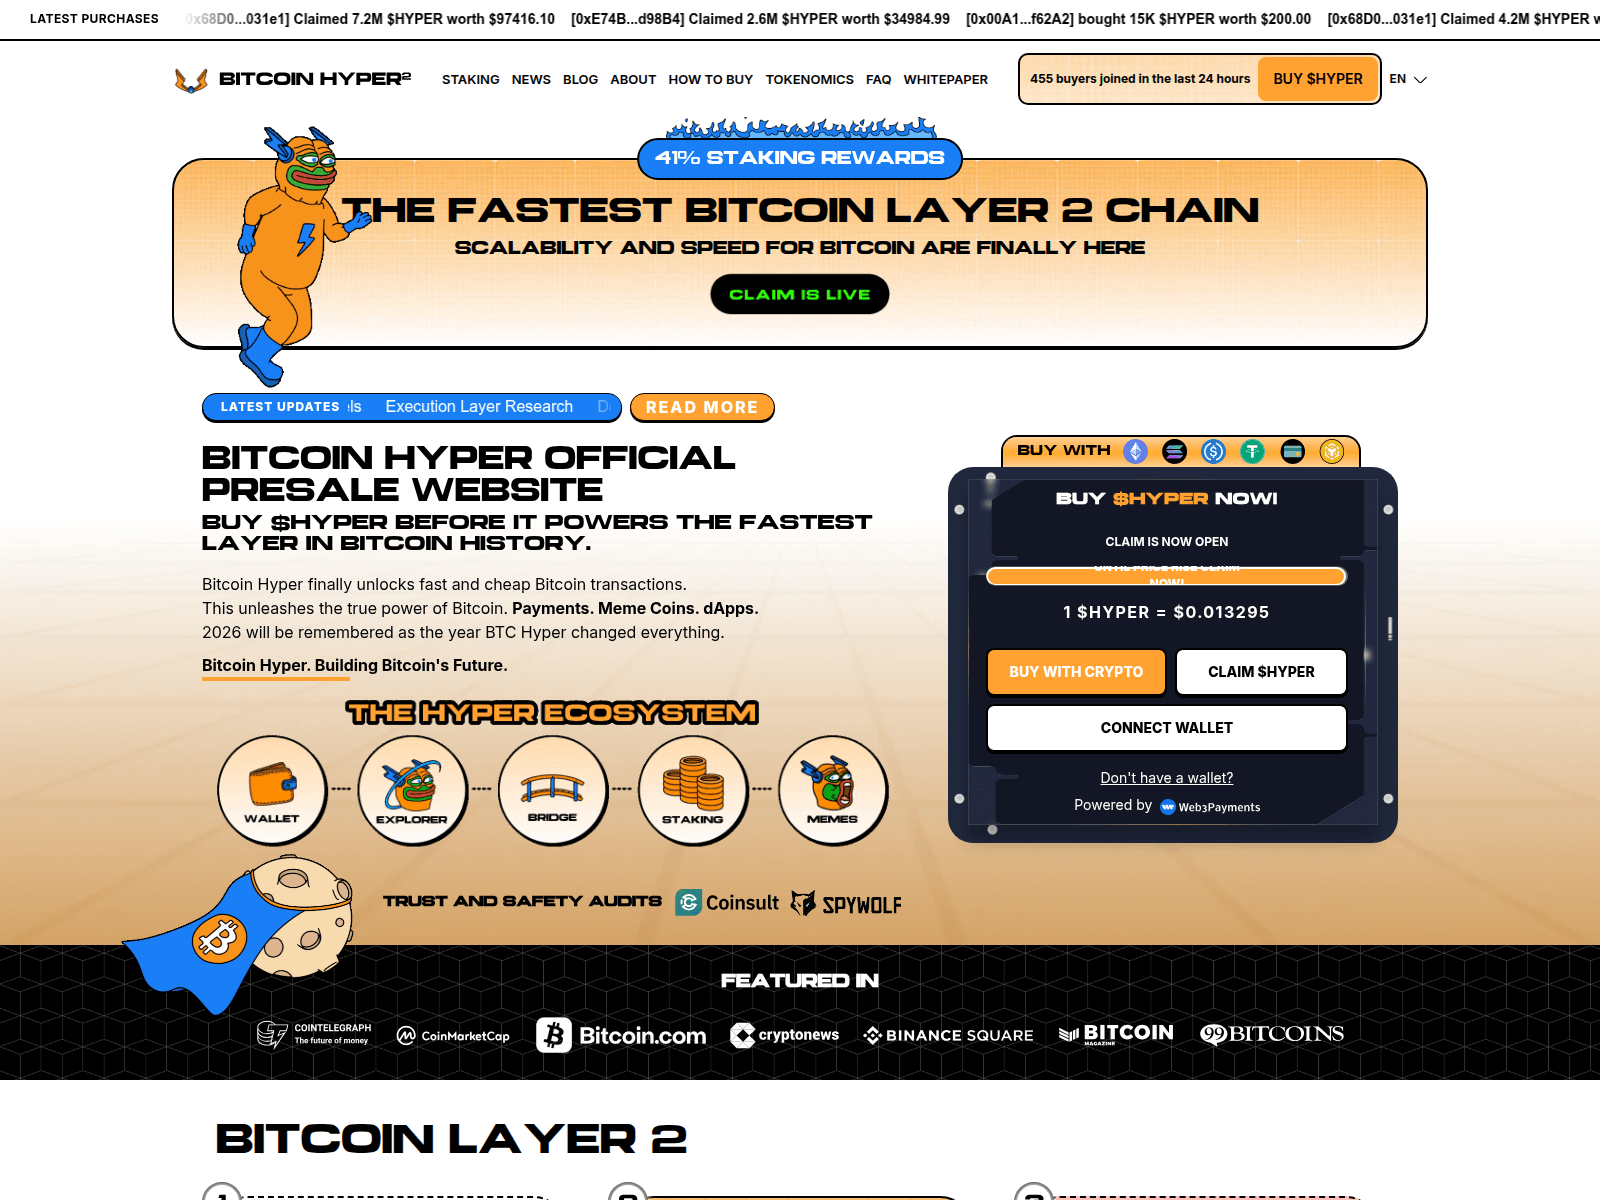
claims-bitcoinhyper-claim.pages.dev
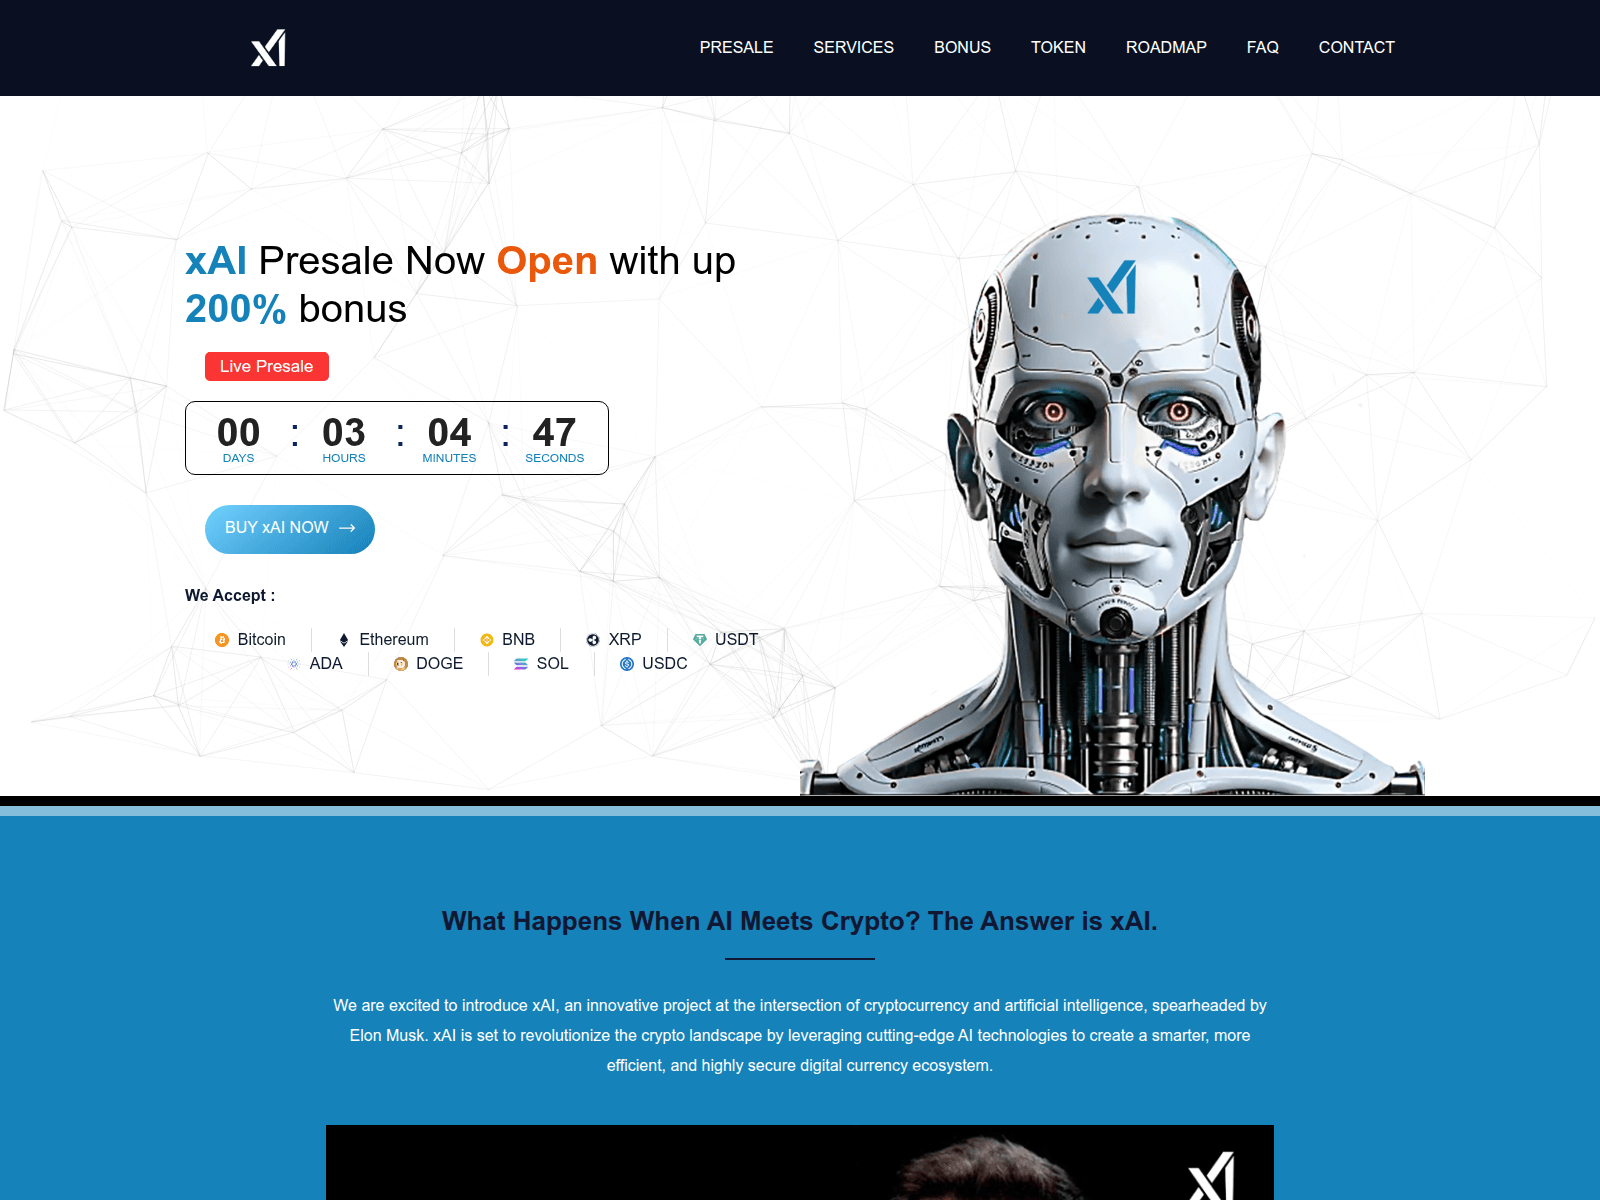
gr0k2025.com
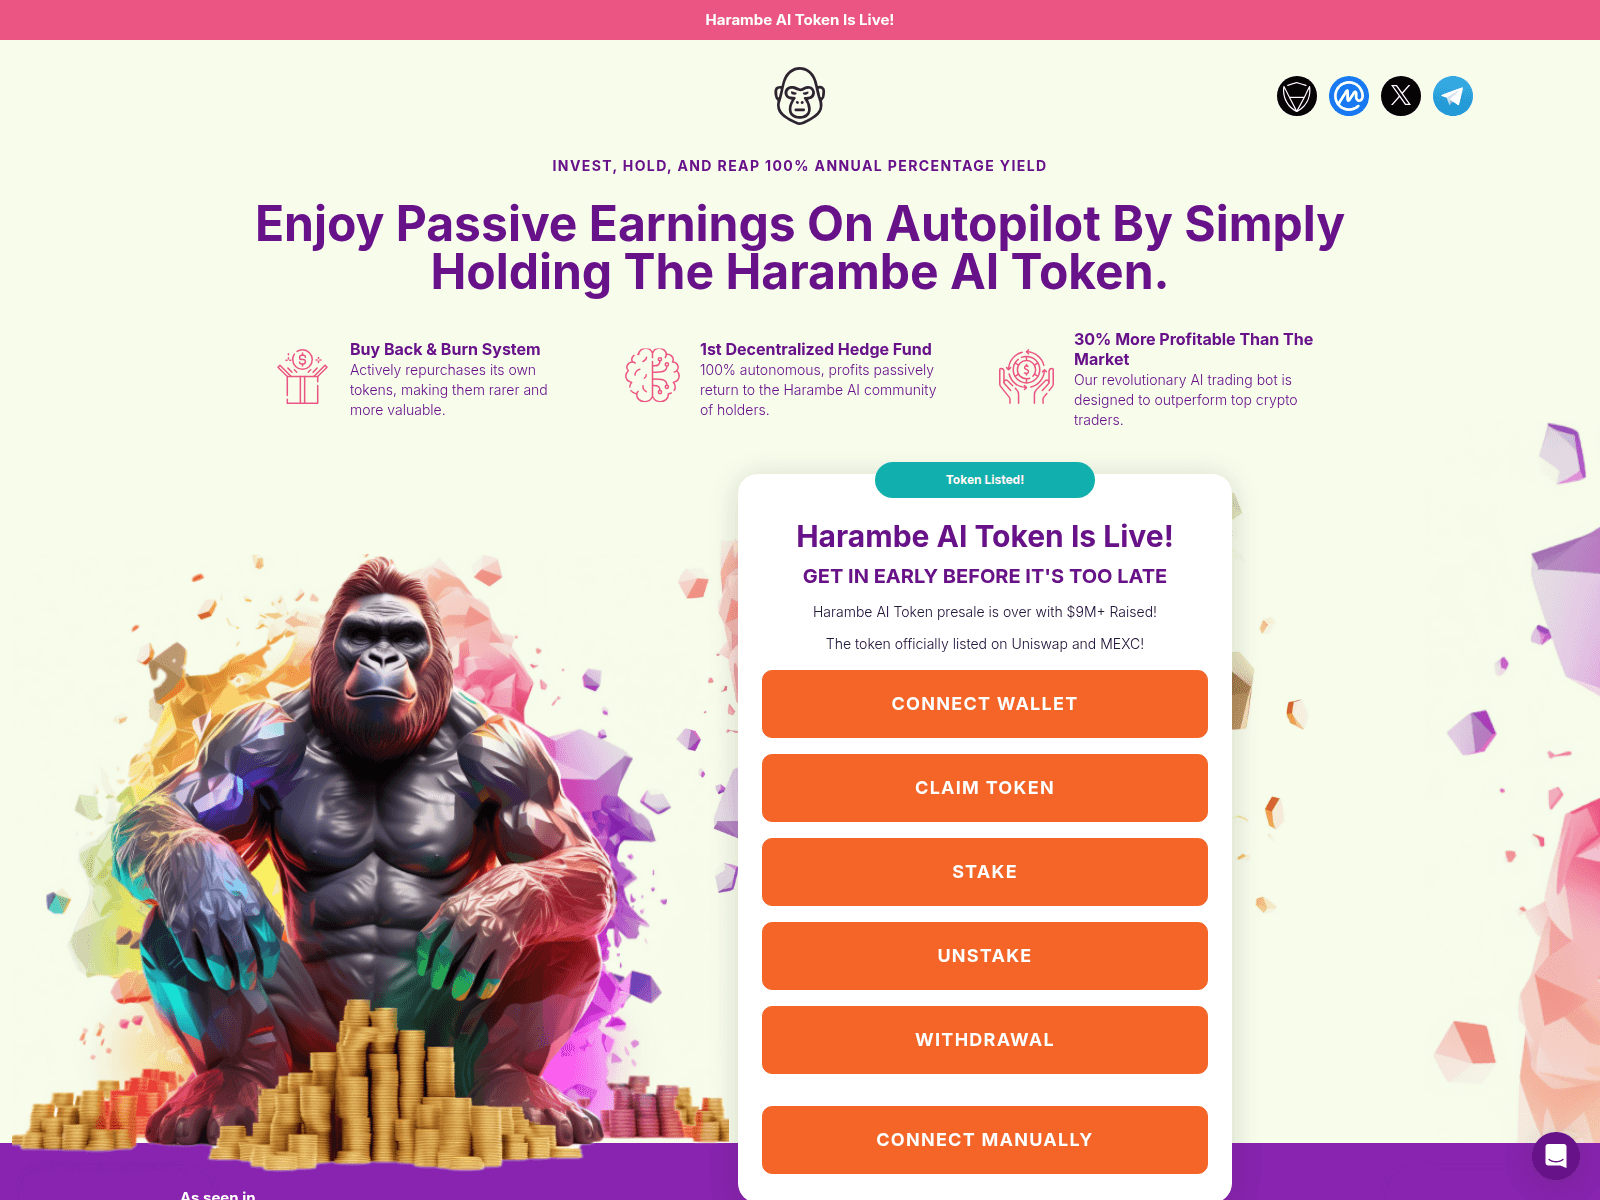
harambeaiclaim.web.app
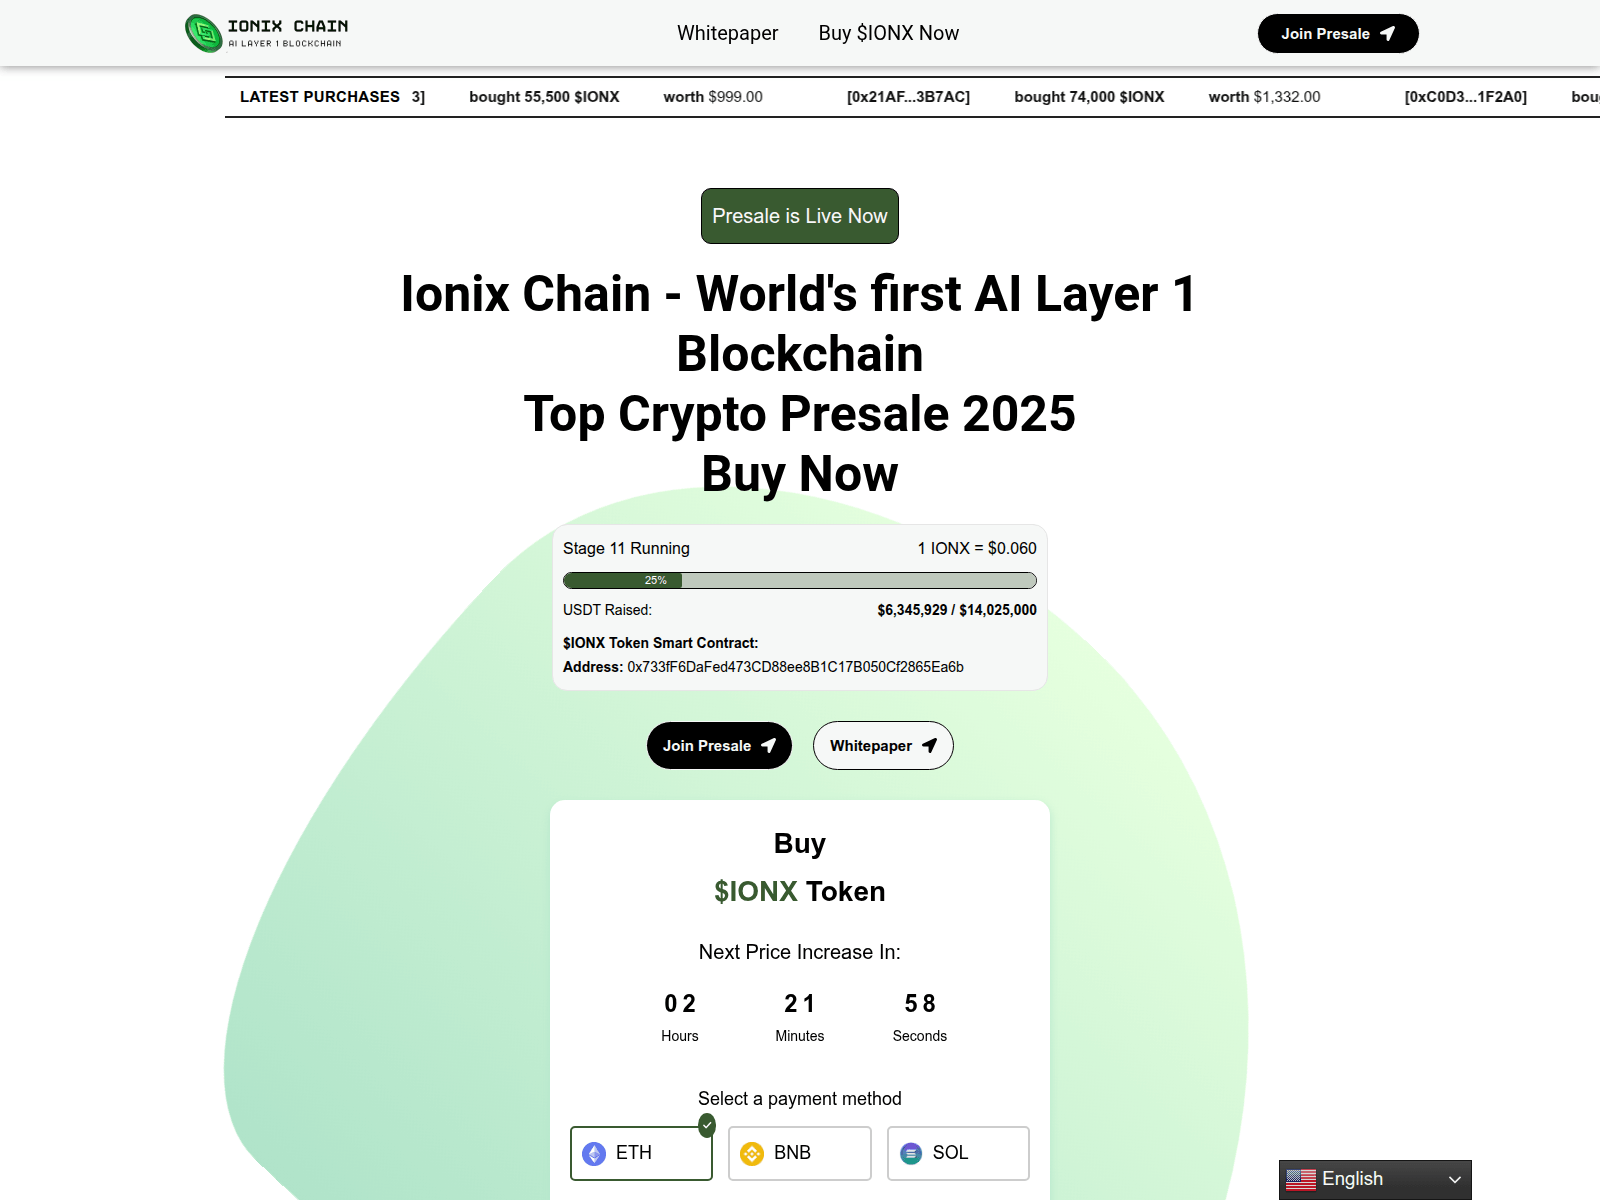
ionichain.com
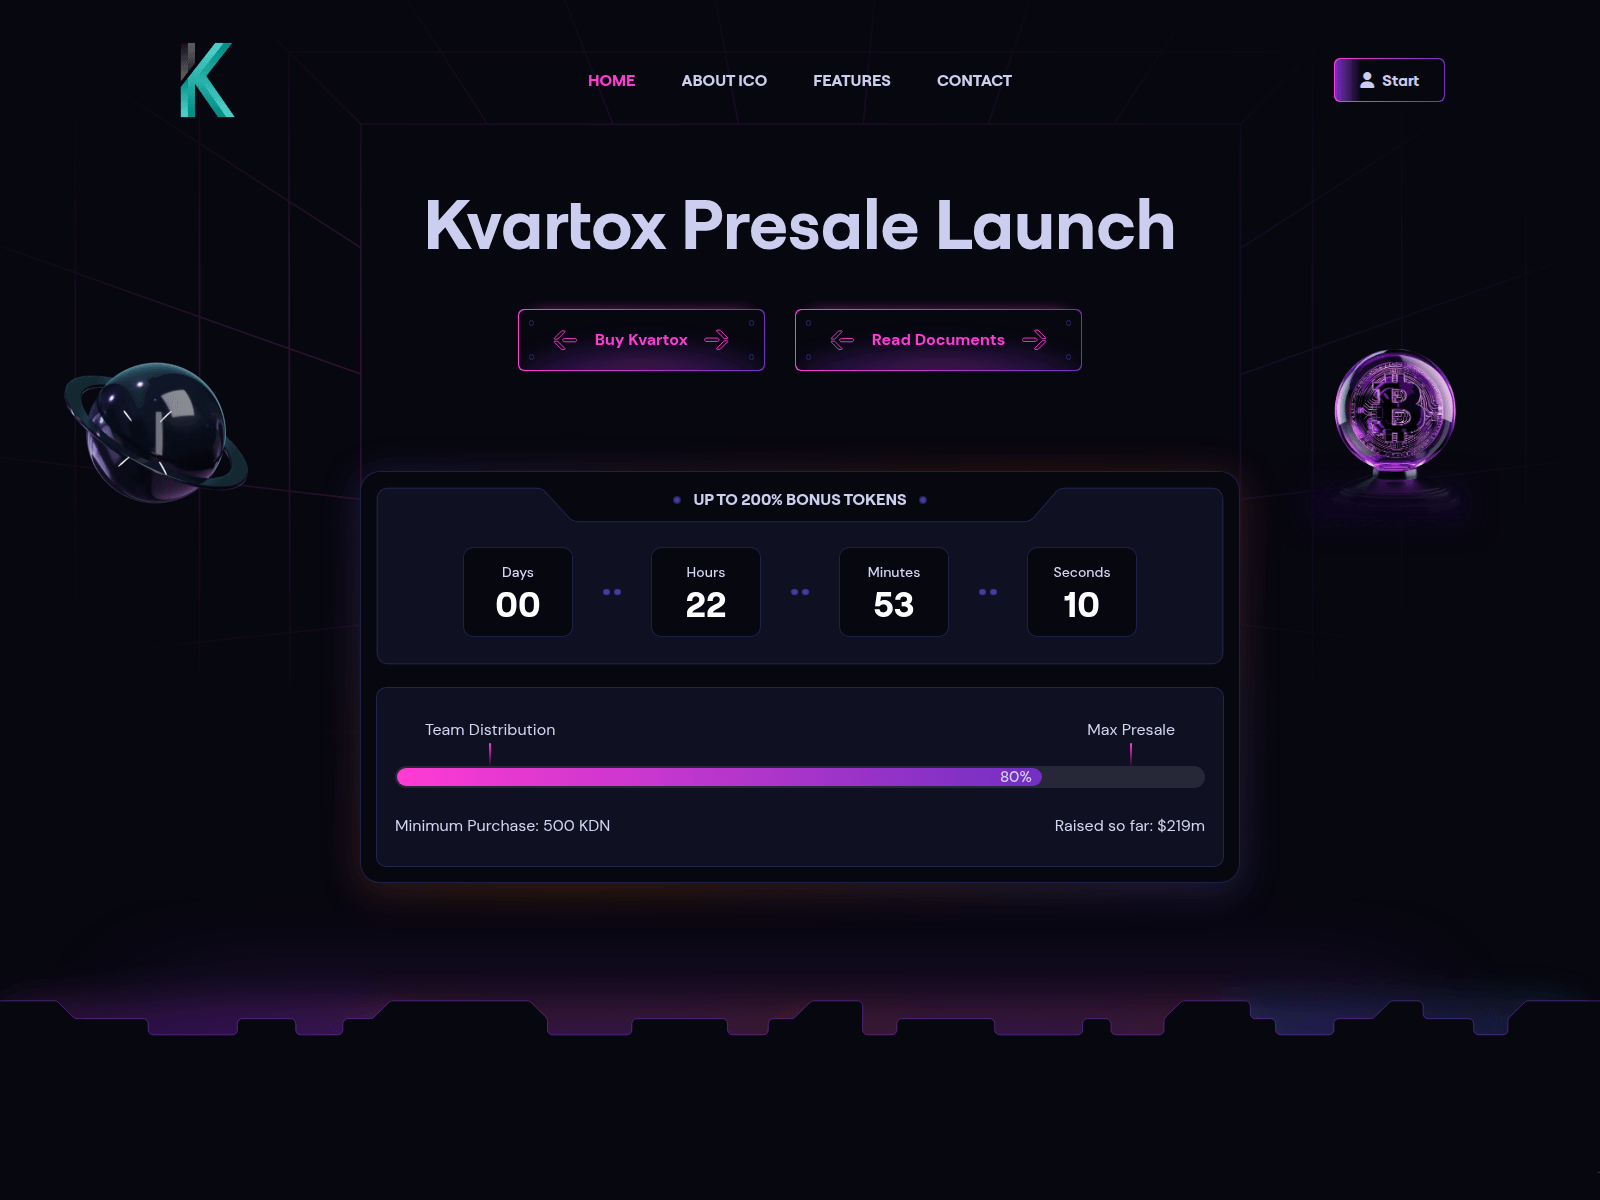
kvartox.com
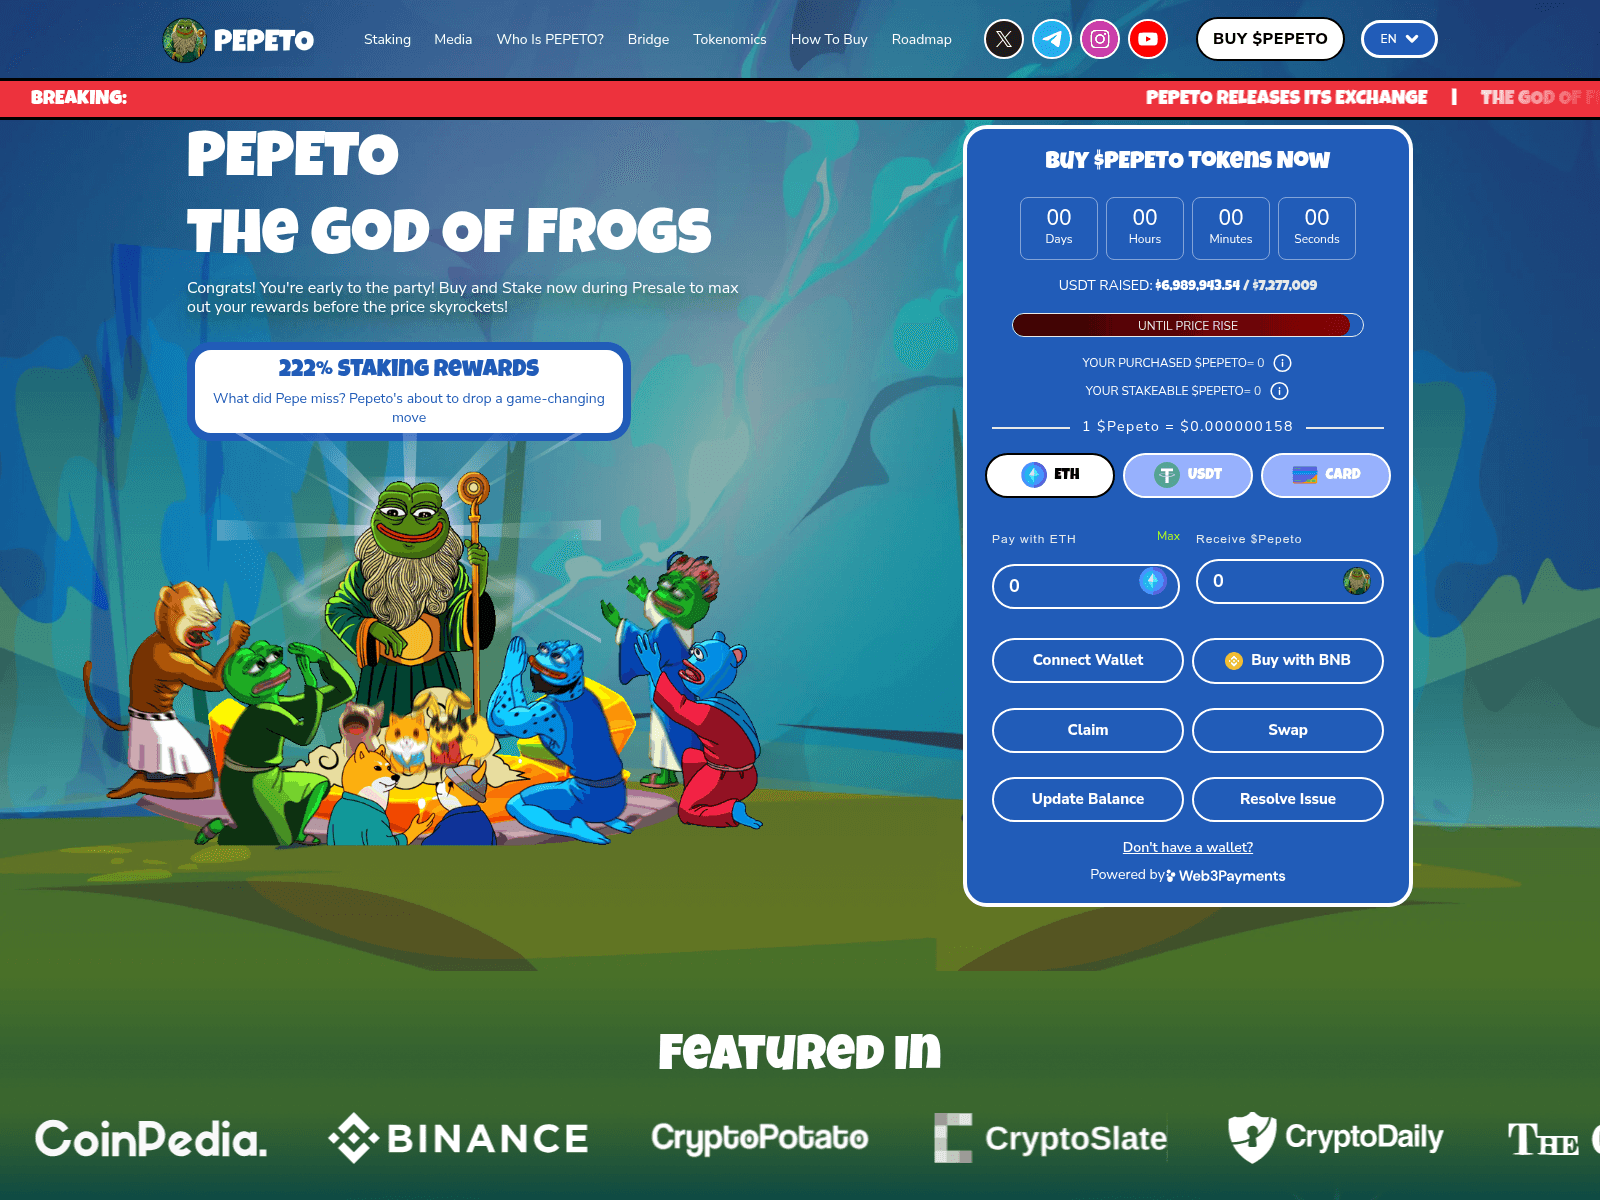
m-pepeto.pages.dev
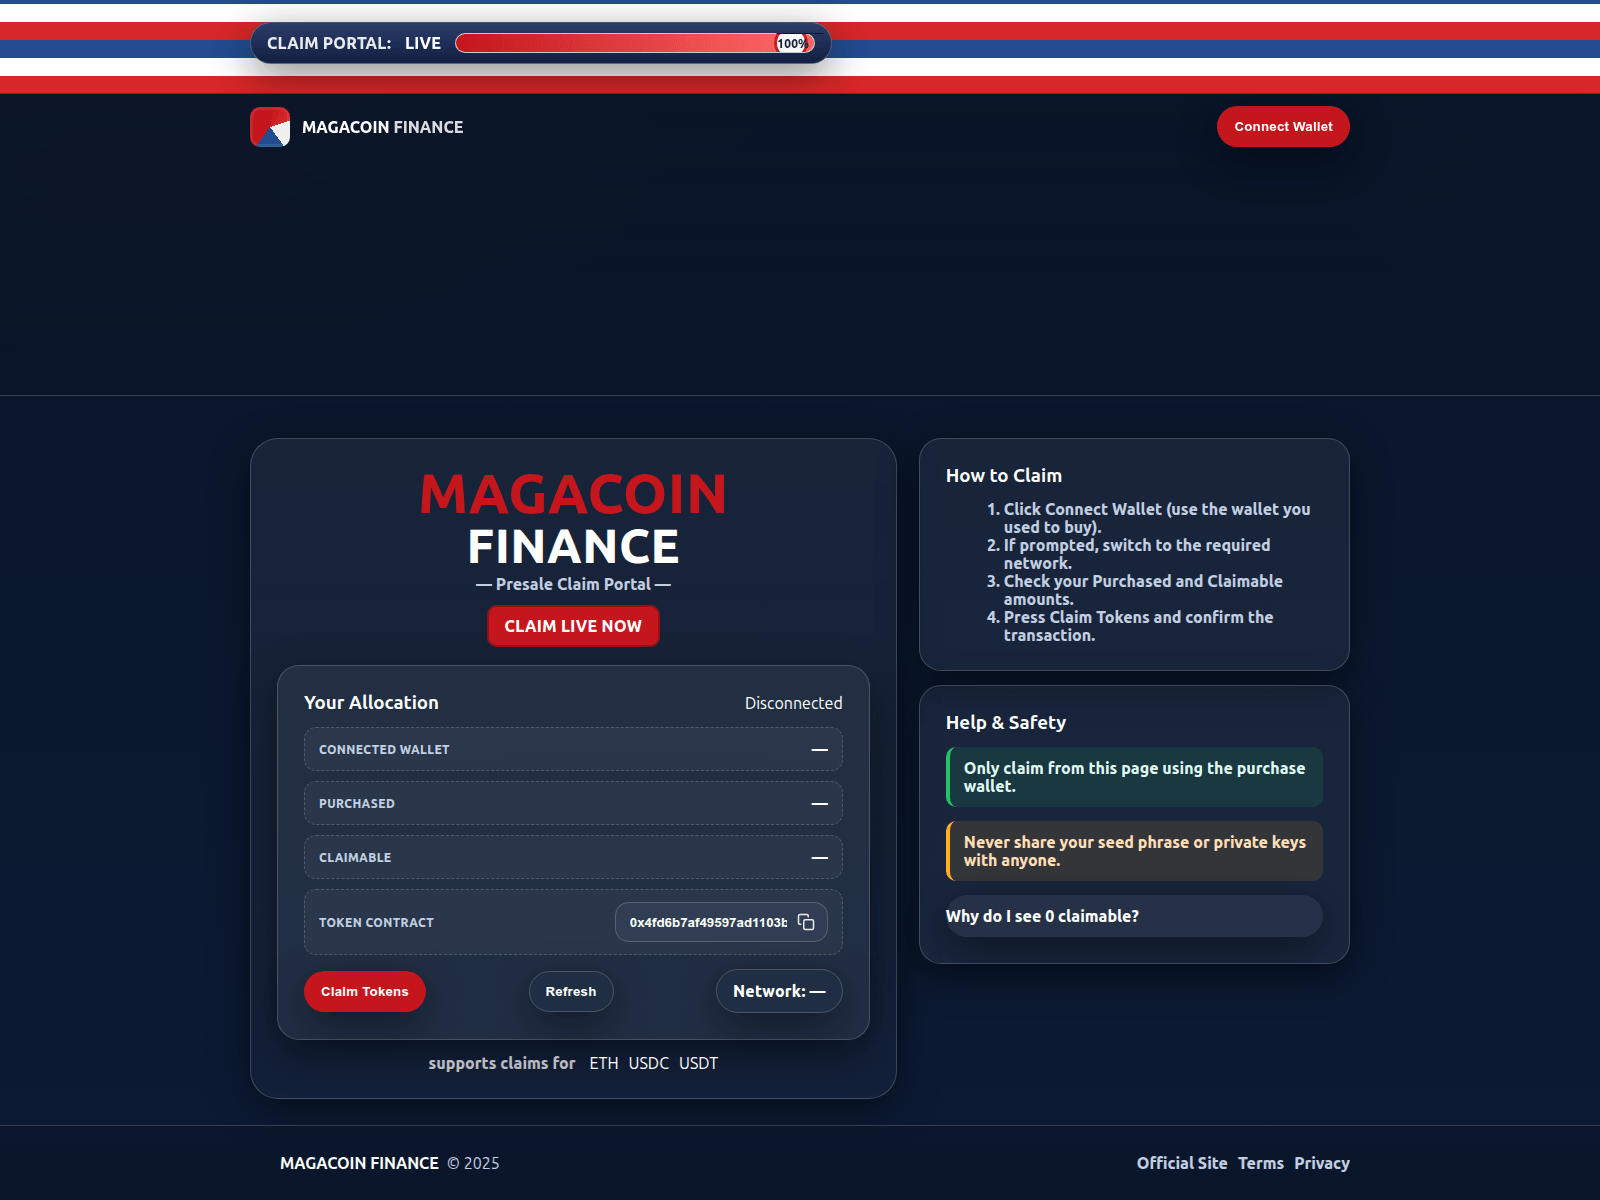
magacoin.info
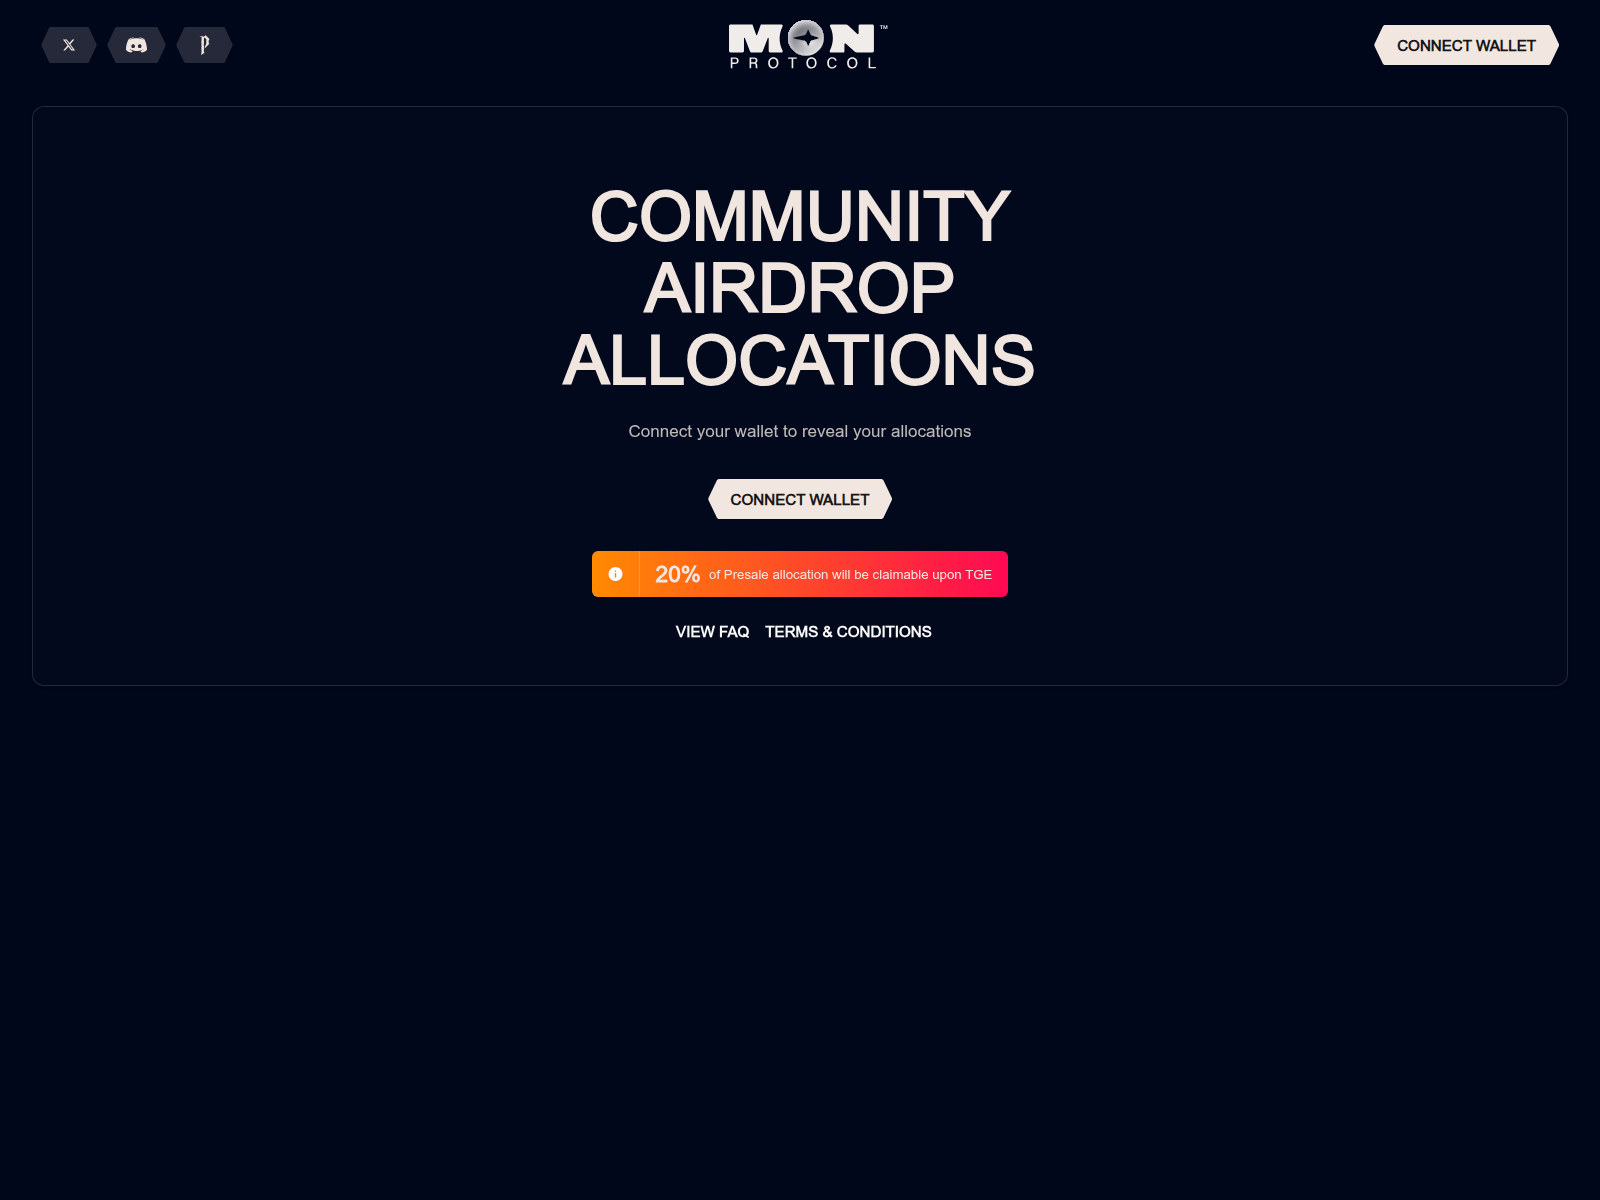
monproto.pages.dev
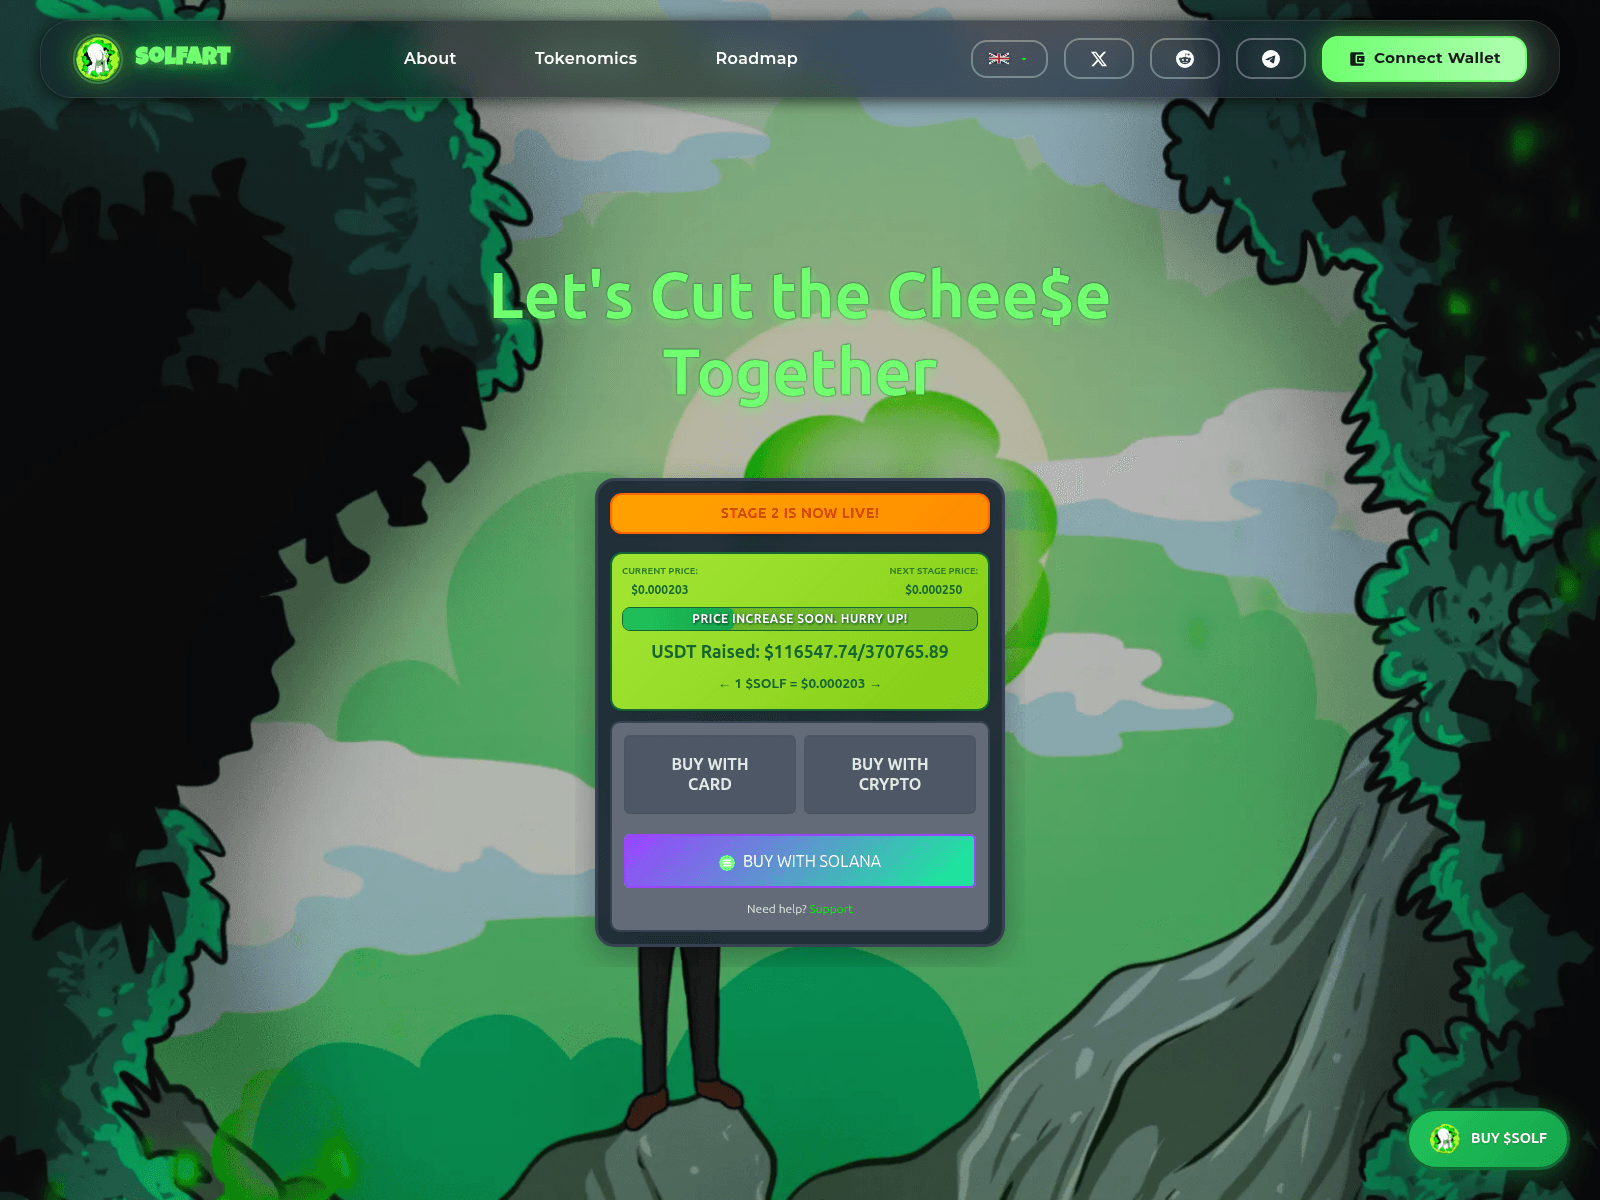
solfart.io
spax21k.icu
spx21k.com
spx80k-cointelegraph.com
spx98k.org
svardin.net
xa70b.com
bdagnetwork.info
bestwallet-app.com
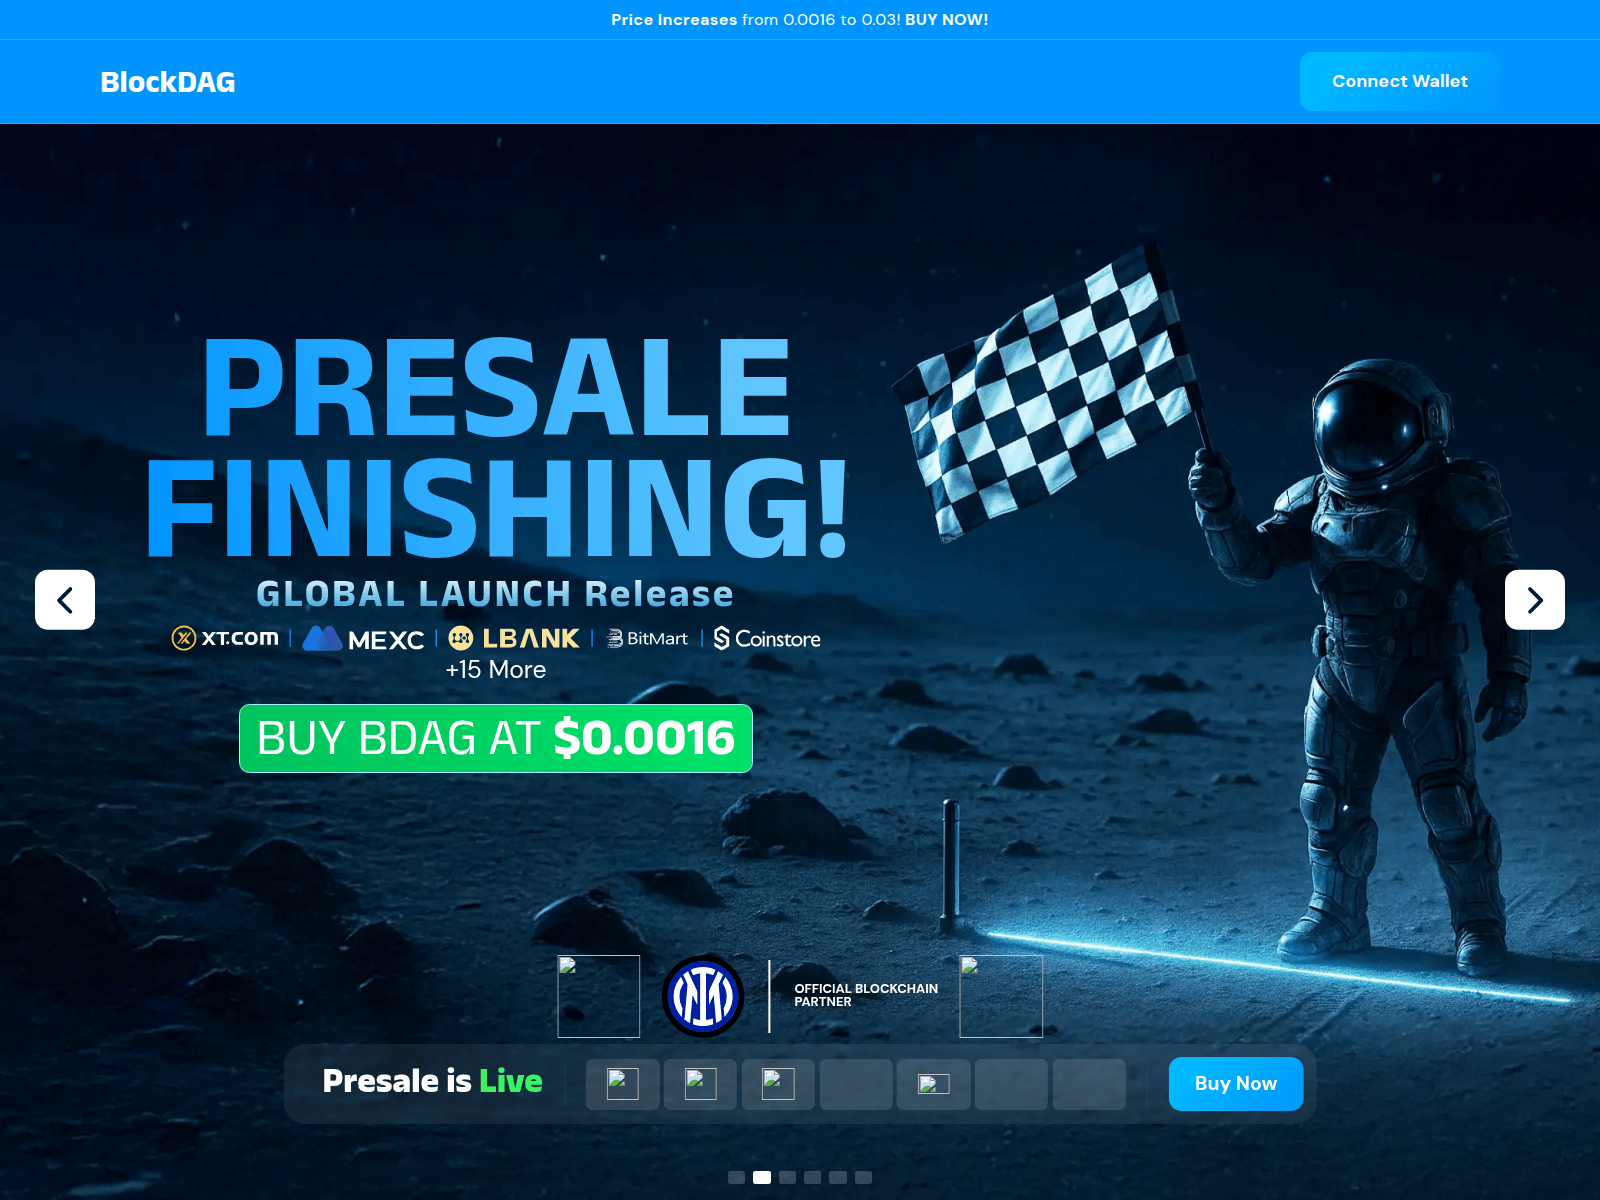
blockdagpresalenetwork.online
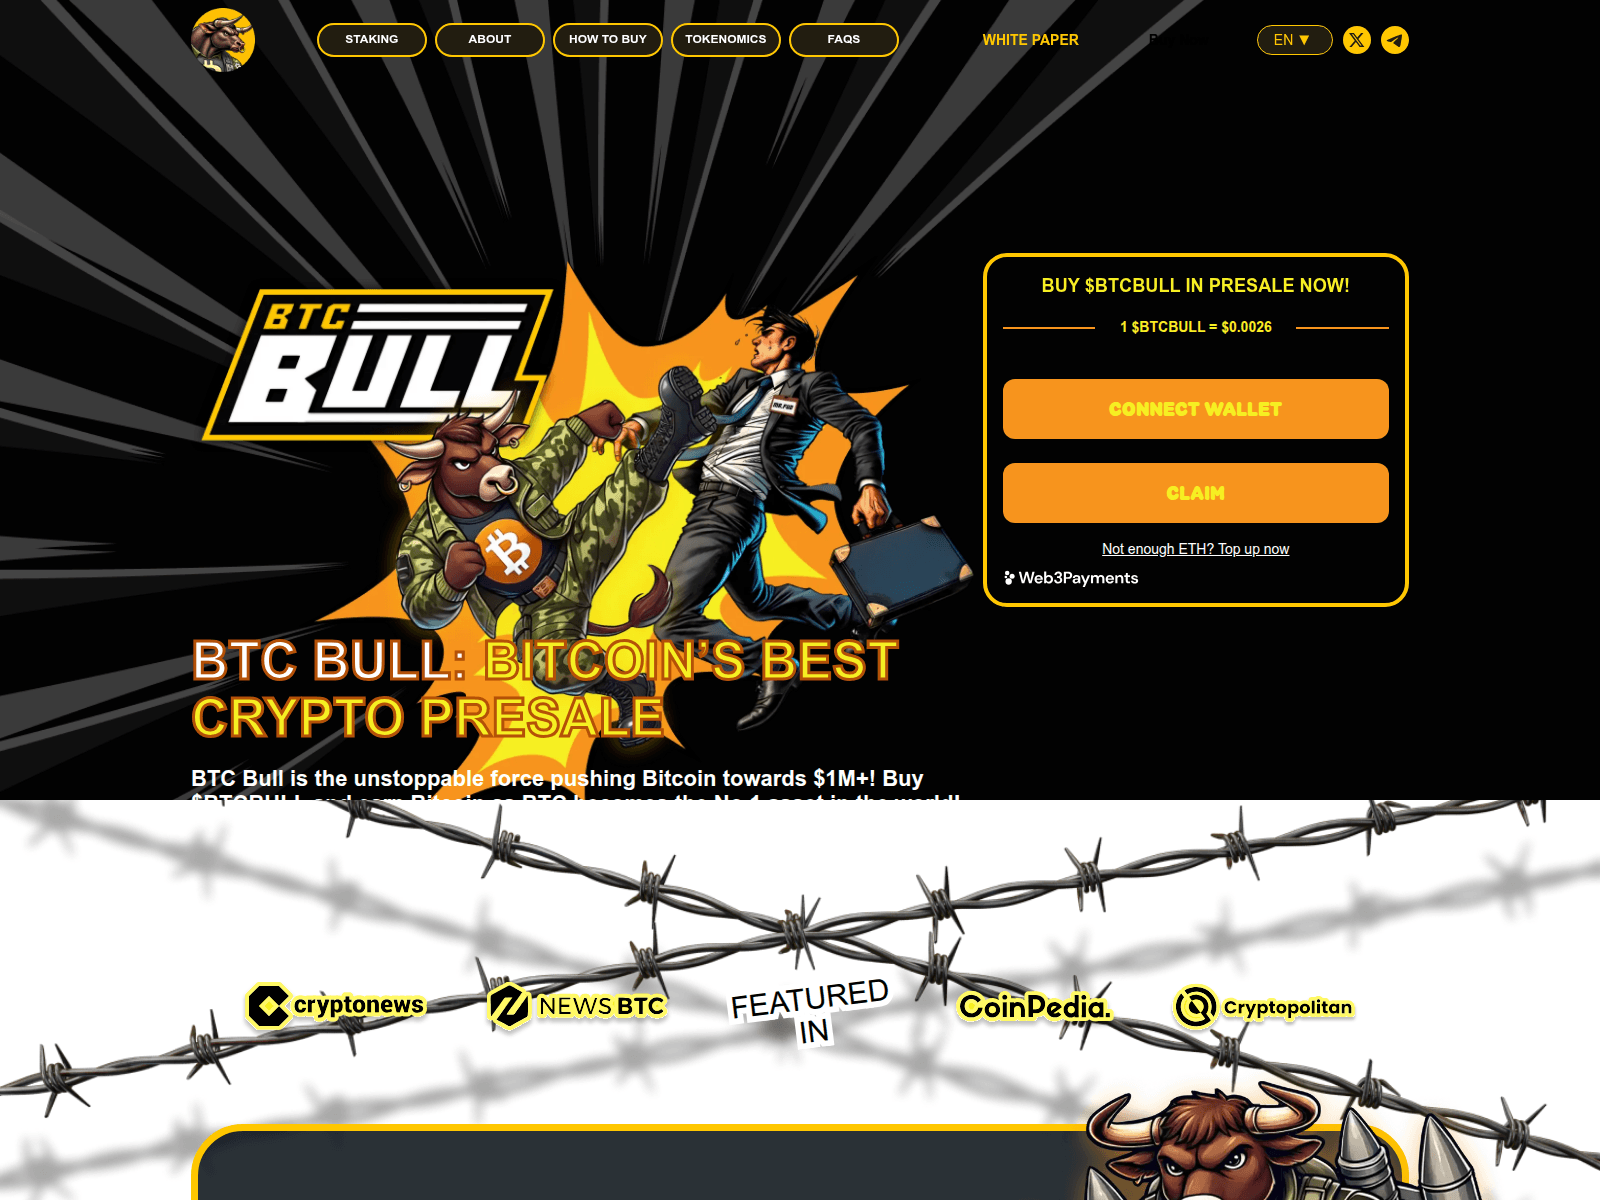
btcbullcoin.pages.dev
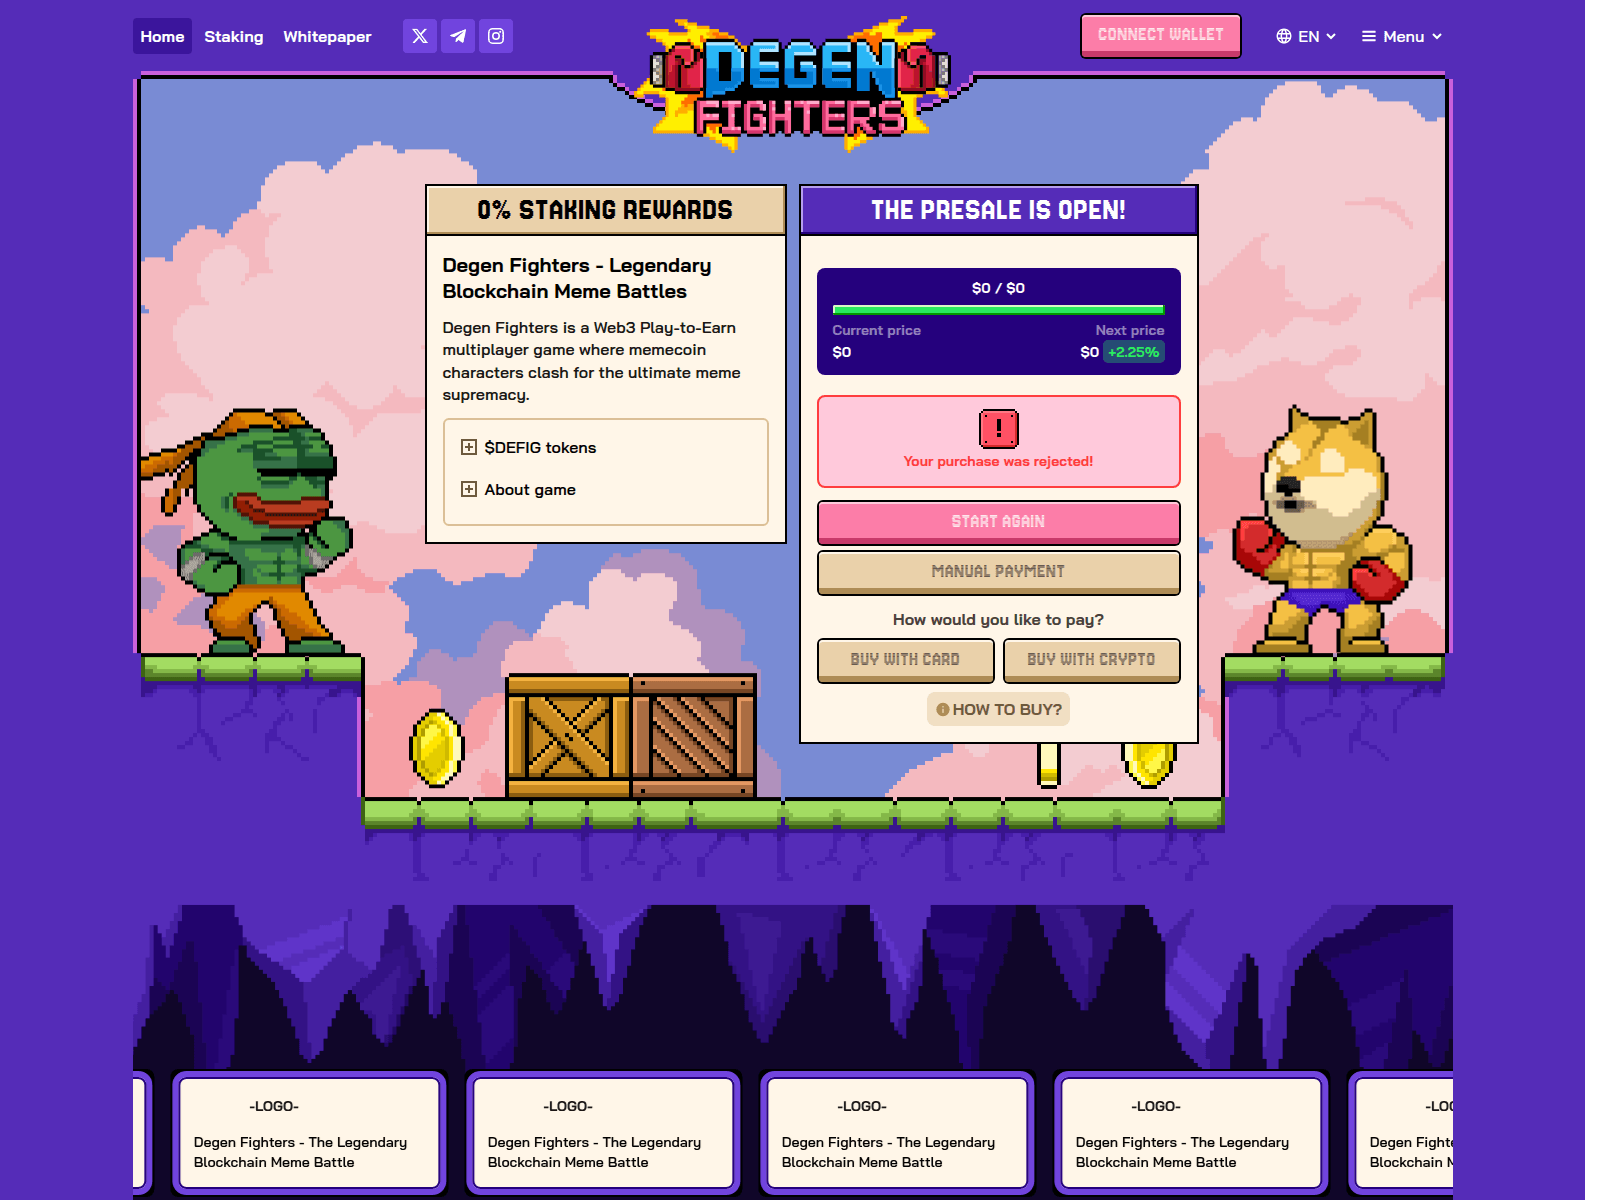
defig-8sw.pages.dev
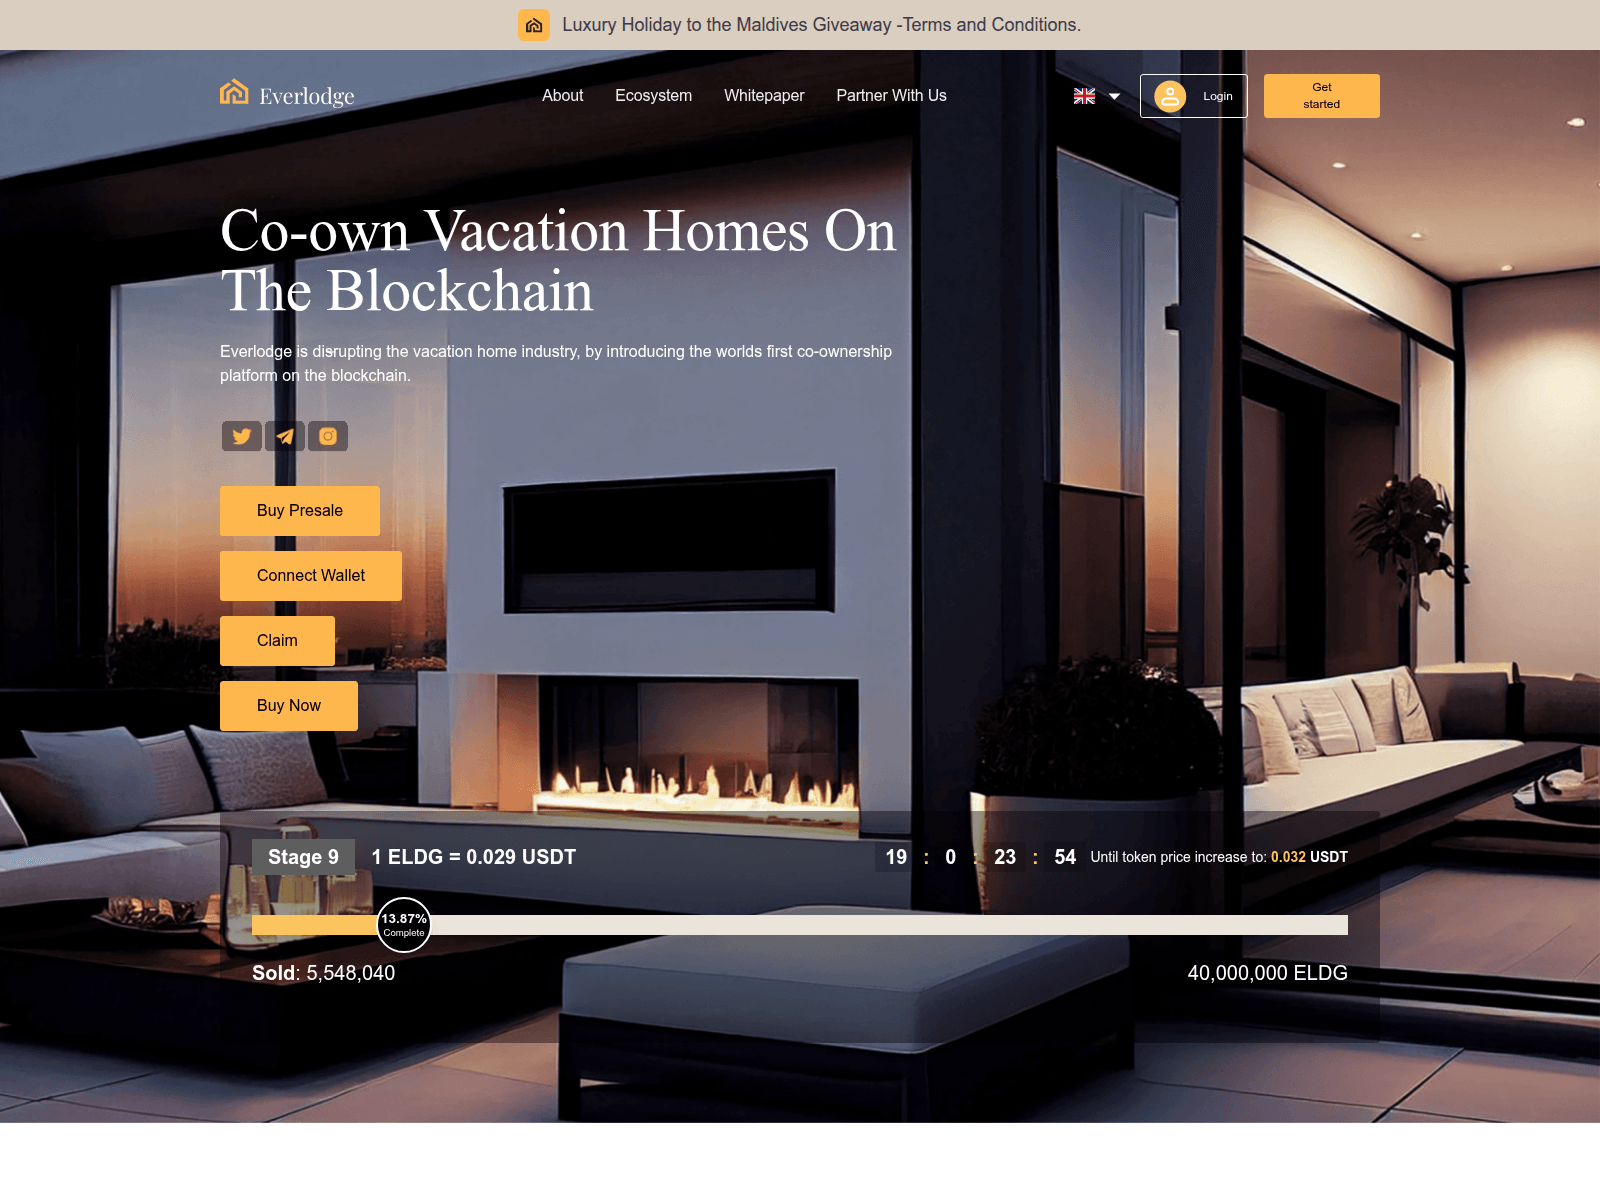
everlodge-claimv2.pages.dev
gro11k.com
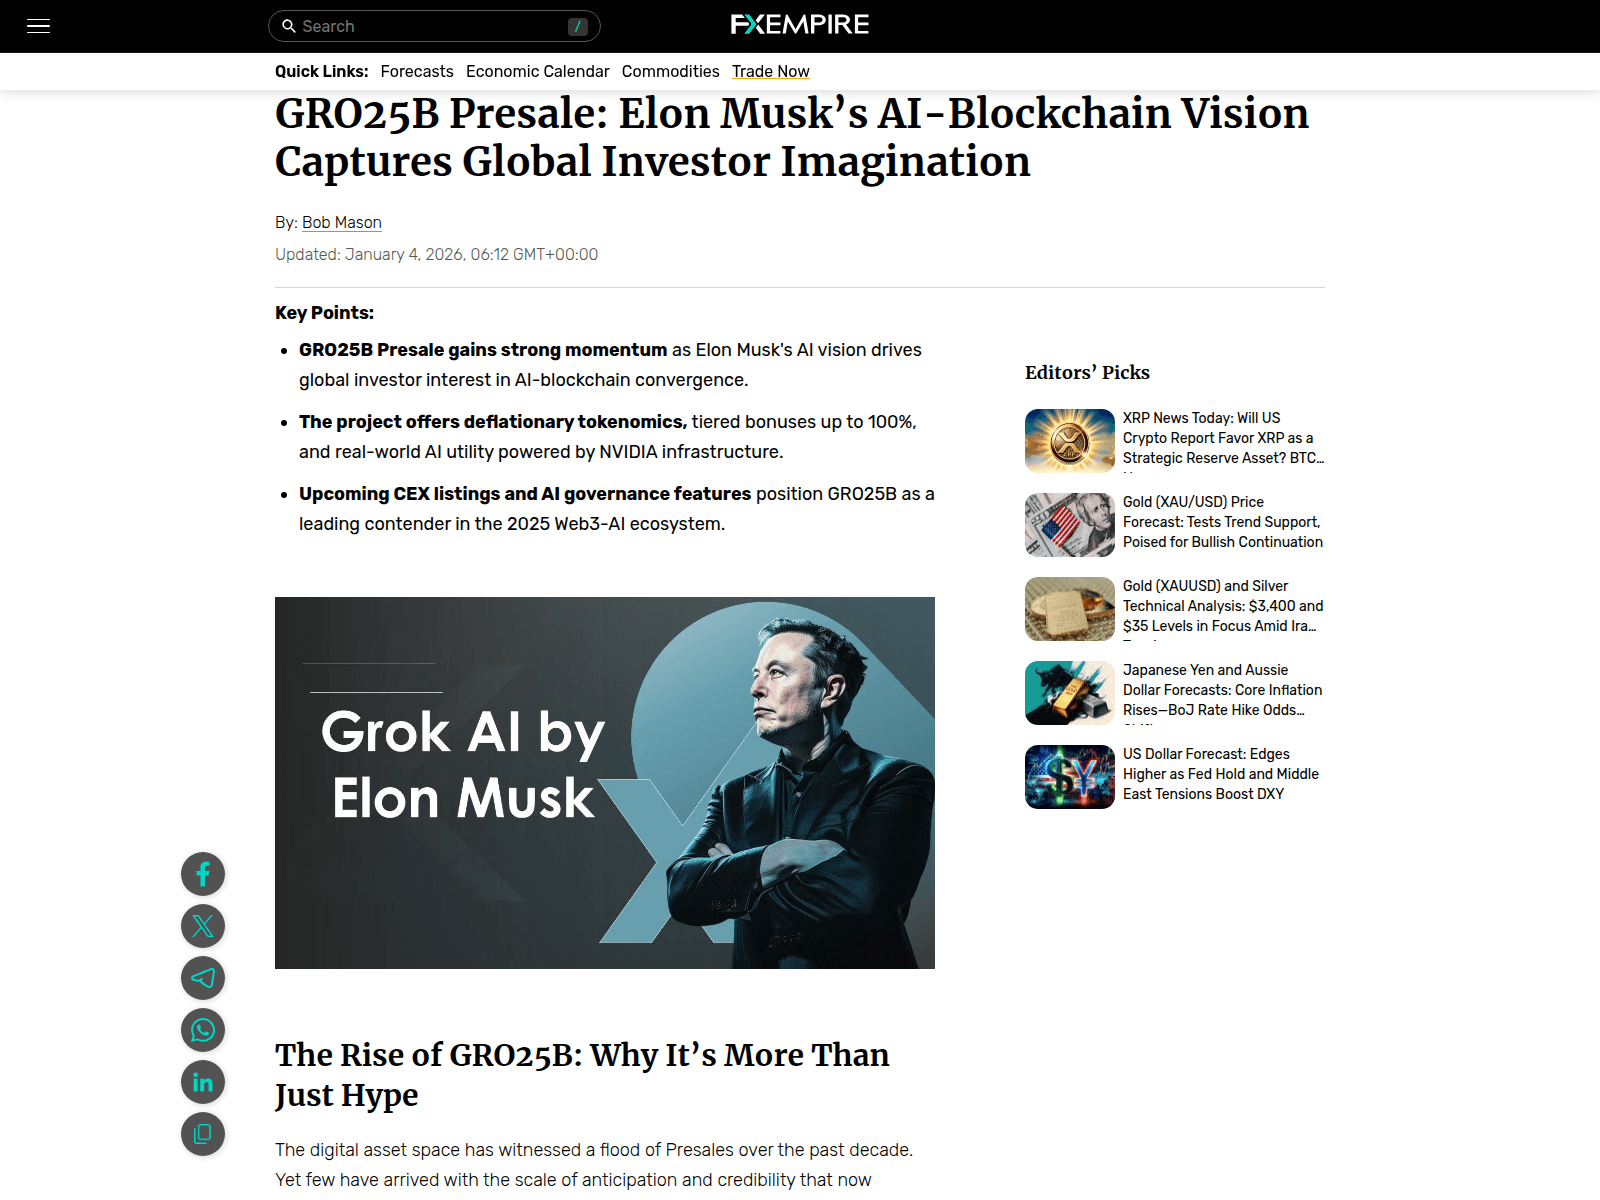
gro25b-fxempire.com
gro34d.com
gro47k.net
gro47k.org
gro87x.com
gro88k.com
gro88k.net
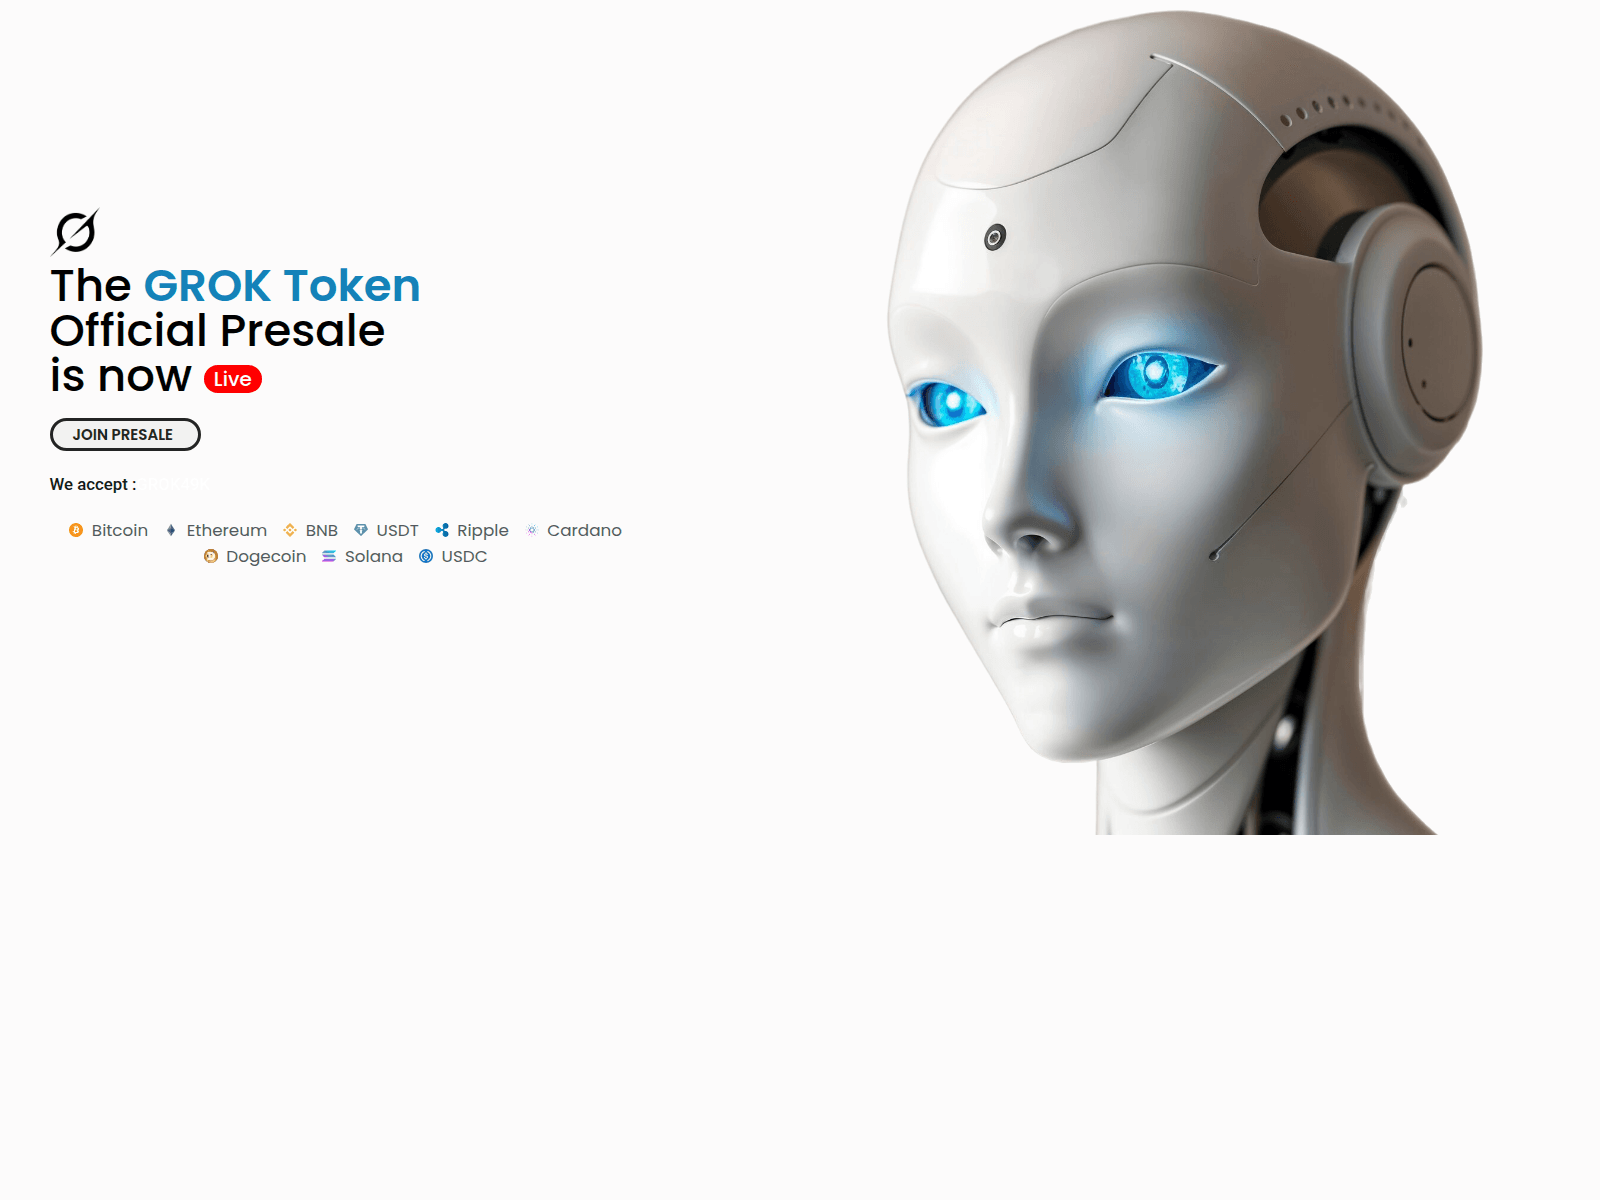
grok49k.com
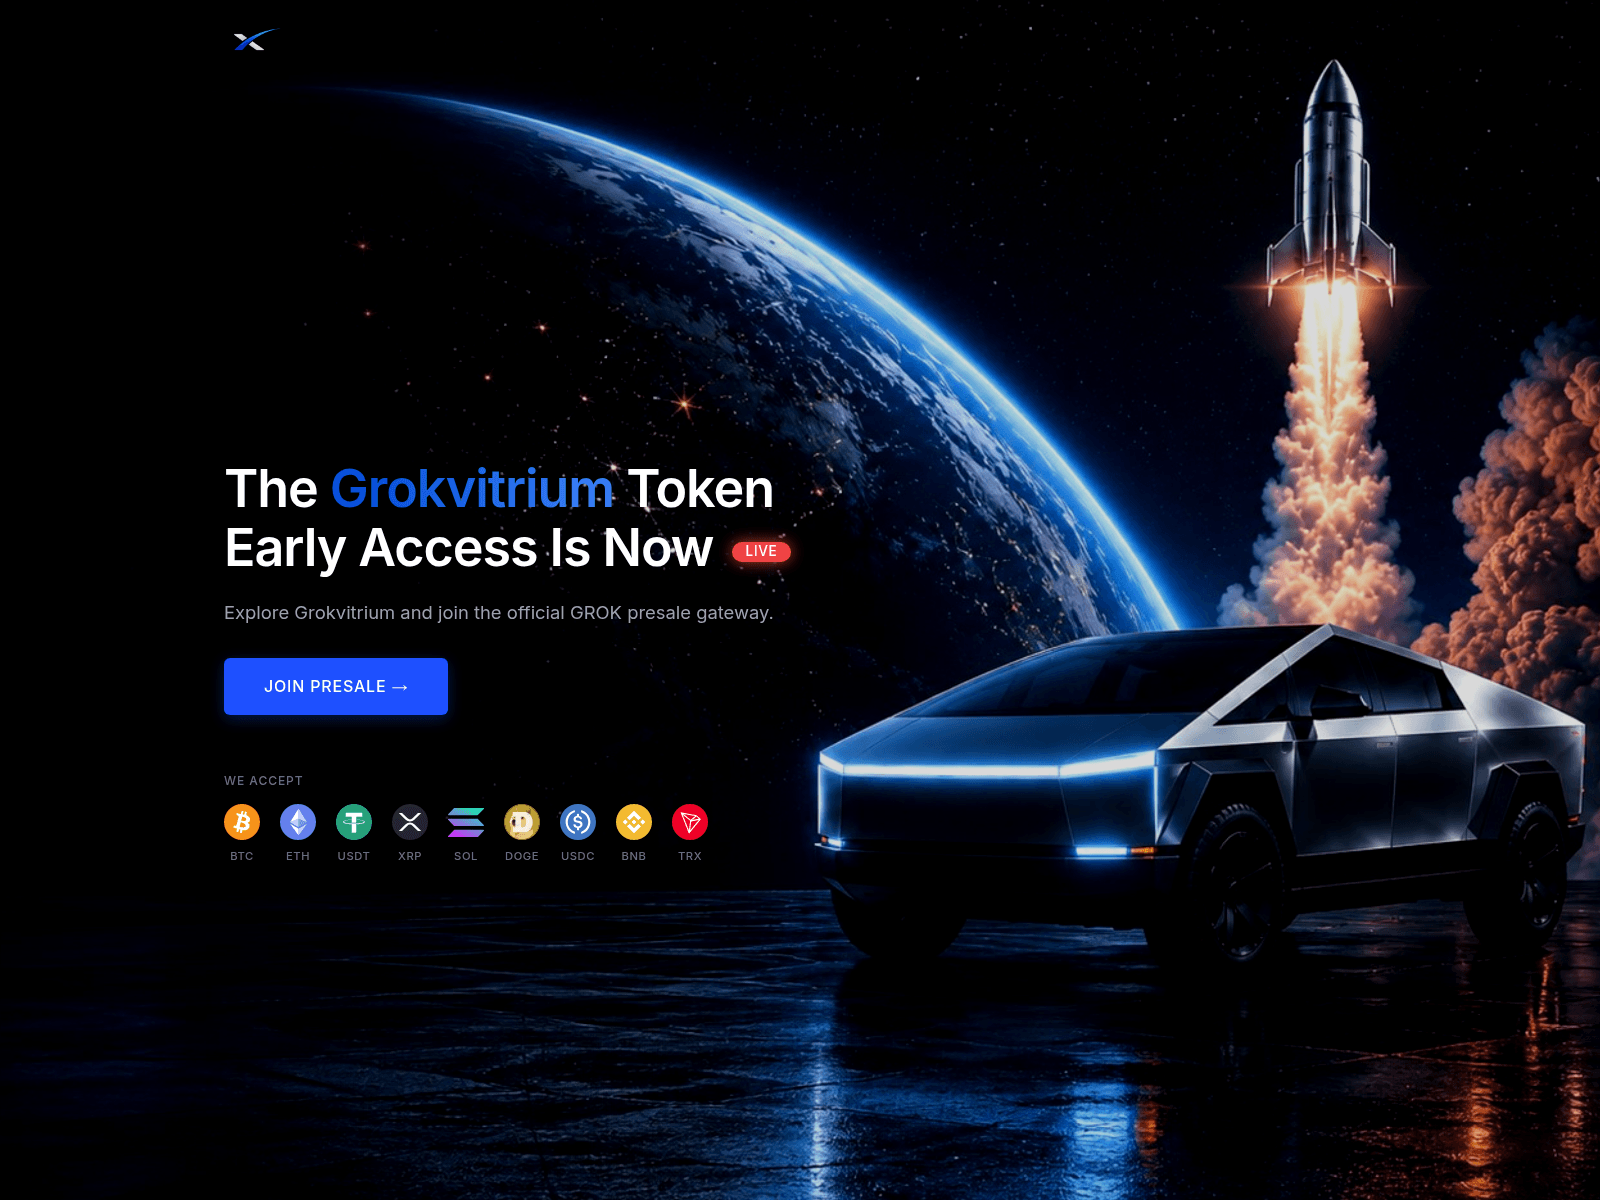
grokvitrium.org
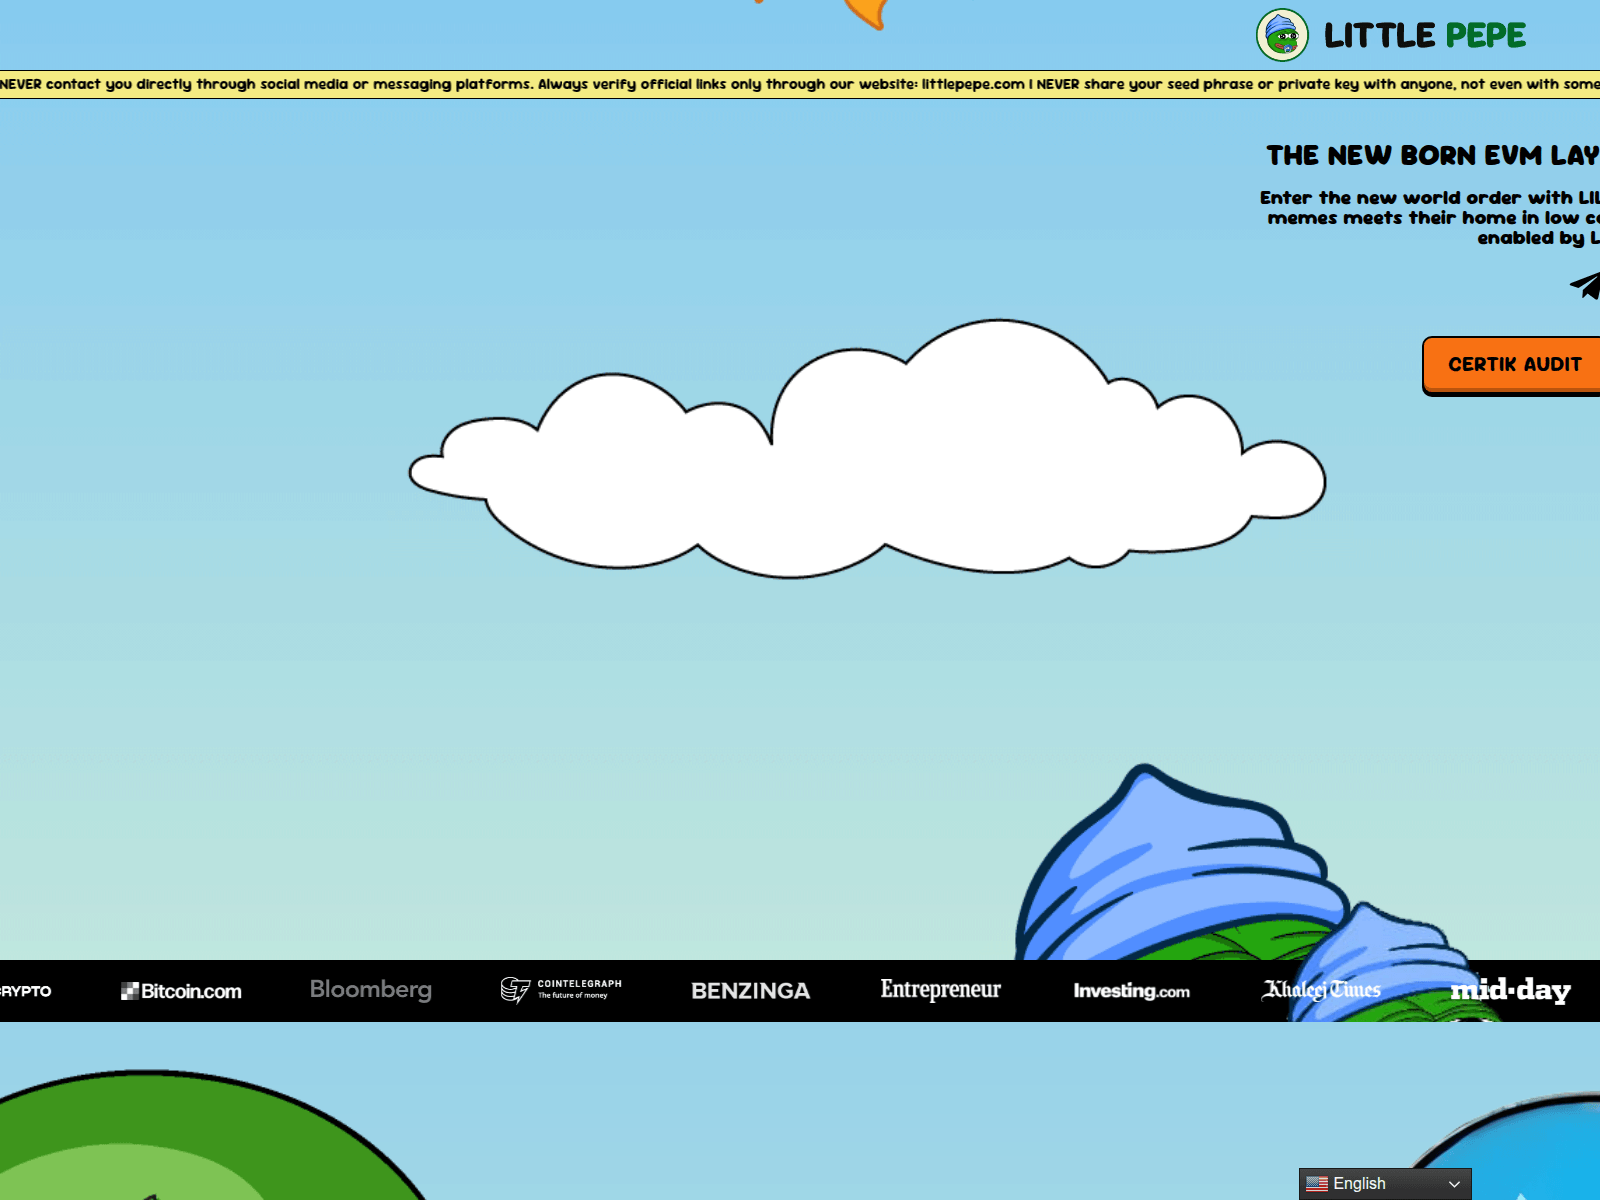
liitlpepe.com
liquidchain.info
litletlepepa.com
polymarketallocation.net
port3-lkfs8.pages.dev
purchase1-blockdag-networks.pages.dev
spax30t.com
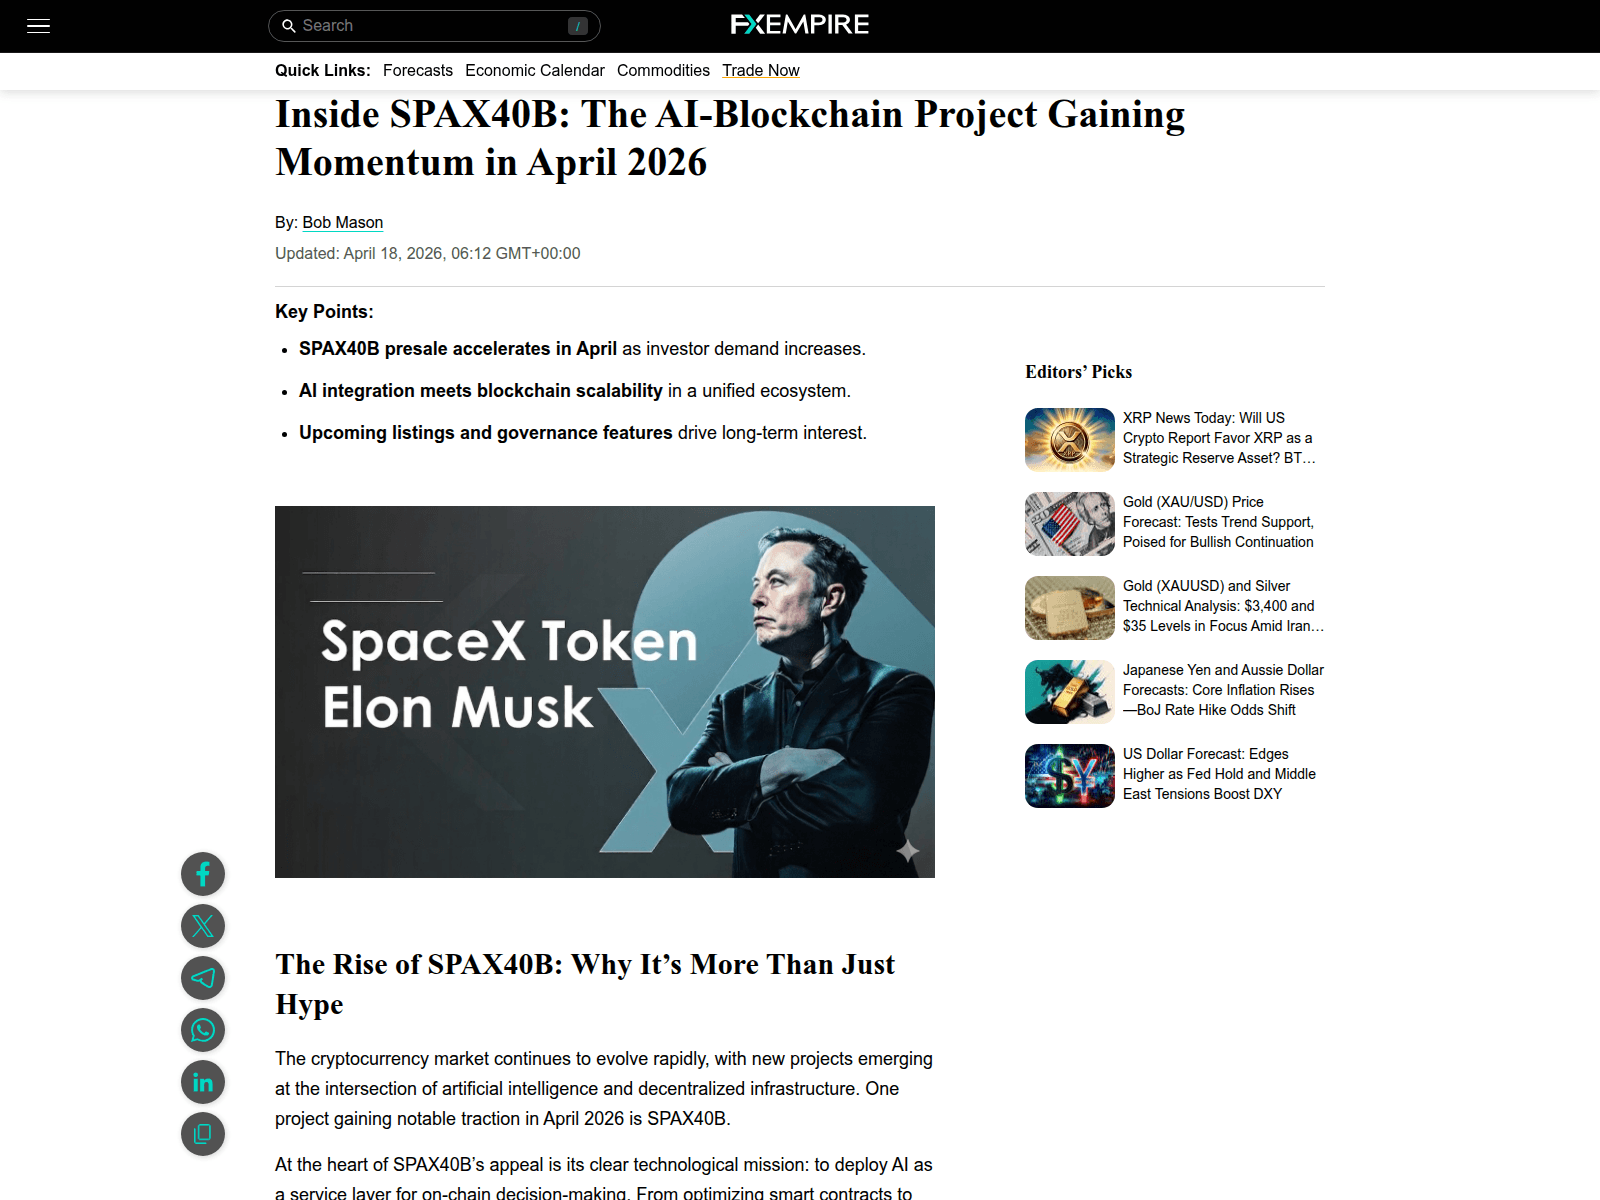
spax40b-fxempire.com
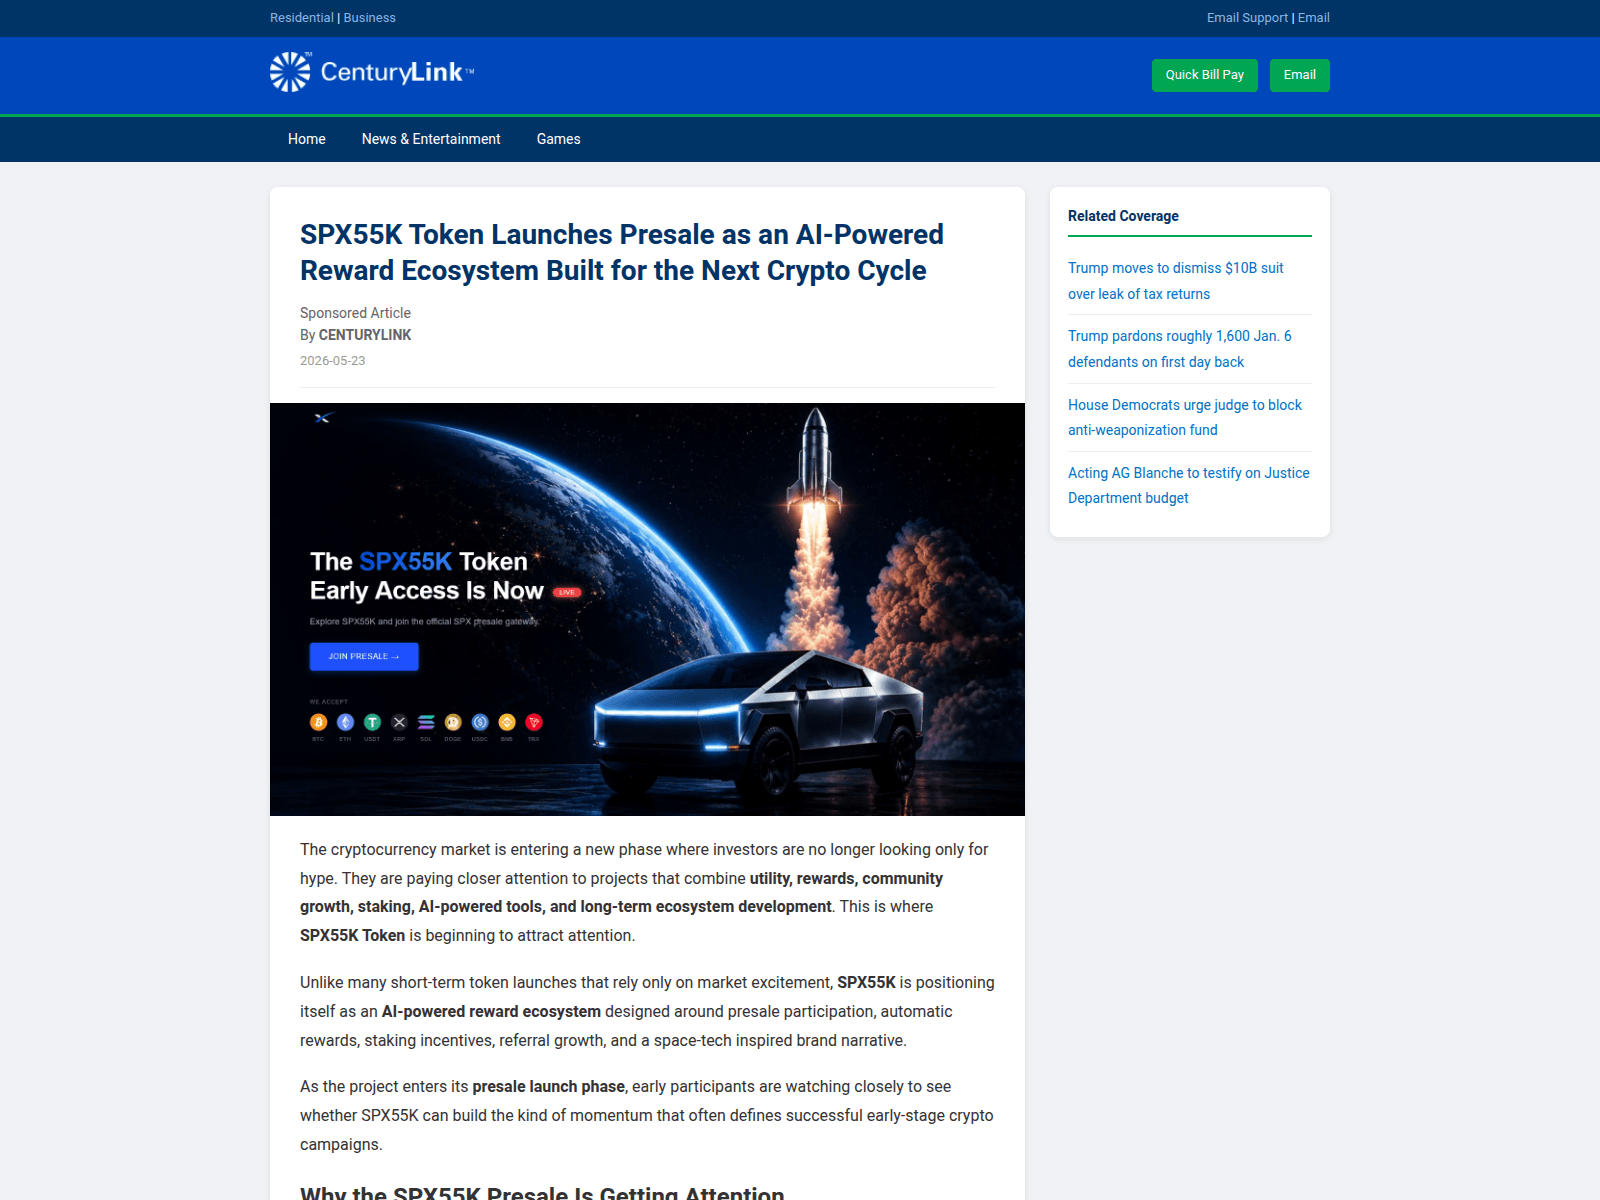
spx21k-centurylink.com
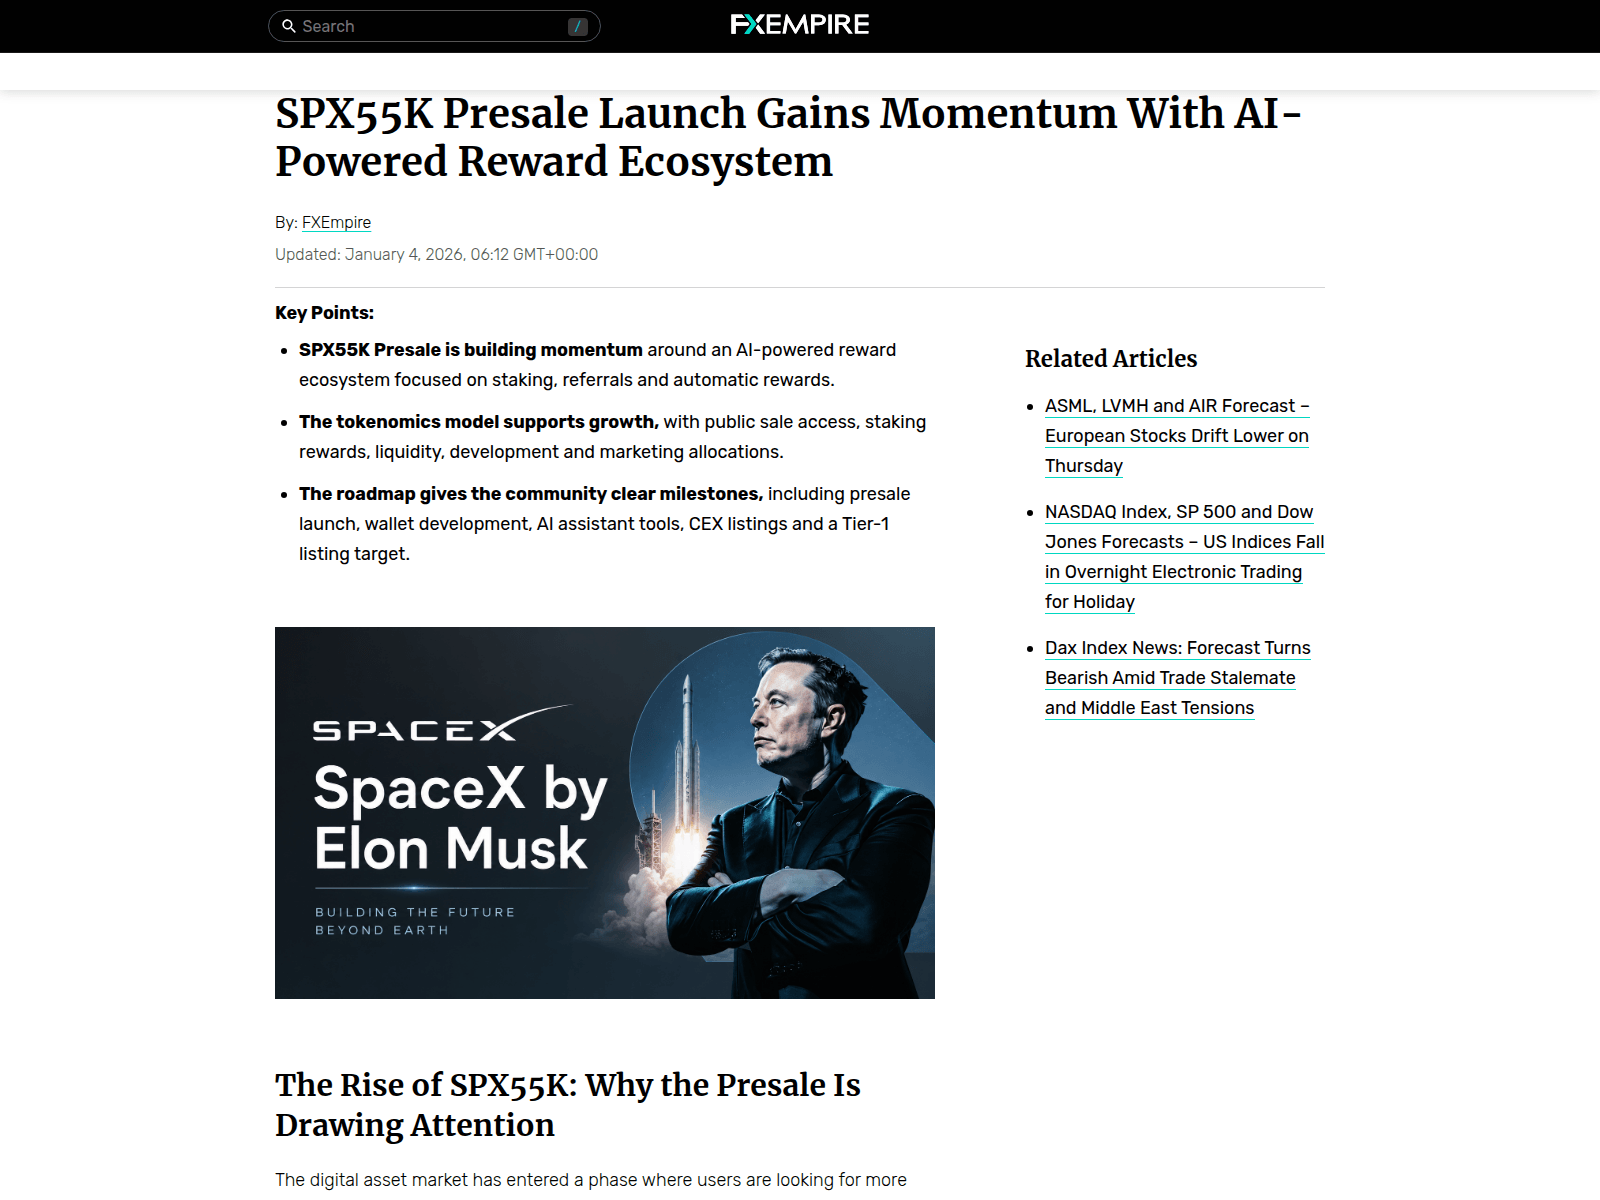
spx21k-fxempire.com
spx23h.com
spx40k.com
spx40k.org
spx45k.com
spx80k-fxempire.com
spx88k.org
spxpresale-coinpwire.com

xai19p.com
مسار الاستجابة للتهديدات Pipeline
كيف يتم التحقق من كل مجال في هذا المركز وكيف يتم تحييد التهديدات المؤكدة. تصور كامل لمسار العمل →
عمليات التحقق من معلومات التهديدات— يتم فحص كل نطاق ومقارنته بما يلي:
urlscan.ioلقطة شاشة · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency تقريررادار CloudflareDNS · certs · categoriesAlienVault OTXThreat-intel pulsesآلة الزمنHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS الأمن FiltersQuad9 · AdGuard · CleanBrowsingWeb-تحققFull surface scan
 crt.sh
المزامنة العالمية للموردين— يتم إرسال الإشعارات المتعلقة بحالات الكشف المؤكدة إلى 29 شريكًا:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardبيتديفندرThreat exchangeNortonSafe WebSymantecمراجعة الموقعAviraCloud detectionAvast / AVGWeb ShieldكاسبرسكيOpenTIPDr.WebOnline scannerنتكرافتإزالة APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.تقريرHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust