VirusTotal
22 / 93
报告
Interpretation & limits
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.


“WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co”
Assessment based on the stored source evidence below. Review sources →
wlfiprobit.com — 内容不可用. 品牌冒充:Arbitrum; 诈骗类型:Crypto Scam. 证据摘要: VirusTotal 22/93 (ADMINUSLabs, ChainPatrol, alphaMountain.ai, BitDefender, Cluster25); URLQuery 6 alerts; PhishDestroy score 95/100.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.
22 / 93
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.
6 threat-system alerts
报告Alerts refer to the preserved scan. They do not describe the current state of the site.
checked — no match recorded
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
2 community references
报告Community publication references, not a vendor verdict or evidence of a common operator.
存储的报告
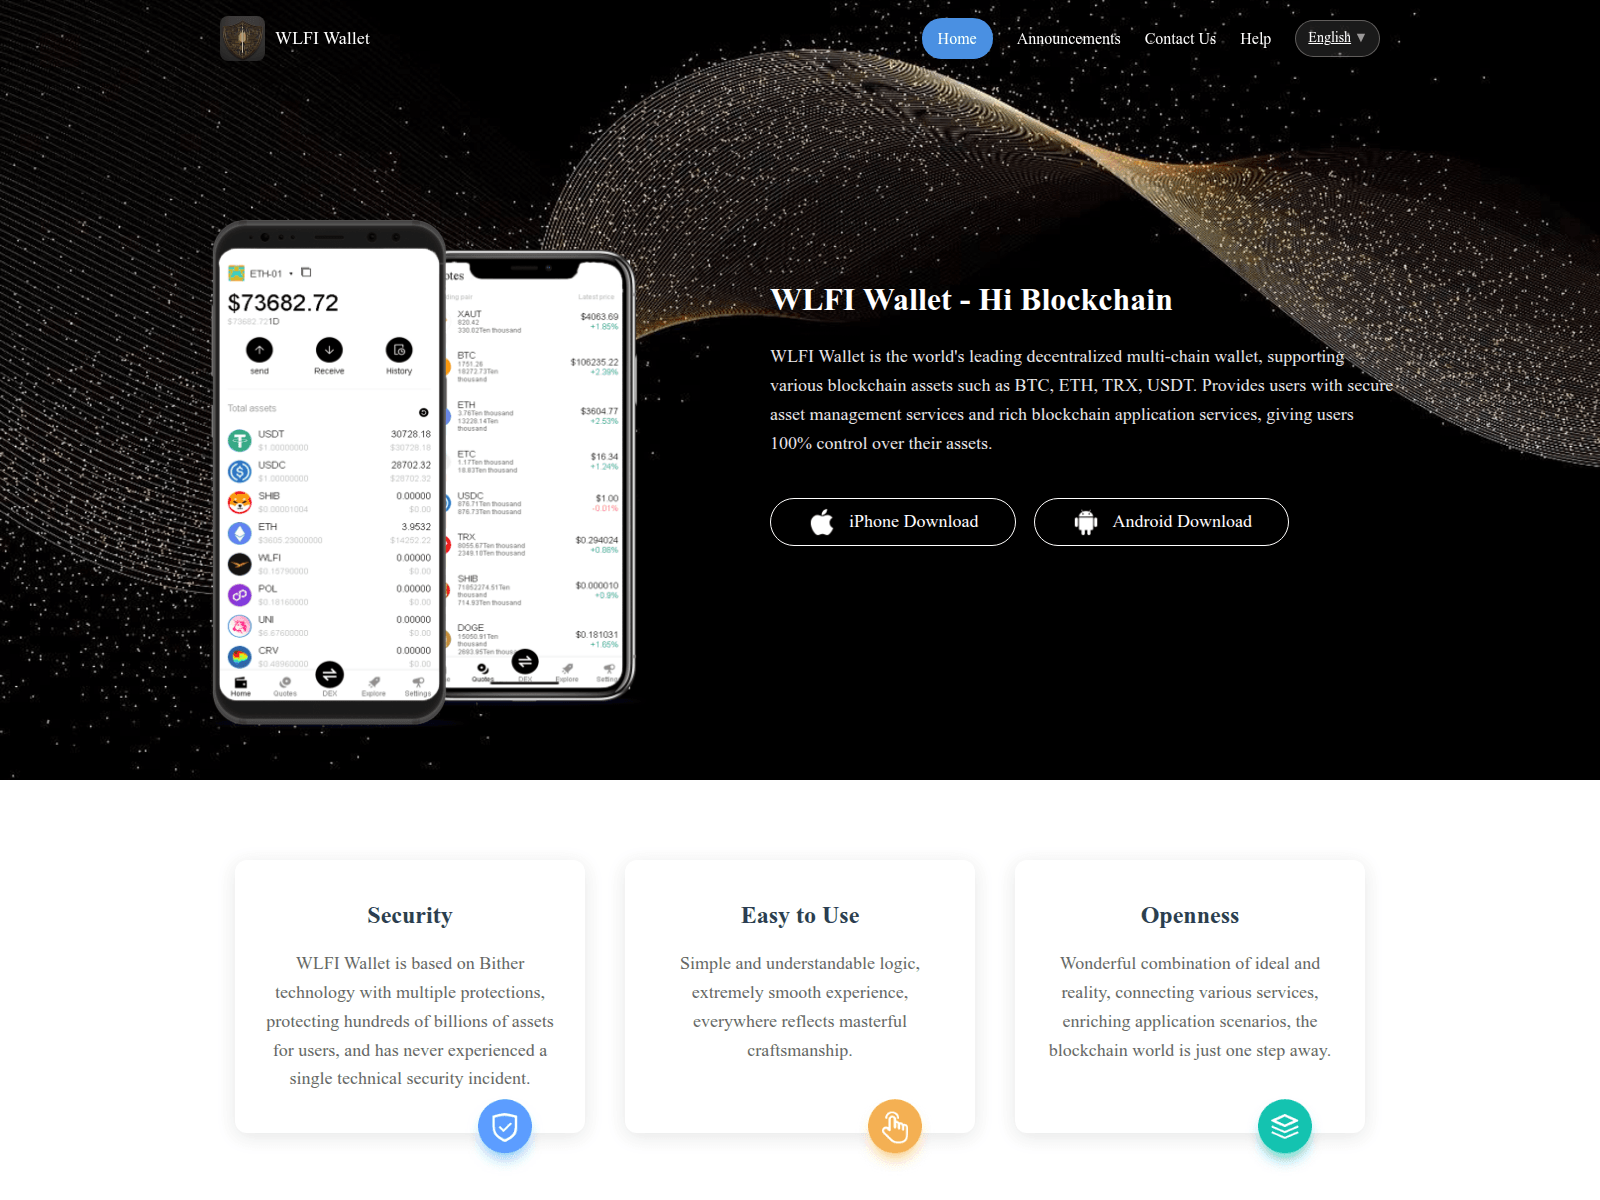
A preserved page image documents what the collector received; a capture is not a safety verdict.
分析完成
报告This is the recorded automated analysis. Completion alone is not a safety verdict.
Checked; no threat flag recorded
报告A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | wlfiprobit.com |
malicious | Sinkholed |
| OpenDNS | wlfiprobit.com |
phishing | Phishing Block |
| DigiCert UltraDNS | wlfiprobit.com |
malicious | Sinkholed |
| Hagezi Threat Feed | wlfiprobit.com |
malicious | Sinkholed |
| DNS4EU | wlfiprobit.com |
malicious | Sinkholed |
| Quad9 DNS | wlfiprobit.com |
malicious | Sinkholed |
The domain wlfiprobit.com is identified as a high-risk brand impersonation threat targeting Arbitrum. It masquerades as a legitimate cryptocurrency wallet service, using the page title "WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co" to deceive users. This domain was likely designed to harvest sensitive user data or credentials under the guise of offering cryptocurrency services.
Technical analysis reveals that wlfiprobit.com is flagged by 22 out of 95 security vendors on VirusTotal, indicating significant recognition as a threat. The domain resolves to IP address 172.67.152.201, located in the United States under AS13335 managed by Cloudflare, Inc. It was created on February 21, 2026, and has been blocked by three security blocklists including PhishDestroy, MetaMask, and SEAL. The domain's SSL certificate is identified as WE1, and it is currently offline, reducing immediate exposure.
The domain's current offline status mitigates immediate risk; however, vigilance is advised as it may resurface or similar threats could emerge. Security teams should ensure that blocklists are updated and implement additional monitoring for similar activities. Users should be educated on recognizing phishing attempts, particularly those involving cryptocurrency platforms.
针对该主机的爬虫与浏览器观察记录,以及针对“Keitaro”式流量分配系统的实时指纹检测。
扫描说明: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='wlfiprobit.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError(
Edge-IP 声誉不属于此域。
Location describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
已存储 28 个仿冒域名
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。
选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。
Template-based draft · optional AI wording assistance requires separate consent
每条路径都代表一个将域名与该主机关联的原因。实心节点表示已检测到VirusTotal,虚线节点表示已离线。完整列表如下。
与该主机的网站图标哈希值相同,或页面标题相同。
这些域名还以Arbitrum用户为目标。 查看所有Arbitrum威胁 →
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。






