报告概览
triangleclub.net — 未验证. 证据摘要: VirusTotal 15/89 (alphaMountain.ai, BitDefender, CyRadar, ESET, Forcepoint ThreatSeeker); URLQuery 2 det.; URLScan capture; PhishDestroy score 95/100. 注册商: GoDaddy.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
证据摘要
重要
PhishDestroy first observed triangleclub.net on Sep 22, 2026. Current evidence score: 95/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and URLQuery. VirusTotal recorded 15 detections among 89 engines: alphaMountain.ai, BitDefender, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, Seclookup, SOCRadar, Sophos, VIPRE, Webroot on Sep 22, 2026 at 19:39 UTC. URLQuery recorded 2 detections; no observation timestamp was retained. Non-positive and contextual checks: On Sep 22, 2026 at 19:39 UTC, AlienVault OTX listed 5 community pulse references (not vendor detections); Google Safe Browsing returned no flag. The separate external-blocklist snapshot contained no matches on Sep 22, 2026 at 18:20 UTC. URLScan captured the page on Sep 22, 2026 at 18:38 UTC.
The collector marked the hostname reachable on Sep 22, 2026 at 18:38 UTC, but did not retain the HTTP response code. Registration records for the domain list GoDaddy.com, LLC as the registrar and Oct 12, 2023 as the creation date. At collection time, the hostname resolved to 154.83.186.199. The evidence archive retains 3 visual captures from PhishDestroy and URLScan; no page title was retained, so the captures preserve the landing-page appearance. TLS metadata lists Let's Encrypt / YR1 as the certificate issuer with validity through Sep 9, 2026; checked Sep 22, 2026 at 19:02 UTC.
The record contains 2 positive source findings supporting the current phishing classification. The stored fields do not identify an impersonated brand or victim interaction.
VirusTotal
15 det.
URLQuery
2 det.
OTX references
URLScan
TLS 证书
已过期或未验证 -14d
年龄
2.9 yr
观测状态
未验证

DestroyList
已列入
Reports Sent
1
数据覆盖范围
VirusTotal
15 / 89
URLQuery
2 det.
OTX
5 community references
URLScan capture
存储的报告
TLS
已过期或未验证
WHOIS
36 mo old
屏幕截图
3 captures · 2 sources
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 22, 2026 · 20:38 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
154.83.186.199.
威胁响应 Pipeline
发现
Checks
Reports
可用性
10/11
Sent Report Recorded
Stored sent-report record for registrar GoDaddy.com, LLC, hosting provider, 1 abuse contact
abuse@godaddy.com
公共封禁名单状态
探测与规避分析
隐身和流量分配检查
尚未扫描
目前尚未记录到爬虫与浏览器之间的差异
针对该主机的爬虫与浏览器观察记录,以及针对“Keitaro”式流量分配系统的实时指纹检测。
- 存储的隐身标志
- 尚未扫描
TDS指纹识别实时演示
七个Keitaro指纹,外加爬虫与浏览器的对比,当此面板打开时,由PhishDestroy扫描器运行。
等待
已保存的截图 · 3 sources
域名情报
域名
IP 信誉
abuse score 0/100 0 reports checked 2026年9月22日
OTX Tags
2026-09activeall-domainsblocklistcontentcrypto域名drainerfraudlivemonthlyphishdestroyphishingscam
注册商
GoDaddy
 (US)
(US)
注册信息创建 2023年10月12日 — Expires 2028年10月12日
技术详情DNS、SSL SAN、时间戳
首次发现2026年9月22日
Submitted URLhttp://triangleclub.net/
域名服务器ns1.mysecurecloudhost.comns2.mysecurecloudhost.comns3.mysecurecloudhost.comns4.mysecurecloudhost.com
TLS Fingerprint
TLS Observation
案件 ID
举报此域名
提交证据,帮助保护他人
VirusTotal 分析
15 / 89 安全供应商标记了该域
View on VT
Last analyzed First positive detection Previous stored snapshot: 15 detections
alphaMountain.ai
BitDefender
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
卡巴斯基
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
证据与外部报告
证券分析
已提交证据快照
Sent: Ledger records: 1
Case ID:
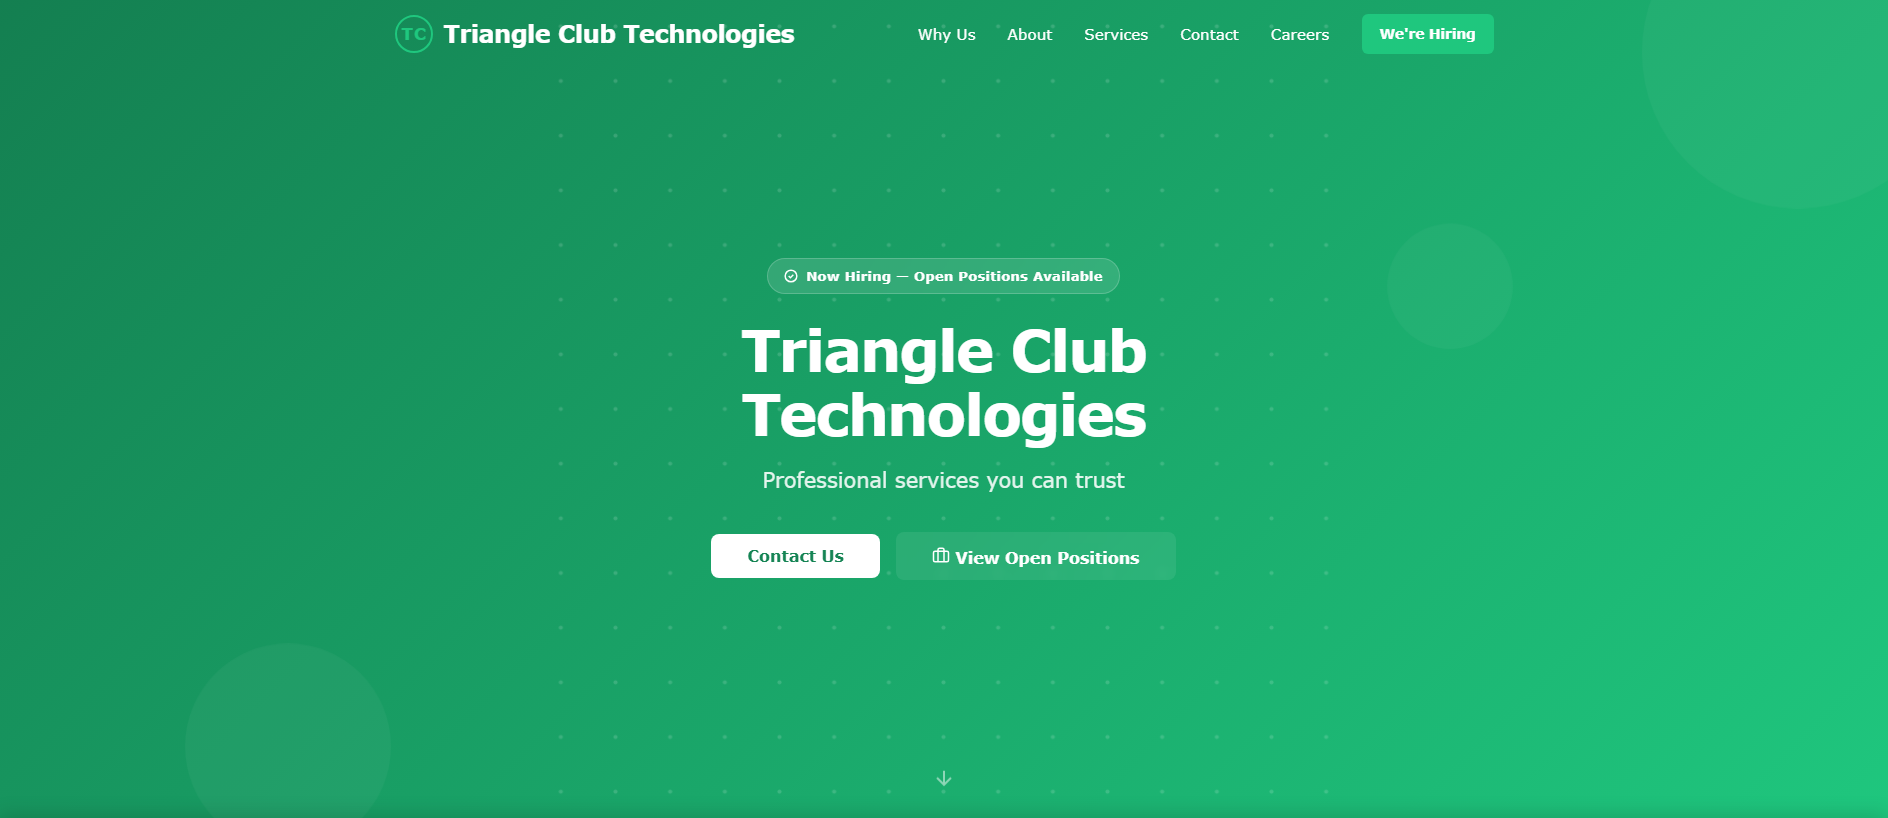
PD-20260922-36F1CC Recipient: abuse@godaddy.com Page title stored with report: Triangle Club Technologies — Professional services you can trust
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT与情报分析
DNS 与网络
SEO 与域名
您是否受到本网站的影响?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。

PhishDestroy listing review 不是执法报告
域名申诉
如果您拥有该域名并认为该列表不正确,请请求审核
警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关康复欺诈的更多信息 →
相关基础设施与报告
- 直接链接 共享一个注册信息或一个完全相同的网络钓鱼工具包。
- 辅助信号 共享基础设施或目标品牌;并非证明由同一家运营商运营。
- 仅限探索 已列入导航列表;与该主机无共同属性。
每条路径都代表一个将域名与该主机关联的原因。实心节点表示已检测到VirusTotal,虚线节点表示已离线。完整列表如下。
共享IP 154.83.186.199 6
该源 IP 托管多个网络钓鱼域 - 基础设施可以在各个活动之间共享。

同一注册商: GoDaddy 6
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。


最近的威胁报告 6
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。