




域安全和威胁情报

dilyauto.com
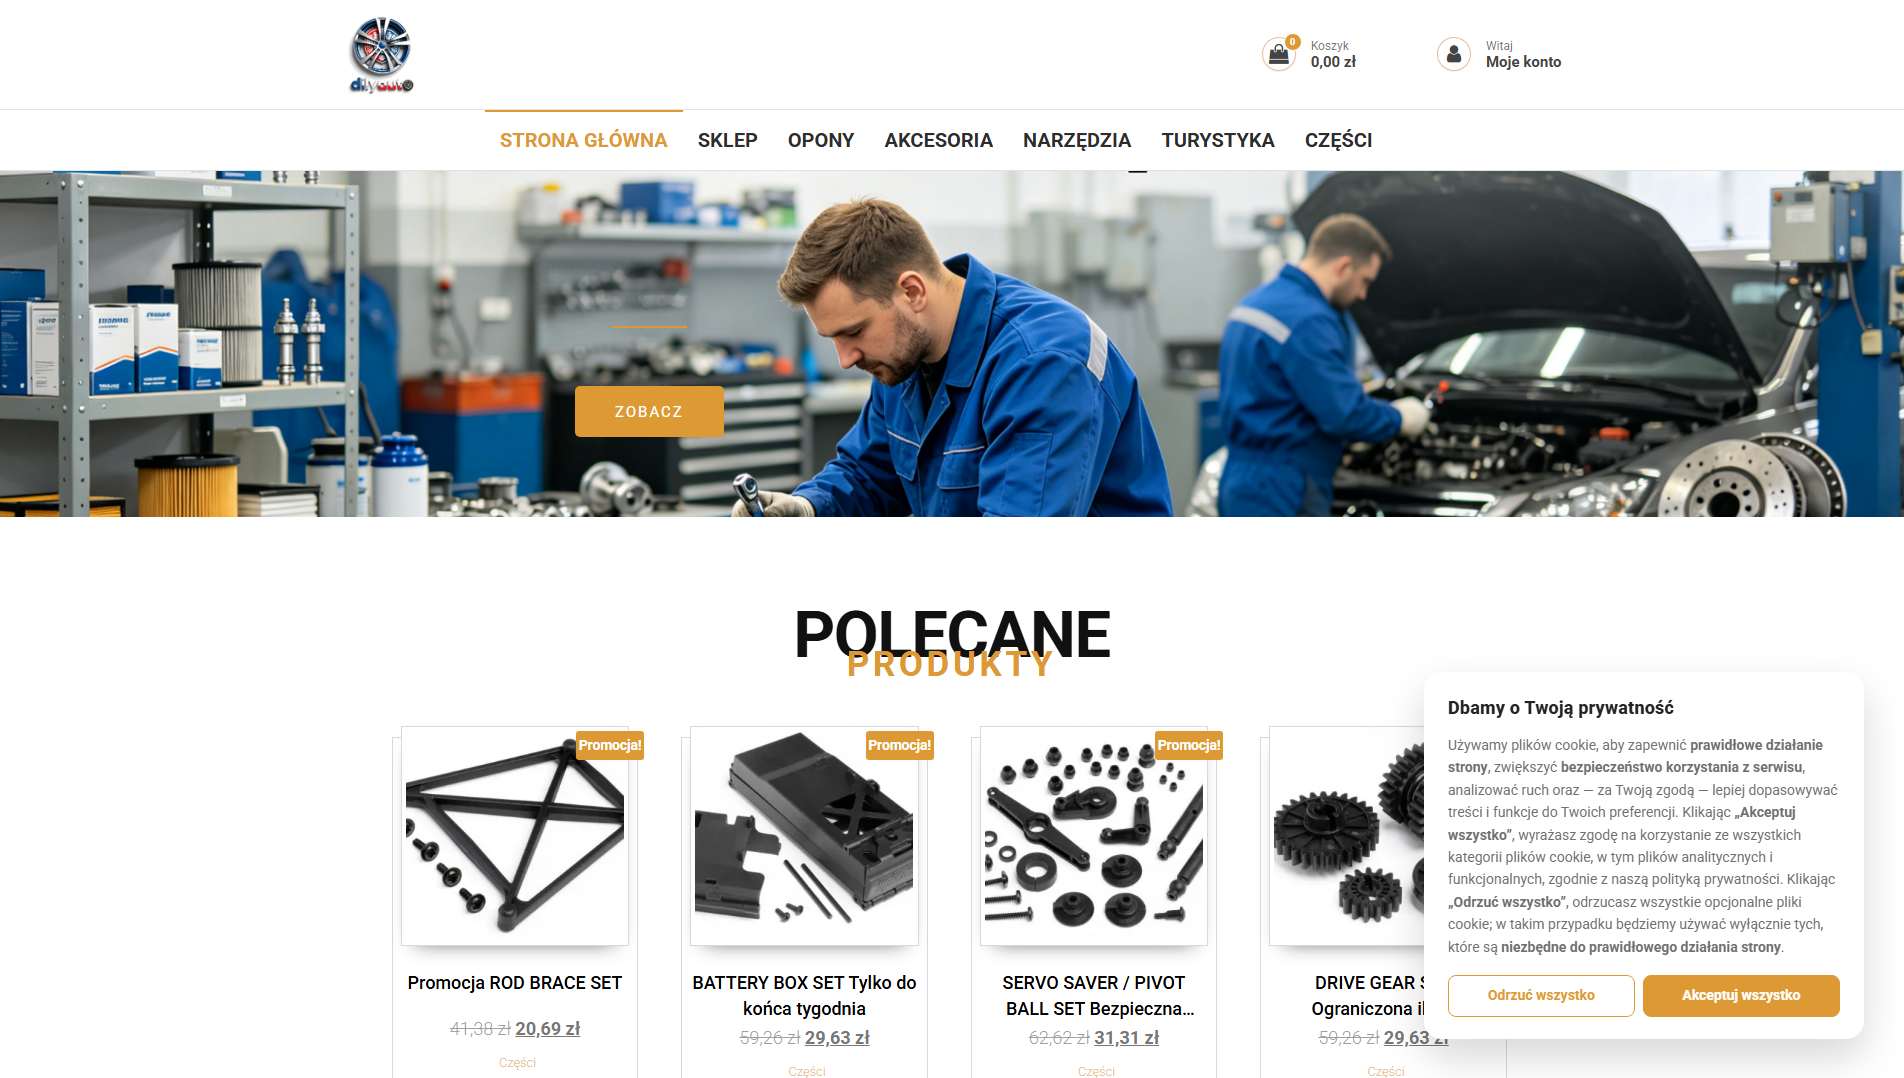
“Części auto – Akcesoria, narzędzia i części warsztatowe | dilyauto”
威胁判定
关键
99/100 证据评分
可用性
最后已知的活跃状态
最新存储的可达性观察
风险信号
病毒检测总数:13/89
品牌冒充:Unknown
最后已知的活跃状态
Actions
API
报告概览
dilyauto.com — 最后已知的活跃状态 (HTTP 301). 品牌冒充:Unknown. 证据摘要: VirusTotal 13/89 (alphaMountain.ai, BitDefender, CRDF, CyRadar, Forcepoint ThreatSeeker); URLScan capture; CF Radar malicious; PhishDestroy score 99/100. 注册商: Spaceship.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
证据摘要
重要
PhishDestroy first observed dilyauto.com on Sep 20, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Części auto – Akcesoria, narzędzia i części warsztatowe | dilyauto”. Current evidence score: 99/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and Cloudflare Radar. VirusTotal recorded 13 detections among 89 engines: alphaMountain.ai, BitDefender, CRDF, CyRadar, Forcepoint ThreatSeeker, G-Data, Gridinsoft, Kaspersky, LevelBlue, Lionic, SOCRadar, Sophos, VIPRE on Sep 20, 2026 at 14:29 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories security threats and malware; its verdict timestamp was not retained. Non-positive and contextual checks: AlienVault OTX listed 4 community pulse references (not vendor detections) on Sep 20, 2026 at 14:30 UTC. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 14:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 14:29 UTC. URLScan captured the page on Sep 20, 2026 at 04:27 UTC.
HTTP 301 was recorded on Sep 20, 2026 at 11:04 UTC. Registration records for the domain list Spaceship, Inc. as the registrar and Apr 27, 2026 as the creation date. At collection time, the hostname resolved to 188.114.96.3 on AS13335 (Cloudflare, Inc.). The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. DOM analysis on Sep 20, 2026 at 06:20 UTC returned 98/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YE2 as the certificate issuer with validity through Nov 21, 2026; checked Sep 20, 2026 at 07:02 UTC.
The content indicators and 2 positive source findings support the current Unknown impersonation and phishing classification. The target field identifies Unknown, but the record does not establish whether the page requested credentials, a seed phrase, or a wallet connection.
VirusTotal
13 det.
OTX references
CF雷达
恶意
URLScan
TLS 证书
Let's Encrypt / YE2
年龄
5 mo
观测状态
最后已知的活跃状态 301

DestroyList
已列入
数据覆盖范围
VirusTotal
13 / 89
OTX
4 community references
CF雷达
provider verdict: malicious
URLScan capture
存储的报告
TLS
valid certificate, 61d
WHOIS
5 mo old
屏幕截图
3 captures · 2 sources
网络安全情报
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Sep 20, 2026 · 12:21 UTCVirusTotal scanner detections updated from 12 to 13. Added scanner alerts: CyRadar.
-
VirusTotal Detections Update Sep 20, 2026 · 08:30 UTCVirusTotal scanner detections updated from 9 to 12. Added scanner alerts: Forcepoint ThreatSeeker, LevelBlue, Lionic.
-
Threat First Observed Sep 20, 2026 · 06:26 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
188.114.96.3.
威胁响应 Pipeline
发现
Checks
Reports
可用性
13/15
公共封禁名单状态
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
cloudflare
Scanner note: redirect: raw=redirect_301; http=301; via=https_proxy; location=https://www.dilyauto.com/; server=cloudflare
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
已保存的截图 · 3 sources
域名情报
域名
服务器 / ASN
cloudflare · AS13335 Cloudflare, Inc.
IP Context
Cloudflare shared edge
origin IP hidden
Edge-IP 声誉不属于此域。
OTX Tags
2026-09activeall-domainsblocklistcontentcrypto域名drainerfraudlivemonthlyphishdestroyphishingscam
注册商
Spaceship
 (US)
(US)
IP 地址
188.114.96.3
CDN
地理位置 Toronto, CA
网络AS13335 · CloudFlare, Inc.
源 IP 隐藏在 CDN 代理后面。边缘地址的反向 IP 结果包含不相关的租户;查找源头需要被动 DNS 或证书透明数据。
注册信息创建 2026年4月27日 (146d) — Expires 2027年4月27日
HTTP 状态码301 Moved Permanently
技术详情DNS、SSL SAN、时间戳
首次发现2026年9月20日
DOM Analysis
Submitted URLhttp://www.dilyauto.com/
域名服务器lorna.ns.cloudflare.comvick.ns.cloudflare.com
TLS Fingerprint
TLS Observation
Favicon Hash
技术 · 13 identified
WordPress
CMS
Blogs
MySQL
Databases
PHP
Programming languages
Bootstrap
UI frameworks
Yoast SEO
SEO
WordPress plugins
Nginx
Web servers
Reverse proxies
jQuery Migrate
JavaScript libraries
jQuery
JavaScript libraries
HSTS
安全
CookieYes
Cookie compliance
Cloudflare Browser Insights
Analytics
RUM
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
举报此域名
提交证据,帮助保护他人
VirusTotal 分析
13 / 89 安全供应商标记了该域
View on VT
Last analyzed Previous stored snapshot: 13 detections
alphaMountain.ai
BitDefender
CRDF
CyRadar
Forcepoint ThreatSeeker
G-Data
Gridinsoft
卡巴斯基
LevelBlue
Lionic
SOCRadar
Sophos
VIPRE
网站性能分析
Google PageSpeed Insights — mobile performance audit of dilyauto.com · checked Sep 20, 2026
57
Needs Work
Performance
FCP
3.67s
First Contentful Paint
LCP
28.76s
Largest Contentful Paint
CLS
0.041
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
10.73s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
证据与外部报告
证券分析
OSINT与情报分析
DNS 与网络
SEO 与域名
您是否受到本网站的影响?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。


PhishDestroy listing review 不是执法报告
域名申诉
如果您拥有该域名并认为该列表不正确,请请求审核
警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关康复欺诈的更多信息 →
相关基础设施与报告
Infrastructure map · dilyauto.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
关于共享 Cloudflare 边缘的其他报告 6
这些报告解析为相同的共享边缘 IP。它们有助于报告发现,但并不意味着共同所有权或共享源服务器。
同一注册商: Spaceship 6
 money-x.ceo
Unknown impersonation 8
These domains also target 未知 users. View all Unknown threats →
最近的威胁报告 6
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。