
搜索受监控的域名,并查看存储的证据、检测结果以及最新观察到的可用性情况。
How This Attack Works
Ice Phishing is a sophisticated technique that targets users by manipulating blockchain transactions. Here's how it typically unfolds.
STEP 1
Target Identification
Attackers identify potential victims, often targeting users with significant cryptocurrency holdings.
STEP 2
Setup Spoofed Environment
The attacker creates a fake website or app mimicking a legitimate service to deceive users.
STEP 3
Credential Harvesting
Users are tricked into entering sensitive information, allowing attackers to gain access to their accounts.
STEP 4
Unauthorized Transactions
With access to the victim's account, attackers execute unauthorized transactions, siphoning funds.
Technical Analysis
Ice Phishing attacks often involve the use of malicious smart contracts that exploit users by redirecting transactions to the attacker's wallet. Attackers employ social engineering techniques to lure victims into signing transactions that they believe are legitimate. These transactions often use clever code obfuscation to hide the true nature of the transaction. Attackers also leverage compromised infrastructure, such as DNS servers or hosting services like those registered through arin or Vercel Inc., to create convincing phishing environments. By mimicking legitimate services, these attacks bypass traditional security checks, making detection challenging.
Real Cases
Ethereum Wallet Scam (2023)
$1.2 million stolen
Attackers used a fake wallet service to steal credentials, resulting in a substantial loss of Ethereum funds.
Crypto Exchange Phishing (2024)
$2.5 million stolen
A phishing site mimicking a popular exchange tricked users into entering their login details, leading to significant asset theft.
DeFi 平台 Breach (2024)
$3.8 million stolen
A decentralized finance platform was targeted by ice phishers who exploited smart contract vulnerabilities to siphon funds.
How to Detect
Unusual domain names that closely resemble legitimate services
Unexpected requests for private keys or seed phrases
Emails or messages urging immediate action on your crypto assets
Anomalies in transaction requests, such as unexpected gas fees
Lack of HTTPS encryption on websites requiring sensitive input
How to Protect Yourself
1
Always verify the URL before entering sensitive information
2
Enable two-factor authentication on all accounts
3
Regularly monitor transaction logs for unauthorized activities
4
Educate yourself about common phishing tactics
5
Use hardware wallets for enhanced security
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 40 domains tracked for this threat type
Ice Phishing 40 domains
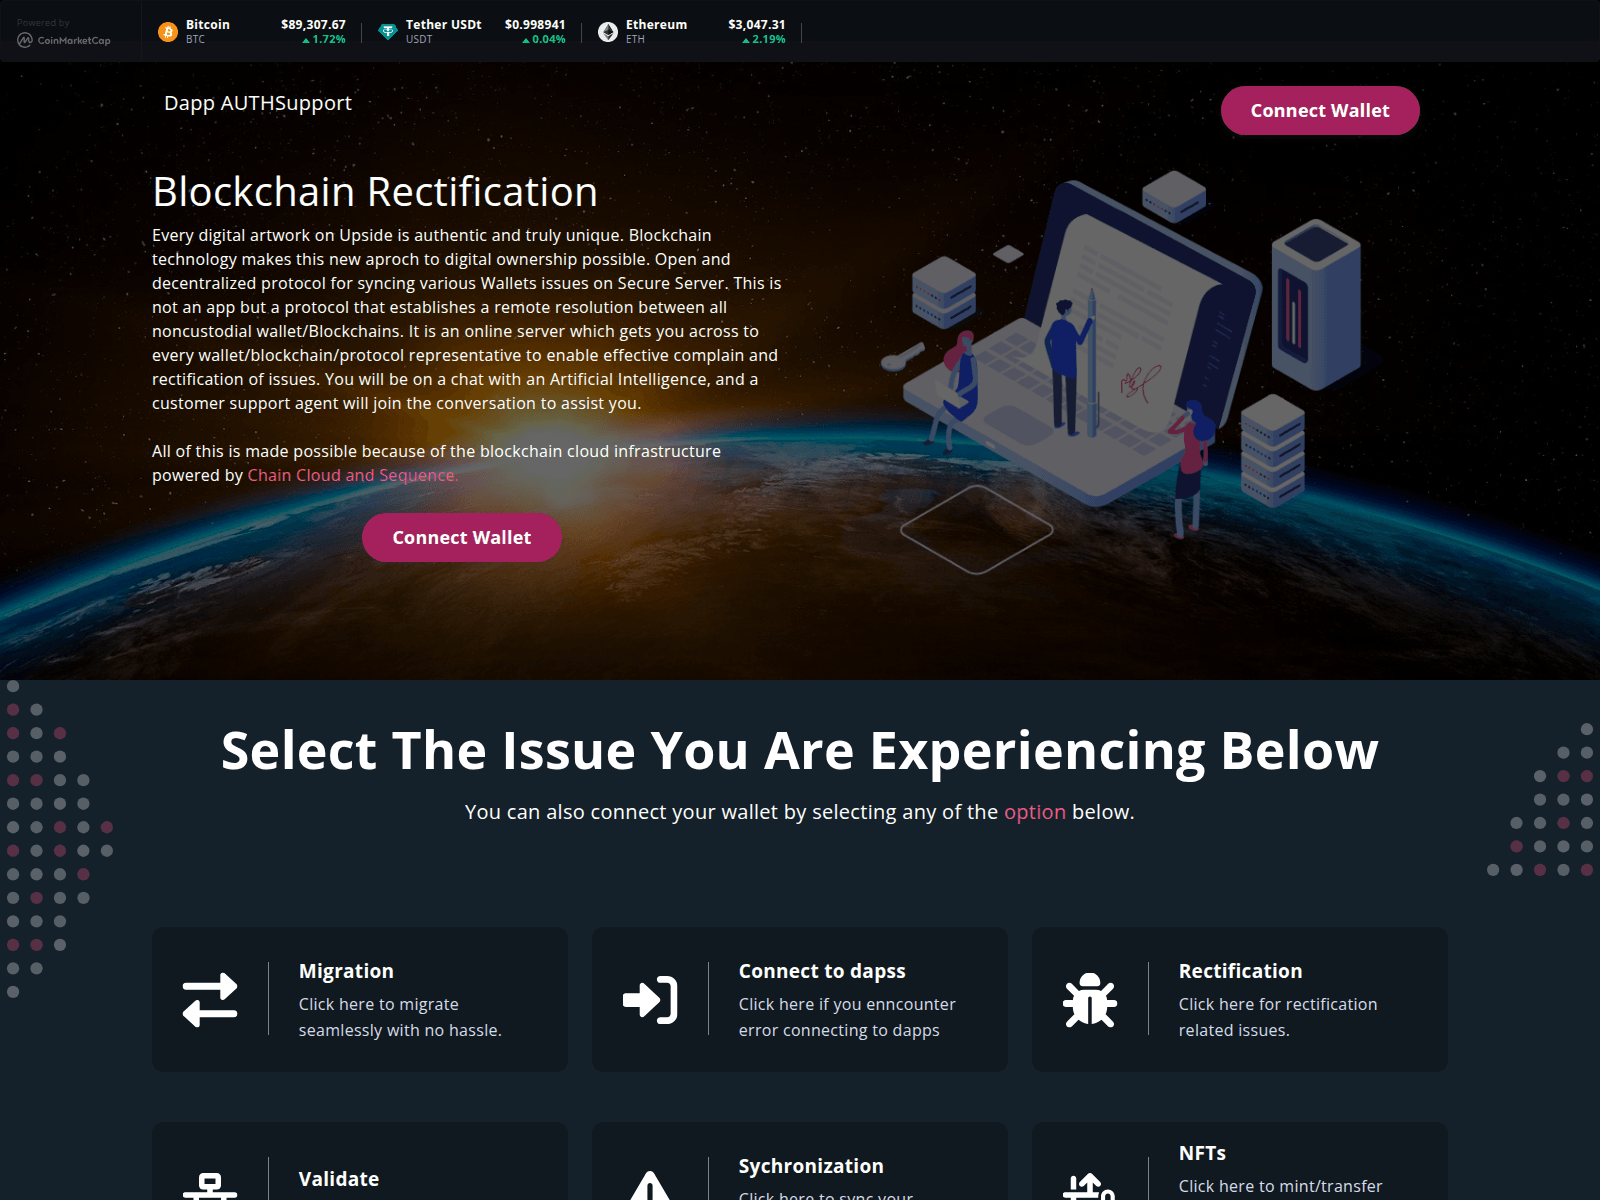
rectification-fixuserauthentication.vercel.app
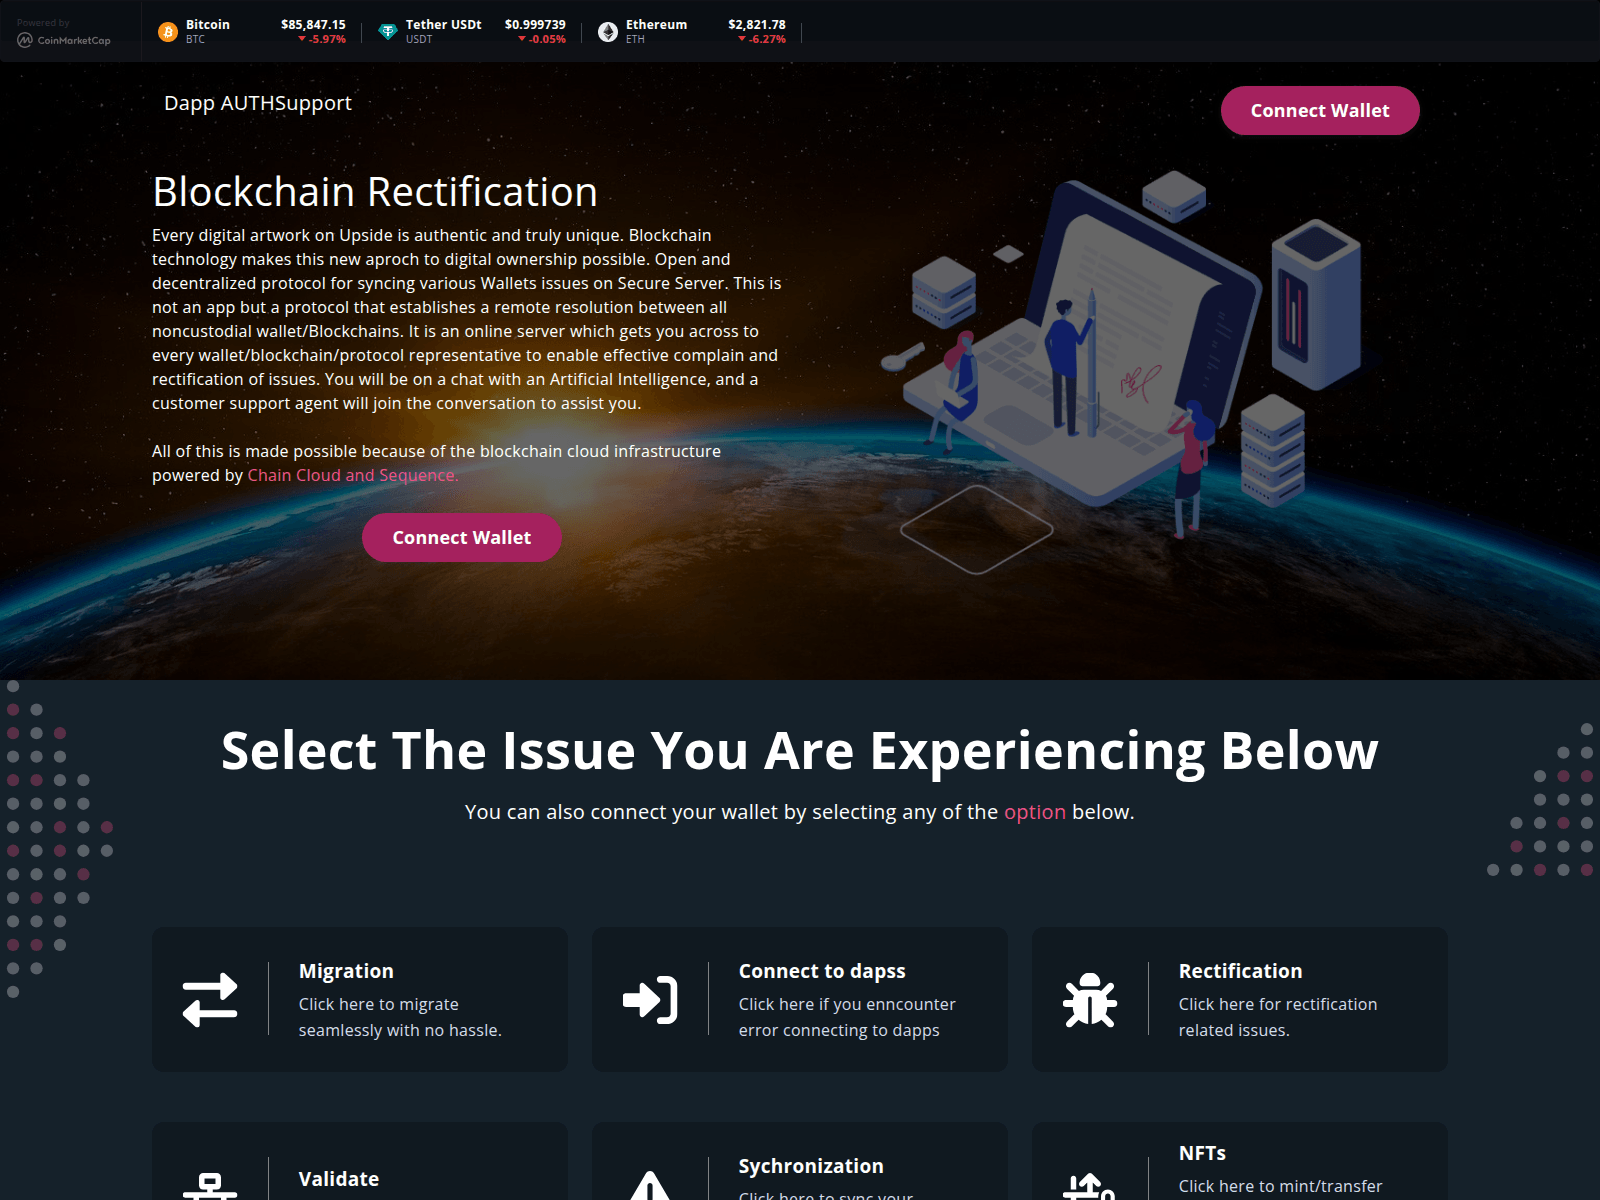
rectifyissues-now.vercel.app
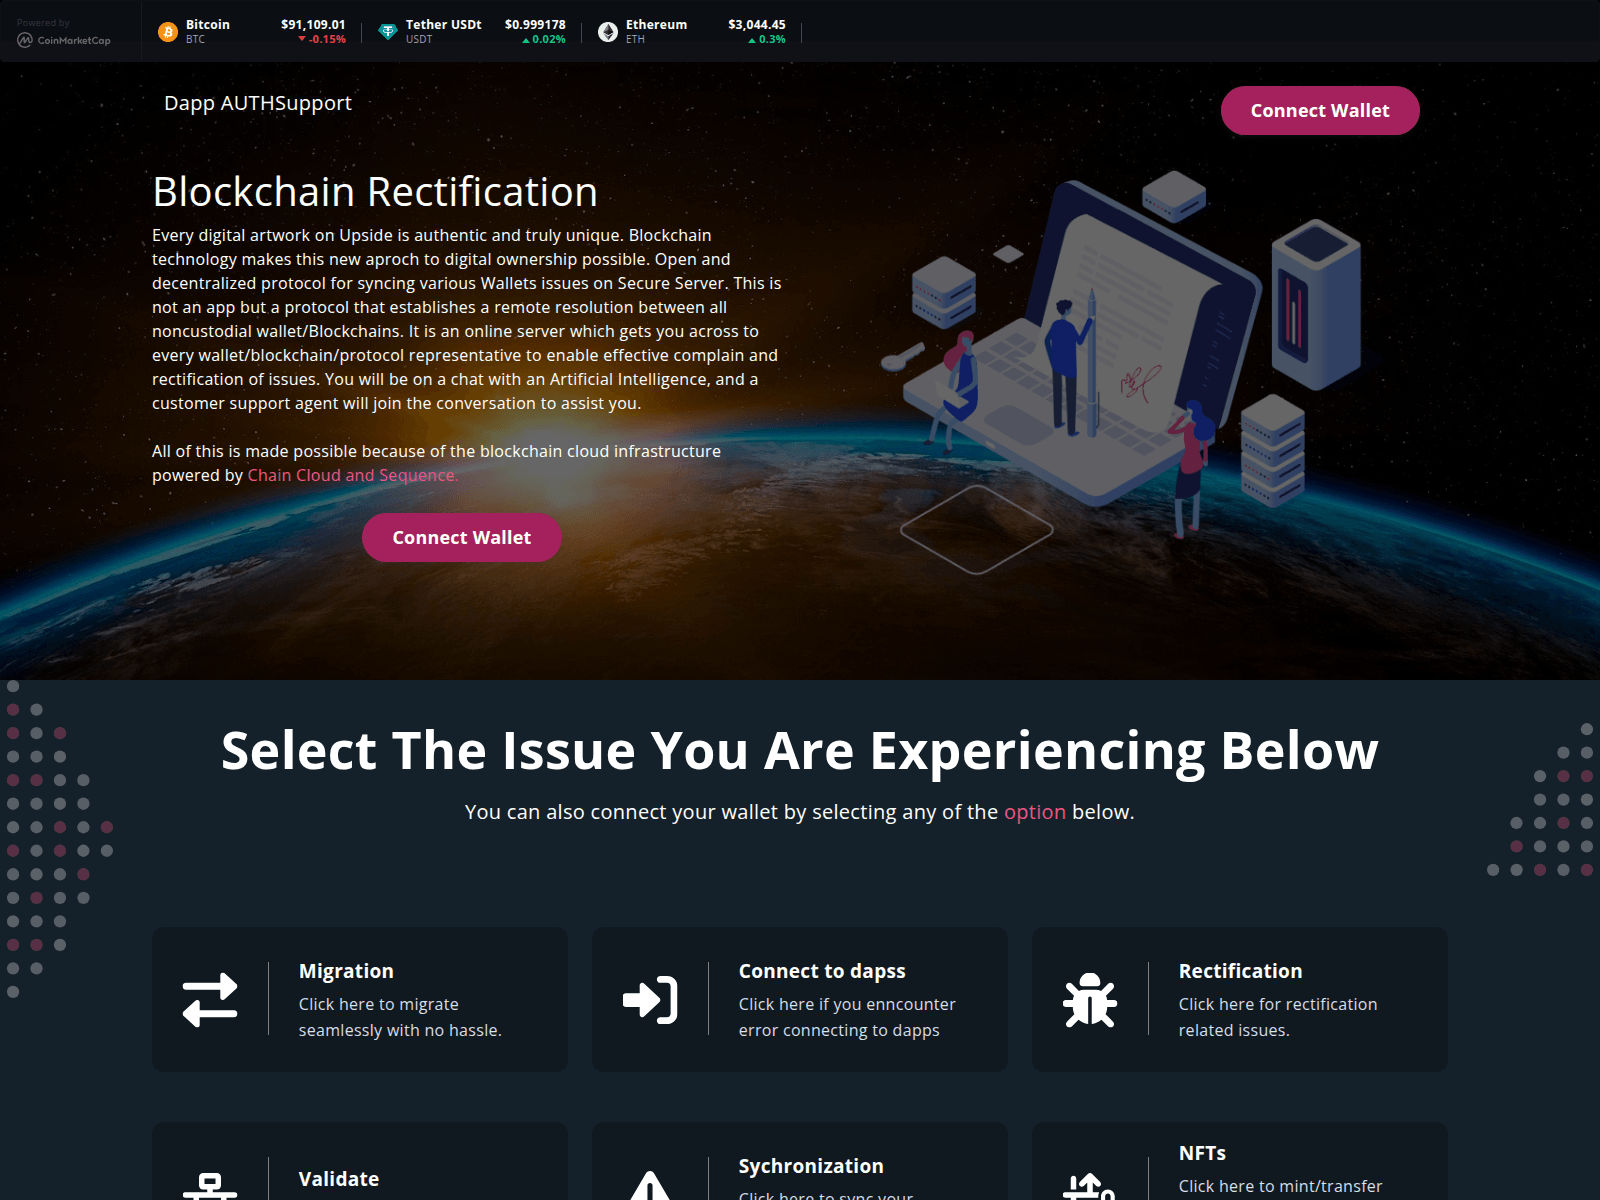
supports-rectification.vercel.app
authwalletconnect.com
flaretokensdrop.com
seaportal.fo
agencyanalyticsframe.us.com
enacoin-newbridge.com
flrconnectportal.live
airdrop.wrlomhole.net
aoerodrome.finance
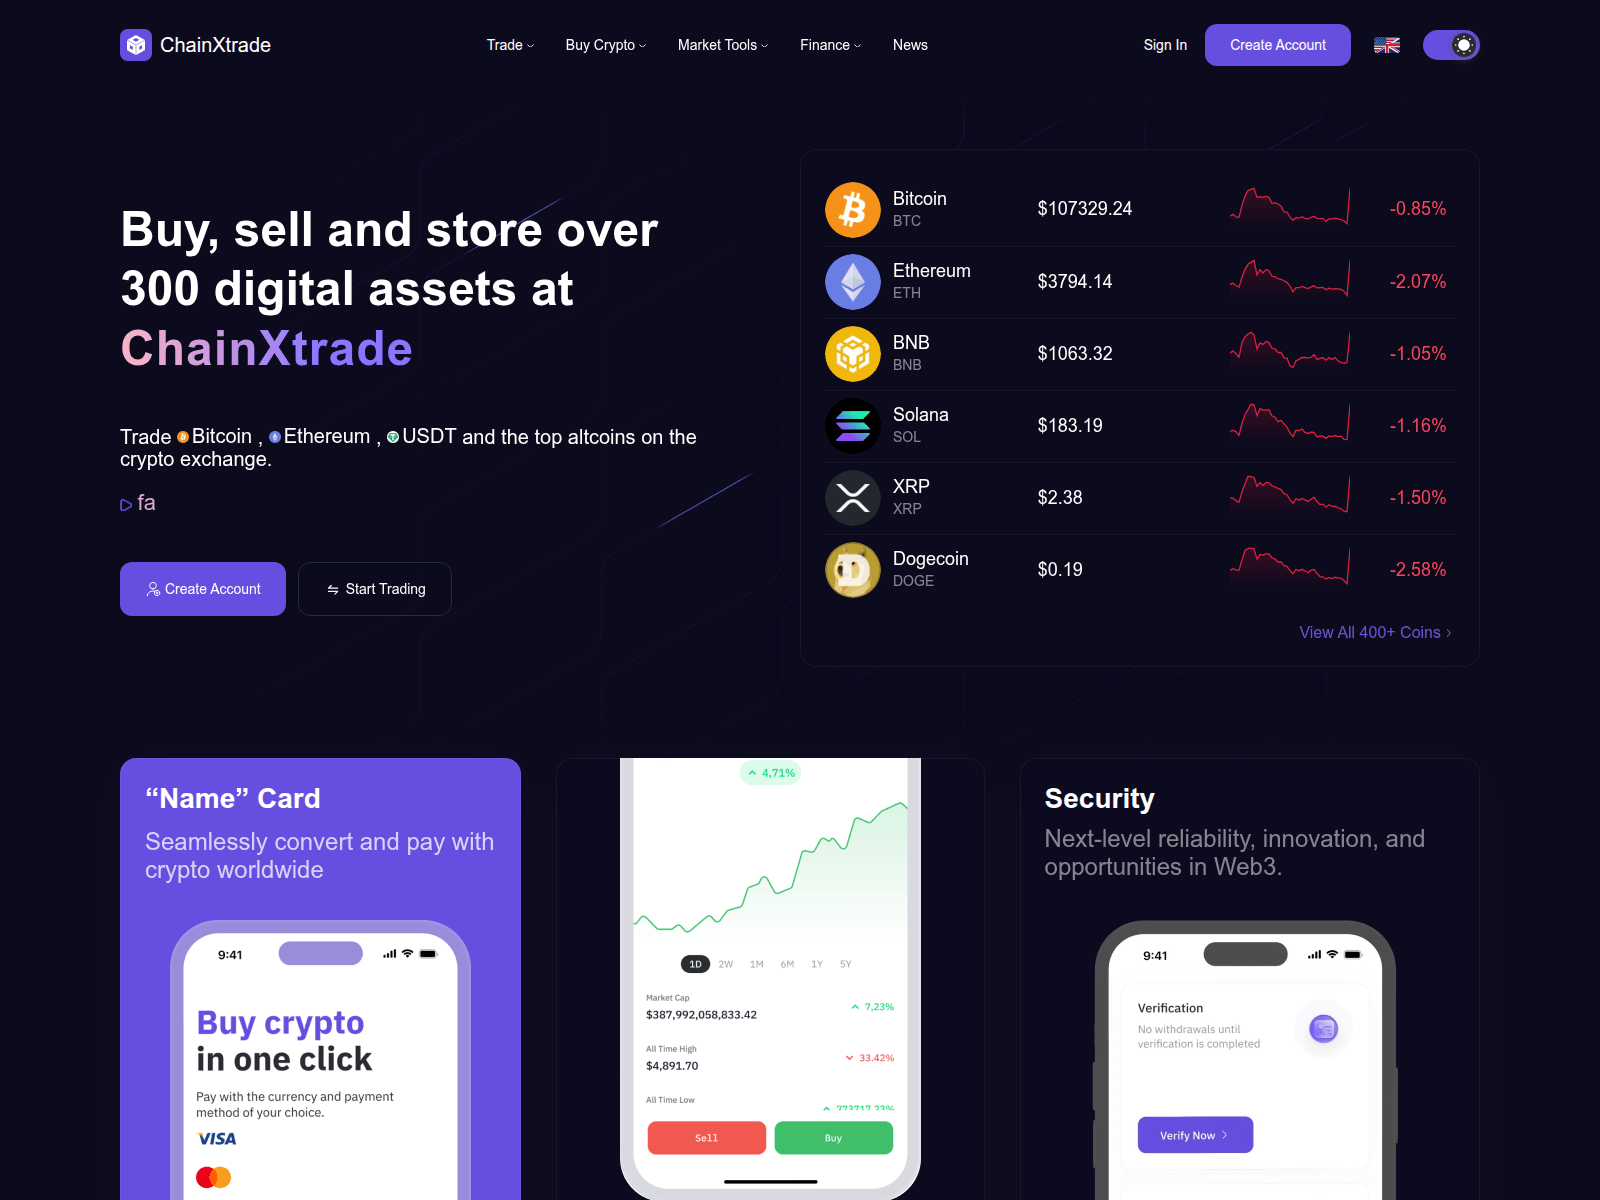
chainxtrade.com
ethdrawclaimdrop.org
test123.sphere-drainer.cc
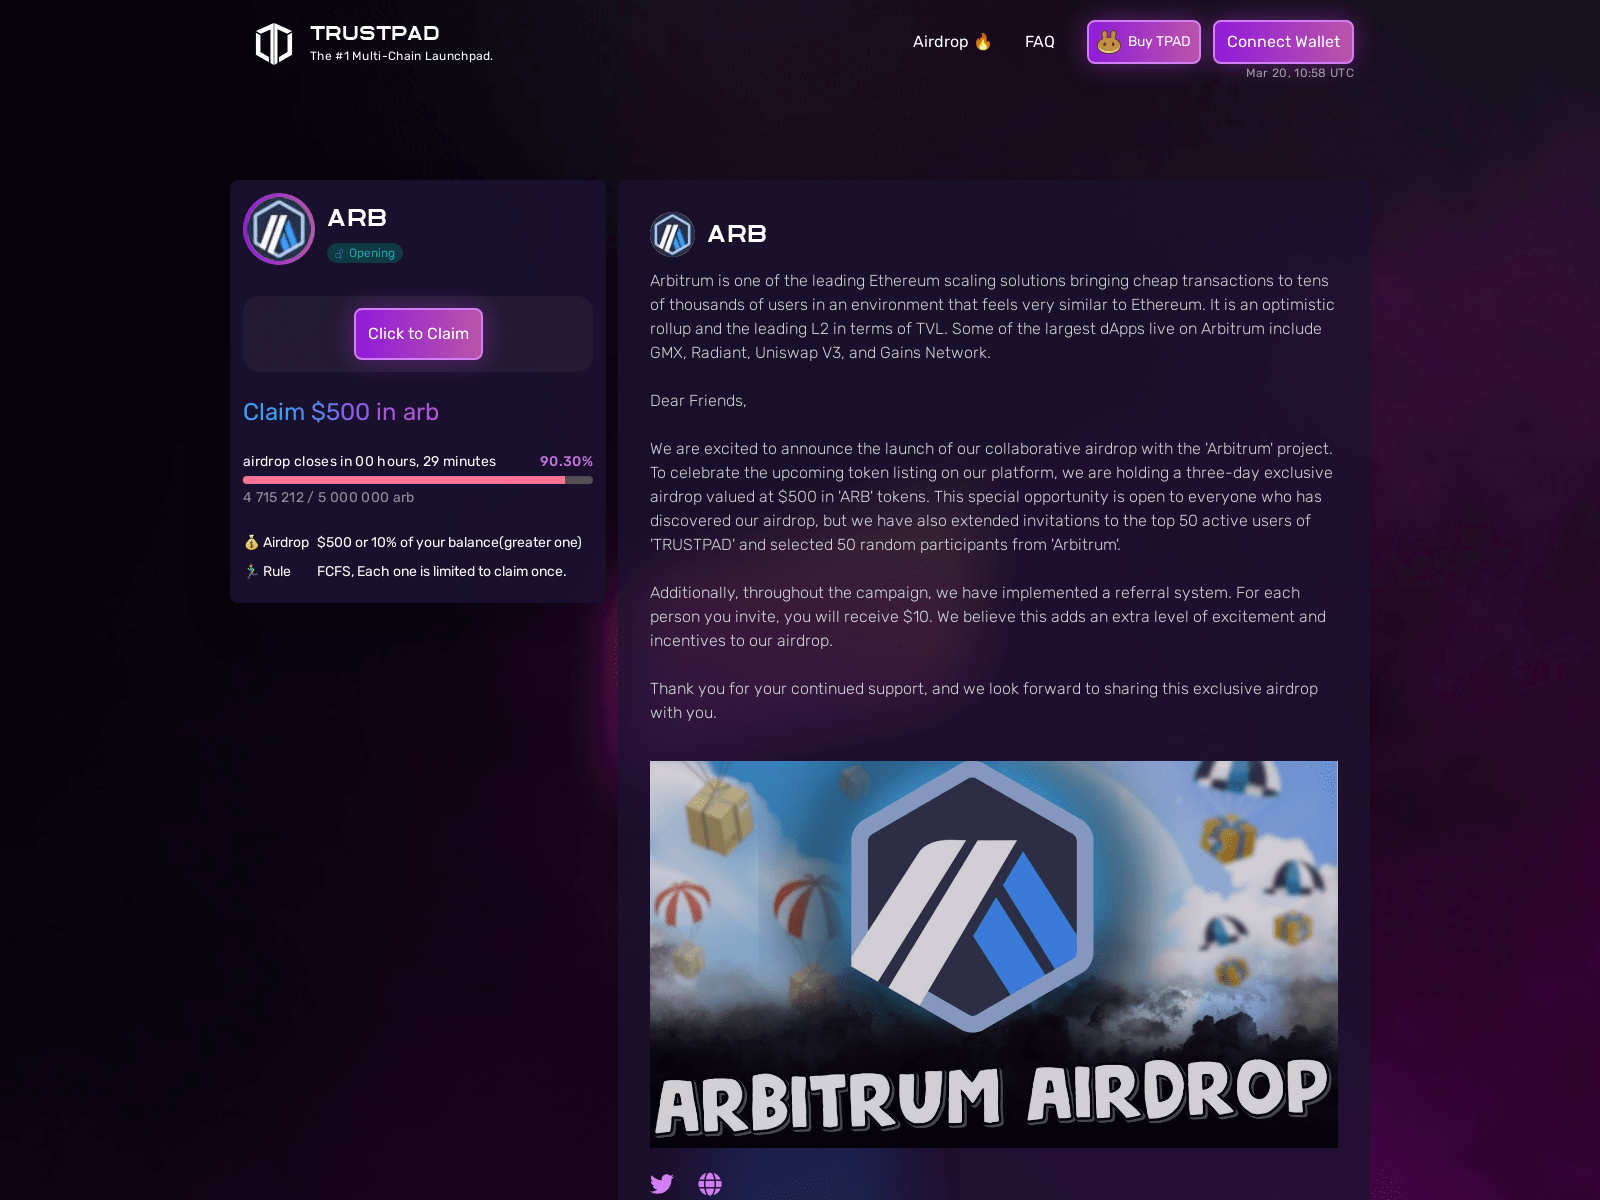
arb.claimscrypto.top
eth-drainer.exontra.com
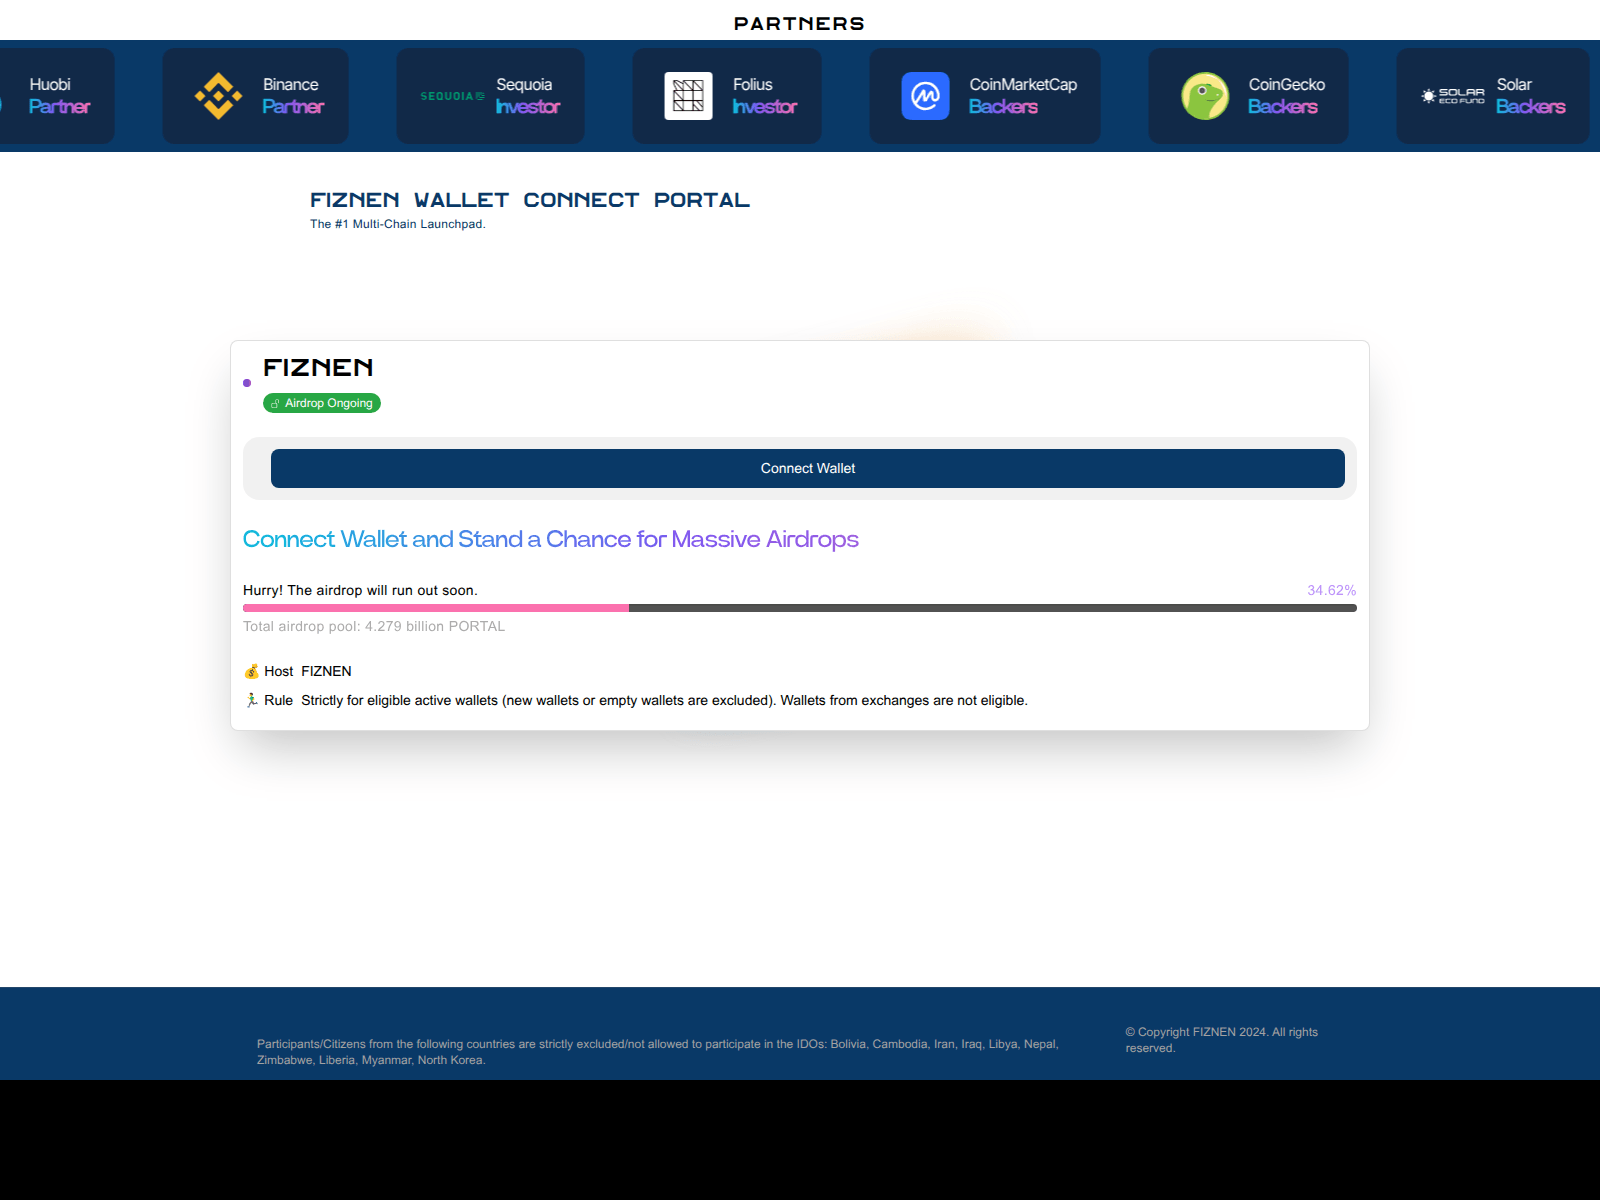
drnr.fiznen.com
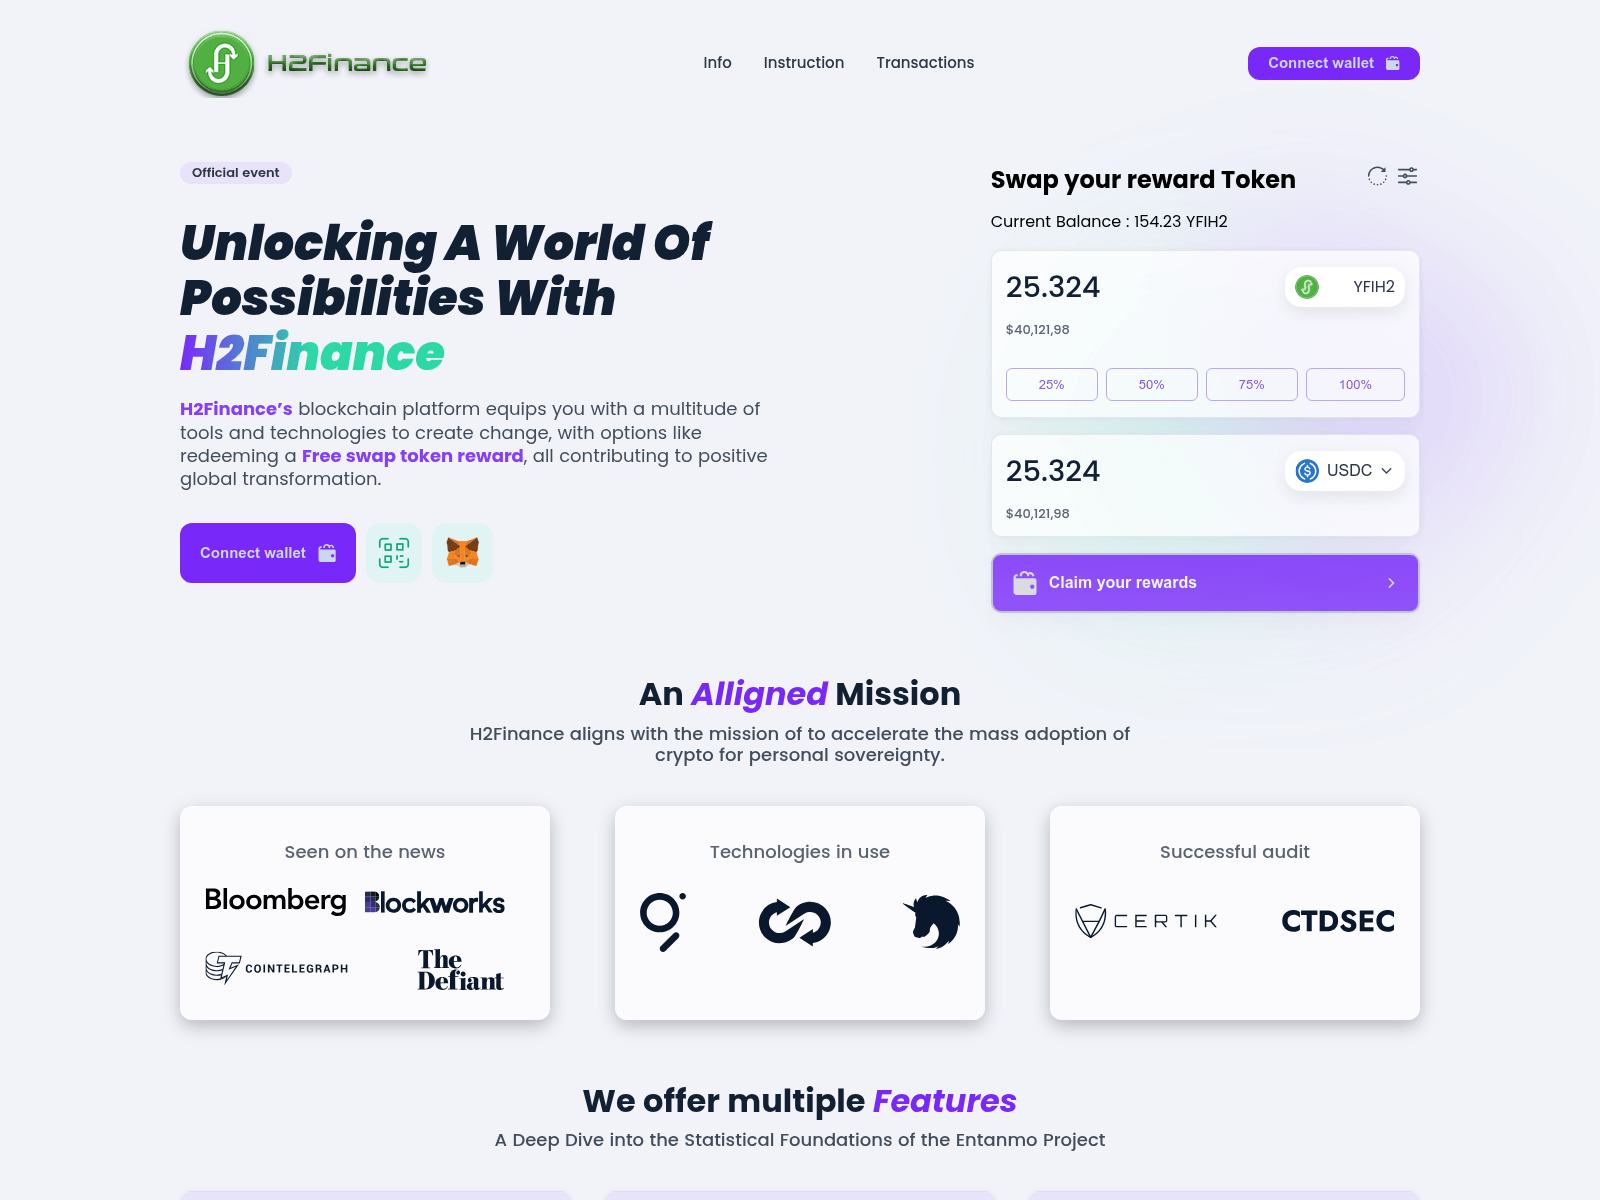
h2-finance.web.app
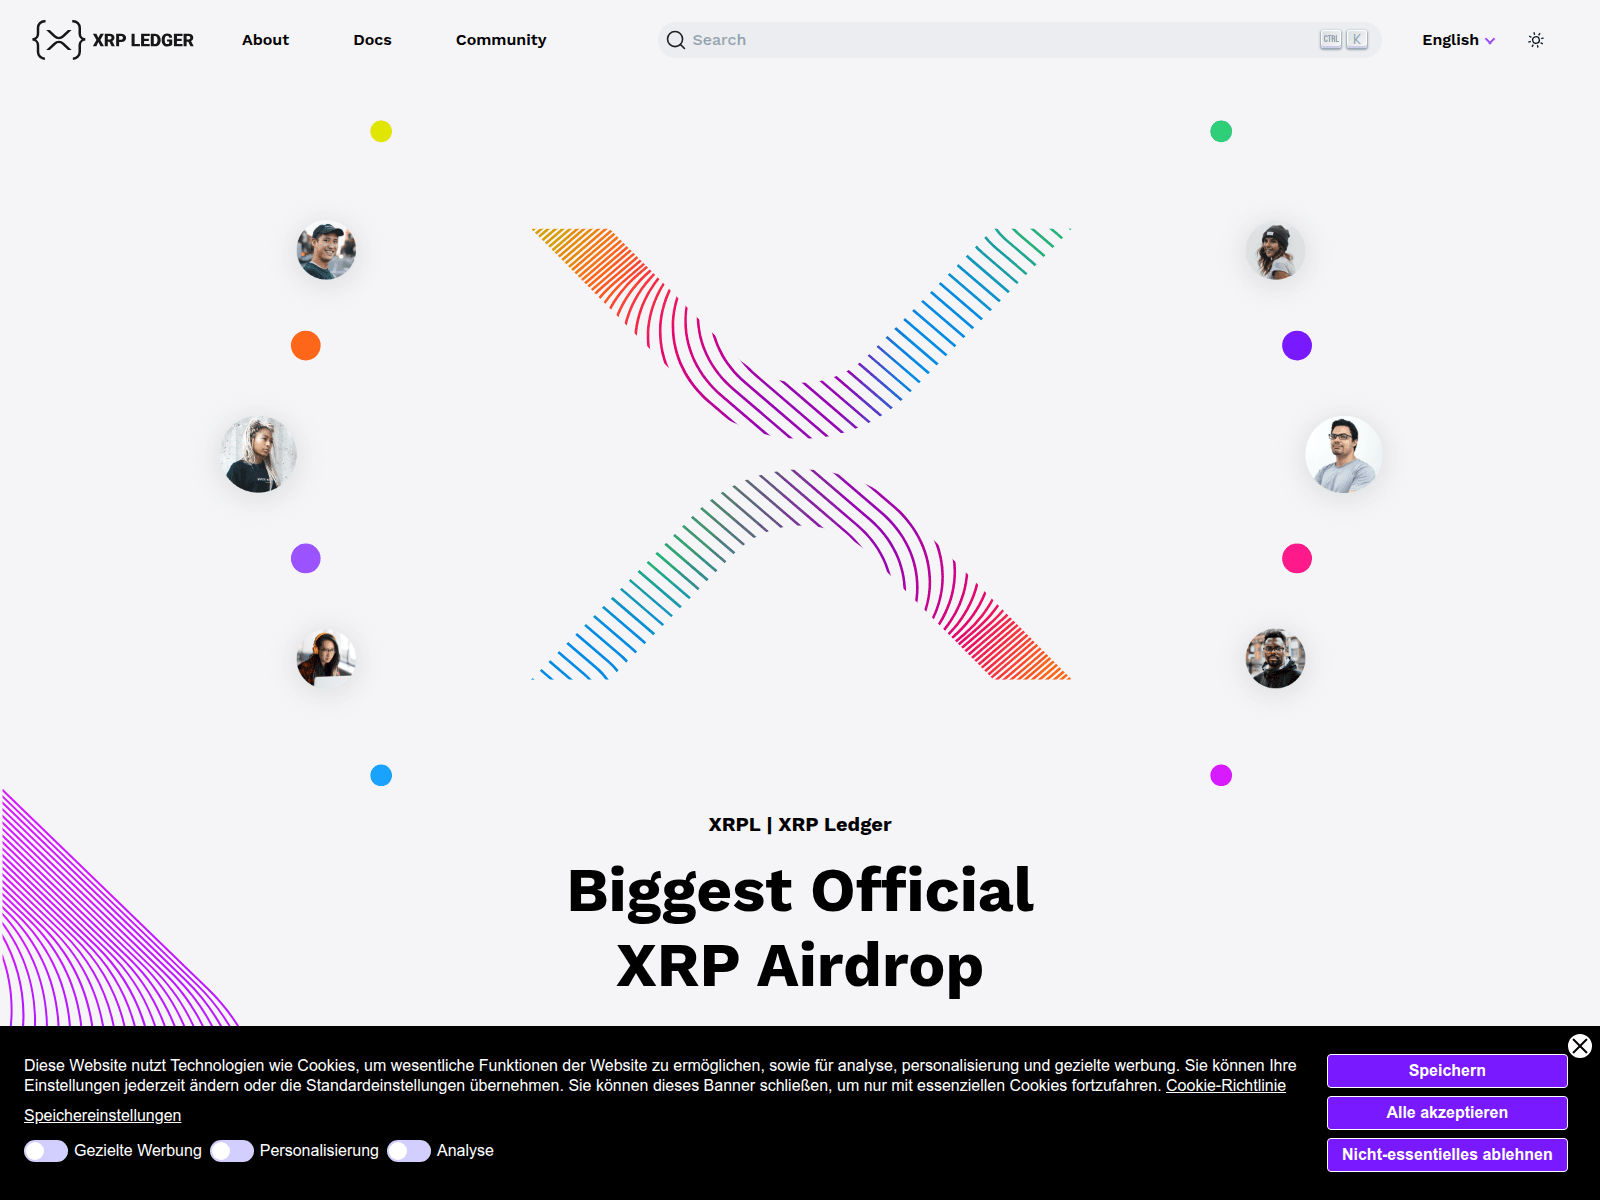
xrpdistributions.firebaseapp.com
ngcrp.com
drainer.bexcapitaltrade.com
flare.linkportalnet.com
trovako.com
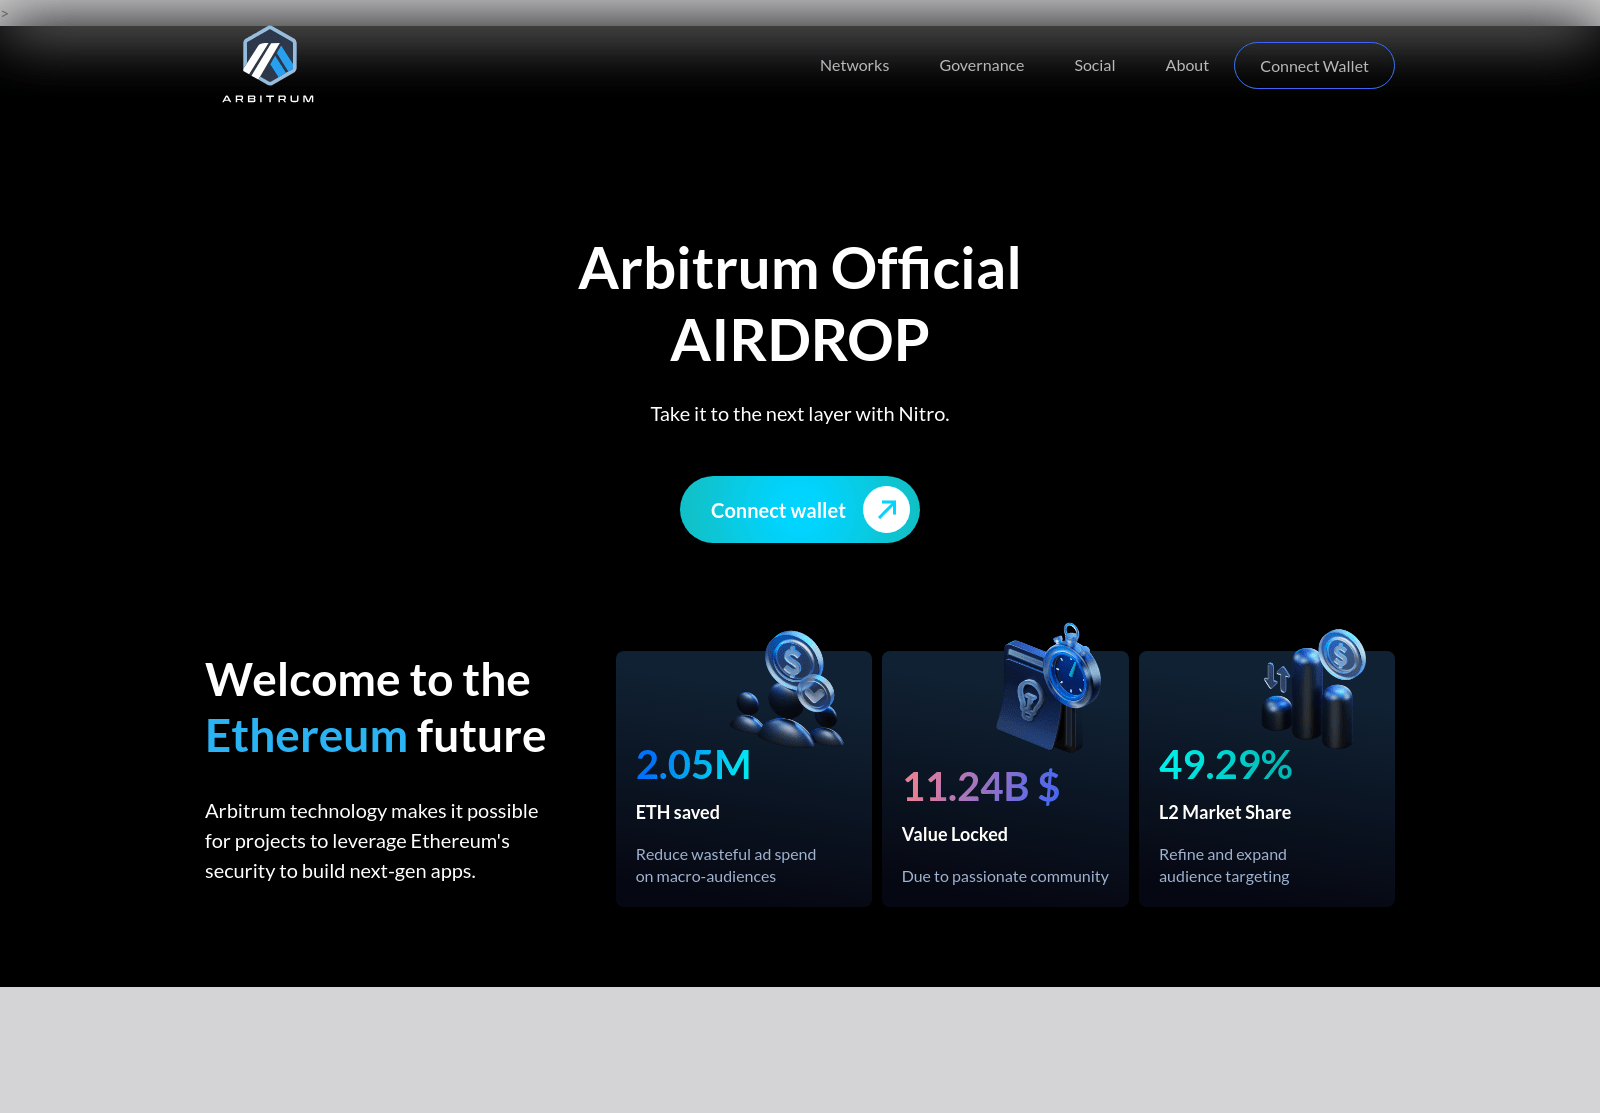
arbitriums.icu
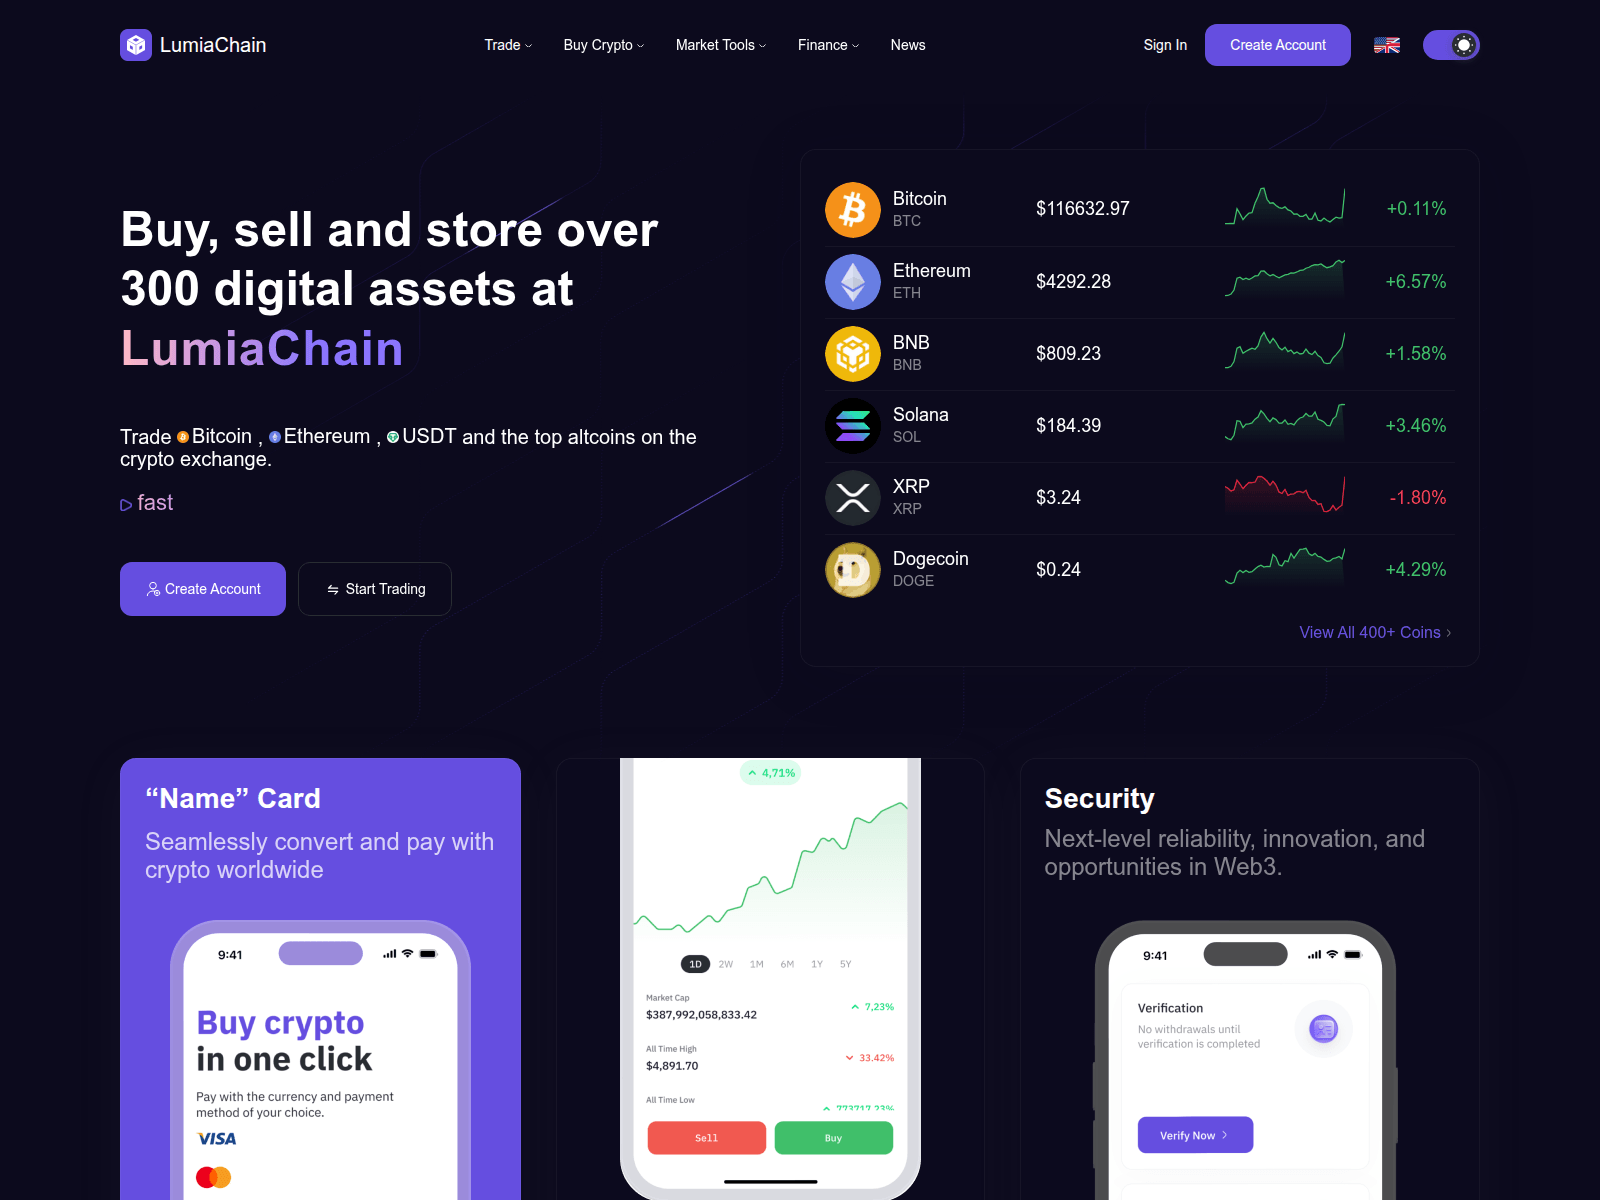
lumiachain.com

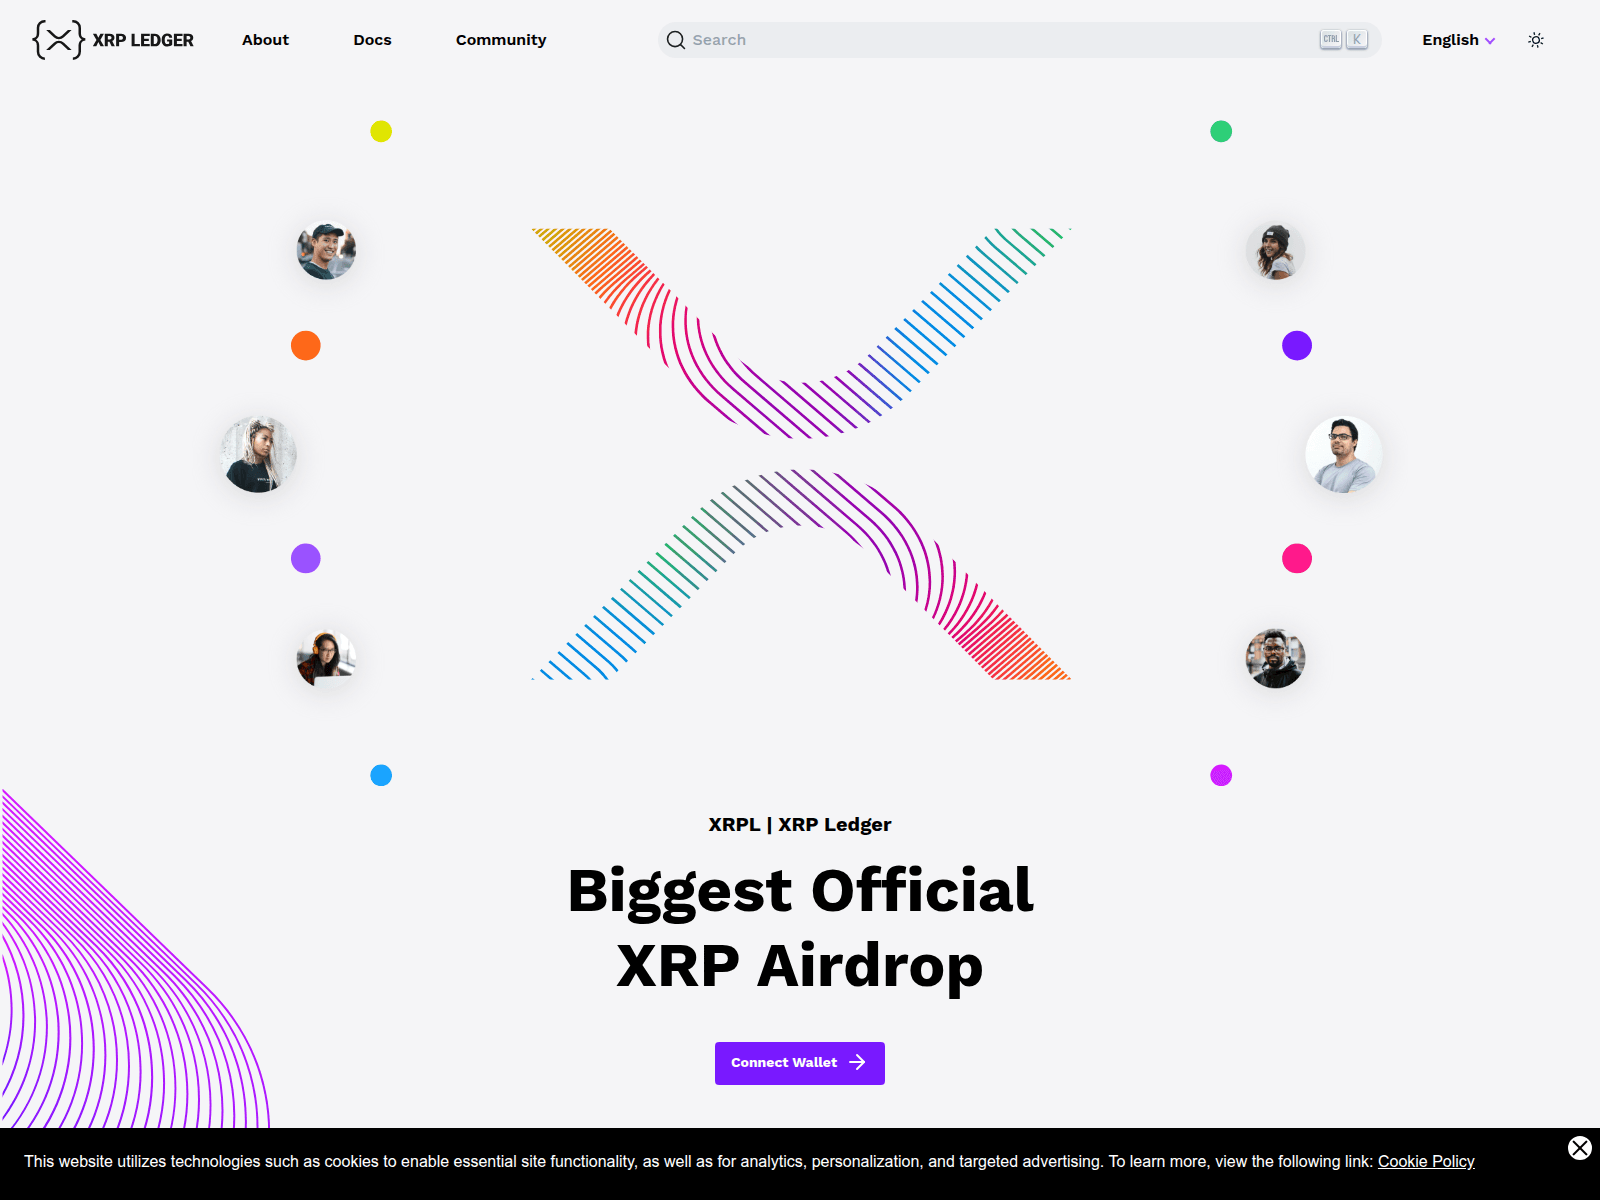
xrpdistributions.web.app
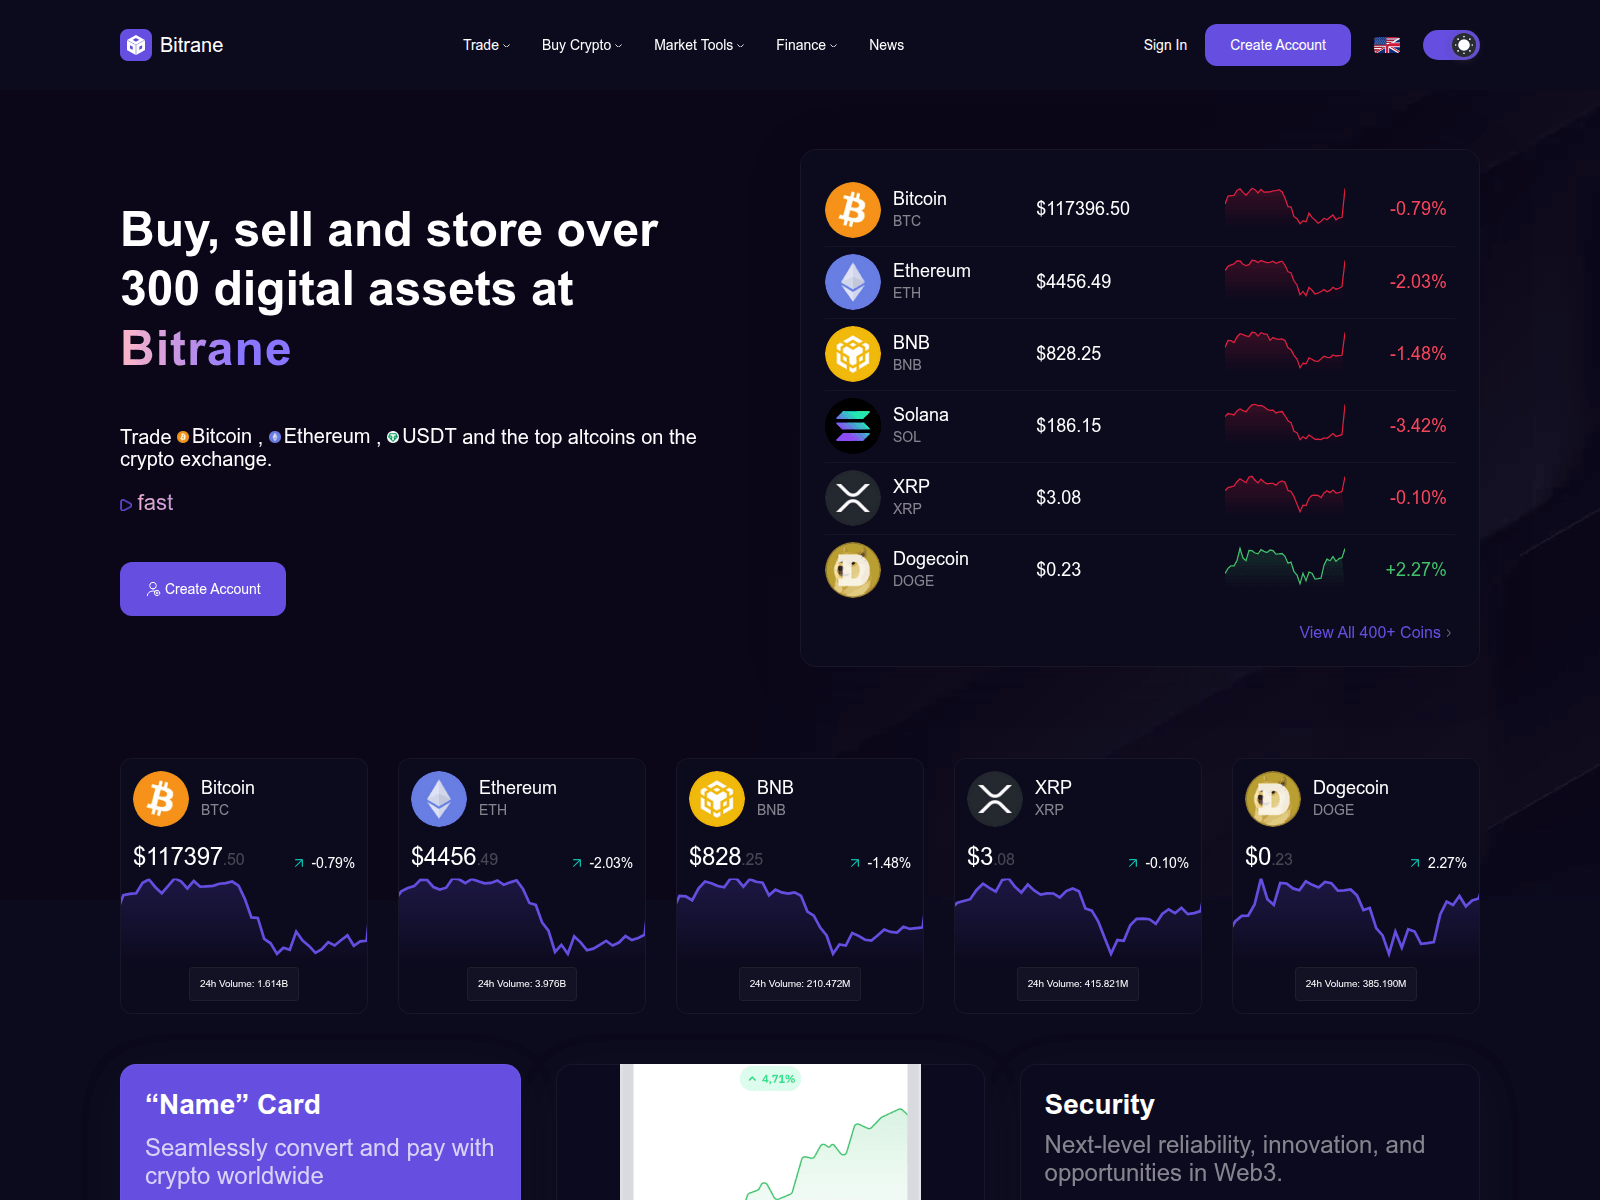
bitrane.com
duplicate-disabled-13104.invalid
ledgerlane.icu
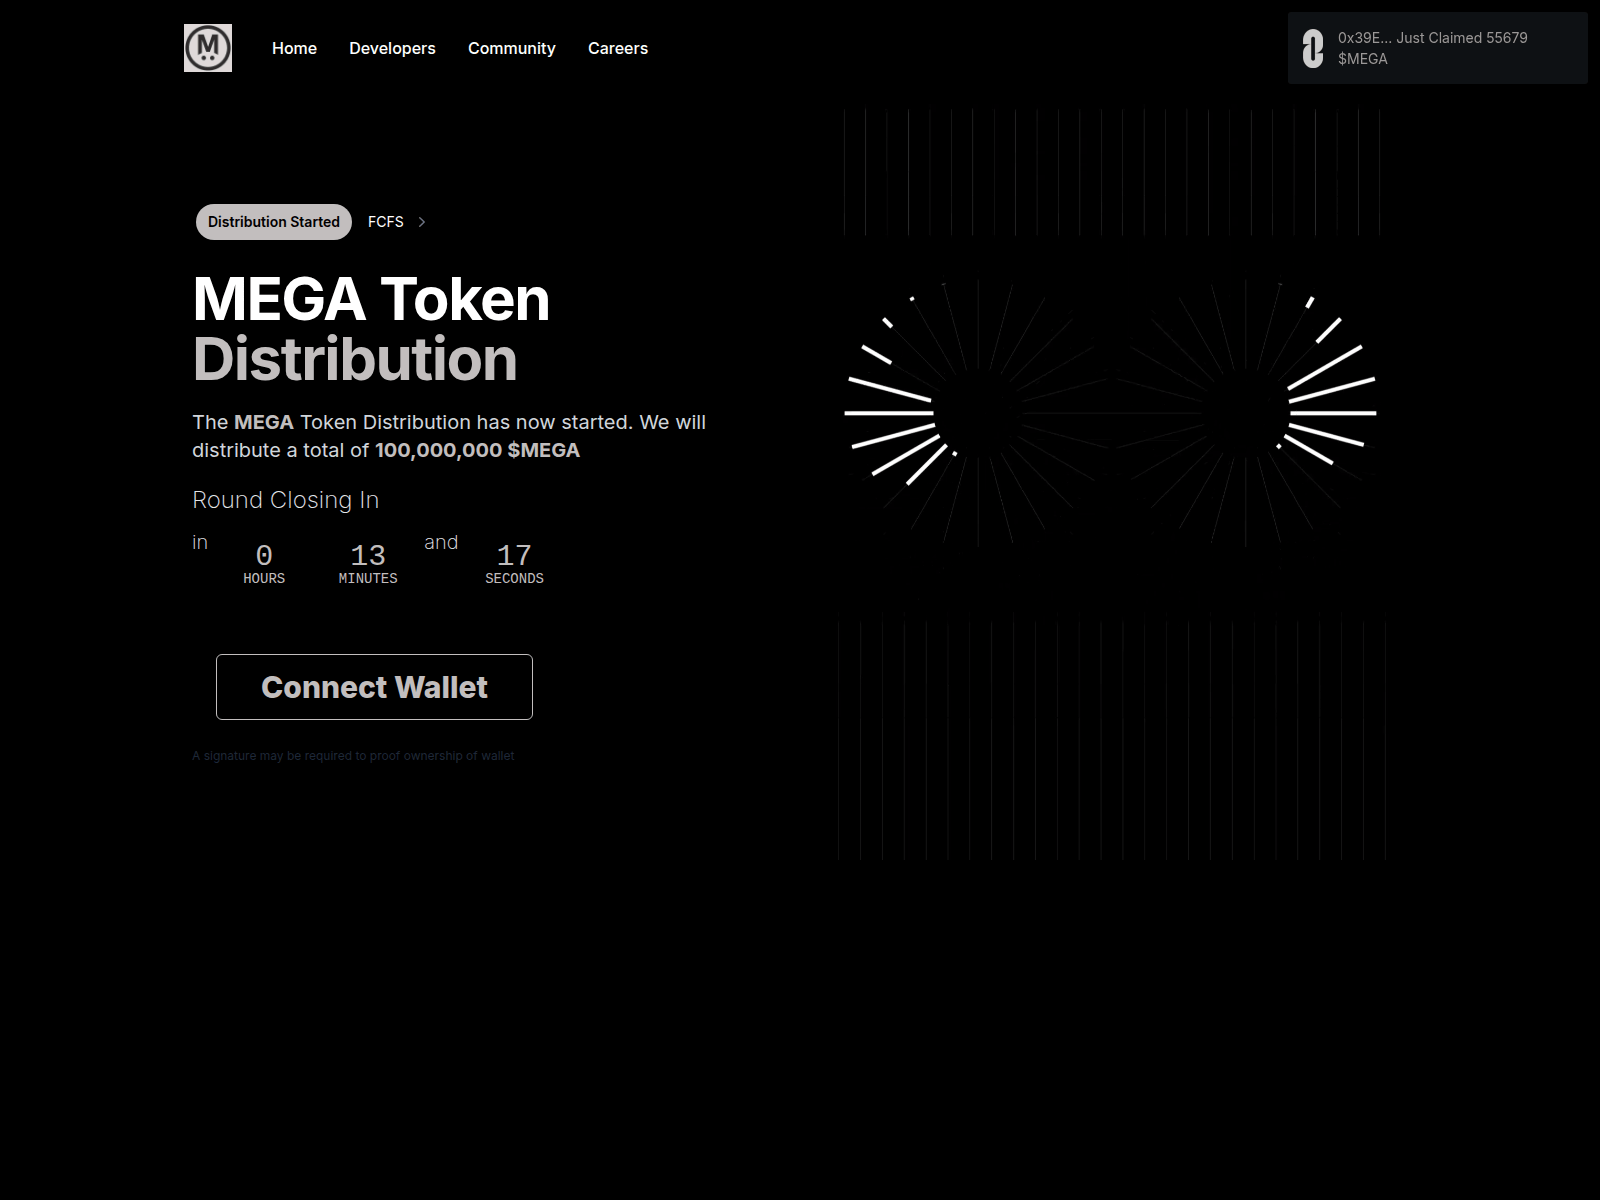
megaethlabs.top
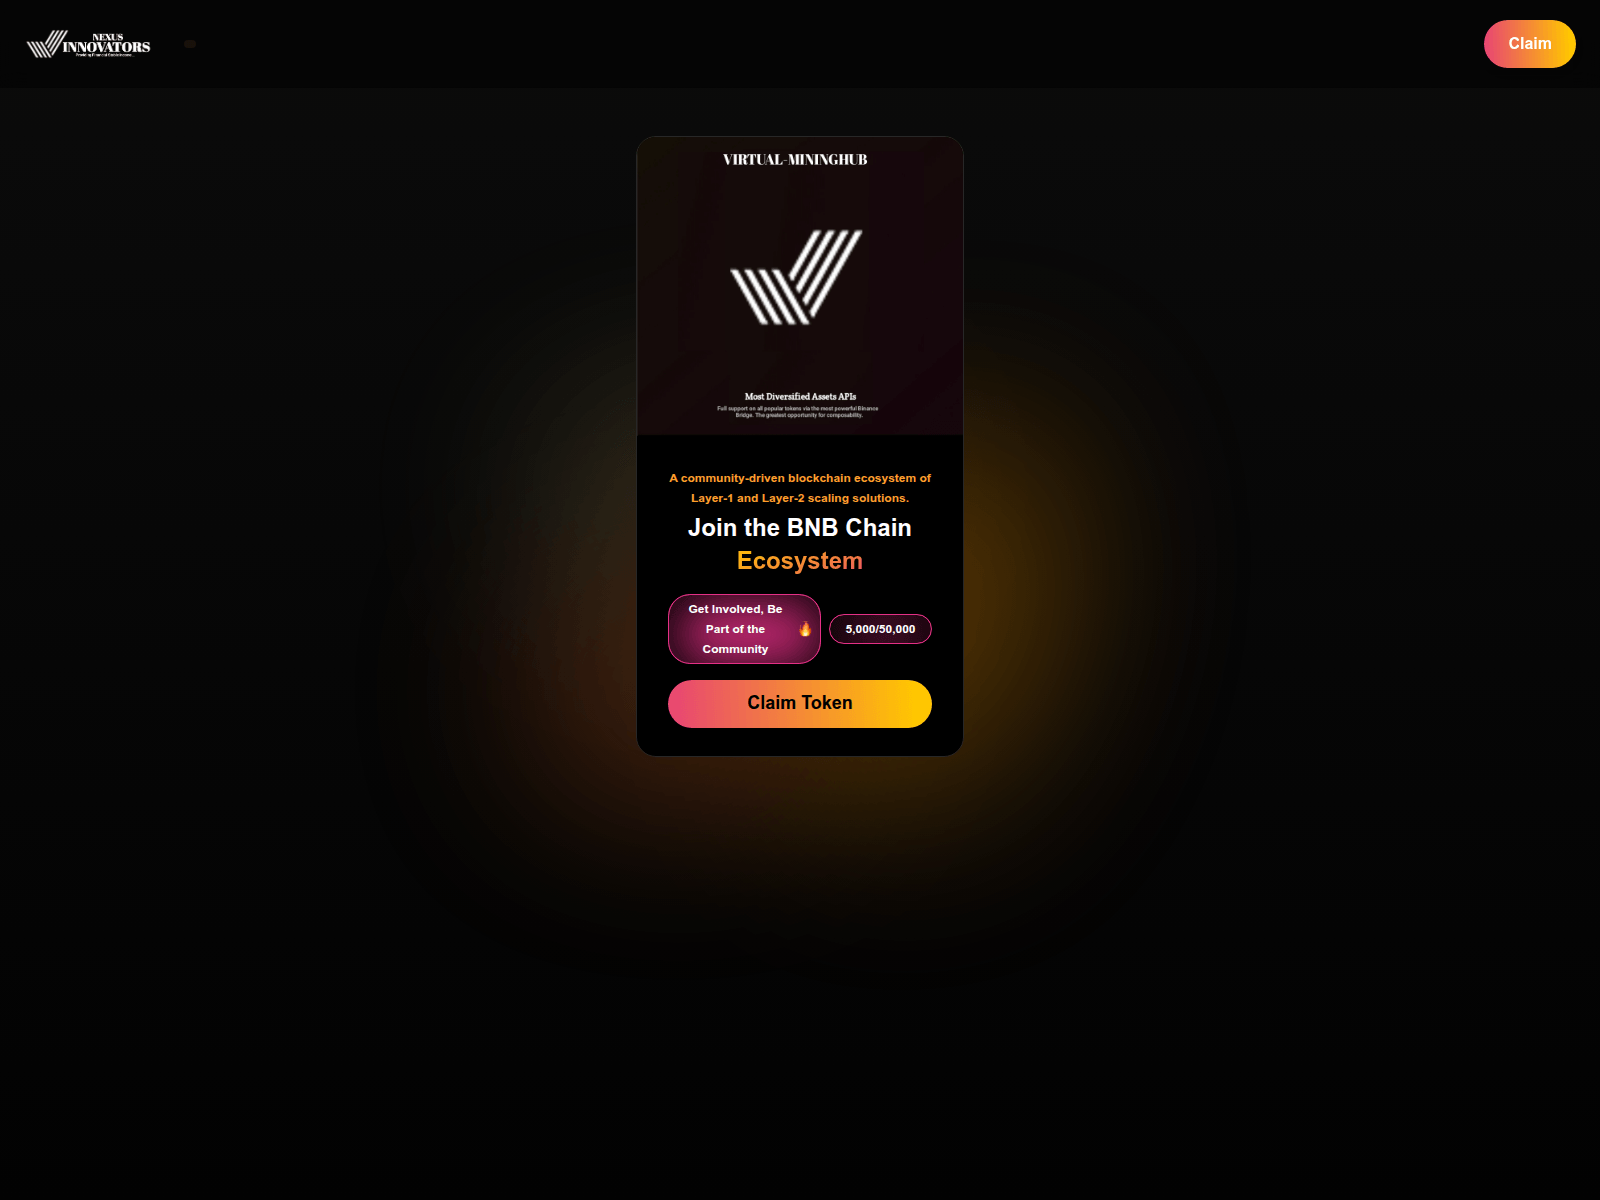
semantic.nexus-innovators.site
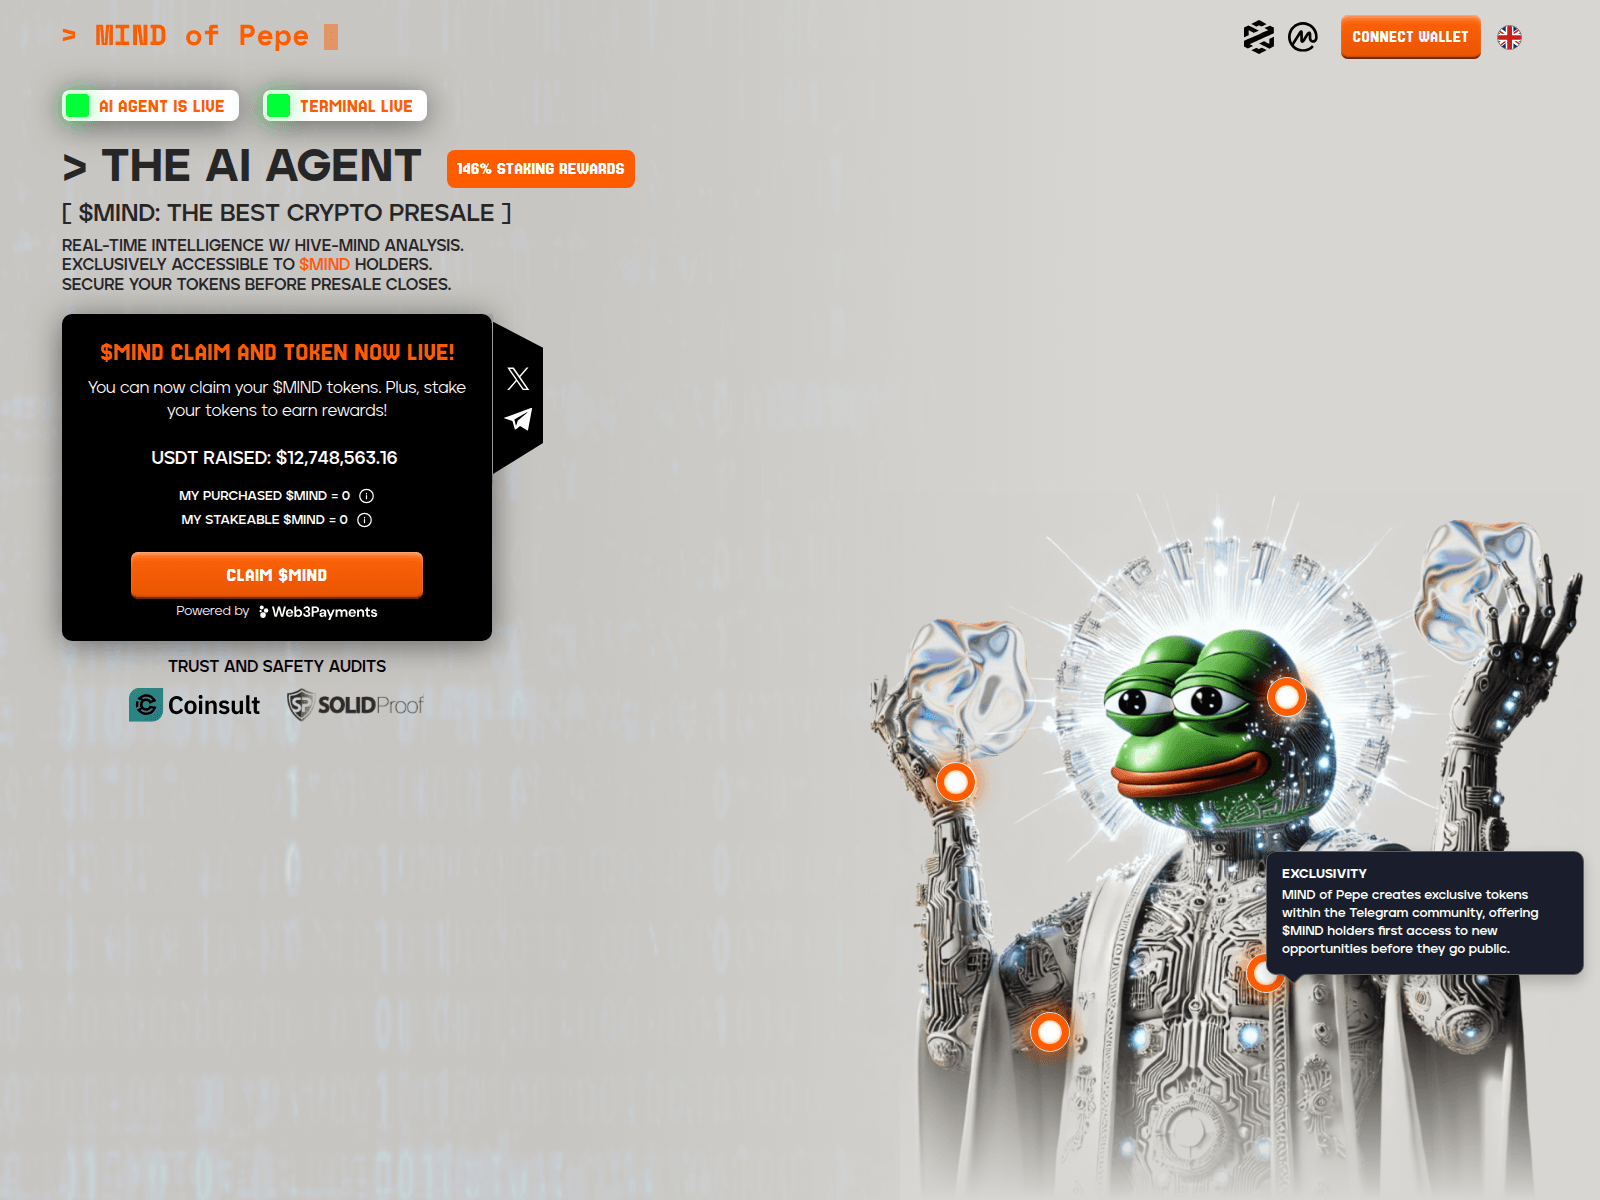
claim.mindof-pepe.world
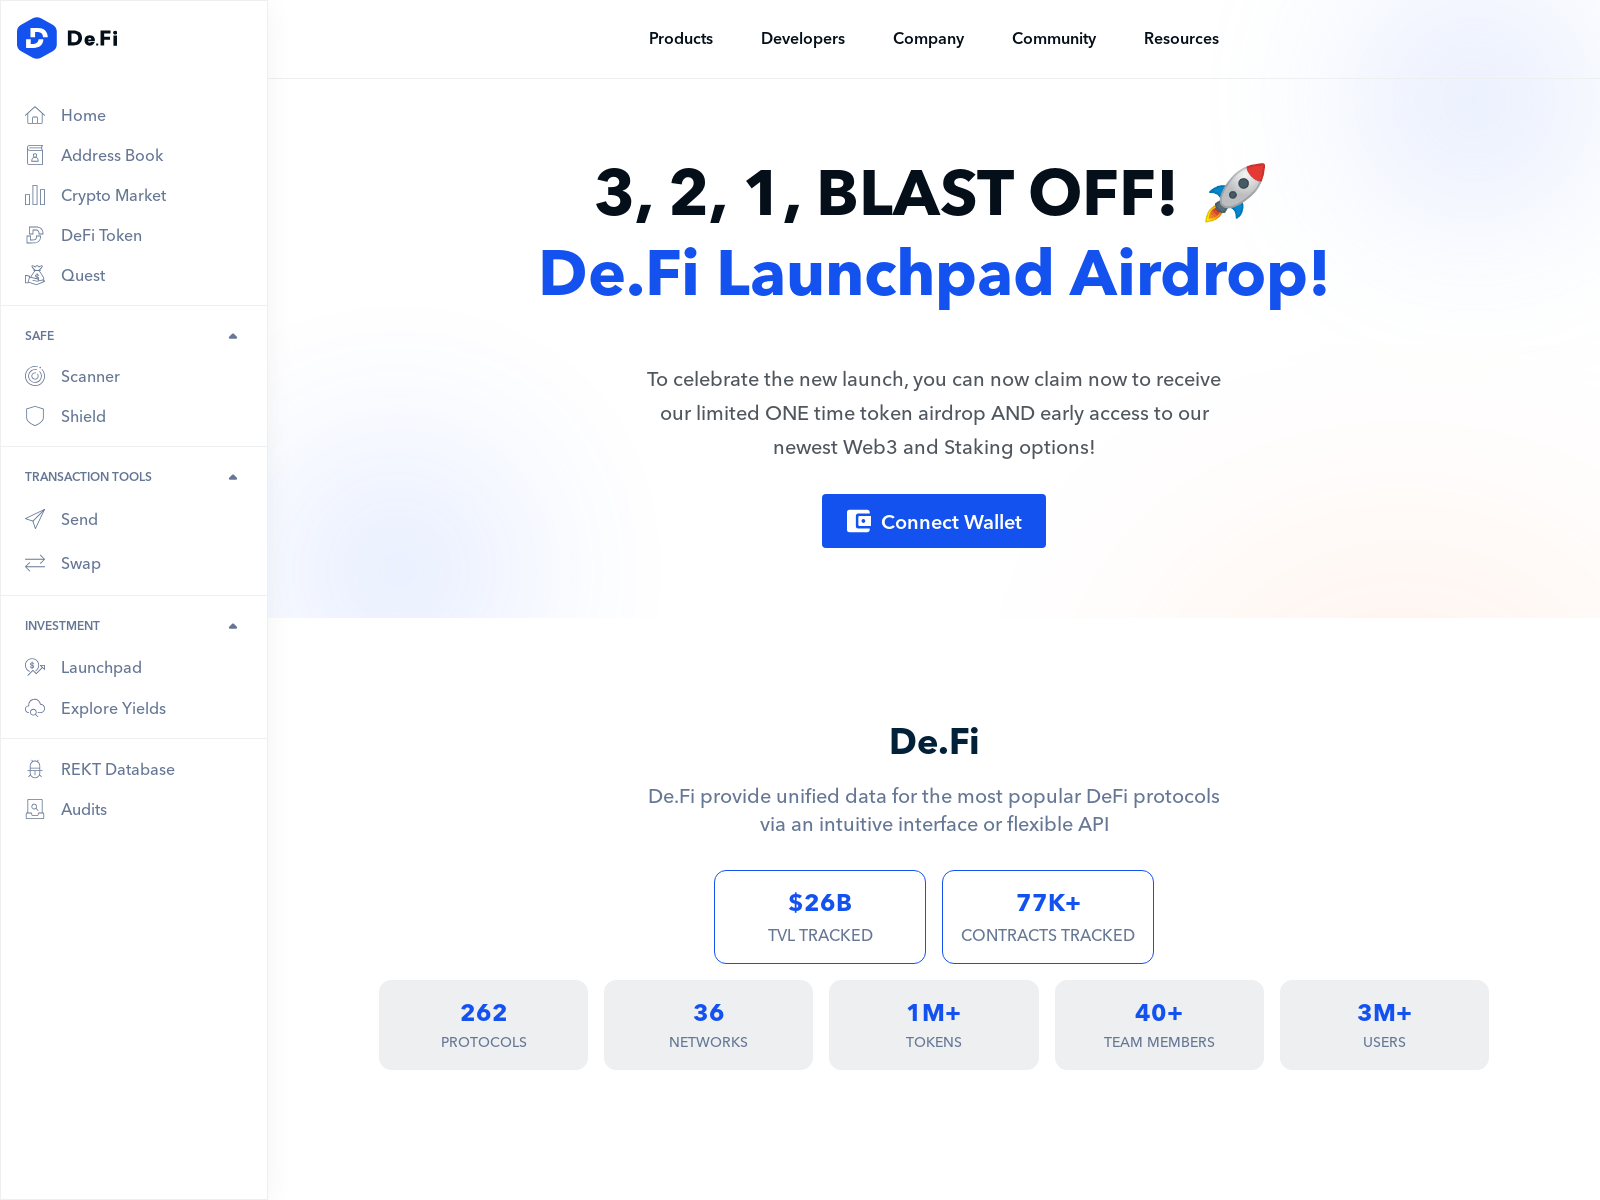
defi-launch.io
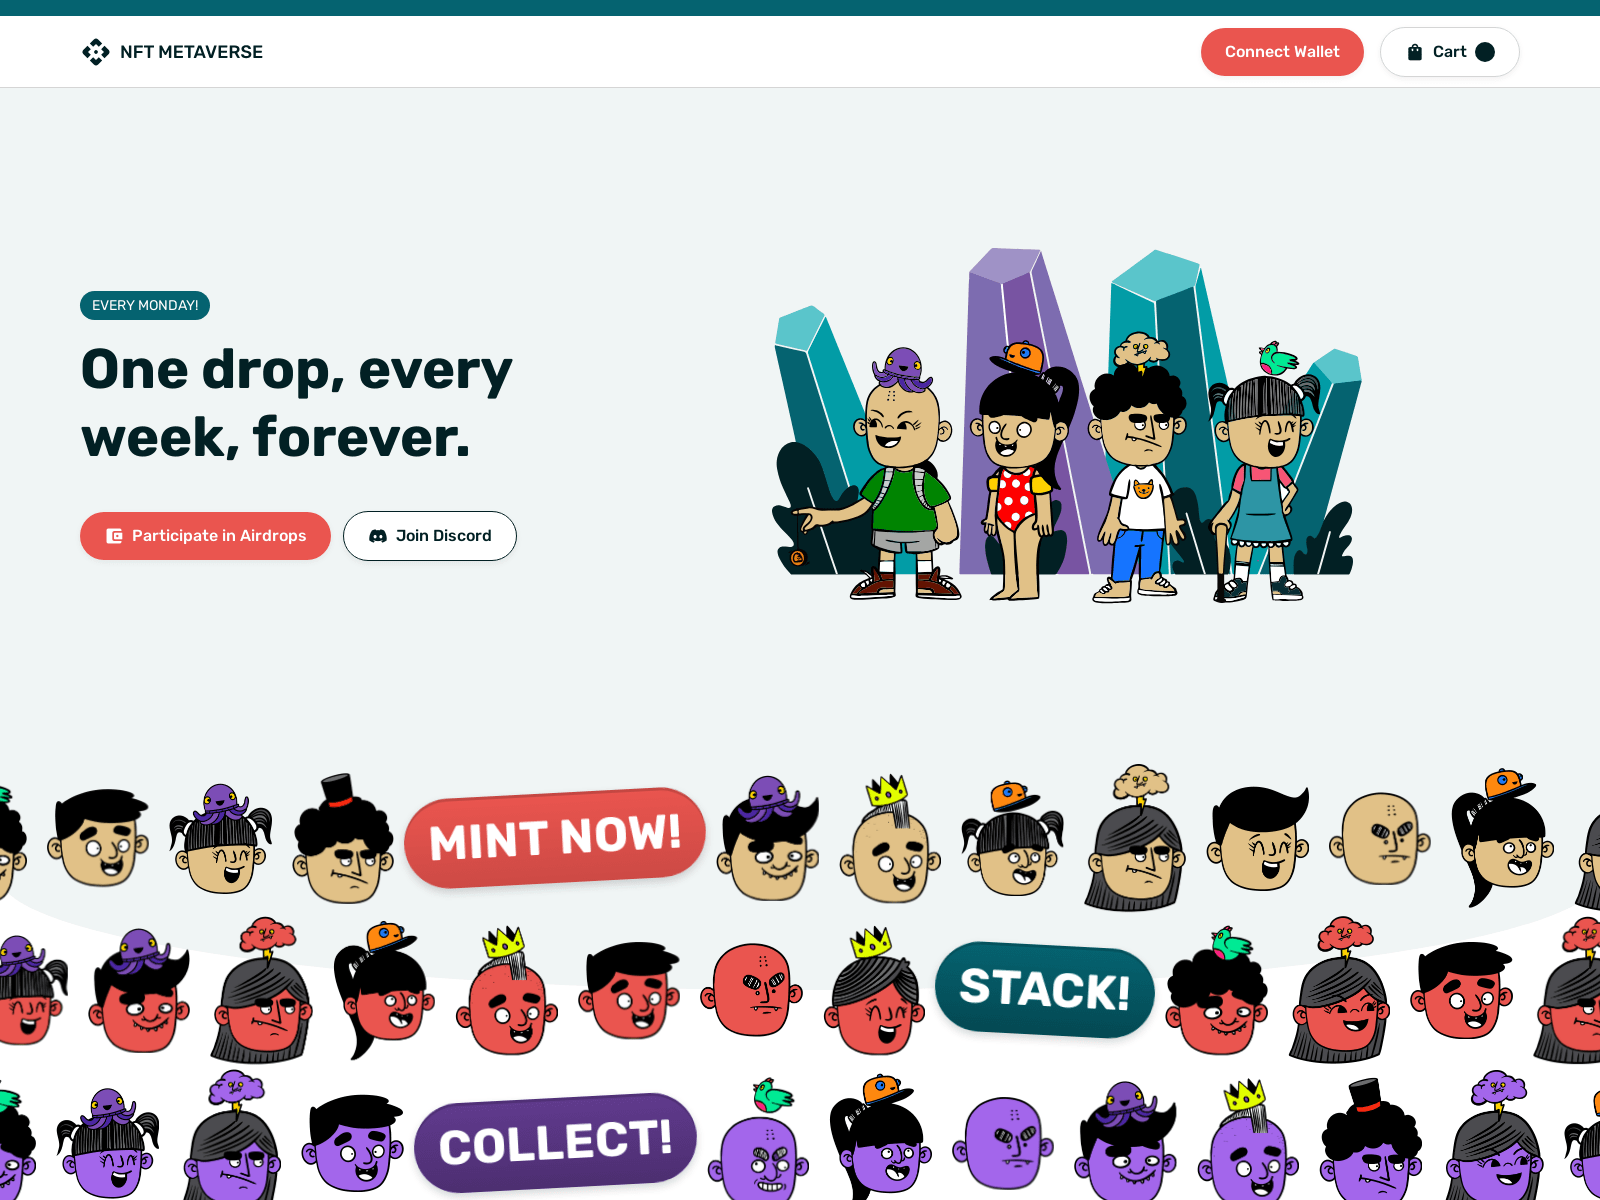
metaversentf.com
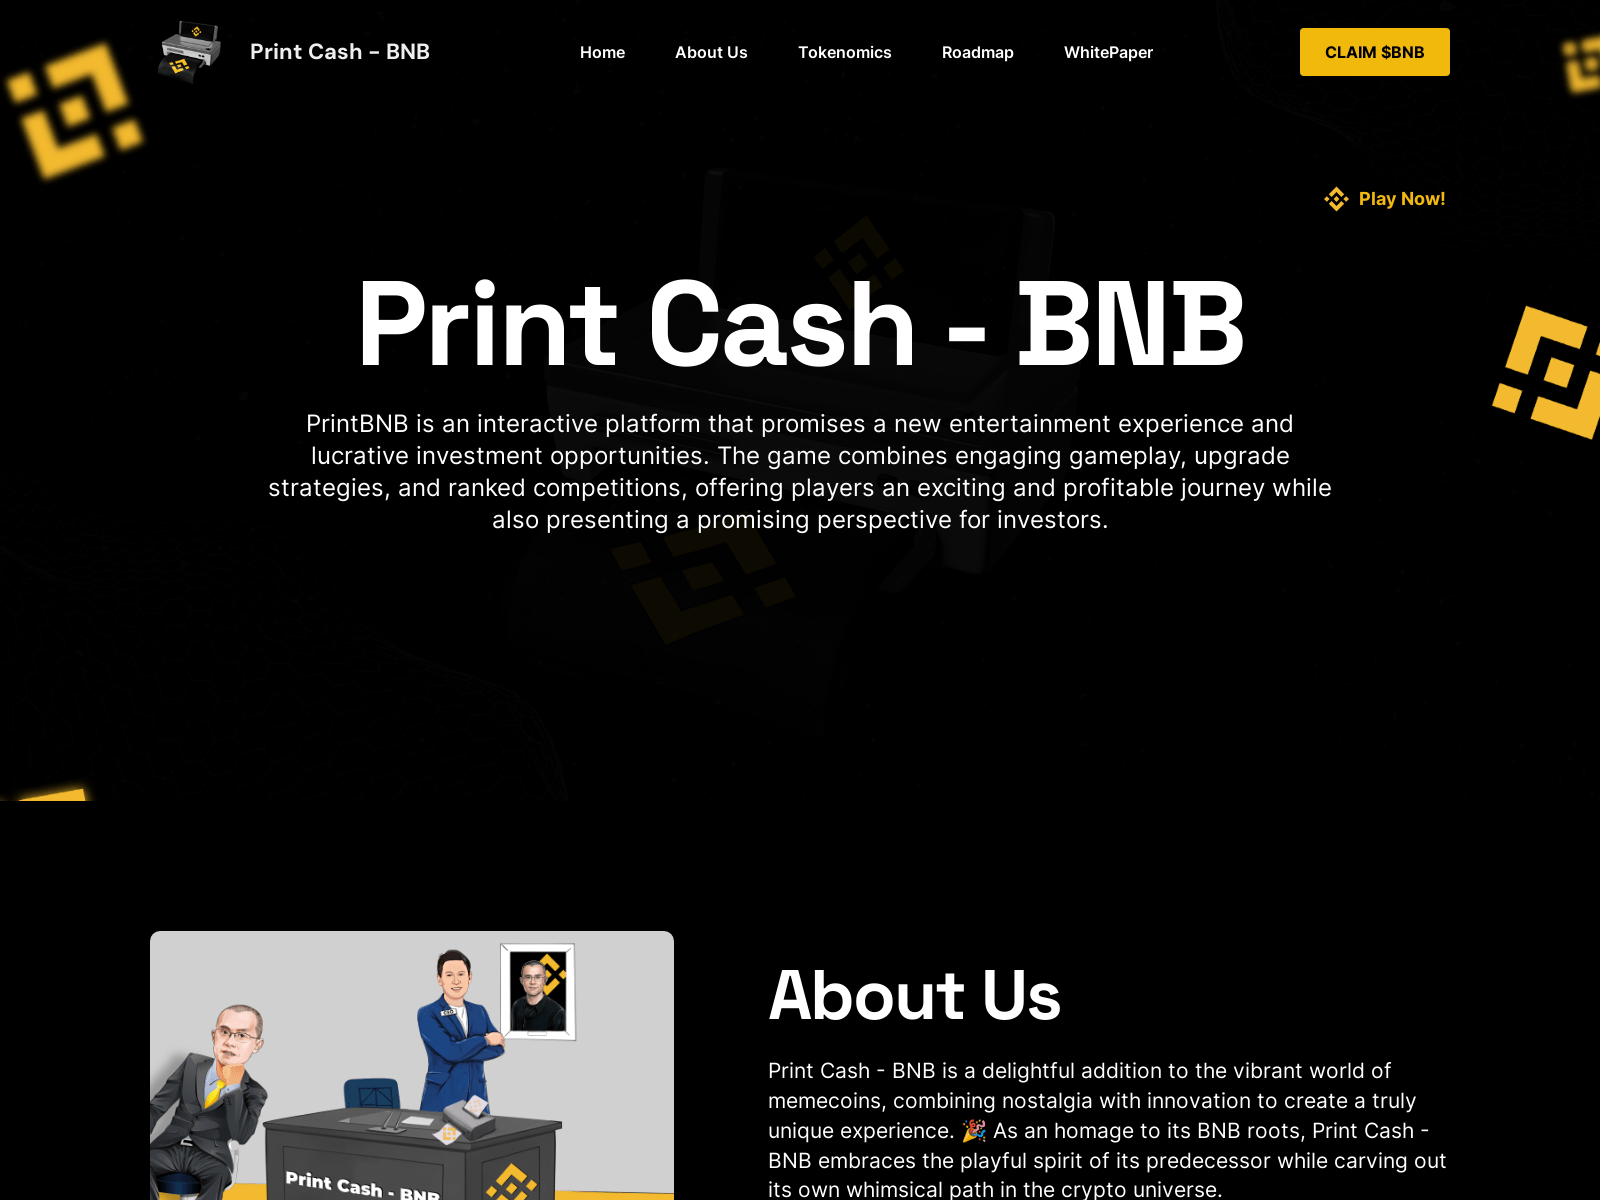
bridge.maob.site
dymensionrollapps.com
fincaptor.app
publicsale.well3.website
randombitcoins.com
威胁响应 Pipeline
该中心内的每个域名是如何经过验证的,以及已确认的威胁是如何被消除的。 完整流程可视化 →
威胁情报核查— 每个域名都会经过扫描,并与以下内容进行交叉核对:
urlscan.io屏幕截图 · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency 报告Cloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulses互联网档案馆Historical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS 安全 FiltersQuad9 · AdGuard · CleanBrowsingWeb-检查Full surface scan
 crt.sh
全球供应商同步— 已确认的检测结果将推送给 29 家合作伙伴:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantec网站评审AviraCloud detectionAvast / AVGWeb Shield卡巴斯基OpenTIPDr.WebOnline scannerNetcraft关停 APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.报告Hosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust