VirusTotal
22 / 93
Segnala


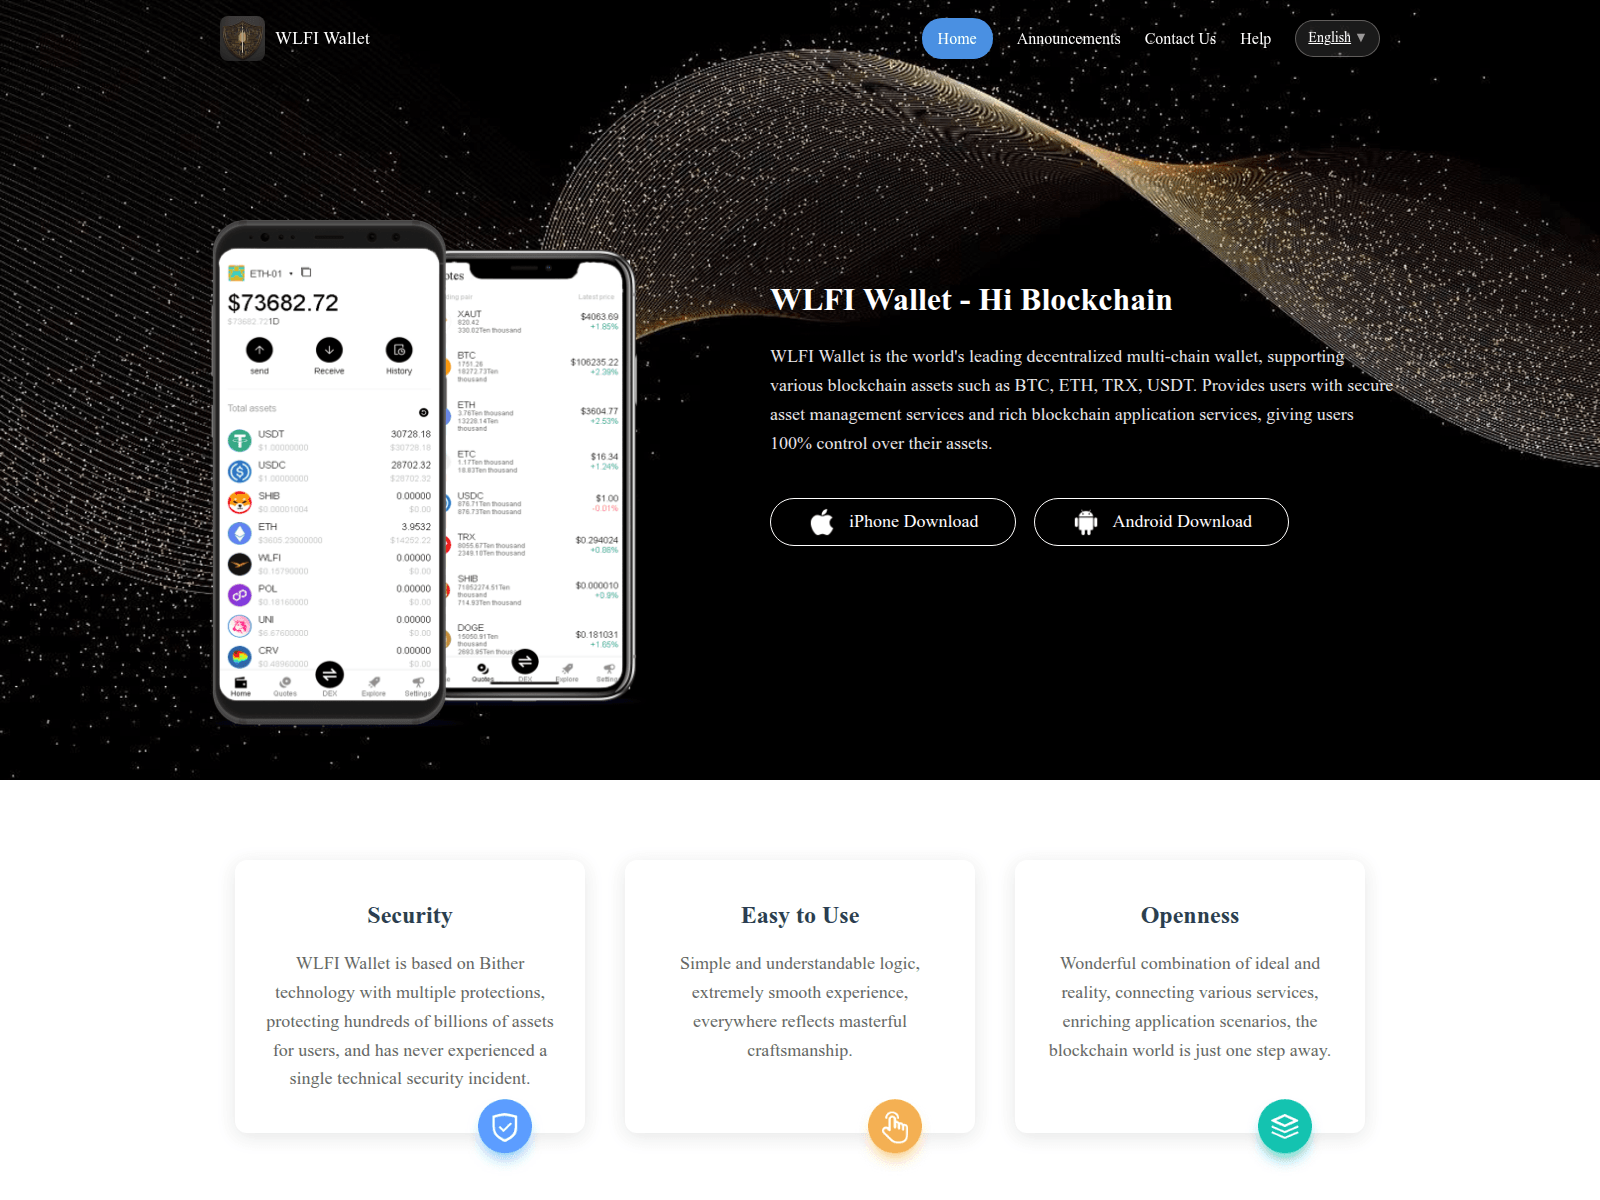
“WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co”
wlfiprobit.com — Contenuto non disponibile. Simulazione del marchio: Arbitrum; Tipo di truffa: Crypto Scam. Riepilogo delle prove: VirusTotal 22/93 (ADMINUSLabs, ChainPatrol, alphaMountain.ai, BitDefender, Cluster25); URLQuery 6 alerts; PhishDestroy score 95/100.
L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | wlfiprobit.com |
malicious | Sinkholed |
| OpenDNS | wlfiprobit.com |
phishing | Phishing Block |
| DigiCert UltraDNS | wlfiprobit.com |
malicious | Sinkholed |
| Hagezi Threat Feed | wlfiprobit.com |
malicious | Sinkholed |
| DNS4EU | wlfiprobit.com |
malicious | Sinkholed |
| Quad9 DNS | wlfiprobit.com |
malicious | Sinkholed |
The domain wlfiprobit.com is identified as a high-risk brand impersonation threat targeting Arbitrum. It masquerades as a legitimate cryptocurrency wallet service, using the page title "WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co" to deceive users. This domain was likely designed to harvest sensitive user data or credentials under the guise of offering cryptocurrency services.
Technical analysis reveals that wlfiprobit.com is flagged by 22 out of 95 security vendors on VirusTotal, indicating significant recognition as a threat. The domain resolves to IP address 172.67.152.201, located in the United States under AS13335 managed by Cloudflare, Inc. It was created on February 21, 2026, and has been blocked by three security blocklists including PhishDestroy, MetaMask, and SEAL. The domain's SSL certificate is identified as WE1, and it is currently offline, reducing immediate exposure.
The domain's current offline status mitigates immediate risk; however, vigilance is advised as it may resurface or similar threats could emerge. Security teams should ensure that blocklists are updated and implement additional monitoring for similar activities. Users should be educated on recognizing phishing attempts, particularly those involving cryptocurrency platforms.
Osservazioni archiviate relative al confronto tra crawler e browser per questo host, oltre a una verifica in tempo reale delle impronte digitali per i sistemi di distribuzione del traffico in stile Keitaro.
Nota dello scanner: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='wlfiprobit.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError(
La reputazione Edge-IP non è attribuita a questo dominio.
Location describes the IP network.
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
28 domini simili memorizzati
Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.


Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.
Template-based draft · optional AI wording assistance requires separate consent
Ogni riga rappresenta un motivo per cui un dominio è collegato a questo host. I nodi a dimensione intera indicano rilevamenti di VirusTotal, mentre quelli tratteggiati sono già offline. Di seguito è riportato l'elenco completo.
Stesso hash della favicon o stesso titolo della pagina di questo host.
Questi report si risolvono nello stesso IP edge condiviso. Aiutano con l'individuazione dei report ma non implicano la proprietà comune o un server di origine condiviso.
Questi domini prendono di mira anche gli utenti di Arbitrum. Visualizza tutte le minacce relative a "Arbitrum" →
Rapporti aggiunti di recente dal database PhishDestroy. Questi collegamenti di scoperta non implicano infrastrutture o proprietà condivise.
Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica
Scansiona oraSegnala i domini sospetti al nostro database delle minacce — proteggi la comunità
SegnalaSegnalazioni recenti di phishing e modifiche osservate della disponibilità
MonitoraControlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo