VirusTotal
5 / 92
Segnala


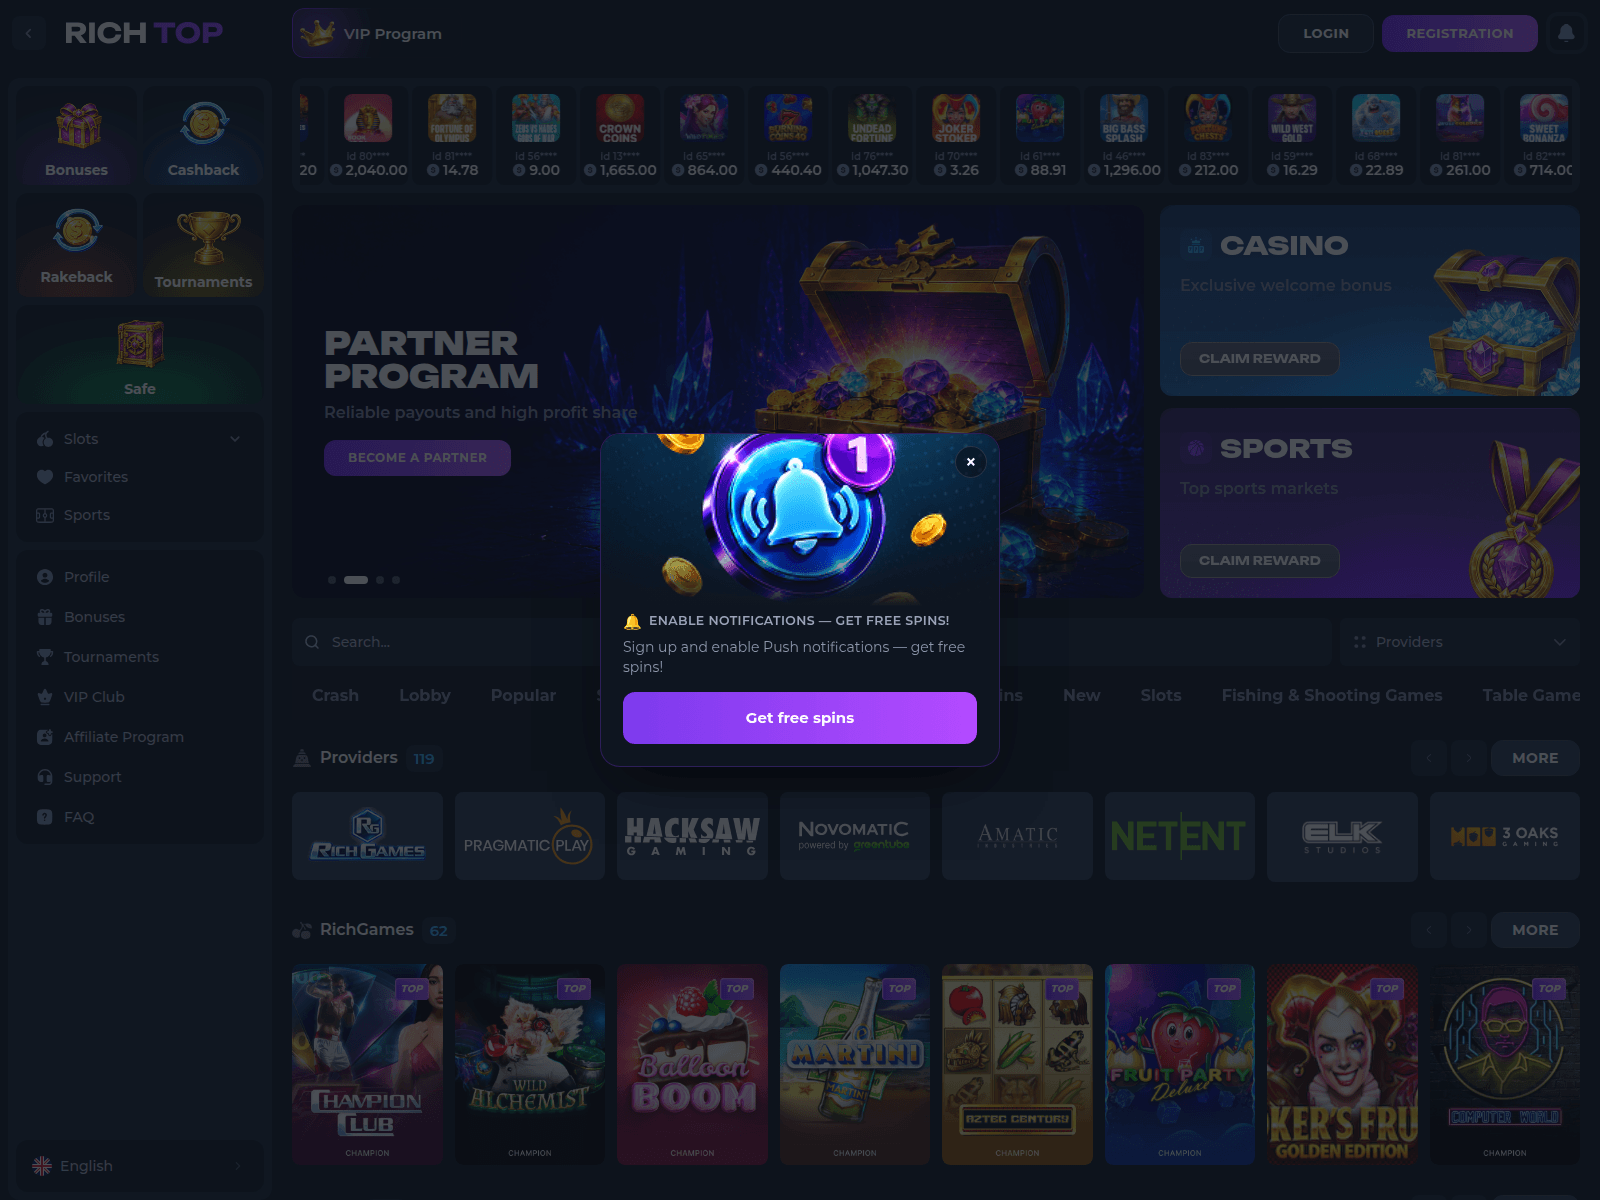
“RichTop Crypto Casino - slots, live games and fast payouts”
r1qwxrt.net — Ultimo attivo conosciuto (HTTP 200). Simulazione del marchio: Ethereum; Tipo di truffa: Gambling. Riepilogo delle prove: VirusTotal 5/92 (alphaMountain.ai, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, SOCRadar); Spamhaus DBL_PHISH; PhishDestroy score 93/100. Registrar: NiceNIC.
L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.

The domain r1qwxrt.net was observed in multiple security sources on 2026-10-07, including a VirusTotal scan and an OTX record. The domain was also included in the publisher-owned PhishDestroy catalogue on this date.
VirusTotal scanned r1qwxrt.net on 2026-10-07 using 92 scanners and reported 0 detections. OTX recorded 4 pulses for the domain on 2026-10-07. The domain was registered on 2026-09-23 with NICENIC INTERNATIONAL GROUP CO., LIMITED, and its SSL certificate was issued by Let's Encrypt / YE1 as of 2026-10-07.
The VirusTotal scan provides a snapshot of how the domain was evaluated by multiple security vendors at the time, while OTX pulses suggest that community members had previously reported or discussed the domain. The presence in the PhishDestroy catalogue indicates that the publisher had recorded the domain for monitoring or further review.
To further assess r1qwxrt.net, retain the VirusTotal scan and OTX pulse records for future comparison. Reference the PhishDestroy catalogue entry alongside these sources to monitor for any new developments. Continue to collect updated records from each source to track changes over time.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/richtop_supportStored page referenceIoC extraction recorded 2026-10-08 04:00:16 UTC
Osservazioni archiviate relative al confronto tra crawler e browser per questo host, oltre a una verifica in tempo reale delle impronte digitali per i sistemi di distribuzione del traffico in stile Keitaro.
cloudflareNota dello scanner: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
 (RU)
PhishDestroy Investigation
La reputazione Edge-IP non è attribuita a questo dominio.
sevki.ns.cloudflare.comvera.ns.cloudflare.comLocation describes the IP network.
1e6866127bc4ba4e2212b1a265a5906fa9dbc0e4aa0274f7908ff994e219b8eaSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
188.114.97.3. 11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
52 domini simili memorizzati
Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.


Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.
Template-based draft · optional AI wording assistance requires separate consent
Ogni riga rappresenta un motivo per cui un dominio è collegato a questo host. I nodi a dimensione intera indicano rilevamenti di VirusTotal, mentre quelli tratteggiati sono già offline. Di seguito è riportato l'elenco completo.
Fa parte della campagna di phishing “Gambler Scam”. Visualizza tutti i domini della campagna →
Questi report si risolvono nello stesso IP edge condiviso. Aiutano con l'individuazione dei report ma non implicano la proprietà comune o un server di origine condiviso.
Questi domini prendono di mira anche gli utenti di Ethereum. Visualizza tutte le minacce relative a "Ethereum" →
Registrati tramite lo stesso registrar. Un registrar serve milioni di clienti non collegati tra loro, quindi questo dato indica semplicemente un raggruppamento piuttosto che dimostrare un nesso.
Rapporti aggiunti di recente dal database PhishDestroy. Questi collegamenti di scoperta non implicano infrastrutture o proprietà condivise.
Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica
Scansiona oraSegnala i domini sospetti al nostro database delle minacce — proteggi la comunità
SegnalaSegnalazioni recenti di phishing e modifiche osservate della disponibilità
MonitoraControlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo