




Sicurezza del dominio e intelligence sulle minacce
ondo.finance.sunio.mov
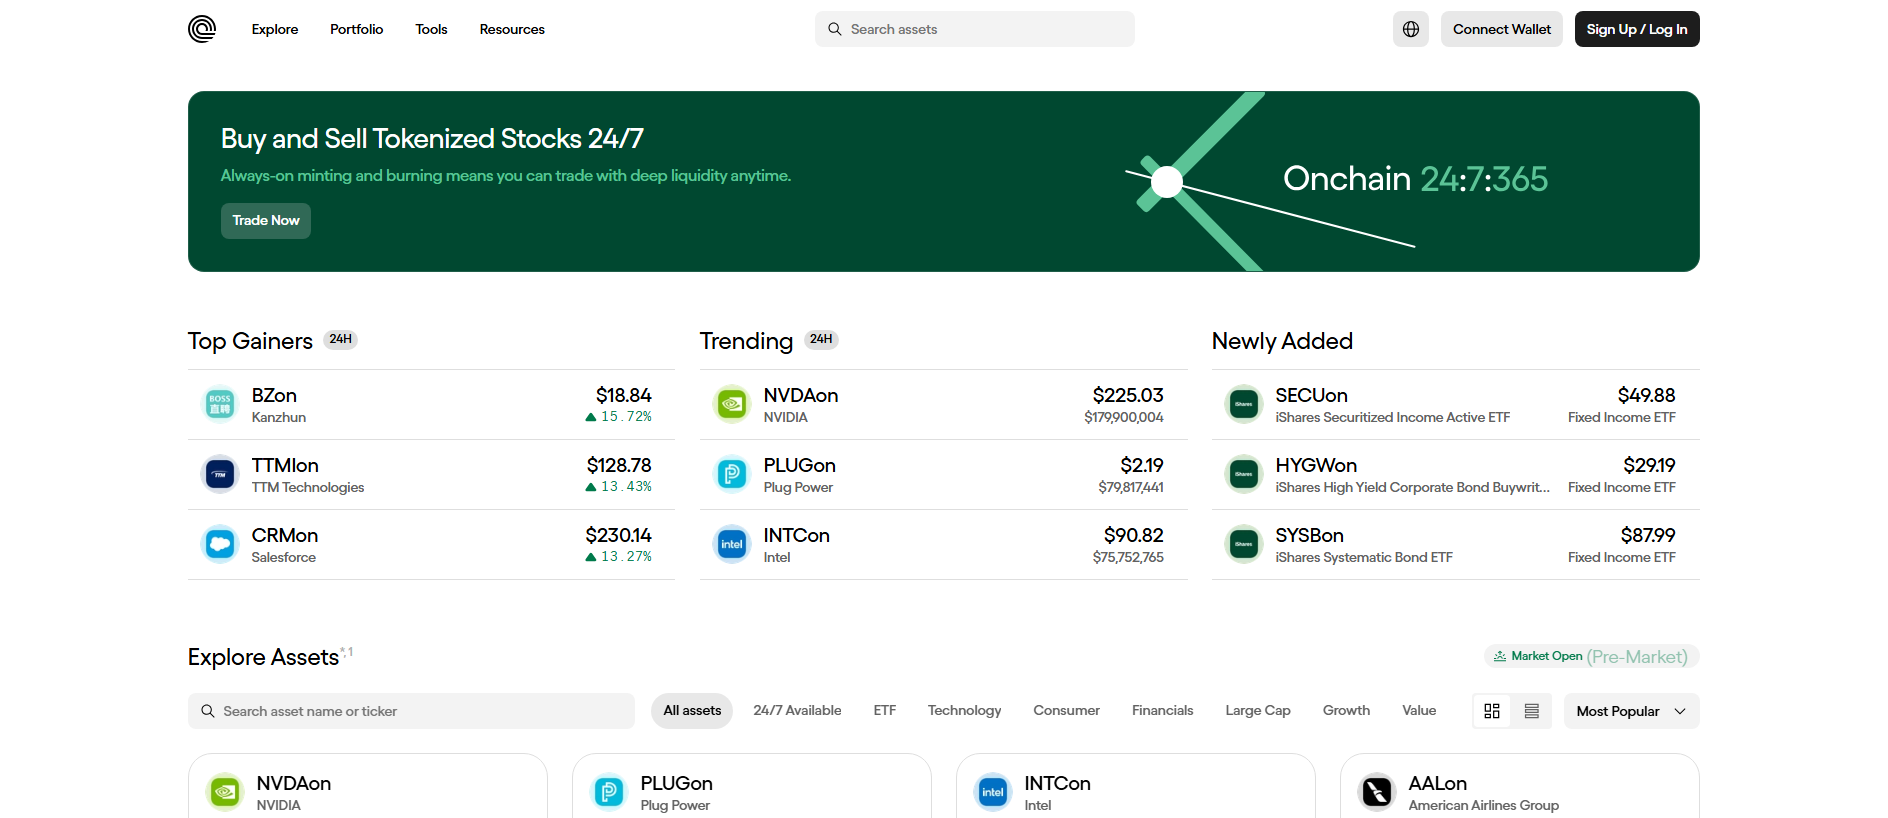
“Ondo | Tokenized Stocks”
Verdetto di minaccia
Critico
Punteggio delle prove 100/100
Disponibilità
Ultimo attivo conosciuto
Ultima osservazione di raggiungibilità memorizzata
Segnali di rischio
Rilevamenti VirusTotal: 13/89
Spamhaus DBL: DBL_SPAM
URLQuery threat systems: 4 alerts
Simulazione del marchio: Ondo
Ultimo attivo conosciuto
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@iqweb.io.
The latest stored availability evidence still shows the domain reachable; 9 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
9 days
Reports sent
1
Latest case ID
PD-20260911-5868C3
Current status
HTTP 200 at latest stored check
Riepilogo del rapporto
ondo.finance.sunio.mov — Ultimo attivo conosciuto (HTTP 200). Simulazione del marchio: Ondo; Tipo di truffa: Impersonation. Riepilogo delle prove: VirusTotal 13/89 (BitDefender, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker); URLQuery 4 alerts; URLScan malicious verdict; Spamhaus DBL_SPAM; CF Radar malicious; PhishDestroy score 100/100.
L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.
Riepilogo delle prove
CRITICO
ondo.finance.sunio.mov is a subdomain of sunio.mov. PhishDestroy first observed the hostname on Sep 11, 2026. The hostname explicitly references Ondo; stored content metadata identifies the same apparent target. The captured page title is “Ondo | Tokenized Stocks”. Stored page analysis classifies the content as impersonation. Campaign clustering links the hostname to the Unknown kit. Current evidence score: 100/100 (critical).
Positive findings are stored from 5 sources: VirusTotal, Spamhaus DBL, Cloudflare Radar, URLQuery, and URLScan. VirusTotal recorded 13 detections among 89 engines: BitDefender, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, MalwareURL, Seclookup, SOCRadar, Sophos, VIPRE on Sep 20, 2026 at 02:16 UTC. Spamhaus DBL: DBL_SPAM on Sep 11, 2026 at 10:30 UTC. Cloudflare Radar classified the hostname as malicious and placed it in the phishing category; its verdict timestamp was not retained. URLQuery recorded 4 threat-system alerts on Sep 11, 2026 at 10:13 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Ondo and assigned phishing as its category on Sep 12, 2026 at 03:30 UTC. Non-positive and contextual checks: ScamAdviser assigned a trust score of 15/100 (Very Likely Unsafe); no observation timestamp was retained. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 22:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 16:01 UTC.
HTTP 200 was recorded on Sep 20, 2026 at 22:15 UTC. The recorded creation date for the registrable domain sunio.mov is Dec 24, 2025. At collection time, the hostname resolved to 186.2.175.25 on AS59692 (IQWeb FZ-LLC). The recorded endpoint location is Belmopan, BZ. The stored server header is ddos-guard. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YR1 as the certificate issuer with validity through Nov 25, 2026; checked Sep 11, 2026 at 10:02 UTC.
The content indicators and 5 positive source findings support the current Ondo-themed impersonation classification.
VirusTotal
13 det.
URLQuery
4 threat alerts
CF Radar
Malevolo
URLScan
Scamadviser
15/100Very Likely Unsafe
Certificato TLS
Let's Encrypt / YR1
Età
9 mo
Stato osservato
Ultimo attivo conosciuto 200

Elenco da eliminare
Presente
Reports Sent
1
Copertura dei dati
VirusTotal
13 / 89
URLQuery
4 threat-system alerts
OTX
no community references
CF Radar
provider verdict: malicious
URLScan capture
rapporto memorizzato
URLScan verdict
malicious
TLS
valid certificate, 65d
WHOIS
9 mo old
Screenshot
4 captures · 3 sources
Scamadviser
15/100
Informazioni sulla sicurezza di rete
Threat Detection Systems
4 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | ondo.finance.sunio.mov |
malicious | Sinkholed |
| OpenDNS | ondo.finance.sunio.mov |
phishing | Phishing Block |
| DNS4EU | ondo.finance.sunio.mov |
malicious | Sinkholed |
| Quad9 DNS | ondo.finance.sunio.mov |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Sep 11, 2026 · 15:04 UTCVirusTotal scanner detections updated from 10 to 11. Added scanner alerts: ESET.
-
Threat First Observed Sep 11, 2026 · 11:56 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
186.2.175.25.
Pipeline di risposta alle minacce
Scoperta
Checks
Reports
Disponibilità
13/14
Sent Report Recorded
Stored sent-report record for domain registrar, hosting provider, 1 abuse contact
abuse@iqweb.io
Stato della lista di blocco pubblica
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
ddos-guard
Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=ddos-guard
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Acquisizione salvata · 4 sources
Analisi dei domini
Dominio
URLScan Verdict
Malevolo
score 100 Phishing brand: Ondo report ↗
Server / ASN
ddos-guard · AS59692 IQWeb FZ-LLC
Reputazione IP
abuse score 0/100 0 reports checked 11/09/2026
Registrar (base domain)
Sconosciuto
Indirizzo IP
186.2.175.25

Registration (base domain)sunio.mov · Creato 24/12/2025 (270d)
Stato HTTP200
Dettagli tecniciDNS, SAN SSL, timestamp
Rilevato per la prima volta11/09/2026
IoC Extraction
Submitted URLhttp://ondo.finance.sunio.mov/
TLS Fingerprint
TLS Observation
Favicon Hash
ID del caso
Riscontro delle informazioni sulle minacce · source references
ScamAdviser
Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Segnala questo dominio
Invia le prove e contribuisci a proteggere gli altri
Analisi di VirusTotal
13 / I fornitori di sicurezza 89 hanno contrassegnato questo dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 11 detections
BitDefender
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
MalwareURL
Seclookup
SOCRadar
Sophos
VIPRE
Analisi delle prestazioni del sito
Google PageSpeed Insights — mobile performance audit of ondo.finance.sunio.mov · checked Sep 11, 2026
73
Needs Work
Performance
FCP
4.38s
First Contentful Paint
LCP
4.56s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
3ms
Total Blocking Time
SI
4.38s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Intelligence della comunità
1 segnalazione della comunità
CategoriaPHISHING
Ondo.finance.sunio.mov trieb to Trick me into connecting my wallet
Dati e relazioni esterne
Analisi della sicurezza
Community Scam Report — ChainAbuse
1 report filed for ondo.finance.sunio.mov (1 written by a person) · category: Phishing · source checked
“Ondo.finance.sunio.mov trieb to Trick me into connecting my wallet”
— reported by Anonymous on Sep 10, 2026 · Source: ChainAbuse (TRM Labs) — full report and evidence there.
Istantanea delle prove inviate
Sent: Ledger records: 1
Case ID:
PD-20260911-5868C3 Recipient: abuse@iqweb.io Page title stored with report: New Private Tab
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT e intelligence
DNS e rete
SEO e dominio
Questo sito ti ha influenzato in qualche modo?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.

Europol
Trova il canale di segnalazione ufficiale per il tuo paese dell'UE
National police directory

Action Fraud
Segnala frodi e crimini informatici in Inghilterra, Galles e Irlanda del Nord
Contact centre0300 123 2040
PhishDestroy listing review Non un rapporto delle forze dell'ordine
Ricorso in materia di domini
Richiedi una revisione se possiedi questo dominio e ritieni che l'elenco non sia corretto
Attenzione ai truffatori che promettono il recupero dei fondi! I criminali possono contattare nuovamente le vittime fingendo di essere investigatori, avvocati o agenti di recupero. Non pagare commissioni anticipate né condividere credenziali. Scopri di più sulle frodi relative ai sussidi di recupero →
Segnalalo alle autorità locali
Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.
Elenco di 97 paesi
Bozza assistita dall'intelligenza artificiale: i dettagli dell'incidente vengono elaborati dal fornitore di intelligenza artificiale
Controllalo e invialo tu stesso
Infrastruttura e rapporti correlati
Infrastructure map · ondo.finance.sunio.mov
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Registrable-domain report Parent
sunio.movParent of ondo.finance.sunio.mov · separate evidence record 16 VTContent matches 5
Shared IP 186.2.175.25 6
Questo IP di origine ospita più domini di phishing: l'infrastruttura può essere condivisa tra campagne.
Ondo impersonation 7
These domains also target Ondo users. View all Ondo threats →
 appondo.finance
Unknown kit 8
Part of the Sconosciuto phishing campaign. View all campaign domains →
Rapporti recenti sulle minacce 3
Rapporti aggiunti di recente dal database PhishDestroy. Questi collegamenti di scoperta non implicano infrastrutture o proprietà condivise.
 primarkpolska.pl
 yeniyerler.com
Verifica qualsiasi dominio
Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica
Scansiona oraSegnala un tentativo di phishing
Segnala i domini sospetti al nostro database delle minacce — proteggi la comunità
SegnalaFeed in tempo reale sulle minacce
Segnalazioni recenti di phishing e modifiche osservate della disponibilità
MonitoraRimani informato, rimani al sicuro
Controlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo