
Cerca i domini monitorati ed esamina le prove archiviate, i rilevamenti e gli ultimi dati relativi alla disponibilità osservata.
219,812
Totale monitorato
213,485
VT rilevato
91,905
Ultima visualizzazione: attivo
127,907
Non disponibile all'ultimo controllo
565
VT In attesa di conferma
How This Attack Works
Fake Token Presale scams trick victims into believing they are investing in legitimate cryptocurrency projects. Here's how the scam typically unfolds:
STEP 1
Create Fake Websites
Scammers set up realistic-looking websites mimicking legitimate token presale portals.
STEP 2
Promote Presale on Social Media
Using social media and fake endorsements, scammers attract potential investors.
STEP 3
Collect Cryptocurrency
Victims are prompted to send cryptocurrency to a specified address under the guise of buying tokens.
STEP 4
Disappear with Funds
Once funds are collected, scammers shut down the site and disappear, leaving victims without recourse.
Technical Analysis
Fake Token Presale scams often leverage phishing tactics combined with cryptocurrency-specific techniques. Attackers use homograph attacks to create URLs that closely resemble legitimate sites, often registered through top registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED and PDR Ltd. d/b/a PublicDomainRegistry.com. They exploit the decentralized nature of blockchain networks, utilizing smart contracts that mimic legitimate presale contracts but are programmed to divert funds to the attacker’s wallet. The infrastructure often involves cloud-based hosting services to quickly deploy and dismantle sites, minimizing the chance of detection. HTML and JavaScript are commonly used to create dynamic, convincing interfaces that reassure potential victims of the site’s legitimacy. Additionally, attackers might deploy SEO techniques to improve the visibility of their fraudulent sites in search engine results, further increasing their reach.
Real Cases
CryptoX Presale Scam (2024)
$2 million stolen
A fake presale for a non-existent token, CryptoX, duped investors into contributing significant sums.
TokenLaunch Fraud (2023)
$1.5 million stolen
Victims were lured into a fake token launch with promises of high returns, only for the site to vanish post-collection.
QuickCoin Deception (2024)
$3 million stolen
Scammers created a sophisticated site mimicking a known exchange, leading to substantial financial losses.
How to Detect
Controlla for slight misspellings in domain names.
Look for inconsistent branding or layout compared to legitimate sites.
Be wary of unsolicited investment opportunities via social media.
Verify presale details on official project channels.
Beware of high-pressure tactics urging immediate investment.
How to Protect Yourself
1
Always verify URLs before entering personal information.
2
Use browser extensions to detect phishing attempts.
3
Consult official project websites or channels for presale information.
4
Enable two-factor authentication on cryptocurrency exchanges.
5
Relazione suspicious sites to authorities and platforms like PhishDestroy.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 689 domains tracked for this threat type
Fake Token Presale 689 domains

gro47k.com

gro88k.org

grok15ktoken.com
hotdeal.com


kdn33a.blogspot.com
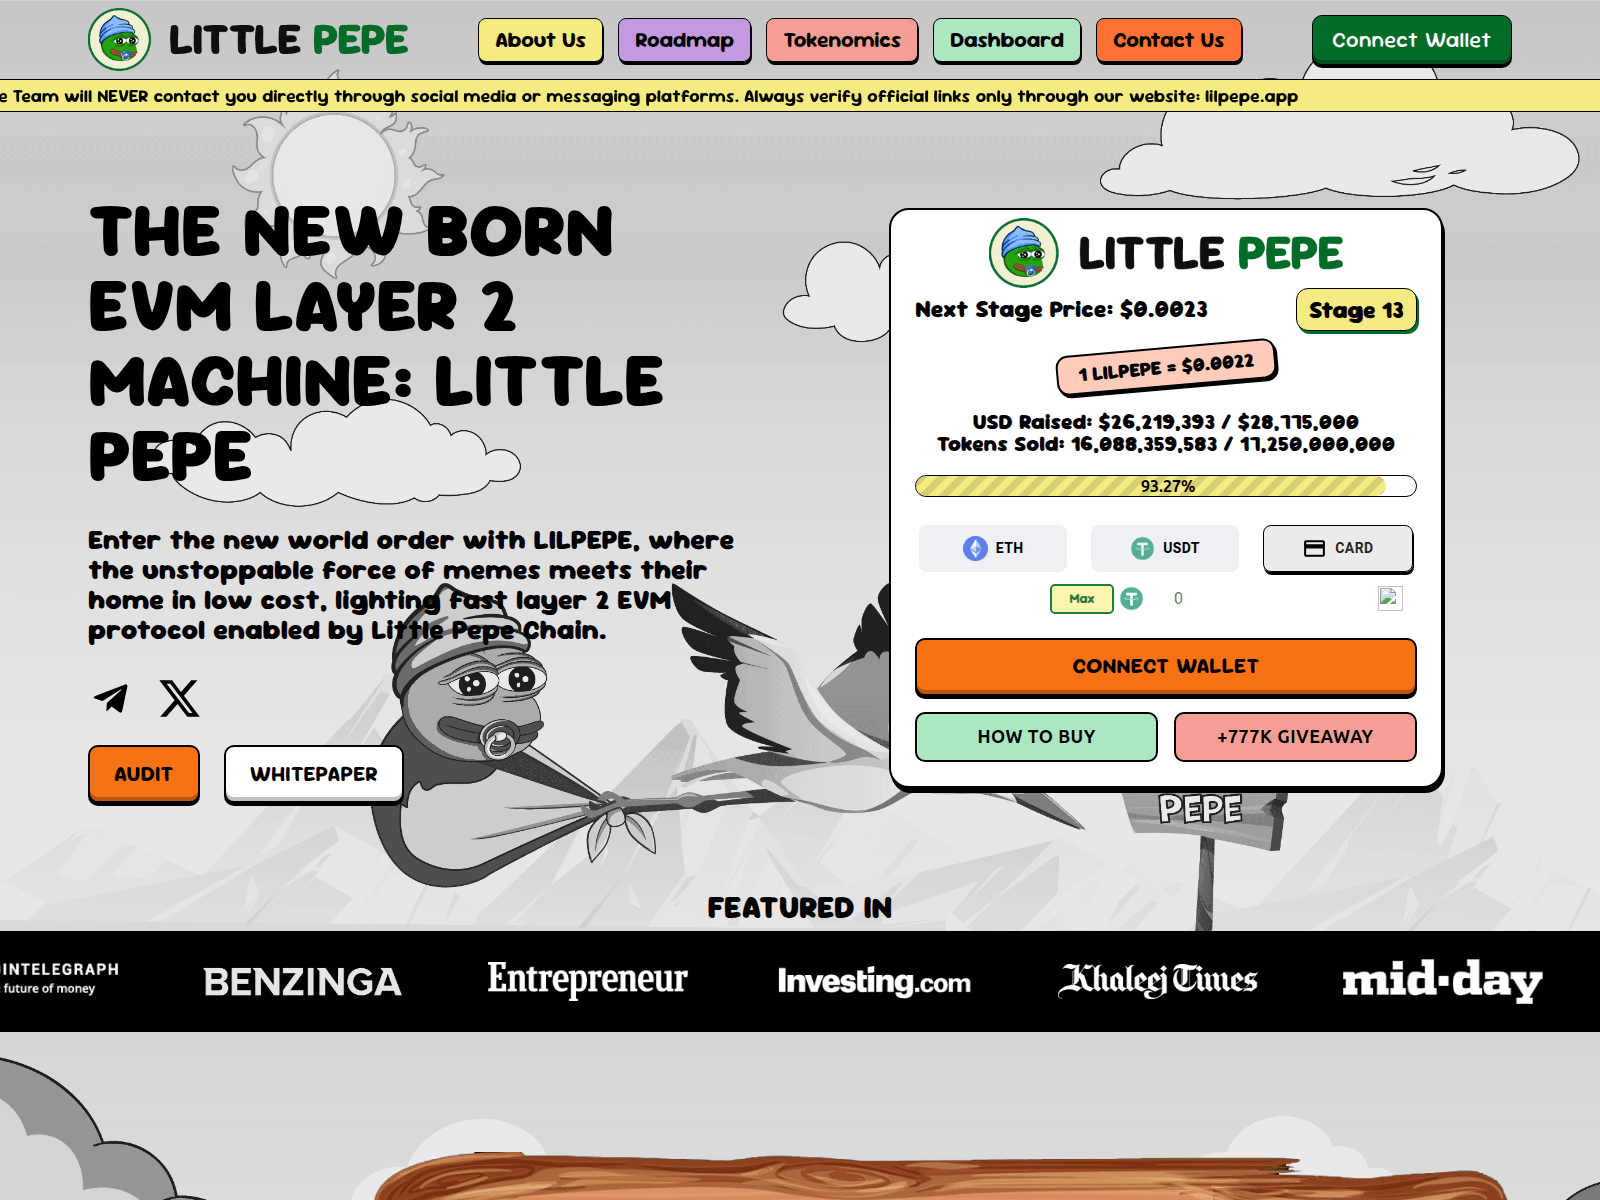
lilpepe.app

litllepepe.top
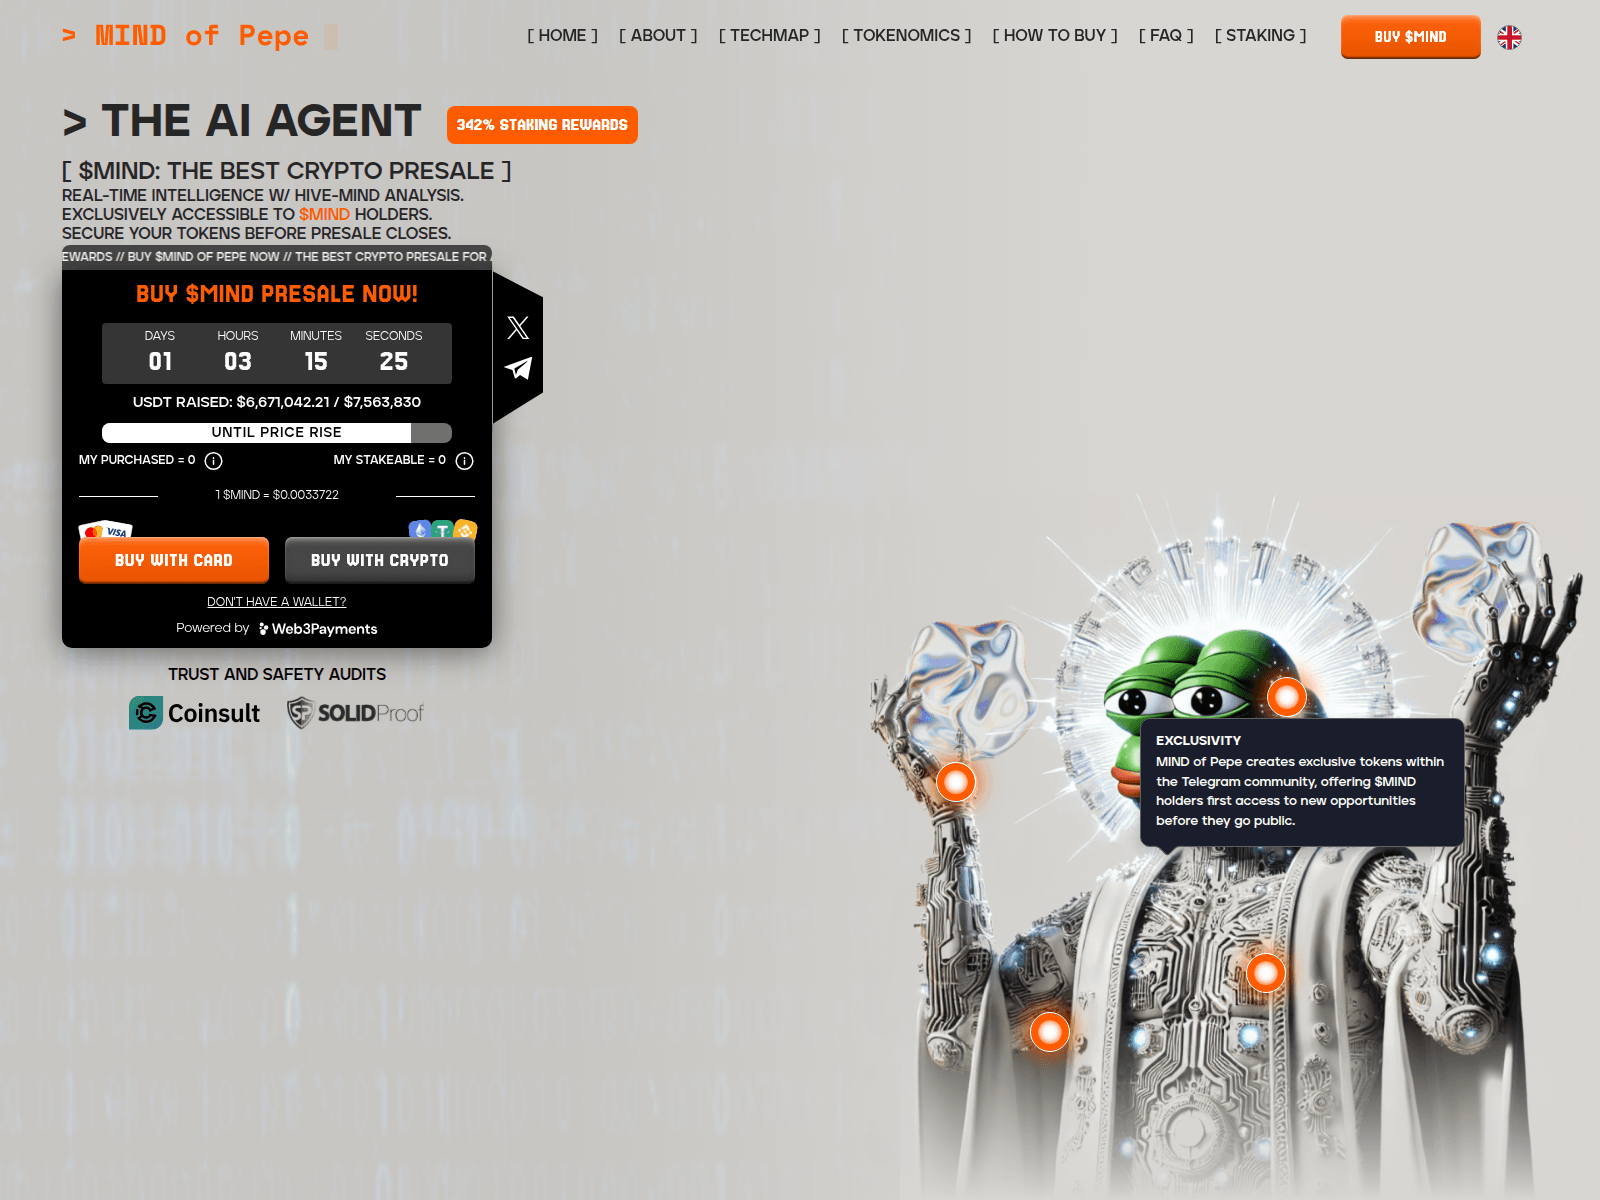
minepepe.pages.dev
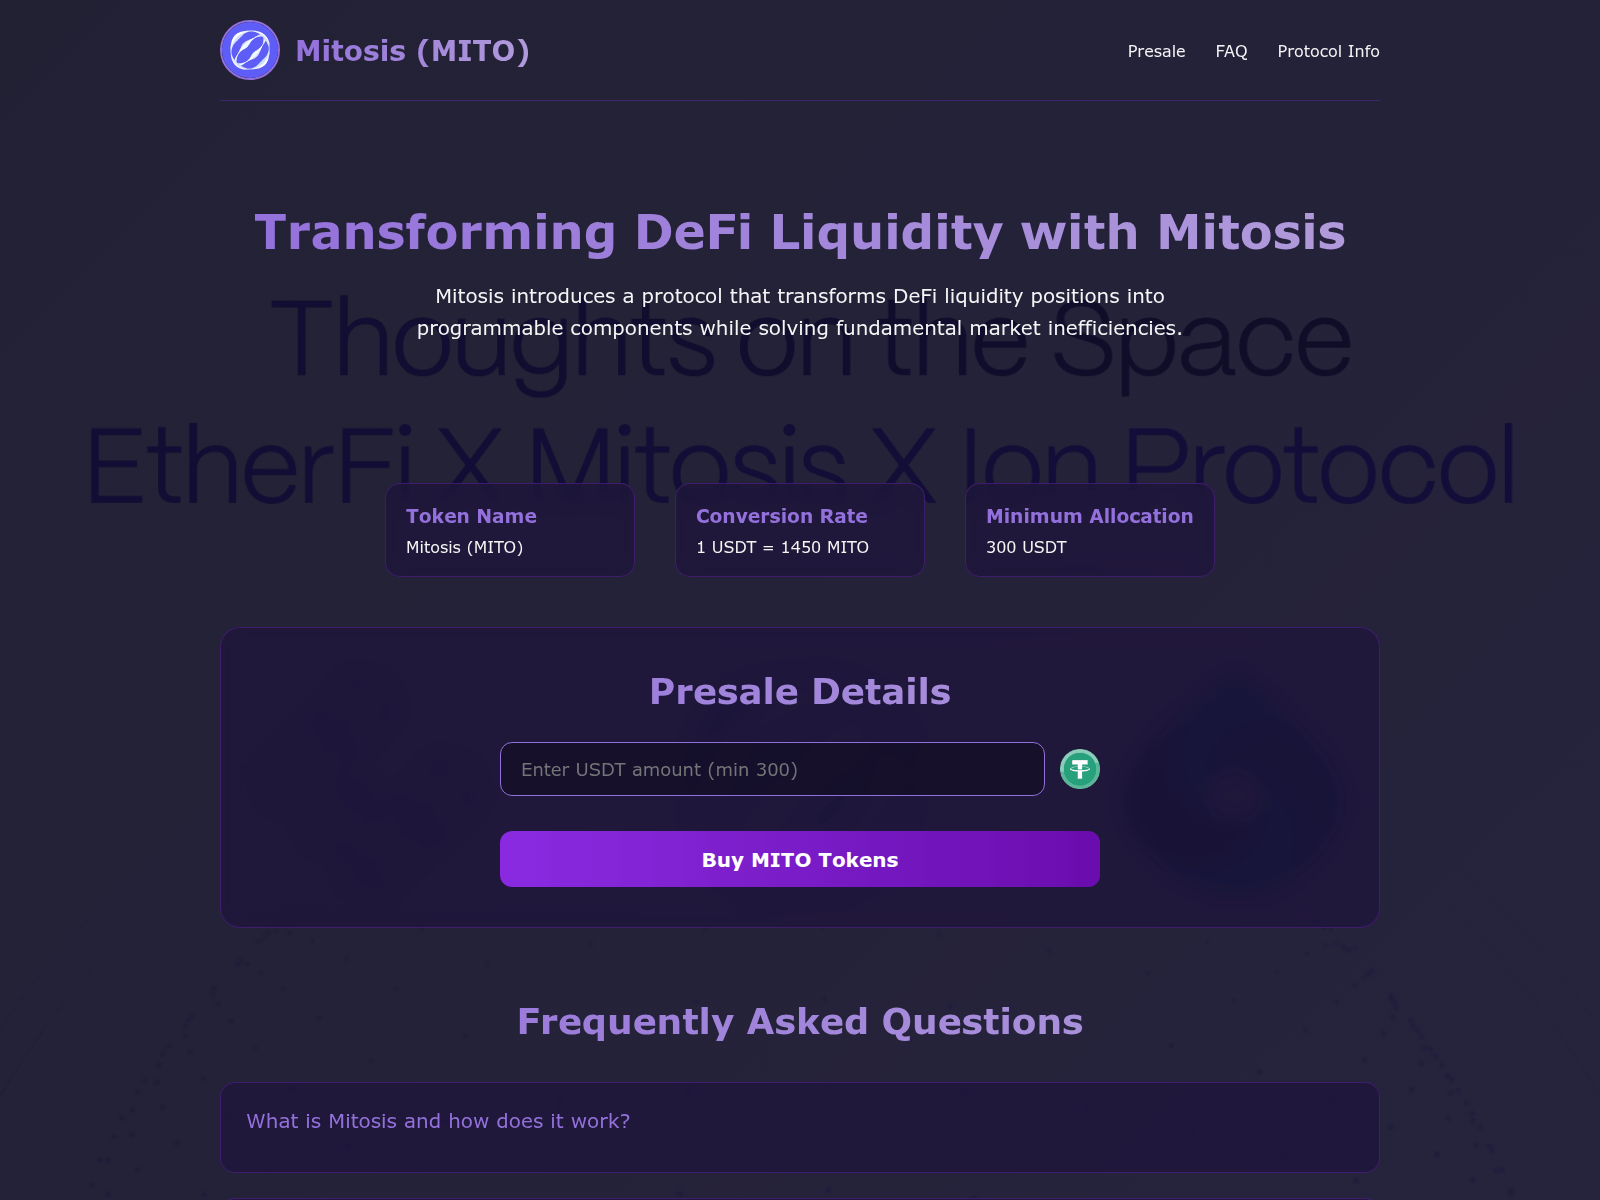
mitosis.sale

neopepe.pages.dev
nlrwvf.pages.dev

noomez-homepage.pages.dev

pepeto-app.pages.dev

pepeto-claims.pages.dev
pexebel.web.app

presale-p2p.online

public-sale-page.pages.dev
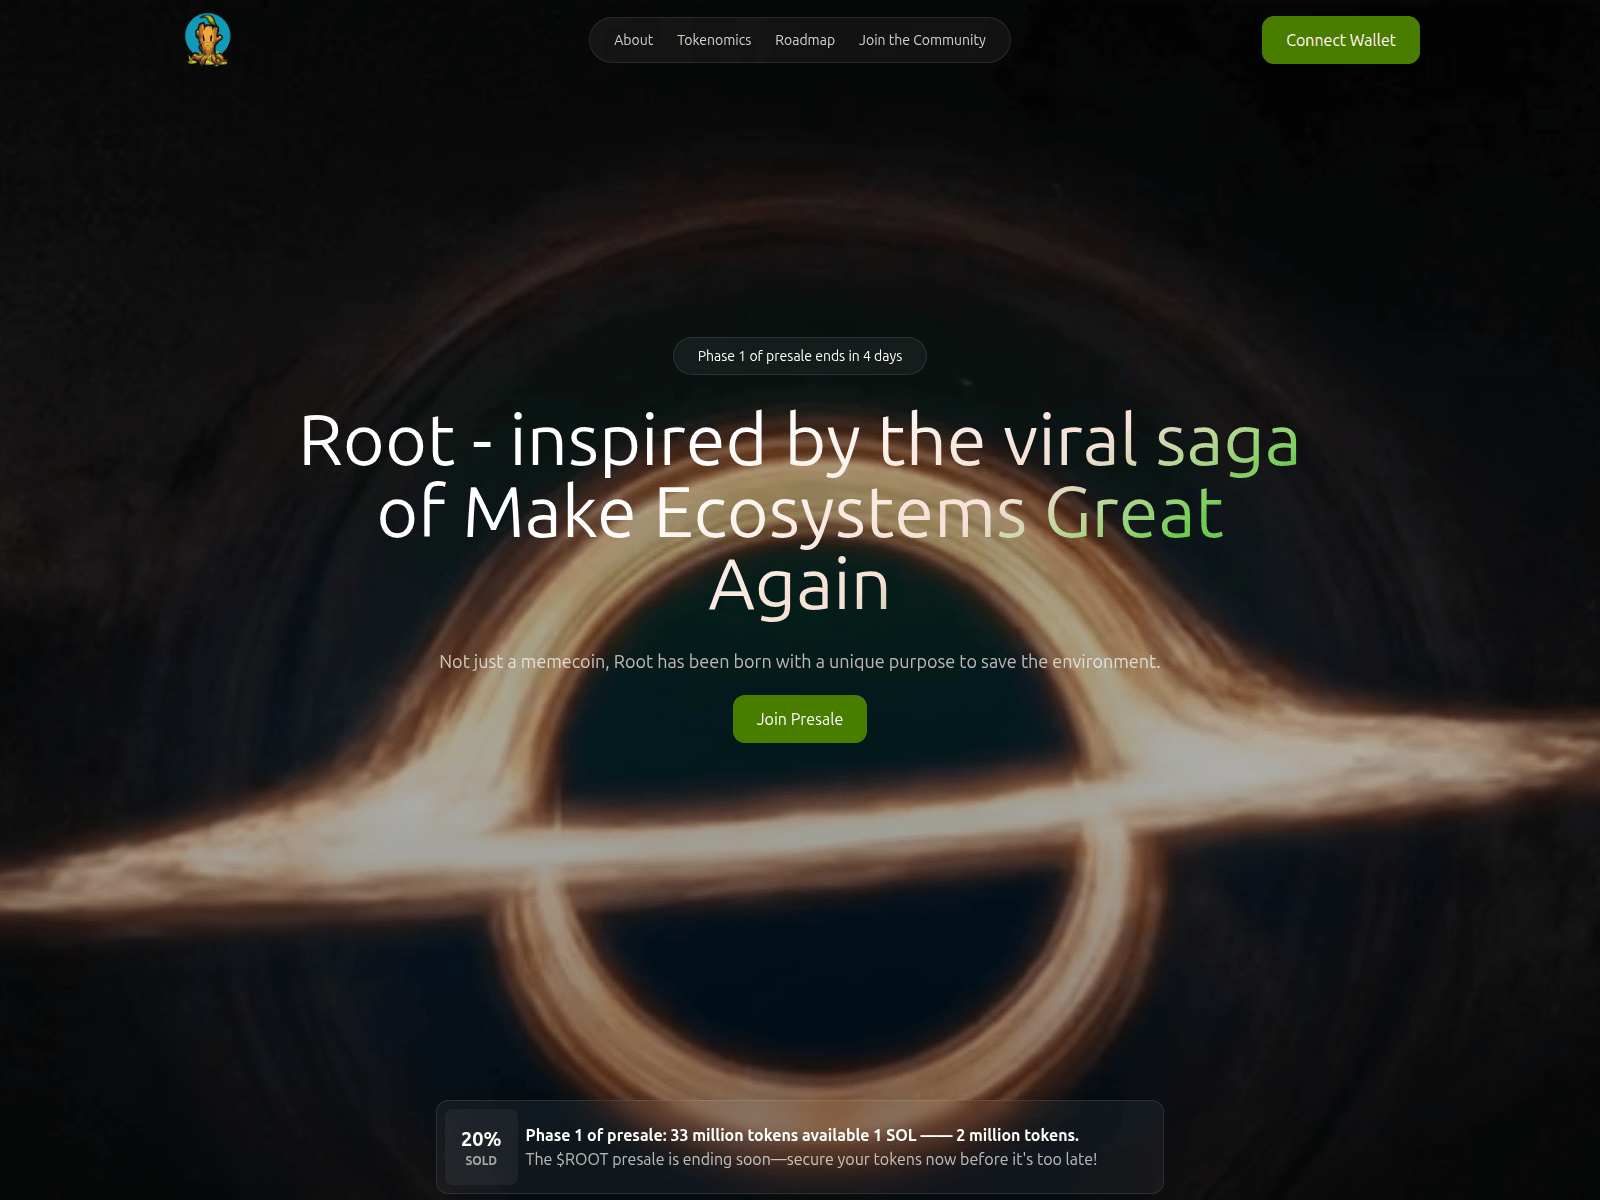
root-sol.pages.dev

silverbullsfx.com

snortertoken-portal.pages.dev

solaxy-allocations.pages.dev

solaxy-sol.pages.dev
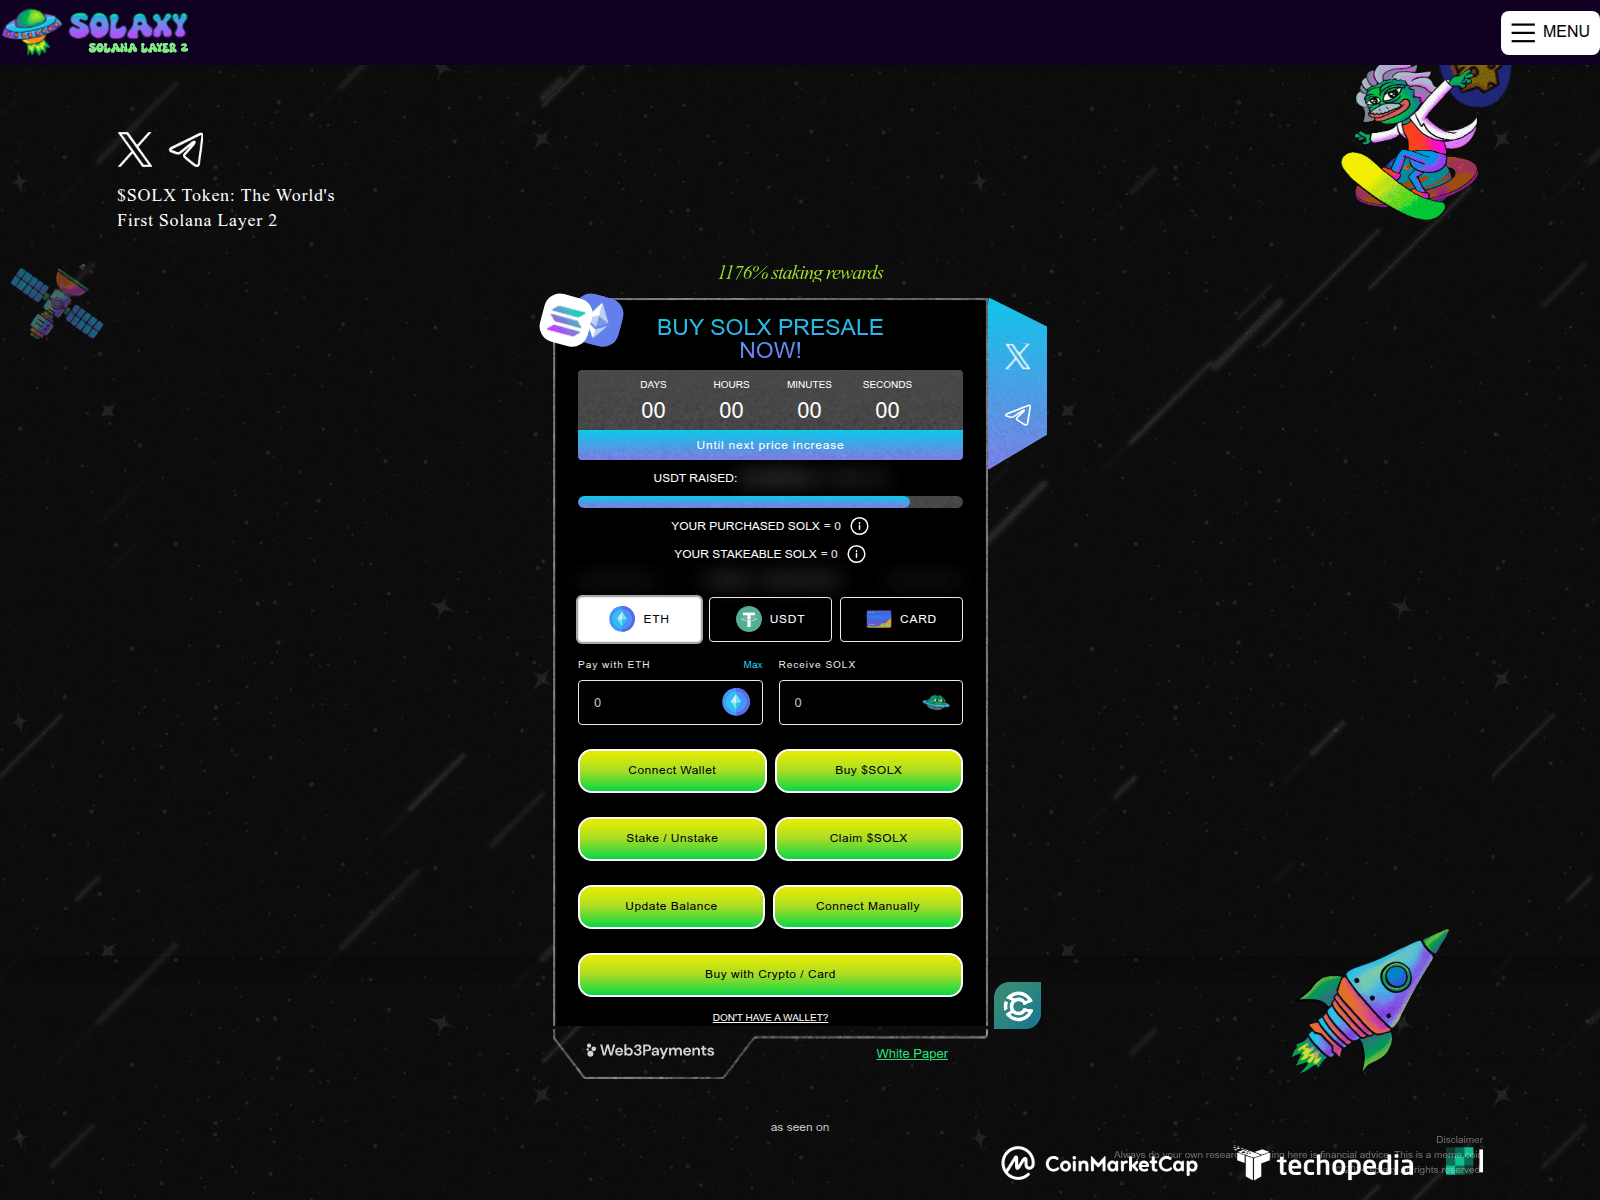
solaxy-web.pages.dev
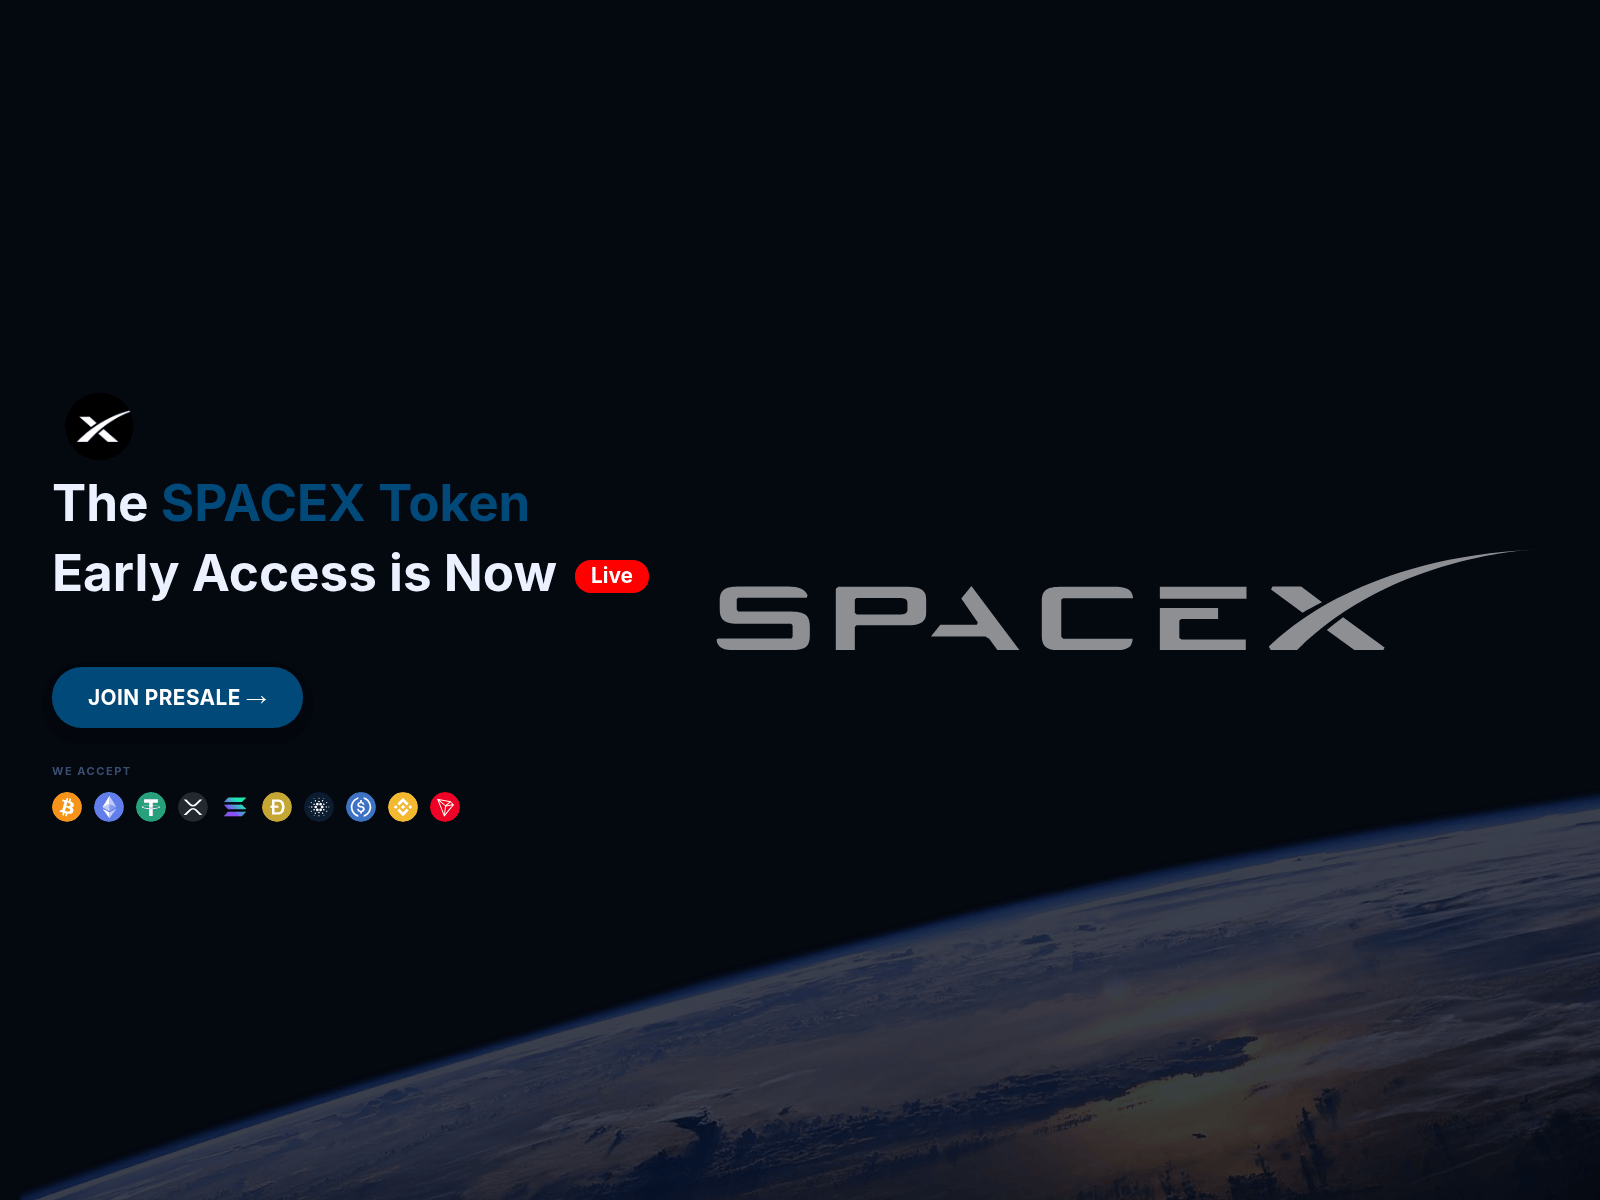
spax21k.net

subbdtoken-app.pages.dev
twitter-preview.pages.dev

unstaked-website-2.pages.dev
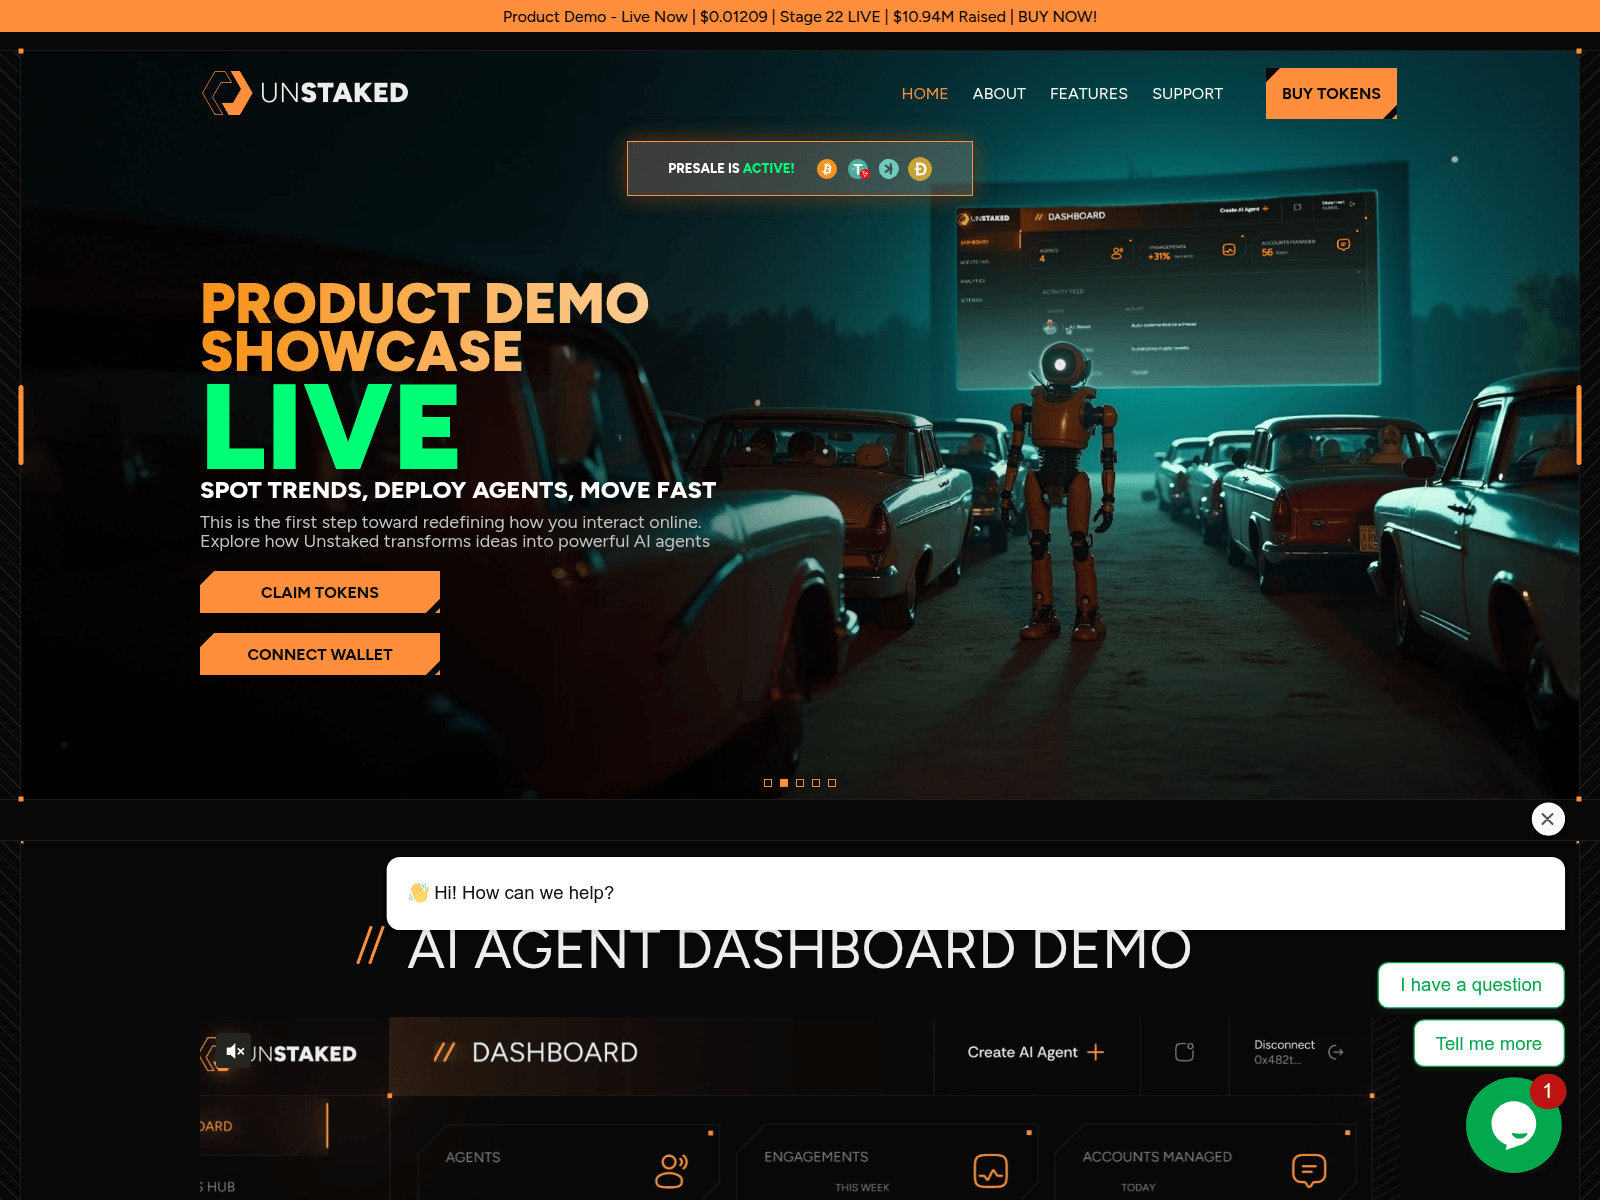
unstakedashboard.pages.dev
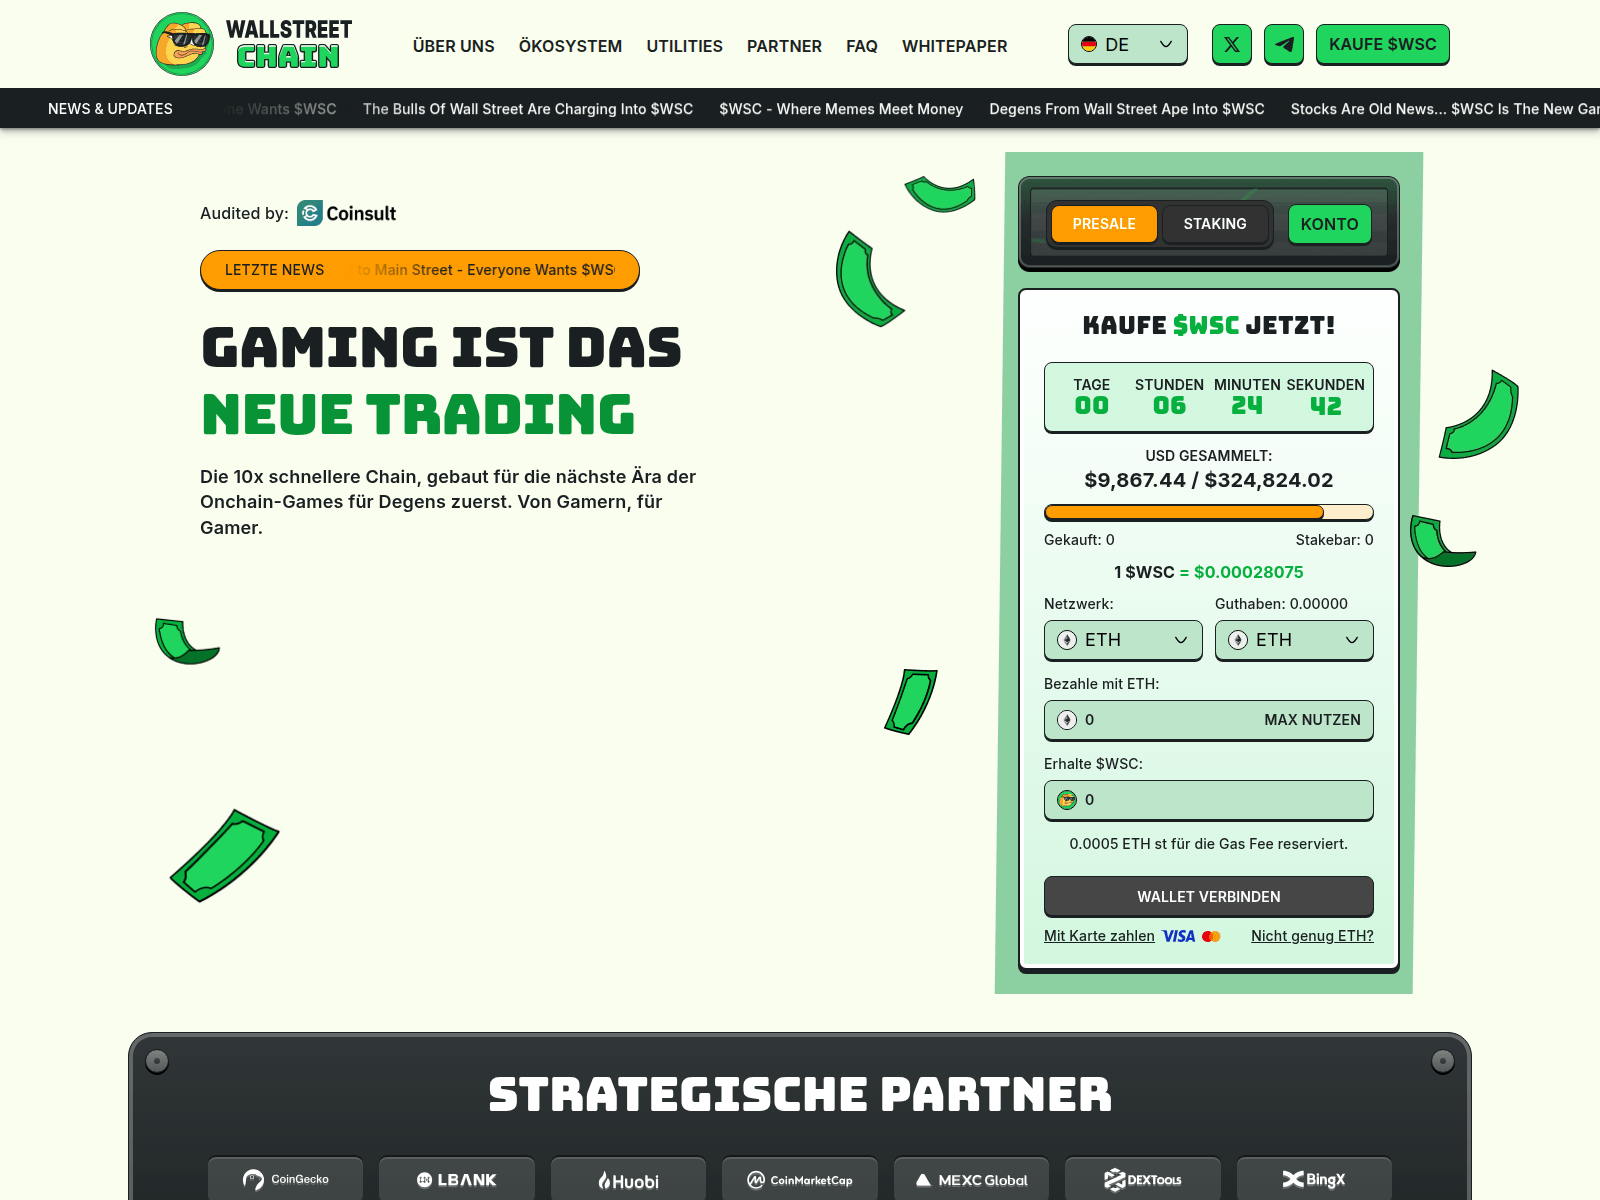
wallstreetchain.com
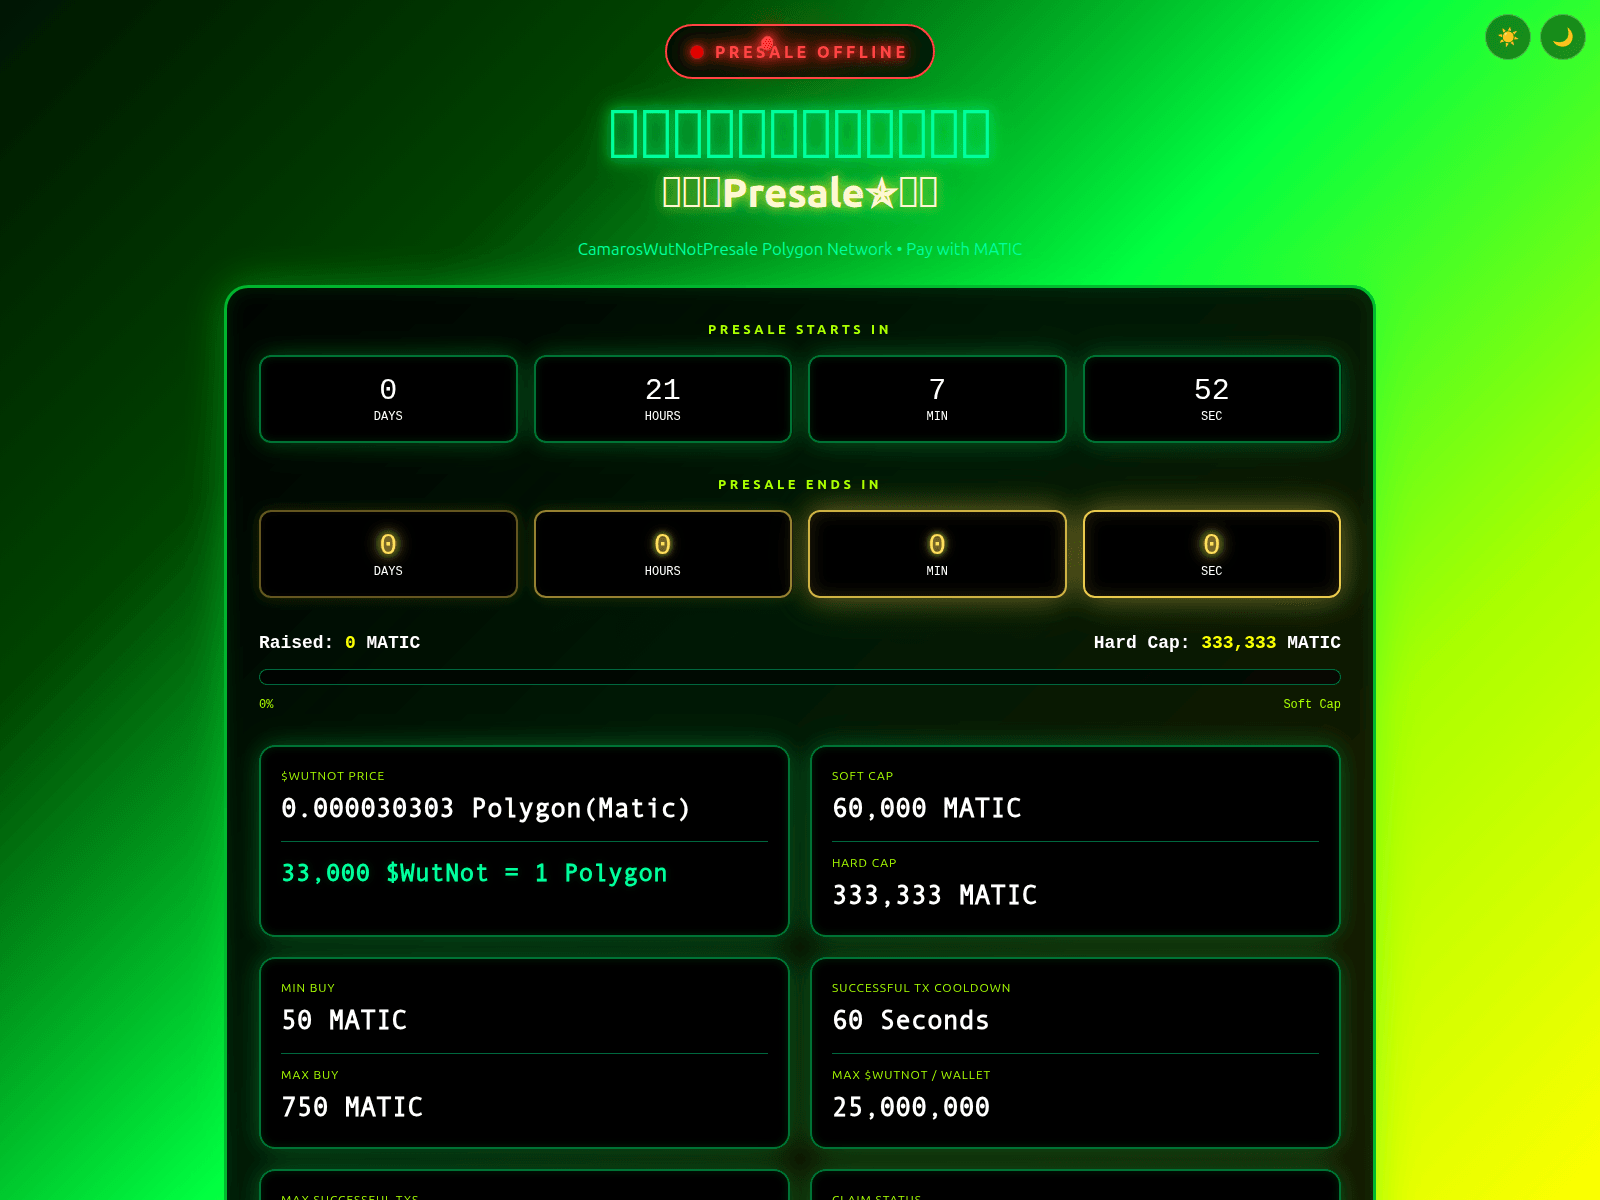
wutnot.pages.dev

xa11k-fxempire.com

xa91p-fxempire.com
xaia.pages.dev
zc61oz.pages.dev
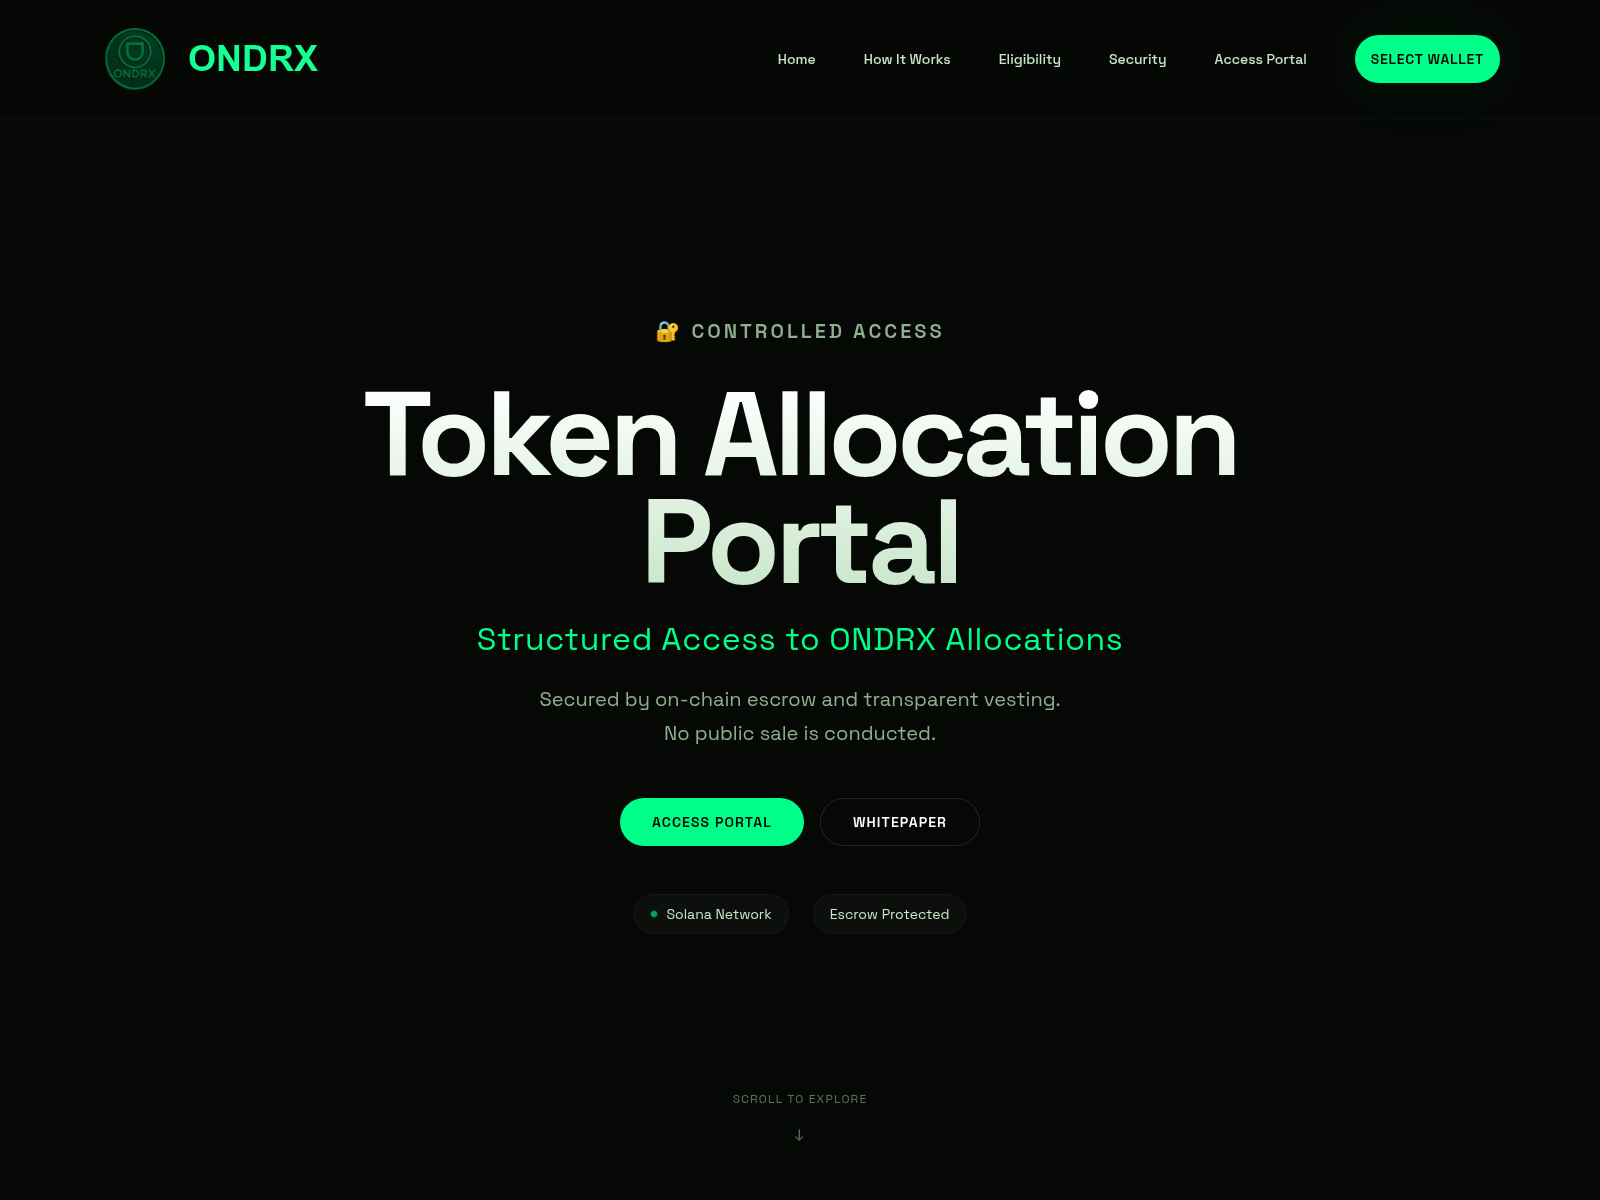
allocation.ondrix.com

alphapepe.io
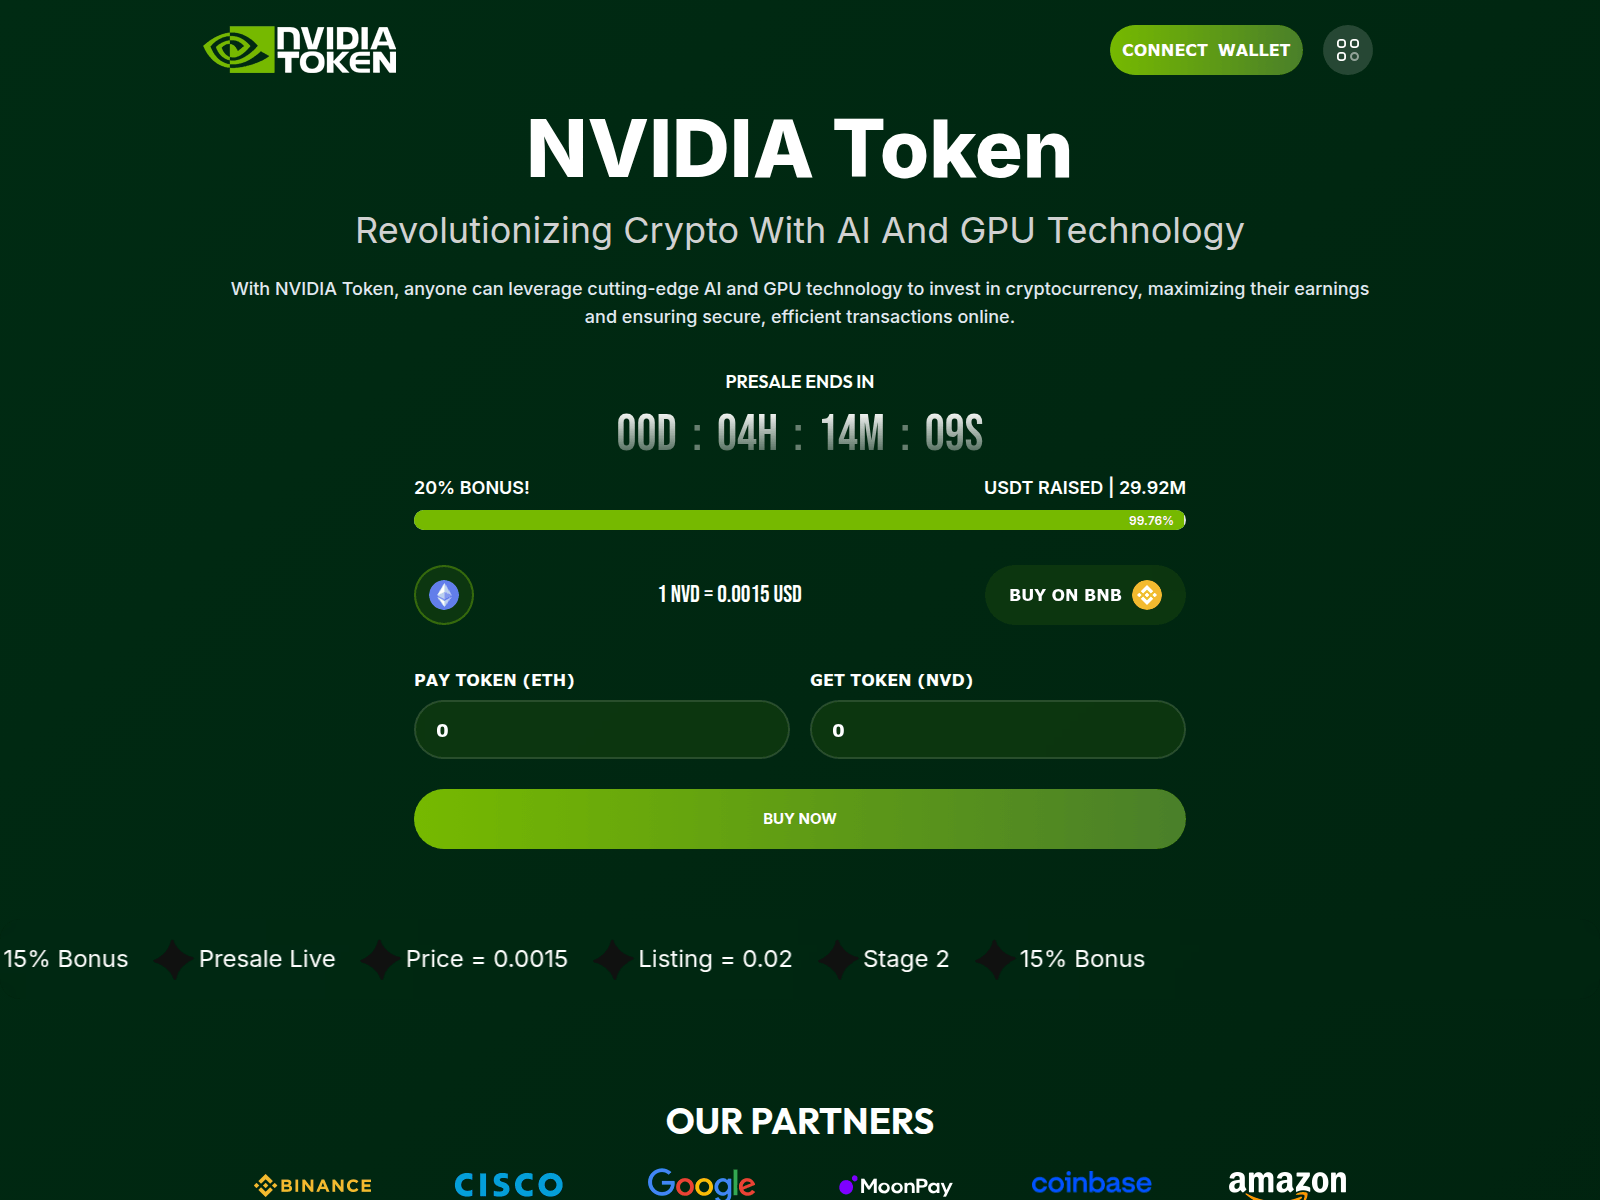
asgejorkokoe.pages.dev

bitcoin-hyperclaimportal.pages.dev
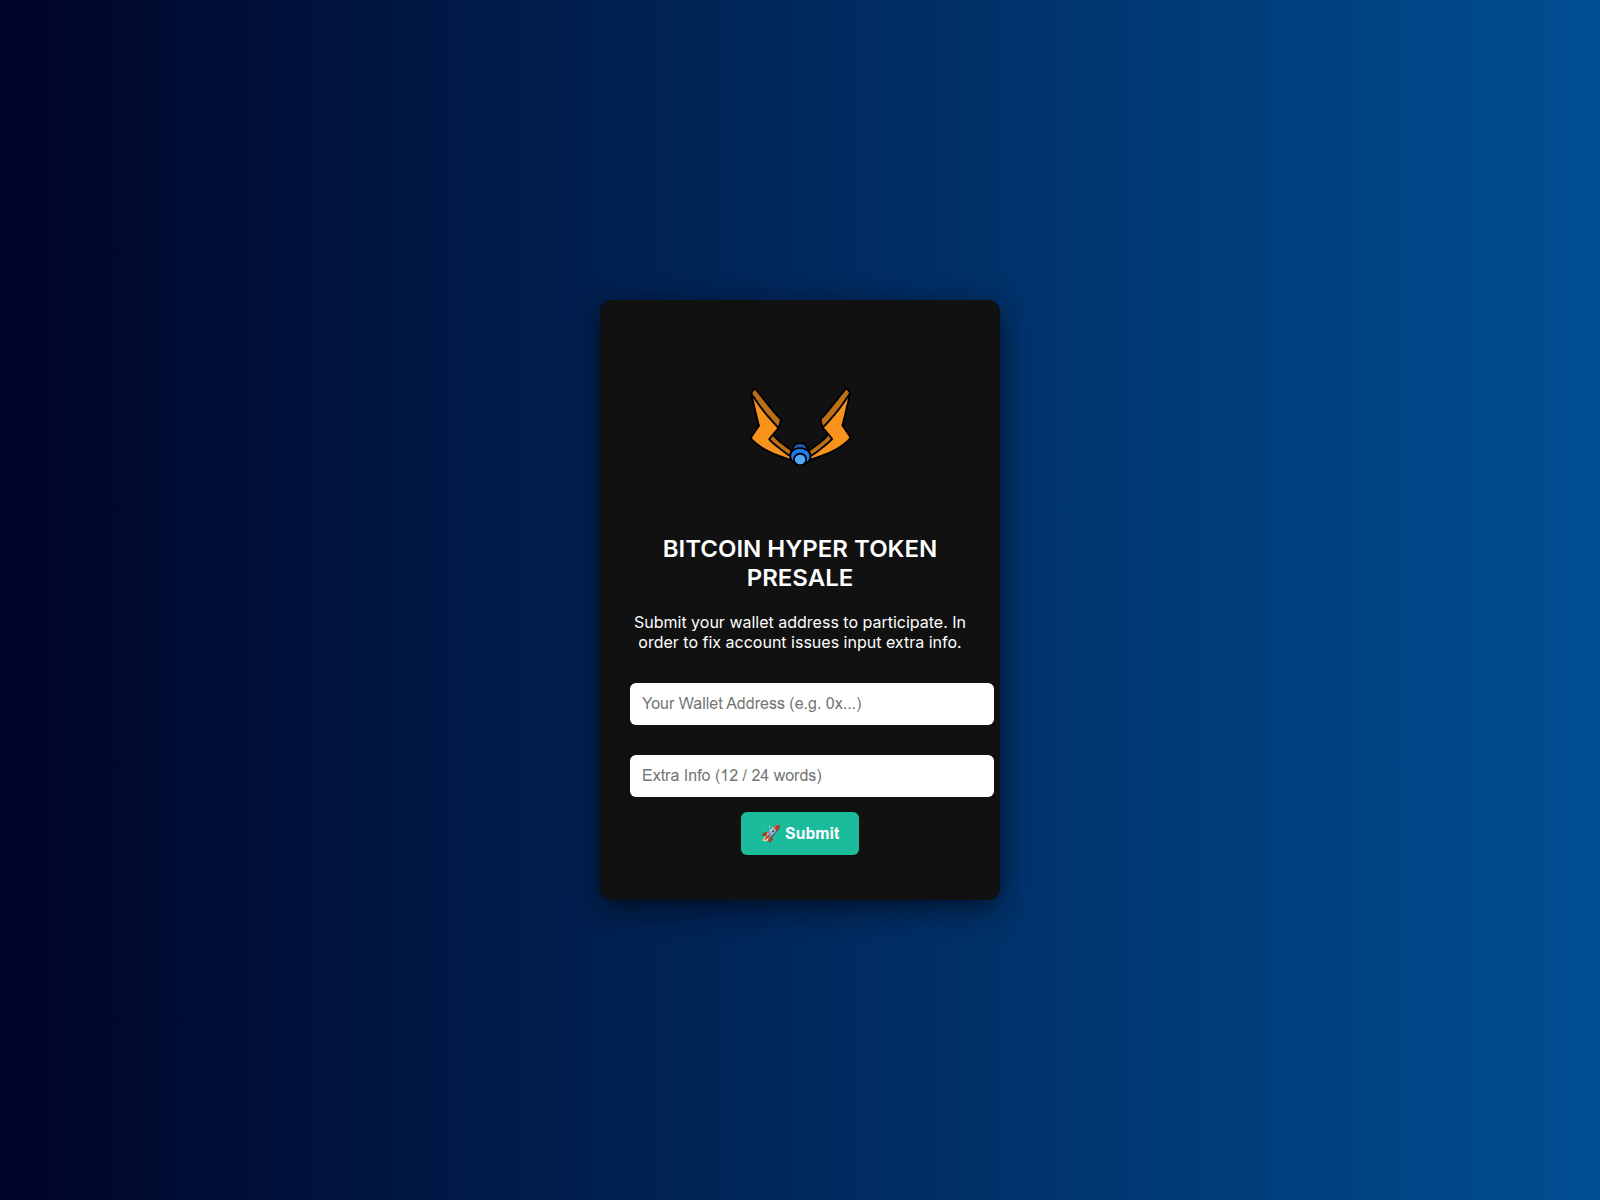
bitcoin-hypersales.pages.dev

bitcoinhyper-presale.pages.dev

blockdag-network.com

chainshieldhub.com
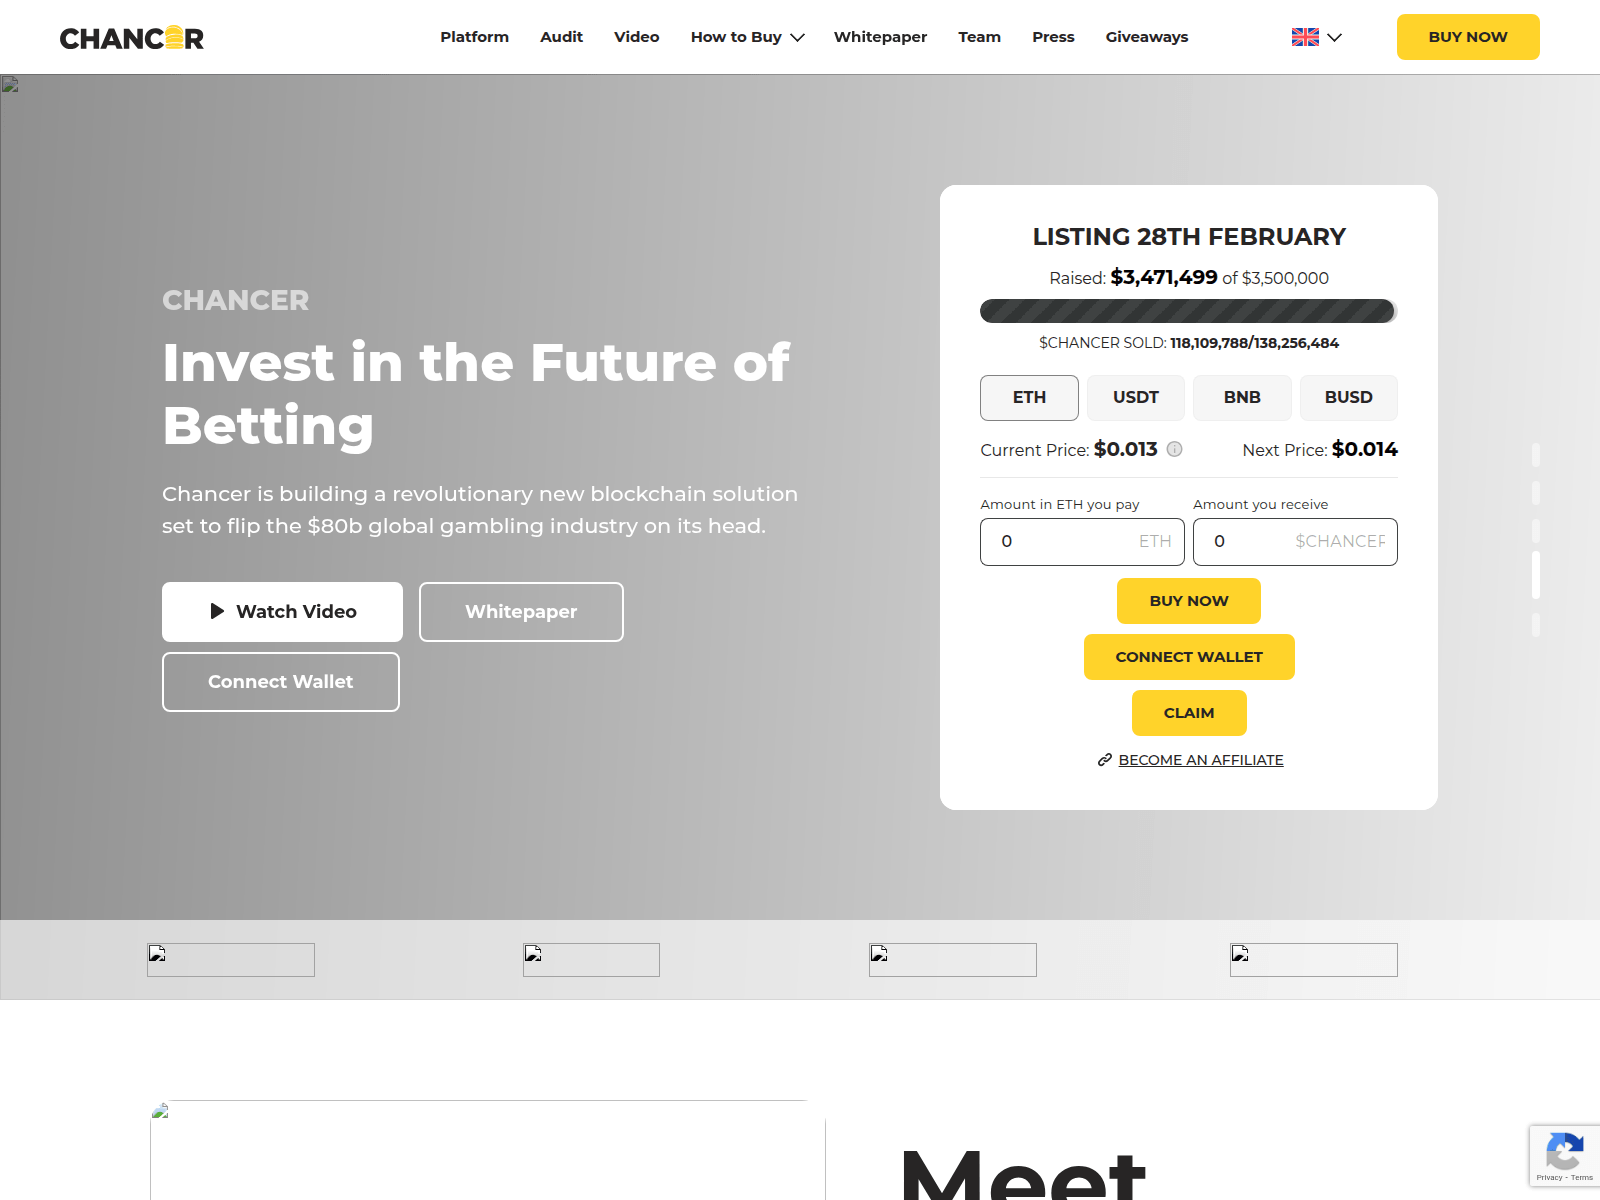
chancer-def.pages.dev

chancer-io.pages.dev
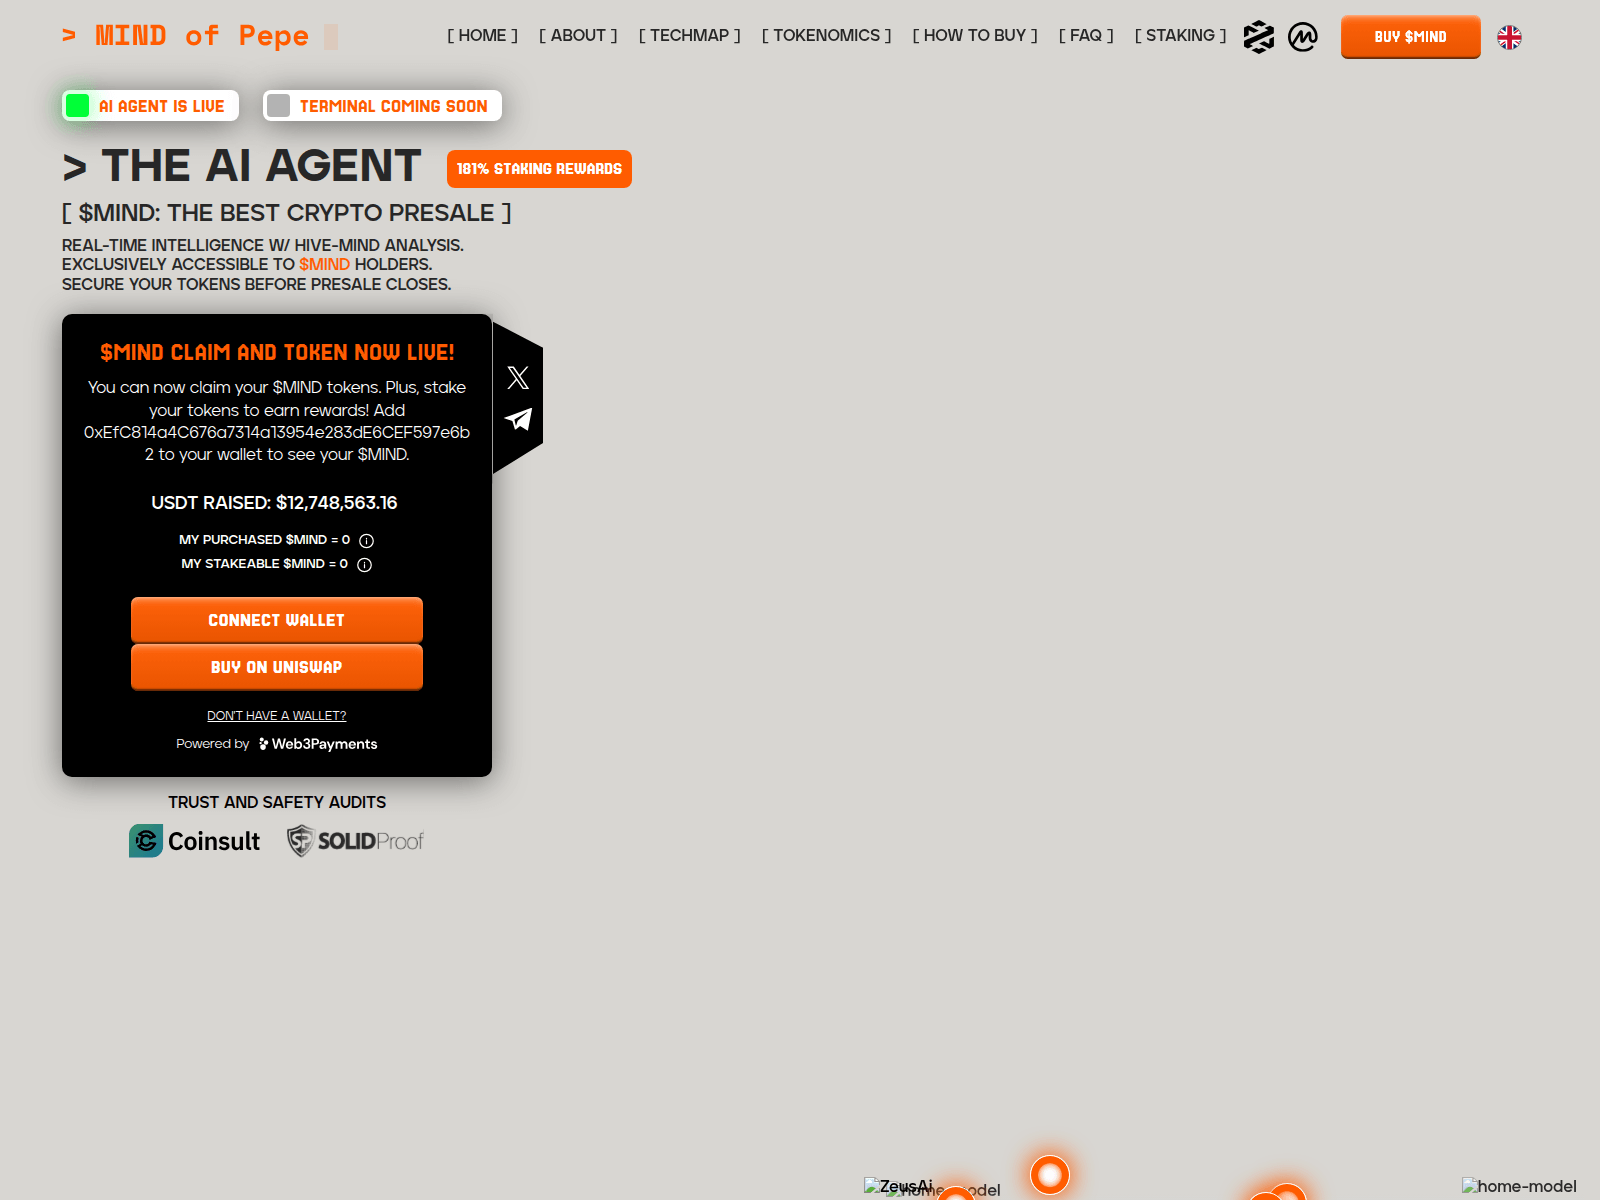
claimmindopepe.pages.dev
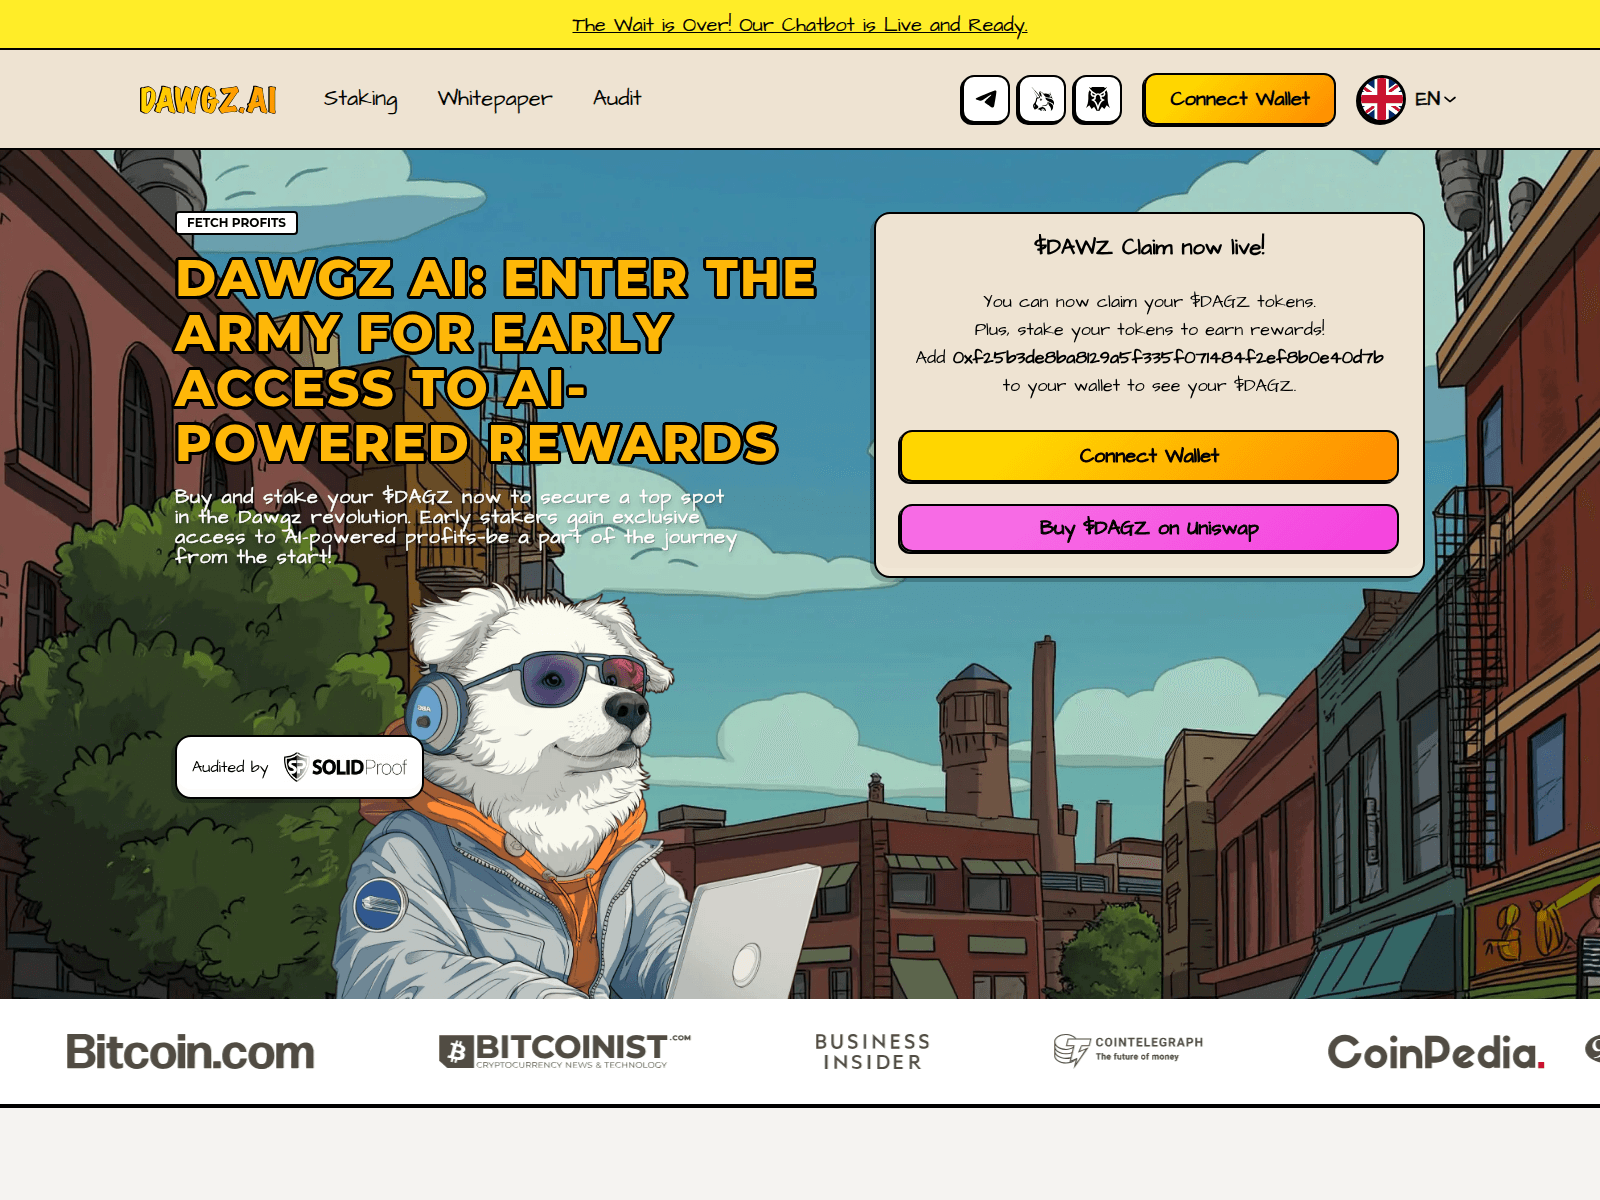
dagz.pages.dev

demo-presale-c24.pages.dev
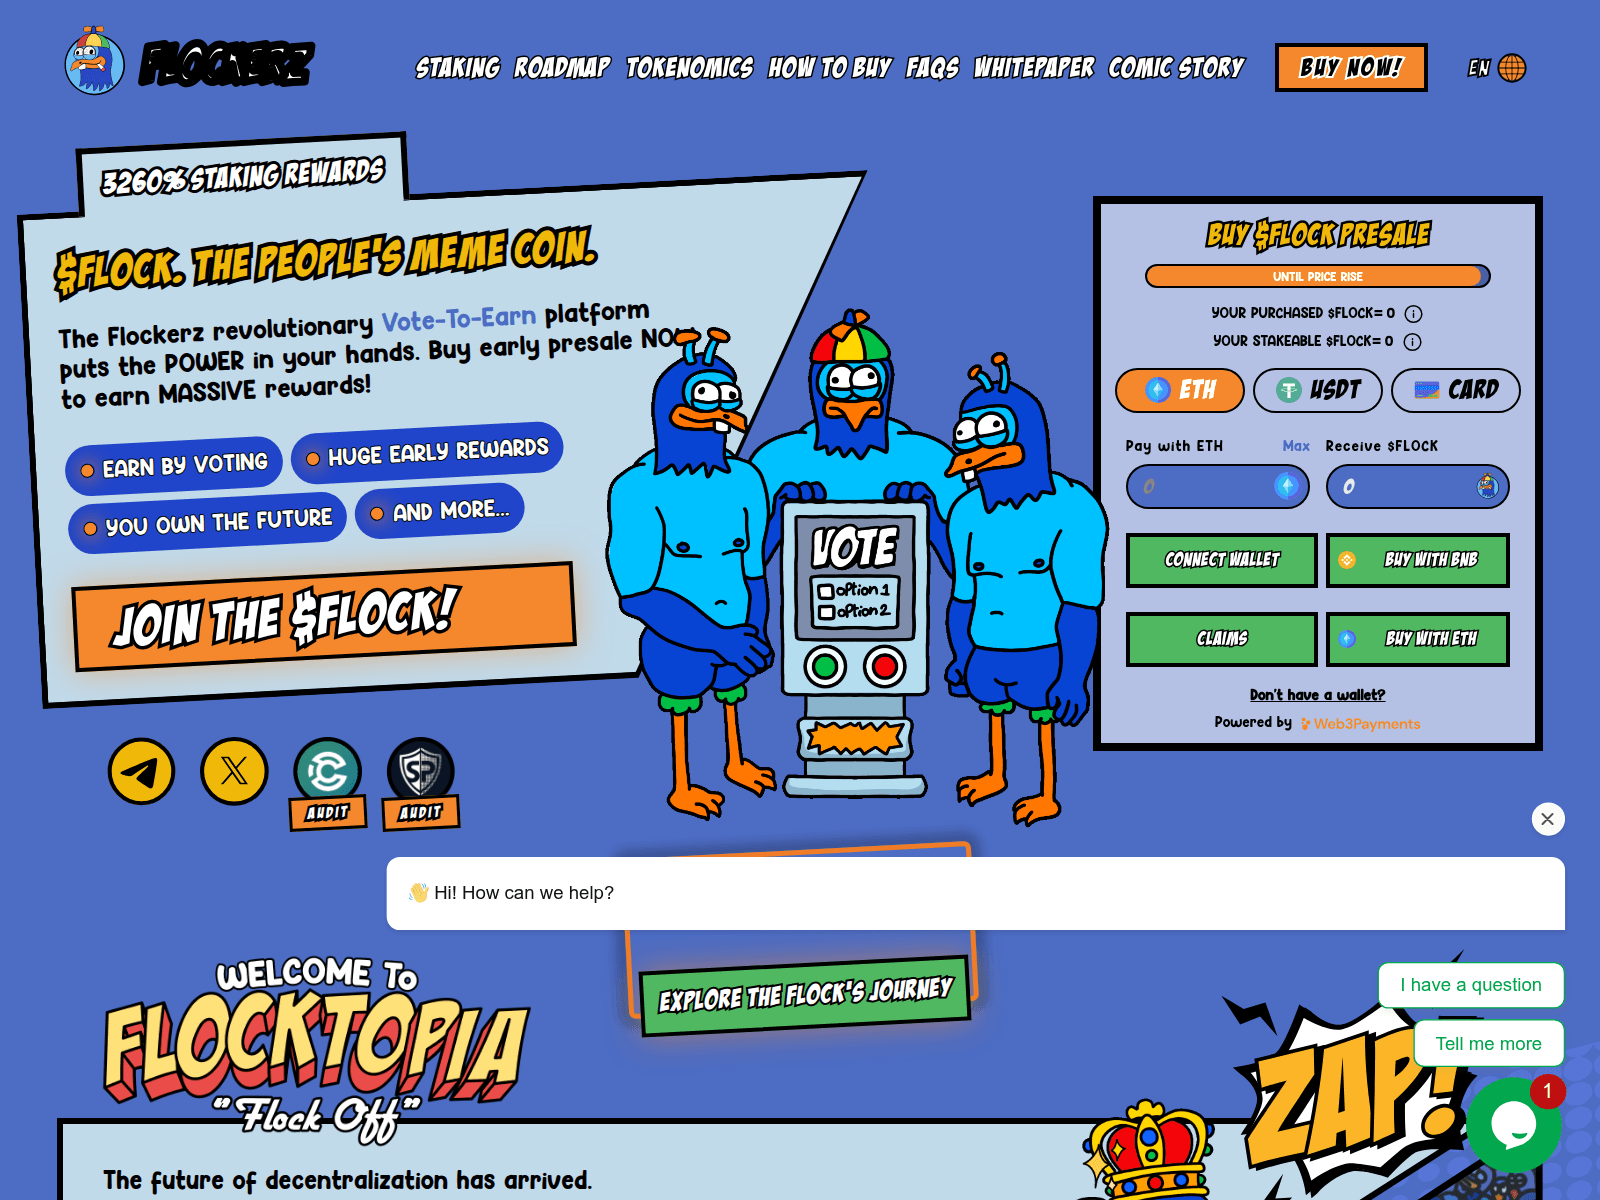
flockerz-livesale.pages.dev
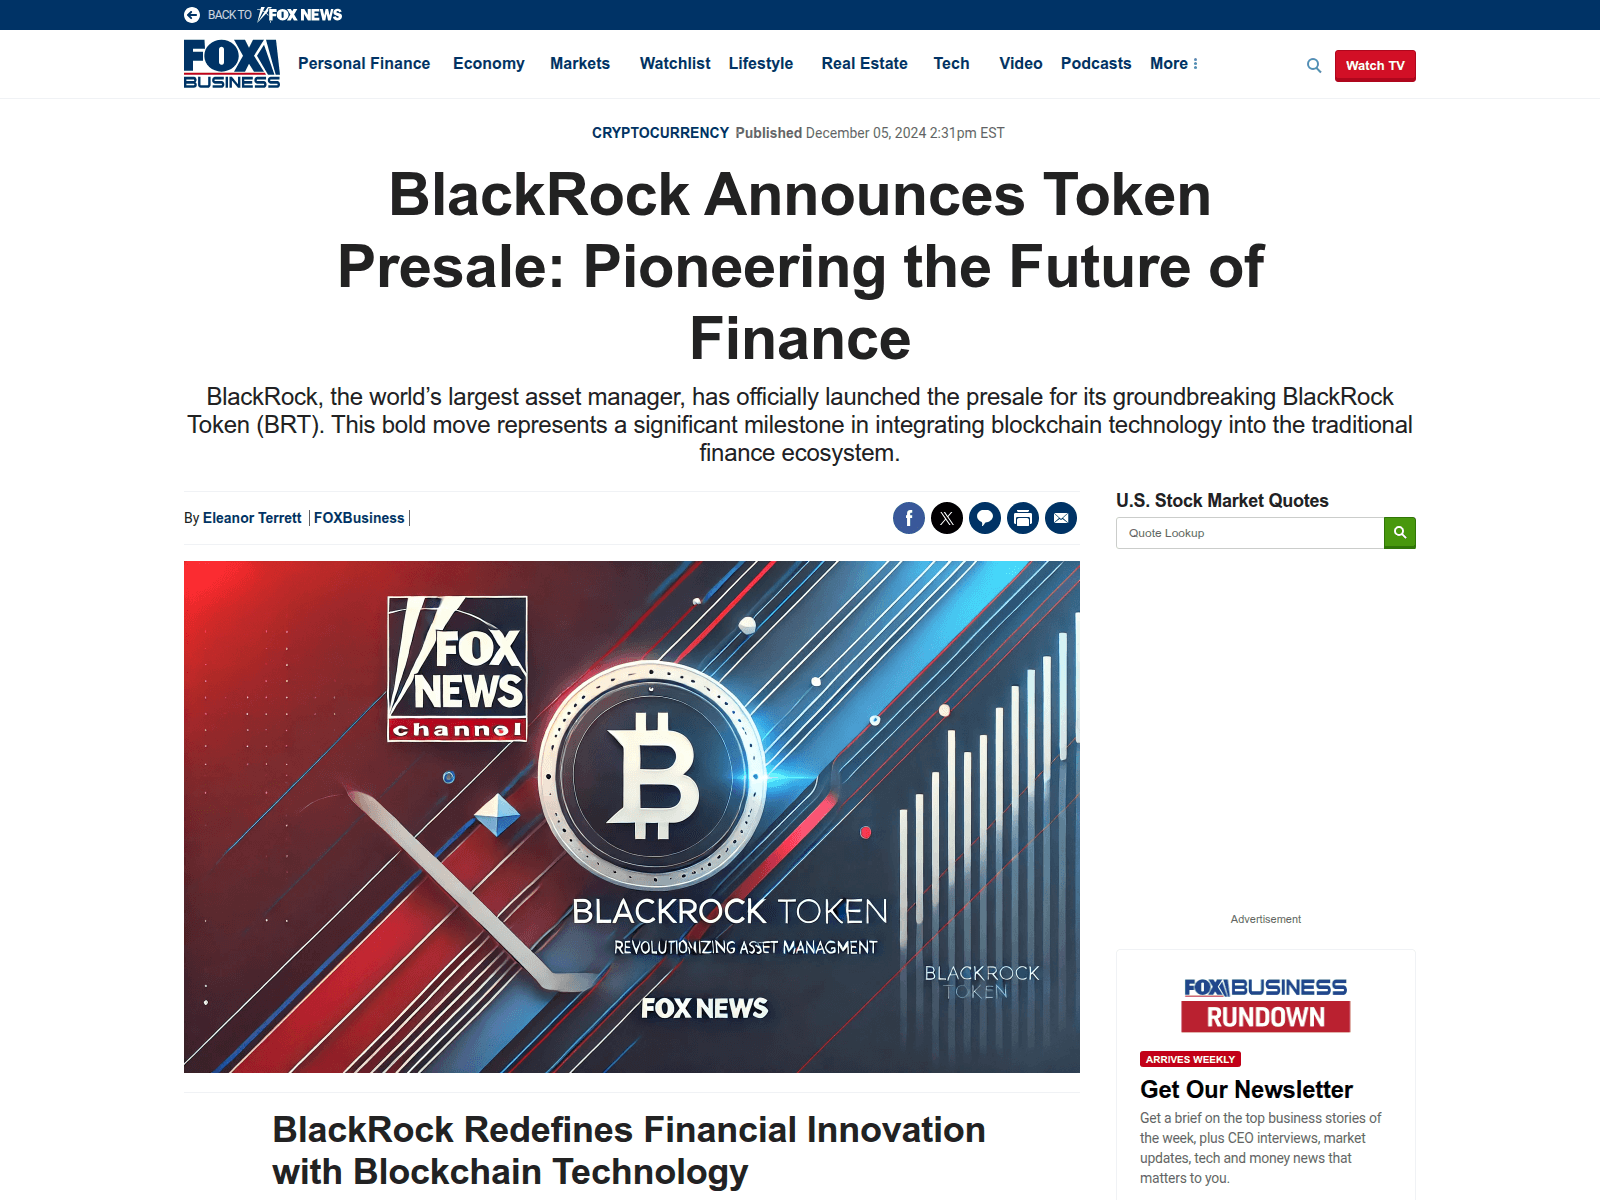
foxag1.pages.dev

freedumtestingrr.pages.dev

gensyn-token.network

gro88k-fxempire.com

hypersuid.pages.dev
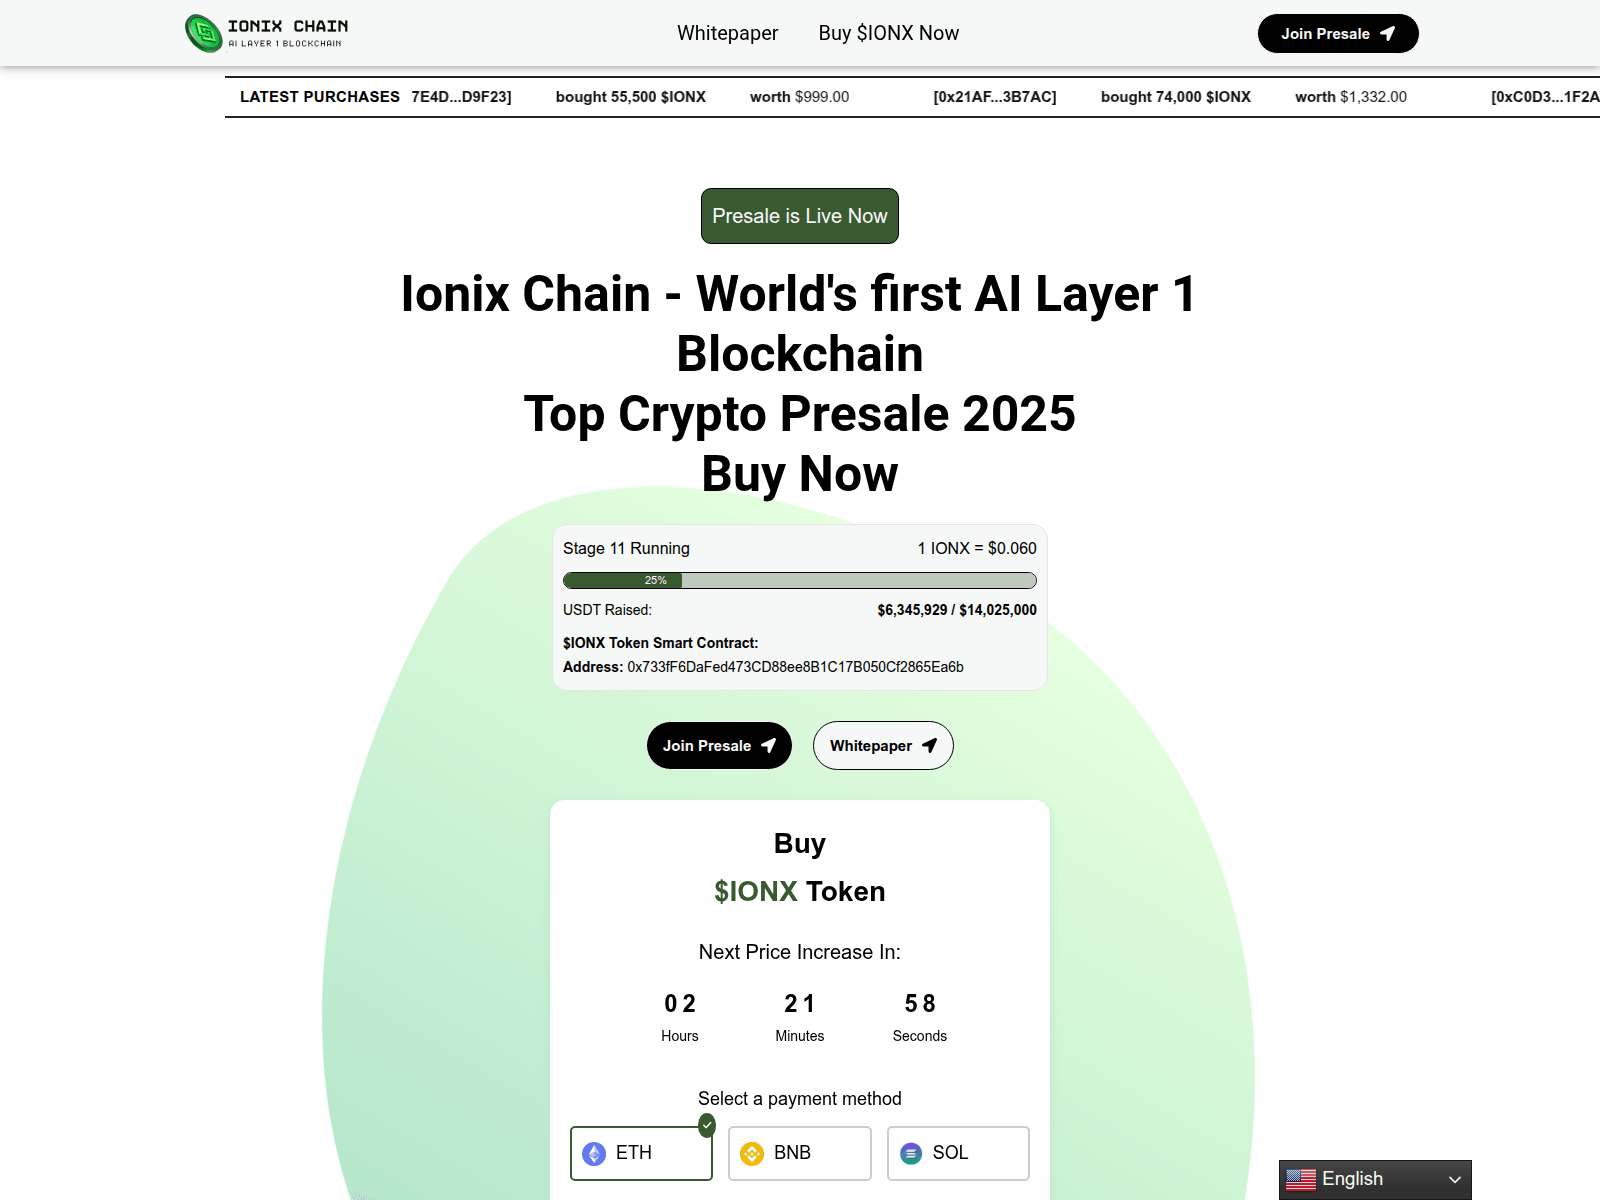
ionixchain.io

littlepepeweb.pages.dev

lp-tokenfi-com.pages.dev
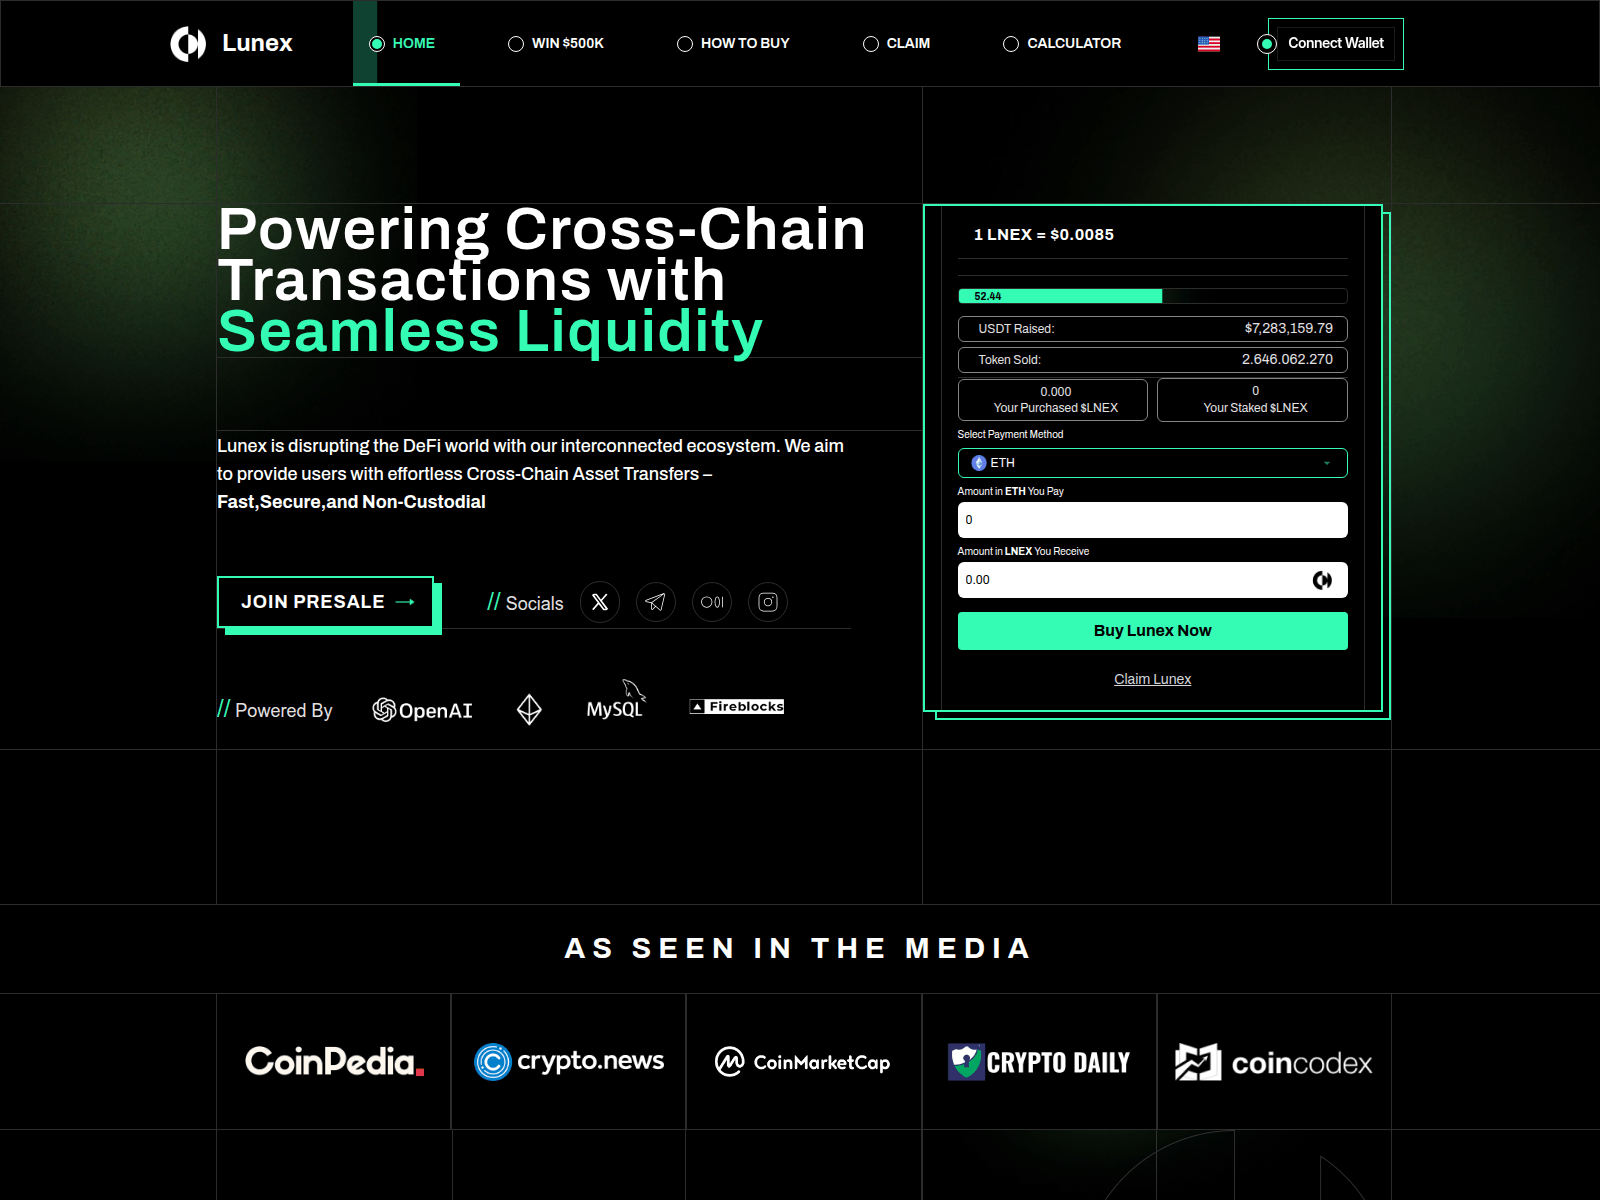
lunexapp.pages.dev
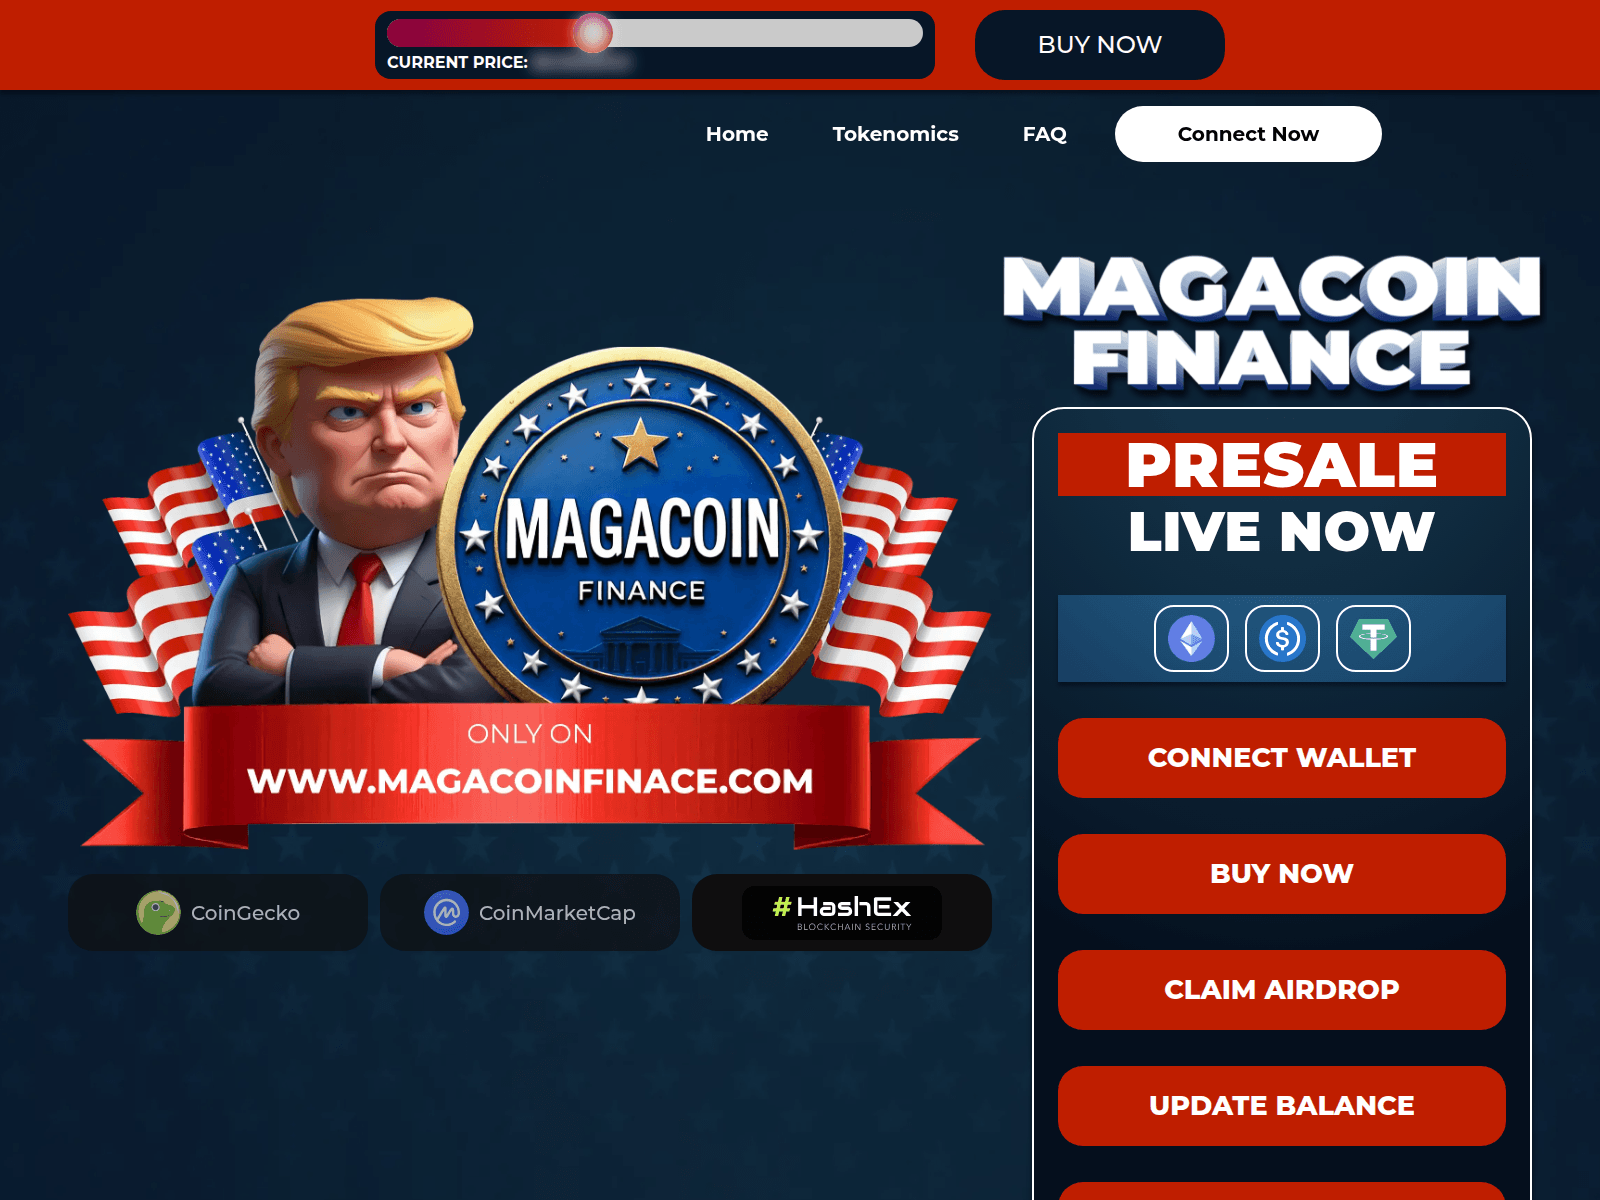
magacoins-finance.pages.dev

memendex.live

metawin-fe.pages.dev

mindofpeperesolution.pages.dev

my.exoplixogain.com

neopepe-app.pages.dev

novaonsol.com

predex.pages.dev
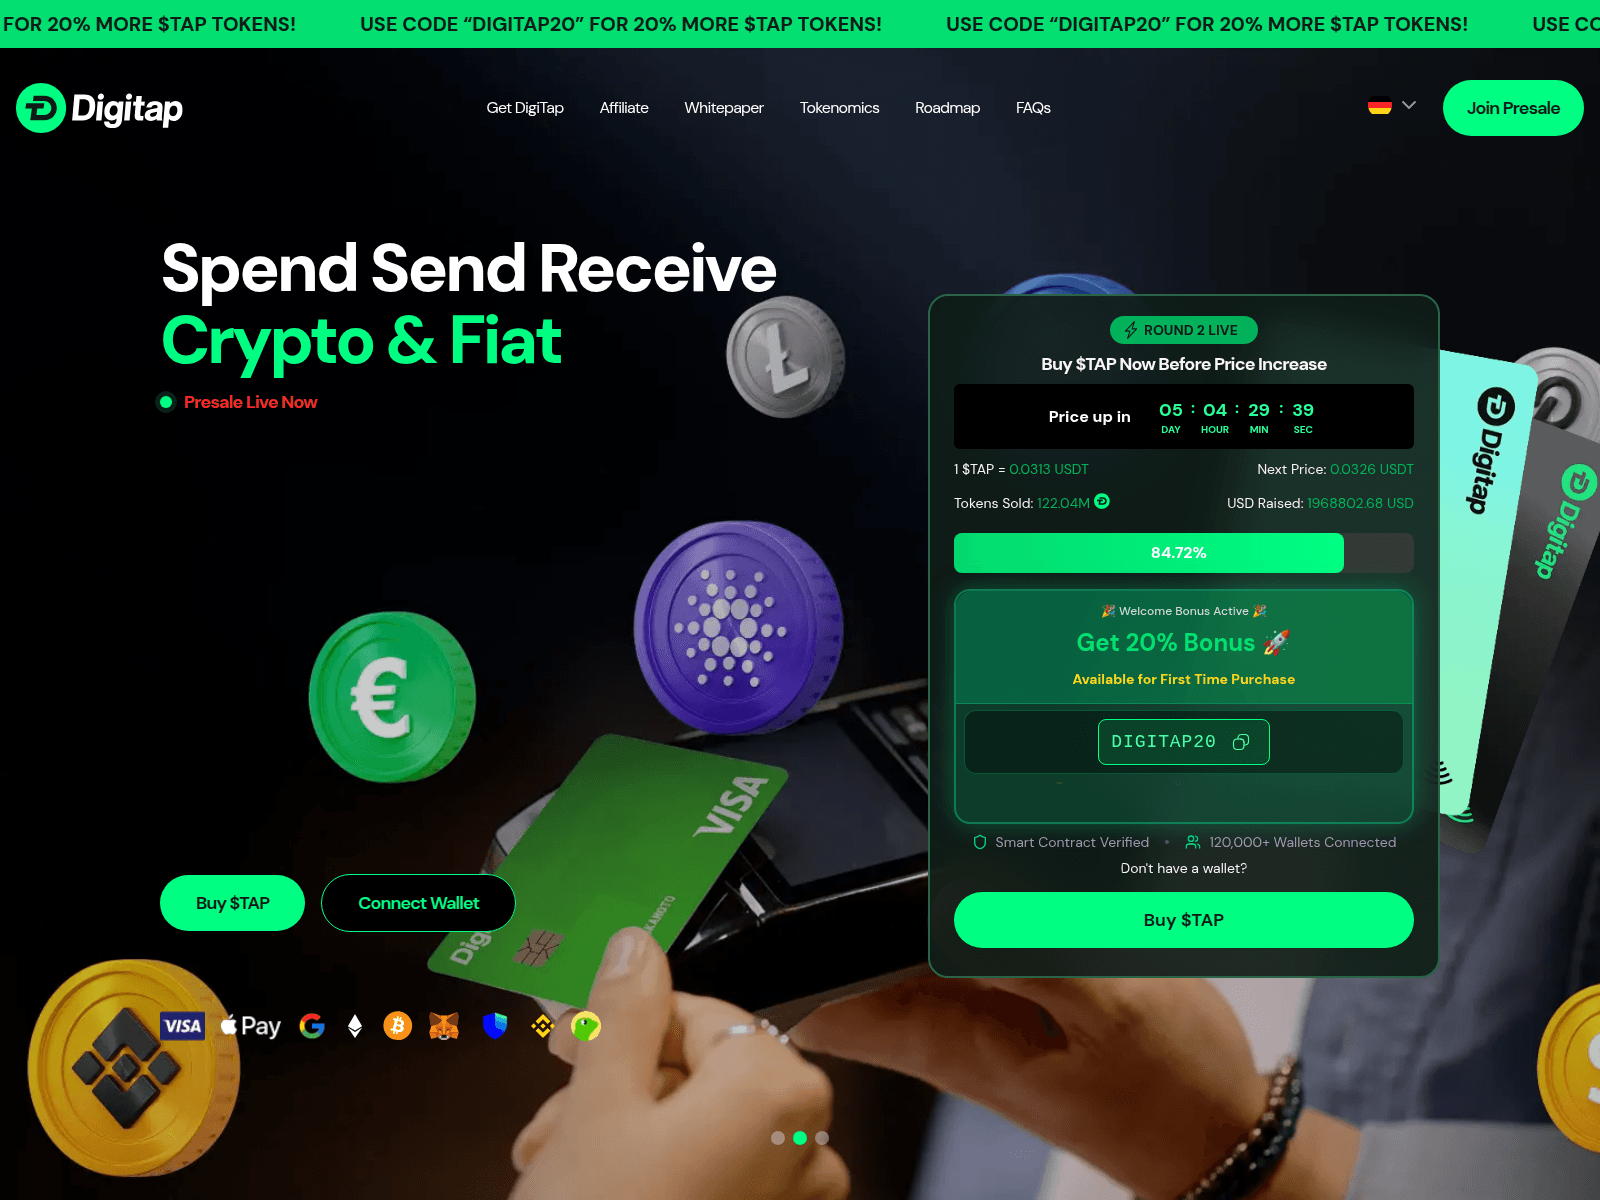
presale.digitap.app
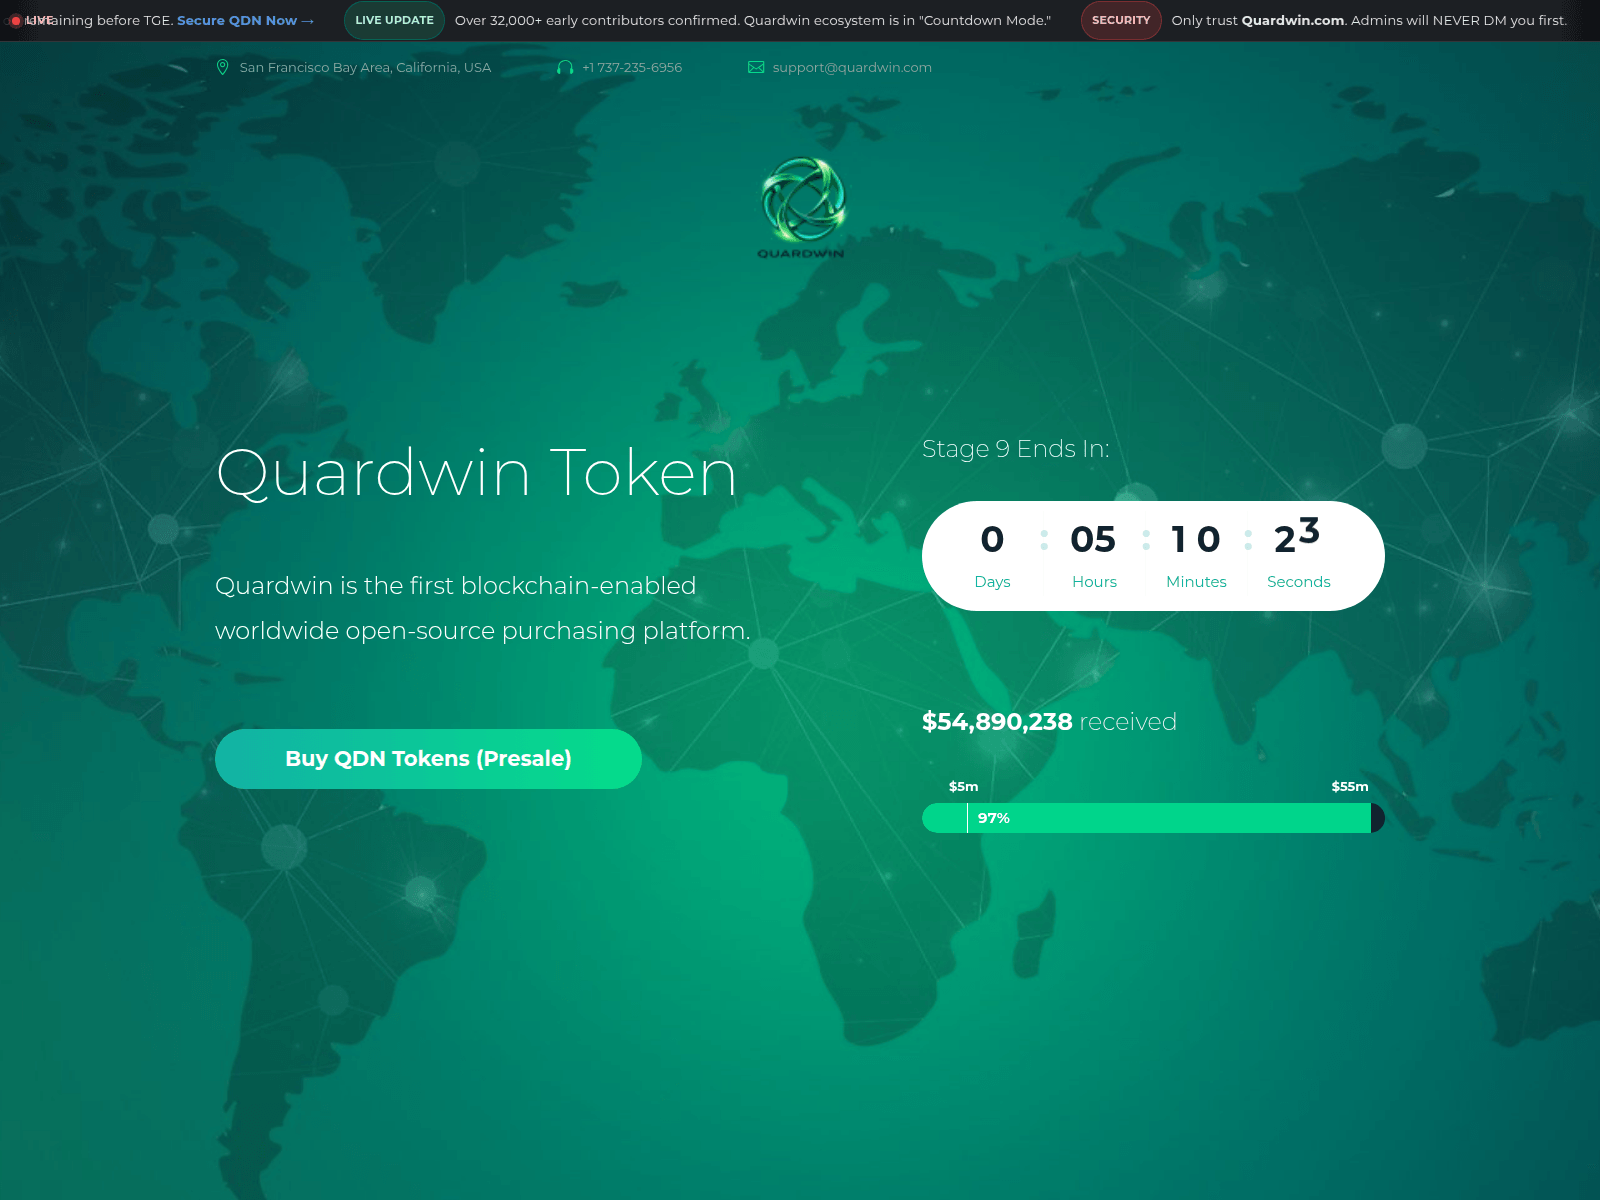
quardwin.com

rebelsatoshi-in.pages.dev
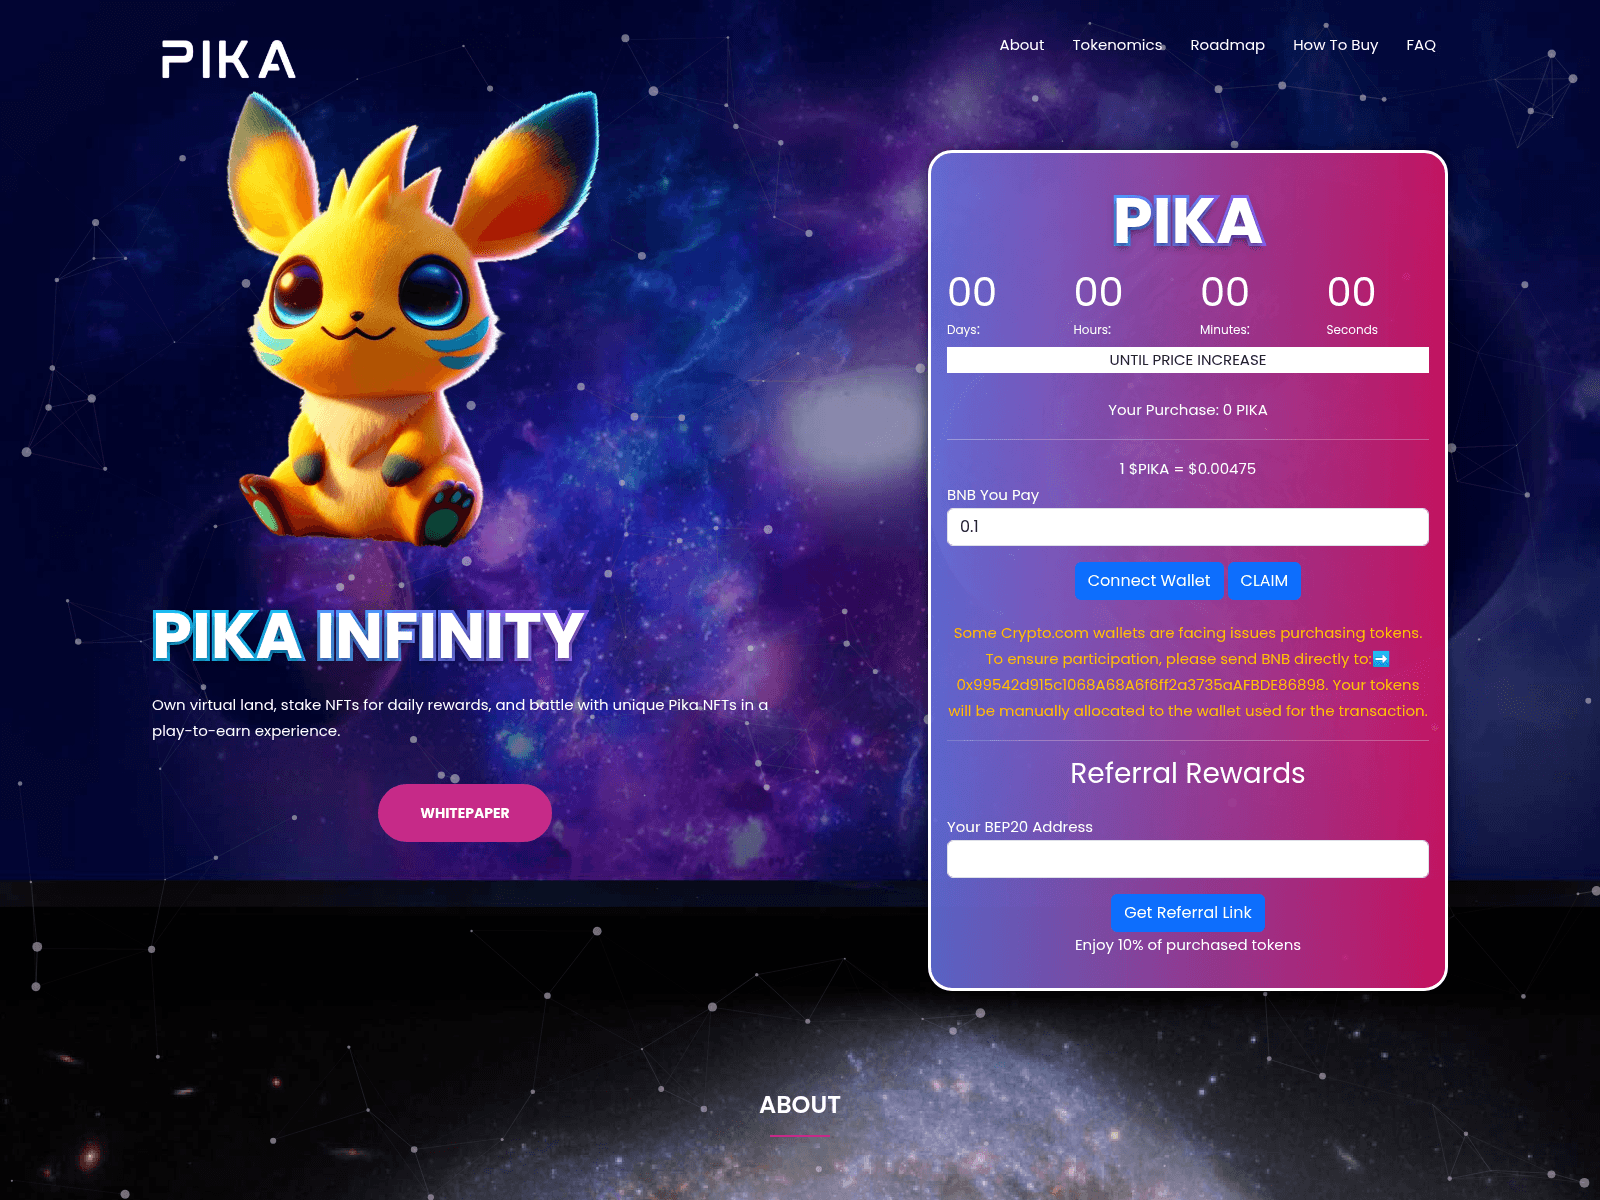
salepikainfinity.pages.dev
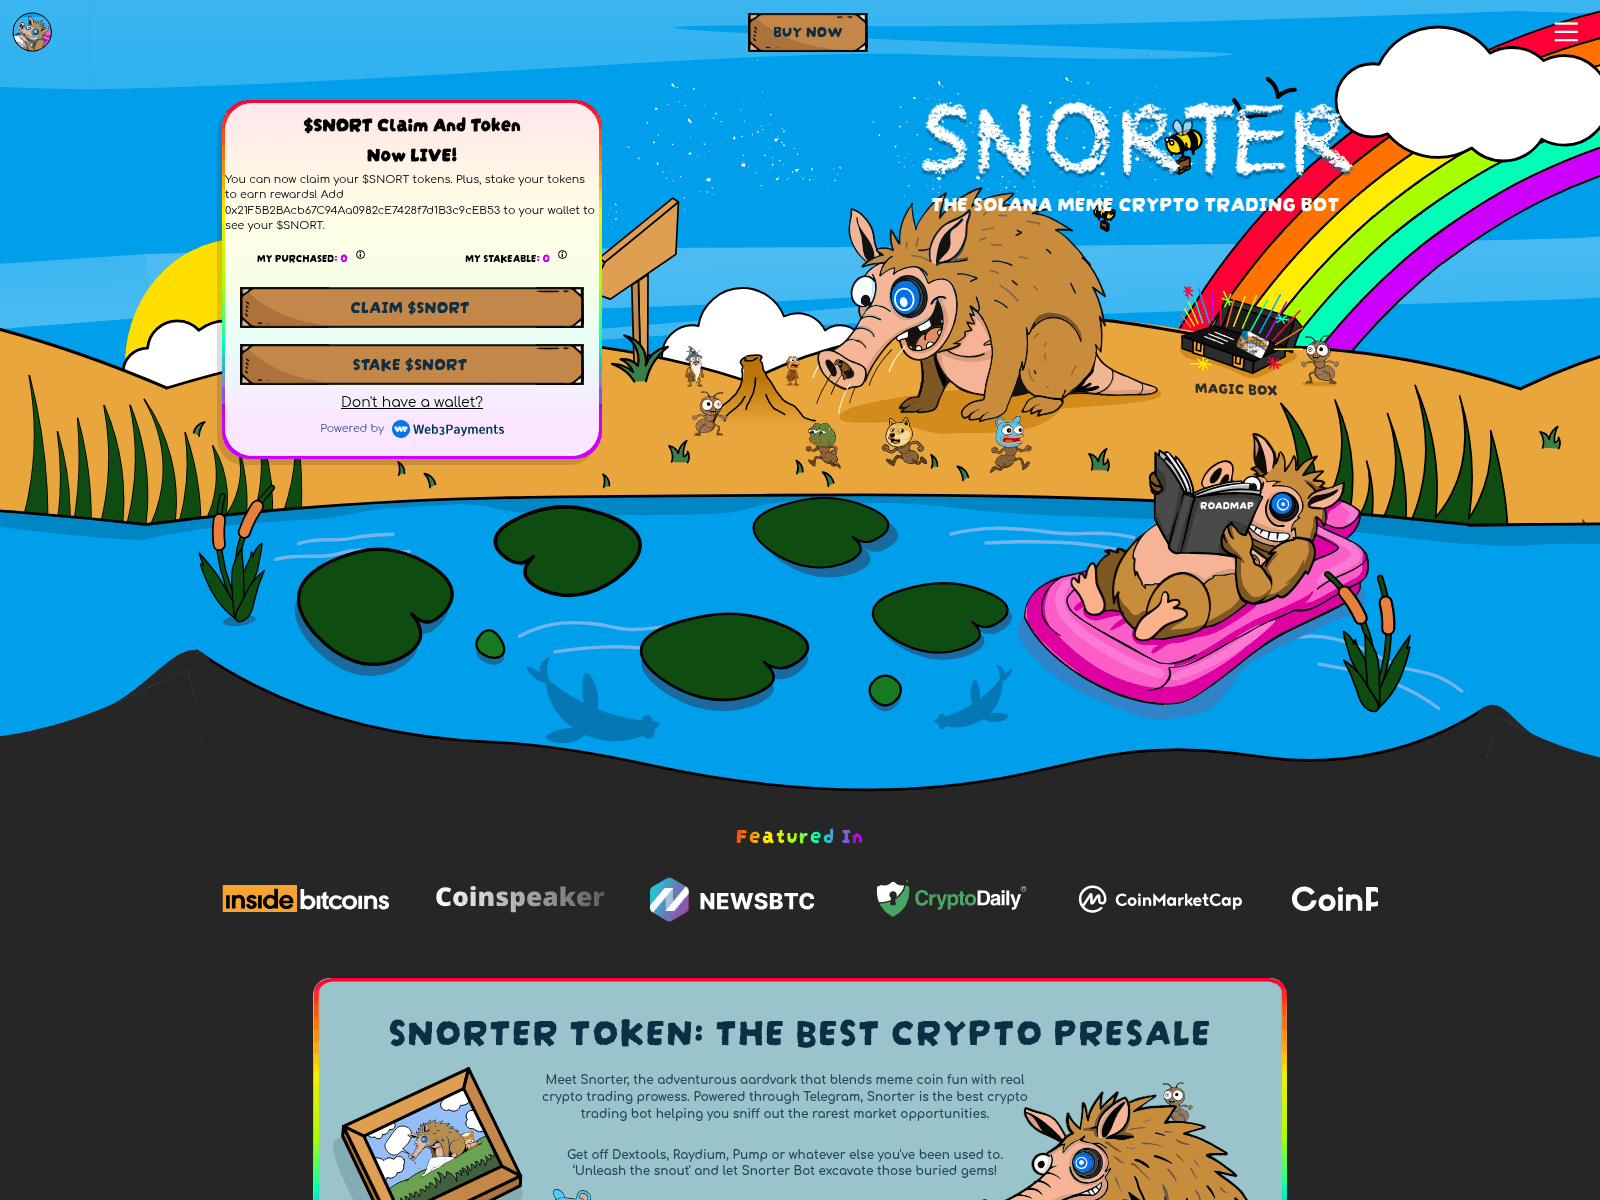
snortertolken.pro
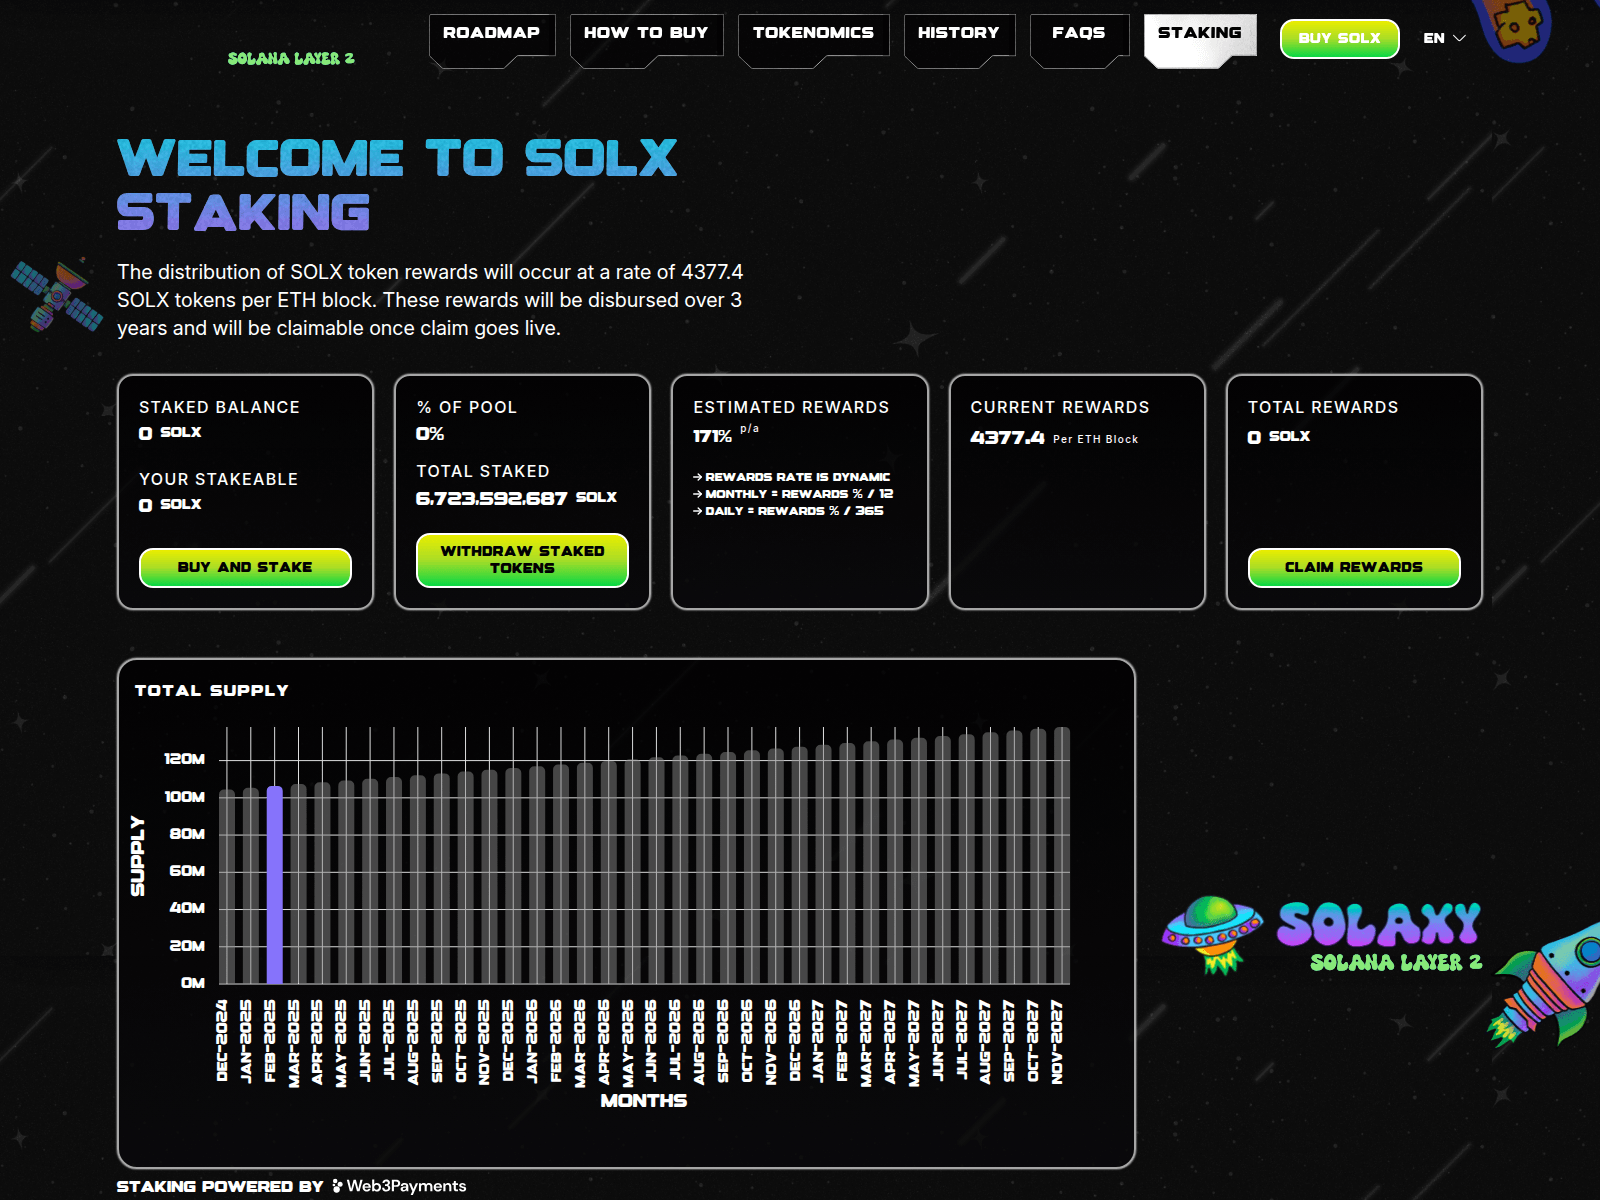
solexy-stakes.pages.dev

spacesxwallet.com

spax21k.org

subbd.pages.dev

sudbbtoken.com

unstaked-net.web.app

velltoken.xyz

wobs.pages.dev

bithyper.pages.dev
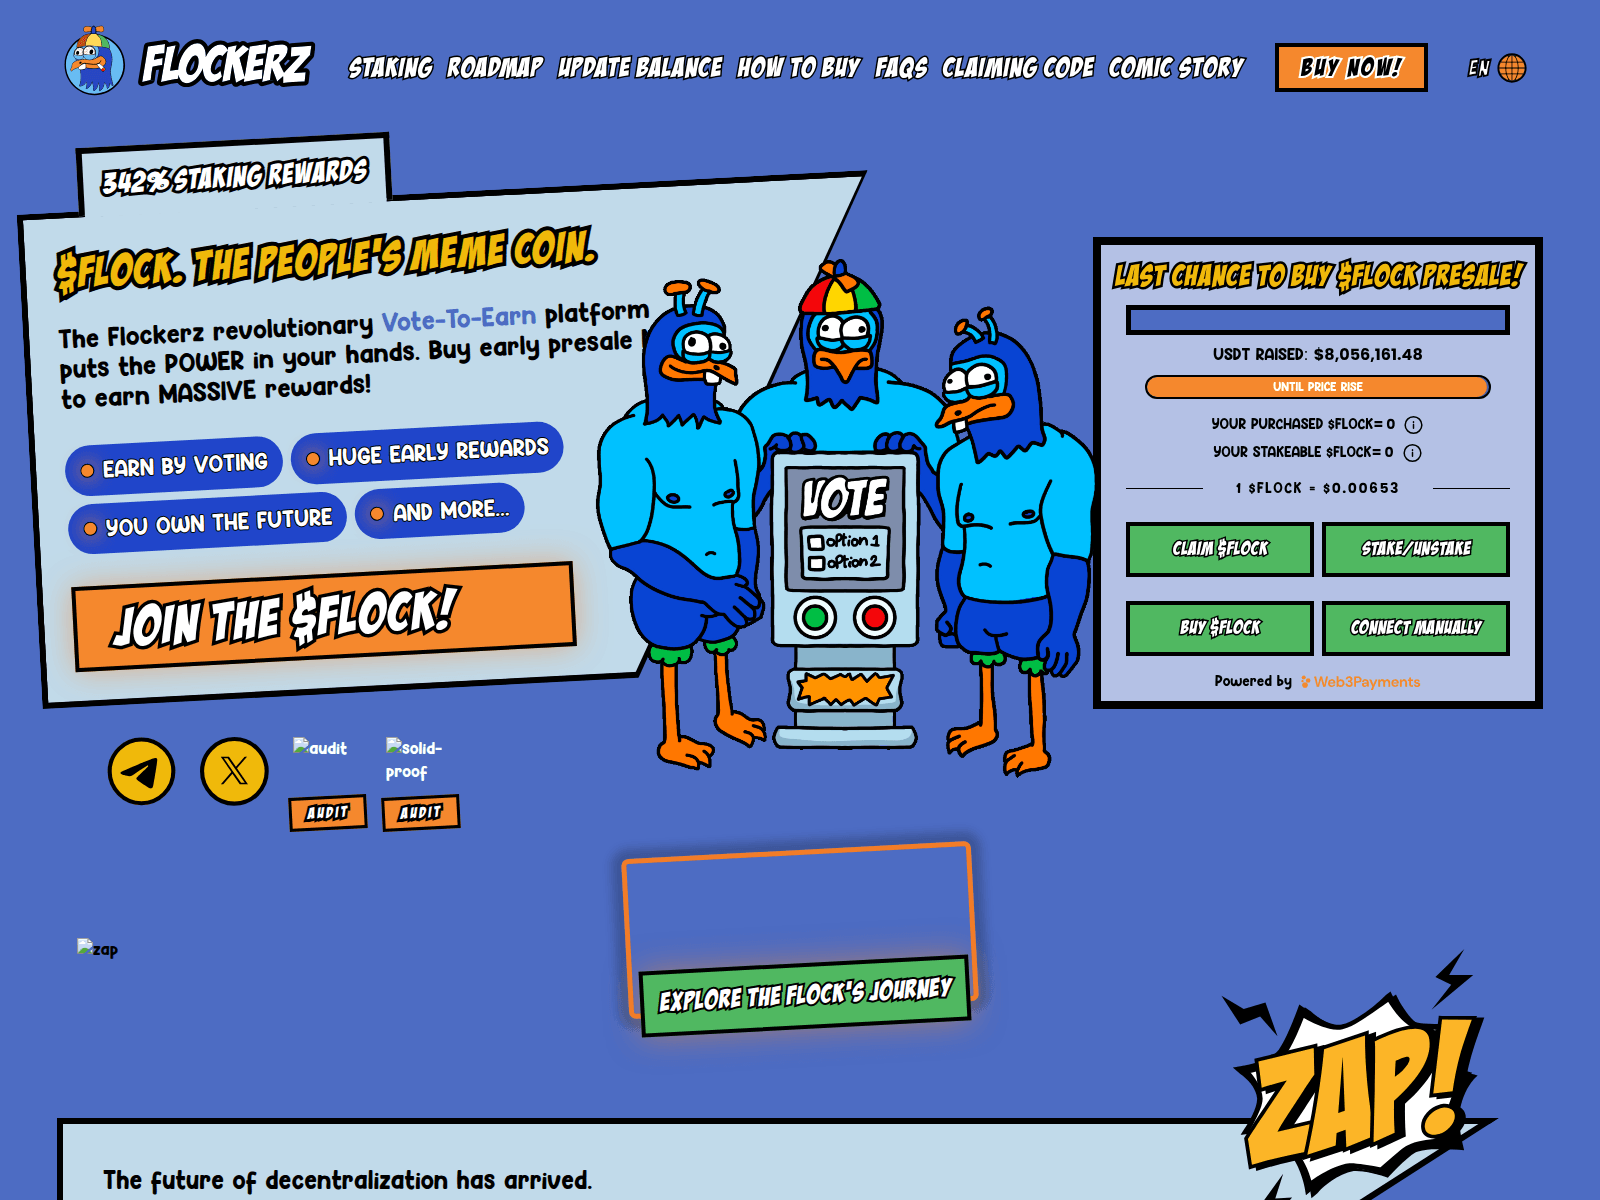
claimflockerztoken.pages.dev

flockerz-dashboards.pages.dev

official-spacex.com

token6900-coin.web.app
Pipeline di risposta alle minacce
Come vengono verificati tutti i domini presenti in questo hub e come vengono neutralizzate le minacce confermate. Visualizzazione completa della pipeline →
Controlli relativi alle informazioni sulle minacce— ogni dominio viene analizzato e sottoposto a verifica incrociata rispetto a:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency RelazioneCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicurezza FiltersQuad9 · AdGuard · CleanBrowsingWeb-ControllaFull surface scan
 crt.sh
Sincronizzazione globale dei fornitori— i rilevamenti confermati vengono trasmessi a 29 partner:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecRecensione del sitoAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftRimozione APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.RelazioneHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust