
Cerca i domini monitorati ed esamina le prove archiviate, i rilevamenti e gli ultimi dati relativi alla disponibilità osservata.
219,806
Totale monitorato
213,476
VT rilevato
91,911
Ultima visualizzazione: attivo
127,895
Non disponibile all'ultimo controllo
568
VT In attesa di conferma
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domini
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains

airdrop-wlfi.org

amltrackerbot.com

app-ratex.org

app-renzoprotocol.network

aster-join.com

auction-zama.org

authereumportal.com

avax-airdrop.click

bcsolver-77n10wf9kk.edgeone.dev

berlinsystem.cfd

bnb-38.cc
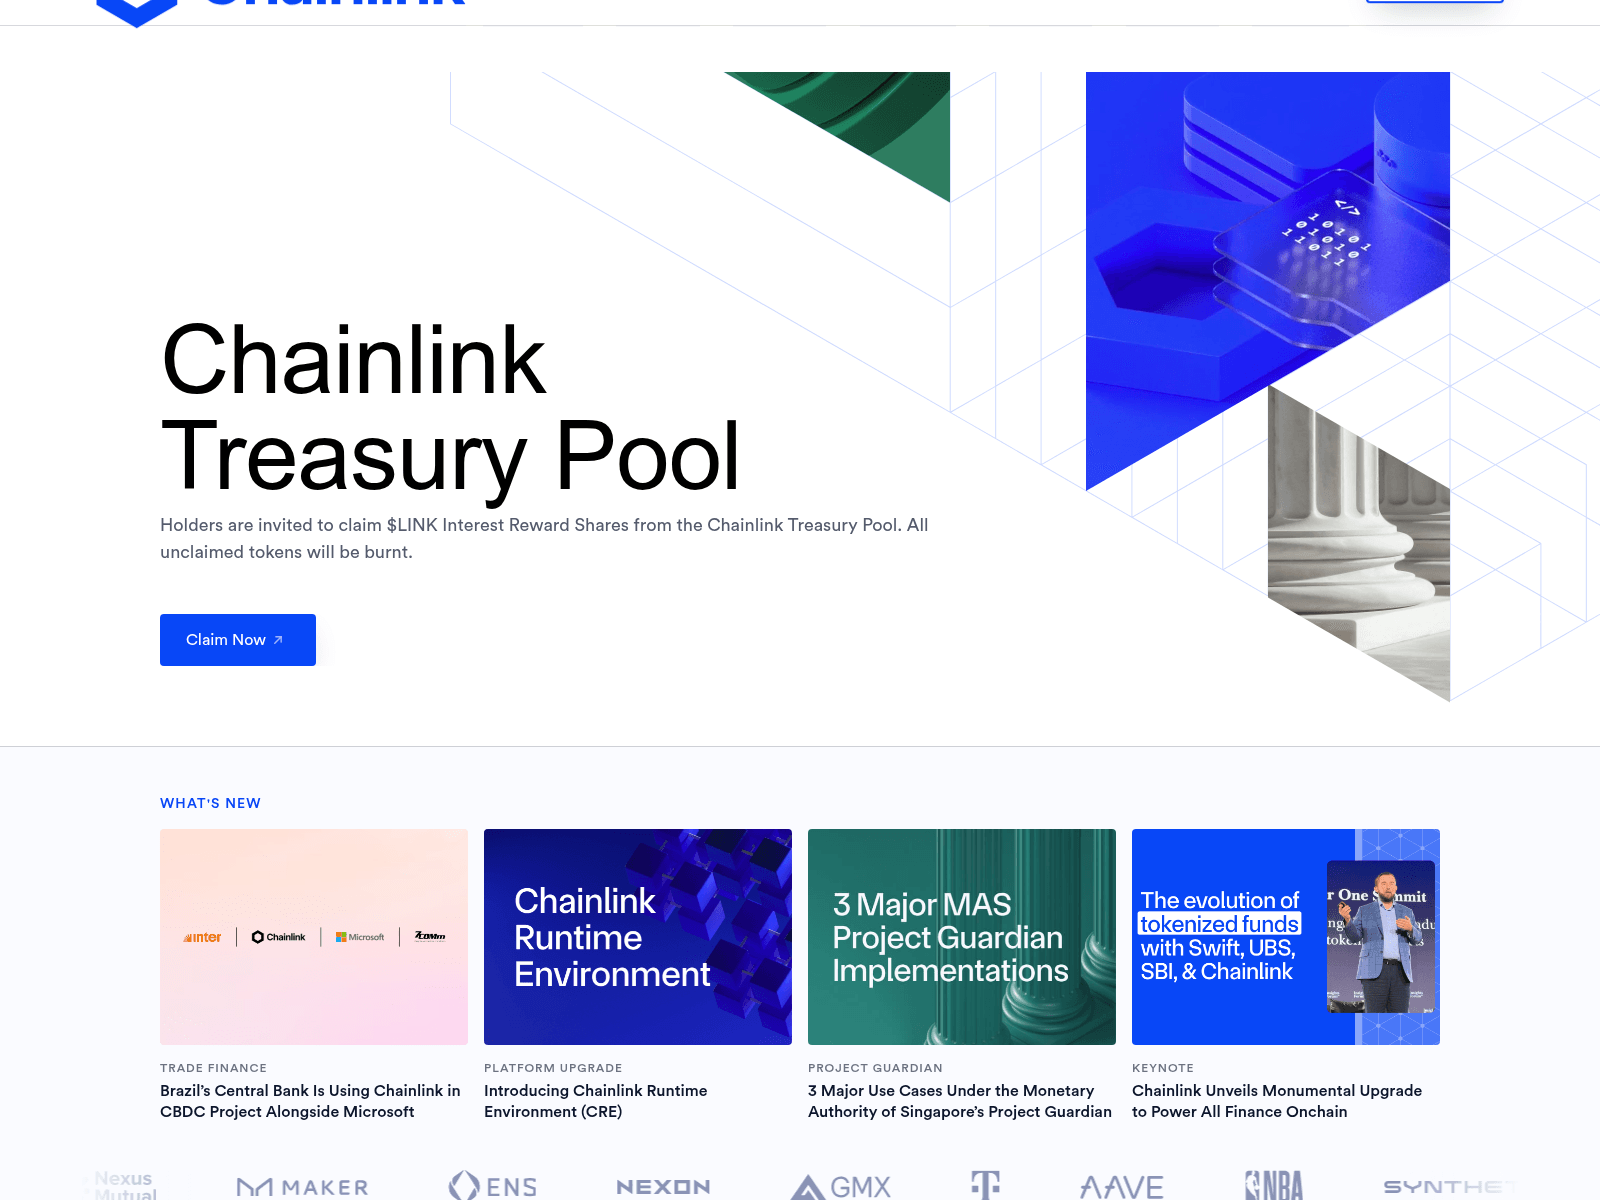
chain.link-treasurypools.app
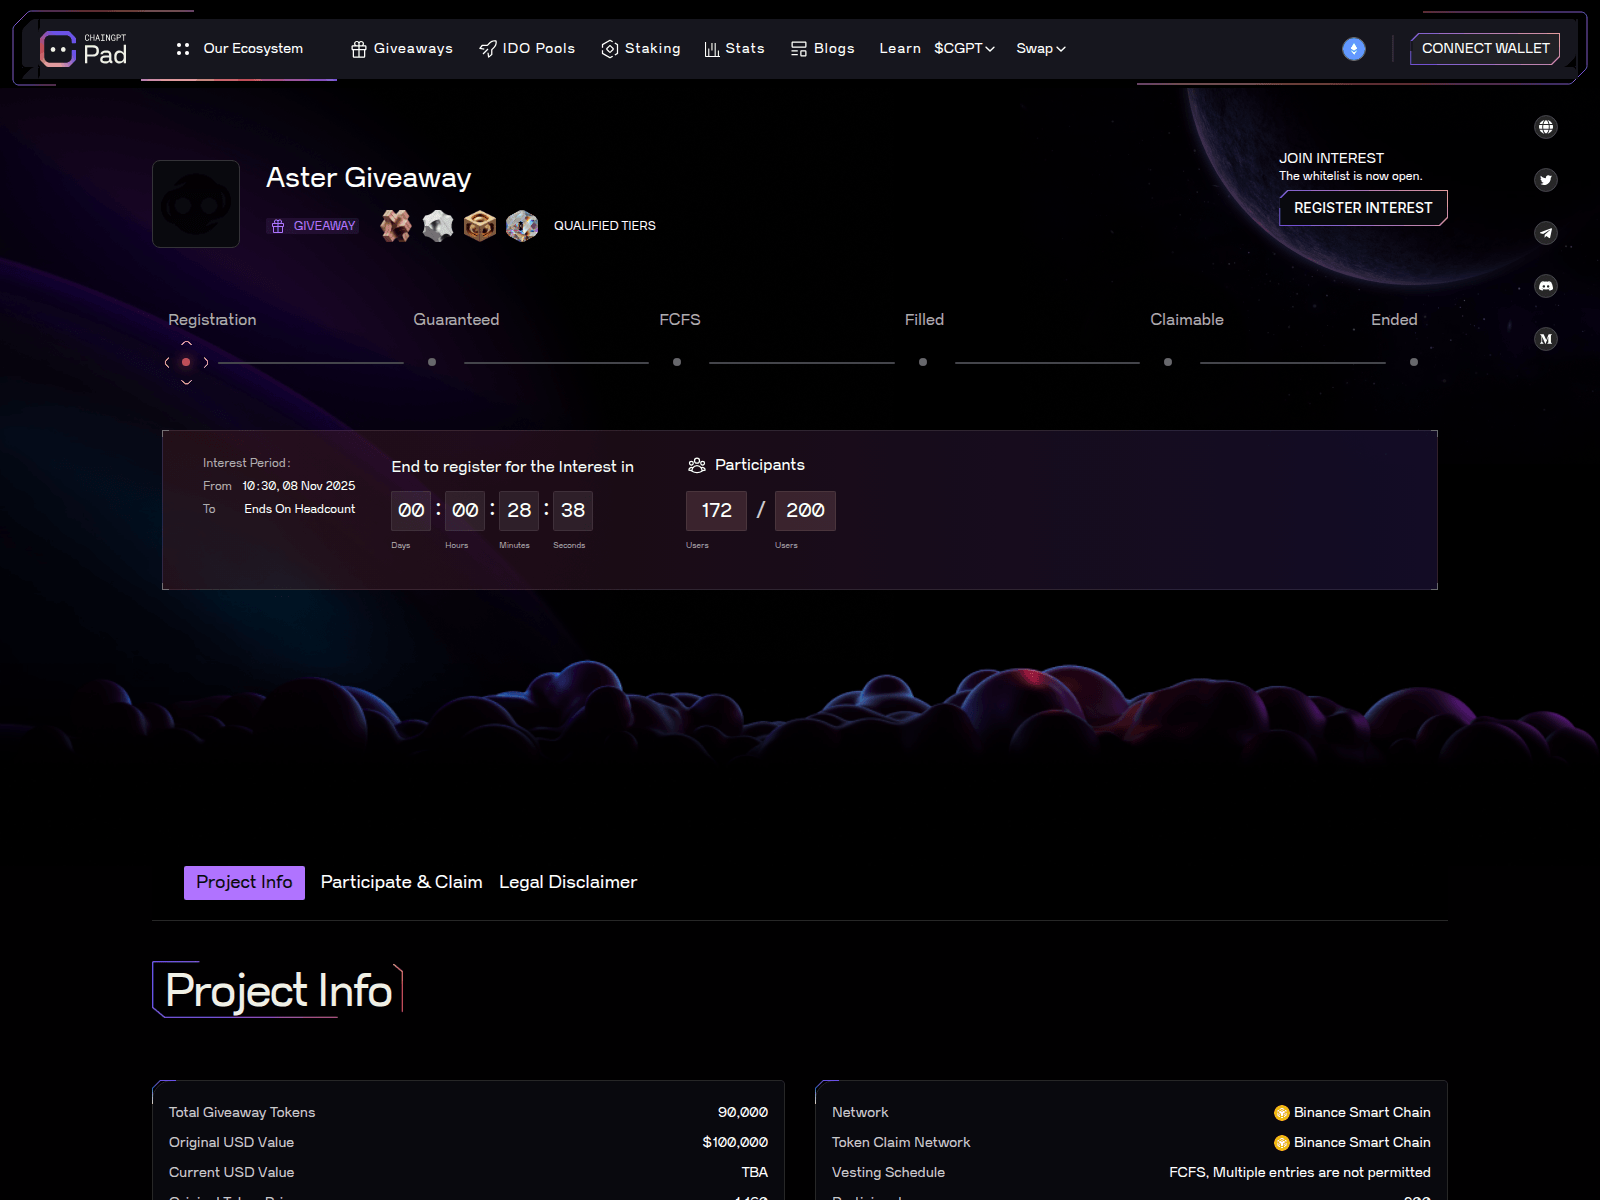
chalngpt-pad.net
claim-walrus.app
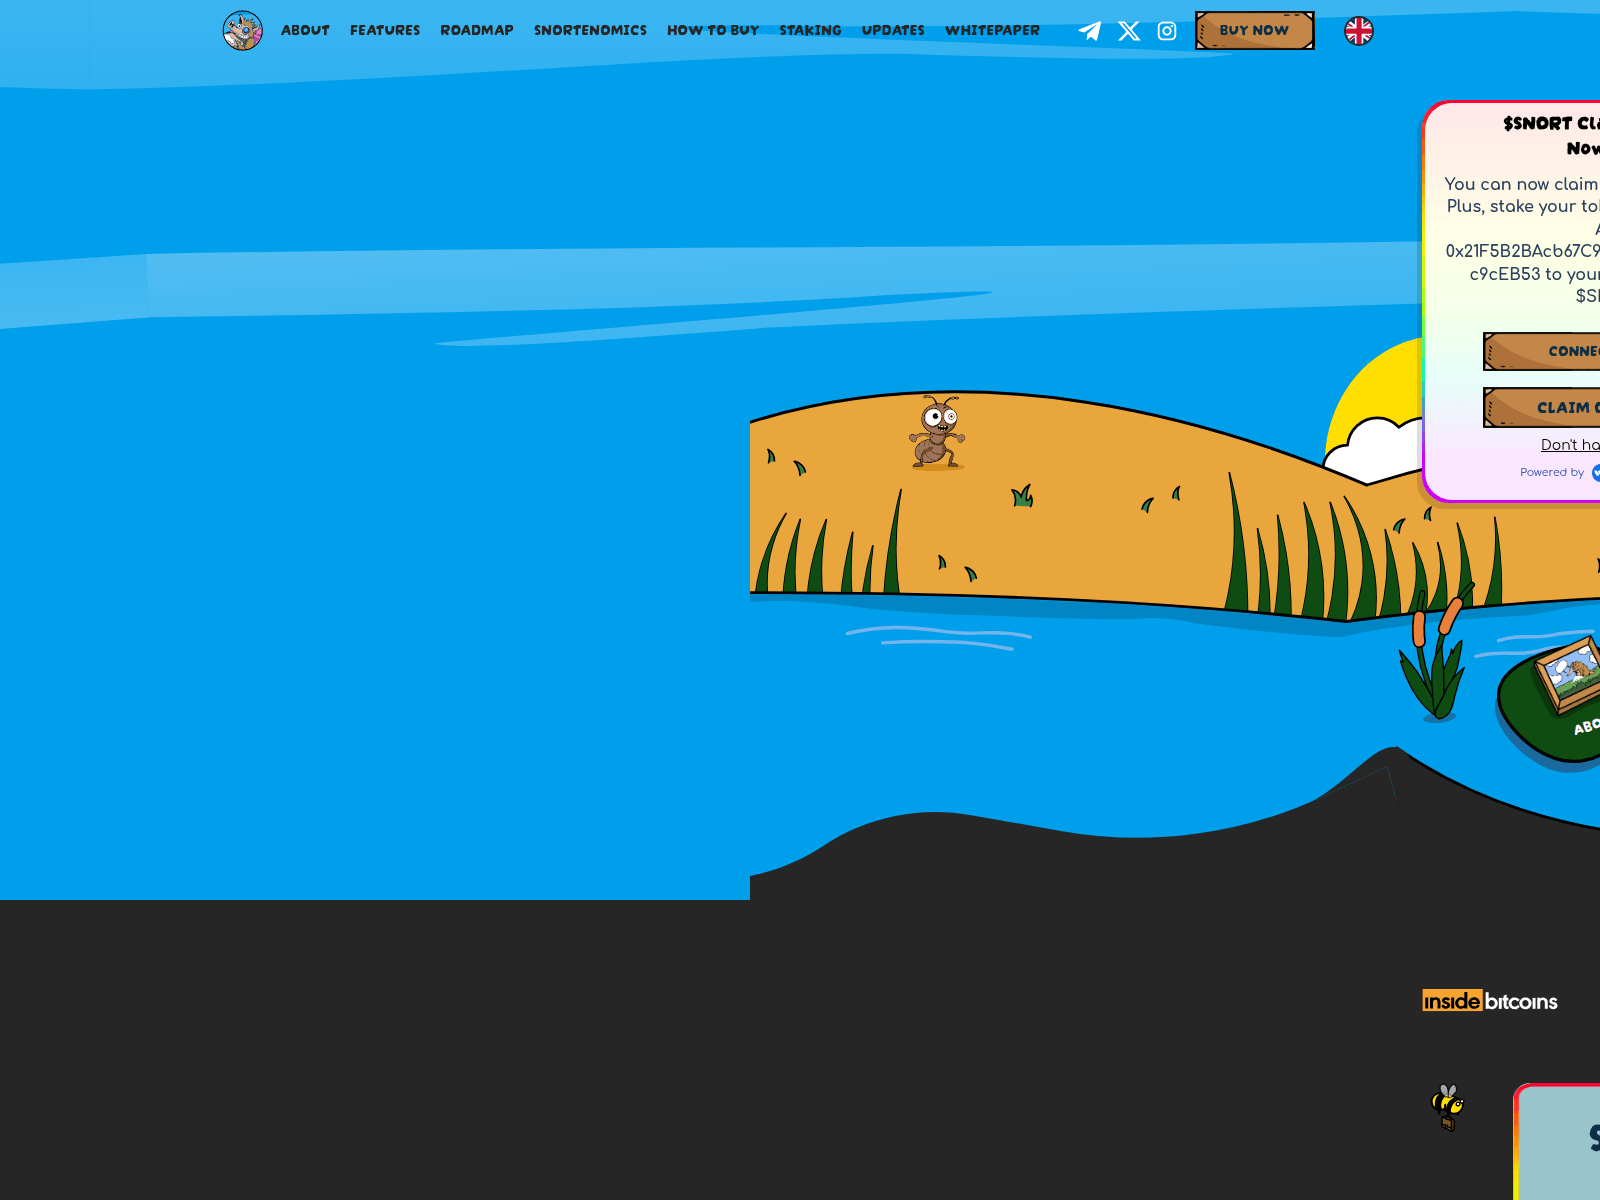
claims-snortertoken.com

crypto-francedeclaration.com

dawgz.ai
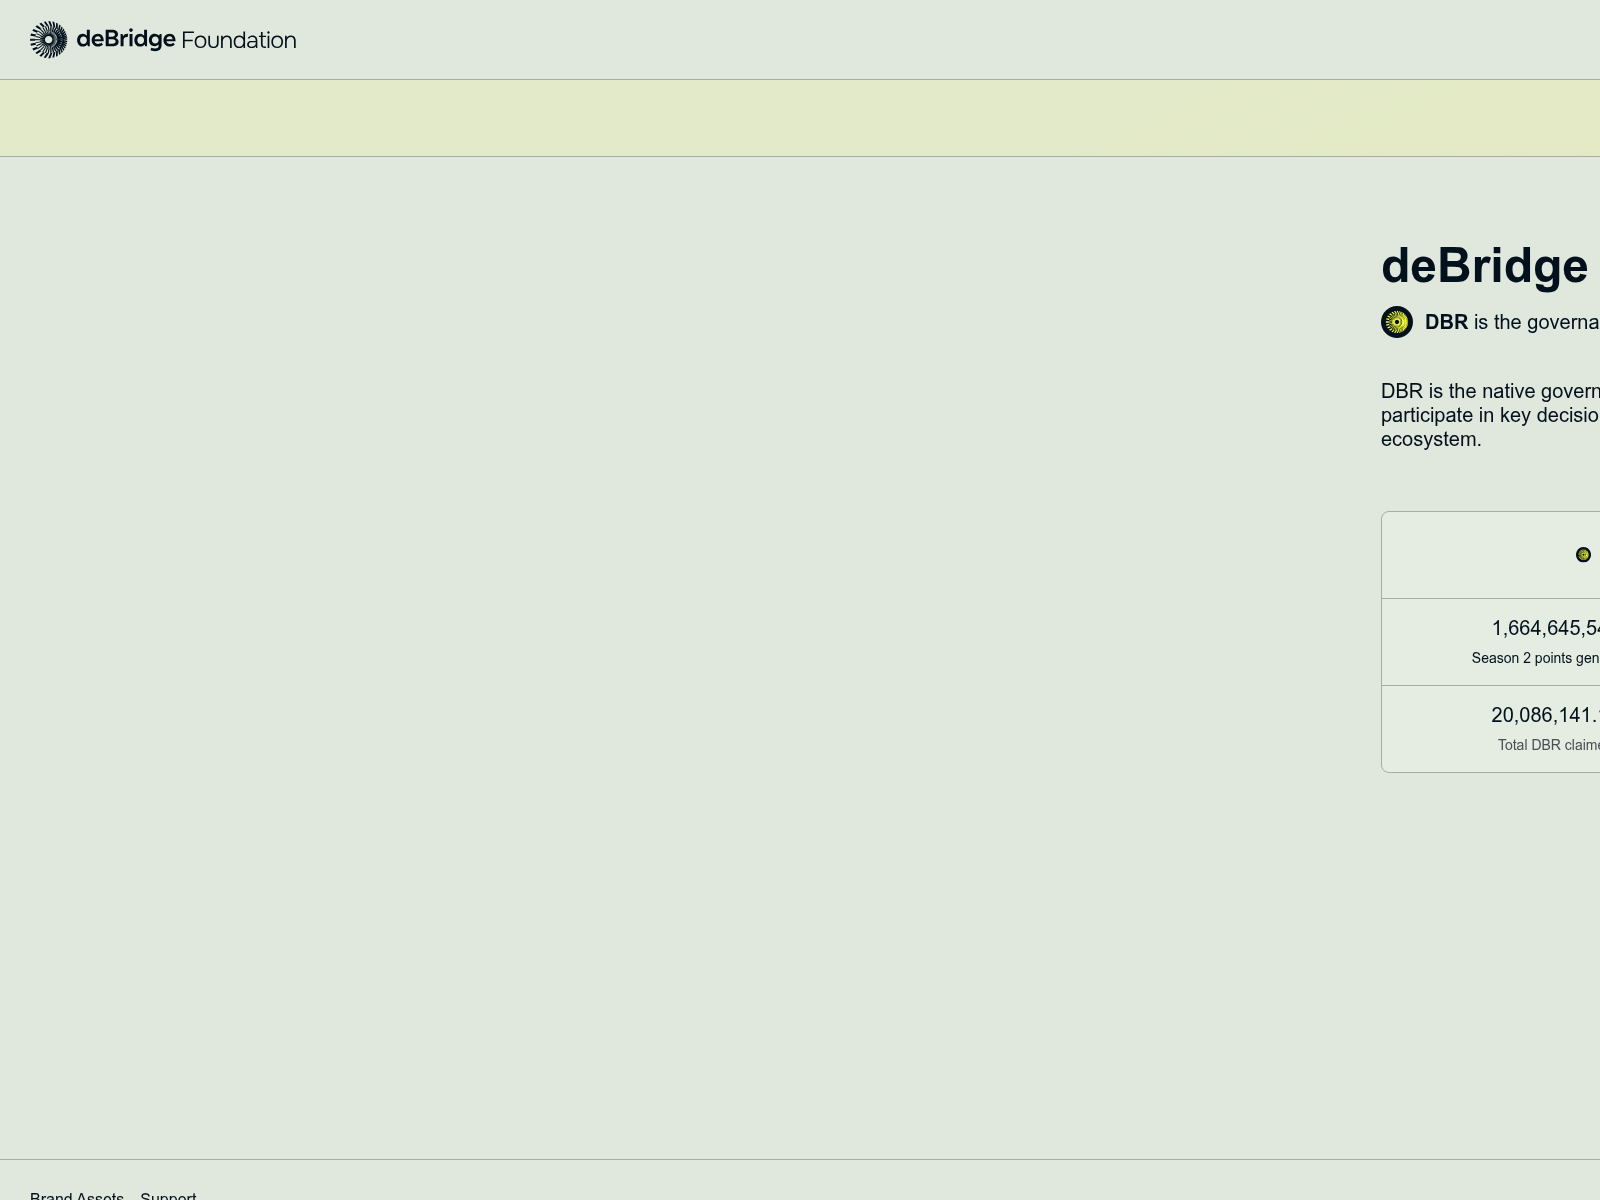
debridge-foundation.app

dextool.netlify.app

eligibility-grass.org
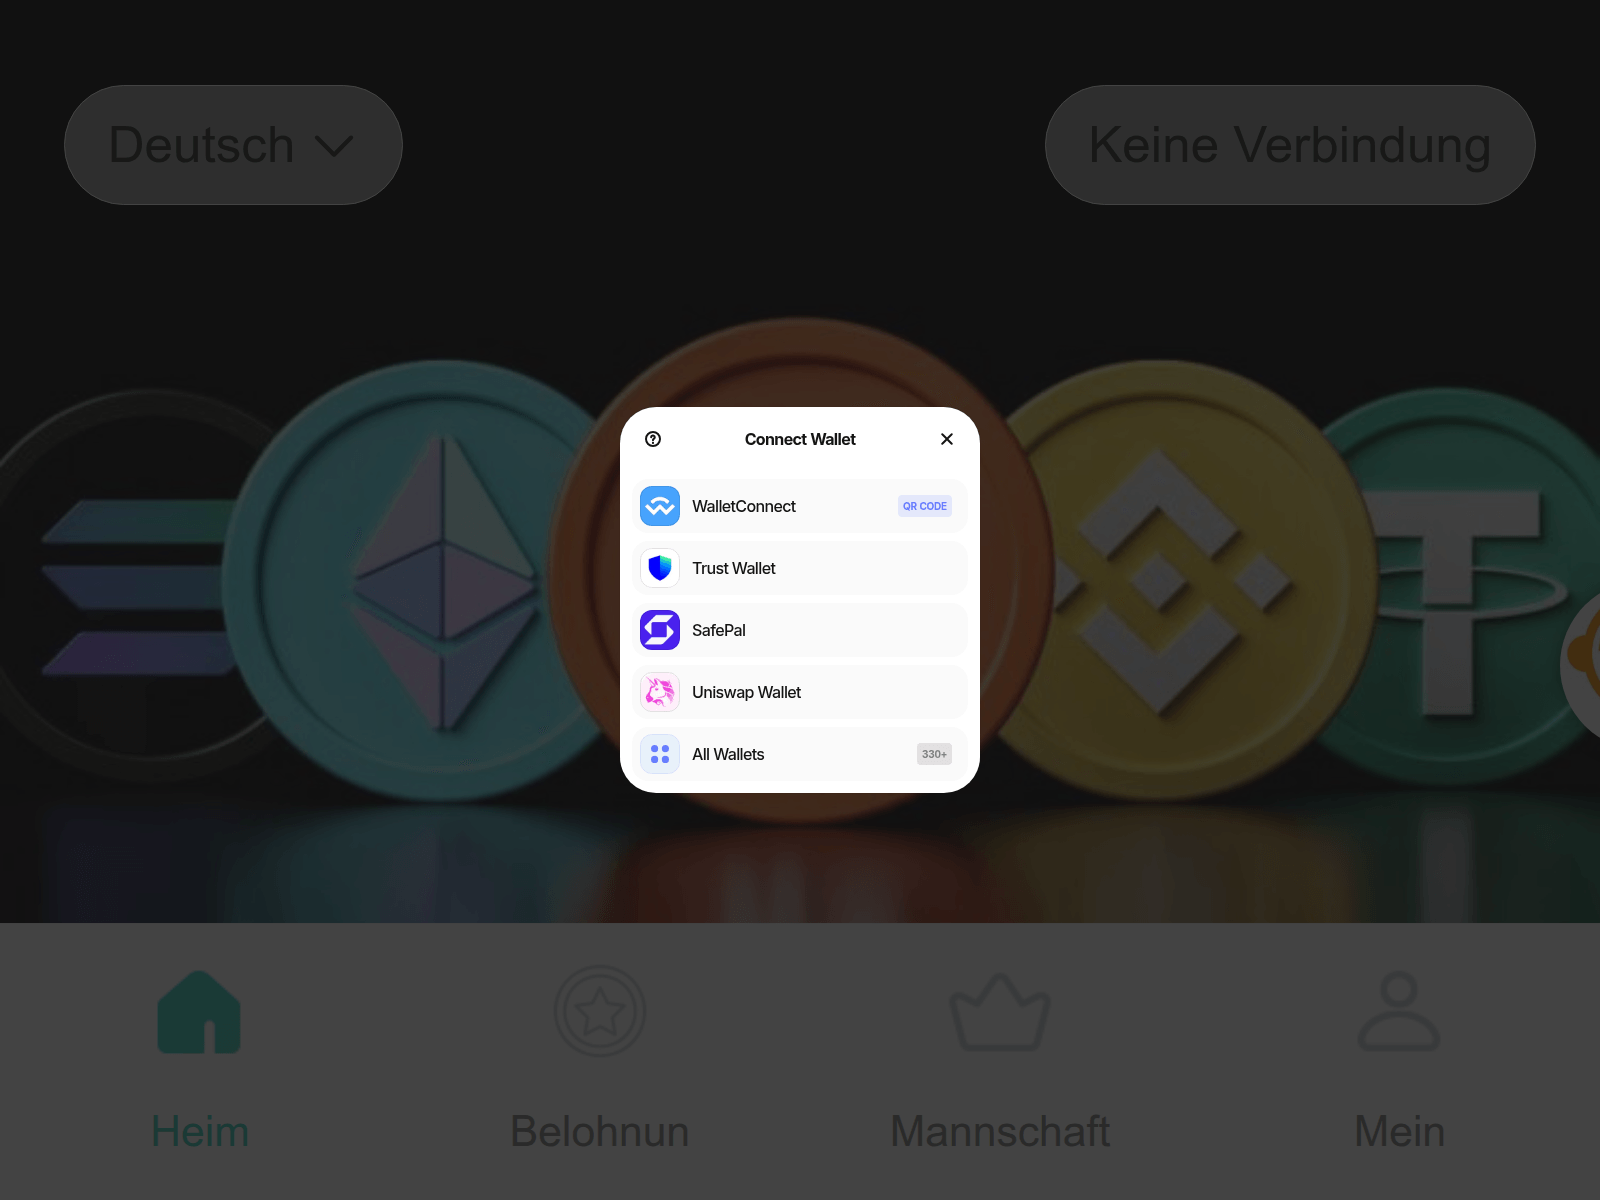
eth-trust.org

ethereum-provider.icu
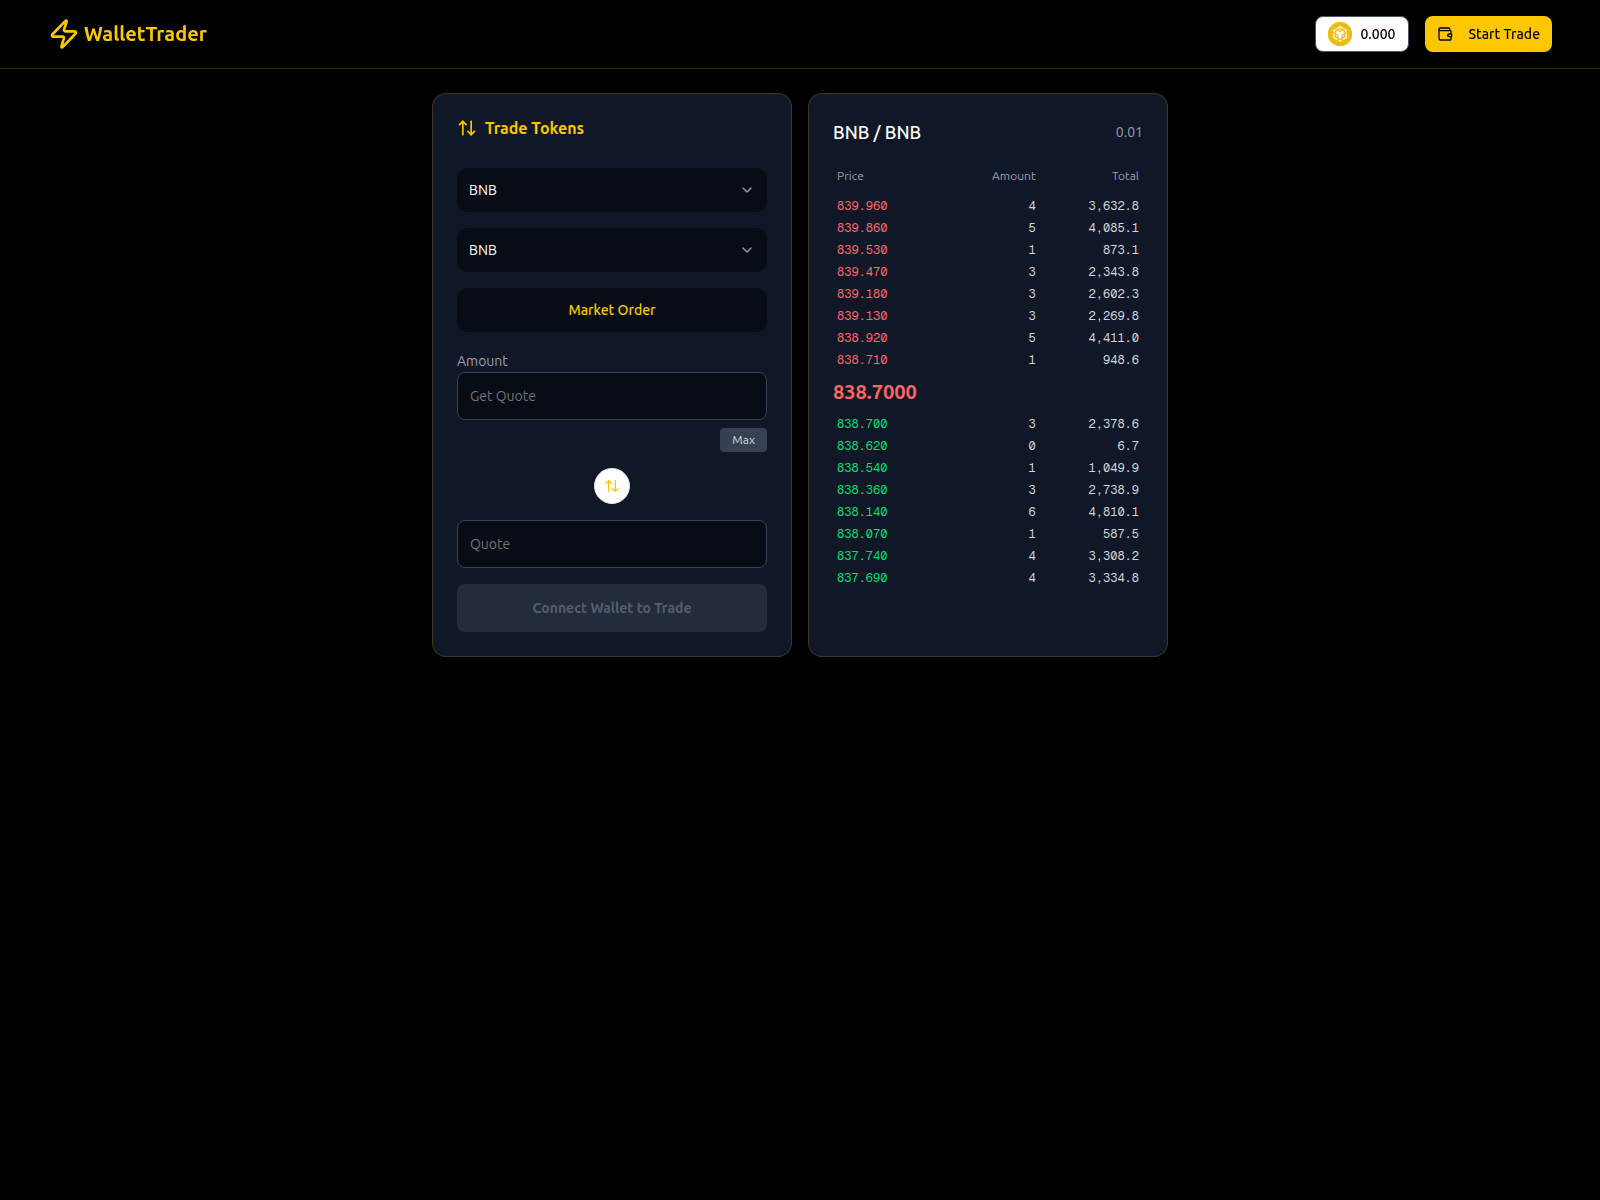
fastwallet.trade
fcfmfy.cc
flyingtulip.finance

folksdrop.xyz

gensyn-ai.app

grass-network.org

hydr.live

impactxconnect.com

join-dein.com
layer2-chain.com

lineabuildscheck.com

lineachecklive.xyz
lunexnetwork.com

mask-reward.app

monadxdevelop.xyz

nexus-dex.web.id

noox.fi

noox.pro

nooxhub.pro
nooxnft.app
ozak.claims

pan-swap.org

pancakeswap.vip

plasmagetclaim.xyz

polyoptions.xyz

protocol-pepe.org

register-dein.com

reward-night.org

reward-pcpe.com

rpc2-uni.com

sdhweyhashkey.top
solanaincinerator.pro

staking-ether-fi.com

swapbytes.net

unlock-wallet-trust.com

update-lido.net

usdtsecureanalyzer.com

vaultblockchain.ink

vooi-app.org
walletconnect--en.typedream.app

walletconnect.one
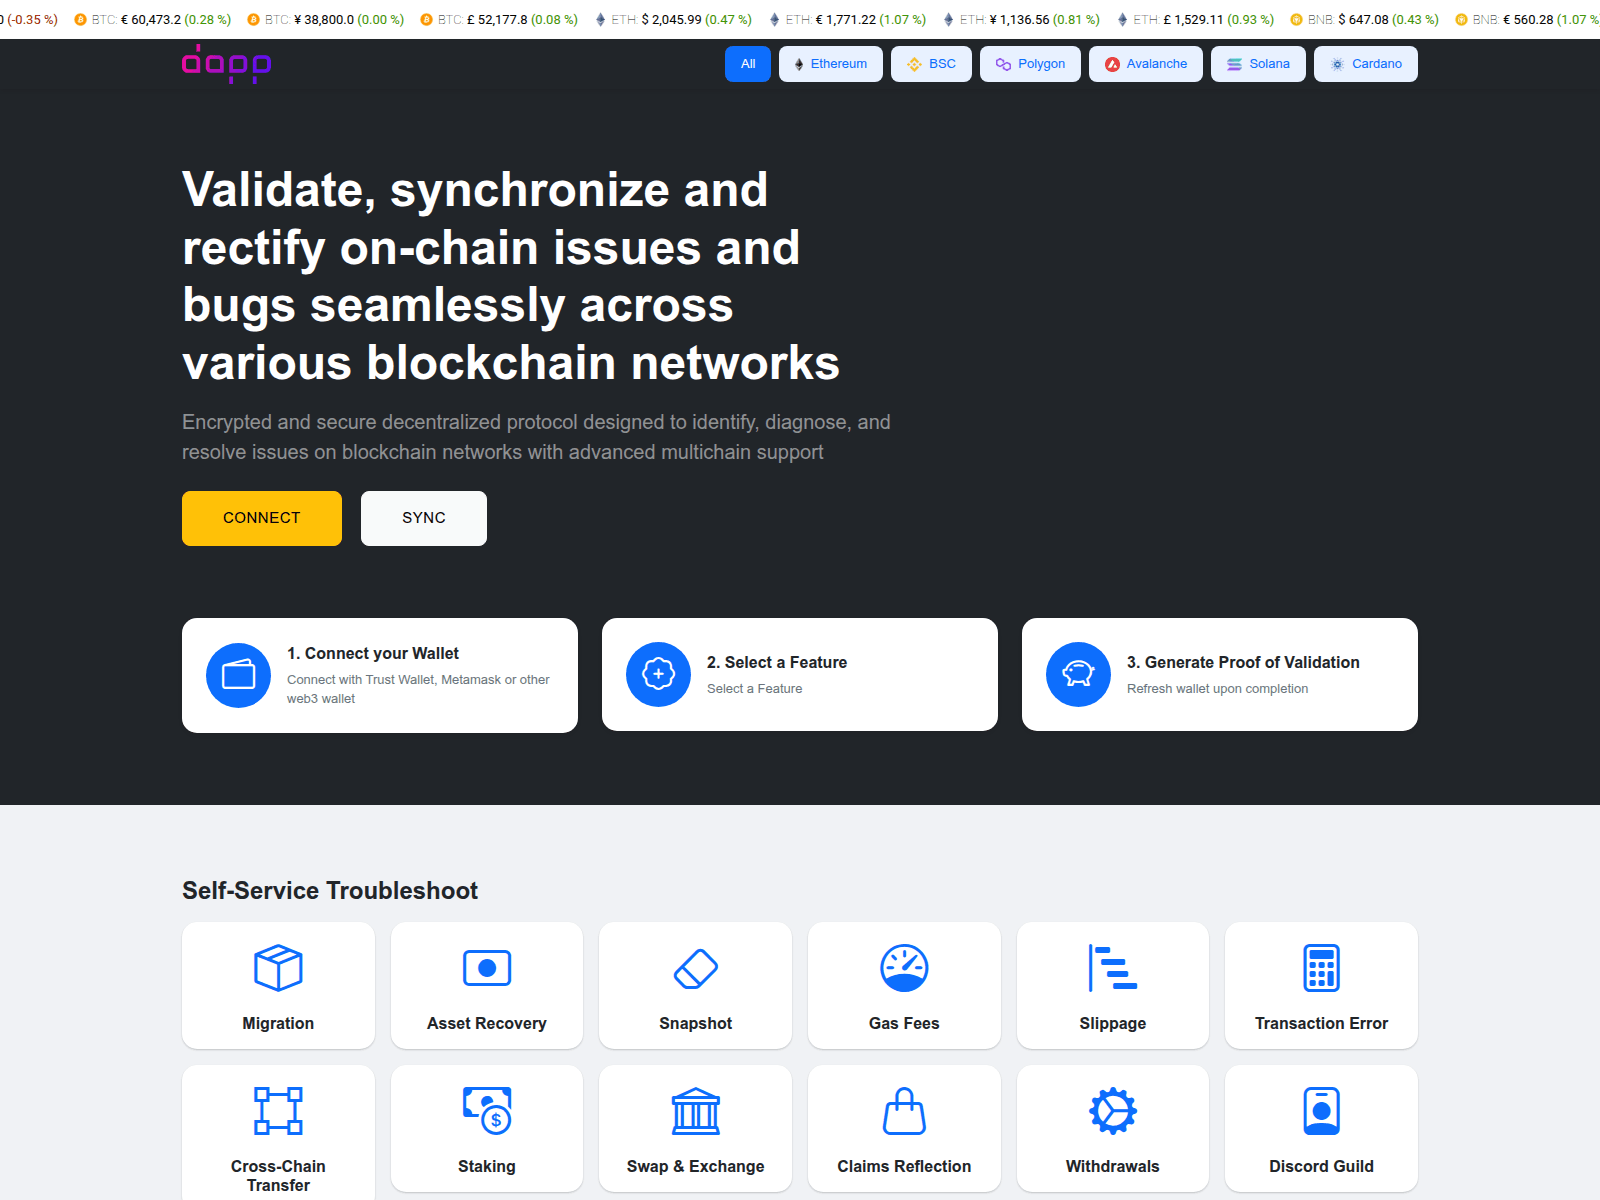
walletconnectnodes.firebaseapp.com

wlfllibertyfinancial.com
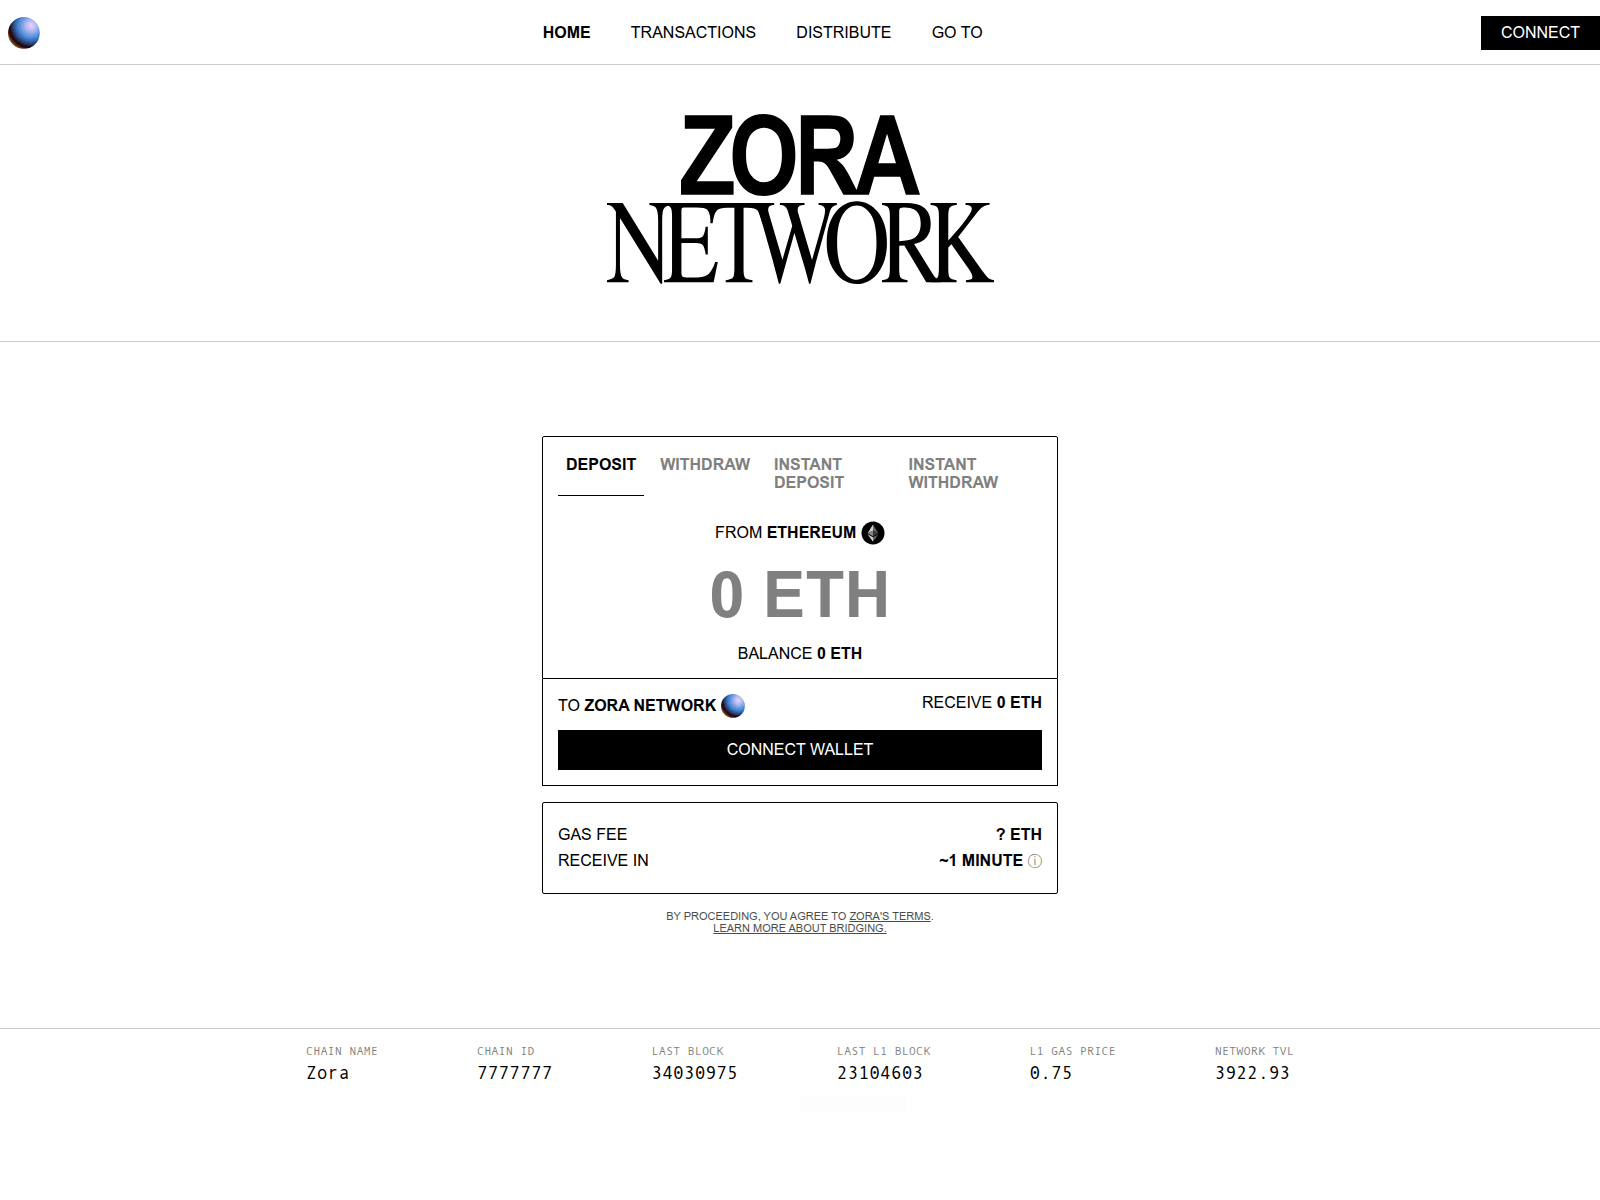
zorabridge.app

amlcheck.in

api-integrate.com

app-bittensor.com

app-kyberswap.com

aster-dex.run

aster-governance.com

aster-register.com
asterdex.com-stake.id

asterdexallocation.com

aureumcapitall.com

bafybeibtcfgrhknlfhnz2c5cddfnsoje4dumrc3wsyoikx2pwuf6fbcsr4.ipfs.dweb.link

bituniswap.com

blockchainapproval.app

bnb-8.cc

bounce-bit.us

bridge.pulsechlan.com

bridgetobnb.com


check-aml.net

claim-espressofoundation.org

claim.monadairdop.xyz

claims-irys.org

claims-standx.app
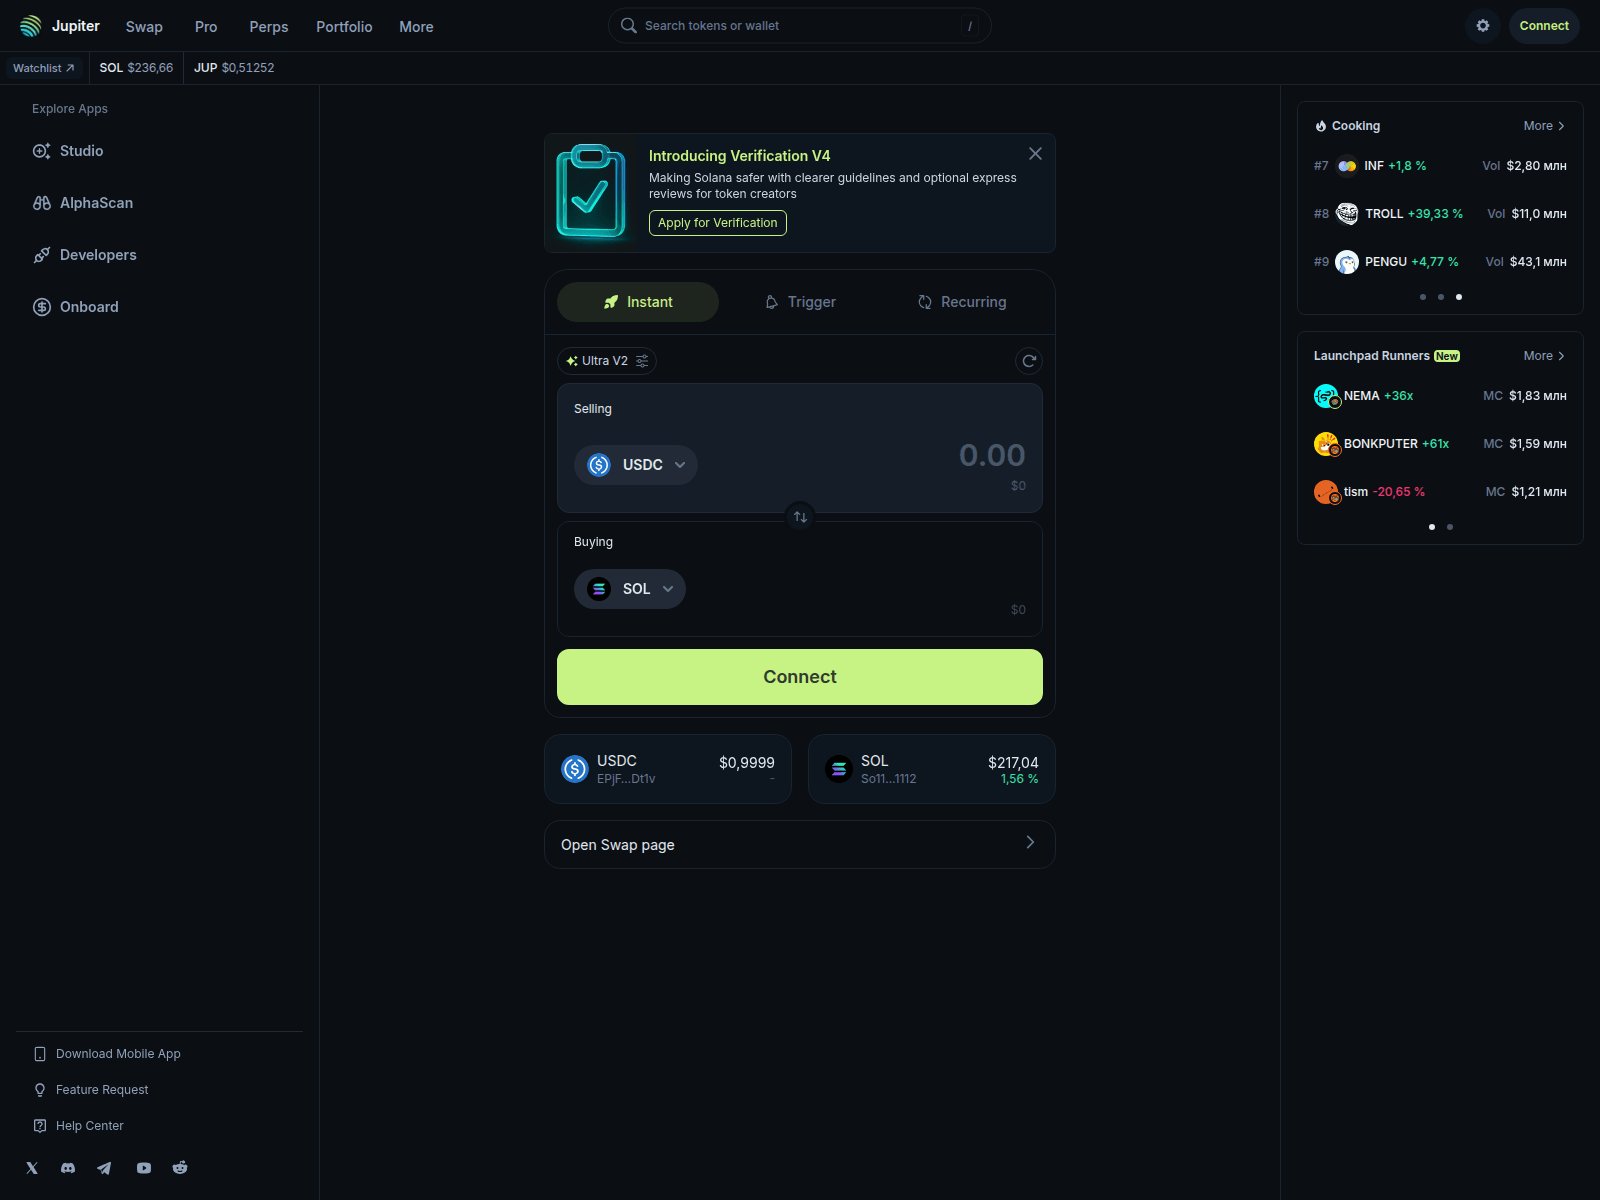
coinbase.commerce-id.net

copyconnection.top

dogsairdrop.live
drop-brevis.network
duplicate-disabled-1067.invalid

duplicate-disabled-4379.invalid

eligibility-alloca.org

eligibility-overtake.org

eligibility-xpl.xyz

getether.net

go-eth.sbs
Pipeline di risposta alle minacce
Come vengono verificati tutti i domini presenti in questo hub e come vengono neutralizzate le minacce confermate. Visualizzazione completa della pipeline →
Controlli relativi alle informazioni sulle minacce— ogni dominio viene analizzato e sottoposto a verifica incrociata rispetto a:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency RelazioneCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicurezza FiltersQuad9 · AdGuard · CleanBrowsingWeb-ControllaFull surface scan
 crt.sh
Sincronizzazione globale dei fornitori— i rilevamenti confermati vengono trasmessi a 29 partner:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecRecensione del sitoAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftRimozione APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.RelazioneHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust