सुरक्षा रिपोर्ट पर जाएँ
डोमेन सुरक्षा और ख़तरे की आसूचना
68932.st favicon

68932.st

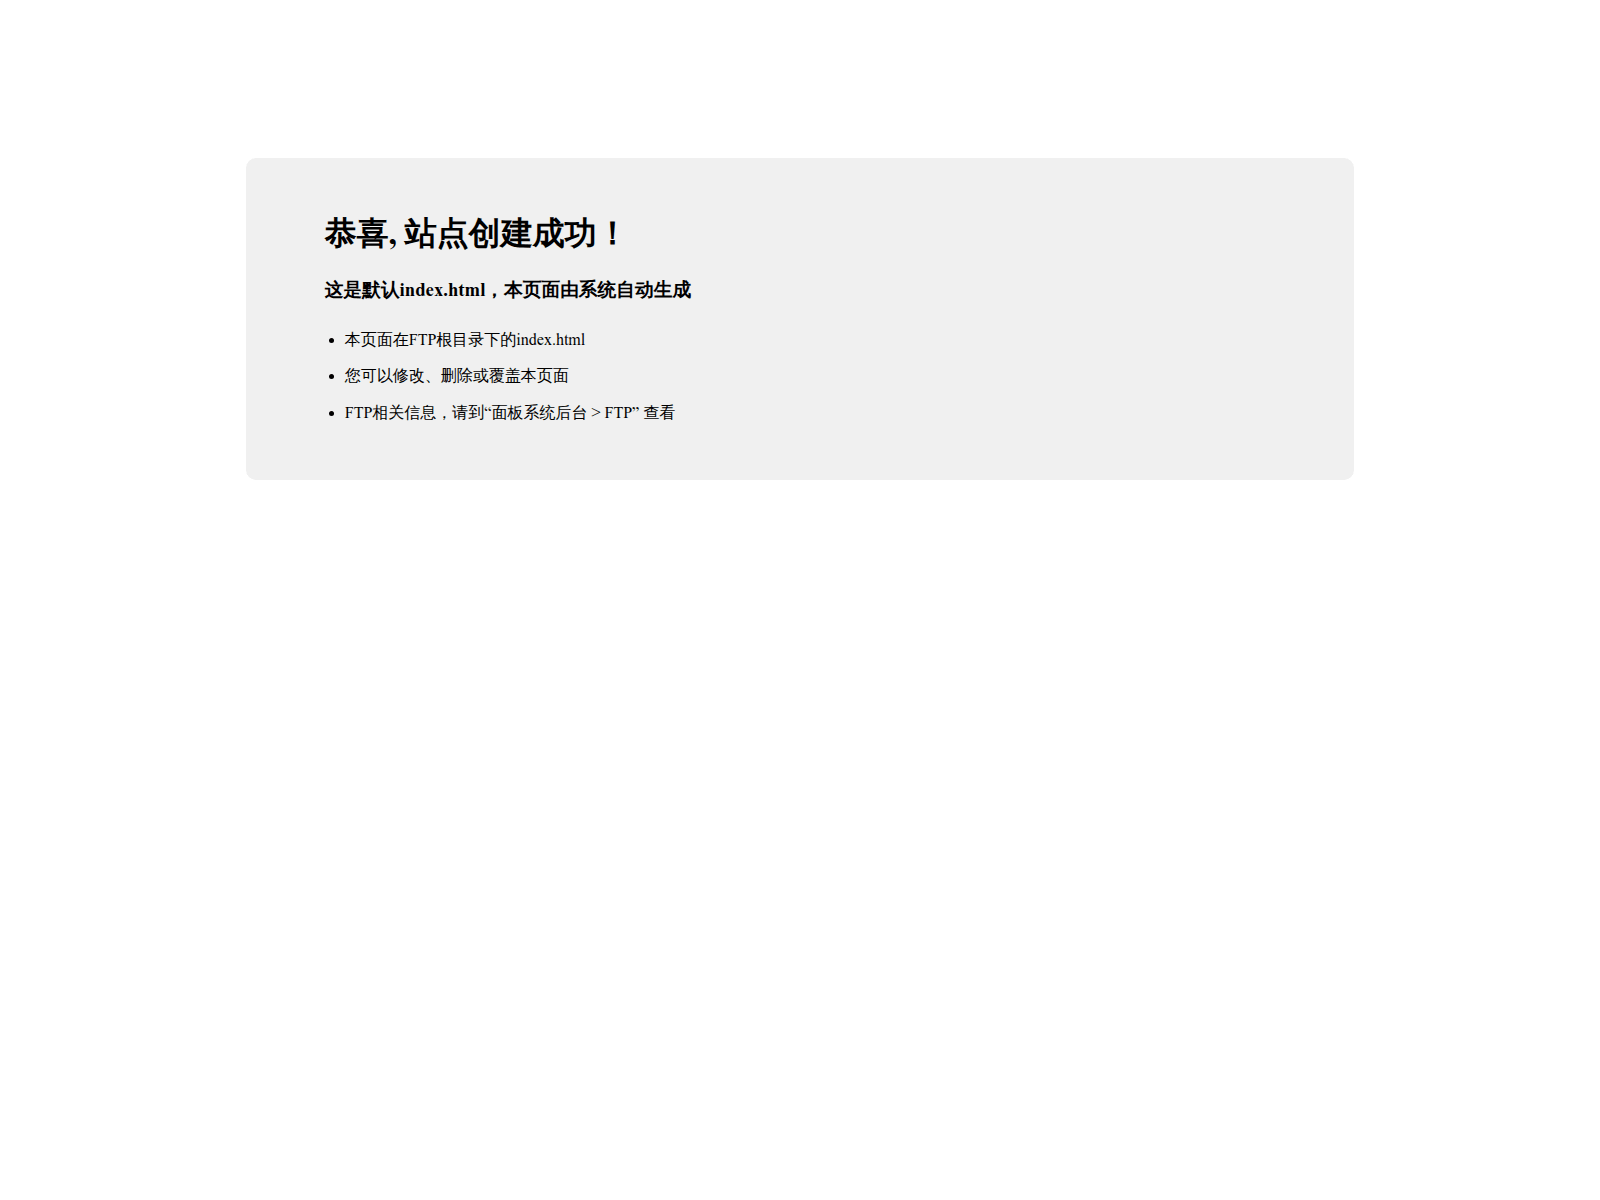
“恭喜,站点创建成功!”

रजिस्ट्रार
Dynadot
Resolved IP
91.92.243.106
Registered
31/08/2026
धमकी भरा फैसला गंभीर
उपलब्धता अंतिम ज्ञात सक्रिय नवीनतम संग्रहीत रीचैबिलिटी अवलोकन
वायरस का कुल पता लगाना: 10/92 Spamhaus DBL: DBL_PHISH संग्रहीत ब्लॉकलिस्ट मिलान: 2 ब्रांड प्रतिरूपण: MetaMask
OTX: 4 refs 04/10/2026 MetaMask 1 Report Sent
एपीआई
इस डोमेन को दुर्भावनापूर्ण के रूप में चिह्नित किया गया है।
सुरक्षा इंजन एक पहचान की रिपोर्ट कर रहे हैं: 10। किसी मैच की रिपोर्ट करने वाली सार्वजनिक ब्लॉक सूचियाँ: 2। अत्यधिक सावधानी बरतें - क्रेडेंशियल या व्यक्तिगत जानकारी दर्ज न करें।
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@omegatech.sc. The latest stored availability evidence still shows the domain reachable; 7 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
7 days
Reports sent
1
Latest case ID
PD-20261004-6C9137
Current status
HTTP 301 at latest stored check
रिपोर्ट सारांश

68932.st — अंतिम ज्ञात सक्रिय (HTTP 301). ब्रांड प्रतिरूपण: MetaMask; घोटाले का प्रकार: Impersonation. साक्ष्य सारांश: VirusTotal 10/92 (alphaMountain.ai, BitDefender, CRDF, CyRadar, Forcepoint ThreatSeeker); URLQuery 2 det.; Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 100/100. रजिस्ट्रार: Dynadot.

मूल फॉरेंसिक रिकॉर्ड सुरक्षित रखने के लिए नीचे का विस्तृत PhishDestroy AI विश्लेषण अंग्रेज़ी में रखा गया है।

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
10 det.
URLQuery
यूआरएलक्वेरी
2 det.
OTX references
URLScan
यूआरएलस्कैन
TLS प्रमाणपत्र
समाप्त या असत्यापित
आयु
1 mo New
देखी गई स्थिति
अंतिम ज्ञात सक्रिय 301
PhishDestroy
विनाश सूची
सूचीबद्ध
Reports Sent
1

Source evidence

8 sources

Spamhaus DBL

DBL_PHISH

नेटवर्क सुरक्षा इंटेलिजेंस
SSL Certificate Invalid
SSL certificate is invalid or expired. Issuer: Let's Encrypt / YE2

साक्ष्य सारांश

गंभीर
VirusTotal
10/92
ओटीएक्स
4 community refs
यूआरएलस्कैन
Stored capture

Assessment

68932.st was observed on 2026-10-04 with a listing in the Phishdestroy internal database, and was recorded as appearing on two external blocklists, MetaMask and SEAL. The domain's registration date is documented as 2026-08-31.

Recorded Evidence

MetaMask and SEAL both listed 68932.st on 2026-10-04 as an external blocklist entry. The Phishdestroy internal listing also included the domain on the same date. The domain was registered with Dynadot on 2026-08-31, and its SSL certificate was issued by Let's Encrypt / YE2, scanned on 2026-10-04.

Interpretation

The records from MetaMask, SEAL, and Phishdestroy indicate that 68932.st was flagged by multiple sources on the same date. The registration and SSL certificate details provide context for its timeline, but do not directly relate to the blocklist observations. These dated entries allow for comparison of how the domain was treated by different sources at a single point in time.

Recommended Actions

For 68932.st, it is recommended to preserve the blocklist entries from MetaMask and SEAL, as well as the Phishdestroy internal listing. Future reviews should reference these specific source records to monitor any changes. Comparing these observations may help inform further steps regarding the domain.

खोज-परहेज़ विश्लेषण

छिपे होने का संदेह: स्कैनर और आगंतुक शीर्षक भिन्न हैं

अभी तक स्कैन नहीं किया गया अभी तक क्रॉलर और ब्राउज़र के बीच कोई अंतर दर्ज नहीं किया गया है।

इस होस्ट के लिए संग्रहीत क्रॉलर-बनाम-ब्राउज़र अवलोकन, साथ ही केइतारो-शैली ट्रैफ़िक वितरण प्रणालियों के लिए लाइव फिंगरप्रिंट जांच।

संग्रहीत छुपाने वाला झंडा
अभी तक स्कैन नहीं किया गया
अंतिम छुपाने का स्कैन
स्कैनर द्वारा देखा गया सर्वर हेडर
openresty_edge

स्कैनर नोट: redirect: raw=redirect_301; http=301; via=http_proxy; location=https://68932.st/; server=openresty_edge

सुरक्षा स्कैनर को दिखाया गया शीर्षक301 Moved Permanently
ब्राउज़र आगंतुक को दिखाया गया शीर्षक恭喜,站点创建成功!
TDS लाइव फिंगरप्रिंट जांच
सात केइतारो फिंगरप्रिंट्स और एक क्रॉलर-बनाम-ब्राउज़र तुलना, जब यह पैनल खुला हो तो PhishDestroy स्कैनर से चलाया जाता है।
इंतज़ार

सहेजा गया कैप्चर · 2 captures

Domain details

डोमेन
URLScan Verdict विश्लेषण पूरा हुआ score 0 report ↗
IP प्रतिष्ठा abuse score 0/100 0 reports checked 05/10/2026
OTX Tags 2026-10activeall-domainsblocklistcontentcryptoडोमेनdrainerfraudlivemonthlyphishdestroyphishingscam
रजिस्ट्रार Dynadot (Unknown)
दुरुपयोग संपर्कprivacy@dynadot.com, abuse@omegatech.sc
आईसीएएनएन रजिस्ट्रीICANN Lookup (RDAP) →
पंजीकरणनिर्मित 31/08/2026 (41d · New) — Expires 31/08/2027
HTTP स्थिति301 Moved Permanently
तकनीकी विवरणProvenance & timestamps
पहली बार पता चला04/10/2026
DOM Analysisanalyzed 09/10/2026score 0/100
Submitted URLhttp://68932.st/
केस आईडी
पेज शीर्षक
恭喜,站点创建成功!
TLS प्रमाणपत्र
Certificate hostname mismatch · जारीकर्ता Let's Encrypt / YE2

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
91.92.243.106
Network ASN
AS202412
Organization
Omegatech LTD
Observed location
Rotterdam, NL
Server header
openresty_edge

नेमसर्वर 2

  • ns1.dnsip.com
  • ns2.dnsip.com

Location describes the IP network.

TLS प्रमाणपत्र

Issuer
Let's Encrypt / YE2
Valid from
2026-08-31 16:42:59
Valid until
2026-11-29 16:42:58
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-04 07:02:06 UTC
Collection source
PhishDestroy collector
Certificate fingerprint47535d9af145a5952fcc679574daa6a9c063073e47789f84869c3e9dbe6a1d06
Certificate names · 1 SANs
  • www.68932.st

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 91.92.243.106rapiddns.io

Latest Classified Outcome 2026-10-11 10:41:20 UTC

Primary outcome Redirecting reason: HTTP redirect observed 80% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Redirecting Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Redirecting HTTP redirect observed 80% 2026-10-11 10:41:20 UTC
RDAP registration अज्ञात
Observed timeline last reachable: 2026-10-11 10:41:20 UTC last content: 2026-10-07 22:43:58 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
इस डोमेन की रिपोर्ट करें सबूत जमा करें और दूसरों की सुरक्षा में मदद करें

वायरसटोटल विश्लेषण

10 / 92 सुरक्षा विक्रेताओं ने इस डोमेन को चिह्नित किया
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
BitDefender
CRDF
साइरेडार
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
कास्परस्की
SOCRadar
साइट प्रदर्शन विश्लेषण

Google PageSpeed Insights — mobile performance audit of 68932.st · checked Oct 5, 2026

100
Good
Performance
FCP
0.81s
First Contentful Paint
LCP
0.81s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.08s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-04 05:24:50 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 91.92.243.106.

धमकी प्रतिक्रिया पाइपलाइन

खोज
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

धमकी निगल ली गई
68932.st पहचाना गया और पूर्ण विश्लेषण के लिए कतारबद्ध किया गया
04/10/2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
05/10/2026
URLScan.io Capture
संग्रहीत URLScan report with capture artifacts
04/10/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
10/92 recorded on VirusTotal
07/10/2026
ब्लॉकलिस्ट का पता लगाना
में पाया गया 2 blocklists: MetaMask, SEAL
11/10/2026
OTX Community References
4 community publication references on एलियनवॉल्ट ओटीएक्स. References are not vendor verdicts and are excluded from the evidence score.
06/10/2026
Brand Impersonation
Impersonation of MetaMask
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
04/10/2026
Technical Analysis Recorded
रिपोर्ट में संग्रहीत प्रौद्योगिकी या फोरेंसिक-विश्लेषण परिणाम शामिल हैं।
11/10/2026
Sent Report Recorded
Stored outgoing record associated with registrar Dynadot, 2 abuse contacts
privacy@dynadot.comabuse@omegatech.sc
04/10/2026
डिस्ट्रॉयलिस्ट प्रकाशित
04/10/2026
Monitoring Continues
डोमेन पहुंच योग्य या पहुंच-प्रतिबंधित रहता है; भविष्य की जाँच इस अवलोकन को अद्यतन कर सकती है।
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

सार्वजनिक ब्लॉकलिस्ट स्थिति

मिलते-जुलते डोमेन

79 संग्रहीत मिलते-जुलते डोमेन

सभी दिखाएँ (67)
metasmask.io insertion आंतरिक रिपोर्ट metramask.io insertion आंतरिक रिपोर्ट mewtamask.io insertion आंतरिक रिपोर्ट mmetamask.io homoglyph आंतरिक रिपोर्ट mtamask.io omission आंतरिक रिपोर्ट mwetamask.io insertion आंतरिक रिपोर्ट nmetamask.io homoglyph आंतरिक रिपोर्ट metamark.io bitsquatting आंतरिक रिपोर्ट metamaskj.io addition आंतरिक रिपोर्ट metammask.io homoglyph आंतरिक रिपोर्ट metamnask.io homoglyph आंतरिक रिपोर्ट emtamask.io transposition m-etamask.io hyphenation meamask.io omission meatmask.io transposition meramask.io replacement mertamask.io insertion metaamask.io repetition metaamsk.io transposition metaask.io omission metalmask.io insertion metamaask.io insertion metamadsk.io insertion metamaek.io replacement metamak.io omission metamas.io omission metamasak.io insertion metamasdk.io insertion metamask-io.com various metamasl.io replacement metamasm.io replacement metamsak.io transposition metamsk.io omission metamusk.io vowel-swap metamzsk.io replacement metarnask.io homoglyph metmaask.io transposition metmask.io omission metsamask.io insertion metsmask.io replacement mettamask.io repetition metwmask.io replacement metyamask.io insertion metzmask.io replacement meyamask.io replacement meytamask.io insertion mitamask.io vowel-swap mnetamask.io homoglyph mretamask.io insertion mrtamask.io replacement mstamask.io replacement mteamask.io transposition mwtamask.io replacement rnetamask.io homoglyph matamask.io bitsquatting mdtamask.io bitsquatting metamasi.io bitsquatting metamasj.io bitsquatting metamaska.io addition metamaskk.io addition metamaskl.io addition metamaso.io bitsquatting metamesk.io bitsquatting metamqsk.io bitsquatting metemask.io bitsquatting netamask.io homoglyph xn--metamas-bhb.io homoglyph

साक्ष्य और बाहरी रिपोर्टें

भेजे गए प्रमाण का स्नैपशॉट
Sent: Ledger records: 1 Case ID: PD-20261004-6C9137 Recipient: abuse@omegatech.sc
Page title stored with report: 恭喜,站点创建成功!
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 24.0 KB
Blocklist hits included with submission: MetaMask, SEAL
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
गहन विश्लेषण

क्या आप इस साइट से प्रभावित हुए?

6 evidence signal groups linked 1 reports recorded अंतिम ज्ञात सक्रिय
If credentials were compromised, report immediately. Do not engage with recovery scammers.

यदि आपने खाता क्रेडेंशियल, व्यक्तिगत या भुगतान जानकारी दर्ज की है, या इस डोमेन से कोई फ़ाइल डाउनलोड की है, तो तुरंत कार्रवाई करें। घटना की रिपोर्ट करने और अपनी सुरक्षा करने में आपकी सहायता के लिए नीचे संसाधन दिए गए हैं।

यूरोपोल
अपने ईयू देश के लिए आधिकारिक रिपोर्टिंग चैनल ढूंढें
National police directory
रिकवरी ठगों से सावधान रहें! अपराधी जांचकर्ता, वकील या रिकवरी एजेंट होने का नाटक करते हुए पीड़ितों से दोबारा संपर्क कर सकते हैं। अग्रिम शुल्क का भुगतान न करें या क्रेडेंशियल साझा न करें। रिकवरी धोखाधड़ी के बारे में और जानें →

अपने स्थानीय अधिकारियों को रिपोर्ट करें

आधिकारिक साइबर अपराध संपर्क, या एक शिकायत ड्राफ्ट बनाएं → प्राप्त करने के लिए अपना देश चुनें।

97-देश निर्देशिका

Template-based draft · optional AI wording assistance requires separate consent

एआई-सहायता प्राप्त ड्राफ्ट - घटना विवरण एआई प्रदाता द्वारा संसाधित किया जाता है · इसकी स्वयं समीक्षा करें और सबमिट करें

किसी भी डोमेन की जाँच करें

संग्रहीत ब्लॉकलिस्ट, WHOIS, DNS और सार्वजनिक स्कैन साक्ष्य का उपयोग करके खतरे का विश्लेषण

अभी स्कैन करें

फ़िशिंग की रिपोर्ट करें

संदिग्ध डोमेन हमारे थ्रेट डेटाबेस में जमा करें — समुदाय की सुरक्षा करें

रिपोर्ट करें

सीधा खतरा फीड

हाल की फ़िशिंग रिपोर्टें और उपलब्धता में परिवर्तन देखे गए

निगरानी करें

जानकारी में रहें, सुरक्षित रहें

लाइव खतरों की निगरानी करें या यदि आपको लगता है कि यह एक गलत सकारात्मक है तो इस लिस्टिंग को चुनौती दें।

सीधा खतरा फीड इस लिस्टिंग के खिलाफ अपील करें
HTML · IFRAME

इस रिपोर्ट को एम्बेड करें

इस थ्रेट इंटेलिजेंस को अपनी वेबसाइट या ब्लॉग पर साझा करें।

embed.html
<iframe
  src="https://phishdestroy.io/hi/embed/domain/68932.st"
  title="PhishDestroy threat report for 68932.st"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>