




Sécurité des domaines et renseignements sur les menaces

www-trezor-io-backups.nhcarwraps.com
“www-trezor-io-backups.nhcarwraps.com”
Verdict de menace
Critique
95/100 score de preuve
Disponibilité
Non vérifié
L'accessibilité actuelle n'est pas vérifiée
Signaux de risque
Détections VirusTotal : 14/89
URLQuery threat systems: 1 alert
Usurpation de l'identité de la marque : Trezor
Actions
API
ABUSE NOTICE · 72H+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@digitalocean.com.
The latest stored availability evidence still shows the domain reachable; 6 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
6 days
Reports sent
1
Latest case ID
PD-20260914-4DD2CD
Current status
Observed active at latest stored check
Résumé du rapport
www-trezor-io-backups.nhcarwraps.com — Non vérifié. Usurpation de l'identité de la marque : Trezor; Type d'arnaque : Impersonation. Résumé des preuves: VirusTotal 14/89 (BitDefender, CRDF, ESET, Forcepoint ThreatSeeker, Fortinet); URLQuery 1 alert; URLScan malicious verdict; PhishDestroy score 95/100. Bureau d’enregistrement: Namecheap.
L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.
Résumé des preuves
CRITIQUE
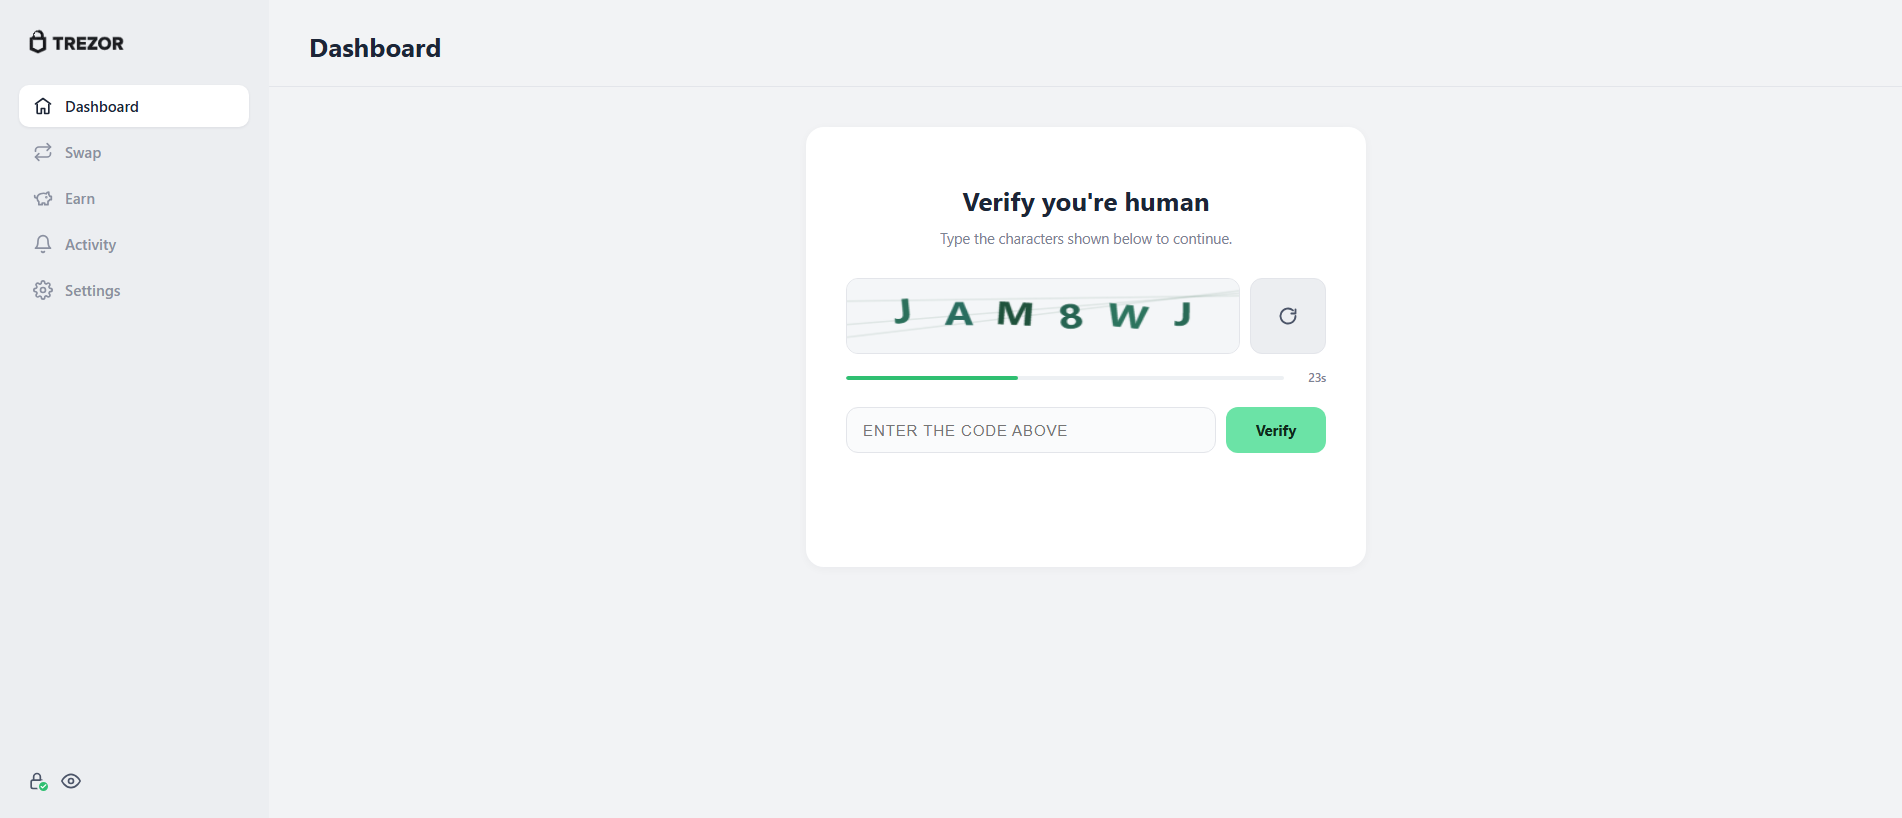
www-trezor-io-backups.nhcarwraps.com is a subdomain of nhcarwraps.com. PhishDestroy first observed the hostname on Sep 14, 2026. The hostname explicitly references Trezor; stored content metadata identifies the same apparent target. The captured page title is “www-trezor-io-backups.nhcarwraps.com”. Stored page analysis classifies the content as impersonation. Current evidence score: 95/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, URLQuery, and URLScan. VirusTotal recorded 14 detections among 89 engines: BitDefender, CRDF, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, MalwareURL, SOCRadar, Sophos, VIPRE, Webroot, desenmascara.me on Sep 16, 2026 at 02:04 UTC. URLQuery recorded 1 threat-system alert on Sep 14, 2026 at 07:29 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Trezor and assigned phishing as its category on Sep 15, 2026 at 03:30 UTC. Non-positive and contextual checks: The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 22:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 10:00 UTC.
The collector marked the hostname reachable on Sep 15, 2026 at 22:18 UTC, but did not retain the HTTP response code. Registration records for the registrable domain nhcarwraps.com list NAMECHEAP INC as the registrar and Apr 1, 2025 as the creation date. At collection time, the hostname resolved to 209.38.203.39 on AS14061 (DigitalOcean, LLC). The recorded endpoint location is Frankfurt am Main, DE. The stored server header is nginx/1.24.0 (Ubuntu). DOM analysis on Sep 14, 2026 at 10:20 UTC returned 88/100. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Dec 12, 2026; checked Sep 14, 2026 at 10:02 UTC.
The content indicators and 3 positive source findings support the current Trezor-themed impersonation classification.
VirusTotal
14 det.
URLQuery
1 threat alert
URLScan
Scamadviser
80/100Likely Safe
Certificat TLS
Let's Encrypt / YE1
Âge
1.5 yr
Statut observé
Non vérifié

DestroyList
Répertorié
Reports Sent
1
Couverture des données
VirusTotal
14 / 89
URLQuery
1 threat-system alert
OTX
no community references
CF Radar
scan completed
URLScan capture
rapport stocké
URLScan verdict
malicious
TLS
valid certificate, 82d
WHOIS
18 mo old
Capture d'écran
3 captures · 3 sources
Scamadviser
80/100
Renseignements sur la sécurité réseau
Threat Detection Systems
1 alert
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| OpenDNS | www-trezor-io-backups.nhcarwraps.com |
phishing | Phishing Block |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 14, 2026 · 09:28 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
209.38.203.39.
Processus de réponse aux menaces Pipeline
Découverte
Checks
Reports
Disponibilité
11/12
Sent Report Recorded
Stored sent-report record for registrar NAMECHEAP INC, hosting provider, 2 abuse contacts
abuse@digitalocean.comabuse@namecheap.com
Statut de la liste de blocage publique
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
Scanner note: timeout: raw=timeout; http=0; via=http_proxy; error=HTTPConnectionPool(host='46.202.59.133', port=8383): Read timed out. (read timeout=7)
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Capture enregistrée · 3 sources
Informations sur les domaines
Domaine
URLScan Verdict
Malveillant
score 100 Phishing brand: Trezor report ↗
Serveur / ASN
nginx/1.24.0 (Ubuntu) · AS14061 DigitalOcean, LLC
Réputation de l’IP
abuse score 0/100 0 reports checked 14/09/2026
Registrar (base domain)
Namecheap
 (US)
(US)
Registration (base domain)nhcarwraps.com · Créé 02/04/2025 — Expires 02/04/2027
Détails techniquesDNS, SAN SSL, horodatages
Première détection14/09/2026
DOM Analysis
IoC Extraction
Submitted URLhttps://www-trezor-io-backups.nhcarwraps.com/trezor/trezor/check-point.php
Serveurs de nomsns1.supercp.comns2.supercp.comns3.supercp.comns4.supercp.com
TLS Fingerprint
TLS Observation
Favicon Hash
ID du dossier
Technologies · 2 identified
Ubuntu
Operating systems
Nginx
Web servers
Reverse proxies
Detected via Cloudflare Radar · Wappalyzer engine
Signaler ce domaine
Envoyez des éléments de preuve et contribuez à protéger les autres
Analyse VirusTotal
14 / Les fournisseurs de sécurité 89 ont signalé ce domaine
View on VT
Last analyzed Previous stored snapshot: 2 detections
BitDefender
CRDF
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
MalwareURL
SOCRadar
Sophos
VIPRE
Webroot
desenmascara.me
Analyse des performances du site
Google PageSpeed Insights — mobile performance audit of www-trezor-io-backups.nhcarwraps.com · checked Sep 14, 2026
100
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
0.76s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
0.76s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Domaines ressemblants
74 domaines ressemblants enregistrés
treaor.io
replacement Rapport interne
treozr.io
transposition Rapport interne
trzezor.io
insertion Rapport interne
trzor.io
omission Rapport interne
rtrezor.io
insertion Rapport interne
terezor.io
insertion Rapport interne
trazor.io
bitsquatting Rapport interne
trexzor.io
insertion Rapport interne
5rezor.io
replacement
6rezor.io
replacement
frezor.io
replacement
grezor.io
replacement
Tout afficher (62)
rezor.io
omission
rrezor.io
replacement
rtezor.io
transposition
tdezor.io
replacement
teezor.io
replacement
terzor.io
transposition
tezor.io
omission
tfezor.io
replacement
tr.ezor.io
subdomain
tr3zor.io
replacement
treeor.io
replacement
treezor.io
insertion
treor.io
omission
treqor.io
replacement
tresor.io
replacement
trezeor.io
insertion
trezer.io
vowel-swap
trezior.io
insertion
trezir.io
replacement
trezkor.io
insertion
trezlor.io
insertion
trezo.io
omission
trezoe.io
replacement
trezoir.io
insertion
trezopr.io
insertion
trezor-io.com
various
trezorio.com
various
trezot.io
replacement
trezpor.io
insertion
trezpr.io
replacement
trezr.io
omission
trezro.io
transposition
trezxor.io
insertion
trezzor.io
insertion
trizor.io
vowel-swap
trozor.io
vowel-swap
trrzor.io
replacement
trtezor.io
insertion
trwezor.io
insertion
trwzor.io
replacement
trzeor.io
transposition
trzzor.io
replacement
ttezor.io
replacement
ttrezor.io
insertion
tyrezor.io
insertion
yrezor.io
replacement
ytrezor.io
insertion
prezor.io
bitsquatting
treazor.io
insertion
trerzor.io
insertion
trewzor.io
insertion
trexor.io
bitsquatting
trez0r.io
homoglyph
trezaor.io
insertion
trezora.io
addition
trezore.io
addition
trezoro.io
addition
trezorr.io
addition
trezors.io
addition
trezort.io
addition
xn--tezor-5bb.io
homoglyph
xn--trezo-9bb.io
homoglyph
Renseignement communautaire
1 signalement communautaire
CatégorieIMPERSONATION
Phishing: impersonation, impersonating Trezor
Données factuelles et rapports externes
Analyse de sécurité
Community Scam Report — ChainAbuse
1 report filed for www-trezor-io-backups.nhcarwraps.com (1 written by a person) · category: Impersonation · source checked
“Phishing: impersonation, impersonating Trezor”
— reported by Anonymous Trusted reporter on Sep 14, 2026 · Source: ChainAbuse (TRM Labs) — full report and evidence there.
Instantané des preuves transmises
Sent: Ledger records: 1
Case ID:
PD-20260914-4DD2CD Recipient: abuse@digitalocean.com Page title stored with report: Trezor — Verify
PDF notice generated Notice text archived (289 chars)
Abuse notice text as sent to the provider
Registrar: Namecheap Inc (United States)
Policy Violations: Domain Registration Agreement prohibits hacking, misuse of domain to conduct attacks, scam and fraudulent activities; AUP allows immediate suspension
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
OSINT et renseignement
DNS et réseau
Référencement naturel et nom de domaine
Ce site vous a-t-il affecté ?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.


Action Fraud
Signaler la fraude et la cybercriminalité en Angleterre, au Pays de Galles et en Irlande du Nord
Contact centre0300 123 2040
PhishDestroy listing review Pas un rapport des forces de l'ordre
Recours en matière de nom de domaine
Demandez un examen si vous possédez ce domaine et pensez que la liste est incorrecte
Méfiez-vous des escrocs qui prétendent vous aider à récupérer vos biens ! Les criminels peuvent recontacter leurs victimes tout en se faisant passer pour des enquêteurs, des avocats ou des agents de recouvrement. Ne payez pas de frais initiaux et ne partagez pas vos informations d'identification. En savoir plus sur la fraude liée aux aides à la reprise →
Signalez-le à vos autorités locales
Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.
Annuaire de 97 pays
Brouillon assisté par l'IA : les détails de l'incident sont traités par le fournisseur d'IA
Examinez-le et soumettez-le vous-même
Infrastructure et rapports associés
Infrastructure map · www-trezor-io-backups.nhcarwraps.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 1
Même bureau d’enregistrement: Namecheap 6
 app.xtbtrade.org
Trezor impersonation 8
These domains also target Trezor users. View all Trezor threats →
 faq-bridge-en-us.typedream.app
 trezor.win
Rapports récents sur les menaces 6
Rapports récemment ajoutés à partir de la base de données PhishDestroy. Ces liens de découverte n’impliquent pas d’infrastructure ou de propriété partagée.
 primarkpolska.pl
 ziajasklep.club
Vérifier n'importe quel domaine
Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique
Scanner maintenantSignaler une tentative d'hameçonnage
Signalez les domaines suspects à notre base de données des menaces — protégez la communauté
SignalerFlux d'alertes en temps réel
Rapports de phishing récents et changements de disponibilité observés
SurveillerRestez informés, restez en sécurité
Surveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif