




Sécurité des domaines et renseignements sur les menaces

movemaisclub.com
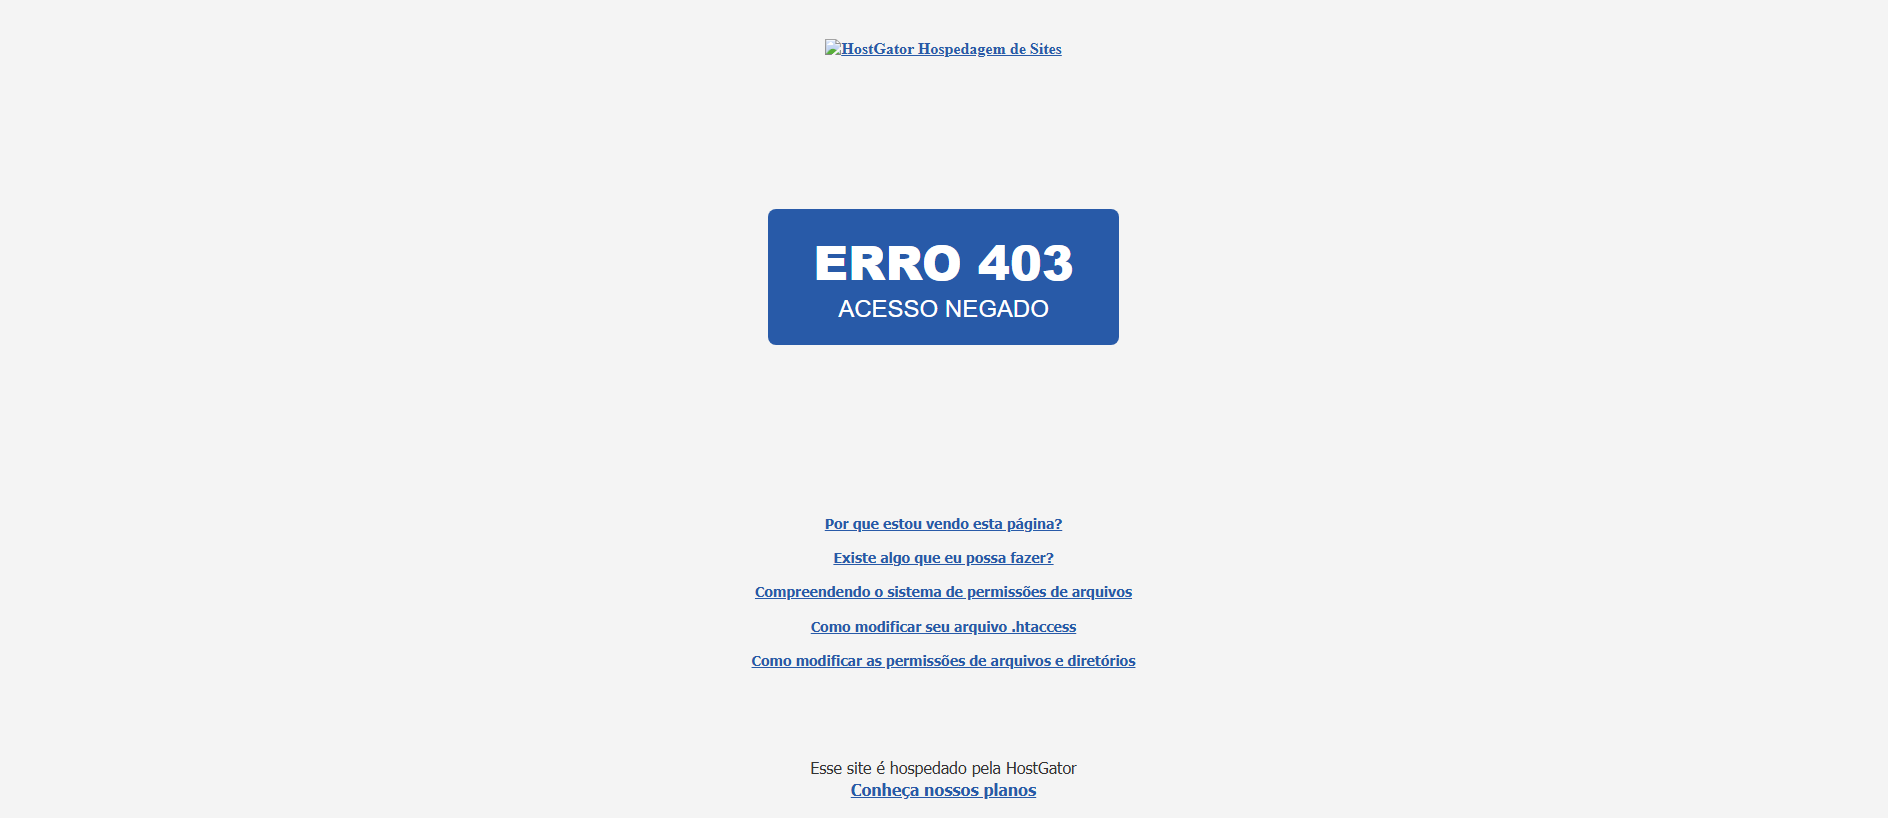
“403 - Acesso negado”
Verdict de menace
Critique
93/100 score de preuve
Disponibilité
Dernier actif connu
Dernière observation d'accessibilité stockée
Signaux de risque
Détections VirusTotal : 5/89
Usurpation de l'identité de la marque : Unknown
Domaine jeune : 22 jours
Dernier actif connu
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is domain-abuse@wix.com.
The latest stored availability evidence still shows the domain reachable; 20 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
20 days
Reports sent
1
Latest case ID
PD-20260831-A9B30E
Current status
HTTP 301 at latest stored check
Résumé du rapport
movemaisclub.com — Dernier actif connu (HTTP 301). Usurpation de l'identité de la marque : Unknown; Type d'arnaque : Impersonation. Résumé des preuves: VirusTotal 5/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar); PhishDestroy score 93/100. Bureau d’enregistrement: Wix.com.
L’analyse détaillée de PhishDestroy AI reste en anglais afin de préserver le relevé forensique original.
Résumé des preuves
CRITIQUE
PhishDestroy first observed movemaisclub.com on Aug 31, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “403 - Acesso negado”. Stored page analysis classifies the content as impersonation. Campaign clustering links the hostname to the Unknown kit. Current evidence score: 93/100 (critical).
One source contains a positive finding: VirusTotal. VirusTotal recorded 5 detections among 89 engines: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar on Sep 14, 2026 at 02:08 UTC. Non-positive and contextual checks: AlienVault OTX listed 4 community pulse references (not vendor detections) on Sep 11, 2026 at 06:06 UTC. The separate external-blocklist snapshot contained no matches on Sep 21, 2026 at 02:20 UTC. URLQuery recorded no positive detection on Aug 31, 2026 at 15:29 UTC. Google Safe Browsing returned no flag on Sep 14, 2026 at 04:00 UTC. URLScan completed without a malicious verdict (score 0) on Aug 31, 2026 at 17:08 UTC.
HTTP 301 was recorded on Sep 21, 2026 at 01:34 UTC. Registration records for the domain list Wix.com Ltd. as the registrar and Aug 29, 2026 as the creation date. Registration preceded first observation by 2 days. At collection time, the hostname resolved to 50.116.87.203. The recorded endpoint location is Vinhedo, BR. The stored server header is Apache. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt as the certificate issuer with validity through Nov 27, 2026; checked Aug 31, 2026 at 16:02 UTC.
Stored content provides classification context, but only one source contains a positive finding.
VirusTotal
5 det.
OTX references
URLScan
Certificat TLS
Let's Encrypt
Âge
22d Very New!
Statut observé
Dernier actif connu 301

DestroyList
Répertorié
Reports Sent
1
Couverture des données
VirusTotal
5 / 89
URLQuery
checked — no detections recorded
OTX
4 community references
CF Radar
scan completed
URLScan capture
rapport stocké
URLScan verdict
Analyse terminée
TLS
valid certificate, 85d
WHOIS
22d old
Capture d'écran
3 captures · 3 sources
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Domain Status Transition Sep 12, 2026 · 00:17 UTCDomain state transitioned from dead to alive.
-
Domain Status Transition Sep 11, 2026 · 00:36 UTCDomain state transitioned from alive to dead.
-
VirusTotal Detections Update Sep 2, 2026 · 00:06 UTCVirusTotal scanner detections updated from 4 to 5. Added scanner alerts: Gridinsoft.
-
VirusTotal Detections Update Sep 1, 2026 · 04:25 UTCVirusTotal scanner detections updated from 3 to 4. Added scanner alerts: CRDF.
-
VirusTotal Detections Update Sep 1, 2026 · 00:40 UTCVirusTotal scanner detections updated from 0 to 3. Added scanner alerts: Forcepoint ThreatSeeker, SOCRadar, alphaMountain.ai.
-
Threat First Observed Aug 31, 2026 · 17:10 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
50.116.87.203.
Processus de réponse aux menaces Pipeline
Découverte
Checks
Reports
Disponibilité
17/18
Sent Report Recorded
Stored sent-report record for registrar Wix.com Ltd., hosting provider, 2 abuse contacts
domain-abuse@wix.commovemaisclub.com@wix-domains.com
Statut de la liste de blocage publique
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
Pepyaka
Scanner note: redirect: raw=redirect_301; http=301; via=https_proxy; location=https://www.movemaisclub.com/; server=Pepyaka
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Capture enregistrée · 3 sources
Informations sur les domaines
Domaine
URLScan Verdict
Analyse terminée
score 0 report ↗
Serveur / ASN
Apache
Réputation de l’IP
abuse score 0/100 0 reports checked 31/08/2026
OTX Tags
2026-08activeall-domainsblocklistcontentcryptodomainesdrainerfraudlivemonthlyphishdestroyphishingscam
Bureau d’enregistrement
Wix.com
 (US)
(US)
EnregistrementCréé 29/08/2026 (22d · Very New!) — Expires 29/08/2027
Statut HTTP301 Moved Permanently
Détails techniquesDNS, SAN SSL, horodatages
Première détection31/08/2026
IoC Extraction
Submitted URLhttp://movemaisclub.com/
Serveurs de nomsns2.wixdns.netns3.wixdns.net
TLS Fingerprint
TLS Observation
Favicon Hash
ID du dossier
Technologies · 2 identified
Apache HTTP Server
Web servers
jQuery
JavaScript libraries
Detected via Cloudflare Radar · Wappalyzer engine
Signaler ce domaine
Envoyez des éléments de preuve et contribuez à protéger les autres
Analyse VirusTotal
5 / Les fournisseurs de sécurité 89 ont signalé ce domaine
View on VT
Last analyzed First positive detection Previous stored snapshot: 5 detections
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Gridinsoft
SOCRadar
Analyse des performances du site
Google PageSpeed Insights — mobile performance audit of movemaisclub.com · checked Aug 31, 2026
100
Good
Performance
FCP
1.11s
First Contentful Paint
LCP
1.11s
Largest Contentful Paint
CLS
0.035
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.05s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Données factuelles et rapports externes
Analyse de sécurité
Instantané des preuves transmises
Sent: Ledger records: 1
Case ID:
PD-20260831-A9B30E Recipient: domain-abuse@wix.com Page title stored with report: 403 - Acesso negado
PDF notice generated Notice text archived (653 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (US):
18 U.S.C. § 1343 - Wire Fraud
18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA)
15 U.S.C. § 45 - FTC Act (Deceptive Practices)
Federal laws prohibit wire fraud, computer fraud, and deceptive business practices.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT et renseignement
DNS et réseau
Référencement naturel et nom de domaine
Ce site vous a-t-il affecté ?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Si vous avez saisi des informations d'identification de compte, des informations personnelles ou de paiement, ou téléchargé un fichier à partir de ce domaine, agissez immédiatement. Vous trouverez ci-dessous des ressources pour vous aider à signaler l'incident et à vous protéger.


Action Fraud
Signaler la fraude et la cybercriminalité en Angleterre, au Pays de Galles et en Irlande du Nord
Contact centre0300 123 2040
PhishDestroy listing review Pas un rapport des forces de l'ordre
Recours en matière de nom de domaine
Demandez un examen si vous possédez ce domaine et pensez que la liste est incorrecte
Méfiez-vous des escrocs qui prétendent vous aider à récupérer vos biens ! Les criminels peuvent recontacter leurs victimes tout en se faisant passer pour des enquêteurs, des avocats ou des agents de recouvrement. Ne payez pas de frais initiaux et ne partagez pas vos informations d'identification. En savoir plus sur la fraude liée aux aides à la reprise →
Signalez-le à vos autorités locales
Sélectionnez votre pays pour obtenir contacts officiels en matière de cybercriminalité ou créer un projet de plainte →.
Annuaire de 97 pays
Brouillon assisté par l'IA : les détails de l'incident sont traités par le fournisseur d'IA
Examinez-le et soumettez-le vous-même
Infrastructure et rapports associés
Infrastructure map · movemaisclub.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 8


Même bureau d’enregistrement: Wix.com 6
 tlknan.net
Unknown impersonation 8
These domains also target Inconnu users. View all Unknown threats →
Unknown kit 8
Part of the Inconnu phishing campaign. View all campaign domains →
Vérifier n'importe quel domaine
Analyse des menaces à l'aide de listes de blocage stockées, de WHOIS, de DNS et de preuves d'analyse publique
Scanner maintenantSignaler une tentative d'hameçonnage
Signalez les domaines suspects à notre base de données des menaces — protégez la communauté
SignalerFlux d'alertes en temps réel
Rapports de phishing récents et changements de disponibilité observés
SurveillerRestez informés, restez en sécurité
Surveillez les menaces en temps réel ou signalez cette alerte si vous pensez qu'il s'agit d'un faux positif