IC3 del FBI
Denunciar delitos cometidos a través de Internet en los Estados Unidos
Federal tips line1-800-CALL-FBI

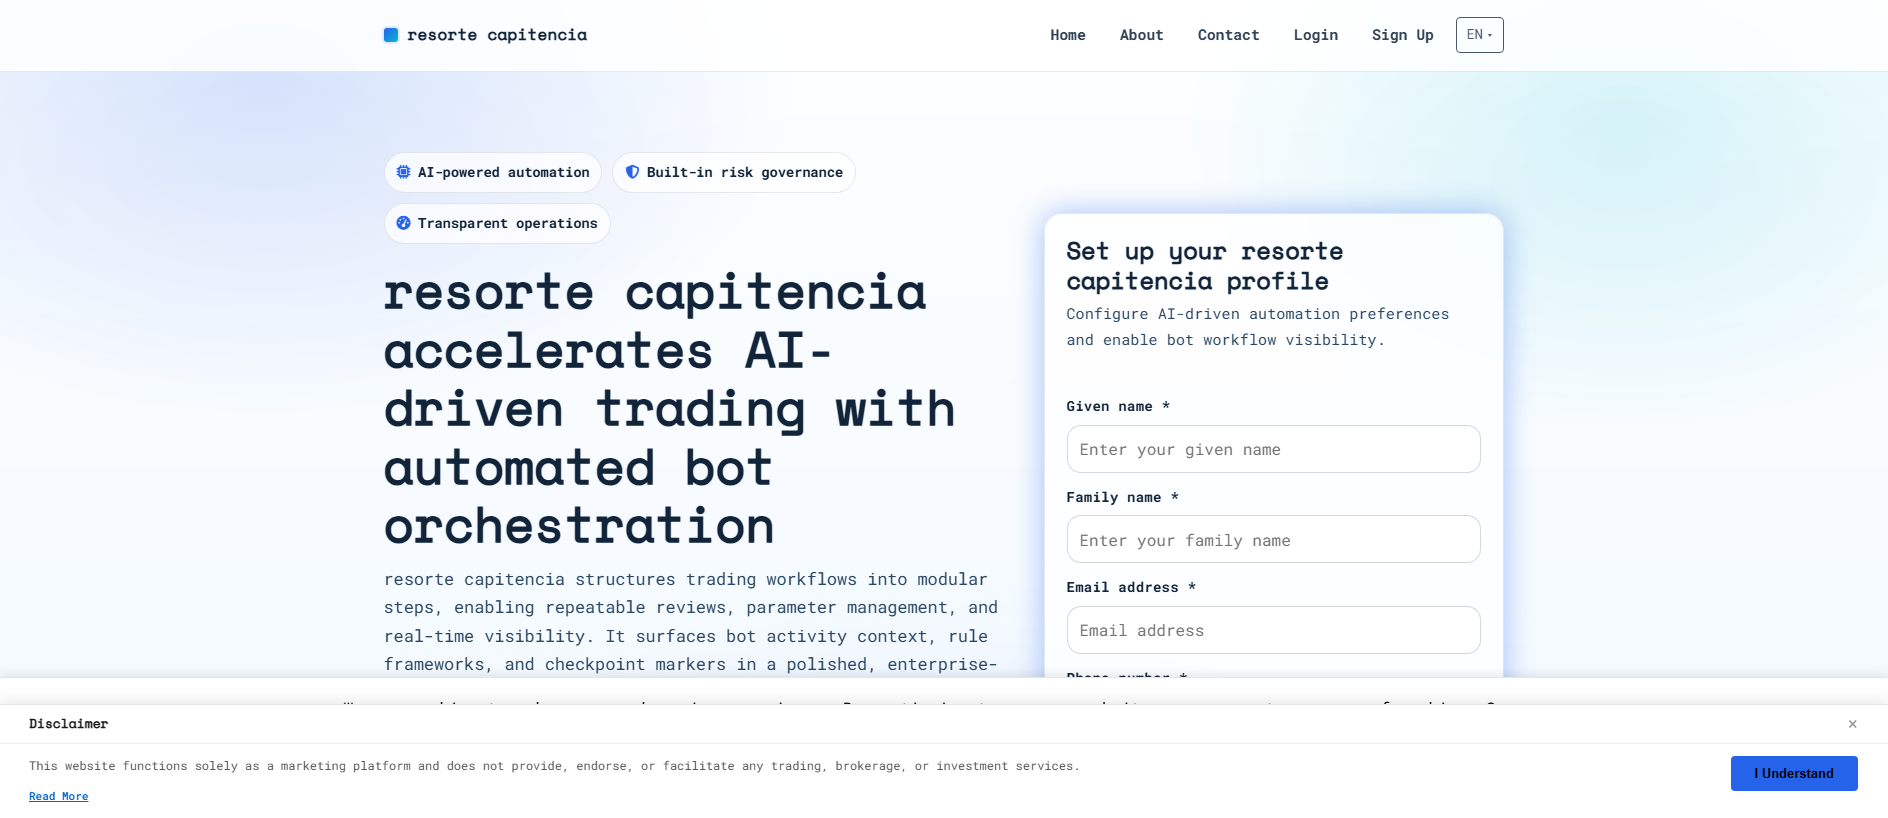
“resorte capitencia | a premium AI | Official Website”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@dynadot.com.
The latest stored availability evidence still shows the domain reachable; 6 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
resortecapitencia.pro — Último activo conocido (HTTP 200). Suplantación de marca: Unknown; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 17/89 (alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, CyRadar); URLQuery 5 alerts; CF Radar malicious; PhishDestroy score 100/100. Registrador: Dynadot.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.
PhishDestroy first observed resortecapitencia.pro on Sep 15, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “resorte capitencia | a premium AI | Official Website”. Page analysis recorded additional brand references to Across and Celer. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, Cloudflare Radar, and URLQuery. VirusTotal recorded 17 detections among 89 engines: alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, Seclookup, SOCRadar, Sophos, VIPRE, Webroot on Sep 19, 2026 at 02:21 UTC. Cloudflare Radar classified the hostname as malicious and placed it in the malware category; its verdict timestamp was not retained. URLQuery recorded 5 threat-system alerts on Sep 15, 2026 at 18:15 UTC. Non-positive and contextual checks: AlienVault OTX listed 5 community pulse references (not vendor detections) on Sep 17, 2026 at 11:34 UTC. The separate external-blocklist snapshot contained no matches on Sep 22, 2026 at 10:20 UTC. Google Safe Browsing returned no flag on Sep 22, 2026 at 10:01 UTC. URLScan completed without a malicious verdict (score 0) on Sep 16, 2026 at 03:30 UTC.
HTTP 200 was recorded on Sep 22, 2026 at 10:44 UTC. Registration records for the domain list Dynadot Inc as the registrar and Jul 12, 2026 as the creation date. At collection time, the hostname resolved to 185.62.58.179 on AS62370 (Snel.com B.V.). The recorded endpoint location is Rotterdam, NL. The stored server header is ESF. DOM analysis on Sep 15, 2026 at 18:20 UTC returned 98/100. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists ZeroSSL GmbH / ZeroSSL ECC DV SSL CA 2 as the certificate issuer with validity through Oct 19, 2026; checked Sep 15, 2026 at 19:02 UTC.
The content indicators and 3 positive source findings support the current Unknown-themed impersonation classification.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| OpenDNS | resortecapitencia.pro |
phishing | Phishing Block |
| Cloudflare DNS | resortecapitencia.pro |
malicious | Sinkholed |
| DigiCert UltraDNS | resortecapitencia.pro |
malicious | Sinkholed |
| DNS4EU | resortecapitencia.pro |
malicious | Sinkholed |
| Quad9 DNS | resortecapitencia.pro |
malicious | Sinkholed |
185.62.58.179. Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy
 (US)

Google PageSpeed Insights — mobile performance audit of resortecapitencia.pro · checked Sep 15, 2026
PD-20260915-9E146D Recipient: abuse@dynadot.com Registrar: Dynadot LLC / Dynadot Inc (United States) Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Estos dominios también se dirigen a los usuarios de Unknown. Ver todas las amenazas de «Unknown» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.