Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
facebookbonus.emmanueldegreatltd.com favicon

facebookbonus.emmanueldegreatltd.com

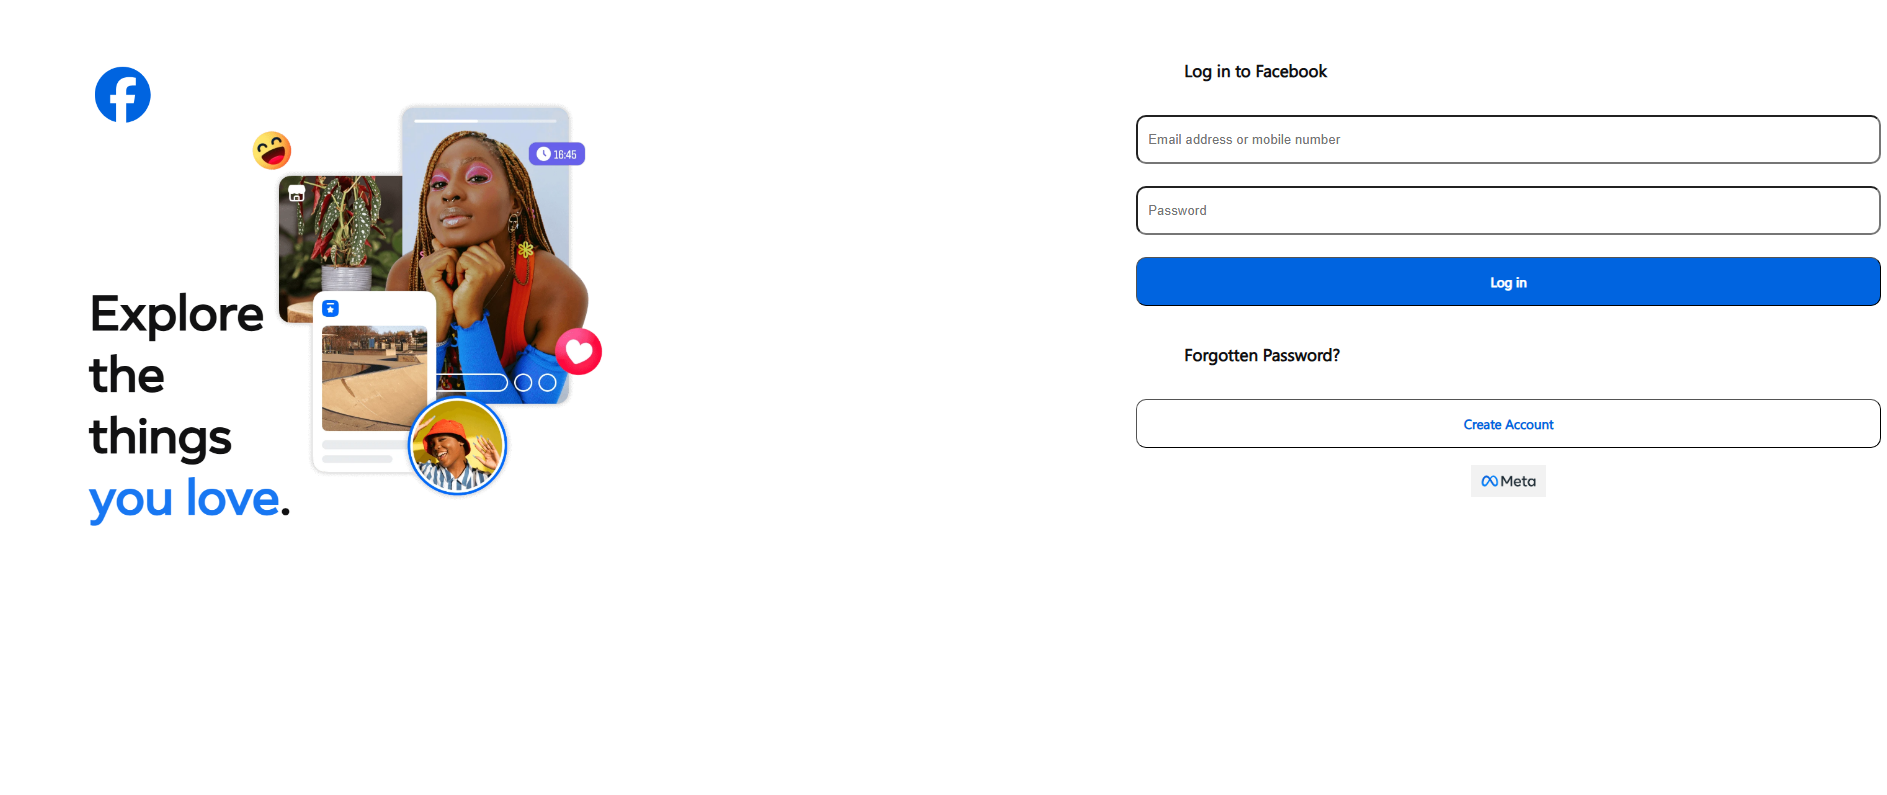
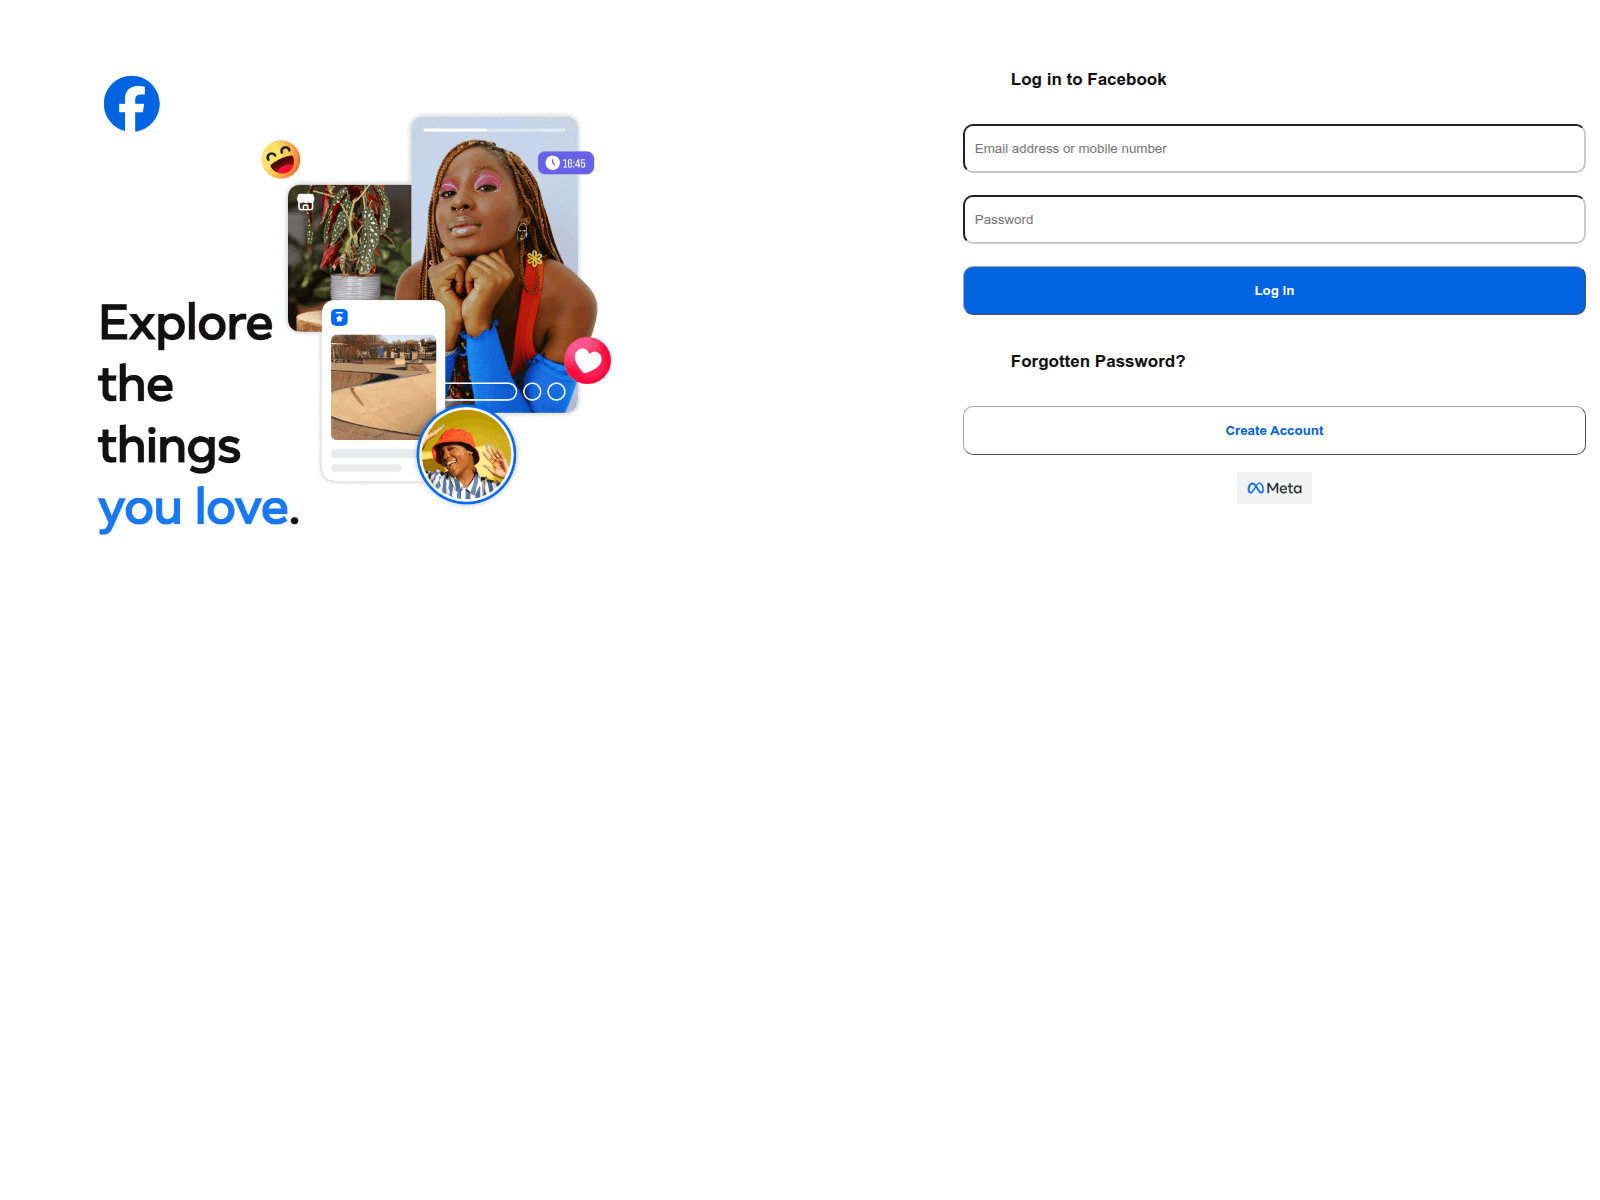
“Facebook”

Registrador
PDR
Resolved IP
147.124.219.81
Registered
13/06/2019
Veredicto de amenaza Crítico
Disponibilidad Último activo conocido Última observación de accesibilidad almacenada Observado
Source: HTTP probe
VirusTotal detecciones: 22/92 Coincidencias de la lista de bloqueo almacenadas: 1 Suplantación de marca: Facebook
06/10/2026 Facebook 1 Report Sent
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 22. Listas de bloqueo públicas que informan una coincidencia: 1. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@spinservers.com. The latest stored availability evidence still shows the domain reachable; 6 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
6 days
Reports sent
1
Latest case ID
PD-20261006-BA6675
Current status
HTTP 302 at latest stored check
Resumen del informe

facebookbonus.emmanueldegreatltd.com — Último activo conocido (HTTP 302). Suplantación de marca: Facebook; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 22/92 (alphaMountain.ai, BitDefender, Certego, CRDF, CyRadar); URLQuery 3 det.; URLScan malicious verdict; 1 external blocklist match (Phishunt); CF Radar malicious; PhishDestroy score 100/100. Registrador: PDR.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

VirusTotal
VirusTotal
22 det.
URLQuery
URLQuery
3 det.
CF Radar
Malicioso
URLScan
URLScan
Certificado TLS
Caducado o no verificado
Edad
7.3 yr
Estado observado
Último activo conocido 302
PhishDestroy
DestroyList
Incluido
Reports Sent
1

Source evidence

7 sources

VirusTotal

22 / 92

Denunciar

CF Radar

provider verdict: malicious

Denunciar

URLScan verdict

malicious

Denunciar

OTX

no community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

Google Safe Browsing

Checked; no threat flag recorded

Denunciar
Inteligencia de seguridad de red
CF Cloudflare Radar Verdict Malicioso
Phishing Security threats Phishing

Resumen de las pruebas

Crítico
VirusTotal
22/92
URLScan
Stored capture

facebookbonus.emmanueldegreatltd.com is a subdomain of emmanueldegreatltd.com. PhishDestroy first observed the hostname on Oct 6, 2026. The hostname explicitly references Facebook; stored content metadata identifies the same apparent target. The captured page title is “Facebook”. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).

Positive findings are stored from 5 sources: VirusTotal, Phishunt, Cloudflare Radar, URLQuery, and URLScan. VirusTotal recorded 22 detections among 92 engines: alphaMountain.ai, BitDefender, Certego, CRDF, CyRadar, ESET, Emsisoft, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, LevelBlue, Lionic, MalwareURL, Netcraft, Seclookup, SOCRadar, Sophos, URLQuery, VIPRE, Webroot on Oct 13, 2026 at 16:20 UTC. Phishunt listed the hostname in the separate external-blocklist snapshot on Oct 13, 2026 at 14:20 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories phishing and security threats; its verdict timestamp was not retained. URLQuery recorded 3 detections; no observation timestamp was retained. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Facebook and assigned phishing as its category on Oct 7, 2026 at 03:30 UTC.

HTTP 302 was recorded on Oct 13, 2026 at 10:08 UTC. Latest classified outcome: redirect observed; cause http redirect on Oct 13, 2026 at 08:08 UTC. Registration records for the registrable domain emmanueldegreatltd.com list PDR Ltd. d/b/a PublicDomainRegistry.com as the registrar and Jun 13, 2019 as the creation date. At collection time, the hostname resolved to 147.124.219.81 on AS396073 (MAJESTIC-HOSTING-01 - Majestic Hosting Solutions, LLC, US). The recorded endpoint location is Dallas, US. The stored server header is LiteSpeed. DOM analysis on Oct 9, 2026 at 18:23 UTC returned 88/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YR1 as the certificate issuer with validity through Dec 6, 2026; checked Oct 6, 2026 at 22:02 UTC.

The content indicators and 5 positive source findings support the current Facebook-themed impersonation classification.

Análisis de detección y evasión

Se sospecha que se está utilizando «cloaking»: los títulos del escáner y del visitante no coinciden

Aún no se ha escaneado Aún no se ha registrado ninguna diferencia entre los rastreadores y los navegadores

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
Aún no se ha escaneado
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
LiteSpeed

Nota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://facebookbonus.emmanueldegreatltd.com/cgi-sys/suspendedpage.cgi; server=LiteSpeed

Título que se muestra en el escáner de seguridad302 Found
Título que se muestra al visitante del navegadorFacebook
Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 captures

Domain details

Dominio
URLScan Verdict Malicioso score 100 Phishing brand: Facebook report ↗
Reputación de IP abuse score 0/100 0 reports checked 07/10/2026
Registration (base domain)emmanueldegreatltd.com · Creado 13/06/2019 — Expires 13/06/2027
Estado HTTP302 Found (Temporary)
Detalles técnicosProvenance & timestamps
Primera detección06/10/2026
DOM Analysisanalyzed 09/10/2026score 88/1001 brand signal
Submitted URLhttps://facebookbonus.emmanueldegreatltd.com/
Favicon Hash
ID del caso
Título de la página
Facebook
Impersonates
Facebook
Certificado TLS
Certificate hostname mismatch · Emitido por Let's Encrypt / YR1 · stored validity ends in 53 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
147.124.219.81
Network ASN
AS396073
Organization
Majestic Hosting Solutions, LLC
Observed location
Dallas, US
Server header
LiteSpeed

Servidores de nombres 2

  • ns41.doveserver.com
  • ns42.doveserver.com

Location describes the IP network.

Certificado TLS

Issuer
Let's Encrypt / YR1
Valid from
2026-09-07 12:51:43
Valid until
2026-12-06 12:51:42
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-06 22:02:08 UTC
Collection source
PhishDestroy collector
Certificate fingerprint05be2dda12735d8bd366fde7cce41d1c81a47d1503b26ca94131dedb44bc72bc
Certificate names · 1 SANs
  • www.facebookbonus.emmanueldegreatltd.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 147.124.219.81rapiddns.io

Latest Classified Outcome 2026-10-13 10:08:23 UTC

Primary outcome Redirecting reason: HTTP redirect observed 80% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Redirecting Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Redirecting HTTP redirect observed 80% 2026-10-13 10:08:23 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-10-13 10:08:23 UTC last content: 2026-10-07 10:17:19 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Tecnologías · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

22 / Los proveedores de seguridad de 92 marcaron este dominio
View on VT
Last analyzed Previous stored snapshot: 22 detections
alphaMountain.ai
BitDefender
Certego
CRDF
CyRadar
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
MalwareURL
Netcraft
Seclookup
SOCRadar
Sophos
URLQuery
VIPRE
Webroot
Análisis del rendimiento del sitio

Google PageSpeed Insights — mobile performance audit of facebookbonus.emmanueldegreatltd.com · checked Oct 6, 2026

88
Needs Work
Performance
FCP
0.76s
First Contentful Paint
LCP
3.9s
Largest Contentful Paint
CLS
0.002
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.29s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-10-12 12:24:53 UTC
    VirusTotal scanner detections updated from 23 to 22. Added scanner alerts: LevelBlue. Resolved alerts: DNS8, OpenPhish.
  2. VirusTotal Detections Update 2026-10-10 08:22:58 UTC
    VirusTotal scanner detections updated from 22 to 23. Added scanner alerts: DNS8.
  3. VirusTotal Detections Update 2026-10-09 15:02:14 UTC
    VirusTotal scanner detections updated from 22 to 22. Added scanner alerts: OpenPhish, URLQuery. Resolved alerts: DNS8, LevelBlue.
  4. VirusTotal Detections Update 2026-10-08 01:01:15 UTC
    VirusTotal scanner detections updated from 21 to 22. Added scanner alerts: DNS8.
  5. Threat First Observed 2026-10-06 21:11:39 UTC
    Domain ingestion complete. Initial state is marked as unknown pointing to IP 147.124.219.81.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Notifications
Monitoring

15 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
facebookbonus.emmanueldegreatltd.com detectados y puestos en cola para su análisis completo
06/10/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
06/10/2026
URLScan Verdict
URLScan returned a malicious verdict · score 100
07/10/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
22/92 recorded on VirusTotal
13/10/2026
Detección de listas de bloqueo
Se encuentra en 1 blocklist: Phishunt
13/10/2026
CF Radar: Malicious
Cloudflare Radar classified this domain as phishing, Security threats, Phishing
Brand Impersonation
Impersonation of Facebook
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
06/10/2026
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
13/10/2026
VT Detection -1
1 detection removed (23 → 22)
12/10/2026
VT Detection +1
+1 new detection (22 → 23): DNS8
10/10/2026
VT Detection +1
+1 new detection (21 → 22): DNS8
08/10/2026
Sent Report Recorded
Stored outgoing record associated with registrar PDR Ltd. d/b/a PublicDomainRegistry.com, 3 abuse contacts
abuse@spinservers.comsamkay92003@gmail.comabuse-contact@publicdomainregistry.com
06/10/2026
Lista de destrucción publicada
06/10/2026
Monitoring Continues
El dominio sigue siendo accesible o tiene acceso restringido; controles futuros pueden actualizar esta observación.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Estado de la lista de bloqueados pública

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20261006-BA6675 Recipient: abuse@spinservers.com
Page title stored with report: Facebook
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 215.6 KB
PDF notice generated Notice text archived (640 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (NG):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and NG's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Análisis en profundidad

¿Te ha afectado esta página web?

5 evidence signal groups linked 1 reports recorded Último activo conocido
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.
Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/facebookbonus.emmanueldegreatltd.com"
  title="PhishDestroy threat report for facebookbonus.emmanueldegreatltd.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>