VirusTotal
5 / 89
Denunciar


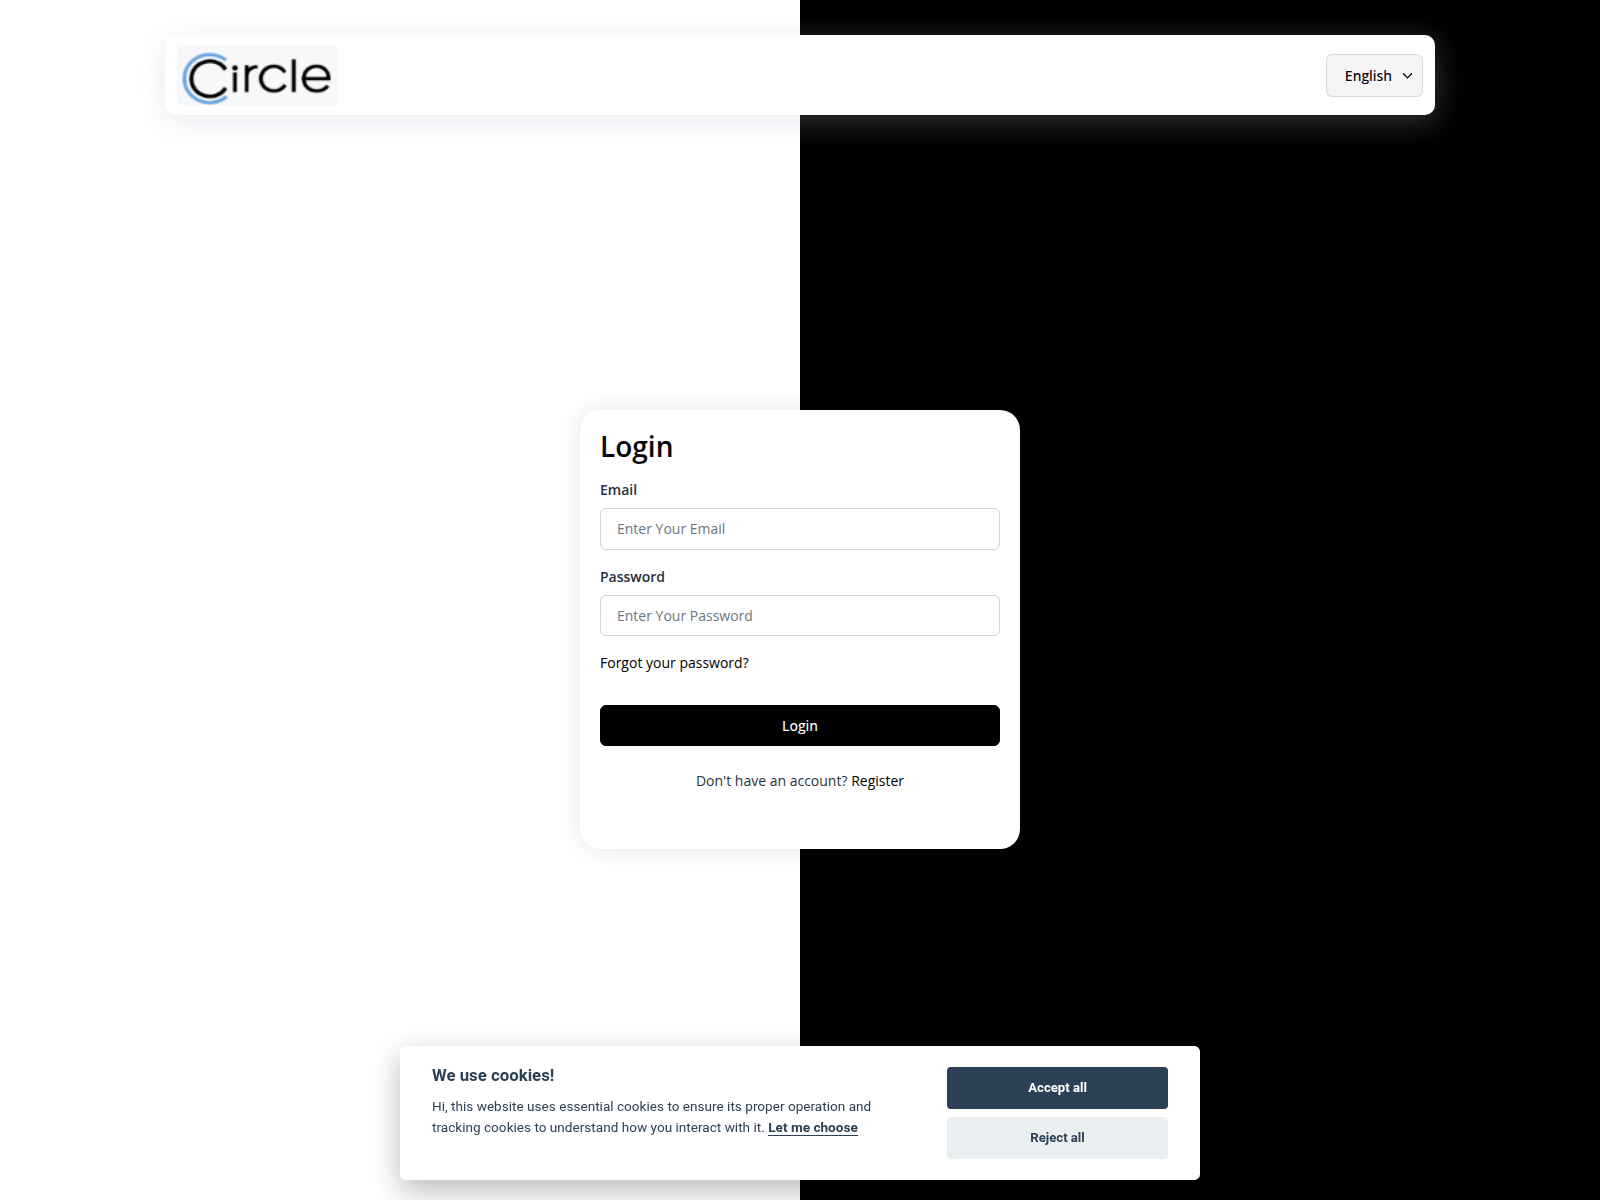
“Circle - Login”
erp.circle.co.zm — Último activo conocido (HTTP 302). Tipo de estafa: Credential Phishing. Resumen de las pruebas: VirusTotal 5/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar); 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 85/100. Registrador: Zamnet.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

On 2026-10-01, erp.circle.co.zm returned an HTTP status code 302 according to the recorded HTTP check. The same evidence set records a PageSpeed performance score of 73, captured on 2026-09-06, which describes a separate measurement of the domain.
The HTTP check on 2026-10-01 recorded a 302 status for erp.circle.co.zm. The external blocklist review named MetaMask and SEAL, with an external blocklist count of 2. On 2026-09-20, VirusTotal reported 5 detections across 89 scanners. The domain was first observed on 2026-09-06, and the SSL certificate issuer was Let's Encrypt / YE2, as scanned on 2026-09-06.
The recorded HTTP status describes one response captured on its check date, while the blocklist entries and VirusTotal detections reflect separate source observations of erp.circle.co.zm. Because the HTTP check, VirusTotal scan, and blocklist review carry different dates, the records allow comparison of what each source reported at its own point in time rather than a single combined picture. The PageSpeed score and SSL scan share a date but measure different things, so they should be read as distinct data points.
Future reviews of erp.circle.co.zm should preserve the HTTP check record and the external blocklist entries so later observations can be compared against them. Keep the VirusTotal result and the PageSpeed score as separate reference records for the same purpose. Retain the first-observed entry alongside the SSL scan record to document the earliest and certificate-related observations in the evidence set.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
LiteSpeedNota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://erp.circle.co.zm/login; server=LiteSpeed
 (ZM)
dns1.namecheaphosting.comdns2.namecheaphosting.comLocation describes the IP network.
3165a588814b974452bb7d5f3360e9fe5ea399150f83fcc988ce8c455712f899Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of erp.circle.co.zm · checked Sep 6, 2026
162.0.209.91. 10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
Otro dominio de phishing comparte esta IP de origen: posible infraestructura compartida.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.