Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
bnbwalle.com favicon

bnbwalle.com

“banwalle”

Veredicto de amenaza Crítico Puntuación de evidencia 100/100
Disponibilidad Último activo conocido Última observación de accesibilidad almacenada
VirusTotal detecciones: 8/89 Coincidencias de la lista de bloqueo almacenadas: 2 Suplantación de marca: Trust Wallet Último activo conocido
OTX: 3 refs 14/09/2026 Trust Wallet 1 Report Sent CDN
Actions API
⚠️
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 8. Listas de bloqueo públicas que informan una coincidencia: 2. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is rtr-security-threats@realtimeregister.com. The latest stored availability evidence still shows the domain reachable; 8 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
8 days
Reports sent
1
Latest case ID
PD-20260914-3D0C13
Current status
HTTP 302 at latest stored check
Resumen del informe

bnbwalle.com — Último activo conocido (HTTP 302). Suplantación de marca: Trust Wallet; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 8/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet, Gridinsoft); URLScan malicious verdict; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 100/100. Registrador: Realtime.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

Resumen de las pruebas

CRÍTICO
Puntuación
100/100

Assessment
Stored evidence for bnbwalle.com: VirusTotal recorded 3 detections among 89 scanners on 2026-09-14. That ratio reproduces the stored check in its original units and is not converted into another measure. MetaMask and SEAL appear as named external blocklist observations for bnbwalle.com. Each item in this report remains at the scope supplied by its dated source record.

Detection Evidence
VirusTotal records 3 detections among 89 scanners in the stored snapshot dated 2026-09-14. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-09-14 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.

Source Context
MetaMask and SEAL are recorded as named external blocklist observations for bnbwalle.com in the snapshot dated 2026-09-14. The stored MetaMask and SEAL blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains bnbwalle.com as a publisher record. That PhishDestroy record is counted separately from the MetaMask and SEAL external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.

Reachability and Timeline
The record first observed bnbwalle.com on 2026-09-14. The MetaMask and SEAL blocklist snapshot is dated 2026-09-14 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-08-06. A URLScan reference was stored on 2026-09-14 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.

Registration and Infrastructure
For bnbwalle.com, the registrar field records Realtime Register B.V.; this is kept as an exact source value. The source stores 104.26.13.220 as the observed address in this record. The registration date for bnbwalle.com is recorded as 2026-08-06. The stored ASN observation records 13335 and Cloudflare, Inc. in this record. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.

Conclusion
The bnbwalle.com record states that VirusTotal recorded 3 detections among 89 scanners on 2026-09-14. MetaMask and SEAL remain named blocklist observations from the snapshot dated 2026-09-14. PhishDestroy remains a separate publisher catalogue entry in the stored record. For bnbwalle.com, the registrar field records Realtime Register B.V.; this remains separate from the other source fields. The observed address field in this record contains 104.26.13.220. The supported conclusion is bounded to the exact stored observations for bnbwalle.com. Any statement beyond those source values would require additional dated material.

Recommended Actions
Avoid submitting sensitive information to bnbwalle.com during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain bnbwalle.com as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and MetaMask and SEAL blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to bnbwalle.com. The stored record does not justify extending that rule to 104.26.13.220 or to other infrastructure records.

VirusTotal
VirusTotal
8 det.
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
Certificado TLS
Google Trust Services / WE1
Edad
2 mo New
Estado observado
Último activo conocido 302
PhishDestroy
DestroyList
Incluido
Reports Sent
1
Cobertura de los datos VirusTotal 8 / 89 URLQuery checked — no detections recorded OTX 3 community references CF Radar scan completed URLScan capture informe almacenado URLScan verdict malicious TLS valid certificate, 44d WHOIS 2 mo old Captura de pantalla 3 captures · 3 sources Scamadviser 80/100

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed Sep 14, 2026 · 15:54 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 104.26.13.220.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Checks
Reports
Disponibilidad
13/14
Sent Report Recorded
Stored sent-report record for registrar Realtime Register B.V., hosting provider, 1 abuse contact
rtr-security-threats@realtimeregister.com
14/09/2026

Estado de la lista de bloqueados pública

Análisis de detección y evasión

Se sospecha que se está utilizando «cloaking»: los títulos del escáner y del visitante no coinciden

Aún no se ha escaneado Aún no se ha registrado ninguna diferencia entre los rastreadores y los navegadores

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
Aún no se ha escaneado
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
cloudflare

Nota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://bnbwalle.com/mobile/index.html; server=cloudflare

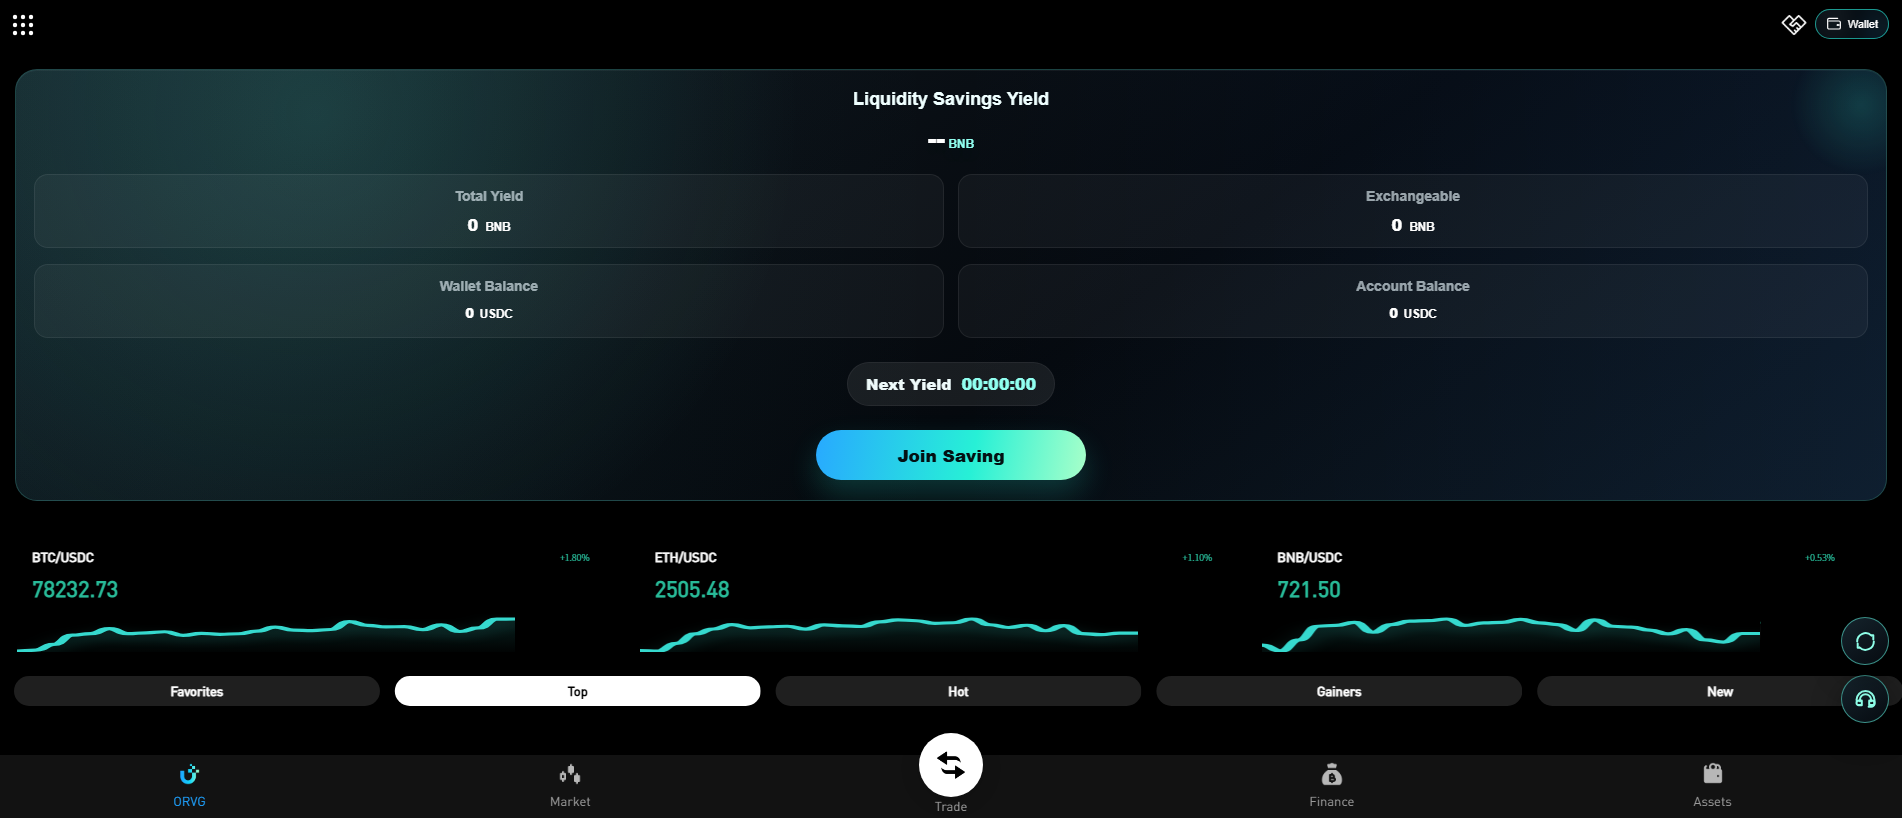
Título que se muestra en el escáner de seguridadRedirecting to https://bnbwalle.com/mobile/index.html
Título que se muestra al visitante del navegadorbanwalle
Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 sources

Inteligencia de dominios

Dominio
URLScan Verdict Malicioso score 100 Phishing brand: Trust Walletbrand: Binance report ↗
Servidor / ASN cloudflare · AS13335 Cloudflare, Inc.
IP Context Cloudflare shared edge origin IP hidden La reputación de Edge-IP no se atribuye a este dominio.
OTX Tags 2026-09all-domainsblocklistcryptodominiosdrainerfraudlivemonthlyphishdestroyphishingscam
Registrador Realtime
Dirección IP 104.26.13.220 CDN
UbicaciónCA Toronto, CA
RedAS13335 · Cloudflare, Inc.
La IP de origen está oculta detrás de un proxy CDN. Los resultados de IP inversa para la dirección perimetral contienen inquilinos no relacionados; encontrar el origen requiere DNS pasivo o datos de transparencia de certificado.
RegistroCreado 06/08/2026 (47d · New) Expires 06/08/2027
Estado HTTP302 Found (Temporary)
Detalles técnicosDNS, SAN de SSL, marcas de tiempo
Primera detección14/09/2026
DOM Analysisanalyzed 14/09/2026score 95/10017 brand signals
IoC Extractionscanned 15/09/20260 wallet · 0 Telegram IoCs
Submitted URLhttp://bnbwalle.com/
Servidores de nombresnico.ns.cloudflare.comval.ns.cloudflare.com
TLS Fingerprint
TLS Observationvalid from 08/08/2026scanned 14/09/2026
Favicon Hash
ID del caso
Título de la página
banwalle
Impersonates
Argent Backpack Binance Bitget Coinbase Exodus Ledger MetaMask +9
Certificado TLS
Valid transport encryption · Emitido por Google Trust Services / WE1 · valid for 44 days
Cruce de inteligencia de amenazas · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Tecnologías · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

8 / Los proveedores de seguridad de 89 marcaron este dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
Kaspersky
SOCRadar
VIPRE

Dominios similares

104 dominios similares almacenados

Mostrar todo (88)
t.rustwallet.com subdomain trastwallet.com vowel-swap trostwallet.com vowel-swap trsutwallet.com transposition trusfwallet.com replacement trusrwallet.com replacement trusstwallet.com plural trusttwallet.com repetition trustw.allet.com subdomain trustwa.llet.com subdomain trustwaklet.com replacement trustwalelt.com transposition trustwalket.com replacement trustwall3t.com replacement trustwalleet.com repetition trustwallef.com replacement trustwaller.com replacement trustwallit.com vowel-swap trustwalllet.com repetition trustwallot.com vowel-swap trustwallte.com transposition trustwlalet.com transposition trustwollet.com vowel-swap trustwullet.com vowel-swap trustwwllet.com replacement trustwzllet.com replacement trutswallet.com transposition truustwallet.com repetition trystwallet.com replacement turstwallet.com transposition rustwallet.com omission trestwallet.com bitsquatting trrustwallet.com insertion tructwallet.com bitsquatting truestwallet.com insertion truhstwallet.com insertion truistwallet.com insertion trusdtwallet.com insertion trusdwallet.com bitsquatting trust-wallet.com hyphenation trust2wallet.com insertion trustewallet.com insertion trustqwallet.com insertion trustrwallet.com insertion trustswallet.com insertion trustuallet.com bitsquatting trustvallet.com bitsquatting trustwa11et.com homoglyph trustwa1let.com homoglyph trustwaallet.com insertion trustwaiiet.com homoglyph trustwailet.com homoglyph trustwal1et.com homoglyph trustwalet.com omission trustwaliet.com homoglyph trustwallat.com bitsquatting trustwalldt.com bitsquatting trustwalle.com omission trustwallet0.com addition trustwallet4.com addition trustwallet5.com addition trustwallet6.com addition trustwalleta.com addition trustwalleth.com addition trustwalletj.com addition trustwalletk.com addition trustwalletr.com addition trustwallets.com addition trustwallett.com addition trustwalletx.com addition trustwallgt.com bitsquatting trustwallmt.com bitsquatting trustwallt.com omission trustwaqllet.com insertion trustwawllet.com insertion trustwellet.com bitsquatting trustwwallet.com insertion trustwzallet.com insertion trustywallet.com insertion truswallet.com omission trvstwallet.com homoglyph ttrustwallet.com insertion xn--trstwallet-beb.com homoglyph xn--trstwallt-i4a6r.com homoglyph xn--trustwalet-6yb.com homoglyph xn--trustwalet-toe.com homoglyph xn--trustwalle-5cc.com homoglyph xn--trustwallt-j7a.com homoglyph

Se muestran 100 de 104

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260914-3D0C13 Recipient: rtr-security-threats@realtimeregister.com
Page title stored with report: bnbwalle.com/mobile/index.html#/
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 638.2 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.

¿Te ha afectado esta página web?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países
Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.

Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/bnbwalle.com"
  title="PhishDestroy threat report for bnbwalle.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>