Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
bhd8fa6-4acb-be64-76e26a.xo.je favicon

bhd8fa6-4acb-be64-76e26a.xo.je

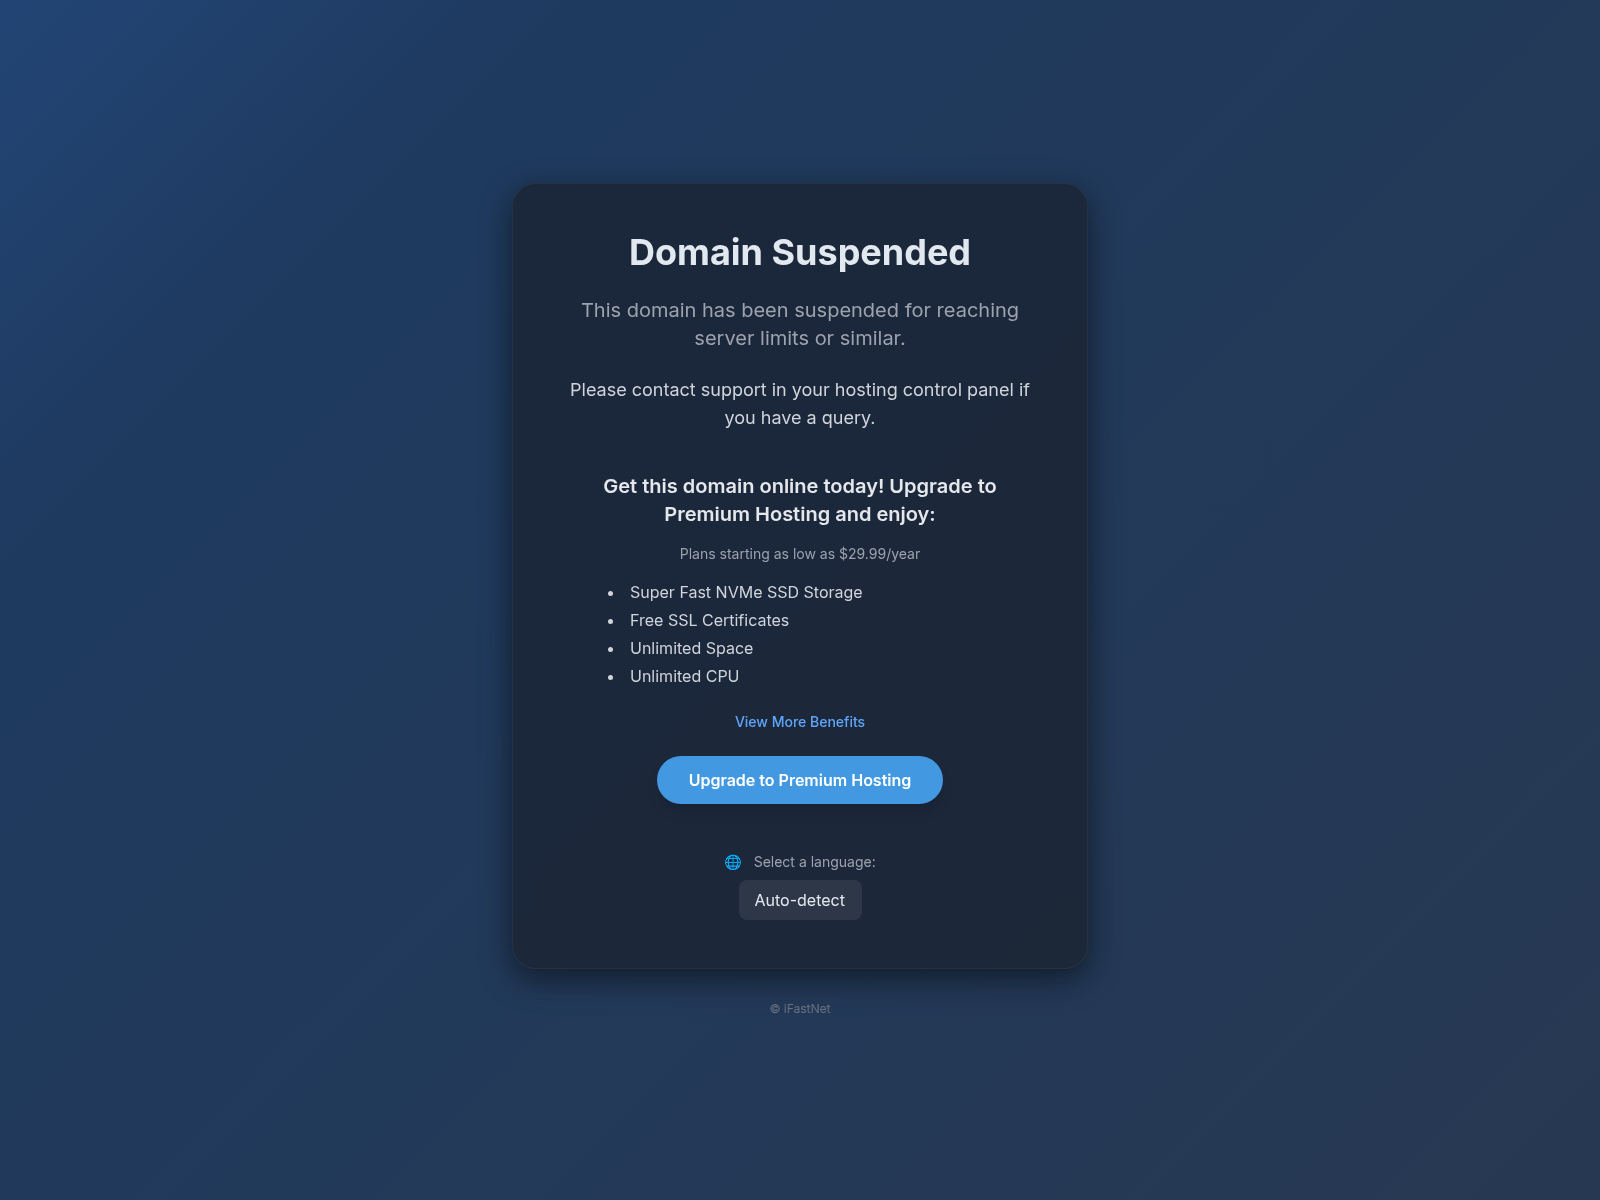
“Domain Suspended”

Resolved IP
77.72.1.44
Veredicto de amenaza Crítico
Disponibilidad No verificado La accesibilidad actual no está verificada Observado
Source: HTTP probe
VirusTotal detecciones: 12/89 Spamhaus DBL: DBL_PHISH Tipo de estafa: Account Takeover
06/12/2025
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 12. Tenga extrema precaución: no ingrese credenciales o información personal.
Resumen del informe

bhd8fa6-4acb-be64-76e26a.xo.je — No verificado. Tipo de estafa: Account Takeover. Resumen de las pruebas: VirusTotal 12/89 (BitDefender, Chong Lua Dao, CyRadar, ESET, Forcepoint ThreatSeeker); Spamhaus DBL_PHISH; CF Radar malicious; PhishDestroy score 91/100.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
12 det.
CF Radar
Malicioso
URLScan
URLScan
ScamAdviser
Scamadviser
1/100Very Likely Unsafe
PhishDestroy
DestroyList
Incluido

Source evidence

8 sources

VirusTotal

12 / 89

Denunciar

CF Radar

provider verdict: malicious

Denunciar

Spamhaus DBL

DBL_PHISH

PhishStats

checked — no match recorded

OTX

no community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

Google Safe Browsing

Checked; no threat flag recorded

Denunciar
Señales de seguridad
SA Scamadviser Warnings 1/100
The Tranco rank (how much traffic) is rather low An iframe has been detected within the website The server of the site has several low reviewed other websites This website seems for sale at this time (how to get your money back) The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
We found a valid SSL certificate
Inteligencia de seguridad de red
CF Cloudflare Radar Verdict Malicioso
Phishing Security threats Phishing

Resumen de las pruebas

Crítico
VirusTotal
12/89
URLScan
Stored capture

The domain bhd8fa6-4acb-be64-76e26a.xo.je was observed returning the page title "Domain Suspended" and is currently taken offline. DNS resolution points to the IPv4 address 77.72.1.44, which is announced by AS12488 (Krystal Hosting Ltd) located in Great Britain. The domain lacks publicly resolvable nameservers, and no TLS certificate was presented when the host was queried, indicating an absence of encrypted traffic. Reputation services record a Scamadviser trust score of 1 out of 100, reflecting extreme suspicion.

The domain appears on a single security blocklist and has been explicitly flagged by the PhishDestroy feed. VirusTotal analysis shows that 20 out of 95 scanned security vendors flagged the domain as malicious, reinforcing the notion of malicious intent despite the offline state. The intelligence categorizes the activity as an "Account Takeover" scam, though the targeted brand or service is not disclosed in the available data. The combination of a low trust score, lack of SSL, presence on a blocklist, and multiple vendor detections suggests the domain was deployed to harvest credentials or session tokens before being shut down.

Uncertainty remains regarding the exact victim profile and the infrastructure used to deliver the malicious payload, as the site content was not captured before suspension. Defenders should continue to deny any outbound connections to 77.72.1.44, add the domain to perimeter deny lists, and monitor DNS logs for any resurgence of the hostname or related sub‑domains. Additional investigation of Krystal Hosting Ltd’s IP range may reveal other malicious actors sharing the same hosting environment.

Análisis de detección y evasión

Comprobación del enmascaramiento y la distribución del tráfico

Aún no se ha escaneado Aún no se ha registrado ninguna diferencia entre los rastreadores y los navegadores

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
Aún no se ha escaneado
Último escaneo de camuflaje

Nota del escáner: timeout: raw=timeout; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='bhd8fa6-4acb-be64-76e26a.xo.je', port=80): Max retries exceeded with url: / (Caused by Con

Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 2 captures

Domain details

Dominio
Reputación de IP abuse score 0/100 0 reports checked 25/09/2026
Registrar (base domain) Desconocido
Contacto de abusoabuse@ifastnet.com
Detalles técnicosProvenance & timestamps
Primera detección06/12/2025
DOM Analysisanalyzed 27/07/2026score 88/100
Submitted URLhttp://bhd8fa6-4acb-be64-76e26a.xo.je/
Título de la página
Domain Suspended

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
77.72.1.44
Network ASN
AS12488
Organization
Krystal Hosting Ltd
Observed location
London, GB
Server header
openresty

Location describes the IP network.

viewdns.info · 77.72.1.44rapiddns.io

Latest Classified Outcome 2026-10-14 10:41:21 UTC

Primary outcome Desconocido reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Desconocido Probe Inconclusive 20% 2026-10-14 10:41:21 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-09-15 22:17:50 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

12 / Los proveedores de seguridad de 89 marcaron este dominio
View on VT
Last analyzed Previous stored snapshot: 14 detections
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SOCRadar
Sophos
VIPRE

Evidencias archivadas

Wayback Machine Snapshot
Una instantánea histórica está disponible para revisión de evidencia.
View Archive

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-07-26 22:23:32 UTC
    Domain state transitioned from dead to alive.
  2. Cloudflare Radar Scan 2026-03-07 11:44:23 UTC
    Cloudflare Radar scan registered: View Radar report.
  3. Domain Status Transition 2026-03-01 04:45:09 UTC
    Domain state transitioned from alive to dead.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
bhd8fa6-4acb-be64-76e26a.xo.je detectados y puestos en cola para su análisis completo
06/12/2025
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
13/10/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
27/02/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
14/03/2026
VirusTotal
12/89 recorded on VirusTotal
19/09/2026
CF Radar: Malicious
Cloudflare Radar classified this domain as Phishing, Security threats, phishing
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
27/02/2026
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
15/10/2026
Site Came Back Online
Domain is responding again — monitoring resumed
27/07/2026
Cloudflare Radar Scan
Escaneado con Cloudflare Radar; análisis de red completado.
07/03/2026
Content Observed Unavailable
El monitoreo registró una respuesta no disponible; la causa no se estableció de forma independiente.
01/03/2026
Lista de destrucción publicada
06/12/2025
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Reportes de la comunidad

Reportado por 1 miembro de la comunidad; visto por primera vez el 06/12/2025

Reportes almacenados
1
URL únicas reportadas
1
Aceptado1

Datos y informes externos

Análisis en profundidad

¿Te ha afectado esta página web?

4 evidence signal groups linked 0 reports recorded No verificado
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.


Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/bhd8fa6-4acb-be64-76e26a.xo.je"
  title="PhishDestroy threat report for bhd8fa6-4acb-be64-76e26a.xo.je"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>