VirusTotal
7 / 92
Denunciar


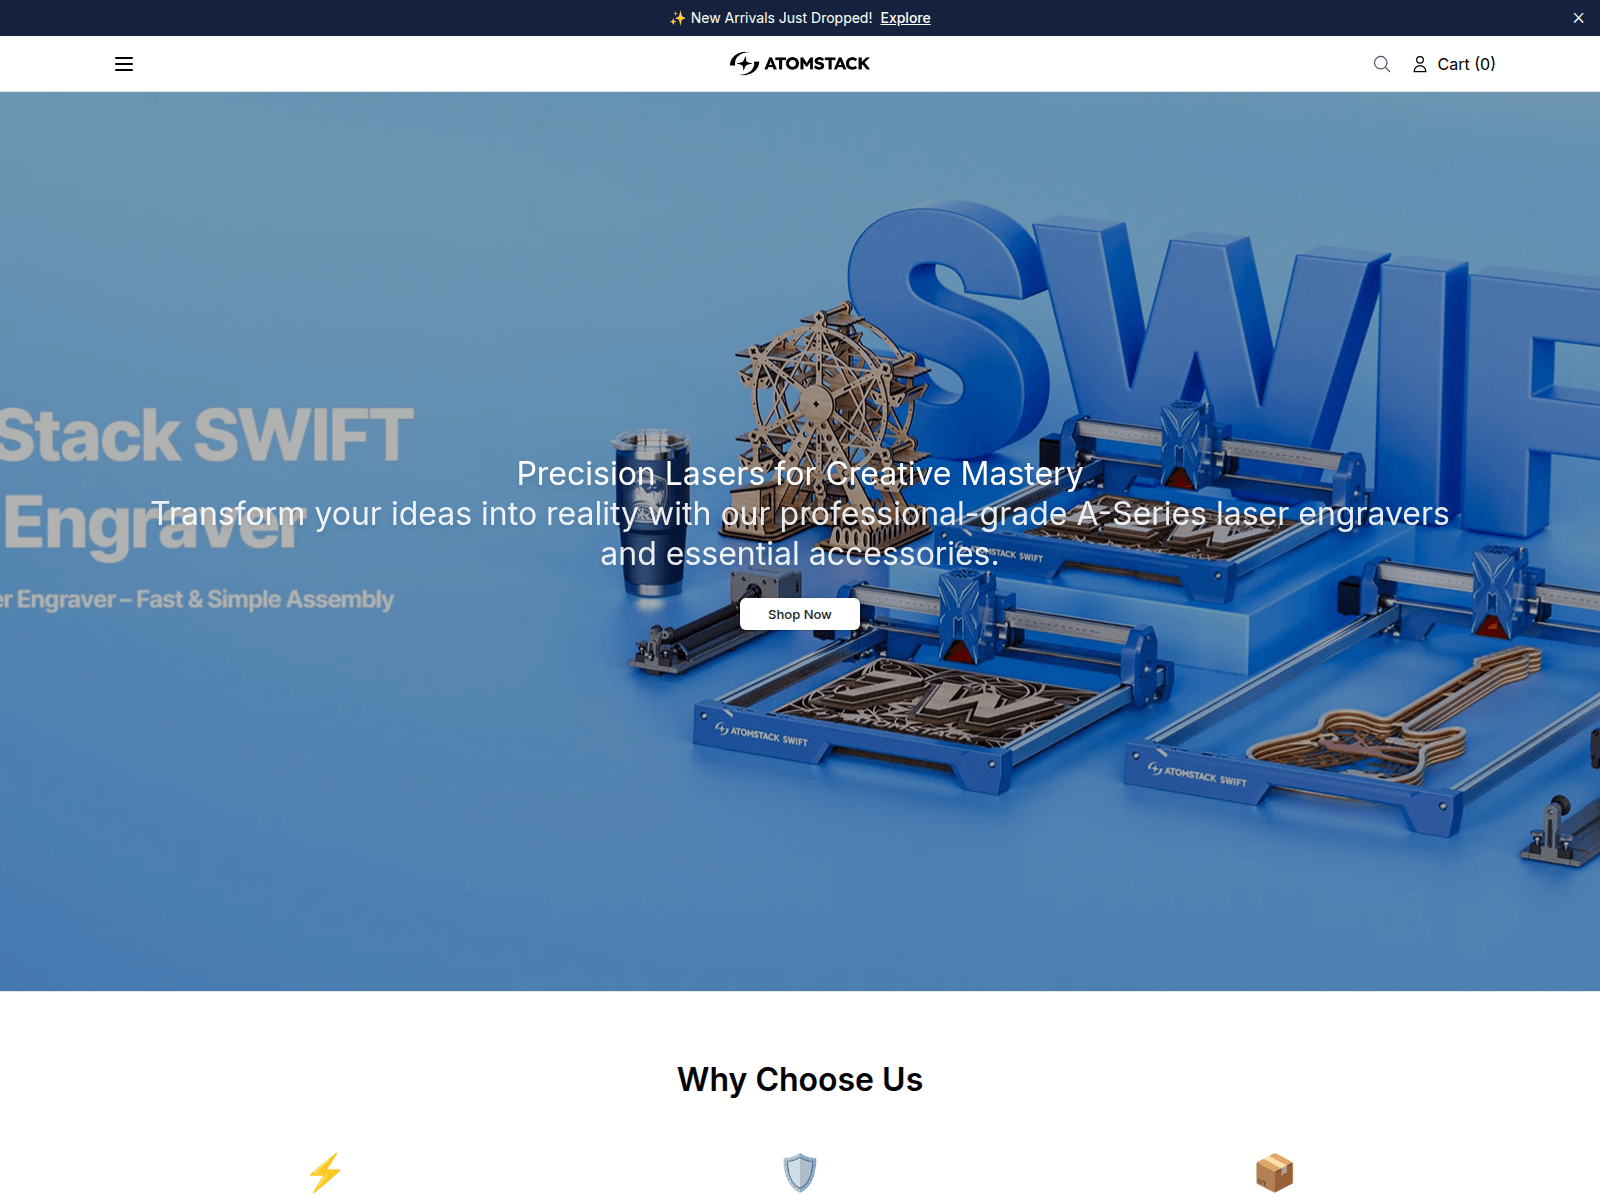
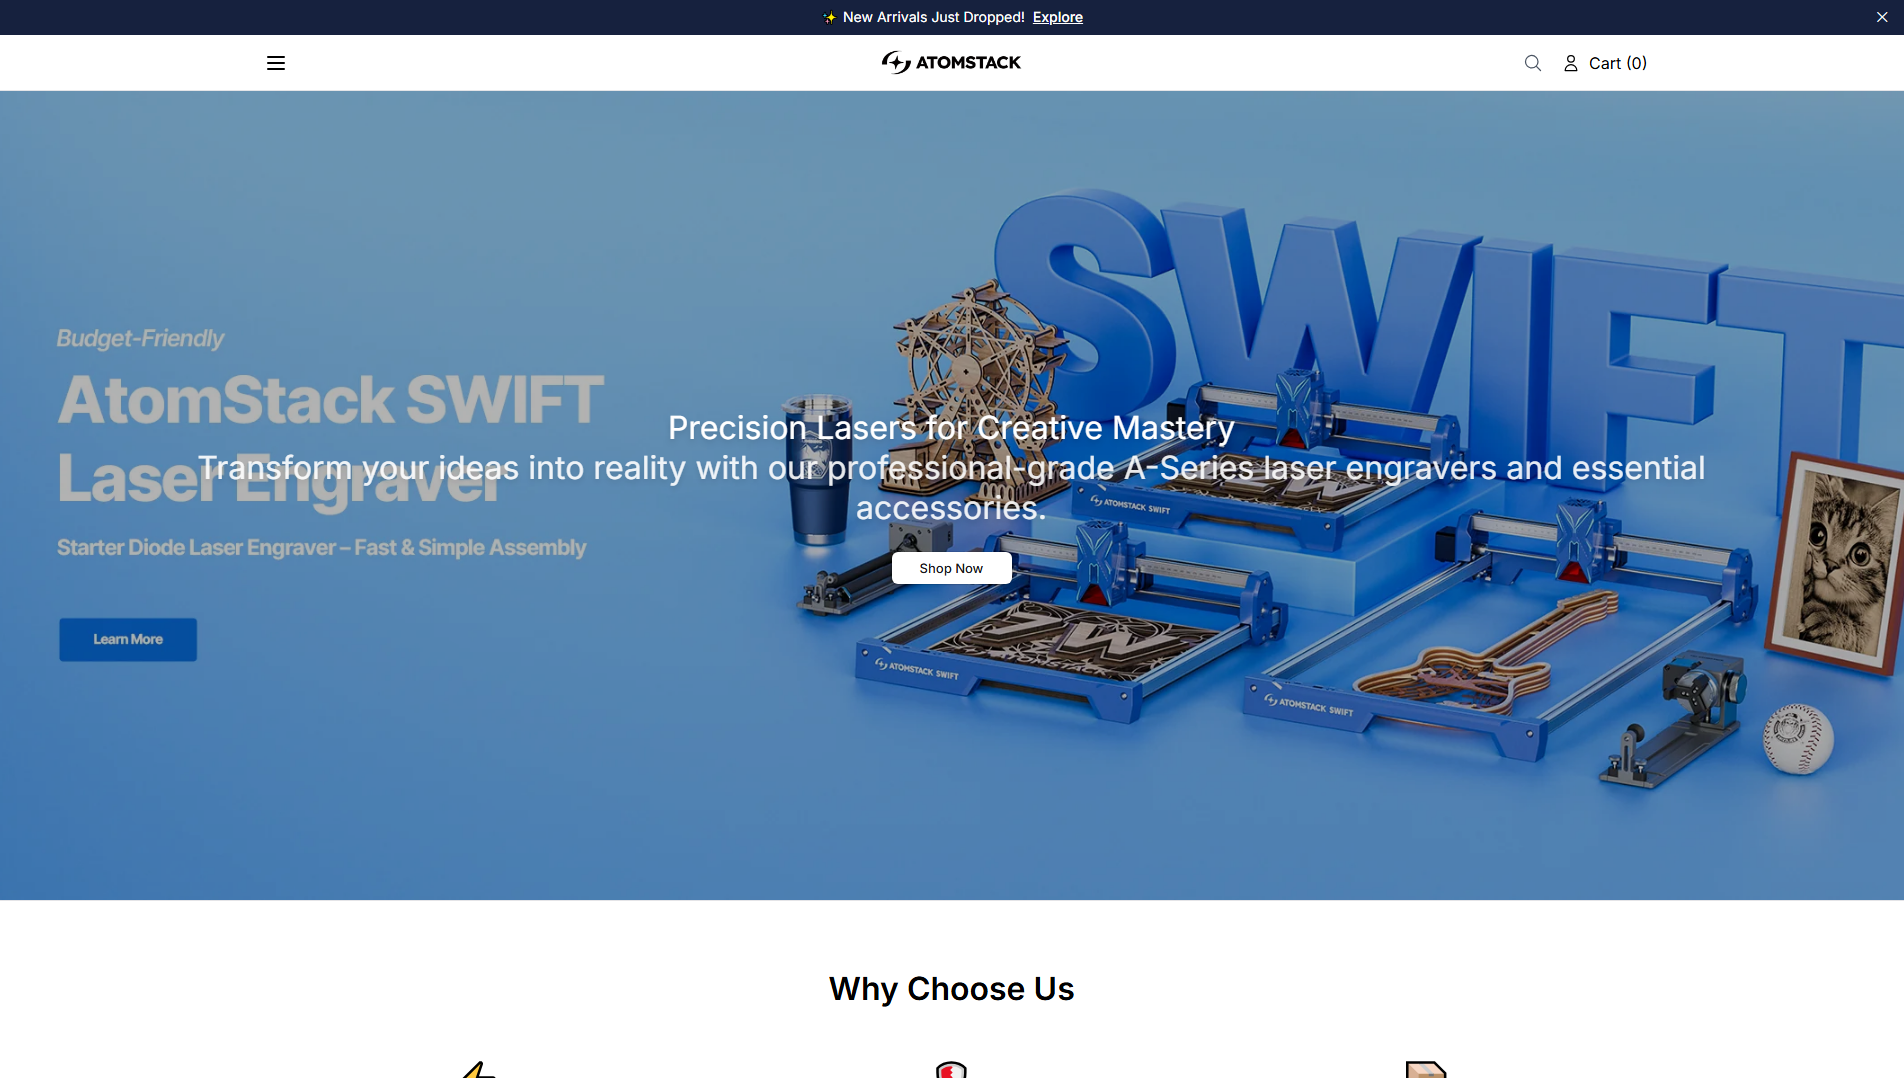
“Unleash Creativity Through Laser Technology | AtomStack”
atomstackstore.shop — Último activo conocido (HTTP 200). Suplantación de marca: Fakeshop; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 7/92 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, G-Data, Gridinsoft); URLScan malicious verdict; PhishDestroy score 81/100.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

The domain atomstackstore.shop returned an HTTP 200 status code on 2026-10-08, confirming a successful web response at that time. It was also recorded in the PhishDestroy internal listing as targeting 'fakeshop'.
On 2026-10-08, atomstackstore.shop responded with an HTTP 200 status code. VirusTotal reported 7 detections out of 92 scanners for this domain on 2026-10-07. OTX recorded 4 pulses as of 2026-10-08. The PhishDestroy internal listing identified the domain with the target brand 'fakeshop'. A PageSpeed performance score of 67 and a URLScan report were both recorded on 2026-10-07.
These records from VirusTotal, OTX, and PhishDestroy provide a multi-source view of atomstackstore.shop's observed status and attention from monitoring services. The HTTP response and PageSpeed score offer technical insight, while the internal listing and OTX pulses show the domain has been flagged for further scrutiny. The available URLScan report adds another layer of technical documentation for this domain.
To support ongoing review of atomstackstore.shop, retain the VirusTotal, OTX, and PhishDestroy records for future comparison. Preserve the PageSpeed and URLScan reports for technical reference. Use the HTTP 200 response as a point of comparison for subsequent web availability checks.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy
macy.ns.cloudflare.comned.ns.cloudflare.comLocation describes the IP network.
fe196409f26b490daaead38df59402632b20e70a83abbddfb192132677c4aaa1Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of atomstackstore.shop · checked Oct 7, 2026
195.96.130.219. 13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
Esta IP de origen aloja múltiples dominios de phishing; la infraestructura puede compartirse entre campañas.
Estos dominios también se dirigen a los usuarios de Fakeshop. Ver todas las amenazas de «Fakeshop» →
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.