VirusTotal
13 / 92
Denunciar


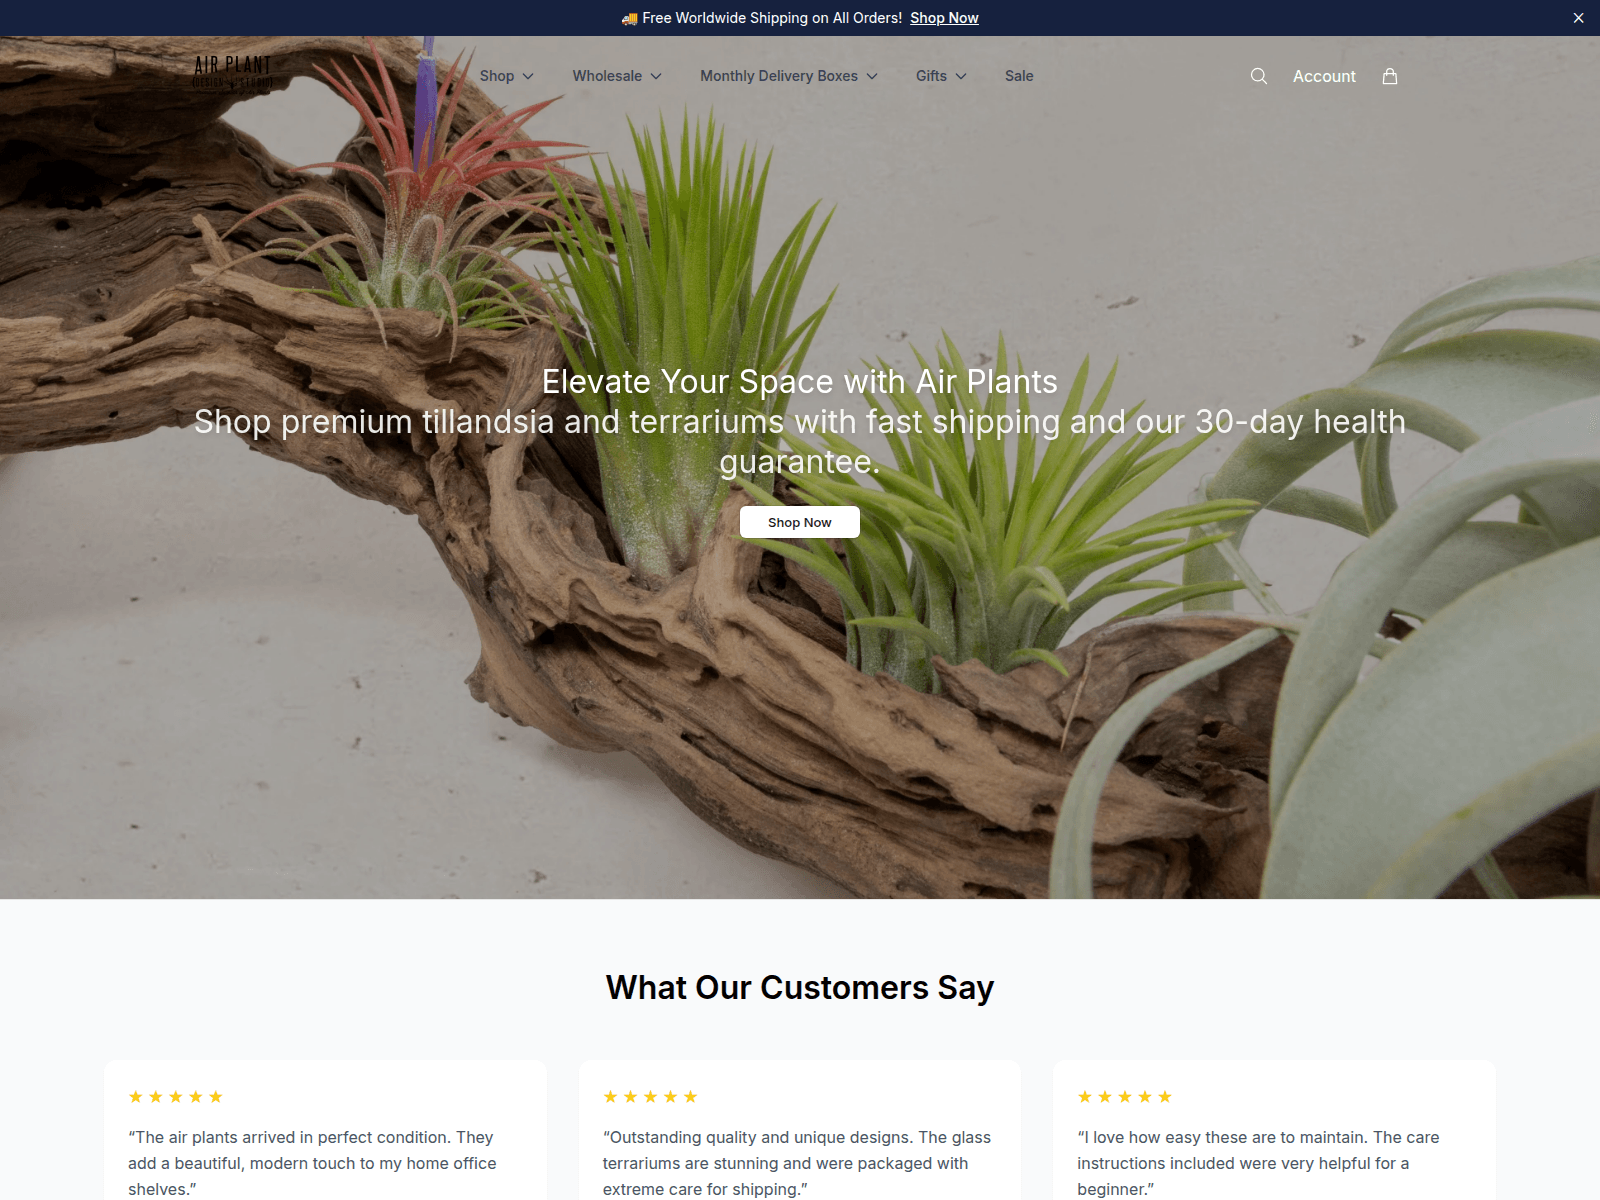
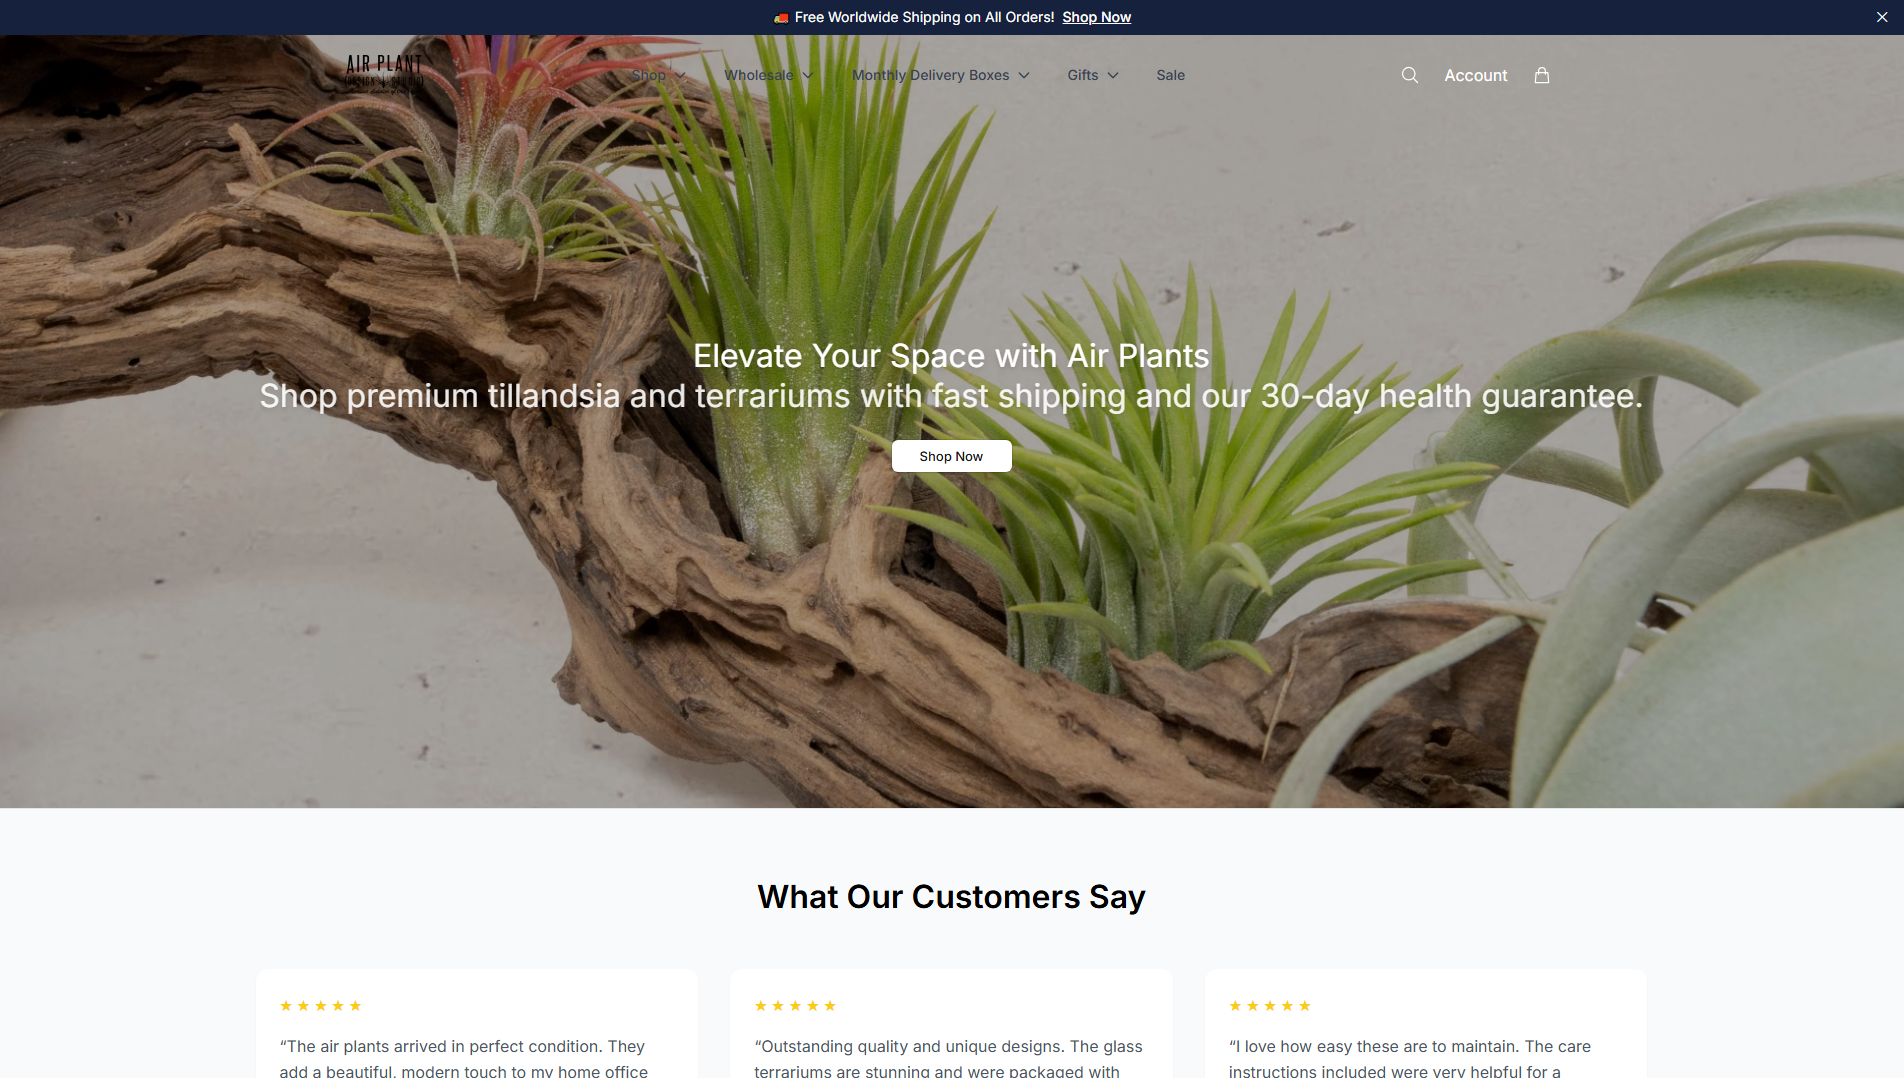
“Shop Terrariums, Gifts,”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 16 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
airplantsshop.shop — Último activo conocido (HTTP 200). Suplantación de marca: Fakeshop; Tipo de estafa: Impersonation. Resumen de las pruebas: VirusTotal 13/92 (BitDefender, CRDF, ESET, Forcepoint ThreatSeeker, Fortinet); URLQuery 2 det.; URLScan malicious verdict; PhishDestroy score 100/100.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

airplantsshop.shop returned HTTP status 301 on 2026-10-01, and its first appearance was recorded on 2026-09-25. The domain’s PageSpeed performance score of 67 was measured on the same day it first appeared.
The SSL certificate issued by Let's Encrypt / YE1 for airplantsshop.shop was scanned on 2026-09-25. OTX recorded 4 pulses on 2026-09-27. VirusTotal detected 7 detections out of 91 scanners on 2026-09-29. The PhishDestroy internal listing for the domain was marked true on 2026-10-01.
PhishDestroy, OTX and VirusTotal observations were captured on different dates, so their values reflect separate snapshots rather than a synchronized view. The HTTP status and SSL scan were also collected at different times, enabling timing comparisons but not direct equivalence of underlying conditions.
For airplantsshop.shop retain the dated PhishDestroy listing, OTX pulse count and VirusTotal result to compare with later checks. Schedule repeat observations at consistent intervals and record any changes in status or scores. Avoid entering sensitive information into the site until the recorded signals have been compared across sources.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
Nota del escáner: alive_content: raw=ok; http=200; via=https_proxy
bradley.ns.cloudflare.comlana.ns.cloudflare.comLocation describes the IP network.
4fce45107e2c8501bec99d7942345e31f5d70862356777be42d6dd1ae928e4a6Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of airplantsshop.shop · checked Sep 25, 2026
31.222.234.226. 13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20260925-DF9981 Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
El mismo hash del favicon o el mismo título de página que este servidor.
Otro dominio de phishing comparte esta IP de origen: posible infraestructura compartida.
Estos dominios también se dirigen a los usuarios de Fakeshop. Ver todas las amenazas de «Fakeshop» →
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.