跳转到安全报告
域安全和威胁情报
qrsu.io favicon

qrsu.io

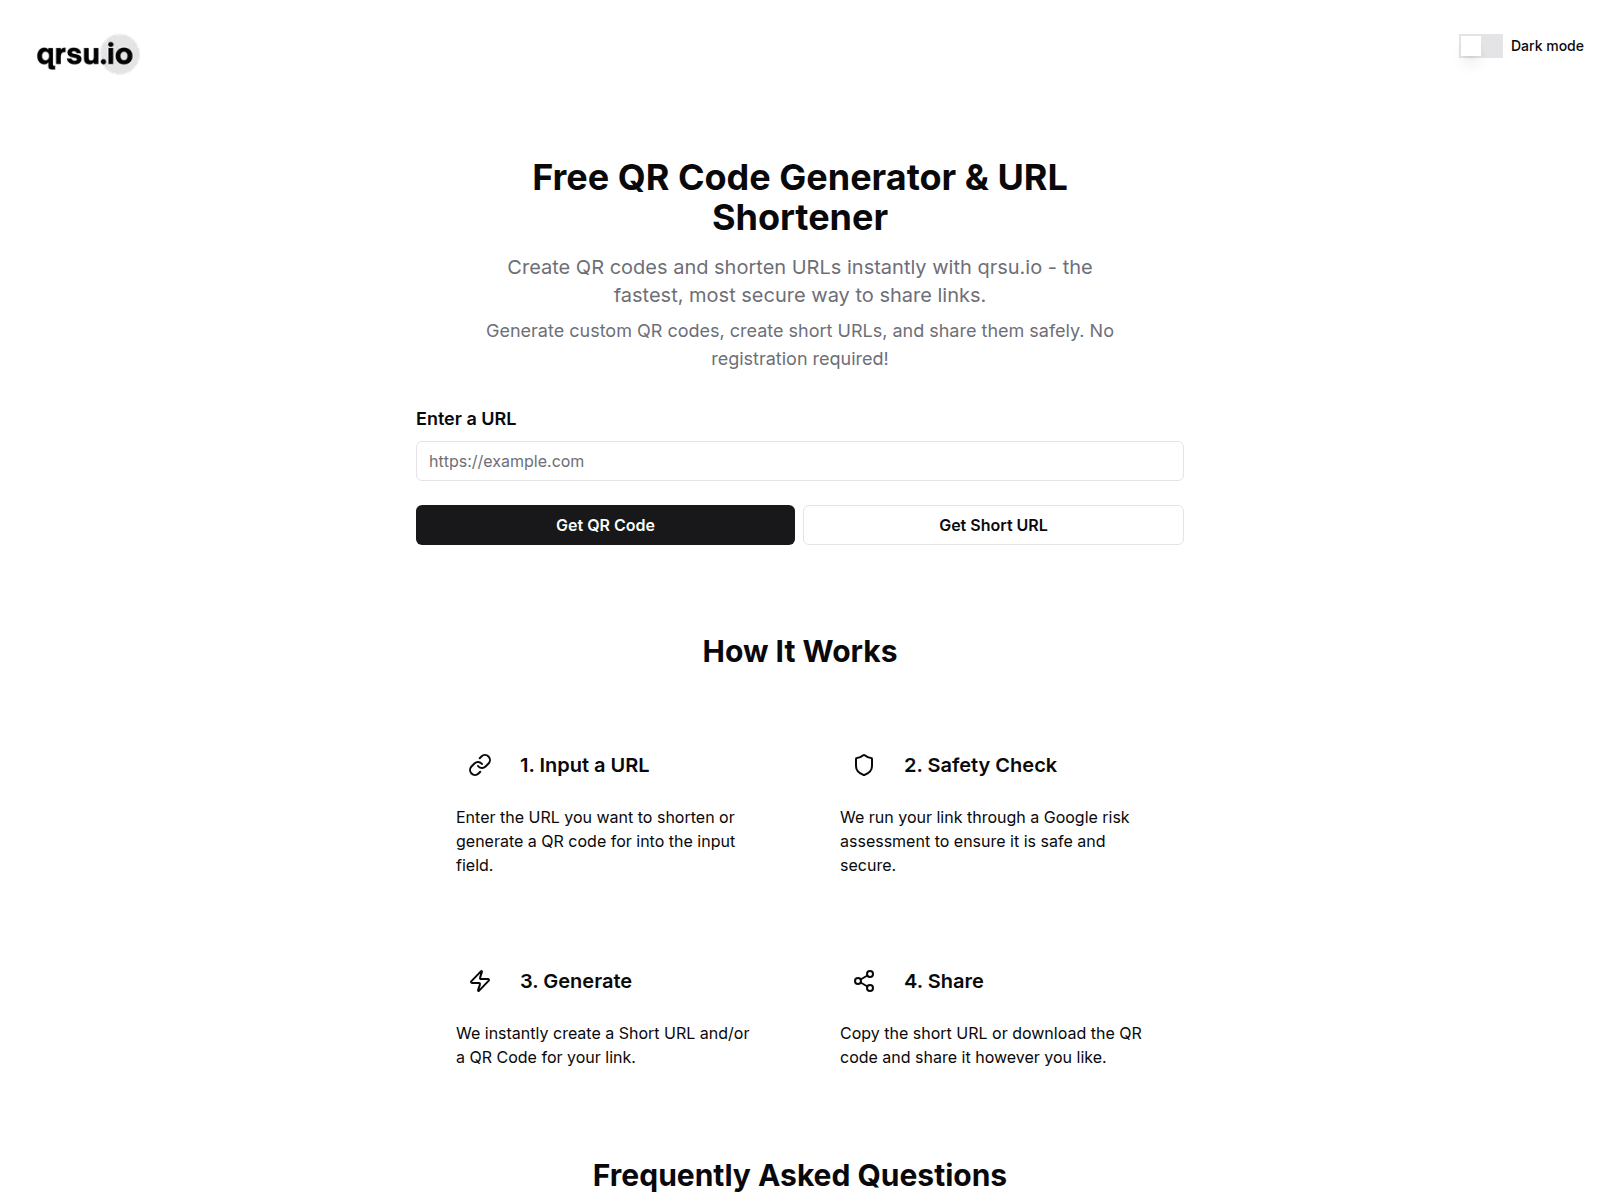
“qrsu.io - QR Code & URL Shortener”

注册商
GoDaddy
Resolved IP
76.76.21.21
Registered
2024年9月20日
威胁判定 关键
可用性 最后已知的活跃状态 以前不可用;最新观察结果已可达 观察到
Source: HTTP probe
病毒检测总数:16/89 Spamhaus DBL: DBL_PHISH 品牌冒充:Google
OTX: 50 refs 2026年8月4日 Google CDN
API
该域名已被标记为恶意域名
安全引擎报告检测:16。 请格外小心——不要输入凭据或个人信息。
报告概览

qrsu.io — 最后已知的活跃状态 (HTTP 200). 品牌冒充:Google; 诈骗类型:Credential Phishing. 证据摘要: VirusTotal 16/89 (ADMINUSLabs, Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao); Spamhaus DBL_PHISH; PhishDestroy score 100/100. 注册商: GoDaddy.

为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
16 det.
OTX references
URLScan
URLScan
Gridinsoft
1/100
TLS 证书
已过期或未验证
年龄
2.1 yr
观测状态
最后已知的活跃状态 200
PhishDestroy
DestroyList
已列入

Source evidence

8 sources

VirusTotal

16 / 89

报告

Gridinsoft

1/100

Spamhaus DBL

DBL_PHISH

OTX

50 community references

报告

CF雷达

provider verdict: clean

报告

URLScan capture

存储的报告

Stored URLScan capture preview
报告

URLScan verdict

分析完成

报告

Google Safe Browsing

Checked; no threat flag recorded

报告

证据摘要

关键
VirusTotal
16/89
OTX
50 community refs
URLScan
Stored capture

On 2026‑08‑04 the domain qrsu.io was observed flagged as part of an elevated‑risk generic phishing campaign. VirusTotal reports indicate that 16 of 91 scanning engines returned a malicious classification for the host, demonstrating a moderate consensus of detection across multiple vendors. The domain is listed on a single public security blocklist and is actively blocked by the PhishDestroy filtering service, confirming that at least one commercial anti‑phishing solution has incorporated it into its deny list.

No additional intelligence such as registrar details, registration date, hosting IP, autonomous system, SSL certificate information, or page title has been published in the current feed, so the underlying infrastructure remains opaque. The absence of these data points limits the ability to attribute the infrastructure to a specific operator or to map its network relationships. Nonetheless, the presence on VirusTotal and a known blocklist, combined with the elevated risk rating, suggests that qrsu.io is being used to harvest credentials or otherwise deceive users.

Defenders should add qrsu.io to local deny lists, enforce URL filtering rules that block the domain, and monitor outbound DNS queries for any attempts to resolve it. Network traffic to the domain should be logged and, where possible, redirected to a sandbox for deeper analysis. Continuous re‑evaluation is advised, as additional indicators such as hosting IPs, certificate fingerprints, or page content may emerge in future threat‑intel updates.

探测与规避分析

隐身和流量分配检查

尚未扫描 目前尚未记录到爬虫与浏览器之间的差异

针对该主机的爬虫与浏览器观察记录,以及针对“Keitaro”式流量分配系统的实时指纹检测。

存储的隐身标志
尚未扫描
上次隐形扫描
扫描器检测到的服务器头信息
Vercel

扫描说明: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel

TDS指纹识别实时演示
七个Keitaro指纹,外加爬虫与浏览器的对比,当此面板打开时,由PhishDestroy扫描器运行。
等待

已保存的截图 · 2 captures

Domain details

域名
URLScan Verdict 分析完成 score 0 report ↗
IP Context Vercel shared edge origin IP hidden Edge-IP 声誉不属于此域。
OTX Tags 2026-032026-08activeall-domainsblocklistcontentcrypto域名drainerfraudlivemonthlyphishdestroyphishing+3 more
注册商 GoDaddy US(US)
ICANN 注册管理机构ICANN Lookup (RDAP) →
注册信息创建 2024年9月20日
Elapsed Since First Report 71 days
统计口径 Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: 最后已知的活跃状态.
每份报告包含哪些内容 存储的传出报告记录可以参考当时可用的证据,例如供应商判决、注册数据、托管详细信息、分类或屏幕截图。此页面无法推断收件人交付、接收、确认或操作的确切有效负载。
HTTP 状态码200
技术详情Provenance & timestamps
首次发现2026年8月4日
DOM Analysisanalyzed 2026年10月9日score 98/1001 brand signal
Submitted URLhttp://qrsu.io/ZBktp
Favicon Hash
页面标题
qrsu.io - QR Code & URL Shortener
Impersonates
Google
TLS 证书
Hostname coverage not recorded · 颁发者 Let's Encrypt · stored validity ends in 38 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
76.76.21.21
Network ASN
AS16509
Organization
Vercel, Inc
Observed location
Walnut, US
Server header
Vercel

Edge-IP 声誉不属于此域。

域名服务器 1

  • ns72.domaincontrol.com

Location describes the IP network.

TLS 证书

Issuer
Let's Encrypt
Valid from
2026-08-14 11:27:57
Valid until
2026-11-12 11:27:56
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-10 16:03:08 UTC
Collection source
PhishDestroy collector
Certificate fingerprint7432a8e126ad4da568b9fd0b69a7a1b919972a714818659dd184e39e6d44f58c

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 76.76.21.21rapiddns.io

Latest Classified Outcome 2026-10-13 22:06:26 UTC

Primary outcome 内容在线 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation 内容在线 Ordinary HTTP content served 90% 2026-10-13 22:06:26 UTC
RDAP registration 未知
Observed timeline last reachable: 2026-10-13 22:06:26 UTC last content: 2026-10-13 22:06:26 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
技术 · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
举报此域名 提交证据,帮助保护他人

VirusTotal 分析

16 / 89 安全供应商标记了该域
View on VT
Last analyzed Previous stored snapshot: 17 detections
ADMINUSLabs
Criminal IP
alphaMountain.ai
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SafeToOpen
Sophos
VIPRE
Webroot

存档证据

Wayback Machine Snapshot
历史快照可供证据审查
View Archive
网站性能分析

Google PageSpeed Insights — mobile performance audit of qrsu.io · checked Aug 4, 2026

99
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
2.1s
Largest Contentful Paint
CLS
0.008
Cumulative Layout Shift
TBT
44ms
Total Blocking Time
SI
2.25s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-10-13 22:29:42 UTC
    Domain state transitioned from alive to dead.
  2. Domain Status Transition 2026-09-11 22:17:55 UTC
    Domain state transitioned from dead to alive.
  3. Domain Status Transition 2026-09-10 22:42:26 UTC
    Domain state transitioned from alive to dead.
  4. Domain Status Transition 2026-08-04 22:14:37 UTC
    Domain state transitioned from dead to alive.
  5. Domain Status Transition 2026-08-04 04:15:11 UTC
    Domain state transitioned from alive to dead.
  6. Threat First Observed 2026-08-04 01:04:35 UTC
    Domain ingestion complete. Initial state is marked as unknown.

威胁响应 Pipeline

发现
Analysis
Monitoring

16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

已捕获威胁
qrsu.io 已检测到并排入队,待进行全面分析
2026年8月4日
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
2026年10月9日
URLScan.io Capture
已存储 URLScan report with capture artifacts
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in 互联网档案馆 — historical evidence archived
2026年8月4日
VirusTotal
16/89 recorded on VirusTotal
2026年9月12日
OTX Community References
50 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026年10月9日
Brand Impersonation
Impersonation of Google
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
Technical Analysis Recorded
该报告包含存储的技术或取证分析结果。
2026年10月14日
Content Observed Unavailable
监控记录了一个不可用的响应 (HTTP 200);原因尚未独立确定。
2026年10月14日
Site Came Back Online
Domain is responding again — monitoring resumed
2026年9月12日
Content Observed Unavailable
监控记录了一个不可用的响应 (HTTP 200);原因尚未独立确定。
2026年9月11日
Site Came Back Online
Domain is responding again — monitoring resumed
2026年8月5日
Content Observed Unavailable
监控记录了一个不可用的响应 (HTTP 200);原因尚未独立确定。
2026年8月4日
DestroyList 已发布
2026年8月4日
Monitoring Continues
该域仍然可达或访问受限;未来的检查可能会更新这一观察结果。
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

证据与外部报告

深度分析

您是否受到本网站的影响?

5 evidence signal groups linked 0 reports recorded 最后已知的活跃状态
If credentials were compromised, report immediately. Do not engage with recovery scammers.

如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。

欧洲刑警组织
查找您所在欧盟国家/地区的官方报告渠道
National police directory
警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关康复欺诈的更多信息 →

向当地主管部门报告

选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。

97个国家目录

Template-based draft · optional AI wording assistance requires separate consent

AI辅助草稿——事件详细信息由AI提供商处理 · 自行审核并提交

检查任意域名

使用存储的阻止列表、WHOIS、DNS 和公共扫描证据进行威胁分析

立即扫描

举报网络钓鱼

将可疑域名提交至我们的威胁数据库——保护社区

报告

实时威胁动态

最近的网络钓鱼报告和观察到的可用性变化

监控

随时掌握最新信息,确保安全

请实时监控威胁,或者如果您认为这是误报,请对该条目提出异议

实时威胁动态 对该列表提出异议
HTML · IFRAME

嵌入此报告

在您的网站或博客上分享此威胁情报

embed.html
<iframe
  src="https://phishdestroy.io/zh/embed/domain/qrsu.io"
  title="PhishDestroy threat report for qrsu.io"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>