VirusTotal
16 / 89
Báo cáo
Interpretation & limits
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.


“qrsu.io - QR Code & URL Shortener”
Assessment based on the stored source evidence below. Review sources →
qrsu.io — Hoạt động được biết đến lần cuối (HTTP 200). Mạo danh thương hiệu: Google; Loại lừa đảo: Credential Phishing. Tóm tắt bằng chứng: VirusTotal 16/89 (ADMINUSLabs, Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao); Spamhaus DBL_PHISH; PhishDestroy score 100/100. Nhà đăng ký: GoDaddy.
Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.
16 / 89
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.
1/100
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
DBL_PHISH
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
50 community references
Báo cáoCommunity publication references, not a vendor verdict or evidence of a common operator.
provider verdict: clean
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
báo cáo được lưu trữ
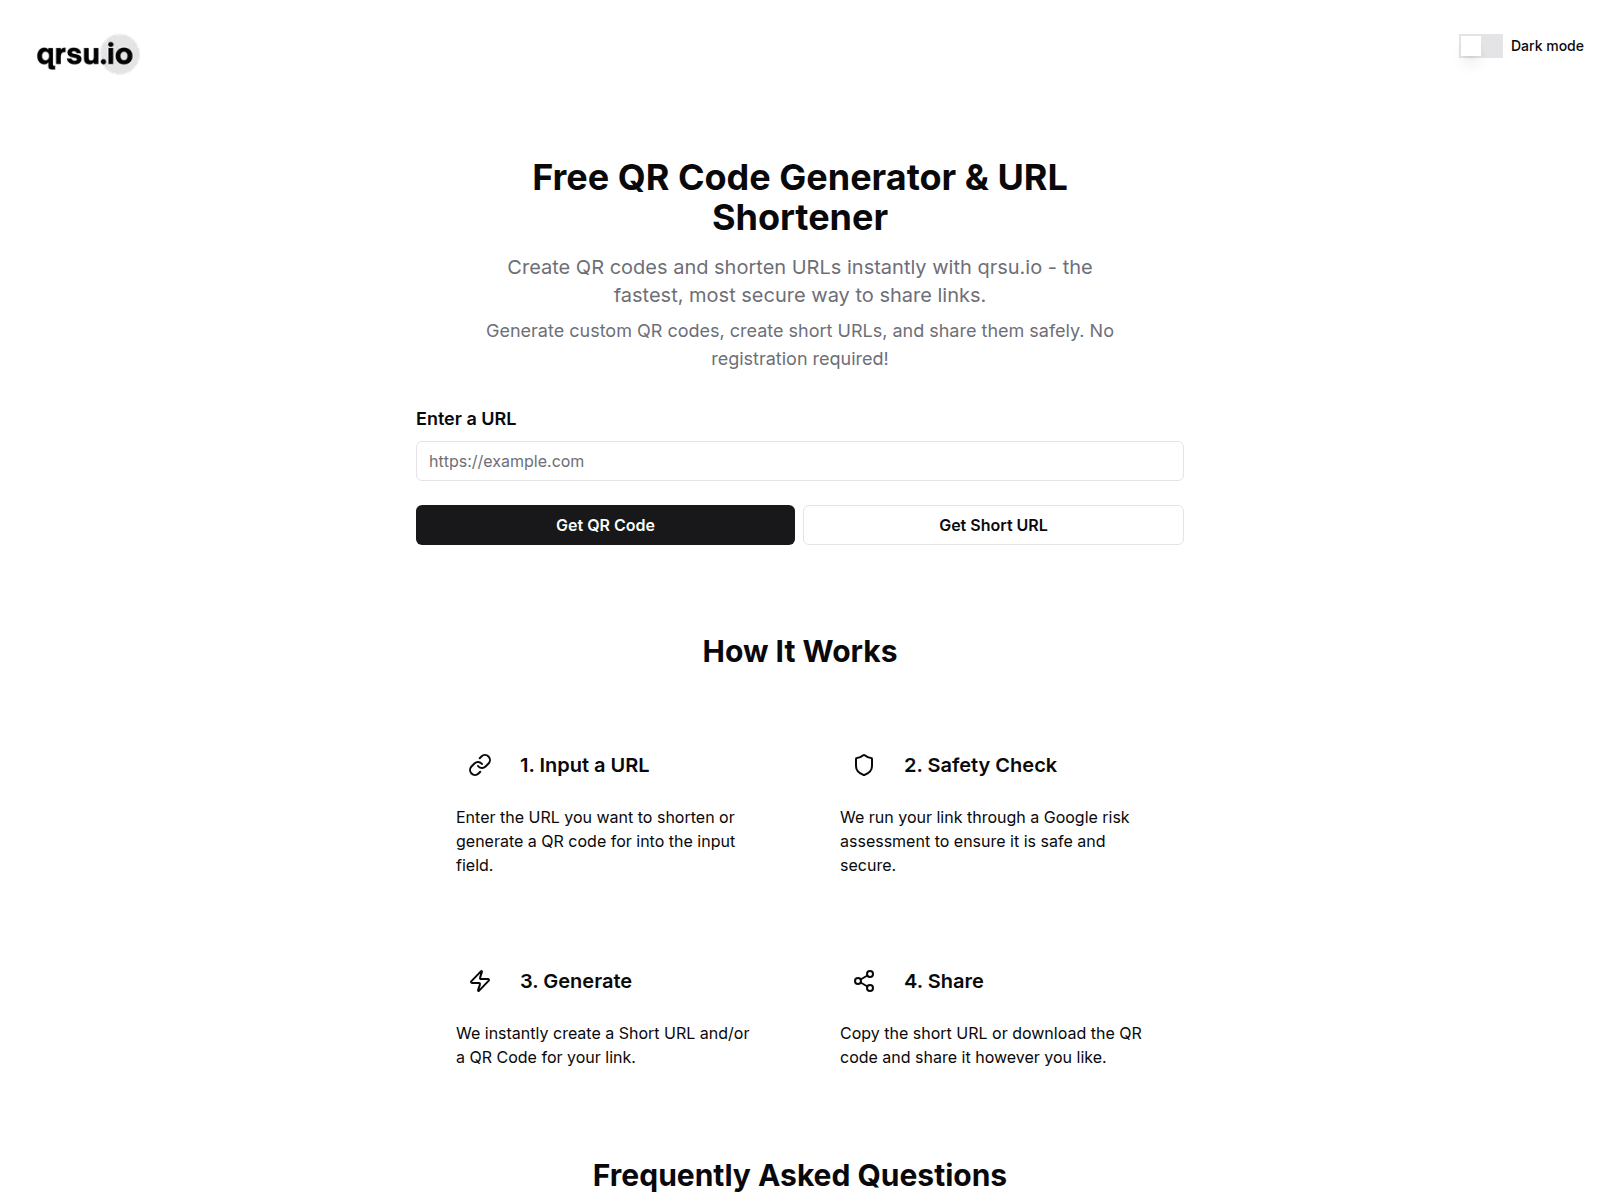
A preserved page image documents what the collector received; a capture is not a safety verdict.
Phân tích hoàn tất
Báo cáoThis is the recorded automated analysis. Completion alone is not a safety verdict.
Checked; no threat flag recorded
Báo cáoA result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
On 2026‑08‑04 the domain qrsu.io was observed flagged as part of an elevated‑risk generic phishing campaign. VirusTotal reports indicate that 16 of 91 scanning engines returned a malicious classification for the host, demonstrating a moderate consensus of detection across multiple vendors. The domain is listed on a single public security blocklist and is actively blocked by the PhishDestroy filtering service, confirming that at least one commercial anti‑phishing solution has incorporated it into its deny list.
No additional intelligence such as registrar details, registration date, hosting IP, autonomous system, SSL certificate information, or page title has been published in the current feed, so the underlying infrastructure remains opaque. The absence of these data points limits the ability to attribute the infrastructure to a specific operator or to map its network relationships. Nonetheless, the presence on VirusTotal and a known blocklist, combined with the elevated risk rating, suggests that qrsu.io is being used to harvest credentials or otherwise deceive users.
Defenders should add qrsu.io to local deny lists, enforce URL filtering rules that block the domain, and monitor outbound DNS queries for any attempts to resolve it. Network traffic to the domain should be logged and, where possible, redirected to a sandbox for deeper analysis. Continuous re‑evaluation is advised, as additional indicators such as hosting IPs, certificate fingerprints, or page content may emerge in future threat‑intel updates.
Các dữ liệu quan sát đã lưu trữ về sự so sánh giữa trình thu thập dữ liệu và trình duyệt đối với máy chủ này, cùng với việc kiểm tra dấu vân tay thời gian thực dành cho các hệ thống phân phối lưu lượng theo phong cách Keitaro.
VercelGhi chú về máy quét: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel
 (US)
Danh tiếng của Edge-IP không được quy cho tên miền này.
ns72.domaincontrol.comLocation describes the IP network.
7432a8e126ad4da568b9fd0b69a7a1b919972a714818659dd184e39e6d44f58cSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of qrsu.io · checked Aug 4, 2026
16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.


Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.
Template-based draft · optional AI wording assistance requires separate consent
Mỗi làn là một lý do khiến một tên miền được liên kết với máy chủ này. Kích thước nút biểu thị các phát hiện từ VirusTotal, còn các nút có đường gạch ngang đã ngừng hoạt động. Danh sách đầy đủ được trình bày dưới đây.
Các báo cáo này giải quyết cùng một IP biên được chia sẻ. Chúng giúp khám phá báo cáo nhưng không ngụ ý quyền sở hữu chung hoặc máy chủ gốc được chia sẻ.
Các tên miền này cũng nhắm đến người dùng Google. Xem tất cả các mối đe dọa liên quan đến “Google” →
Được đăng ký thông qua cùng một nhà đăng ký tên miền. Một nhà đăng ký tên miền phục vụ hàng triệu khách hàng không có mối liên hệ với nhau, do đó việc này chỉ cho thấy sự trùng hợp về số liệu chứ không chứng minh được mối liên hệ nào.
Các báo cáo được thêm gần đây từ cơ sở dữ liệu PhishDestroy. Các liên kết khám phá này không ngụ ý cơ sở hạ tầng hoặc quyền sở hữu chung.
Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai
Quét ngayHãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng
Báo cáoCác báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy
Theo dõiTheo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai







