VirusTotal
23 / 94
Сообщить


“My Framer Site”
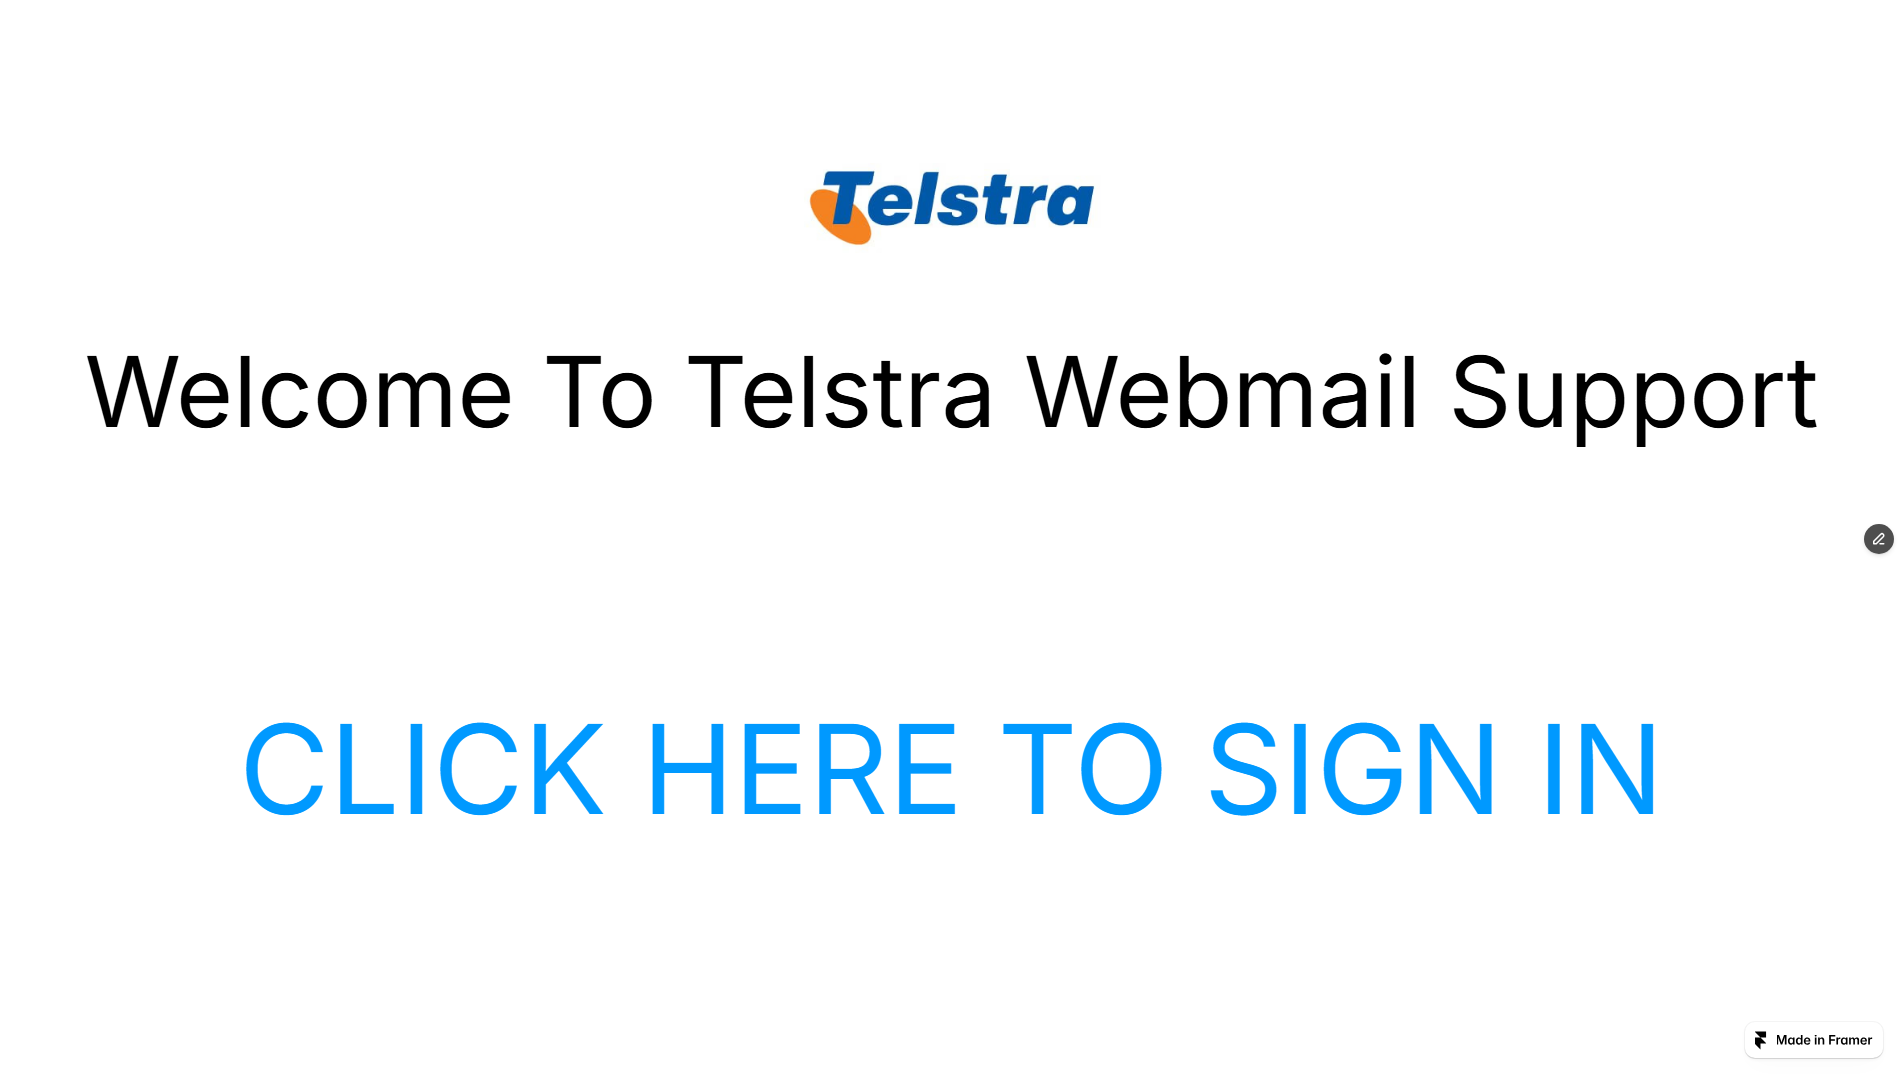
considerate-prism-546071.framer.app — Контент недоступен (HTTP 404). Олицетворение бренда: Telstra; Тип мошенничества: Generic Phishing. Сводка доказательств: VirusTotal 23/94 (ADMINUSLabs, alphaMountain.ai, BitDefender, Chong Lua Dao, Cluster25); URLQuery 3 alerts; URLScan malicious verdict; CF Radar malicious; PhishDestroy score 100/100. Регистратор: Framer.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

23 / 94
3 threat-system alerts
Сообщитьprovider verdict: malicious
Сообщитьmalicious
Сообщить2/12
checked — no match recorded
no community references
Сообщитьсохраненный отчет
 Сообщить
Checked; no threat flag recorded
Сообщить| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | considerate-prism-546071.framer.app |
malicious | Sinkholed |
| OpenDNS | considerate-prism-546071.framer.app |
phishing | Phishing Block |
| DNS4EU | considerate-prism-546071.framer.app |
malicious | Sinkholed |
PhishDestroy identifies the domain considerate-prism-546071.framer.app as an active crypto drainer phishing site, currently flagged with an elevated risk level. This domain is designed to deceive users into connecting cryptocurrency wallets under false pretenses, specifically targeting victims with fraudulent transaction prompts that drain funds directly from connected wallets. The site remains operational and is actively circulating among unsuspecting users, posing a significant threat to cryptocurrency holders who may inadvertently authorize malicious transactions.
This domain resolves to IP address 31.43.160.6 and utilizes a valid SSL certificate issued by Let's Encrypt, which may contribute to a false sense of security. According to VirusTotal intelligence, the domain is flagged by 19 of 95 security vendors, indicating widespread suspicion but not yet universal detection. While exact creation dates and registrar details are not provided in the available data, this domain exhibits multiple red flags consistent with crypto drainer operations, including active status and low trust scores across threat intelligence platforms. The absence of established reputation and the presence of malicious indicators further underscore the elevated risk associated with this domain.
Given the confirmed malicious nature of considerate-prism-546071.framer.app, users are strongly advised to avoid interacting with this domain under any circumstances. If you have already visited this site, disconnect your cryptocurrency wallet immediately and revoke any unauthorized permissions granted to unknown applications. To verify the safety of a domain before interaction, use PhishDestroy’s real-time scanning tool. Additionally, consider reporting this domain to relevant cybersecurity authorities, such as URLVoid or abuse channels of hosting providers, to aid in its takedown. Stay vigilant and prioritize wallet security by using hardware wallets and verifying transaction details carefully before approval.
Сохраненные данные сравнения данных сканера и браузера для данного хоста, а также проверка отпечатков в режиме реального времени для систем распределения трафика типа «Кейтаро».
Framer/af6a429Примечание к сканированию: hosting_placeholder: raw=placeholder; http=404; via=https_proxy; server=Framer/af6a429
Репутация Edge-IP не связана с этим доменом.
Location describes the IP network.
cd6872444e27b4b62ad9b72262b437a6f89a7bdf14f5aab53847756b2d4e769eSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of considerate-prism-546071.framer.app · checked Mar 30, 2026
15 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Сообщил 1 участник сообщества; впервые замечено 30.03.2026
PD-20260330-A2C2A7 Recipient: abuse@framer.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Template-based draft · optional AI wording assistance requires separate consent
Каждая полоса — это одна из причин, по которой домен связан с этим хостом. Размер узла обозначает обнаружения VirusTotal, а пунктирные узлы уже находятся в автономном режиме. Полные списки приведены ниже.
Тот же хеш фавиконы или тот же заголовок страницы, что и у этого хоста.
Эти отчеты относятся к одному и тому же общему граничному IP-адресу. Они помогают при обнаружении отчетов, но не подразумевают совместное владение или общий исходный сервер.
Эти домены также нацелены на пользователей сайта Telstra. Просмотреть все угрозы, связанные с «Telstra» →
Зарегистрированы через одного и того же регистратора. Регистратор обслуживает миллионы клиентов, не связанных друг с другом, поэтому данный факт скорее свидетельствует о сходстве данных, чем доказывает наличие связи.
Недавно добавленные отчёты об угрозах. Эти ссылки не означают общую инфраструктуру или одного владельца.
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасДобавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьНедавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьОтслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание