
Выполняйте поиск по отслеживаемым доменам и просматривайте сохраненные доказательства, данные об обнаружениях и последние данные о доступности.
221,361
Всего отслеженных
215,525
Обнаружено VT
85,984
Последнее появление: активен
135,377
По последним данным — недоступно
0
VT — в процессе рассмотрения
How This Attack Works
Solana Ecosystem scams are on the rise, targeting unsuspecting users with sophisticated phishing tactics. Here's how these scams typically unfold.
STEP 1
Домен Регистрация
Attackers register domains with misleading names such as solana-drop.app to mimic legitimate Solana services.
STEP 2
Phishing Campaign
Scammers launch phishing campaigns using emails or social media to lure victims to the fake websites.
STEP 3
Data Harvesting
Once on the fake site, victims are prompted to enter sensitive information, such as private keys or seed phrases.
STEP 4
Asset Theft
The collected data is used to access victims' wallets, leading to unauthorized transactions and asset theft.
Technical Analysis
Solana Ecosystem scams often utilize a variety of technical methods to deceive users. Attackers typically use typosquatting to register domains that closely resemble legitimate Solana services. Common tactics include deploying phishing kits that clone the appearance of genuine websites to trick users into inputting sensitive information. Many of these sites are hosted on platforms like Cloudflare for additional anonymity and protection against takedowns. Attackers may also employ smart contract functions to execute automated asset transfers once they gain access to a victim's wallet. This infrastructure enables rapid and often irreversible transactions, making recovery difficult.
Real Cases
Solana Wallet Phishing Scheme (2024)
$4.5 million stolen
A phishing campaign targeting Solana users resulted in the theft of $4.5 million worth of SOL and other tokens.
Fake Solana Staking Site (2023)
$2 million stolen
Scammers created a fake staking site that led to $2 million in stolen funds from users attempting to earn staking rewards.
Deceptive Token Airdrop (2024)
$1.2 million stolen
An airdrop scam promising free tokens tricked users into revealing private keys, resulting in $1.2 million in losses.
How to Detect
Unusual domain names mimicking Solana-related services
Unexpected emails or messages prompting action
Websites requesting private keys or seed phrases
Lack of HTTPS on websites claiming to be secure
Promises of unrealistic returns or free token offers
How to Protect Yourself
1
Verify the authenticity of websites before entering sensitive information
2
Enable two-factor authentication on your wallets
3
Regularly update your security software
4
Be cautious of unsolicited messages or offers
5
Используйте аппаратный кошелек for added security
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 3,245 domains tracked for this threat type
Solana Ecosystem Scam 3,245 domains
amlscores.com
hyperliquid-solana.xyz
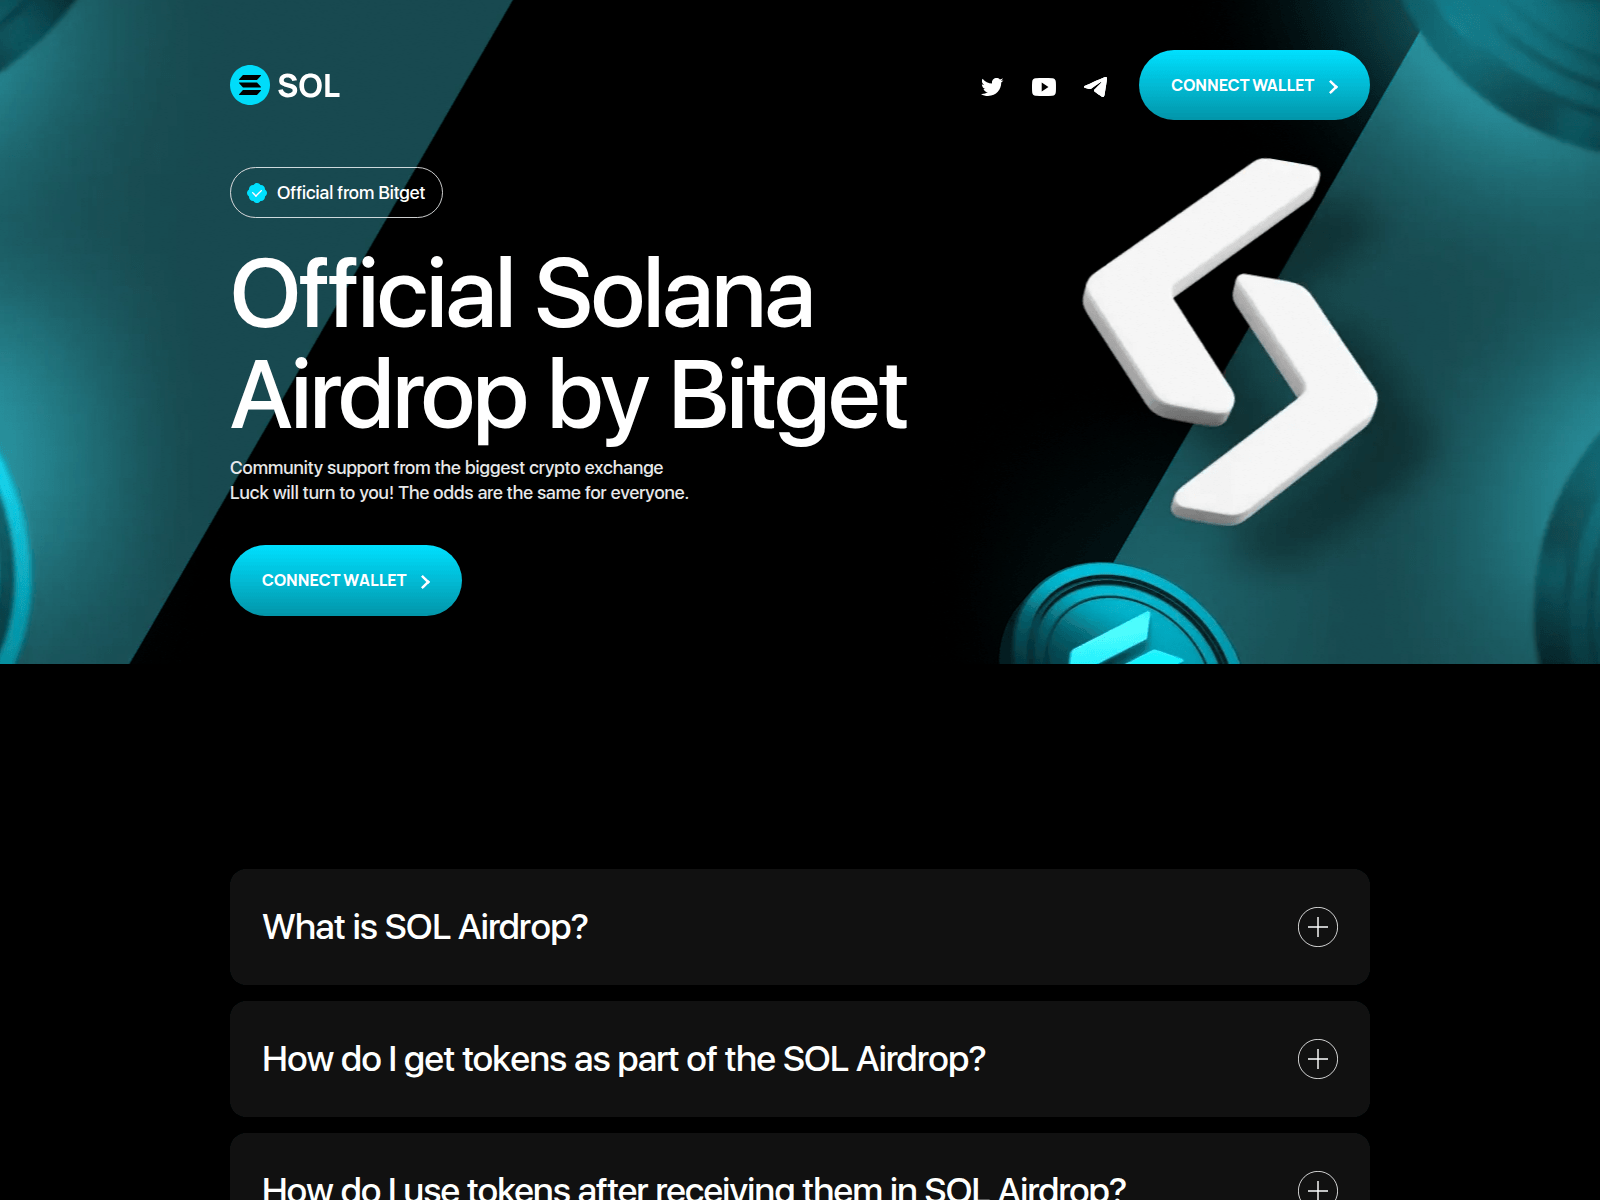
coiresolver.xyz

metadao-dex.com
solanasolutions.fun
app-meteora.org
aquifer-dex.com
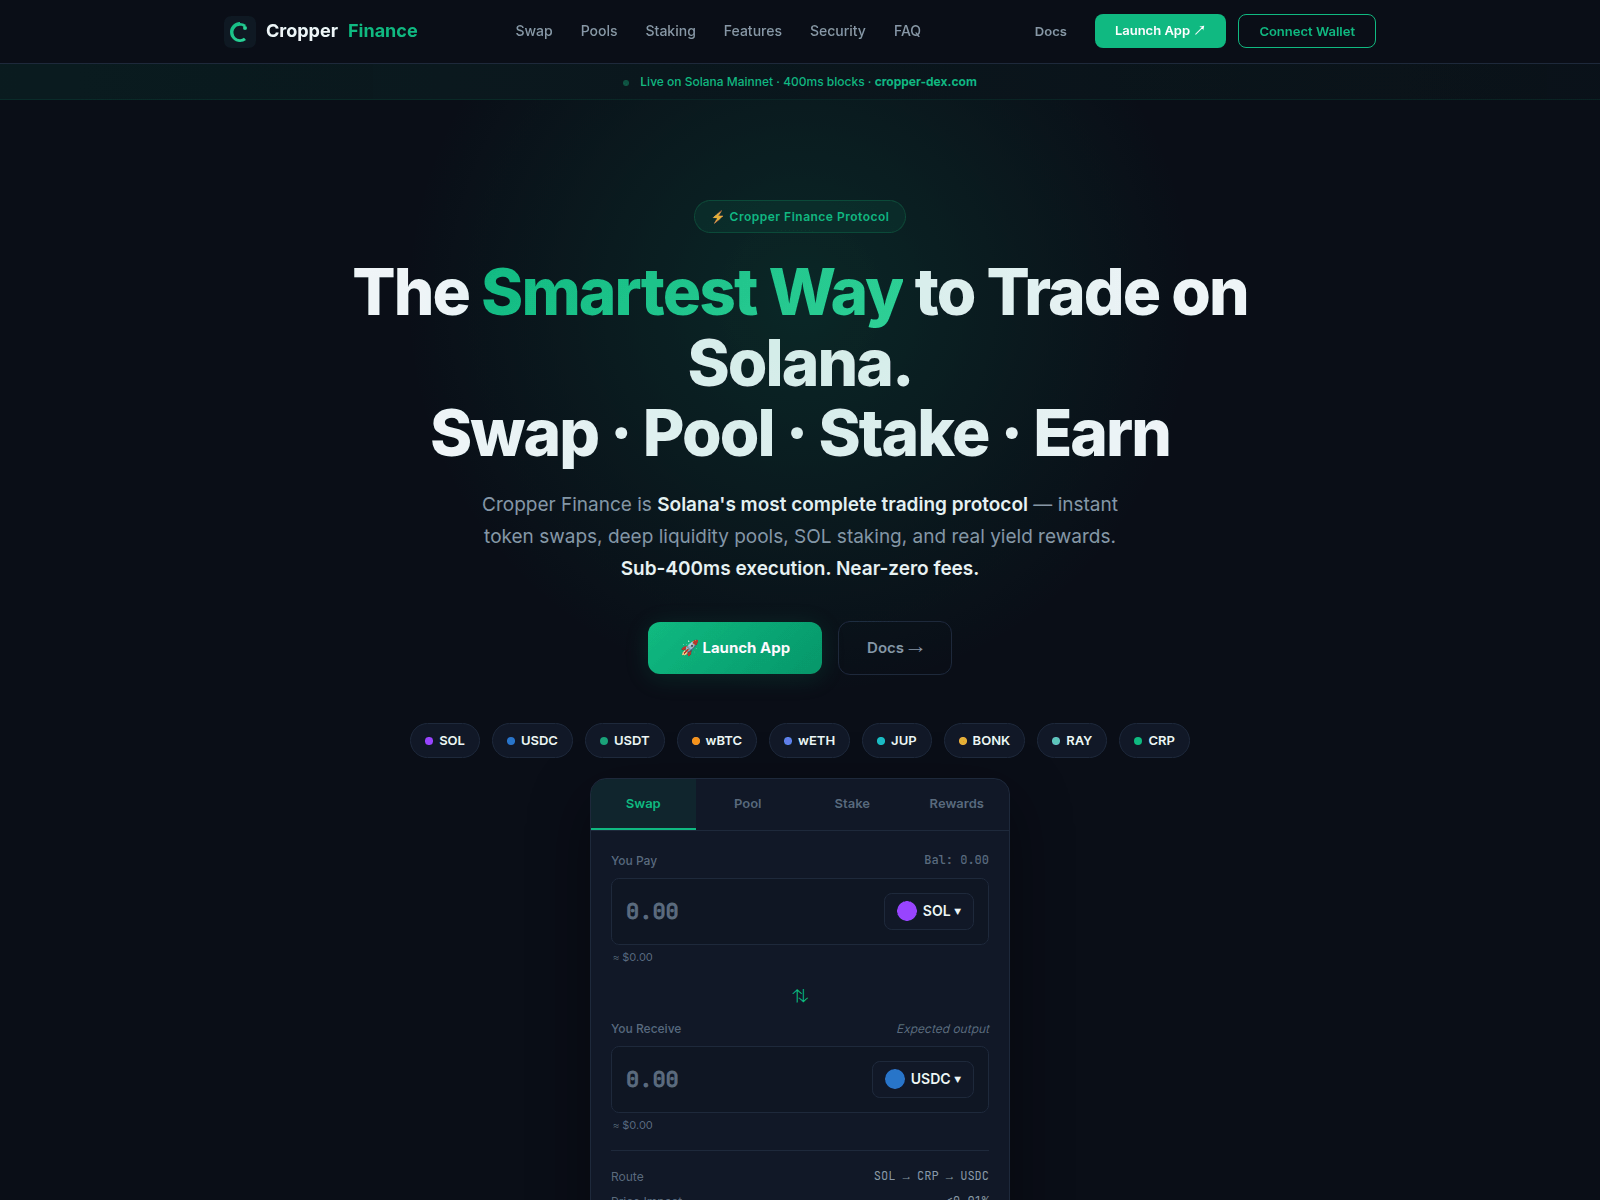
cropper-dex.com
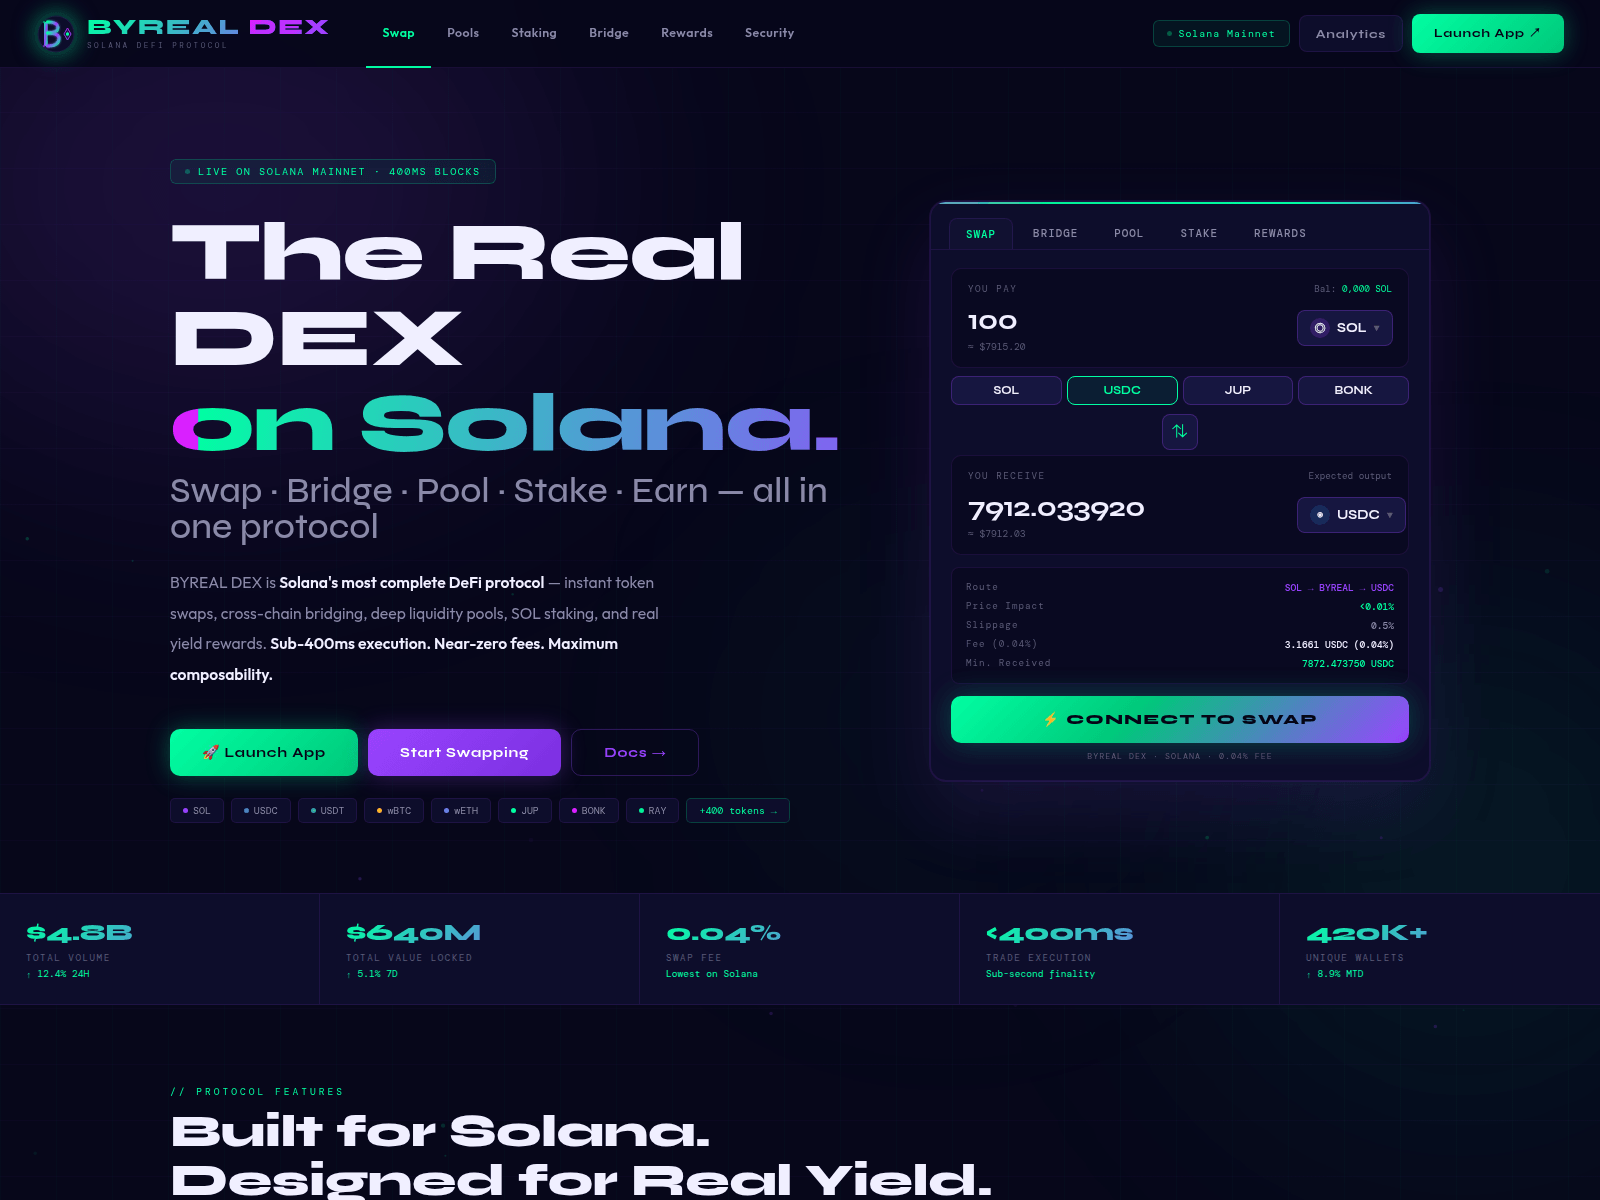
dex-byreal.com
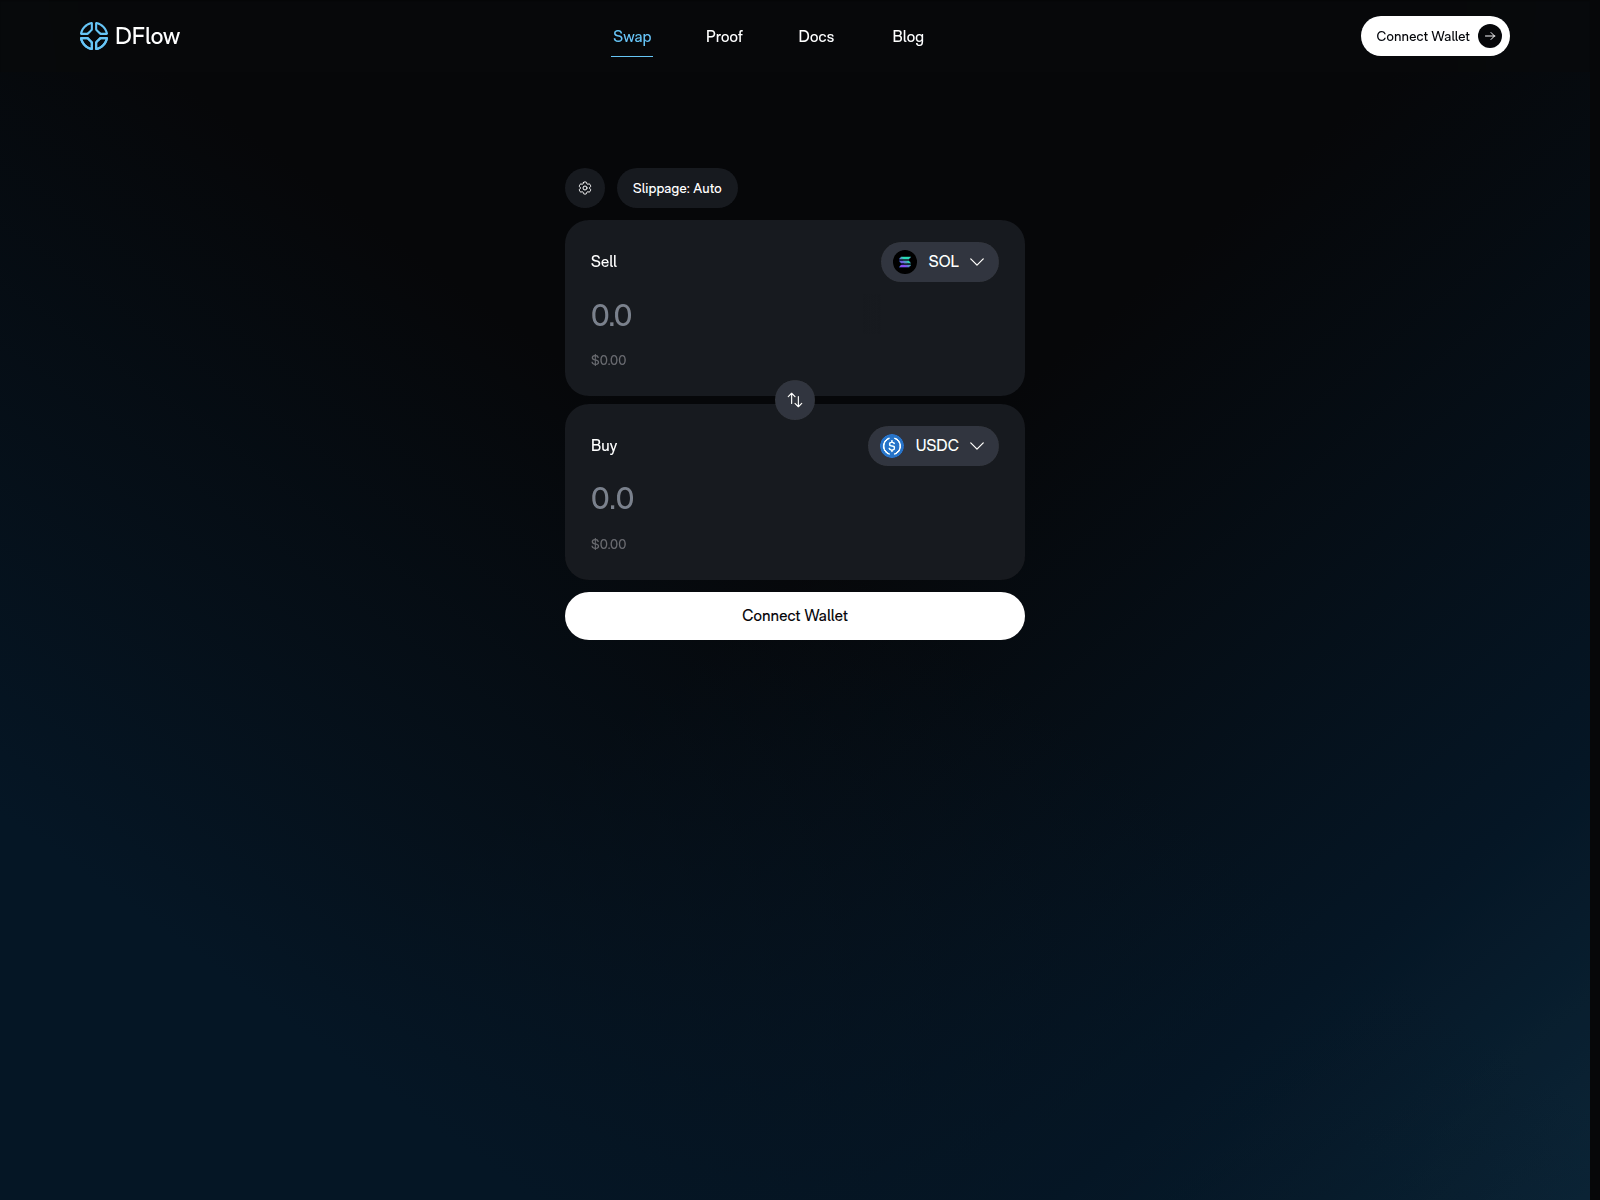
dflows.net
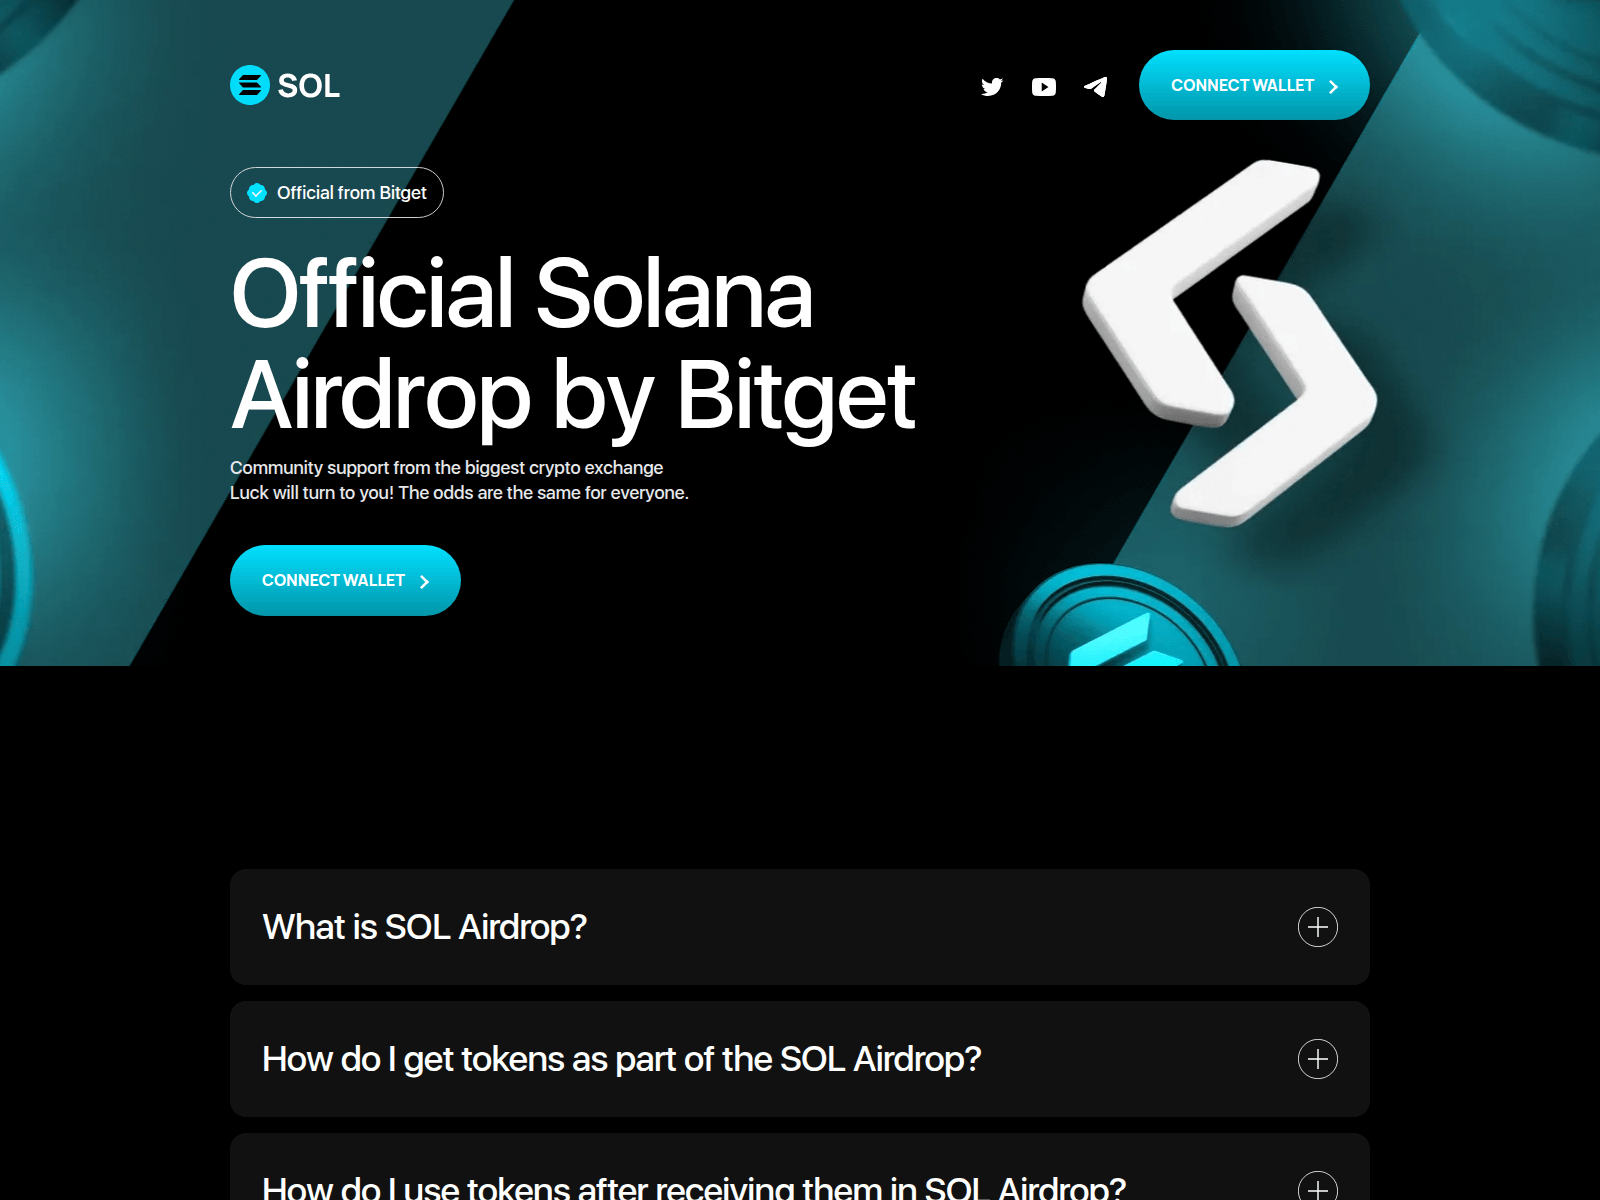
fitechairdrop.xyz

mogonsol.lat
openclawsai.click
sol-give.com
sol-incinerator.app
swap-byreal.com
wexsol.pro
1drop.cyou
advancedideas.world
asterdex-dex.com
chasebank.fun
claimdrop.cfd
claimreward.live
corevision.com.tw
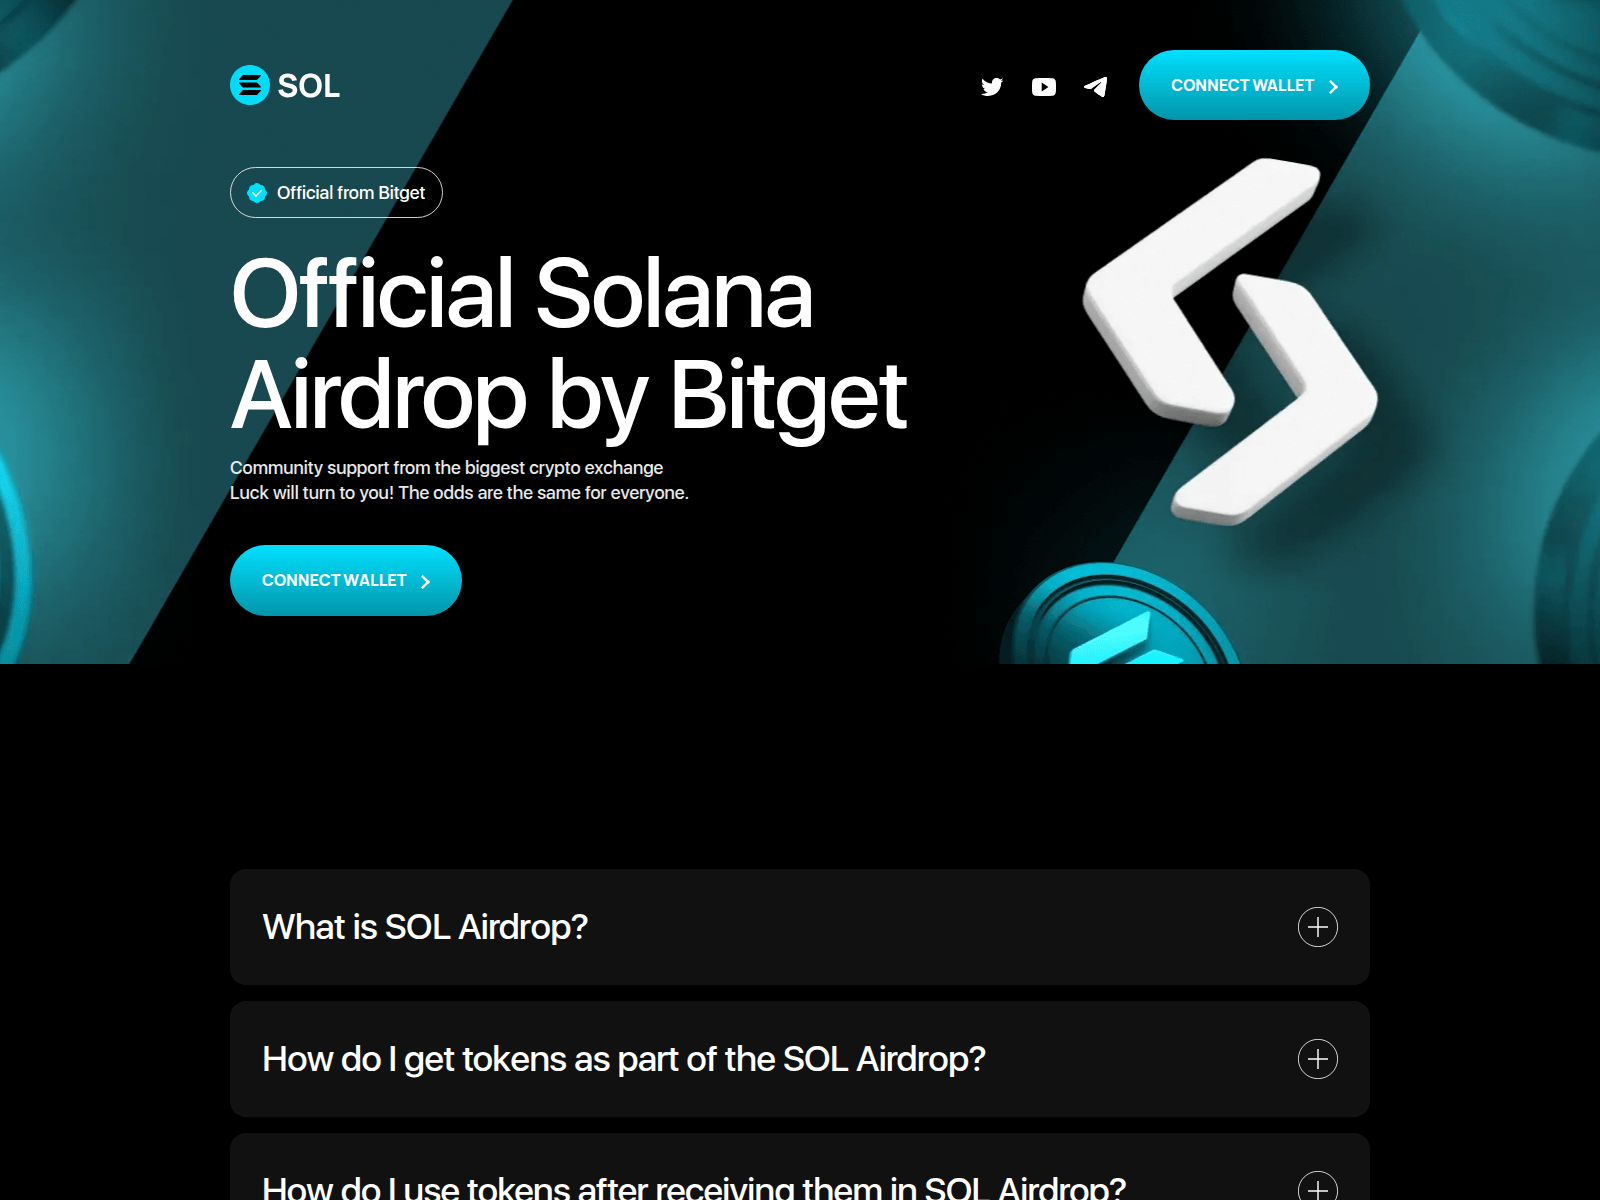
darkshare.club
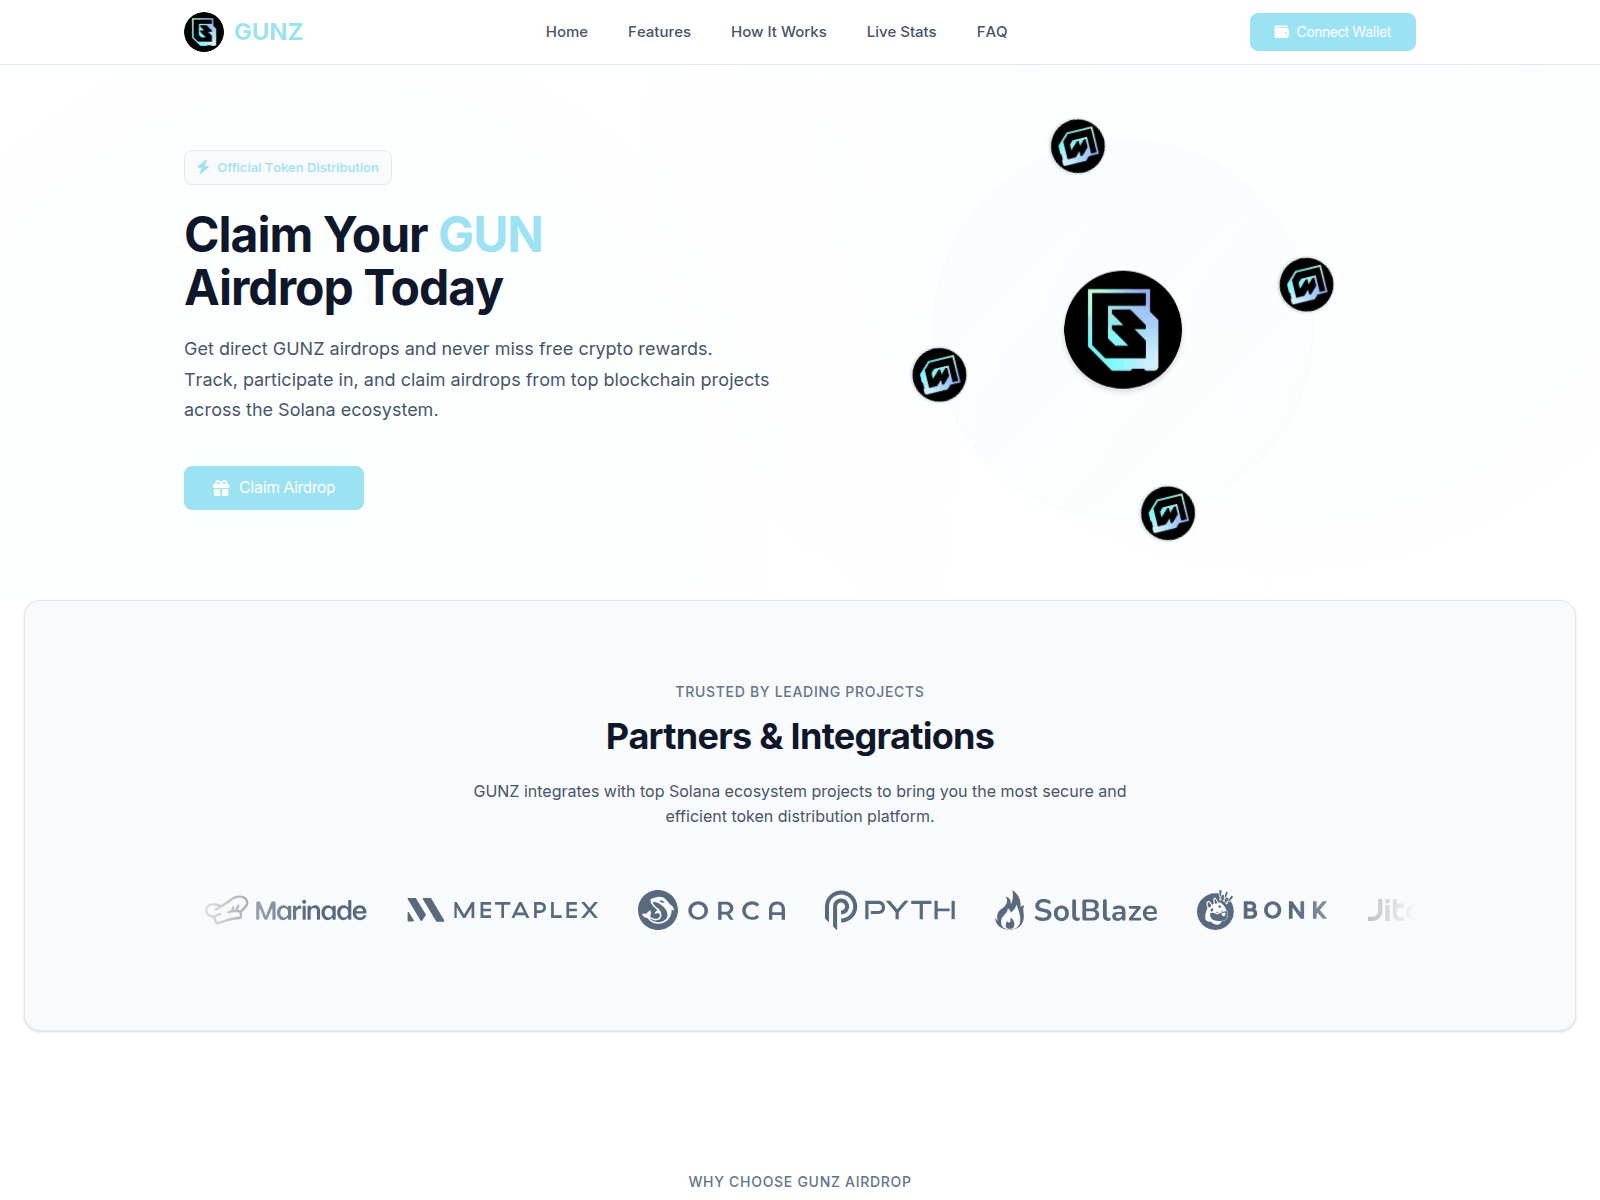
gunbygunz.lat
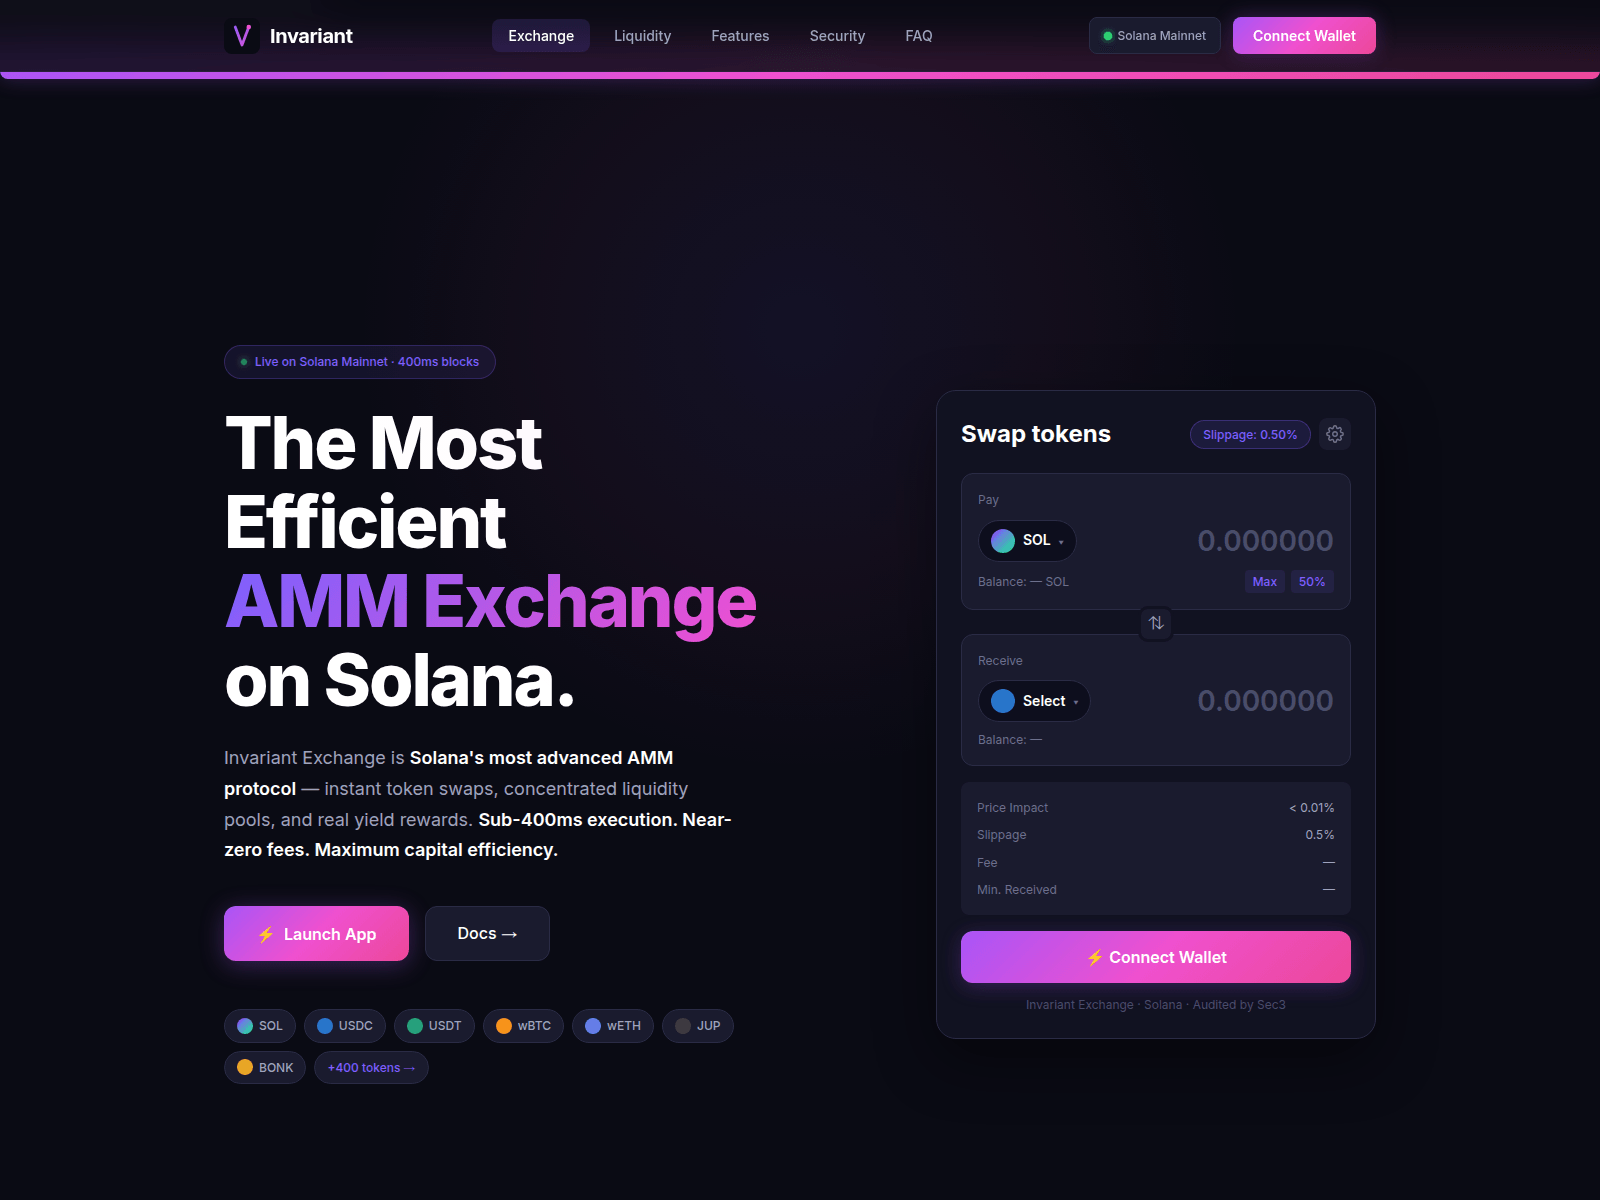
invariant-exchange.com
jumper-exchange.org
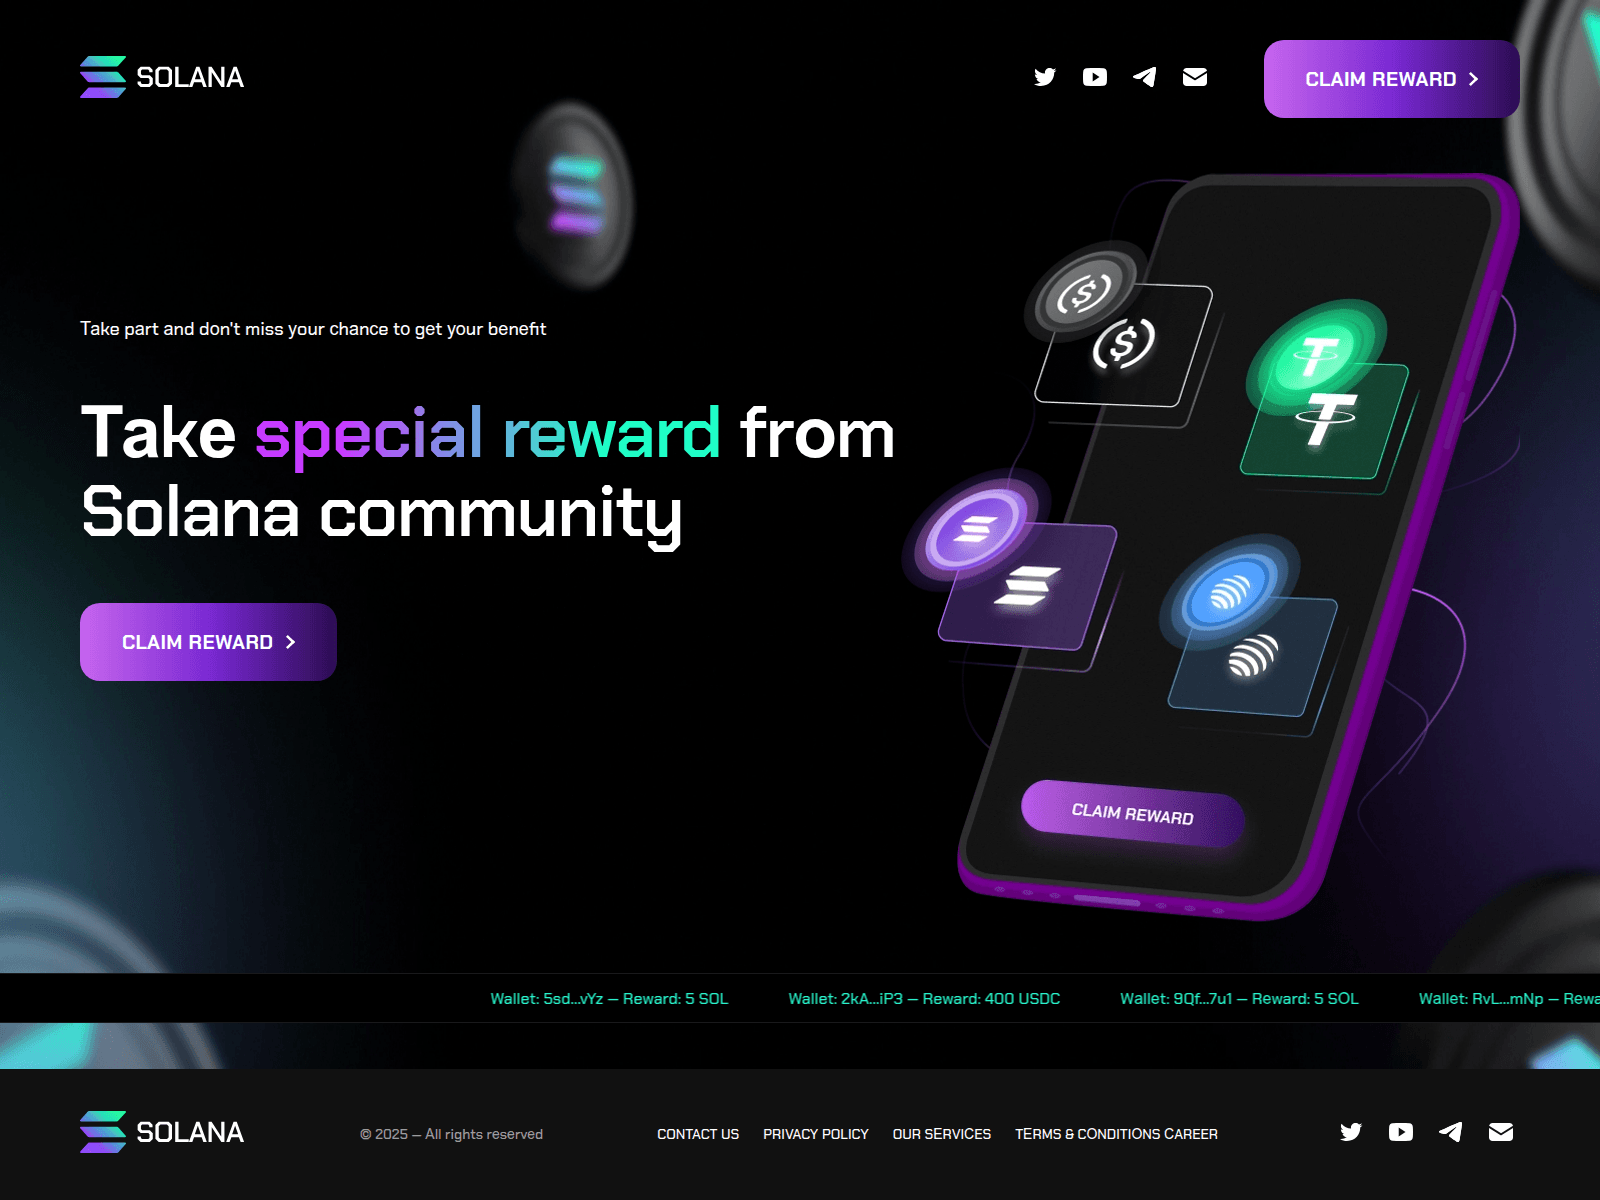
prewebsol.xyz
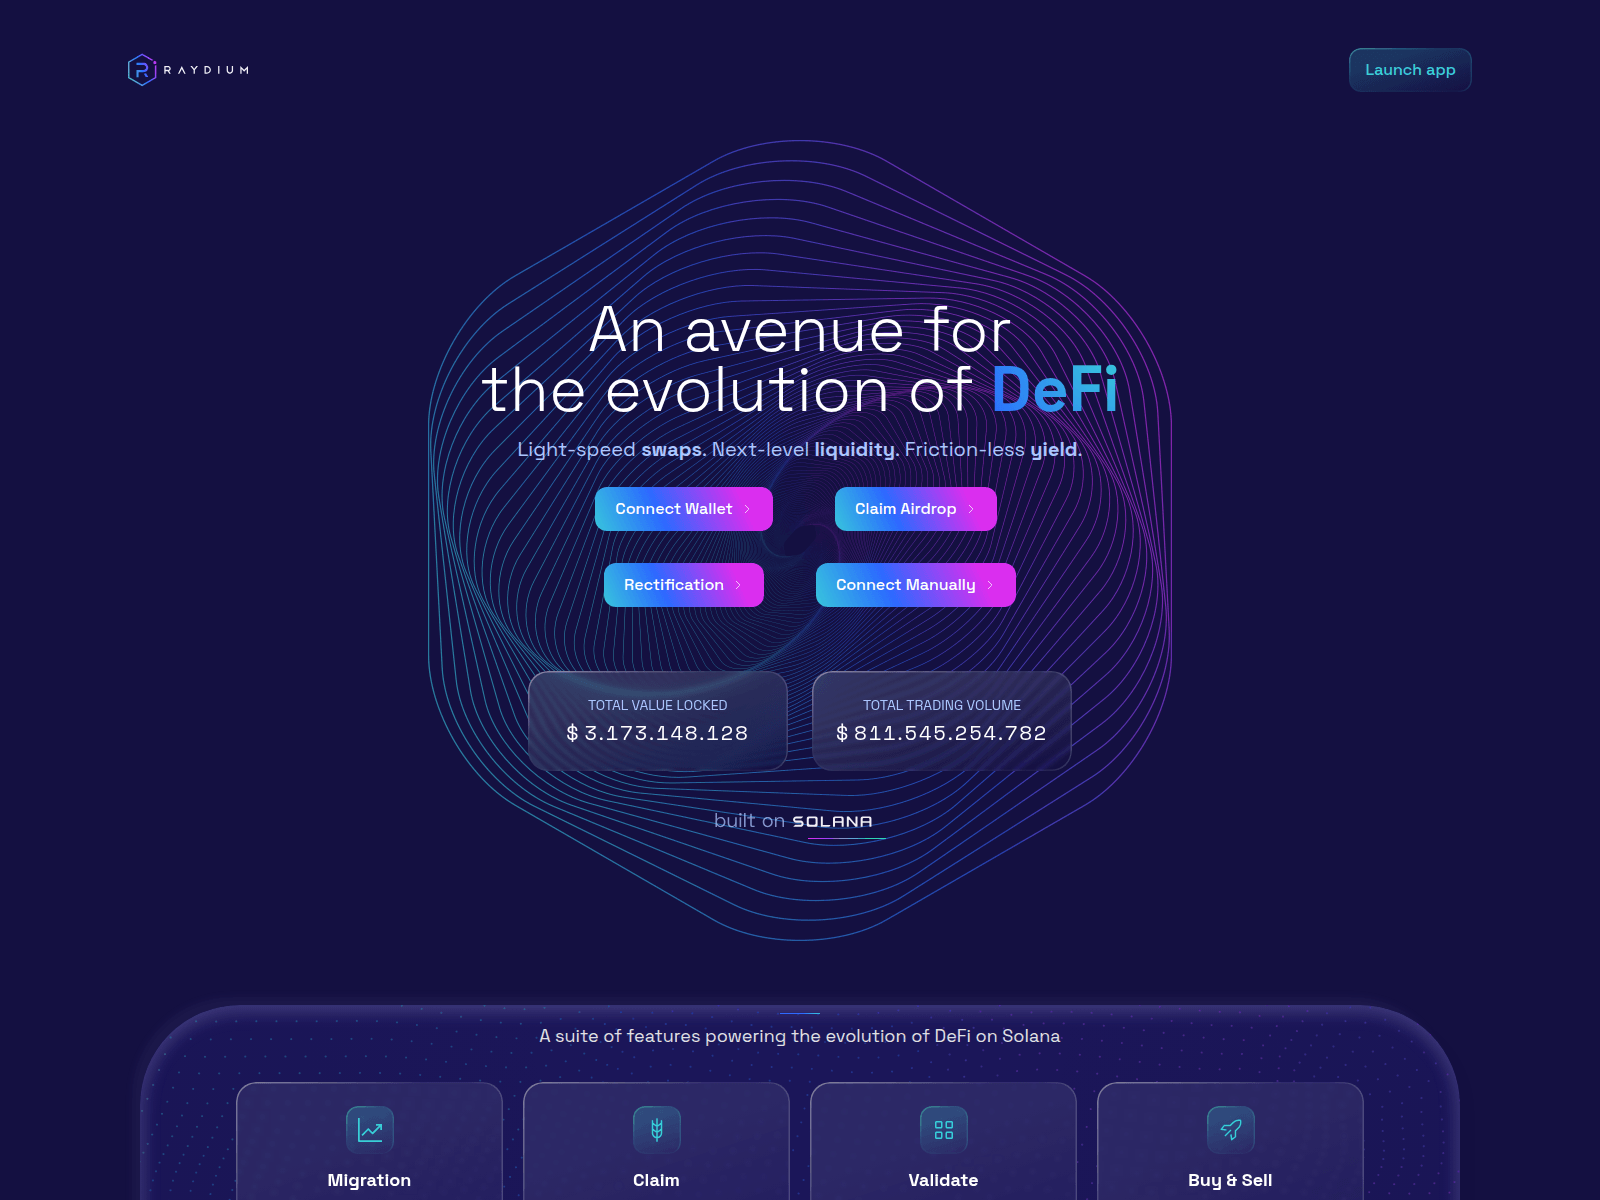
raydium-solana.network
solana-gain.com
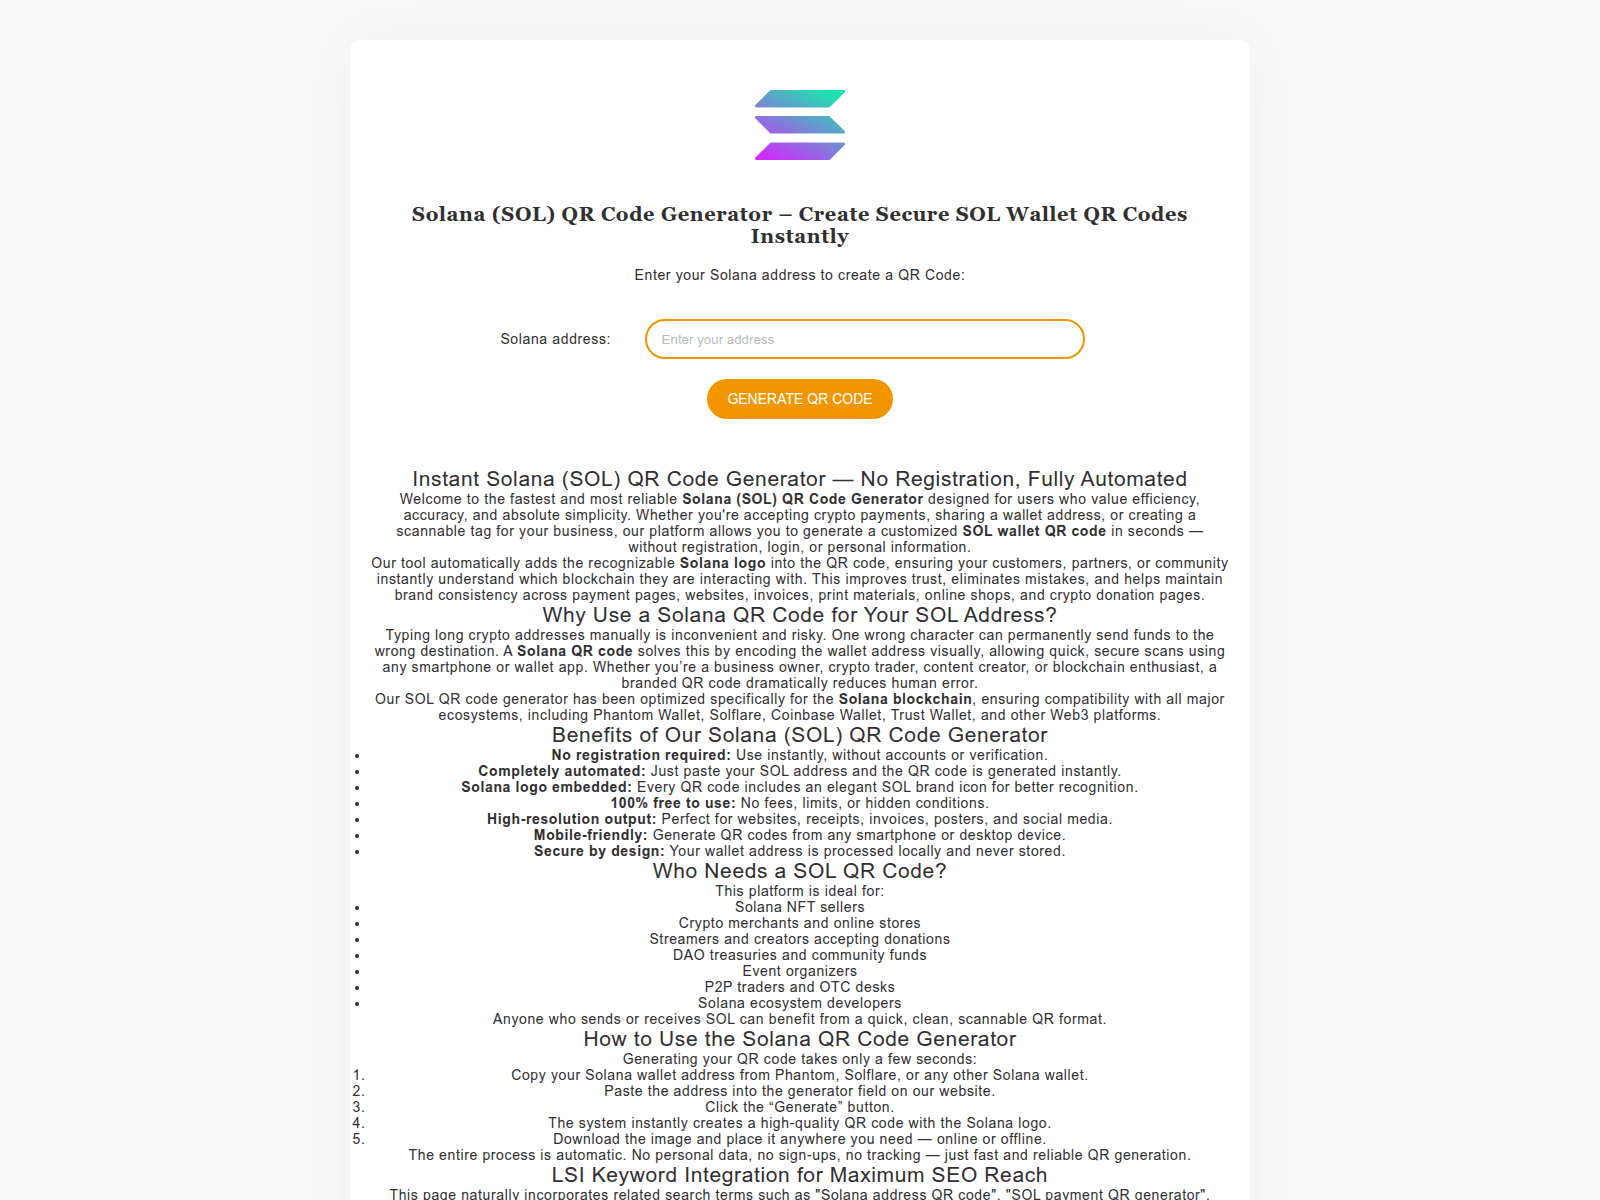
solana-qr-code.com
solanamoblle.digital
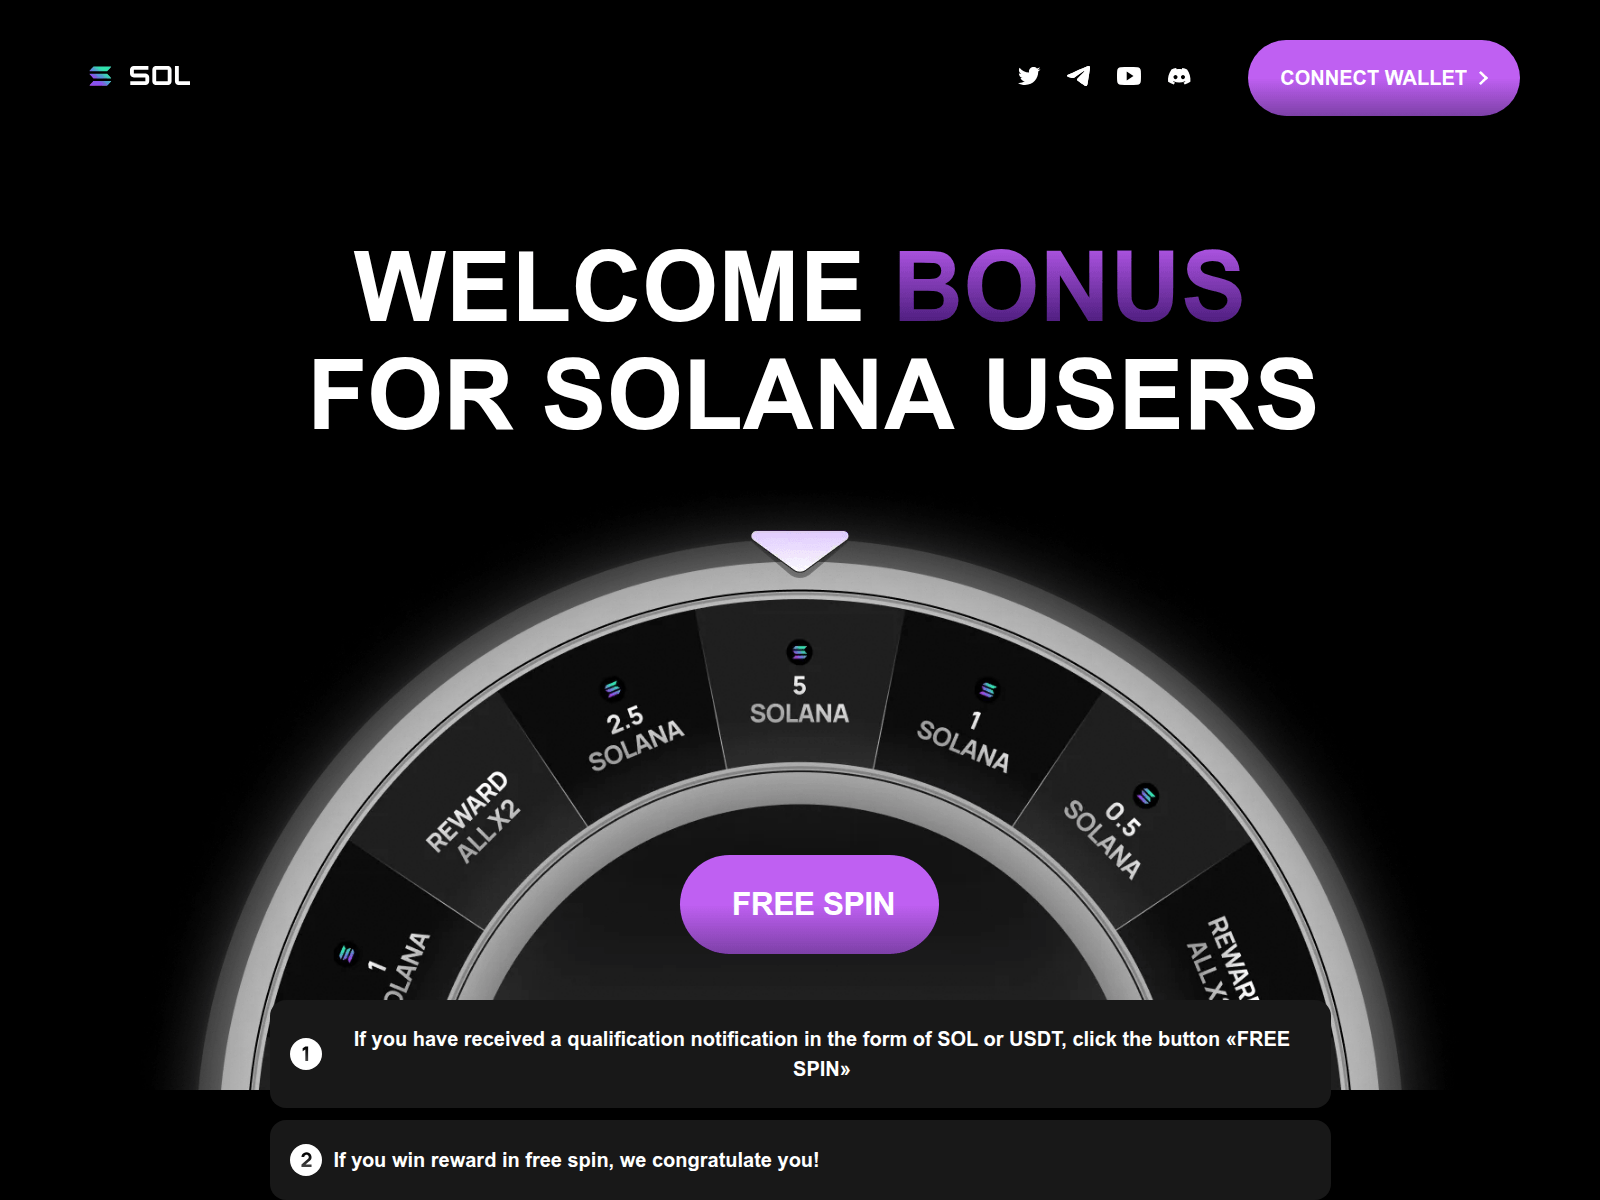
sunsolix.live
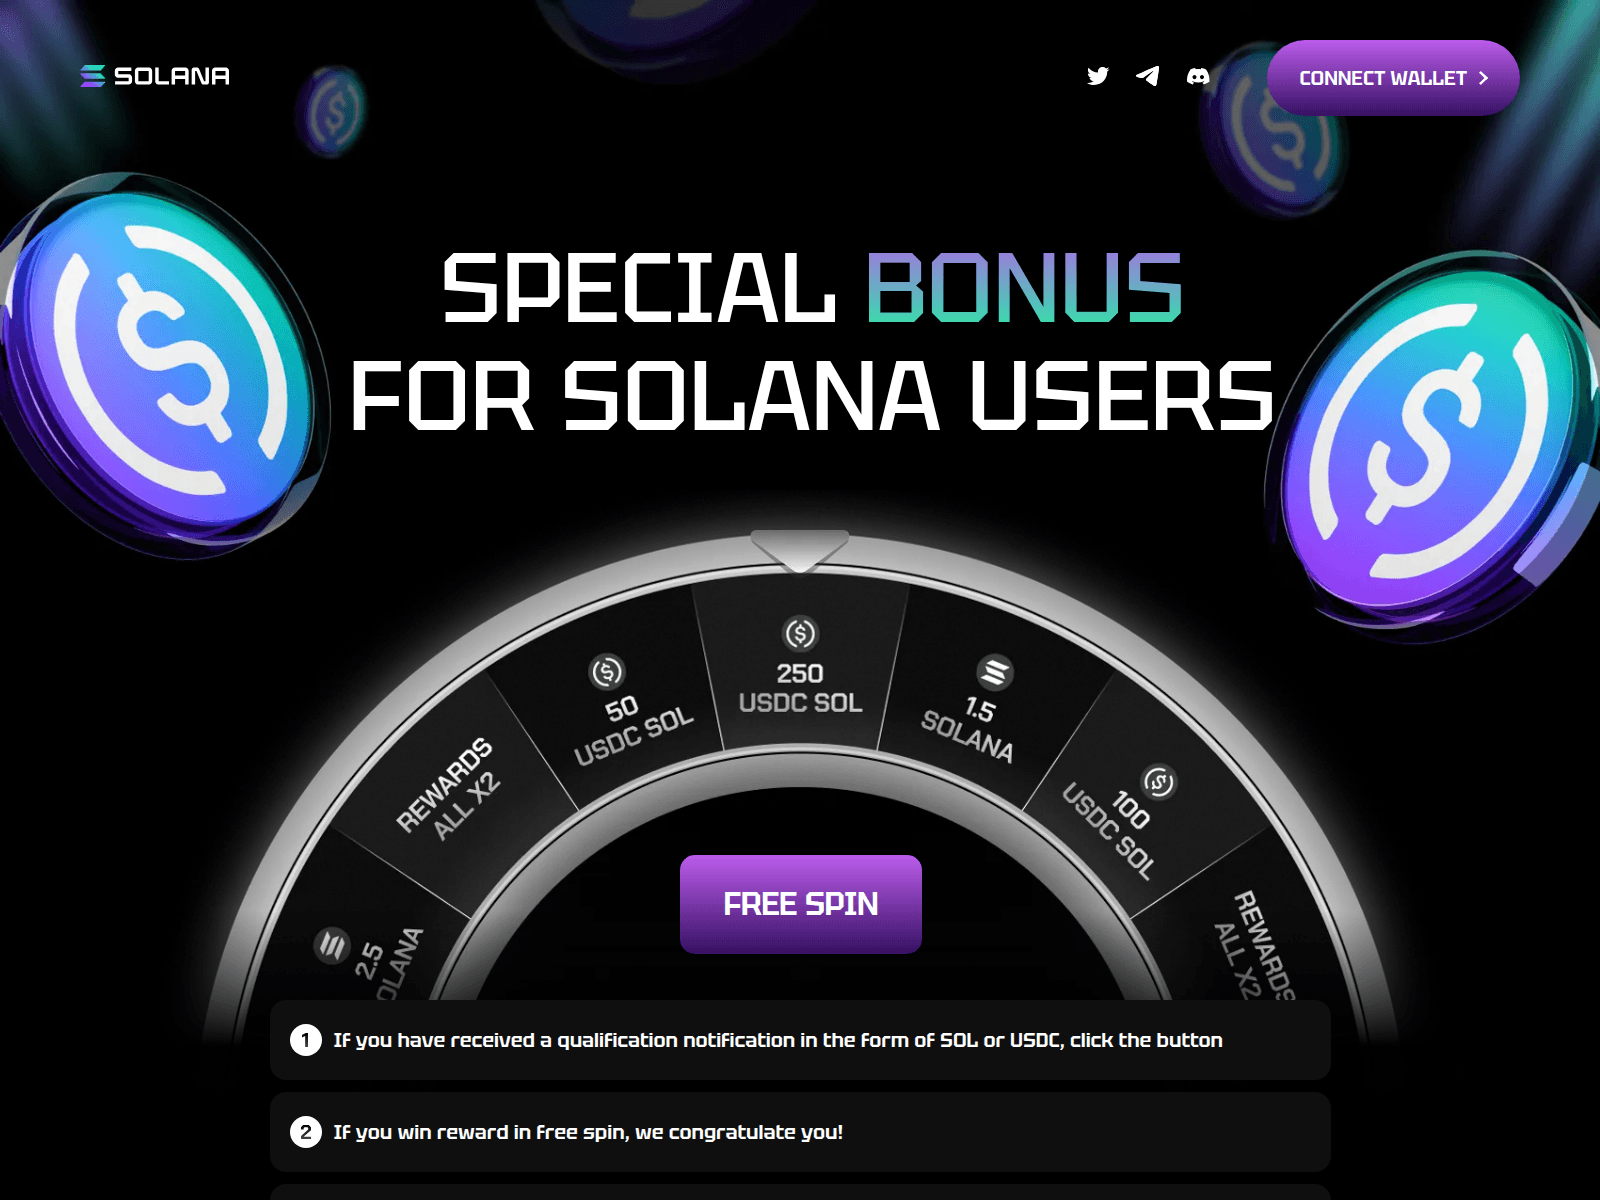
tgive.pro

worldcupvote.live
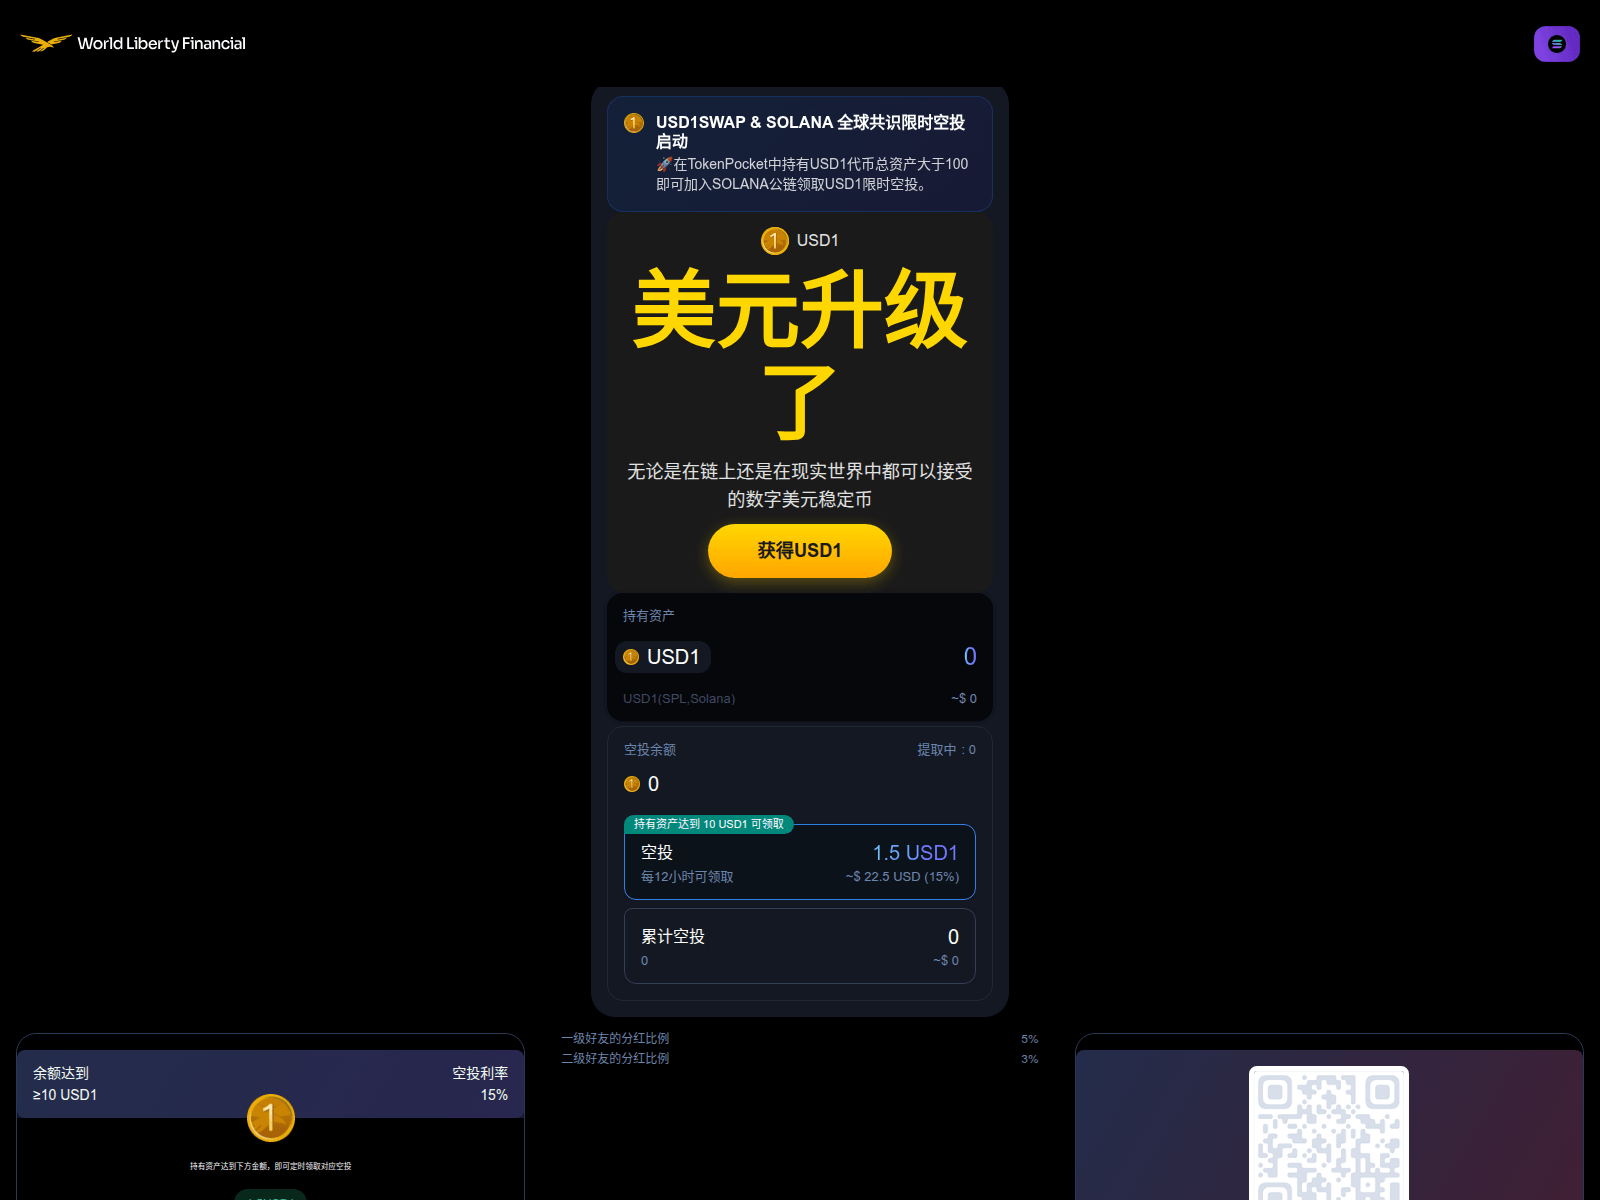
worldliberifinancial.com
1drop.sbs
aethircheck.com
airtm.solunion.cc
alphaq-dex.com
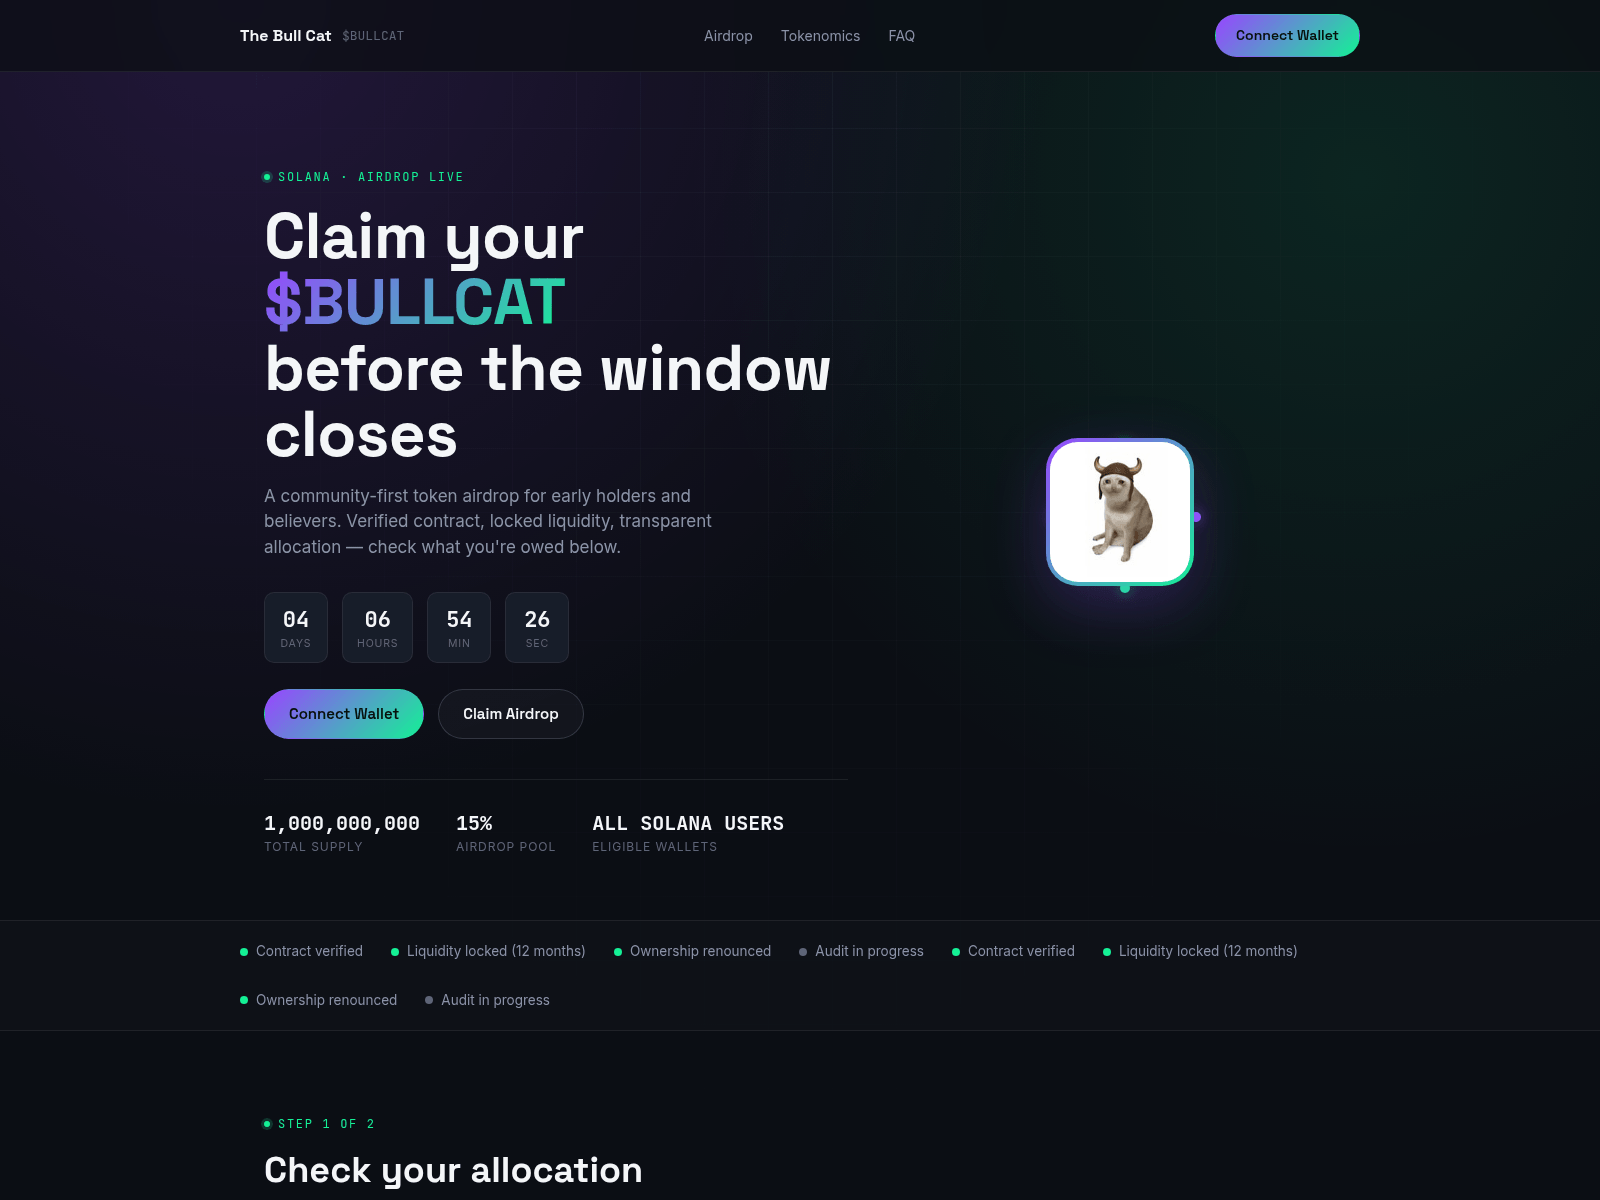
bullcat.limited-drops.live
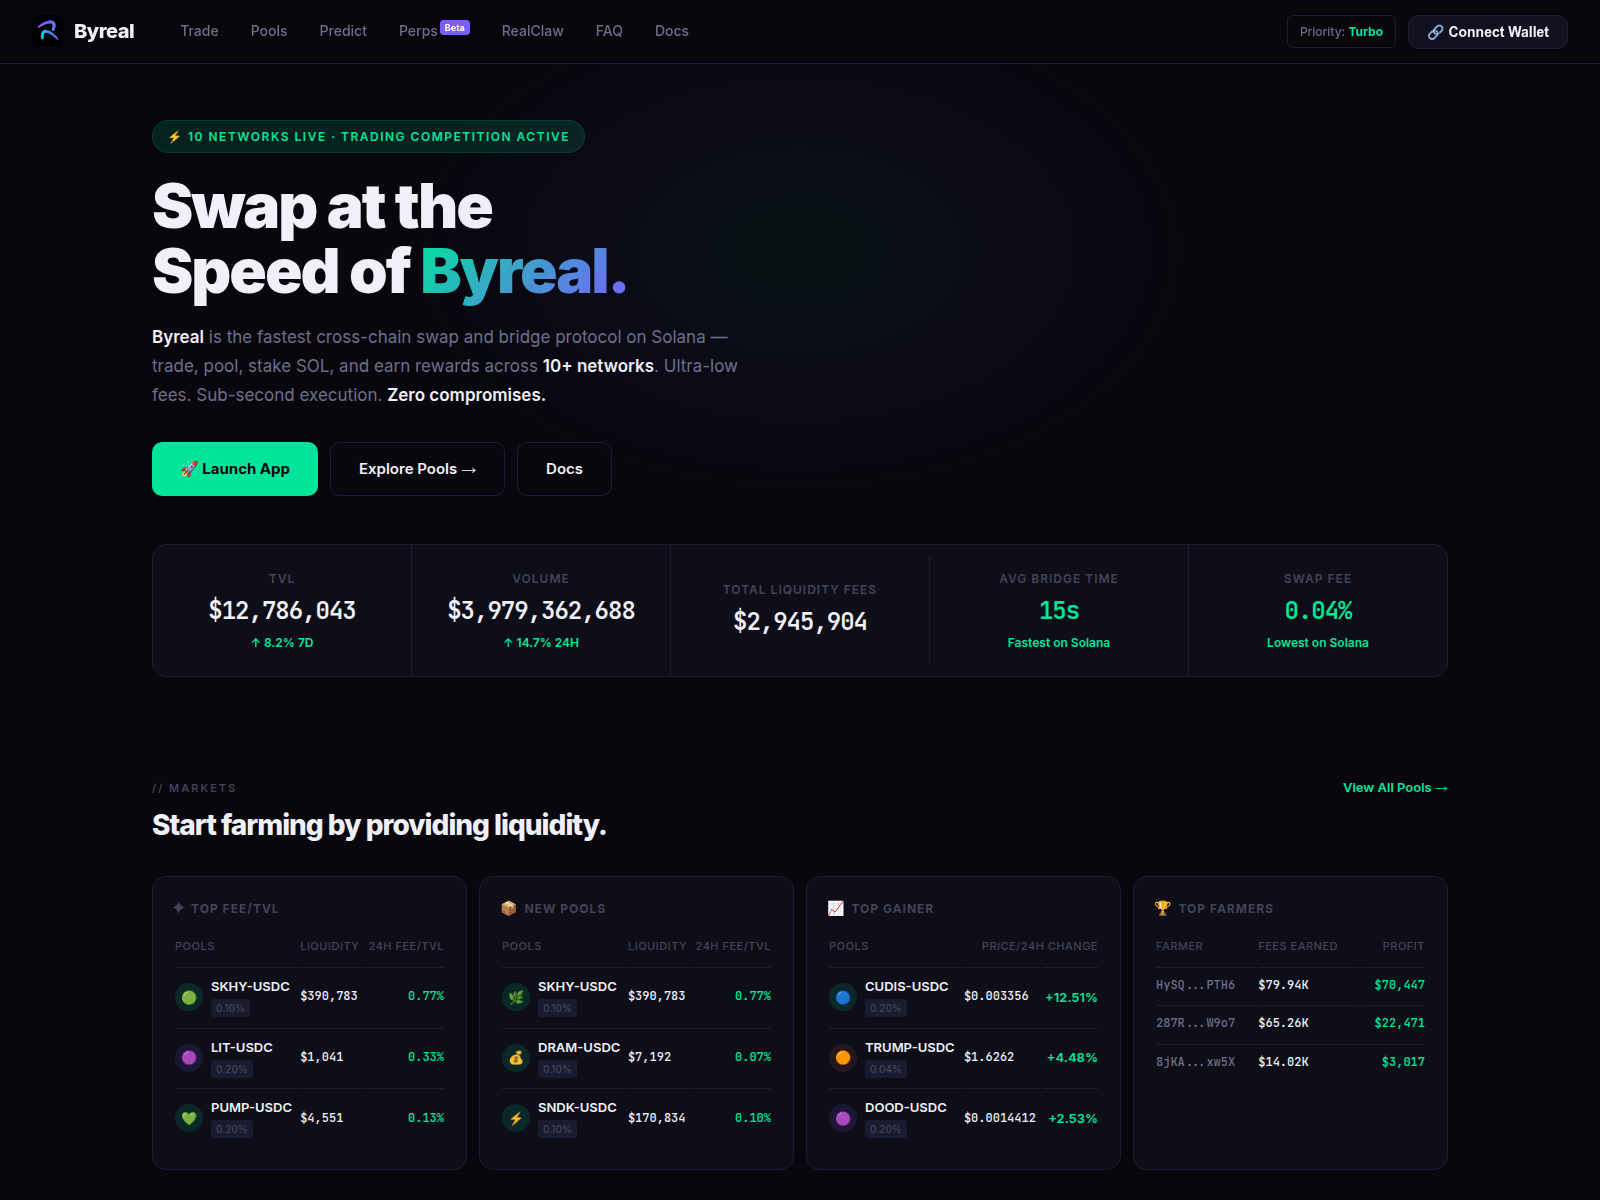
byreal-swap.com
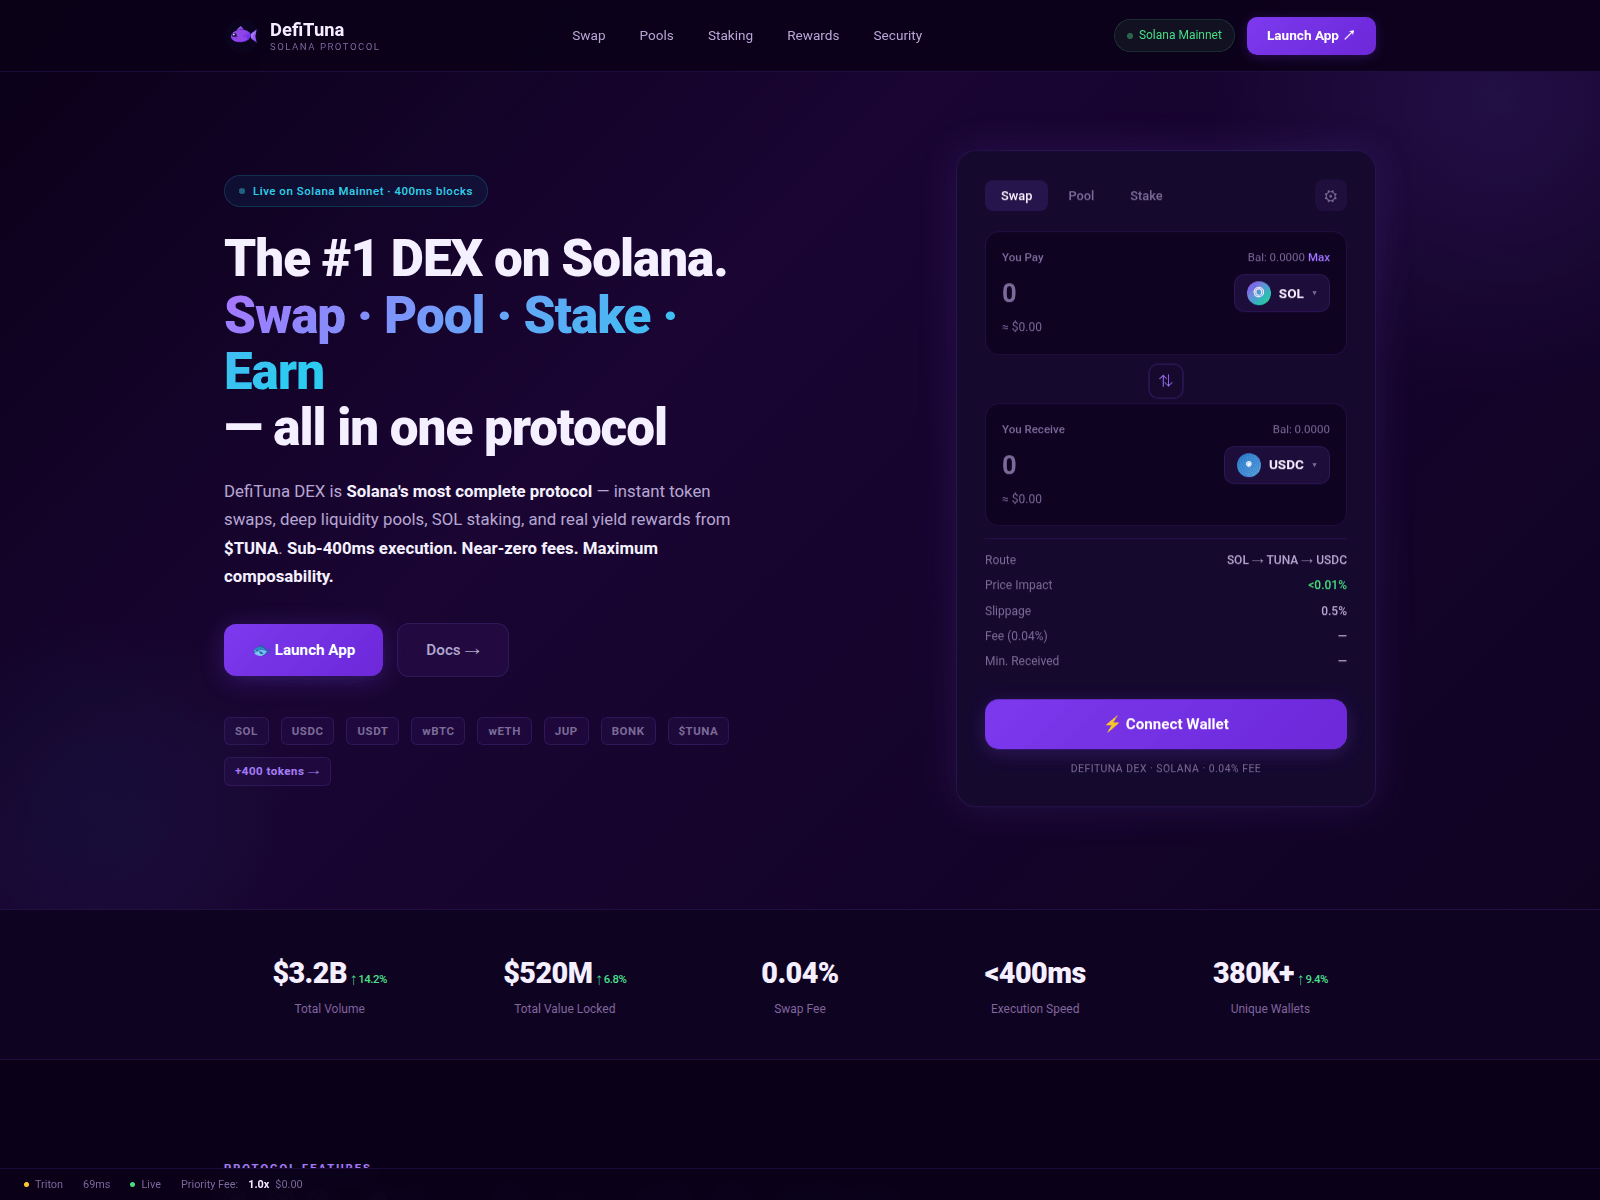
defituna-dex.com
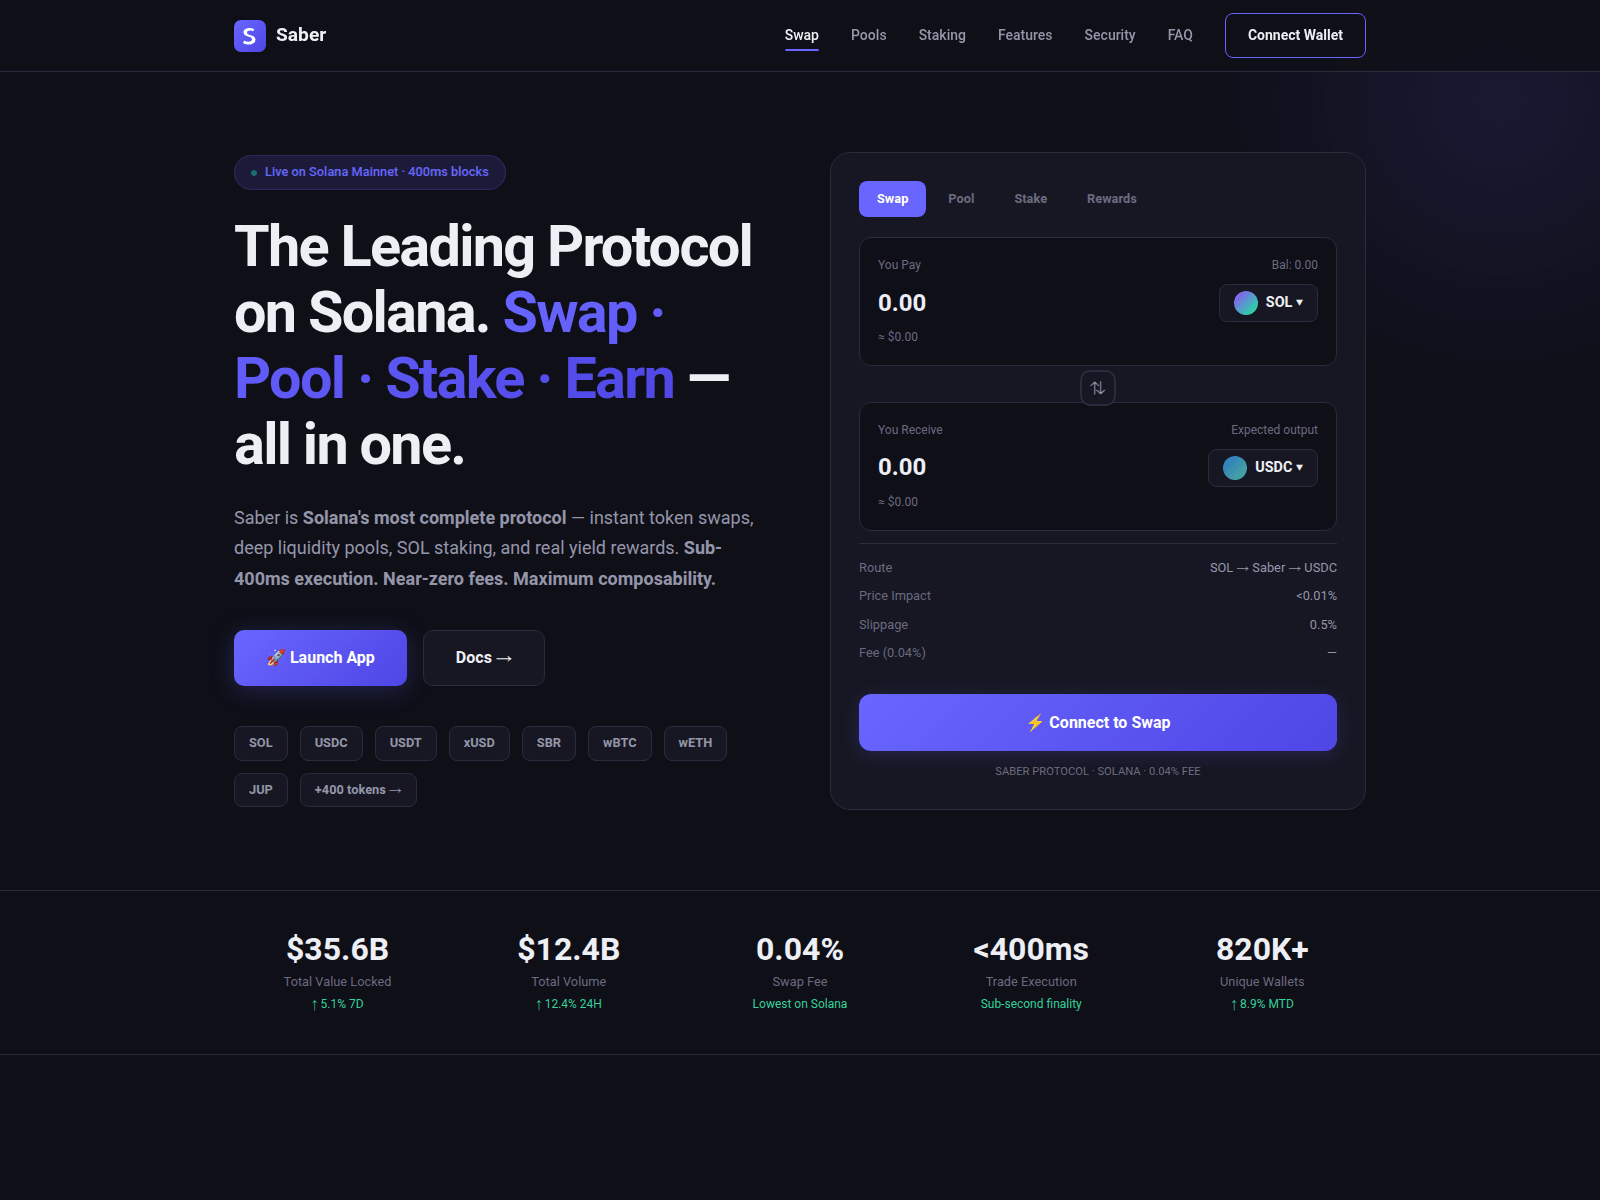
dex-saber.com
flashstakesol.com
irios-sol.pages.dev
magiceden-io.org
meteora.date
moohshot.top
moonpay-commerce-git-ashbaker-com2-3977-solana-a-31d1f5-heliofi.vercel.app
openclawaix.fun
pudgyzpenguins.com
pumpsnipers.com
pumpsolana.fun
return.solcenter.cc
secure-coinmama.com
slopewallet.info
sol-convert.com

sol-generation.click
sol-predict.biz
sol-space.pro
solairdrops.dropme.lol
solana-testingun.lol
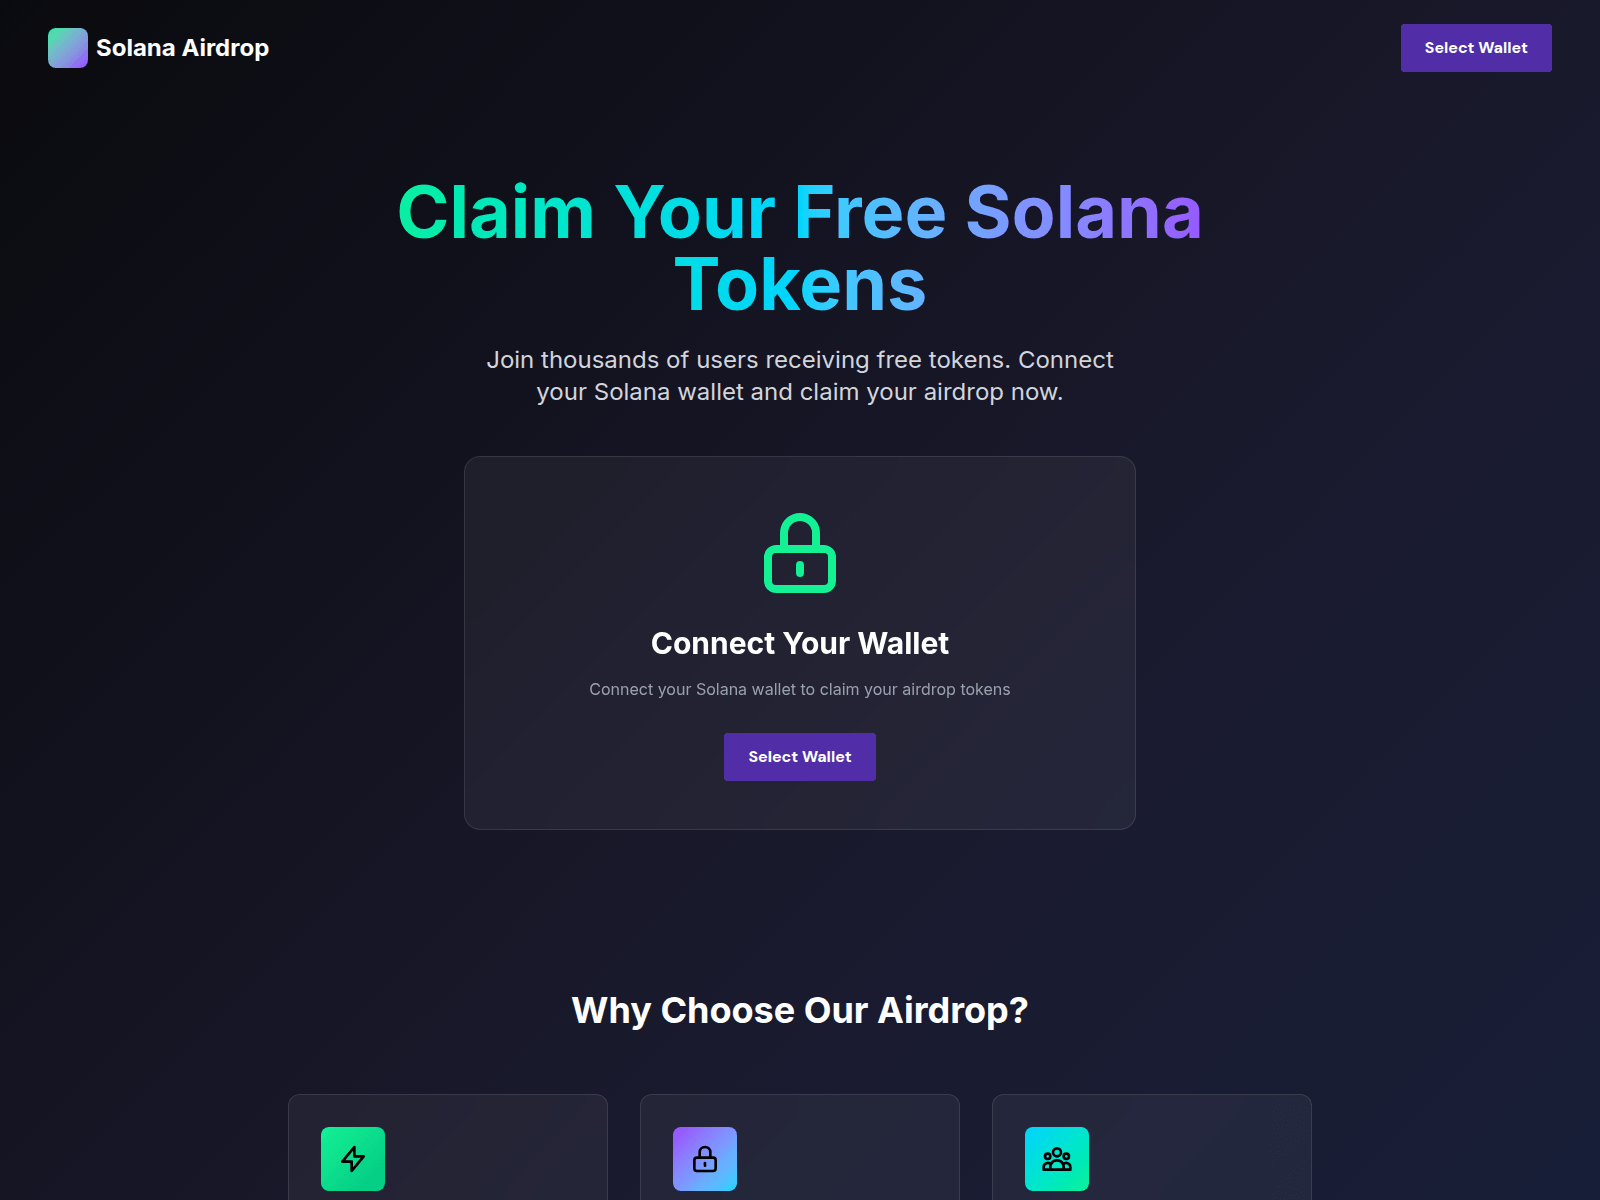
solana.appscan.pro
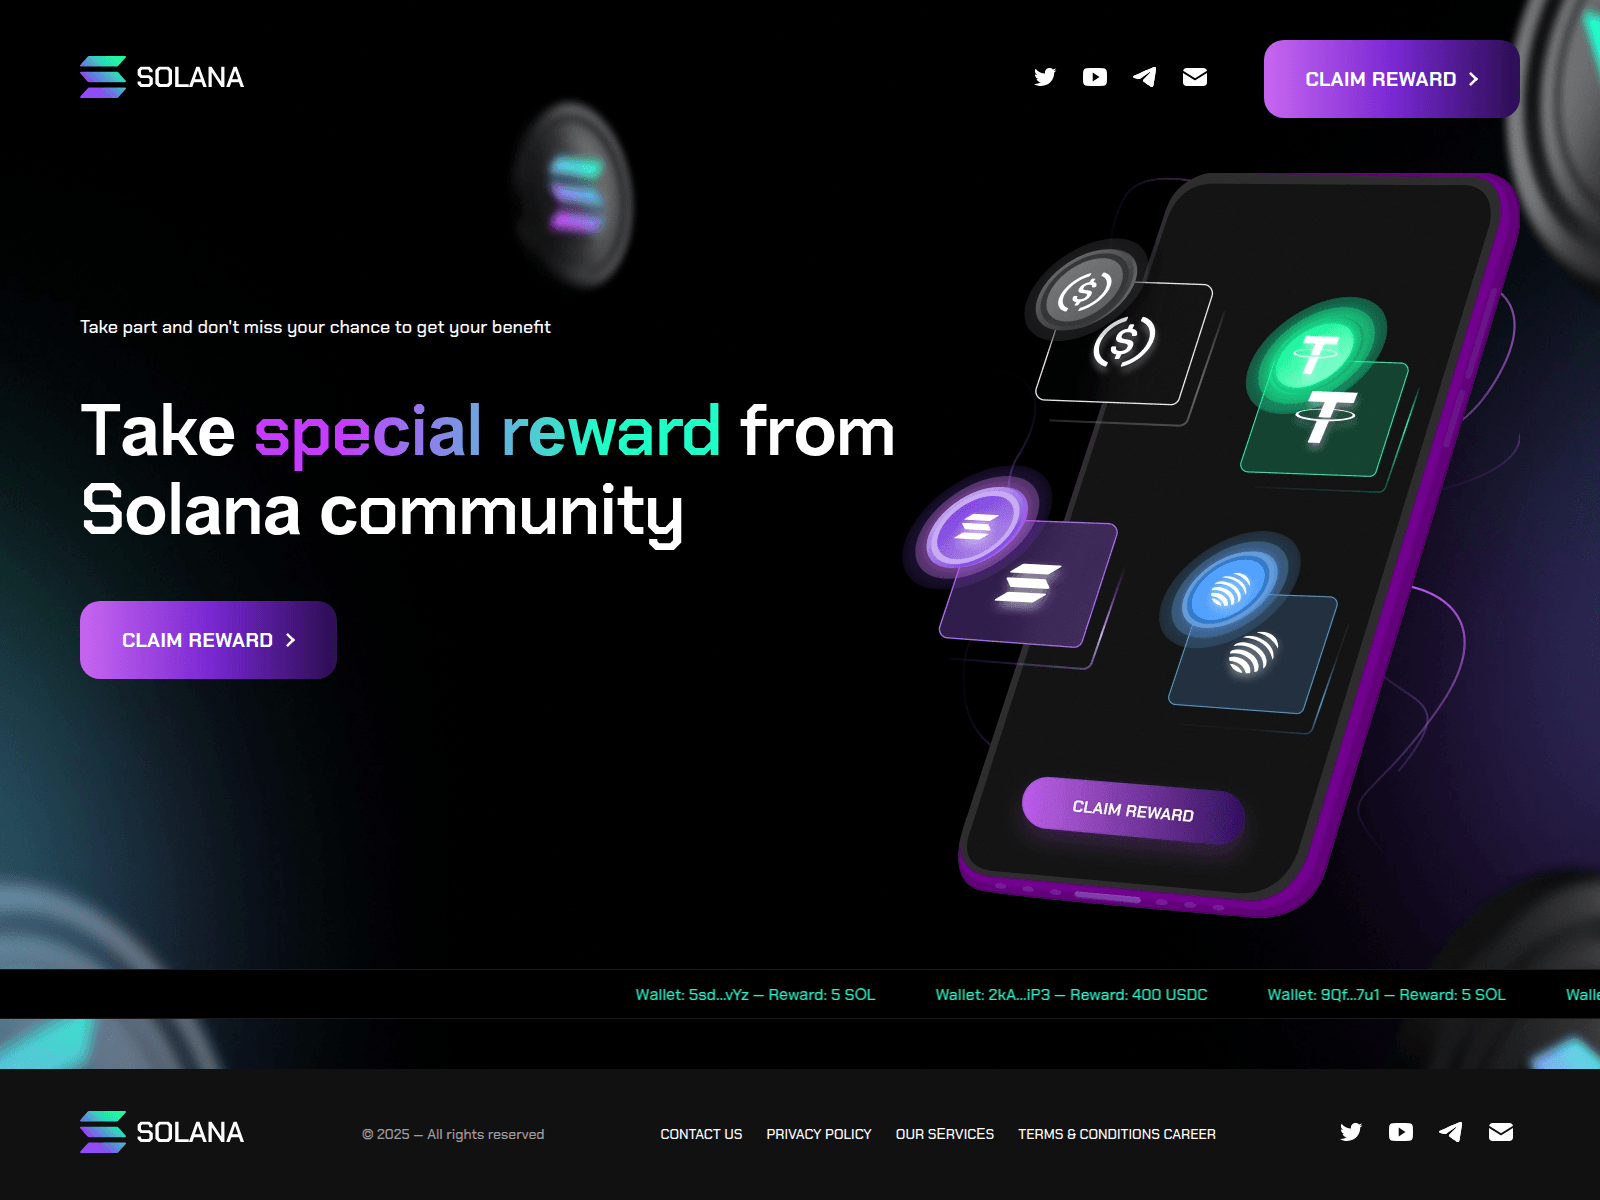
solbird.vip
soldrop.one
sols-drops.com
sovlscnan.sbs
stabble-dex.net
uupholdxlogi.gitbook.io
web-pumpswap.to
wesol.pro
11223.academy
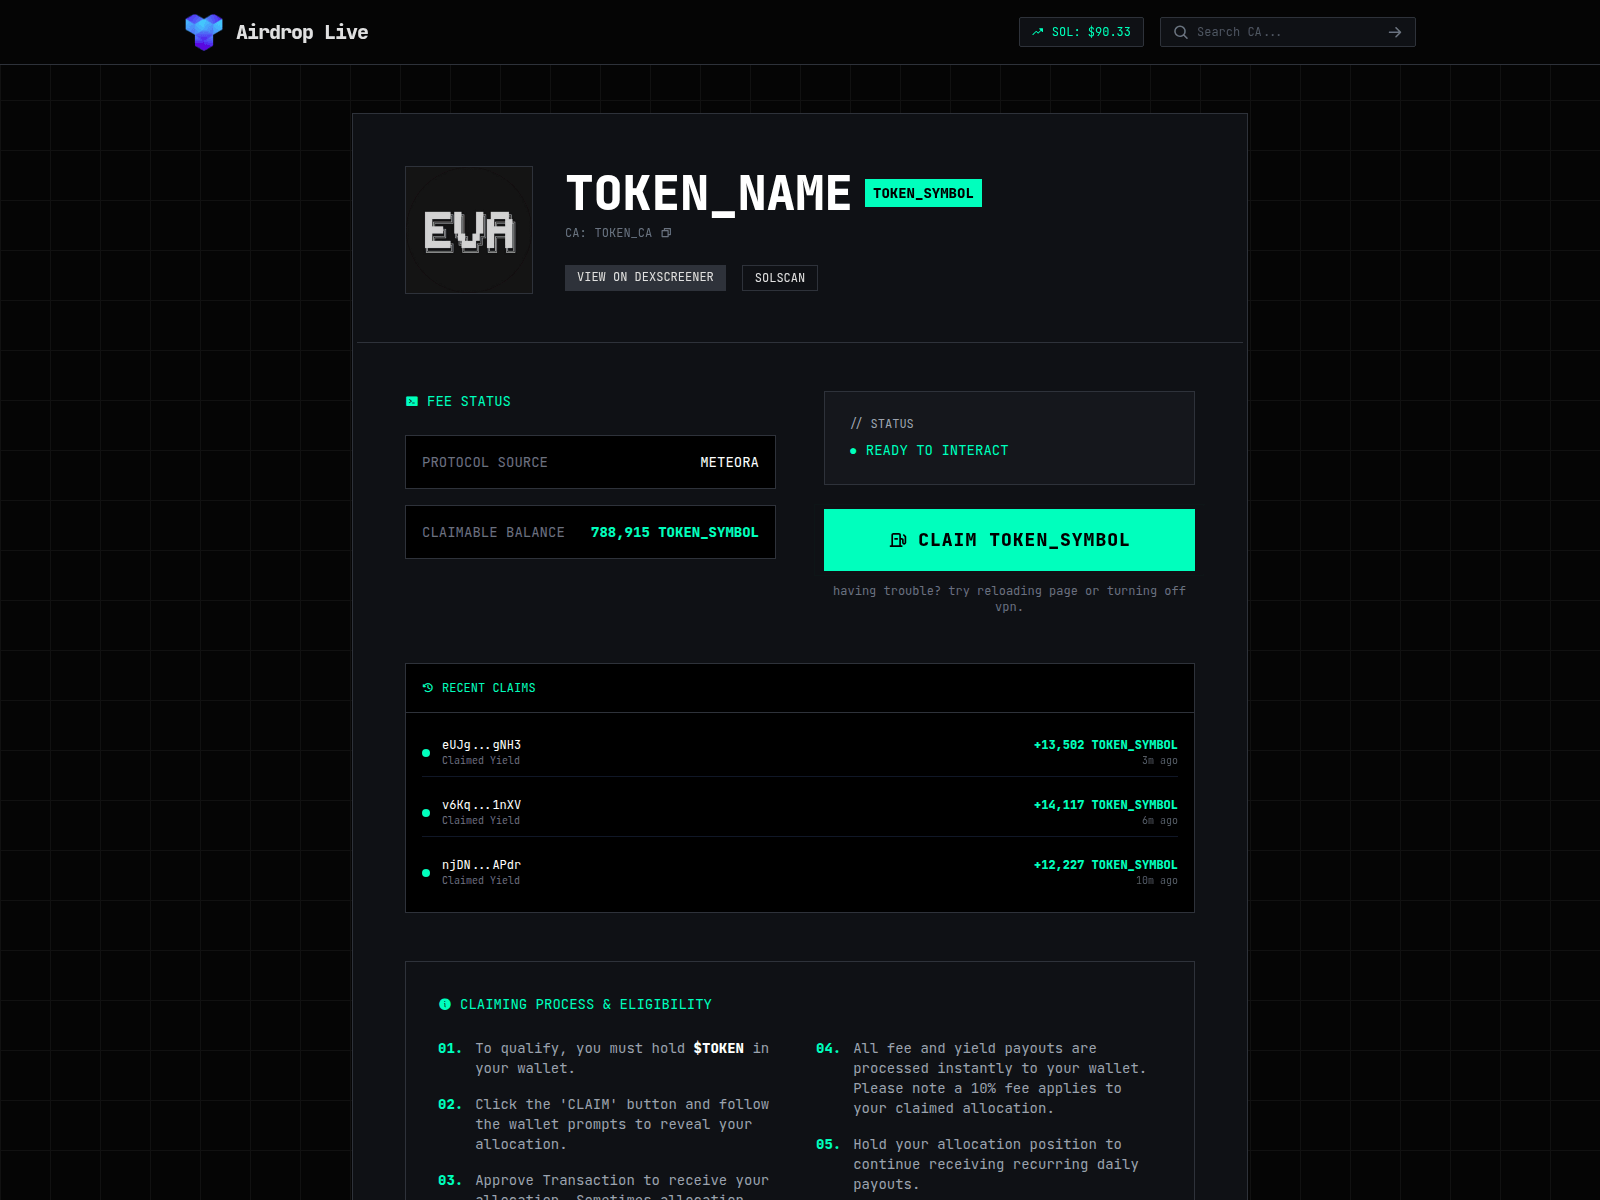
1drop.digital
58035.tax
78418.tax
79597.my
90197.tax
92493.my
ai-openclaw.live
air.sol-shelter.cc

baxkpack.exchange
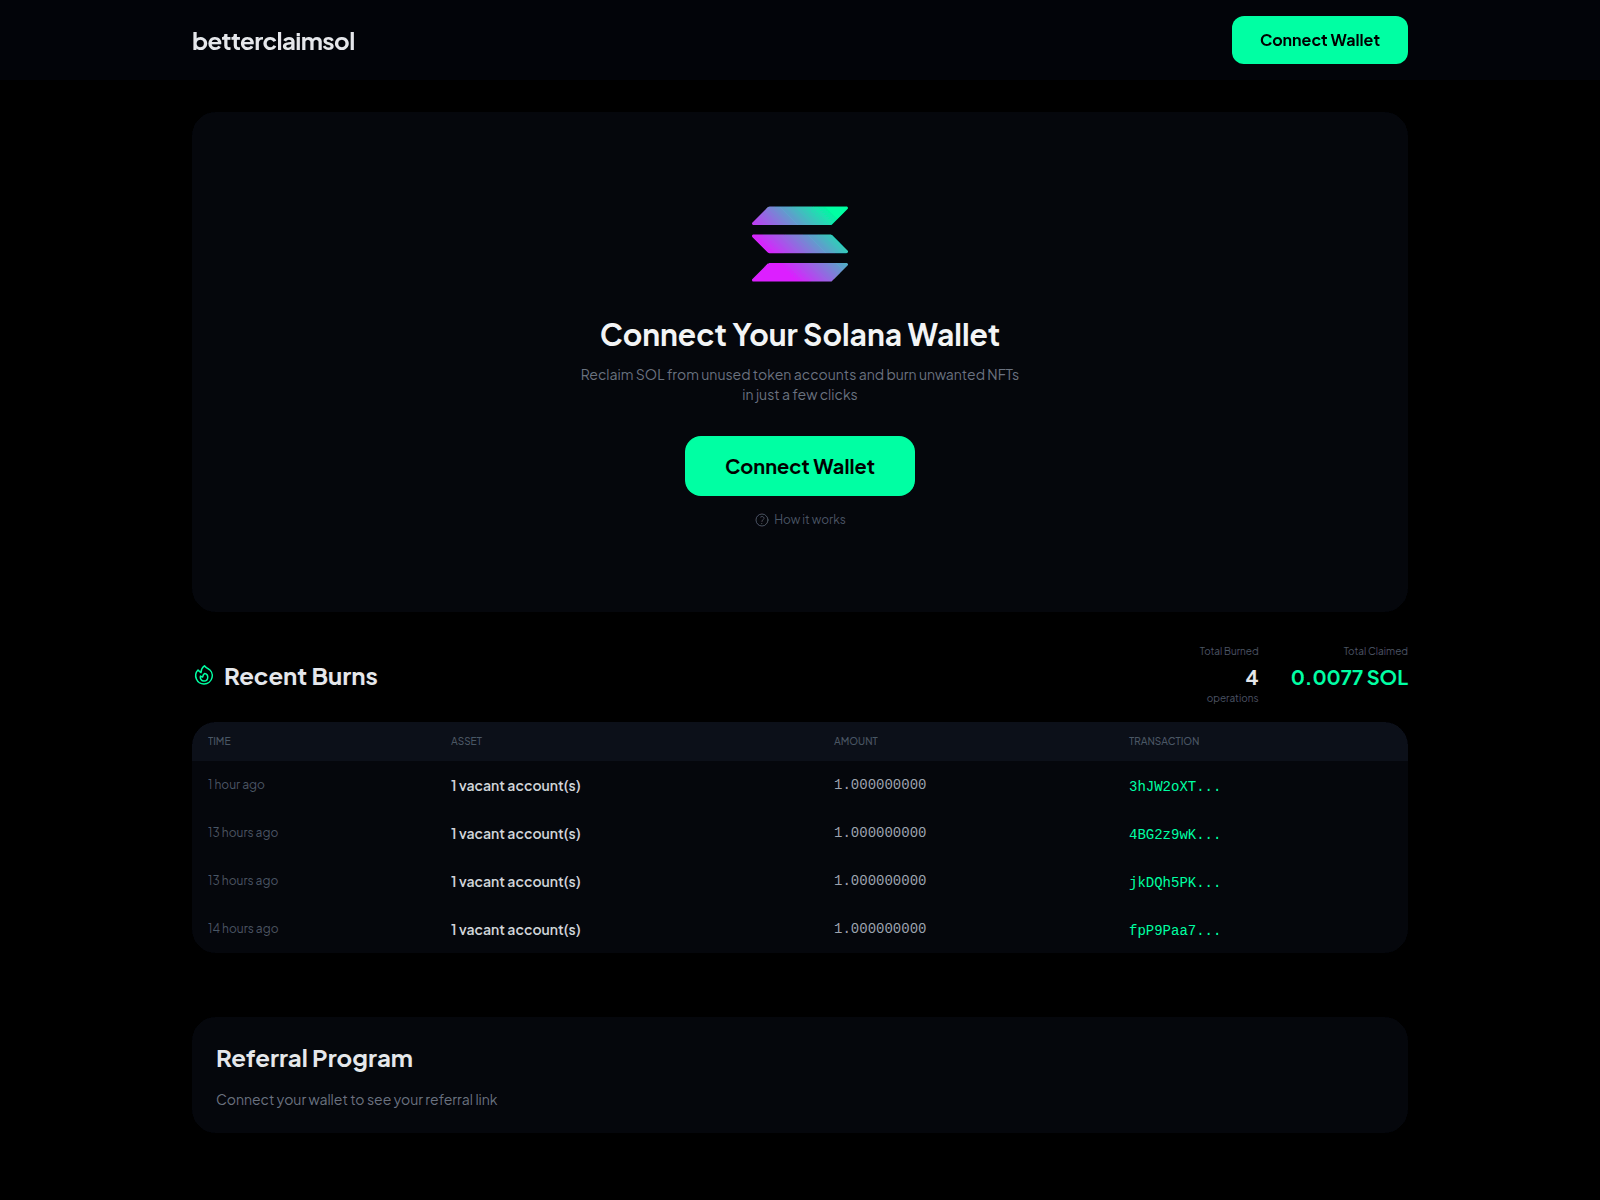
betterclaimsolana.com
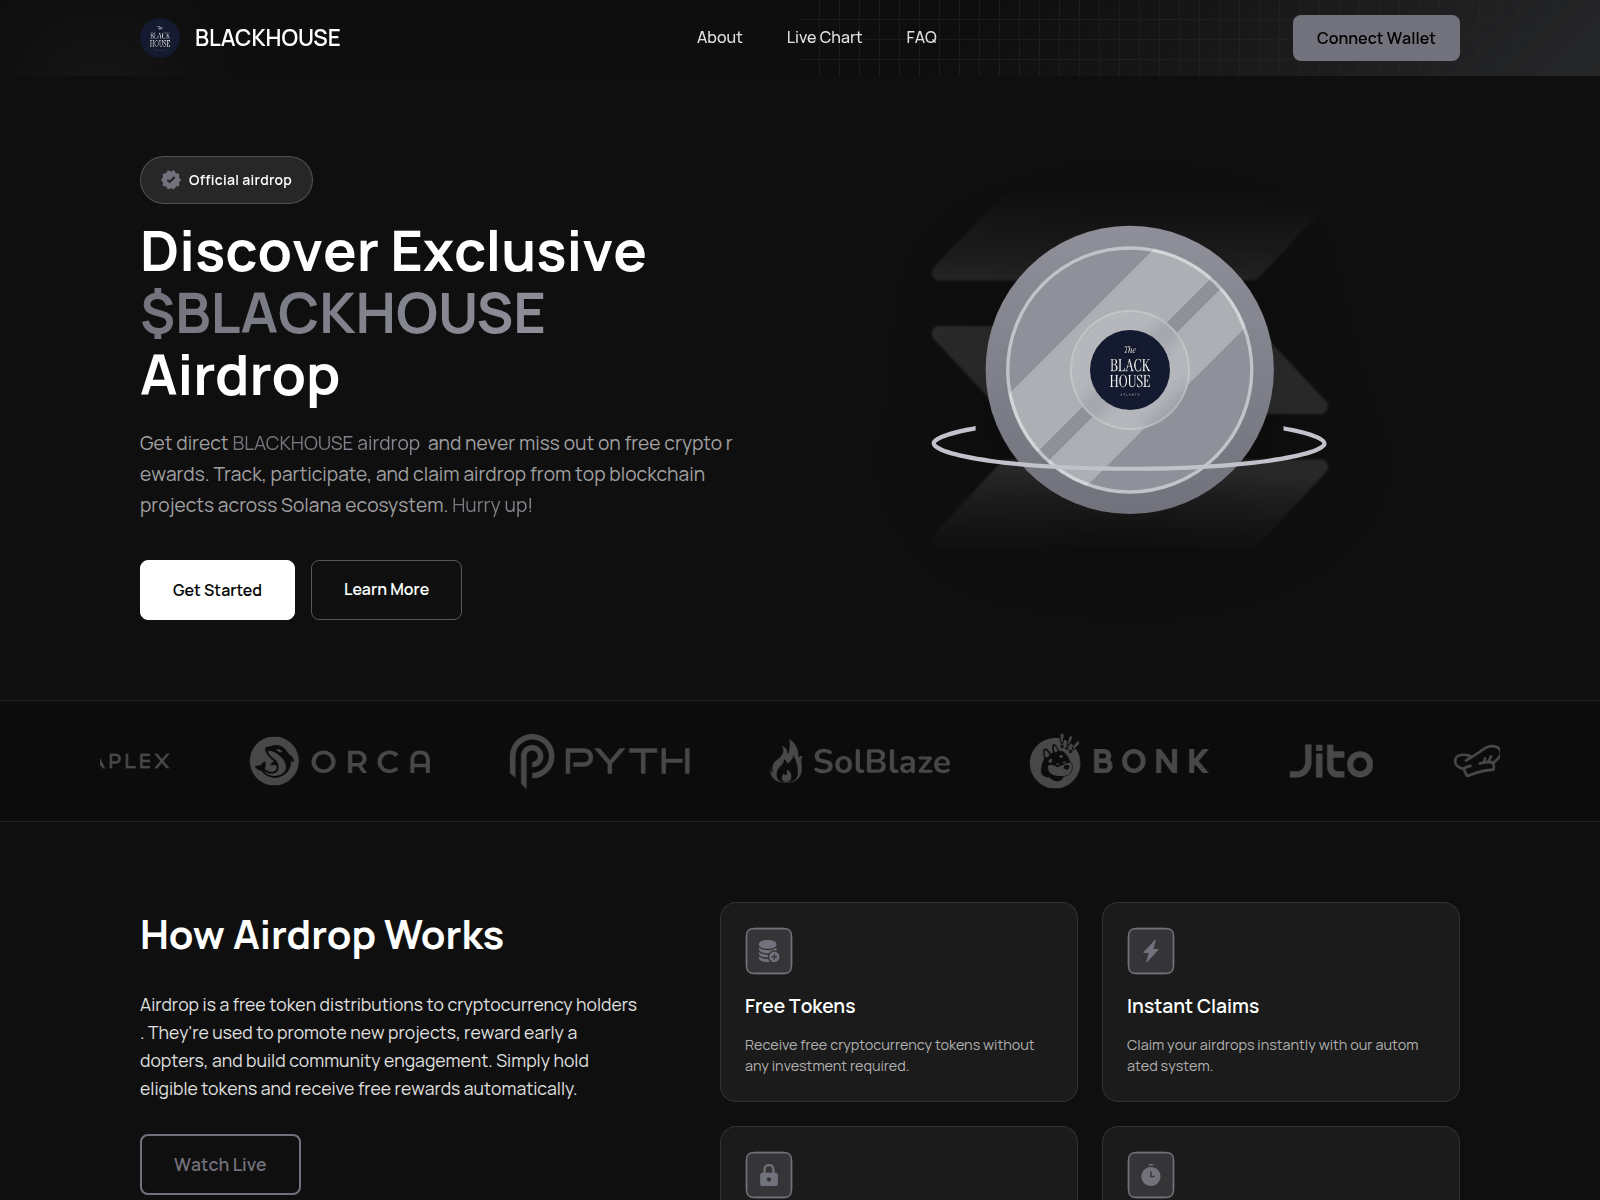
blackhouse.lol
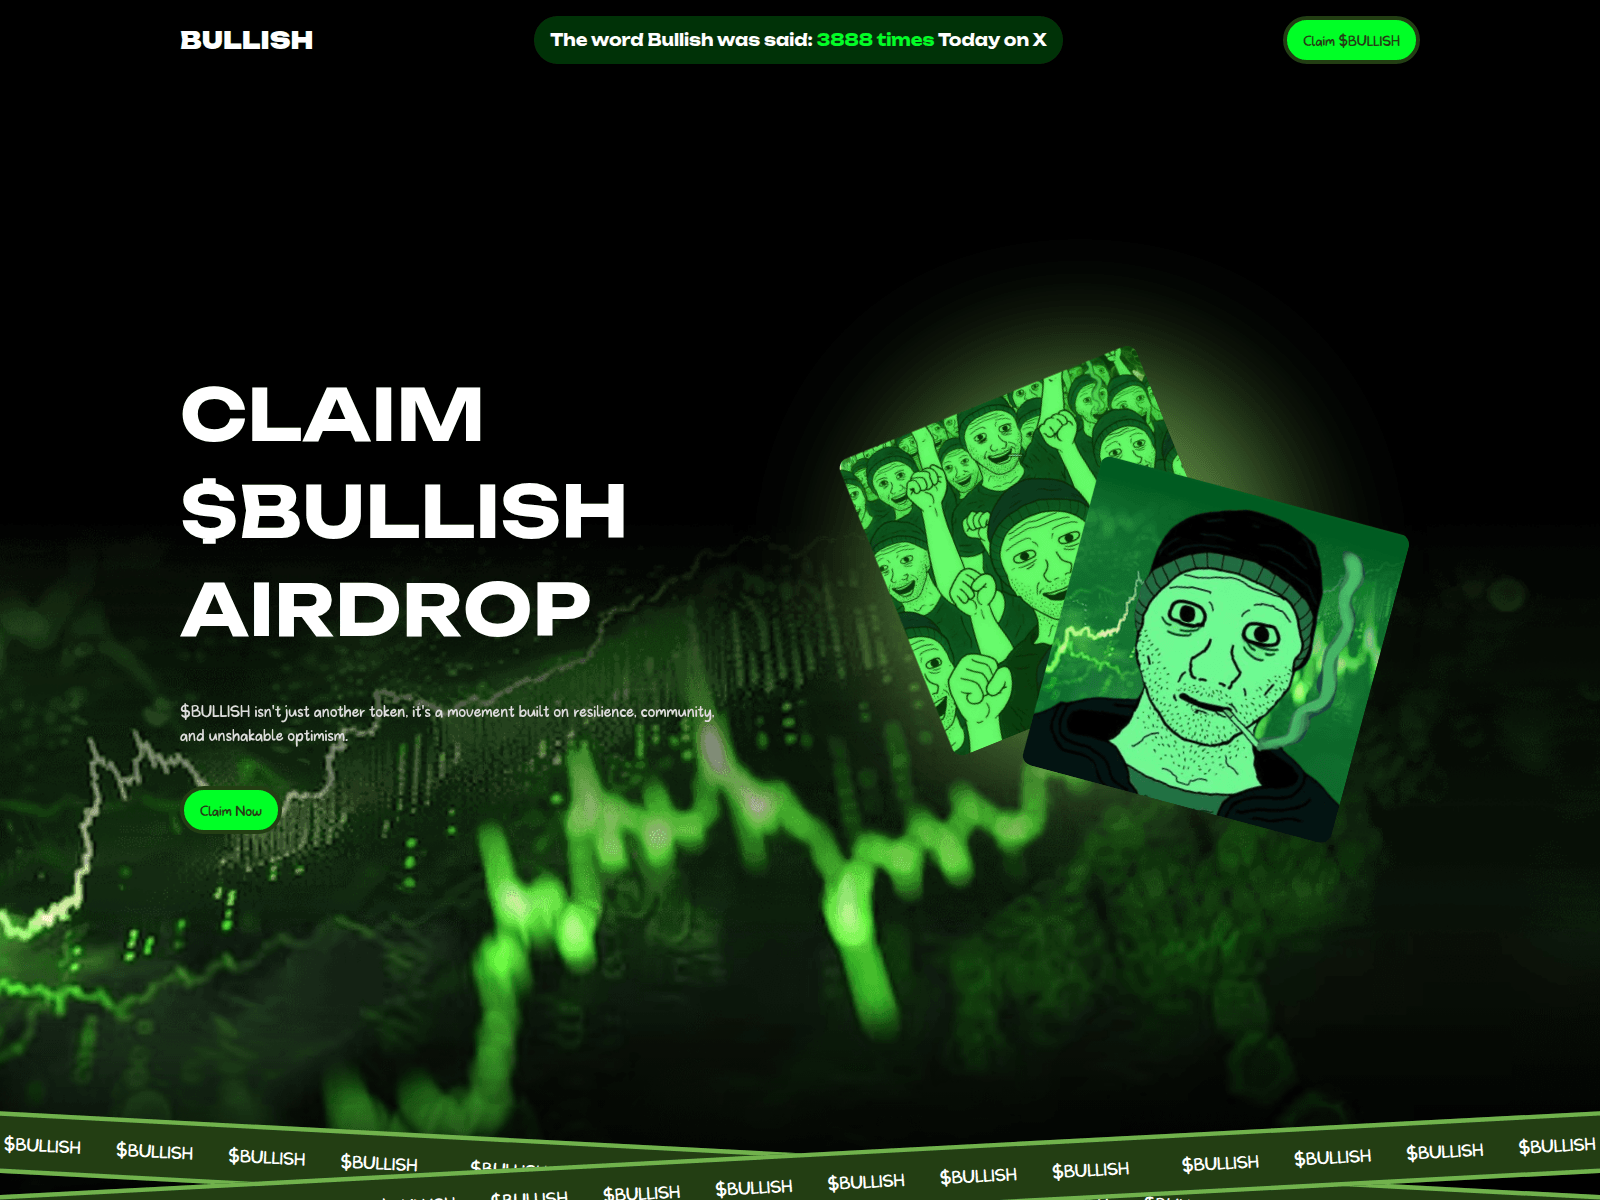
bullishcoin.solhq.cc
Процесс реагирования на угрозы
Как мы проверяем каждый домен в этом разделе и нейтрализуем подтверждённые угрозы. Полная визуализация конвейера →
Проверка по источникам данных об угрозах— каждый домен сканируется и сверяется со следующими источниками:
urlscan.ioСнимок экрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ОтчетCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безопасность FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПроверитьFull surface scan
 crt.sh
Передача данных партнёрам— подтверждённые детекты передаются 29 партнёрам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОбзор сайтаAviraCloud detectionAvast / AVGWeb Shield«Касперский»OpenTIPDr.WebOnline scannerNetcraftЛиквидация APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ОтчетHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust