セキュリティレポートへ移動
ドメインのセキュリティと脅威インテリジェンス
qrsu.io favicon

qrsu.io

“qrsu.io - QR Code & URL Shortener”

レジストラ
GoDaddy
Resolved IP
76.76.21.21
Registered
2024年9月20日
脅威の評決 クリティカル

Assessment based on the stored source evidence below. Review sources →

可用性 最後に確認されたアクティブな状態 以前は利用できませんでした。最新の観測結果に到達しました 観測された
Source: HTTP probe
VirusTotal 検出数: 16/89 Spamhaus DBL: DBL_PHISH ブランドの偽装: Google
OTX: 50 refs 2026年8月4日 Google CDN
API
このドメインは悪意のあるものとして報告されています
検出を報告するセキュリティ エンジン: 16。 細心の注意を払ってください — 資格情報や個人情報を入力しないでください。
レポート概要

qrsu.io — 最後に確認されたアクティブな状態 (HTTP 200). ブランドの偽装: Google; 詐欺タイプ: Credential Phishing. 証拠の概要: VirusTotal 16/89 (ADMINUSLabs, Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao); Spamhaus DBL_PHISH; PhishDestroy score 100/100. レジストラ: GoDaddy.

元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。

Additional indicators at a glance
Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
16 det.
OTX references
Gridinsoft
1/100
TLS証明書
期限切れまたは未検証
年齢
2.1 yr
観測ステータス
最後に確認されたアクティブな状態 200
PhishDestroy
DestroyList
掲載あり

Source evidence

8 sources

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.

VirusTotal

16 / 89

レポート
Interpretation & limits

Engine detections from this stored analysis. Vendors and collection times may differ from other sources.

Gridinsoft

1/100

Observation time not recorded
Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

Spamhaus DBL

DBL_PHISH

Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

OTX

50 community references

レポート
Interpretation & limits

Community publication references, not a vendor verdict or evidence of a common operator.

CFレーダー

provider verdict: clean

Observation time not recorded
レポート
Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

URLScan capture

保存されたレポート

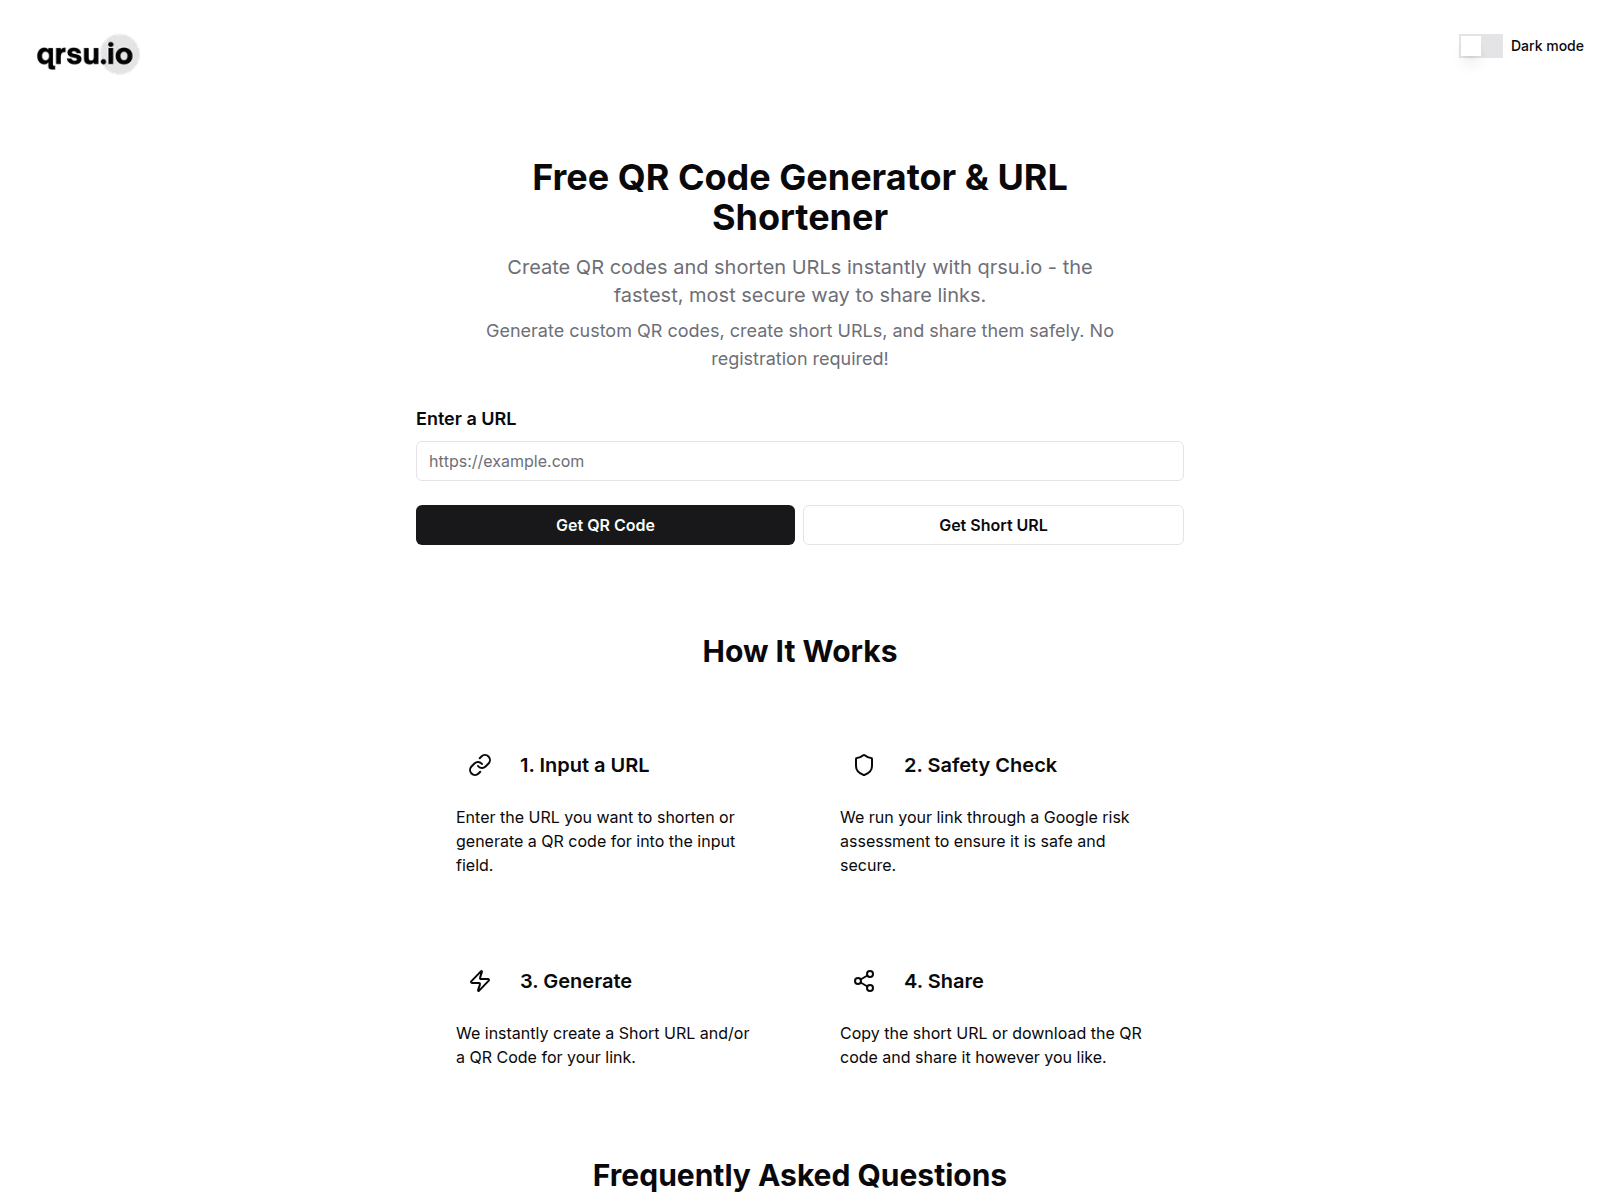
Stored URLScan capture preview
Observation time not recorded
レポート
Interpretation & limits

A preserved page image documents what the collector received; a capture is not a safety verdict.

URLScan verdict

分析完了

レポート
Interpretation & limits

This is the recorded automated analysis. Completion alone is not a safety verdict.

Google Safe Browsing

Checked; no threat flag recorded

レポート
Interpretation & limits

A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

証拠の概要

クリティカル
VirusTotal
16/89
OTX
50 community refs
URLScan
Stored capture

On 2026‑08‑04 the domain qrsu.io was observed flagged as part of an elevated‑risk generic phishing campaign. VirusTotal reports indicate that 16 of 91 scanning engines returned a malicious classification for the host, demonstrating a moderate consensus of detection across multiple vendors. The domain is listed on a single public security blocklist and is actively blocked by the PhishDestroy filtering service, confirming that at least one commercial anti‑phishing solution has incorporated it into its deny list.

No additional intelligence such as registrar details, registration date, hosting IP, autonomous system, SSL certificate information, or page title has been published in the current feed, so the underlying infrastructure remains opaque. The absence of these data points limits the ability to attribute the infrastructure to a specific operator or to map its network relationships. Nonetheless, the presence on VirusTotal and a known blocklist, combined with the elevated risk rating, suggests that qrsu.io is being used to harvest credentials or otherwise deceive users.

Defenders should add qrsu.io to local deny lists, enforce URL filtering rules that block the domain, and monitor outbound DNS queries for any attempts to resolve it. Network traffic to the domain should be logged and, where possible, redirected to a sandbox for deeper analysis. Continuous re‑evaluation is advised, as additional indicators such as hosting IPs, certificate fingerprints, or page content may emerge in future threat‑intel updates.

探知・回避の分析

クローキングおよびトラフィック分散の確認

まだスキャンされていません クローラーとブラウザの間に違いは見られていない

このホストに関するクローラーとブラウザの観測データの蓄積に加え、ケイタロ式トラフィック分散システム向けのリアルタイムフィンガープリントチェック。

保存されたクローキングフラグ
まだスキャンされていません
前回のクローキングスキャン
スキャナーが検知したサーバーヘッダー
Vercel

スキャナーに関する注記: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel

TDSの指紋認証のライブデモ
このパネルが開いている間、PhishDestroyスキャナーから、7つのケイタロの指紋と、クローラー対ブラウザの比較が実行されます。
待つ

保存済みキャプチャ · 2 captures

Domain details

ドメイン
URLScan Verdict 分析完了 score 0 report ↗
IP Context Vercel shared edge origin IP hidden Edge-IP の評判はこのドメインに起因しません。
OTX Tags 2026-032026-08activeall-domainsblocklistcontentcryptoドメインdrainerfraudlivemonthlyphishdestroyphishing+3 more
レジストラ GoDaddy US(US)
ICANNレジストリICANN Lookup (RDAP) →
登録情報作成日 2024年9月20日
Elapsed Since First Report 71 days
集計対象 Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: 最後に確認されたアクティブな状態.
各レポートの内容 保存された送信レポートの記録は、ベンダーの評決、登録データ、ホスティングの詳細、分類、スクリーンショットなど、その時点で入手可能な証拠を参照する場合があります。このページは、配信された正確なペイロード、受信者による受信、確認、またはアクションを推測するものではありません。
HTTPステータス200
技術詳細Provenance & timestamps
初確認2026年8月4日
DOM Analysisanalyzed 2026年10月9日score 98/1001 brand signal
Submitted URLhttp://qrsu.io/ZBktp
Favicon Hash
ページタイトル
qrsu.io - QR Code & URL Shortener
Impersonates
Google
TLS証明書
Hostname coverage not recorded · 発行者 Let's Encrypt · stored validity ends in 38 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
76.76.21.21
Network ASN
AS16509
Organization
Vercel, Inc
Observed location
Walnut, US
Server header
Vercel

Edge-IP の評判はこのドメインに起因しません。

ネームサーバー 1

  • ns72.domaincontrol.com

Location describes the IP network.

TLS証明書

Issuer
Let's Encrypt
Valid from
2026-08-14 11:27:57
Valid until
2026-11-12 11:27:56
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-10 16:03:08 UTC
Collection source
PhishDestroy collector
Certificate fingerprint7432a8e126ad4da568b9fd0b69a7a1b919972a714818659dd184e39e6d44f58c

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 76.76.21.21rapiddns.io

Latest Classified Outcome 2026-10-13 22:06:26 UTC

Primary outcome コンテンツ公開中 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation コンテンツ公開中 Ordinary HTTP content served 90% 2026-10-13 22:06:26 UTC
RDAP registration 不明
Observed timeline last reachable: 2026-10-13 22:06:26 UTC last content: 2026-10-13 22:06:26 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する 証拠を提出し、他の人を守る手助けをしましょう

VirusTotalによる分析

16 / 89 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed Previous stored snapshot: 17 detections
ADMINUSLabs
Criminal IP
alphaMountain.ai
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SafeToOpen
ソフォス
VIPRE
Webroot

アーカイブ済み証拠

Wayback Machine Snapshot
過去のスナップショットは証拠のレビューに利用可能です
View Archive
サイトパフォーマンス分析

Google PageSpeed Insights — mobile performance audit of qrsu.io · checked Aug 4, 2026

99
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
2.1s
Largest Contentful Paint
CLS
0.008
Cumulative Layout Shift
TBT
44ms
Total Blocking Time
SI
2.25s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-10-13 22:29:42 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain state transitioned from alive to dead.
  2. Domain Status Transition 2026-09-11 22:17:55 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain state transitioned from dead to alive.
  3. Domain Status Transition 2026-09-10 22:42:26 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain state transitioned from alive to dead.
  4. Domain Status Transition 2026-08-04 22:14:37 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain state transitioned from dead to alive.
  5. Domain Status Transition 2026-08-04 04:15:11 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain state transitioned from alive to dead.
  6. Threat First Observed 2026-08-04 01:04:35 UTC
    Source: PhishDestroy monitoring
    Event details
    Domain ingestion complete. Initial state is marked as unknown.

脅威対応 Pipeline

ディスカバリー
Analysis
Monitoring

16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

脅威の検知
qrsu.io 検出され、詳細な分析のためにキューに入れられた
2026年8月4日
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
2026年10月9日
URLScan.io Capture
保存済み URLScan report with capture artifacts
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in ウェイバック・マシン — historical evidence archived
2026年8月4日
VirusTotal
16/89 recorded on VirusTotal
2026年9月12日
OTX Community References
50 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026年10月9日
Brand Impersonation
Impersonation of Google
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
Technical Analysis Recorded
レポートには、保存されたテクノロジーまたはフォレンジック分析の結果が含まれます。
2026年10月15日
Content Observed Unavailable
監視により、使用できない応答 (HTTP 200)が記録されました。原因は独立して確立されていませんでした。
2026年10月14日
Site Came Back Online
Domain is responding again — monitoring resumed
2026年9月12日
Content Observed Unavailable
監視により、使用できない応答 (HTTP 200)が記録されました。原因は独立して確立されていませんでした。
2026年9月11日
Site Came Back Online
Domain is responding again — monitoring resumed
2026年8月5日
Content Observed Unavailable
監視により、使用できない応答 (HTTP 200)が記録されました。原因は独立して確立されていませんでした。
2026年8月4日
DestroyList 公開
2026年8月4日
Monitoring Continues
ドメインはアクセス可能またはアクセス制限されたままになります。今後のチェックにより、この観察結果が更新される可能性があります。
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

証拠および外部報告書

詳細な分析

このサイトによって何か影響を受けましたか?

5 evidence signal groups linked 0 reports recorded 最後に確認されたアクティブな状態
If credentials were compromised, report immediately. Do not engage with recovery scammers.

アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

ユーロポール
EU 加盟国の公式報告チャネルを見つける
National police directory
復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →

お住まいの地域の当局へ報告してください

サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。

97か国のディレクトリ

Template-based draft · optional AI wording assistance requires separate consent

AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます · 自分で確認して送信する

任意のドメインを確認する

保存されたブロックリスト、WHOIS、DNS、および公開スキャン証拠を使用した脅威分析

今すぐスキャン

フィッシングを報告する

不審なドメインを当社の脅威データベースに報告してください — コミュニティを守りましょう

レポート

リアルタイム脅威情報フィード

最近のフィッシングレポートと観察された可用性の変化

監視

最新情報を入手し、安全を確保しましょう

リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください

リアルタイム脅威情報フィード この掲載情報について異議を申し立てる
HTML · IFRAME

このレポートを埋め込む

この脅威情報を、ご自身のウェブサイトやブログで共有してください

embed.html
<iframe
  src="https://phishdestroy.io/ja/embed/domain/qrsu.io"
  title="PhishDestroy threat report for qrsu.io"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>