Skip to security report
Domain security and threat intelligence
web-whatsapp.co favicon

web-whatsapp.co

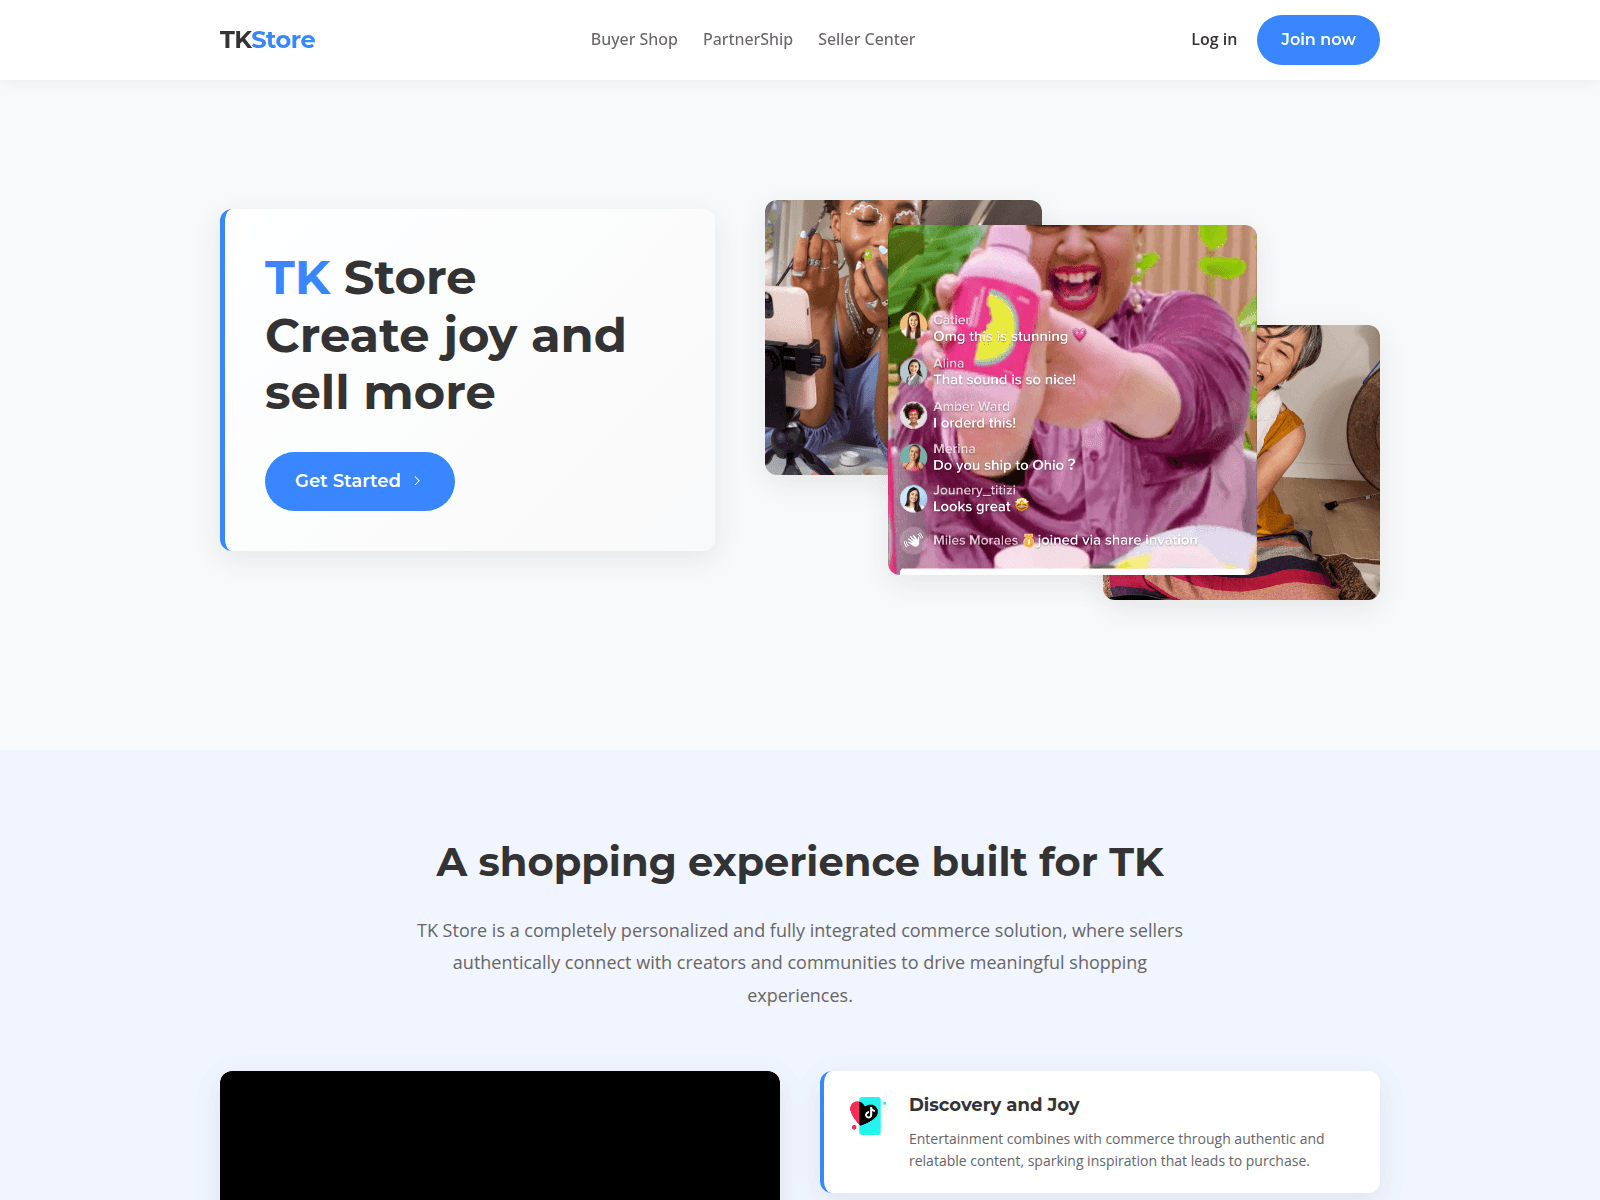
“TK Store | buy, sell and discover on TK”

Registrar
GoDaddy
Resolved IP
45.135.237.33
Registered
Aug 10, 2025
Threat verdict Critical
Availability Content unavailable Content was unavailable in the latest observation
VirusTotal detections: 18/89 Brand impersonation: Telegram
OTX: 15 refs Dec 16, 2025 Telegram
API
This domain has been flagged as malicious
Security engines reporting a detection: 18. Exercise extreme caution — do not enter credentials or personal information.
VirusTotal
VirusTotal
18 det.
OTX references
CF Radar
Malicious
URLScan
URLScan
TLS Certificate
Expired or unverified -268d
Age
1.2 yr
Observed status
Content unavailable 502
PhishDestroy
DestroyList
Listed

Source evidence

7 sources

VirusTotal

18 / 89

Report

CF Radar

provider verdict: malicious

Report

URLScan verdict

malicious

Report

Google Safe Browsing

Threat flag recorded

Report

PhishStats

checked — no match recorded

OTX

15 community references

Report

URLScan capture

stored report

Stored URLScan capture preview
Report
Network Security Intelligence
CF Cloudflare Radar Verdict Malicious
Phishing Security threats Phishing

Evidence Summary

Critical
VirusTotal
18/89
OTX
15 community refs
URLScan
Stored capture

This domain, web-whatsapp.co, is flagged as a high-risk phishing infrastructure designed to impersonate WhatsApp Web, a widely used messaging platform. Analysis indicates the domain was likely engineered to harvest user credentials through fraudulent login portals, mimicking the legitimate WhatsApp Web interface. The page title, 'TK Store | buy, sell and discover on TK,' suggests an attempt to disguise the malicious intent under a generic e-commerce facade, though the primary objective remains credential theft. No specific drainer kit signatures were identified in the available intelligence, but the domain aligns with known phishing tactics targeting communication platforms. Infrastructure analysis reveals the domain was registered on August 10, 2025, through GoDaddy.com, LLC, and resolves to the IP address 45.135.237.33, hosted under AS153656 (OWGELS INTERNATIONAL CO., LIMITED) in Hong Kong. Google Safe Browsing explicitly flags this domain as phishing, while VirusTotal reports 19 out of 95 security vendors detecting it as malicious. The domain appears on two security blocklists, including PhishDestroy and PhishingDB. The SSL certificate, issued by Let's Encrypt (serial number E8), provides minimal assurance, as phishing domains frequently leverage free certificates to appear legitimate. As of the latest assessment, web-whatsapp.co has been taken offline, likely due to suspension by the registrar or hosting provider following abuse reports. However, the residual risk remains elevated due to the domain's recent creation and the potential for threat actors to re-establish infrastructure under similar naming conventions. Organizations and users are advised to block the domain and its associated IP (45.135.237.33) at the network level, monitor for credential leakage, and validate any WhatsApp Web sessions against the official domain (web.whatsapp.com). Proactive hunting for related domains using the seed '8d4780' in threat intelligence feeds may uncover additional malicious infrastructure.

Detection-evasion analysis

Cloaking and traffic-distribution check

Not yet scanned No crawler-versus-browser difference has been recorded yet

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan

Scanner note: transient_502: raw=transient_502; http=502; via=http_proxy

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this panel is open.
Waiting

Stored Capture · 2 captures

Domain details

Domain
URLScan Verdict Malicious score 100 Phishing brand: Tiktokshop report ↗
Google Safe Browsing Flagged Social engineering checked Mar 2, 2026
IP Reputation abuse score 0/100 0 reports checked Aug 26, 2026
OTX Tags phishingphishing-databasethreatfox
Registrar GoDaddy US(US)
RegistrationCreated Aug 10, 2025
HTTP Status502 Error
Time to First Unavailability 90 days
What we count Elapsed time from the first stored abuse report to the first observation that the content was unavailable. This does not establish the cause.
What each report contains Stored outgoing-report records may reference evidence available at the time, such as vendor verdicts, registration data, hosting details, classifications, or screenshots. This page does not infer the exact payload delivered, receipt, acknowledgement, or action by a recipient.
Technical detailsProvenance & timestamps
First DetectedDec 16, 2025
DOM Analysisanalyzed Mar 11, 2026score 100/1001 brand signal
Submitted URLhttp://web-whatsapp.co/
Page Title
TK Store | buy, sell and discover on TK
Impersonates
Telegram
TLS Certificate
Certificate hostname mismatch · Issued by Let's Encrypt / E8

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
45.135.237.33
Network ASN
AS153656
Organization
OWGELS INTERNATIONAL CO., LIMITED
Observed location
Hong Kong, HK
Server header
nginx

Nameservers 2

  • ns25.domaincontrol.com
  • ns26.domaincontrol.com

Location describes the IP network.

TLS certificate

Issuer
Let's Encrypt / E8
Valid from
2025-10-16 06:16:57
Valid until
2026-01-14 06:16:56
Hostname coverage
Certificate hostname mismatch
Validity
Stored certificate expired
Collection time
2026-03-12 01:31:17 UTC
Collection source
PhishDestroy collector
Certificate fingerprint6000ac11aafcaaac9e6f753247567674a2d0445616f69a976b17e4dc80166c1d
Certificate names · 1 SANs
  • abavn.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 45.135.237.33rapiddns.io

Latest Classified Outcome 2026-10-08 20:20:32 UTC

Primary outcome DNS inactive reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: Unknown Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Unknown Origin unreachable Http 5xx 20% 2026-10-07 02:07:08 UTC
RDAP registration Unknown
Observed timeline last reachable: 2026-09-15 22:18:16 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

18 / 89 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 20 detections
AILabs (MONITORAPP)
alphaMountain.ai
BitDefender
Chong Lua Dao
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Google Safe Browsing
Gridinsoft
Kaspersky
LevelBlue
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot

Archived Evidence

Wayback Machine Snapshot
A historical snapshot is available for evidence review
View Archive
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of web-whatsapp.co · checked Mar 1, 2026

75
Needs Work
Performance
FCP
2.95s
First Contentful Paint
LCP
5.26s
Largest Contentful Paint
CLS
0.002
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
3.33s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-03-11 03:04:09 UTC
    VirusTotal scanner detections updated from 18 to 22. Added scanner alerts: Cluster25, Emsisoft, Netcraft, OpenPhish, Trustwave. Resolved alerts: Seclookup.
  2. Cloudflare Radar Scan 2026-03-06 23:29:54 UTC
    Cloudflare Radar scan registered: View Radar report.
  3. VirusTotal Detections Update 2026-03-01 05:29:55 UTC
    VirusTotal scanner detections updated from 19 to 18. Resolved alerts: MalwareURL.

Threat Response Pipeline

Discovery
Analysis
Monitoring

18 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Threat Ingested
web-whatsapp.co detected and queued for full analysis
Dec 16, 2025
URLScan.io Capture
Stored URLScan report with capture artifacts
Feb 26, 2026
URLScan Verdict
URLScan returned a malicious verdict · score 100
Jul 29, 2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
Mar 14, 2026
VirusTotal
18/89 recorded on VirusTotal
Sep 19, 2026
Google Safe Browsing
Mar 2, 2026
OTX Community References
15 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
Mar 1, 2026
CF Radar: Malicious
Cloudflare Radar classified this domain as Phishing, Security threats, phishing
Brand Impersonation
Impersonation of Telegram
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
Feb 26, 2026
Technical Analysis Recorded
The report contains stored technology or forensic-analysis results.
Oct 9, 2026
VT Detection +4
+4 new detections (18 → 22): Cluster25, Emsisoft, Netcraft, OpenPhish +1
Mar 11, 2026
Cloudflare Radar Scan
Scanned with Cloudflare Radar; network analysis completed.
Mar 7, 2026
VT Detection -1
1 detection removed (19 → 18)
Mar 1, 2026
DestroyList Published
Dec 16, 2025
Content Observed Unavailable
The latest stored checks indicate that the reported content is unavailable; this does not establish who or what caused the change.
Jun 6, 2026
Time to First Unavailability
2152 hours elapsed from detection to the first unavailable observation.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Community reports

Reported by 1 community member, first seen Mar 9, 2026

Stored reports
1
Unique reported URLs
1
Accepted1

Evidence & External Reports

Deep Analysis

Were You Affected by This Site?

5 evidence signal groups linked 0 reports recorded Content unavailable
If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory

Template-based draft · optional AI wording assistance requires separate consent

Template-based draft • optional AI wording assistance requires separate consent · Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive
Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/web-whatsapp.co"
  title="PhishDestroy threat report for web-whatsapp.co"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>


