VirusTotal
19 / 93
Report

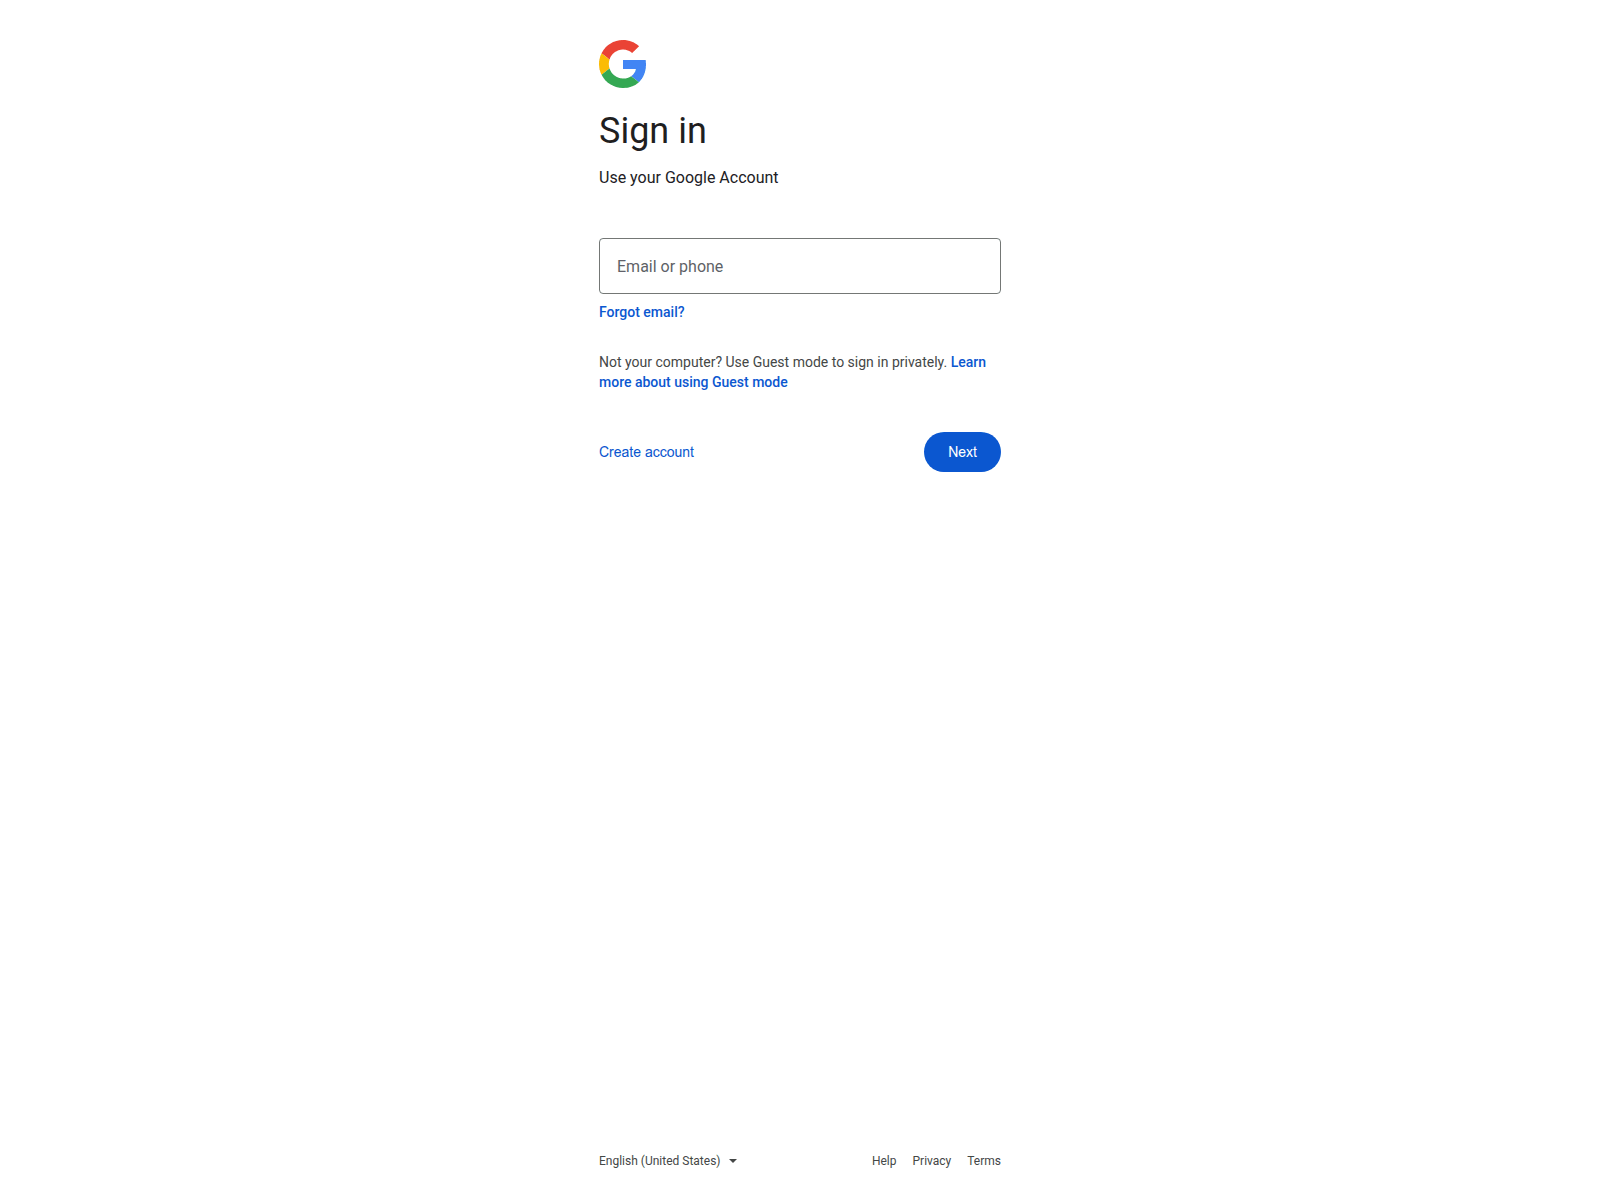
“Sign in - Google Accounts”

19 / 93
3 threat-system alerts
Reportprovider verdict: malicious
ReportThreat flag recorded
Reportchecked — no match recorded
no community references
Reportstored report
 Report
Analysis completed
Report| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | charming-marshmallow-61005d.netlify.app |
malicious | Sinkholed |
| OpenDNS | charming-marshmallow-61005d.netlify.app |
phishing | Phishing Block |
| DNS4EU | charming-marshmallow-61005d.netlify.app |
malicious | Sinkholed |
Infrastructure analysis reveals that the domain charming-marshmallow-61005d.netlify.app, registered on March 2, 2026, was flagged as a high-risk phishing site impersonating Google Accounts. The page title 'Sign in - Google Accounts' directly indicates an attempt to mimic Google's authentication portal, aligning with the scam type classified as banking phishing. The domain was hosted on Netlify infrastructure and resolved to IP 63.176.8.218, located in Germany under Amazon.com, Inc.'s AS16509. Google Safe Browsing categorized this domain as social engineering, while PhishDestroy and at least one additional security blocklist blocked access to it. The SSL certificate, issued by DigiCert Inc (DigiCert Global G2 TLS RSA SHA256 2020 CA1), does not mitigate the risk, as phishing sites frequently use valid certificates.
As of July 24, 2026, the domain returns an HTTP 404 status, suggesting it has been taken offline, though residual DNS or cached records may persist. Nineteen of 93 security vendors on VirusTotal flagged the domain, reinforcing its malicious classification. No evidence of a phishing kit or additional brand impersonation beyond Google was identified in the available data. Defenders should treat this domain as compromised infrastructure.
Historical logs should be reviewed for connections to 63.176.8.218 or the domain itself, particularly during its active period. Netlify's role as the registrar and hosting provider indicates a pattern of abuse leveraging legitimate cloud platforms. While the domain is currently offline, similar infrastructure may re-emerge under different subdomains or aliases. Organizations are advised to block the domain and IP at perimeter controls and monitor for related indicators of compromise.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
NetlifyScanner note: dead_http: raw=http_404; http=404; via=https_proxy; server=Netlify
 (US)
Edge-IP reputation is not attributed to this domain.
Location describes the IP network.
bc3a8134c21a842e64ea34d488826dd2ba50f59a3bcbaed1e6b71a4242de1478netlify.appSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of charming-marshmallow-61005d.netlify.app · checked Mar 2, 2026
18 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Reported by 1 community member, first seen Mar 2, 2026
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Shared edge IP; unrelated tenants may be present.
These domains also target Gmail users. View all Gmail threats →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive







