VirusTotal
5 / 91
Report

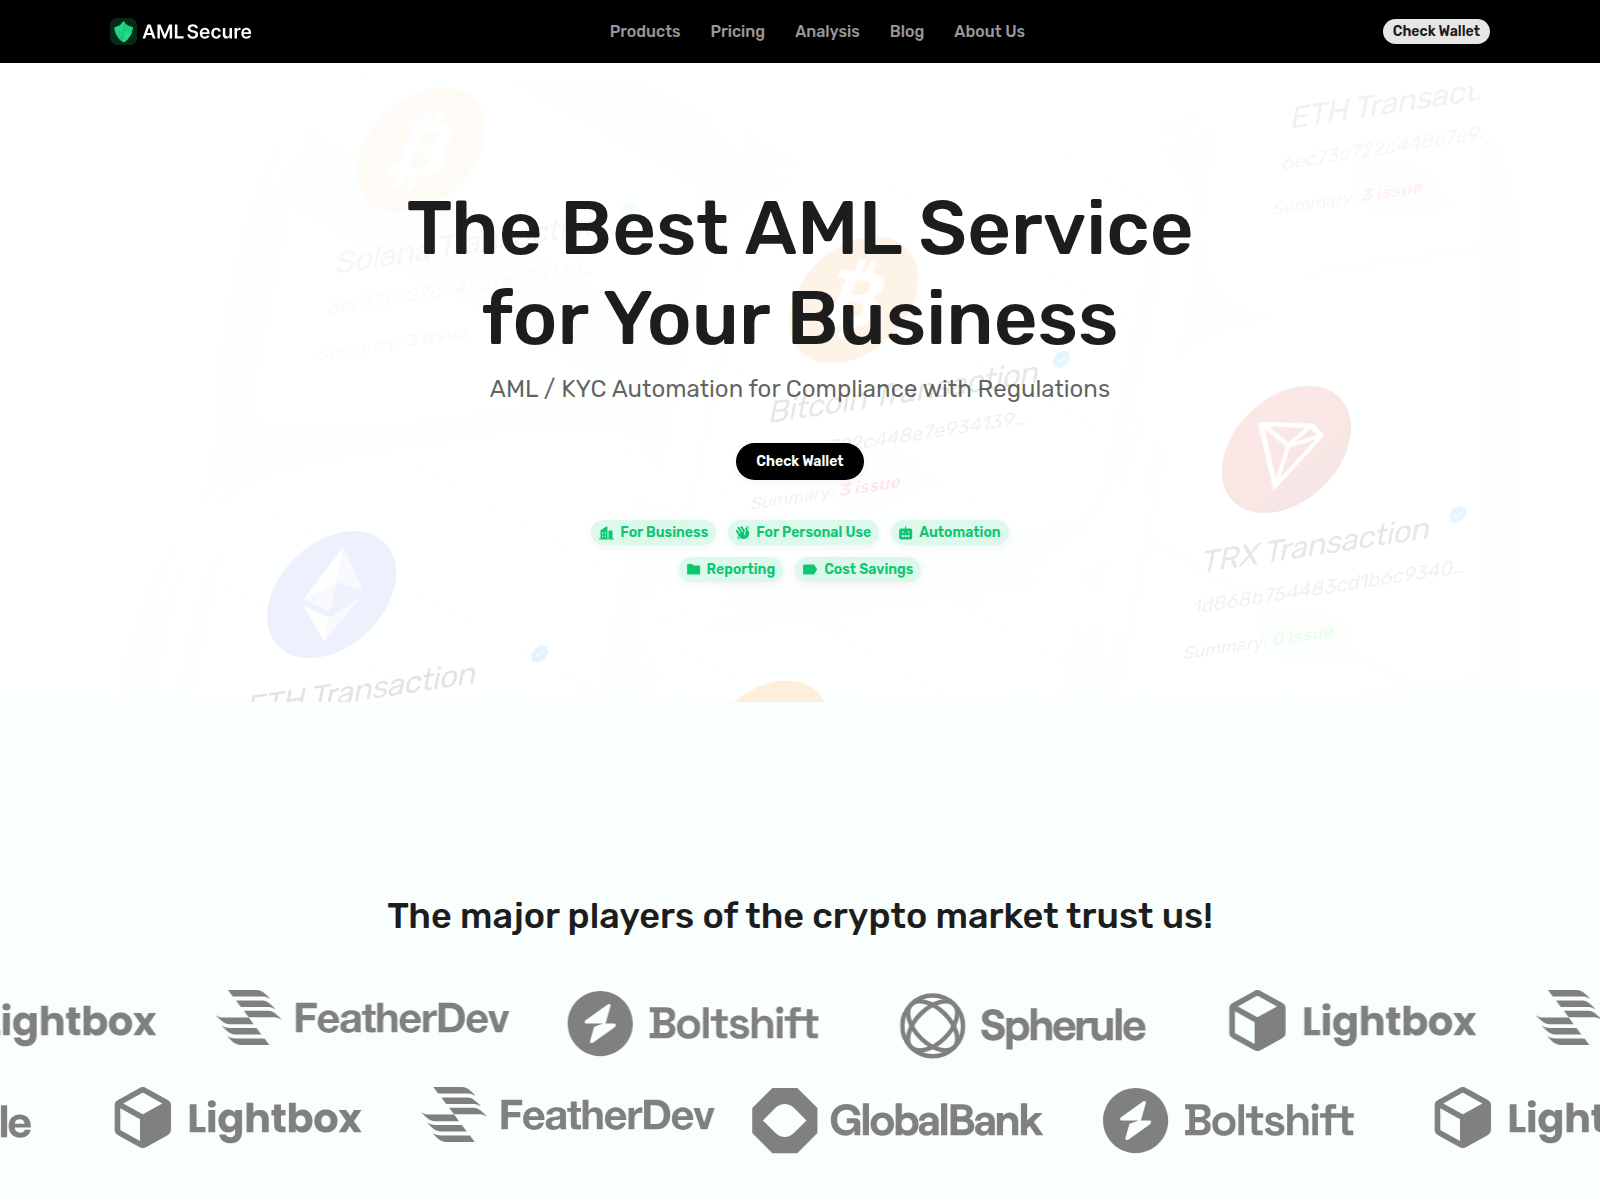
“The Best AML Service for Your Business - AML Secure”

Analysis of the domain amlsecure.blog, observed as offline at the time of reporting on July 25 2026, indicates that it was used for credential phishing aligned with a crypto‑related scam. The site was registered on October 29 2025 through Web Commerce Communications Limited, a registrar frequently associated with malicious registrations. No SSL certificate was presented, leaving the connection unencrypted. The authoritative nameservers are augustus.ns.cloudflare.com and eve.ns.cloudflare.com, pointing to Cloudflare’s DNS service. DNS resolution returned the IP address 172.67.141.15, which belongs to AS13335 Cloudflare, Inc. located in the United States.
The page title retrieved from the site reads “The Best AML Service for Your Business – AML Secure,” suggesting a fraudulent attempt to lure victims interested in anti‑money‑laundering services. Reputation services rate the domain extremely poorly: Scamadviser assigns a trust score of 1/100, Gridinsoft 0/100, and the domain appears on five security blocklists. VirusTotal scans reported four detections out of ninety‑five vendors, confirming malicious activity. The site is also listed on blocklists operated by PhishDestroy, ScamSniffer, Polkadot, Enkrypt, and Codeesura.
The combined evidence points to a credential‑phishing infrastructure targeting users seeking crypto or AML solutions. Uncertainty remains regarding the exact phishing kit or any additional payloads, as no content analysis beyond the title is available. Defenders should block the domain and its associated IP at perimeter defenses, update URL filtering rules, and monitor for any future re‑use of the Cloudflare IP range. Incident responders should also inspect logs for traffic to amlsecure.blog and consider tightening controls around AML‑related communications to mitigate potential credential compromise.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: transient_502: raw=transient_502; http=502; via=http_proxy
 (MY)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Edge-IP reputation is not attributed to this domain.
augustus.ns.cloudflare.comeve.ns.cloudflare.comLocation describes the IP network.
12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Reported by 1 community member, first seen Nov 3, 2025
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Shared edge IP; unrelated tenants may be present.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive